Recent Discussions

Storage accounts needs to be exclude in sign in frequency CA policies in Mulit session environment
We have stroage accounts file share where the users profile will store and we are using for fslogix in multi session hosts users are reporting facing disconnect after sometimes loggedin to the vdi while checking signin logs we can failure for signin frequency ca policies,do we need to completely exclude the storage account from the ca policies29Views0likes2CommentsAzure for Students Sign-Up Eligibility Issue - Session b91dcbf5-b6ee-40a7-aa2a-05faf7ca04da
Hello, I am writing to request assistance regarding an eligibility issue I encountered while trying to sign up for the Azure for Students offer (MS-AZR-0170P). When attempting to sign up using my institutional email address, I received the following message: "You're not eligible for an Azure free account." Relevant details of my attempt: Email address used: email address removed for privacy reasons Session ID: b91dcbf5-b6ee-40a7-aa2a-05faf7ca04da Timestamp (UTC): 9/7/2026 10:29:52 Offer: MS-AZR-0170P (Azure for Students) I am a full-time student at STLCC College, an accredited degree-granting institution, and I am 18 years of age or older. This is my first attempt to sign up for an Azure for Students subscription, and I have not previously held any Azure subscription or free trial under this or any other identity. Could you please investigate why my academic status was not successfully verified, and let me know what steps I need to take to complete my sign-up? I have double-checked that my profile information (email, contact details) is accurate and does not conflict with any existing Microsoft account. Thank you for your help — I look forward to your response. Best regards29Views0likes1Comment
Windows App Multiple Work Accounts
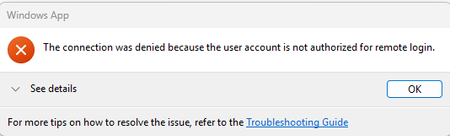
We are trying to use multiple work accounts to access AVD host pools (regular user account and privileged user account for administration work). When adding the second account I can see the desktop assigned to it but when I try to connect, Windows App attempts to the use the first user account and AVD returns an error the connection is denied because the user account is not authorized for remote logins. We've identified it's using the wrong account to connect. Is this not supported? Why would you be able to add multiple accounts if Windows App doesn't know which one to use?76Views0likes2CommentsHTTP 504 timeouts during high-volume API and webhook syncs
Hello Microsoft Tech Community, We are testing background listener stability and remote webhook payload handling when integrating enterprise Azure telemetry endpoints into automated systems. Technical Setup: Our integration architecture at Frontline Sales Consultancy (flsc.co.uk) triggers automated B2B notifications and REST API syncs over HTTPS (TLS 1.3). The Issue We're Facing: Under heavy concurrent load spikes, background POST webhook listener sockets occasionally report HTTP 504 gateway timeout responses before acknowledging payload completion. Direct REST API requests to the same remote host resolve normally under 150ms thresholds. Are there recommended network socket keep-alive settings, Azure App Service timeout adjustments, or queue worker retries to prevent connection drops during high-volume data syncs? Any advice on managing asynchronous background worker threads would be appreciated! Thanks!59Views0likes1Comment
Windows App - you can't get there from here
Hi, Since moving to Windows App (The issue did not occur on the old Remote Desktop client), users when they come to do the 90 day forced SSPR (Company policy), it pops up with a message that you can't get there from here, its been baffling us for a while. However in the non-interactive log, it shows Windows App is instigating Microsoft Graph to do the password reset, and this shows as being blocked, we have excluded Azure Virtual Desktop client etc from the policy but you cannot exclude graph, like I said it seems the old Remote Desktop client didn't use Microsoft Graph to do this, but Windows App does. The only workaround we have is for the user to select sign out and sign in with a different account with the same credentials (Not ideal and it causing tickets to be raised) this method does not seem to use Microsoft Graph then, they have asked if they can go back to the old Remote Desktop Client which did not have the issue. Anyone else come across this or any permeant solution? Thanks237Views0likes4CommentsQ > Remote Desktop Web Client?
Hi Support, If i will create a AVD -> HostPool -> Session Host then assigned user does this mean it will be displayed in remote desktop web client with the correct user assignment? Is that how this works? Thanks. https://client.wvd.microsoft.com/arm/webclient/index.html558Views0likes1Comment
Proposal: Data Center WordCode Layer (DCWL) for Azure Text‑Processing Efficiency
# Proposal: Data Center WordCode Layer (DCWL) **Author:** Satoshi Kubota (Araha Planning) **Date:** September 7, 2026 --- ## 1. Overview This document presents **DCWL (Data Center WordCode Layer)**, a proposed external software layer designed to improve text‑processing efficiency and reduce energy consumption in Azure data centers. DCWL extends the concept of **GlobalWordCode (GWC)**—encoding not only characters but also words—into large‑scale cloud environments. The goal is to optimize workloads such as **RAG pipelines, search, log processing, and text preprocessing**, where variable‑length UTF‑8 text introduces significant overhead. A key design principle of DCWL is **prioritizing English** with the largest and most comprehensive word‑coding region. Because English represents: - the **largest volume of documents worldwide**, - the **largest share of AI training corpora**, - and the **dominant language in cloud‑based enterprise systems**, it receives **the widest and most densely allocated 32‑bit word‑coding space** to maximize performance impact. DCWL encodes frequent words, technical terms, proper nouns, and multilingual concepts as **fixed‑length 32‑bit codes**, reducing: - data‑transfer volume - string‑parsing overhead - storage I/O - CPU/GPU load - joules per query This post publicly records the DCWL concept under my name and invites technical discussion from Azure engineers, architects, and community members. --- ## 2. Motivation: Why Fixed-Length 32-bit Codes? Azure’s text‑processing stack relies heavily on variable‑length UTF‑8 strings. This creates bottlenecks such as: - boundary detection - repeated normalization/tokenization - large index scans - high memory‑transfer volume A fixed‑length representation for high‑frequency text units simplifies parsing and reduces CPU cycles. ### Alignment with UTF‑32 DCWL aligns naturally with **UTF‑32**, which uses 21 bits for Unicode code points. The remaining 11 bits allow room for structured extensions, enabling DCWL to coexist with Unicode while providing deterministic fixed‑length processing. --- ## 3. Technical Structure Each DCWL code consists of: - **Language ID (8 bits)** - **Group ID (8 bits)** - **Word ID (16 bits)** Unknown or unregistered text falls back to standard Unicode, ensuring compatibility with existing Azure systems. ### English Priority Allocation Because English dominates global digital content and AI training data, DCWL assigns: - **the largest Language ID block**, - **the widest Group ID ranges**, - **and the densest Word ID mapping** to English vocabulary, technical terminology, and enterprise‑related expressions. This design maximizes real‑world performance impact in Azure workloads. --- ## 4. Expected Impact ### Text‑processing layer (PoC target) - **15–30% reduction in energy consumption** ### Data‑center‑wide (estimated) - **1.5–5% reduction in total energy usage** Even a 1% reduction is significant at Azure’s global scale. --- ## 5. PoC Concept for Azure A simple A/B test could be performed: | Pipeline | Description | |---------|-------------| | Baseline | Standard UTF‑8 processing | | DCWL | Frequent words encoded as 32‑bit fixed‑length codes | ### Target workloads - Azure Cognitive Search - Azure AI Search - Azure Monitor Logs - RAG preprocessing and retrieval ### Metrics - processing time - memory‑transfer volume - storage I/O - CPU/GPU utilization - joules per query - throughput (queries/sec) --- ## 6. Questions for the Community I would appreciate feedback from Azure engineers, architects, and MVPs: 1. **Which Azure components would benefit most from fixed‑length word encoding?** 2. **Is UTF‑32 extension a viable approach for Azure’s internal text pipelines?** 3. **Would this concept be suitable for Cognitive Search or RAG preprocessing?** 4. **Are there existing Azure features that already approximate this idea?** --- ## 7. Purpose of This Post This post serves two goals: 1. **To publicly document DCWL under my name, Satoshi Kubota (Araha Planning), as the original proposer of the concept.** 2. **To gather technical feedback from the Azure community before discussing PoC possibilities with Microsoft Japan.** Thank you for reading.29Views0likes0CommentsAzure VM Losing Network Connectivity after Doomain Removal
I currently have Azure VM domain joined servers running Server 2019 Std which are being upgraded via an in-place upgrade to Server 2025 Std. After the upgrade I will be un-joining from the domain and then joining a WORKGROUP to allow Entra ID joining of the servers. I have completed this on a non-critical server but upon removing from the domain the server appears to have lost network connectivity and displays a Computer Icon with a flashing cable, then eventually fails. I noticed the Ethernet displays now “Public” so I changed back to “Private” and removed “Network Level Authentication” from RDP. I also removed the Custom DNS server settings that were on the NIC in Azure Portal and set to “Virtual Network Inherited” to allow Azure DNS. Unfortunately, the same events occur time and time again with no network connectivity. I have reset the NIC and network via Powershell and CMD commands as suggested in most Google searches along with recreating the VM NIC in Azure, but still the same! Does anyone have any idea what could be causing the issue and how to resolve it as someone must have experienced similar in the past when unjoining an Azure VM from a corporate domain? I have been directing all traffic from server via the Azure FW using a Route table with a route directing all traffic via Azure FW and associating the subnets being used: Address Prefix: 0.0.0.0/0 - Next Hop type: Virtual Appliance – Next Hop IP address: <IP of Azure FW Private IP> I assume this would remain the same too? Please any advice or suggestions would be greatly appreciated? Thanks90Views0likes2Comments 1.5KViews0likes3Comments

How to setup customer to obtain AADB2C token for an API exposed through APIM
I am setting up Azure APIM instance behind a Azure Application gateway. Developer portal will be exposed so external customers will be able to subscribe to products containing the APIs and obtain the subscription key that way. There will be approvals required for subscription. I want to setup OIDC on top of the subscription key validation. For that I believe I have to setup a Validate JWT policy on the API in APIM, using this guide below and use scopes/roles:- https://learn.microsoft.com/en-us/azure/api-management/validate-jwt-policy And seems like I will have to setup client credentials flow for customers to be able to obtain token from AADB2C, using the below KB:- https://learn.microsoft.com/en-us/azure/active-directory-b2c/client-credentials-grant-flow?pivots=b2c-custom-policy Q1 - Firstly, is that the correct way of setting it up? Secondly, with client credentials flow seems like customers will have to use the POST request (or PowerShell) like the one below to obtain the token:- https://<tenant-name>.b2clogin.com/<tenant-name>.onmicrosoft.com/<policy>/oauth2/v2.0/token But this will mean that I will have to document my B2C token endpoint in Developer portal documentation to advise customers on how to obtain token. I have 2 questions related to that:- Q2 - Is advising/advertising B2C token endpoint good practice from security point of view? Q3 - With client credentials flow, setting up the calling app APP Registration in B2C and providing related APP secret will become a manual process. This will remove the benefit of having Product/API subscriptions process automated through APIM and bring in the complexity of securely communicating the secret to customers. Is there a better way of doing this?129Views0likes2CommentsInstalling and configuring Windows App on Thin Client environments
I am seeking technical guidance on accessing the new Windows App from Thin Client environments, following the end of support for the Microsoft Remote Desktop client (27 March 2026). Current Environment End-user devices: Thin Clients used by customers Thin Client OS types in use: Windows 10 IoT Enterprise, and/or Thin Clients running custom NComputing firmware Backend environment: Windows Server–based environment hosting a line-of-business application (accessed via RDP / RDS) Current Access Method Users currently connect using the Microsoft Remote Desktop (RDP) client, accessing either: A full desktop session, or Published RemoteApps via RDS This setup is functioning today but is impacted due to Remote Desktop app end of support. Issue / Challenge Microsoft is recommending migration from Remote Desktop app to the Windows App. However, during evaluation, we are facing blocking limitations on Thin Client devices, specifically: Windows App is not supported / cannot be installed on: Windows 10 IoT–based thin clients, and Thin clients running custom NComputing firmware These devices have: Limited hardware resources Restricted OS / firmware‑level constraints No support for installing modern Store / Windows App packages As a result, users cannot access the environment using Windows App, creating a risk of service disruption. What We Need : We request Microsoft’s official technical and product guidance on the following: Confirmation Is the Windows App officially supported on: Windows 10 IoT Enterprise? NComputing or other firmware‑based thin clients? Alternative Supported Options Are there supported alternatives for thin clients after Remote Desktop app end of support: Web-based access? Legacy RDP components still supported for Windows Server? Specific RDS client versions approved for IoT devices? Best‑Practice Architecture Recommended Microsoft‑supported architecture for: Thin client environments RDS / RemoteApp access Scenarios where Windows App installation is not possible Risk & Compliance Clarification Guidance on continued use of RDP clients in end-of-support but still operational mode, and Associated security or compliance implications, if temporary continuation is required. This information is critical to ensure business continuity for customers who cannot upgrade thin client hardware or firmware immediately.532Views0likes4Comments
Unable to load large delta table in azure ml studio
I am writing to report an issue that I am currently experiencing while trying to read a delta table from Azure ML. I have already created data assets to register the delta table, which is located at an ADLS location. However, when attempting to load the data, I have noticed that for large data sizes it is taking an exceedingly long time to load. I have confirmed that for small data sizes, the data is returned within few seconds, which leads me to believe that there may be an issue with the scalability of the data loading process. I would greatly appreciate it if you could investigate this issue and provide me with any recommendations or solutions to resolve this issue. I can provide additional details such as the size of the data, the steps I am taking to load the data, and any error messages if required. I'm following this document: https://learn.microsoft.com/en-us/python/api/mltable/mltable.mltable?view=azure-ml-py#mltable-mltable-from-delta-lake Using this command to read delta table using data asset URI from mltable import from_delta_lake mltable_ts = from_delta_lake(delta_table_uri=<DATA ASSET URI>, timestamp_as_of="2999-08-26T00:00:00Z", include_path_column=True)700Views0likes1CommentAADSTS5000228 - Locked Out of Trial Tenant
I created a free trial tenant, and was immediately locked out. Upon doing research, I basically discovered that the tenant is locked due to unknown reasons, and I have to contact support. I have tried calling 4 different support numbers a total of 8 times. I have never made it through the laughable automated phone system to a real person, I eventually get hung up on for no reason. I've tried creating chats from personal accounts to basically just be told to log in with my new tenant account and submit a ticket. I can't log in, I would love to be able to log in. I am at a loss for what to do. I can't open a case. I can't call a number. I can't log in. Does anyone have any advice on how to get this taken care of? At this point, I just want to cancel the tenant so when the auto-renew comes up, it doesn't charge my card.88Views0likes1CommentACS Teams interop meeting chat suddenly returns 403 Forbidden on all sends since late Aug 2026
Since approximately Aug 24, 2026, every Azure Communication Services (anonymous interop) user joining Microsoft Teams meetings in our tenant gets 403 Forbidden on ALL meeting chat operations, while calling, roster, and screen-share work normally. This broke suddenly with no changes on our side. The error on both ChatThreadClient.sendMessage and sendTypingNotification is "CommunicationError" Code "Forbidden", Message "The initiator doesn't have the permission to perform the requested operation." ACS users also receive no thread messages (Teams-native participants chat with each other fine in the same meeting), and the communication-react composite shows "You are no longer in this chat thread" immediately on join - so the ACS user appears to never be attached to the meeting chat thread, even though the call roster add works. What we have verified and ruled out - Reproduces with the minimal azure/communication-react (1.32.0) CallWithChatComposite quickstart and a freshly minted ACS identity (voip+chat scopes) - not our application. - Reproduces on BOTH Graph-app-created online meetings AND a meeting created by a human organizer in the Teams desktop app with default options. - Fails on chat api-versions 2024-06-05-preview and 2025-03-15. - All CsTeamsMeetingPolicy instances have MeetingChatEnabledType = Enabled (verified via Teams PowerShell as Global Admin). - ACS federation is configured. EnableAcsUsers = True and our ACS resource's immutable ID is in AllowedAcsResources. External access policies have EnableAcsFederationAccess = True. EnableExternalAccessRestrictionsForChatParticipants and EnableMutualFederationForChatParticipants are both False. - Per-meeting allowMeetingChat = enabled. Anonymous join allowed. BlockedAnonymousJoinClientTypes empty. - User is fully admitted and call state is Connected when sends fail (not the known join-timing issue), and the failure persists for the entire meeting. Sample failing request - POST to (resource).canada.communication.azure.com /chat/threads/19%3Ameeting_...%40thread.v2/messages?api-version=2025-03-15 returns 403, Ms-Cv IGMF4wkAI0+MIaxuFQ0kJw.0, 2026-08-31 16:04:38 UTC (Canada region resource). Was there a recent service-side change or rollout to how ACS interop users are added to Teams meeting chat threads, or a new tenant/meeting setting that now gates this? Is anyone else seeing this since late August 2026? We can share tenant ID, resource ID, and additional Ms-Cv values privately with Microsoft engineers. An Azure support case is also being opened in parallel. Also posted on Microsoft Q&A - https://learn.microsoft.com/en-us/answers/questions/5990218/acs-teams-interop-meeting-chat-suddenly-returns-40140Views0likes2CommentsHow to run failed Tests in Azure DevOps
Hello I have a Test pipeline that runs Regression tests , In azure Devops once the pipeline is completed we have some Failing tests suppose Total Tests are around 500 , there are 10 tests failing , and i want to rerun those particular 10 fail tests automatically in Azure devOps Is there any way to acheive this???2.5KViews1like1CommentMonitor a Hybrid computer shutdown in Azure Arc
Hi, I have created this alert to monitor when a Hybrid computer I have in Azure Arc is down. The computer is running but I am receiving emails. The query is not returning any values. I tried setting the threshold value to 1 but it did not work. Thank you!432Views1like2CommentsWho Can Access What? Designing RBAC and Identity in Azure
Who should be allowed to access an Azure resource? Azure makes it easy to create resources. The harder question comes afterwards: who should be allowed to access them? A Function App may need to read secrets from Key Vault. A Logic App may need to call APIs through API Management. A developer may need to deploy to Dev but have no access to Production. A CI/CD pipeline may need to deploy infrastructure without becoming an Owner of the entire subscription. This is where Azure Role-Based Access Control (RBAC) and Managed Identity become critical. In this article, I look at how to design access around people, applications and deployment pipelines, while keeping permissions as narrow as practical. The article covers: Azure RBAC and access scopes Least-privilege access Managed Identities Developer vs Production access boundaries Application identities CI/CD deployment permissions RBAC vs API authentication Privileged access and PIM Common RBAC design mistakes One of the key principles is simple: Give an identity only the permissions it actually needs. For example, if a Function App only needs to read secrets from Key Vault, giving it Contributor access to the entire Resource Group solves the problem with a much broader permission than necessary. Good RBAC design is not about assigning more permissions. It is about understanding: Who needs access? Why do they need it? What exactly do they need to do? At what scope should access be granted? How can that access be managed securely over time? I would be interested to hear how others approach RBAC and identity design in enterprise Azure environments. Full article: https://www.linkedin.com/pulse/who-can-access-what-designing-rbac-identity-azure-chethan-raj-ud6gc/81Views0likes0Comments







Events
Recent Blogs
- 8 MIN READIntroduction AI agents are rapidly becoming a core component of enterprise transformation strategies. Organizations are deploying agents to assist employees, automate business processes, improve c...Sep 10, 202670Views0likes0Comments
- 24 MIN READPublic cloud platforms — including Microsoft Azure — are built on three foundational principles that distinguish them from traditional on-premises infrastructure: Elasticity: The platform can aut...Sep 10, 202641Views0likes0Comments

