Recent Discussions

get-exchangeCertificate show blank ex 2019 last updates
Hi, I get-certifcates and show blank [PS] C:\Windows\system32>Get-ExchangeCertificate Thumbprint Services Subject ---------- -------- ------- I renew with MonitorExchangeAuthCertificate.ps1 Microsoft Exchange Server Auth Certificate restart servers and still the same can You have solution ? thanksSolved15KViews1like3Comments
Exchange online - shared personal calendar dissapear
User A has been given full delegate access to User B mailbox - set in exchange admin backend When user A open OWA (or outlook app) - the calendar of User B does not show up. Manually when adding User B calendar the calendar shows up - but only with limited view (details of meeting not shown) If User A do a F5/refresh in OWA (or close and open outloo app) - the calendar of User B is gone again Have tried to reset the rights on calendar of user B - so to remove all access for user A. And wait 24 hours - and then set the rights again. But issue on calendar keep going on Running exchange online15Views0likes0Comments
Exchange SE 15.2.2562.46: MRSProxy returns HTTP 401 after successful NTLM authentication
Hello, Anonymization note: The domain names contoso.com and contoso.local, the server name EXCH-SE-01, and the account name CONTOSO\MigrationAccount used in this post are anonymized placeholders. They do not represent the actual production domain, server, or account names. The Exchange versions, configuration values, HTTP status codes, diagnostic results, and sequence of events are unchanged. We are experiencing an issue with remote mailbox moves from Exchange Server Subscription Edition to Exchange Online. The Exchange Online migration endpoint and the following command both fail: Test-MigrationServerAvailability -ExchangeRemoteMove -RemoteServer "mail.contoso.com" -Credentials $cred The error returned by Exchange Online is: The connection to the server 'mail.contoso.com' could not be completed. The call to: https://mail.contoso.com/EWS/mrsproxy.svc failed with: The HTTP request is unauthorized with client authentication scheme 'Negotiate'. The authentication header received from the server was: 'Negotiate, NTLM'. The remote server returned an error: (401) Unauthorized. Environment Exchange version: Exchange Server Subscription Edition RTM Installed update: August 2026 Security Update KB5121573 Binary version: 15.2.2562.46 Topology: Single Exchange server Mailbox role Classic Full Hybrid Operating system: Windows Server 2022 Exchange Online migration type: Remote Move / onboarding The environment does not have separate frontend and backend Exchange servers. Both the Client Access frontend and mailbox backend services are hosted on the same Exchange server. All checked MRS binaries have the same version: Microsoft.Exchange.MailboxReplicationService.dll Microsoft.Exchange.MailboxReplicationService.Common.dll Microsoft.Exchange.MailboxReplicationService.ProxyClient.dll Microsoft.Exchange.MailboxReplicationService.ProxyService.dll MSExchangeMailboxReplication.exe File version: 15.2.2562.46 MRSProxy configuration Get-WebServicesVirtualDirectory | Format-List Identity, MRSProxyEnabled, BasicAuthentication, WindowsAuthentication, WSSecurityAuthentication, OAuthAuthentication, ExternalUrl Current configuration: MRSProxyEnabled : True BasicAuthentication : False WindowsAuthentication : True WSSecurityAuthentication : True OAuthAuthentication : True ExternalUrl : https://mail.contoso.com/EWS/Exchange.asmx Extended Protection settings have been validated by the latest Exchange Health Checker: Default Web Site/EWS: Extended Protection = Allow SSL flags = Ssl, Ssl128 Authentication = Windows, Negotiate, NTLM Exchange Back End/EWS: Extended Protection = Require SSL flags = Ssl, Ssl128 Authentication = Windows, Negotiate, NTLM Anonymous authentication = enabled Exchange Health Checker reports: Exchange SE RTM Aug26SU Build Number: 15.2.2562.46 MRS Proxy Enabled: True Extended Protection configured correctly for EWS Default Web Site: Started Exchange Back End: Started MSExchangeServicesAppPool: Started Local MRS health All local MRS health checks pass: Get-MailboxServer | Test-MRSHealth | Format-Table Check,Passed,Message -Wrap Results: ServiceCheck : Passed RPCPingCheck : Passed MRSProxyPingCheck : Passed QueueScanCheck : Passed Migration accounts The test was performed with two different on-premises accounts. Both accounts return the same HTTP 401 result. The primary migration account: Enabled : True LockedOut : False PasswordExpired : False The account is also a direct member of: Organization Management One of the accounts used for testing also has domain administrative permissions, so the symptom does not appear to be caused by missing Exchange RBAC permissions. Changing the password and updating the credentials stored in the migration endpoint did not change the result. Failed Request Tracing results Failed Request Tracing was enabled temporarily for Default Web Site. The MRSProxy request is processed in three stages. Stage 1: anonymous request The initial anonymous request to: /EWS/mrsproxy.svc returns HTTP 401, which appears to be the expected authentication challenge. Stage 2: NTLM negotiation The next request shows: WindowsAuthenticationModule AUTH_SSPI_CONTINUE_NEEDED HTTP 401.1 0x8009030e This also appears to be the normal intermediate NTLM challenge. Stage 3: authenticated request The final request shows: Authentication type : Negotiate NTLMUsed : true AUTH_SUCCEEDED : true RemoteUserName : DOMAIN\MigrationAccount AuthUserName : DOMAIN\MigrationAccount The Exchange frontend also calculates the expected backend server. However, after authentication succeeds, the request ends with: ModuleName : ManagedPipelineHandler Notification : EXECUTE_REQUEST_HANDLER HttpStatus : 401 HttpSubStatus : 0 ErrorCode : 0 Therefore, Windows Authentication appears to complete successfully. The final HTTP 401 is returned later, while the Exchange/WCF MRSProxy handler is executing. No corresponding failed domain logon events are recorded in the Windows Security log. No new ASP.NET event stating: MRS proxy service is disabled is generated for the current requests. Additional checks already completed We have already verified the following: MRSProxyEnabled=True Test-MRSHealth passes Two migration accounts tested Migration account is in Organization Management Basic Authentication enabled temporarily for testing Windows Authentication enabled Negotiate and NTLM providers present Frontend Extended Protection set to Allow Backend Extended Protection set to Require Frontend TLS certificate valid Backend port 444 certificate valid MSExchangeServicesAppPool running Mailbox Replication Service running EWS physical paths valid WCF *.svc handler mapping present MRS binaries present and version-consistent Exchange server fully restarted IIS restarted MRSProxy disabled and enabled again Temporarily enabling Basic Authentication did not change the result. Using another migration account did not change the result. The dedicated Exchange hybrid application and Microsoft Graph hybrid flow are also configured and Test-OAuthConnectivity succeeds. We understand that this configuration is not used for MRS remote mailbox moves. August 2026 SU known issue We reviewed the Exchange Team announcement for the August 2026 Security Update. The article mentions that MRS migrations can fail if a backend mailbox server has the August 2026 SU while the frontend Exchange server proxying the connection is on an older build. This does not seem to match our topology because this is a single Exchange server and all MRS components are on version 15.2.2562.46. The error is also HTTP 401 rather than TooManyTransientFailureRetriesPermanentException. Questions Has anyone observed the following behavior after installing Exchange SE August 2026 SU, KB5121573? MRSProxyEnabled=True Test-MRSHealth passes NTLM authentication reaches AUTH_SUCCEEDED ManagedPipelineHandler returns final HTTP 401.0 Test-MigrationServerAvailability fails In particular: Is there a known issue in KB5121573 related to MRSProxy authorization after successful NTLM authentication? Does MRSProxy require any additional authorization configuration introduced by the August 2026 security changes? Is there a supported way to validate the MRSProxyAuthorizationManager decision? Are there additional diagnostic logs that show why the WCF MRSProxy handler returns HTTP 401 after AUTH_SUCCEEDED? Is reapplying KB5121573 the recommended repair action in this situation? Has anyone resolved the issue without recreating the EWS virtual directory or disabling Extended Protection? We have retained the following diagnostic evidence and can provide sanitized excerpts: Exchange Health Checker TXT/XML Test-MigrationServerAvailability output Test-MRSHealth output Frontend EWS Failed Request Tracing EWS HttpProxy logs EWS and backend IIS configuration MRS binary versions and hashes Any guidance or confirmation from the Exchange Team or administrators who encountered the same behavior would be appreciated. Thank you.272Views2likes4CommentsOutlook Classic Stamps Its Style on the New Outlook
In an attempt to ease the transition to the new Outlook, Microsoft has introduced the classic Outlook style for the new Outlook and OWA. The style essentially redoes the existing GUI for the web clients to make their appearance very close to the win32 client. After using the two clients side by side for a week, sometimes I find it difficult to know what client I’m interacting with. The question is what average users rather than IT people think of a different face for the new Outlook. https://office365itpros.com/2026/09/07/classic-outlook-style/44Views0likes0CommentsDepreciation of Custom Controls in favor of External MFA
Deprecation of Custom controls Custom controls are being deprecated in favor of External MFA. Existing configurations keep working during the transition, but you should begin migration planning now. Custom controls retire September 30, 2026, and reach end of life in May 2027. When will you see this change? Custom controls will be retired on September 30, 2026, and the service will reach end of life in May 2027. Who will be affected by this change? This update affects organizations currently using Custom controls to integrate third-party MFA providers with Conditional Access. How will this affect your organization? Organizations relying on Custom controls will need to transition to External MFA to maintain support and continue using third-party MFA solutions within Microsoft Entra ID. Moving to External MFA also enables more consistent Conditional Access enforcement and improved integration with Microsoft Entra security capabilities. What do you need to do to prepare? Organizations should: Review existing Custom controls integrations Evaluate External MFA migration requirements Test Conditional Access policies and user experiences before migration Begin migration planning ahead of the retirement date Read more in the External MFA General Availability announcement and migration guidance.Exchange Server OWA does not display lnline Images after EEMS M2.1.0 mitigation.
Exchange Server can automatically apply applicable mitigations by using the Exchange Emergency Mitigation Service (EEMS) to retrieve mitigation information from Microsoft's Office Config Service (OCS). EEMS can apply several types of mitigations: 1. IIS URL Rewrite Rule Mitigation: Blocks specific malicious HTTP request patterns that could put an Exchange Server at risk. 2. Exchange Service Mitigation: Disables a vulnerable Exchange service. 3. Application Pool Mitigation: Disables a vulnerable application pool on the Exchange Server. In this case, inline images were displayed correctly in Outlook, but the same images were not displayed in OWA. The issue was identified as being related to the IIS URL Rewrite rule deployed by the M2.1.0 mitigation for CVE-2026-42897. Verification Run the following commands in the Exchange Management Shell. 1. Check the installed Exchange Security Update version (Get-Command ExSetup.exe).FileVersionInfo.ProductVersion 2. Check whether the Emergency Mitigation Service is enabled Get-OrganizationConfig | fl MitigationsEnabled 3. Check applied and blocked mitigations Get-ExchangeServer | fl Name,MitigationsApplied,MitigationsBlocked For example, a server affected by this issue may show: MitigationsApplied : {PING1, M2.1.0} MitigationsBlocked : {M2.1.0} 4. Check the IIS URL Rewrite rule Import-Module WebAdministration Get-WebConfigurationProperty -PSPath "IIS:\Sites\Default Web Site\owa" -Filter "system.webServer/rewrite/outboundRules/rule" -Name "." | Select-Object name The following rule may be present: EEMS M2.1 OWA CSP - outbound Microsoft provides Security Updates (SUs) to address security vulnerabilities in Exchange Server. Exchange Server SE is currently supported, while Exchange Server 2016 and Exchange Server 2019 can continue to receive applicable security updates through the Extended Security Updates (ESU) program. Note: Exchange Server 2016 and Exchange Server 2019 reached end of support in October 2025. ESU must be purchased separately to continue receiving applicable security updates. Resolution 1. Install the July 2026 SU or later Install the July 2026 SU or a later Security Update (preferably the latest available SU), and then restart the server. Installing the update does not automatically remove the previously applied CVE-2026-42897 mitigation. 2. Block M2.1.0 from being reapplied If M2.1.0 is not already listed under MitigationsBlocked, add it: Set-ExchangeServer -Identity EXSE-01 -MitigationsBlocked @{Add="M2.1.0"} Note: Adding M2.1.0 to MitigationsBlocked does not remove the IIS rules that have already been applied. It prevents EEMS from reapplying the M2.1.0 mitigation. 3. Back up the OWA web.config file Copy-Item ` -Path "$env:ExchangeInstallPath\FrontEnd\HttpProxy\owa\web.config" ` -Destination "$env:ExchangeInstallPath\FrontEnd\HttpProxy\owa\web.config.$((Get-Date).ToString('yyyyMMdd-HHmmss')).bak" 4. Remove the M2.1.0 IIS URL Rewrite rule and precondition Remove-WebConfigurationProperty ` -PSPath "IIS:\Sites\Default Web Site\owa" ` -Filter "system.webServer/rewrite/outboundRules" ` -Name "." ` -AtElement @{name="EEMS M2.1 OWA CSP - outbound"} Then remove the associated precondition: Remove-WebConfigurationProperty ` -PSPath "IIS:\Sites\Default Web Site\owa" ` -Filter "system.webServer/rewrite/outboundRules/preConditions" ` -Name "." ` -AtElement @{name="EEMS M2.1 OWA SPA HTML shell - precondition"} Verification After Rollback Without restarting the Exchange Server or running IISReset, reopen the same OWA message that previously failed to display the inline image and verify that the image is now displayed correctly. Test Results I reproduced the issue in an Exchange Server SE June 2026 SU test environment. After EEMS automatically applied the M2.1.0 mitigation, an inline PNG image that was displayed correctly in Outlook was no longer displayed in OWA. After blocking M2.1.0 and removing the M2.1.0 IIS rules according to Microsoft's rollback guidance, the inline image in the same message was displayed correctly again in OWA. No Exchange Server restart or IISReset was required after removing the IIS rules.112Views0likes0CommentsMicrosoft Entra Connect 2.x Version Retirement Reminder
Microsoft is retiring older versions of Microsoft Entra Connect Sync 2.x as part of its version lifecycle policy. Version 2.5.79.0 Retirement date: 23 October 2026 This version will retire 12 months after the release of version 2.5.190.0. Important to know Microsoft Entra Connect Sync 2.x versions retire 12 months after a newer version is released. This retirement policy has been in effect since 15 March 2023. For new installations: Always install the latest available version. For existing environments: Plan your upgrade to the latest version before your currently installed version reaches its retirement date.
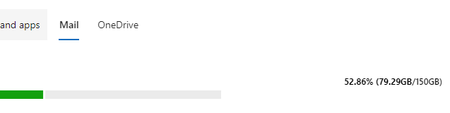
Anyone else seeing mailboxes with Exchange Online 2 showing they now have 150gb?
Noticed this this morning. I understand that Basic was going to go to 100gb as they roll that out, but did they also increase Exchange 2 to 150gb to make it still worth paying for it vs an archive license? Or is this a glitch that is going to give us a problem later when people blow through the limit and MS corrects it? This example mailbox is licensed with Business Basic, then Exchange Online added on. It now shows 150gb. I'm seeing this for every user in every tenant I have looked at so far.595Views1like3CommentsThe Demise of the OWA Light Client
On July 8, Microsoft said that they will retire the OWA Light client for Exchange Server in August 2026. But what happened to the OWA Light client for Exchange Online? It seems like Microsoft announced the retirement of OWA Light for Exchange Online in June 2024, but didn’t really make the fact clear in a blog post about consumer accounts. In any case, you can’t run OWA Light for Exchange Online, even if you wanted to. https://office365itpros.com/2026/07/17/owa-light-retirement/130Views1like1CommentExchange Online PowerShell Updates to 3.10.1 to Fix CBA
Microsoft rushed out version 3.10.1 of the Exchange Online management PowerShell module to fix a problem with certificate-based authentication. It seems like a change in an internal Microsoft identity platform caused the tokens issued after a successful connection to Exchange Online to not authorize the execution of further cmdlets. To their credit, Microsoft fixed the issue, but is this the kind of thing that should be caught in testing? https://office365itpros.com/2026/07/27/exchange-online-management-3-10-1/248Views0likes1CommentPrimary Mailbox Quota Increases to 100 GB for Microsoft 365 Business Plans
Microsoft announced details about how they will deploy the 100 GB mailbox quota to Microsoft 365 Business tenants. A new service plan is being deployed to tenants to liberate the additional 50 GB of quota. Having a larger mailbox quota delivers a fantastic opportunity to fill a mailbox with all sorts of digital debris, something that can cause problems in the era of AI. Perhaps enabling mailbox archiving for Business tenants to allow them to clear out old mailbox items would have been better? https://office365itpros.com/2026/08/21/100-gb-mailbox-quota-m365-business/214Views0likes1CommentHow to submit support tickets?
Hi, folks. How does one submit a support request for the Exchange Online PowerShell v3 module? The following article instructs you what not to do, but provides zero detail on what to do: About the Exchange Online PowerShell V3 module | Microsoft Learn Similarly, the following articles highlight the "correct" process, however, it doesn't work: Get support - Microsoft 365 admin | Microsoft Learn How can I get support for M365 Exchange Online? - Microsoft Q&A Where having used the above option, you get to the end and are shown the following completely unrelated message with the support request having been lost in the process: The bug I'm trying to submit is outlined here: UShort Error with the Exchange Module - Microsoft Community Hub Cheers, LainSolved744Views0likes3Comments
Email Migration Error
While migrating emails from On-Prem MDaemon server to Microsoft Exchange Online , we are getting the following error - Too Many Transient Failure Retries Permanent Exception. I have also attached the snapshot for reference. We have tried migrating live users and new freshly created users (Test users) but still the same error. Request you to help on same.559Views0likes2CommentsHELP - cannot add email to the exchange with outlook classic 2021 and 2024
We have recently upgraded and have a exchange email accounts. We have tried to add emails to connect through exchange we constantly get this error message The action cannot be completed. The name cannot be matched to a name in the address list. We have searched and undertaken many things to and still says this, would anyone know how to fix this?134Views0likes1Comment
Remove-Calendarevents
VasilMichev and TonyRedmond Does it need permission on Termed employees calendar? i am Global Admin and when i run this command with preview it does not preview any results Remove-CalendarEvents -Identity james.bond@domain.com -CancelOrganizedMeetings -QueryStartDate 11-7-2016 -QueryWindowInDays 120 -PreviewOnly -Verbose5.3KViews0likes9Comments
Canon Maxify Printer & Authentication
I recently added Microsoft Authenticator for all our domain email accounts. I have an account that I use for devices and applications to send emails to our domain internally. In each app, I re-tested the account, went into Microsoft Authenticator, approved the request and sent a test email: the apps work! My problem is my Canon Maxify printer. I entered the following information: sender address: user@ domain.com Outgoing mail server SMTP: smtp.office365.com Port Number: 587] Checked on Secure Connection (SSL) Checked on Don't verify certificate For authentication: SMTP authentication But it doesn't work. Do I need to enable a setting in Microsoft Entra and Exchange to get this to work? It is important that the printer send me status messages so I know when there is an issue. I also want to add that the email settings were working until I added the Microsoft Authenticator. Thank you!Solved236Views0likes2Comments
Exchange Room Resource Name Change
We have Room resources on Exchange online which were migrated from on-premise exchange server, last year we completely migrated the on-premise exchange to EXO, now when we had to change the names of these room resources due to some relocations of the meeting rooms, we had to rename it from the on-premise ad since it is syncd. I have just renamed the AD object property(display name, SMTP etc), and once it is syncd via AAD, now could see the new name from the EXO but when we use Get-Mailbox -Identity via Exchange online powershell its still showing up the old name, is there any other on-premise ad attribute which needs to be changed?5KViews0likes7CommentsUsing a scanner device with HVE
Has anyone had any success in setting up a scanner device with HVE? Everything I've read about the HVE option allows for a scanner to send to HVE, but as I've had no luck in getting my Brother ADS-2800 to communicate with HVE. I've confirmed the settings multiple times, but keep getting the same error when I attempt a test email from the scanner. " Communication over the network using SSL was unsuccessful. The SSL settings may not be configured to match the server settings. Confirm the send e-mail server "Port" and the setting for "SSL/TLS". We'd like to use these scanners for sending into a pre-designated internal mailbox. In theory it should work - in practice however, different story.177Views0likes1Comment




Events
Recent Blogs
- We have released Security Updates for Exchange Server SE. Exchange Server 2019 and 2016 ESU updates only.Sep 08, 20263.2KViews3likes4Comments
- Expanded Outlook client support for Exchange Server AD FS Modern Authentication is here!Sep 08, 2026947Views0likes0Comments