microsoft 365 admin center
18 Topics
Export list users never loged in
I'm trying to use this script I've found on the internet : #Set admin UPN $UPN = 'email address removed for privacy reasons' #Time range $startDate = (Get-Date).AddDays(-30).ToString('MM/dd/yyyy') $endDate = (Get-Date).ToString('MM/dd/yyyy') #We are looking for accounts that are active - not deactivated $allUsers = @() $allUsers = Get-MsolUser -All -EnabledFilter EnabledOnly | Select UserPrincipalName #We search $loggedOnUsers = @() $loggedOnUsers = Search-UnifiedAuditLog -StartDate $startDate -EndDate $endDate -Operations UserLoggedIn, PasswordLogonInitialAuthUsingPassword, UserLoginFailed -ResultSize 5000 #Create the list $inactiveInLastSixMonthsUsers = @() $inactiveInLastSixMonthsUsers = $allUsers.UserPrincipalName | where {$loggedOnUsers.UserIds -NotContains $_} #We get a result Write-Output "The following users have no logged in for the last 180 days:" #written to the screen Write-Output $inactiveInLastSixMonthsUsers #Export list to CSV $inactiveInLastSixMonthsUsers $inactiveInLastSixMonthsUsers > "C:\Temp\InactiveUsers.csv" dont know why, but this command never return any data in the variable : $loggedOnUsers = Search-UnifiedAuditLog -StartDate $startDate -EndDate $endDate -Operations UserLoggedIn, PasswordLogonInitialAuthUsingPassword, UserLoginFailed -ResultSize 5000 When I check other variable, I get info, but this one never return anything. I tried with different option and nothing ... that's where my problem is. Any suggestion would be appreciate, or if you have another solution to find all users in the tenant that never loged in, that's what I need! Thanks!2.1KViews0likes2Comments
Managing Multiple M365 Administrator Accounts with Microsoft Authenticator Backup
Hello Tech Community, I am looking for some advice on how to efficiently manage and back up multiple M365 Administrator accounts using the Microsoft Authenticator app. As an IT Support professional working with multiple clients, I have a dedicated Global Administrator account for each client, and all accounts are secured with Multi-Factor Authentication (MFA) using Microsoft Authenticator. Setting up each Global Admin account with the Authenticator app is fairly straightforward, but I’ve run into an issue when trying to transfer these accounts to a new smartphone. While the Microsoft Authenticator app does transfer accounts to the new device, it seems that MFA will no longer work unless you scan a new QR code for each account. However, logging into these Global Admin accounts to obtain the new QR code is not feasible since MFA is required, creating a bit of a catch-22. I’d prefer not to resort to other authentication methods (SMS, email, etc.) for these Global Admin accounts, as it adds unnecessary complexity and potential vulnerabilities. Has anyone found a reliable solution for seamlessly backing up and transferring these MFA-enabled Global Admin accounts to a new phone without needing to re-authenticate via QR code? Any insights or best practices would be greatly appreciated!Solved1.6KViews0likes5Comments
Locked out from my global admin account
I made a mistake an locked my global admin account by accident. No, I don't have an alternate way to get access. Yes, that's my mistake and I won't make it again. However, I opened a case with Microsoft 4 days ago and I've been told someone from the data protection team will call me. But I haven't heard back since... Does anyone know a way to speed up things? Thanks and best regards Raphael1.3KViews0likes1CommentConditional Access enforces MFA but Service Account still ask to secure account
Hi, I've setup Conditional Access policies to enforce MFA. But it excludes a group for service accounts. Whenever we login to a Service Account, they all ask to secure your account. Hit next > It says no MFA options are available > Skip. Both our own MFA conditional access policy and MS per-user conditional access policy excludes this group. The Legacy per-user authentication policy has all accounts disabled there in favour of the conditional access policy. We must be missing something here. Some of these are shared inboxes, others regular user accounts. Many of these services requires login through the typical Microsoft sign in screen to authorize access. Some does not support OpenID. So how do I 100% exclude service accounts from MFA? And how do I get rid of this popup to secure these accounts when it says no MFA options are available? TIA1.1KViews0likes2Comments
Strange redirect when signing in - phishing?
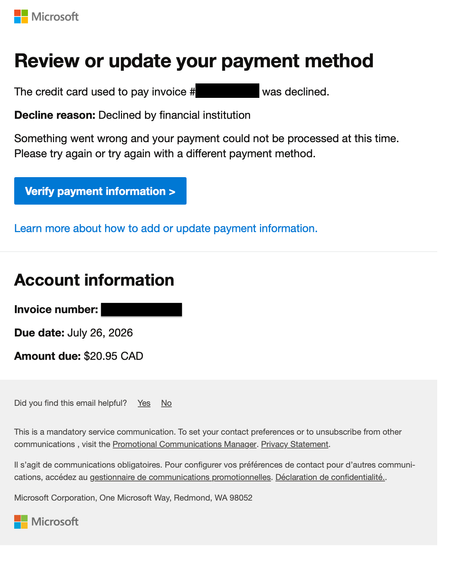
I just restarted my Business Standard 365 license today and this afternoon got an email from email address removed for privacy reasons with the following content: But when I clicked on the 'Verify payment information' button I am redirected to a page with the following URL: https://admin.cloud.microsoft/Error/UnAuth?errorCode=100014 looking like this: This looks highly suspicious (Times New Roman font, URL with no top-level extension such as .com, unusual graphics). Is this legitimate or a phishing attempt? Now, when I try to login to admin.microsoft.com to check my account the same suspicious "Sign out and login with a different account" page pops up repeatedly.701Views0likes6Comments
Can't access Microsoft Authenticator for business accounts
Hello. I am the tech support for a small church, where I am the admin for our MS 365 accounts, which are set up as "business accounts". I have been using Microsoft Authenticator for MFA for years. Recently I switched to a new phone and installed Microsoft Authenticator. All of my personal Authenticator accounts transferred over just fine, but all of the church's business accounts say "Scan the QR Code provided by your organization to finish recovering this account". The thing is, I am the "organization" and I don't know how to generate any QR code to recover the accounts. It was suggested that I could do something about this by logging into my Microsoft 365 administrator account, but when I try to log into my admin account, the only MFA option is "enter the code from Microsoft Authenticator". It's not offering a text or alternate email, only Microsoft Authenticator, which is what I'm locked out of. So I'm stuck in a loop. I opened a ticket with Microsoft Support nine days ago. I have received one phone call since then. The support person insisted that they needed to talk to the account's "alternate administrator", which I set up as my pastor, who is pretty computer savvy but not a deep IT person. They tried to call him one time, but he was not available to answer right then. There has been no communication since then. I'm hoping someone in this group can help me figure this out.700Views2likes4Comments
Sole Global Admin locked out - lost MFA device, SSPR phone verification returns error
Hello, I am the sole Global Administrator of a Microsoft 365 Business Standard tenant and I am completely locked out of the account. What happened: - My phone with Microsoft Authenticator was physically destroyed. - I installed Authenticator on a new phone. My personal account restored from cloud backup, but the work account only appears as a "connected account" - it shows no TOTP code and receives no push notifications. Push requests still go to the old device. What I tried while my admin session was still alive: - Entra ID > per-user MFA > "Require selected users to provide contact methods again" - saved successfully. - User > Authentication methods > "Require re-register multifactor authentication" - returned "Delete operation failed. Try this command again or delete them one by one in the user authentication methods blade." - The Authentication methods list for the user was EMPTY, and default sign-in method showed "No default". "Add authentication method" button was greyed out. - "Revoke sessions" - succeeded, but this also terminated my own admin session and signed me out of Outlook and OneDrive. - aka.ms/mfasetup cannot be reached because it requires a fresh MFA challenge. Self-service password reset (passwordreset.microsoftonline.com): - First verification via alternate email succeeds every time (I have full access to that mailbox). - Second verification fails: both "Text my mobile phone" and "Call my office phone" return "Sorry, we ran into a problem contacting you." I tried +370xxxxxxx, 370xxxxxxx and 8xxxxxxxx formats - same error every time. This looks like a service-side failure, not a formatting issue. - Sign-in Helper now also reports "Account blocked due to multiple incorrect password attempts." Error codes seen: 500121 and AADSTS50133. I have tried calling Microsoft support in several countries. The automated system either asks for an internal extension number or the AI assistant disconnects the call before reaching a human. There is no second Global Admin and no recovery codes. I can provide the tenant ID, user unique identifier, subscription order number and proof of access to the billing email address privately. Requesting escalation to the Data Protection team for admin account recovery. Any guidance on how to reach a human agent would be greatly appreciated. Thank you.600Views1like4CommentsIn "Per-user multifactor authentication" I disabled MFA for one user; All got disabled
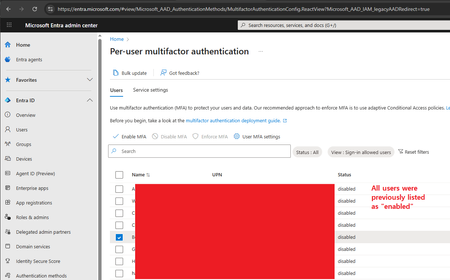
Hi, I'm the 365 admin for our org. Today I had a user that got a new phone and became stuck in a MS Authenticator app loop. (The app required MFA to login to the app, but they can't login to the app because they aren't logged into the app. This happened once before, and is a ridiculous Kafkaesque situation; but I digress.) To solve it, I went to disable MFA on their account, allowing them to login to the app. Then MFA could be re-enabled. Problem solved. And indeed that did work. However, on the admin side (per the screenshot) I checked off their user account (the user starting with the letter "B") and hit the "Disable MFA" link. A confirmation appeared asking me if I wanted to disable MFA for all selected users. Because I'm the careful sort, I could still see that only that one user was checked off as the popover div didn't cover that much of the screen. Hence I confirmed that I wanted to disable MFA for the selected users (i.e. that one user). I then refreshed the page, and all users are now shown as having MFA disabled. I'm 100% sure only that one user was selected, not everyone in my org. That would've been foolish. Trying to figure out what's wrong with this portion of the admin site.599Views0likes2Comments
Stuck in an authenticator loop
I have a 365 Business account. Haven't logged in for a while due to reasons, i was just starting up as a sole trader. Anyway decided now is the time to resurrect it and get up and running, except Authenticator doesn't work because I changed my phone, and my back up email is out of date, and no longer exists. I have tried the support web chat which wants to send a code to authenticator or my back up email. Just called the help line that referred me to the web chat which doesn't work, I couldn't get past the bot. So I am stuck. Any recovery options does not recognise my log in details, i think this is because its been a while since I logged in (I still pay but ....) but I can't resurrect it because I don't have a way of getting a code due to authenticator/back up email as cited above. I am really at a loss as to what to do. I don't want to abandon it and start again as there are documents in my one drive that I need. Can anyone help please. (I think all that needs to happen is an update to my back up email and then I can get going). I am the sole administrator on my business account.403Views1like3Comments