microsoft 365 admin center
1108 Topics
Planning a Google Workspace to Microsoft 365 Migration? What Should You Consider?
Hi everyone, Has anyone recently migrated from Google Workspace to Microsoft 365? I’m interested in knowing what challenges you faced during the migration, especially around mailbox data, calendars, contacts, user mapping, or the final cutover process. For those planning the migration, what are the key things you recommend preparing before getting started? Would like to hear your experiences and suggestions.214Views0likes4CommentsHas anyone migrated from one Google Workspace to another after a company merger?
Hi all, Our company recently went through a merger and we now have two separate Google Workspace accounts that need to be consolidated into one. I need to move everything across, emails, contacts, calendars and tasks, for all users without anything getting lost in the process. Honestly not sure where to begin. Google's native tools seem limited for something like this and I don't want to start without a solid plan. Has anyone gone through a similar consolidation? How did you handle it and is there anything you wish you had known before starting?292Views0likes3Comments
How much of your Microsoft 365 environment can you actually see at once?
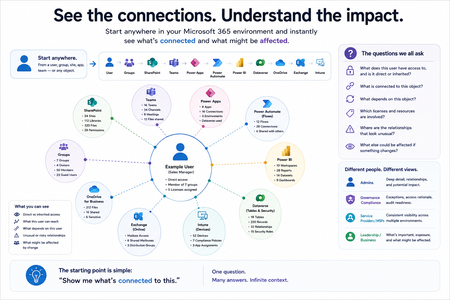
Not how many users you have. Not how many sites, teams, apps or flows you have. How much of it can you actually see connected together? I've been working across Microsoft 365 environments for a while, and I kept running into the same thing. There is no shortage of information. If anything, there is probably too much of it. Users, groups, permissions, SharePoint, Teams, Power Apps, Power Automate, Power BI, Dataverse, OneDrive, Exchange, Intune, licensing, configuration... It's all there. But when you're actually trying to understand how everything fits together, it can be a different story. You open one blade. Find something. Open another. Cross-check it. Go back. Open something else. Before long, you're jumping between different parts of the tenant trying to build the bigger picture in your head. And if you're working with larger environments, that gets difficult pretty quickly. The information isn't necessarily missing. The relationships between the information are what can be difficult to see. That got me thinking about a slightly different question: Instead of "where do I find this information?" "Show me what's connected to this." That's where VisibleState started. Start anywhere. Follow the connections. Imagine starting with a single user. Instead of seeing that user simply as a record with a list of properties, imagine being able to explore the relationships around them: User → Groups → SharePoint → Teams → Power Apps → Power Automate → Power BI → Dataverse → OneDrive → Exchange → Intune Then the questions become different: What does this user have access to? Is that access direct or coming through a group? What resources are connected to them? What depends on something they're associated with? Which licenses are involved? Are there relationships that look unusual? If something changes, what else might be affected? Those questions aren't necessarily about finding another piece of information. They're about putting information that already exists into context. A report can tell you that something exists. A connected view helps you understand what it is connected to. Illustrative example below — not a real customer environment. I'm not suggesting Microsoft 365 doesn't already give us this information Quite the opposite. Microsoft 365 already gives administrators an incredible amount of information and tooling. The thing I've been thinking about is what happens when you want to look across those boundaries. Sometimes I don't want another export. I don't want another list. I don't necessarily want another dashboard. I want to start with something I'm looking at and ask: "What's connected to this?" And then keep following the trail. That's the idea I'm exploring with VisibleState. The interesting part is what happens when you change the viewpoint The same relationships can be useful for completely different reasons. For example: Administrators may want to understand access, permissions and dependencies. Security and governance teams may want to find unusual relationships or exceptions. Compliance teams may need to understand who can access something and why. People managing multiple environments may want a consistent way to understand what's there without rebuilding the picture manually every time. Leadership may not need to see the graph at all. They may simply want to know what's important, what's exposed and what could be affected. It's still the same underlying environment. You're just looking at it from a different angle. And that's where I think things get interesting. Where I'm at with it VisibleState started as something I was building to make my own work easier. I was spending a lot of time investigating environments, tracing access and putting information together for reports. The individual tasks weren't necessarily difficult. It was the jumping between different places and reconstructing the bigger picture that took the time. So I started building something that would let me approach the environment through the relationships instead. It's grown quite a bit from where it started, and I'm continuing to build it. I'm not posting this as a product launch, and I'm not looking for people to sign up. I'm genuinely interested in whether the problem I'm seeing is familiar to other people working with Microsoft 365. So I'm curious... If you could start with any object in your Microsoft 365 environment and immediately see what it's connected to, where would you start? Would it be: Users and access Groups and permissions SharePoint and Teams Power Apps, Power Automate, Power BI and Dataverse Licensing and resources Governance and unusual relationships Something completely different Maybe you've already got a good way of doing this. Maybe you still find yourself jumping between different services and piecing things together manually. Or maybe I'm looking at the problem from the wrong direction. What's the one relationship in your Microsoft 365 environment that you wish you could see instantly?92Views0likes0Comments
Sole Global Admin locked out - lost MFA device, SSPR phone verification returns error
Hello, I am the sole Global Administrator of a Microsoft 365 Business Standard tenant and I am completely locked out of the account. What happened: - My phone with Microsoft Authenticator was physically destroyed. - I installed Authenticator on a new phone. My personal account restored from cloud backup, but the work account only appears as a "connected account" - it shows no TOTP code and receives no push notifications. Push requests still go to the old device. What I tried while my admin session was still alive: - Entra ID > per-user MFA > "Require selected users to provide contact methods again" - saved successfully. - User > Authentication methods > "Require re-register multifactor authentication" - returned "Delete operation failed. Try this command again or delete them one by one in the user authentication methods blade." - The Authentication methods list for the user was EMPTY, and default sign-in method showed "No default". "Add authentication method" button was greyed out. - "Revoke sessions" - succeeded, but this also terminated my own admin session and signed me out of Outlook and OneDrive. - aka.ms/mfasetup cannot be reached because it requires a fresh MFA challenge. Self-service password reset (passwordreset.microsoftonline.com): - First verification via alternate email succeeds every time (I have full access to that mailbox). - Second verification fails: both "Text my mobile phone" and "Call my office phone" return "Sorry, we ran into a problem contacting you." I tried +370xxxxxxx, 370xxxxxxx and 8xxxxxxxx formats - same error every time. This looks like a service-side failure, not a formatting issue. - Sign-in Helper now also reports "Account blocked due to multiple incorrect password attempts." Error codes seen: 500121 and AADSTS50133. I have tried calling Microsoft support in several countries. The automated system either asks for an internal extension number or the AI assistant disconnects the call before reaching a human. There is no second Global Admin and no recovery codes. I can provide the tenant ID, user unique identifier, subscription order number and proof of access to the billing email address privately. Requesting escalation to the Data Protection team for admin account recovery. Any guidance on how to reach a human agent would be greatly appreciated. Thank you.294Views1like4Comments
Entra MFA for seniors using W365 Biz Basic
Entra MFA for seniors using W365 Biz Basic, these folks cannot and will not deal with mobile auth apps or keyfobs. This is a Historical Society. Need MFA bypass or non-technical solution that Senior Citizens with only enough knowlege to work MS Word can handle. There is zero risk of data loss or hackers or the like. We have nothing to lose as all is websearch and simple word docs. MFA without SMS or voice is going to put a lot of non-tech seniors out of their livelihoods. Need a simple non-tech solution. MS is so worried about CYA with regard to security, that they are pushing people out of technology. Do I have to go to Google Docs for a solution? Libre? It's not MS responsibility to remove all possibilities for poor decisions. Give us the tools for wise decisions, but quit binding us up. I need a solution or I'll have to move these folks off M365.118Views0likes1CommentAI agent ownership change
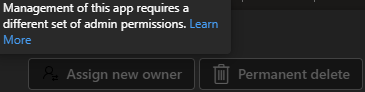
I was just in the M365 Admin Center because I needed to transfer ownership of an agent for a colleague – but it now suddenly looks like Microsoft has changed something in their permission structure. As a result, I can no longer transfer ownership of agents, and the system tells me that I don't have permission to manage that particular app. So, the question is: do I now also need the Application Administrator role in order to continue managing this? I get this message:230Views1like2Comments
Not For Profit Licence suddenly disappeared and then deleted
Hi All Have a big issue. Have a not for profit account for our charity. Renewed licence earlier in the year and all was ok and working. Then a few days ago I had reports of not being able to access data. After much hunting I found the below. Seems account was suddenly and without warning disabled and then reported as deleted a few days later. What do I do? I desperately need to recover the files that were on the associated teams? Any help would be much appreciated846Views0likes15Comments
Where does Teams get its user list from? I can't make sense of which accounts I see vs which I can't
OK, so I have a currently rather unusual situation. I am looking at a 365 Tenant. A number of users have four accounts on the same tenant (let's not even get into why, cleaning things up is part of the reason I got called in). When you start typing their name into teams it comes up with three of them as a suggestion (I only want one) Account 1: has just been used for ActiveDirectory for permissions to the company's Distributed File System (stored in on on premises servers in various locations). This account has to the best of my knowledge never had a license or mailbox associated with it, and so has never been on the global address list, it's also never had the teams app enabled for it. I don't want this one to show, but it does Account 2: A now defunct account which used to have a Business Standard license assigned to it, but has now had the licensed removed. Before the license was removed this account was hidden from the GAL and its teams app disabled. I don't want this one to show, but it does Account 3: An now defunct account which still has a Business Standard license, but with Teams deselected in the Apps. I don't want this one to show... and it doesn't Account 4: An account shared via a multi tenant organization (the users in question have been migrated to a new tenant). So these are members (not guests) but external ones. I want this to show, and it does. Now, accounts 2 and 3 will be deleted soon, whether we can get rid of account 1 depends on whether the necessary access to the DFS can be done using account 4 (which I need to look into next). However for the time being they are all there so I was trying to hide accounts I don't want users trying to message on teams from teams, and I cannot make any sense of which I see which I don't. To sum up. Account that has never been on the Global Address List and never been activated for Teams - Shows Account that used to have a license and was on the GAL, and used in teams - Shows Account that still has a license, but has been removed from GAL and had teams app disabled - Doesn't show Account that has no license and is not on the GAL, but has teams on it's host tenant - Shows After a previous inquiry I set "Scope directory search using an Exchange address book policy" in the teams setup, but I have not set up any specific address book policy as yet. I have tried showing and hiding people from the global address list, and also the "ShowInAddressList" setting in Entra (which seems to only be available through graph?). Nothing seems to make a difference (it doesn't help that Teams takes forever to update its local cache for this stuff, so maybe a change DID make a difference at some point and I missed it). I cannot find any logic as to which of these accounts is showing in the auto suggests and which not, most notably that account 1 shows but account 3 doesn't. So, where is Teams getting its list of contacts from?2.9KViews0likes4Comments