training
1295 TopicsThe CISO Cheat Sheet to Microsoft Digital Defense Report 2026
I know we’re all busy, so I’ve pulled the most important data from this year’s Microsoft Digital Defense Report into one short read. The full report is well worth exploring, but this article focuses on the numbers and trends most relevant to security leaders. This year’s edition shows that AI is lowering the time, expertise and cost required to discover and exploit weaknesses, enabling attackers to operate with greater speed, scale and autonomy. The report describes this as AI “changing the physics of cybersecurity”: attack timelines are compressing and agentic systems are beginning to automate more of the attack lifecycle. Trend 1: Time has collapsed The clearest finding is about speed. Vulnerability discovery is increasingly running ahead of remediation, while the time from discovery to weaponisation is shrinking. In the AI era, weaponisation can follow in hours. Vulnerability discovery and weaponisation now often needs only a well-written prompt. The median time from discovery in the wild to weaponisation is below 24 hours. Vulnerabilities were on track for a record estimated 72,000 CVEs in 2026. The report expects a multi-year period in which the number of known but unpatched vulnerabilities rises sharply before eventually declining. The median time from container start to first exploit attempt is 5.3 hours. The ransomware actor Storm-1175 moved from web-facing exploitation to deploying Medusa ransomware in as little as 24 hours. CISA added over 110 CVEs to its Known Exploited Vulnerabilities catalogue between November 2025 and May 2026, most within a week of disclosure. The mismatch with enterprise reality is the uncomfortable part. The report says the disclosure-to-exploitation window has shrunk to single-digit days. Between November 2025 and May 2026, CISA added more than 110 vulnerabilities to its Known Exploited Vulnerabilities catalogue, most within a week of disclosure. In one example, Storm-1175 moved from exploiting a web-facing vulnerability to deploying Medusa ransomware in as little as 24 hours. Microsoft’s Red Team makes an important point: a patch is also a disclosure. Every fix points attackers towards the flaw it closes. As AI-assisted analysis makes reversing patches faster and more reliable, the report argues that patch velocity, not simply patch availability, becomes the control that matters. Trend 2: Attack chains are gaining autonomy The report charts a clear progression: September–November 2025: AI assists in orchestrating a campaign, as in the Anthropic-reported espionage case. April–June 2026: Full-chain autonomy is demonstrated in labs. July 2026: Real-world autonomous attacks of increasing complexity appear. Two frontier models, Mythos and GPT-5.5, completed a 32-step attack chain against an emulated enterprise with no human help. The test environment had no defenders. The UK AI Security Institute reached a similar finding independently. GPT-5.5 was the second model to solve its end-to-end corporate network attack simulation, a task AISI estimates would take a human about 20 hours. Open-weight models lag closed models at orchestrating attacks by about seven months. In the wild, early July 2026 saw the first documented automated ransomware extortion attack, named JADEPUFFER by Sysdig. Microsoft has seen AI-orchestrated intrusions that share elements with it. Initial access consistently came from internet-exposed services running known-vulnerable software. The report is measured on this point. Volumes of AI-orchestrated activity remain low. In most observed real-world operations, complex end-to-end intrusions still retain meaningful human direction. The Red Team's framing is the most useful one: AI doesn't create a new class of attack, it collapses the effort needed to find and exploit existing attack paths. Trend 3: AI has become an attack surface The report's second takeaway is that attackers are already targeting AI itself. The adoption numbers explain why. 88% of enterprises are experimenting with agents, and 82% of leaders plan broader rollouts within 12–18 months. The report cites industry projections of roughly 1.3 billion agents in production by 2028. What attackers are doing to AI systems: Four techniques accounted for roughly 90% of observed attack activity in telemetry from Azure AI workloads: malicious link injection (52%), jailbreaks (16%), tool and agent abuse (12%), and identity and credential abuse (10%). Memory poisoning: An attacker who can place content anywhere an agent reads can often place it where the agent remembers. Email is the dominant pathway the Red Team has observed. Human-in-the-loop isn't a complete control: Red team testing saw approval prompts ignored, or bypassed by a policy stored in poisoned memory. Developer tools turned against their owners: The "s1ngularity" malware hijacked locally installed AI command-line tools to hunt for secrets. It leaked about 2,000 secrets and 20,000 files across 225 victims. AI browsers: In daily use at more than 40% of organisations in Microsoft's dataset, they were the initial infection vector in incidents involving 57 malware families in a May 2026 analysis. Chat histories as a target: Malicious AI-assistant extensions reached nearly 900,000 installs and more than 20,000 enterprise tenants, harvesting AI chat histories that often contain code, architecture and credentials. The identity implications are direct. Each agent needs its own identity, not one borrowed from an employee, and a named human sponsor. The report also treats revocation latency, the time to cut off a compromised agent, as a measured outcome. Trend 4: The front door is still identity AI changes the speed and personalisation of social engineering. It hasn't changed where attacks start. Initial access in Defender Experts data: User execution: 30% Valid accounts: 20% Malicious copy-and-paste: 13% Phishing: 11% Together, user execution and valid accounts account for over half of observed activity. In incident response engagements, phishing as an initial access vector jumped from 7% to 23% year on year. The standout numbers: ClickFix: Defender saw user-pasted malicious commands on more than 1.1 million unique devices between February and early May 2026, roughly an 8x increase. AiTM: URLs accounted for 45% of the identified phishing techniques in the report’s breakdown. Separately, the share of AiTM phishing and token-theft attacks more than doubled during the first six months of 2026, although the report notes that their overall share remained comparatively small. Teams vishing: Weekly confirmed malicious volume increased 502% year on year. Per attempt, 48% of vishing calls kept the victim engaged for more than 20 seconds, and 30% lasted more than one minute. When a call succeeds, attackers can persuade the victim to install a remote-management tool and complete reconnaissance in two minutes or less. Business contact impersonation (BCI): The report introduces this term for conversations that start with a trusted-looking contact. Microsoft detected more than 46 million attacks in 12 months, with a 121% spike in April 2026. The share of first-contact messages that explicitly asked for money or documents fell from 17% to 3%. The first message is deliberately bland, like "Are you at your desk?" Password attacks declined 26% year on year, which the report describes as strong evidence that MFA and passkeys are forcing attackers to pivot. That pivot includes techniques such as fatigue attacks, AiTM phishing and token theft designed to circumvent conventional MFA. Trend 5: Attackers are inheriting trust rather than breaking in The report's headline theme is that risk is increasingly interconnected. Threats travel through the trusted relationships between identities, software supply chains, partners and cloud platforms. The numbers: Supply chain: Major open-source ecosystems saw attacks roughly every ten days, accelerating through Q2 2026. Shai-Hulud 2.0 affected 25,000 repositories. Megalodon backdoored 5,561 GitHub repositories in under six hours. Trusted signing: In May 2026, Microsoft disrupted Fox Tempest, a "malware-signing-as-a-service" operation that obtained genuine certificates for ransomware loaders and infostealers. Microsoft revoked over a thousand fraudulent code-signing certificates. Legitimate access: An unsanctioned remote monitoring tool is now one of the most reliable mid-stage indicators of a human-operated intrusion. Cloud identity: Cloud identity abuse was the most observed technique against critical infrastructure, representing 78% of the technique mix in Microsoft’s data for March to June 2026. Hybrid intrusions: The Storm-2885 case showed an attacker using a privileged cloud identity to close and downgrade security alerts. The report says identity governance and alert-handling workflows deserve Tier 0 treatment. Dwell time: DART data shows a statistically significant increase in dwell time year on year, meaning organisations took longer to detect intrusions. Ransomware shows the same ecosystem pattern. Qilin led leak-site data with 16.4% of victims, up 386%. Defender detections tell a different story, with Akira at 22%. Trend 6: Defence works best when it's connected The report is not only a catalogue of threats. The strongest defensive evidence: Disruption works. Following the March 2026 disruption, Tycoon2FA activity had fallen 95% from its November 2025 peak by June. Its share of CAPTCHA-gated phishing declined from 76% in December 2025 to 12% in June 2026. Correlation is the highest-leverage variable. The report argues that how well defenders share and correlate signals across endpoint, identity, cloud, email and network is one of the highest-leverage strategic variables under their control. AI is also changing defensive operations. The report describes AI-assisted triage, incident summarisation, hunting-query generation and detection engineering as ways to accelerate investigations and allow analysts to concentrate on higher-value work. Automated disruption can compress response time. The report says that when a correlated incident reaches a defined confidence threshold, defensive systems can automatically isolate devices, disable compromised accounts, revoke sessions or quarantine affected cloud resources. It also stresses the importance of appropriate governance and human oversight for high-risk AI actions. The report also recommends changing what leaders measure. It suggests moving from patches deployed to exposure reduced, detection coverage increased and time-to-mitigate compressed. What the MDDR recommends: ten security priorities The report starts its recommendations with the foundations: Secure by Design, Secure by Default and Secure Operations, applied through identity-centric Zero Trust. Microsoft says these keep the priorities below durable as AI adds more identities, applications, agents and dependencies to govern. Govern cyber risk at leadership level. Report identity exposure, patch latency, agent permissions, critical dependencies, dwell time and recovery readiness to the board. Defend identity as the primary control plane. Deploy passkeys and phishing-resistant MFA, reduce privilege and govern human and non-human identities. Invalidate and rotate tokens and session credentials quickly. Establish governance, visibility and data controls for AI. Keep visibility of approved AI tools, services and agents, and monitor for unauthorised or unmanaged use. Apply sensitivity-aware access and data protection to the data those systems can reach. Reduce exposure and edge risk. Continuously discover internet-facing assets and patch edge devices quickly. Centralise high-fidelity logging, enforce strong authentication and combine network visibility with threat intelligence. Focus on cross-signal correlation. Correlate endpoint, identity, cloud, application, email and network signals to detect intrusions earlier. Correlation also helps defenders anticipate attack paths and likely targets. Enact a continuous threat and vulnerability management model. Combine asset visibility, vulnerability identification, threat detection and AI-accelerated insight into a single continuous programme. Validate exposure through proactive testing. Run assume-breach exercises on cloud services, SaaS platforms, APIs and workflow automation. Prioritise them by where your highest-value data is stored, accessed or aggregated. Secure software dependencies. Harden software installation, keep a software inventory and validate provenance. Monitor packages and prepare for rapid containment. Participate in collective defence. Share actionable threat indicators and victim-informed intelligence with trusted partners and law enforcement. This supports coordinated tracking, investigation and disruption. Prepare for long-horizon technology transitions. Build a cryptographic inventory and advance post-quantum planning alongside AI governance. Read together, the numbers tell one story: the attacker’s workflow is becoming faster and less expensive. AI can shorten vulnerability discovery, exploitation, secret discovery and lateral movement, while organisations still face the slower operational work of testing, coordinating and deploying safe changes across complex environments. At the same time, agent identities can proliferate faster than organisations can inventory, govern and revoke them The defining question for boards today is not whether disruption will occur, but whether the organization can continue operating, contain harm, recover quickly, and maintain trust when it does. Source: Microsoft Digital Defense Report 2026, Version 1.1. Reporting period: July 2025–June 2026.
Conditional formatting
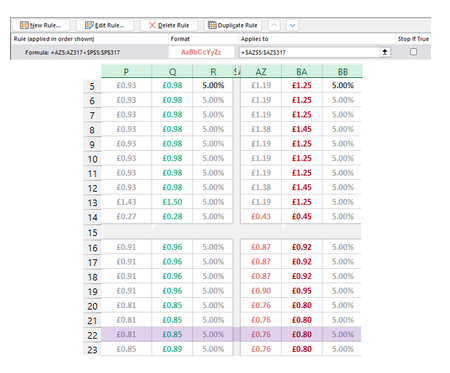
I'm making a rule to Highlight cells in Column AZ when the value is lower than Adjacent cells in Column P. For the most part it works except for two cells in AZ (1 shown as an example) that are higher than P but are being picked up by the conditional formatting. The two cells I'm focusing on here are P14 (£0.27) and AZ14 (£0.43). £0.43 should not be being highlighted pink as it isn't lower than £0.27. This has to be something obvious but I have looked at it too long. Please help if you can :)Solved239Views0likes3Comments
Looking for advice on leveraging AI for Excel in a price-sensitive, third-world country
I work for a training company in a price-sensitive, third-world country and have been conducting training in MS Excel for close to 2 decades. My company has asked me to design Excel training that teaches how to use AI to improve productivity. Ethical considerations aside, it’s something I have been thinking about for a while. The main roadblock I see is the average purchasing power of participants in our market. Right now the cheapest Copilot plan is USD 99.99/yr for MS 365 Personal. The cheapest plan for Business or Enterprise is USD 18/user/month for MS 365 Copilot business (billed at USD 216/user/year). I’ve been casually speaking with the participants in training sessions and most are happy with the free chatbot versions of Copilot/ChatGPT/Gemini that almost no one would upgrade to a paid subscription to integrate AI with Excel - they describe their problem to the AI, send screenshots or upload files and then try and implement the solution that’s returned. It’s similar in the business/enterprise context. Larger organisations may have paid for AI subscriptions for their employees but those are few in number. Most businesses in this market are classified as Small-Medium-Enterprises (SMEs) and feedback from participants is that their management would not likely approve of the cost. It’s worth mentioning that my training company does not provide computers instead requiring participants to bring their own laptops with valid Excel licences though we standardize things as much as possible e.g. Windows only, no tablets etc… This means if we design a training that requires a paid Copilot subscription, then it is up to the participants to buy it for themselves which I don’t think many of them will. After speaking with management, they are open to designing a training that uses the free AI chatbots. I’m fine with that but don’t know how much value that would add to what people are already doing. I’m quite sure this strategy is management trying to revive Excel training which used to be top-sellers (demand fell off ever since COVID) and they see other Excel training incorporating AI so want to follow suit. So right now the most viable option is to create training that teaching using free AI chatbots. But I’d like to hear the opinions of others - what other options do you see for a price-sensitive, third-world market? And yes, I did ask AI how Excel users can leverage AI without paying for expensive subscriptions and it basically said “use the free chatbots”.174Views0likes1Comment
Creating Sankey Diagrams
Hi, Does anyone have any guides for creating Sankey Diagrams in Excel. I deal with the analysis of a reasonably long process which has various customer inputs and outcomes. I am looking for a visual way to show everyone who came into the process, and what happened to each person. Sankey Diagrams seem to fit that bill perfectly. Any help would be appreciated. Thanks T319KViews0likes9CommentsScenario basic help please
Hi. I have a spreadsheet which calculates electricity usage and solar input etc. As the price keeps changing I am putting the new prices into the spreadsheet. I was thinking that I could use Scenarios or similar to be able to see what the bill would have been previously. I have looked at the Scenario instructions but I'm not quite sure how to use it (bit rusty in Excel recently). Is there a training video or similar I could watch. Any help gratefully received. Regards Bluey318Views0likes2Comments
Remove a comma from a number treated as text
Greetings! I'm new to this forum, and I don't know if this is the right place to ask. But, here it goes: I have a column of currency values which is a mess. I managed to clean it as much as possible using the functions SUBSTITUTE and TRIM. These functions transformed the unformated numbers into text, and now it looks something like this: 6,764,68 1,319 1,948 301,40 2848,08 The former is a sample from 165 entries. Is it possible to remove the first comma of the string, so the values look like this instead? 6764,68 1319,00 1948,00 301,40 2848,08 What I would like to do is to remove the second comma from right to left in each value, while keeping the first which marks the cents of the transaction. Can this be done? Thanks all in advance :D442Views0likes3CommentsCopilot Chat Adoption Feedback : Model Selection Governance and Prompt Library Reusability ?
Hello, As part of several Microsoft Copilot adoption projects that I am currently leading across different organizations, two questions frequently come up from both users and administrators. The first concerns the ability to lock or enforce a specific model in Copilot Chat for certain use cases. Several customers would like to guide users toward a particular model when working on specific scenarios (Opus for example) that require a certain level of reasoning, behavior, or response quality. To date, I have not found any official documentation or roadmap information indicating whether this capability is planned. The second concerns the Prompt Gallery / Prompt Library. Saved prompts are very useful for starting a conversation, but they do not appear to be reusable directly within an ongoing conversation. In several business scenarios, users would like to chain multiple approved prompts within the same conversation in order to preserve context while applying different working methods, analysis steps, or processes. Are there any planned developments regarding these two topics? The ability to lock or enforce a specific model in Copilot Chat. The ability to use prompts from the Prompt Gallery / Prompt Library during an already active conversation. I have not found any official information on these topics in Microsoft Learn documentation or in the Microsoft 365 roadmap. However, these capabilities seem likely to facilitate user adoption and help standardize usage patterns across organizations.683Views3likes2Comments
GLSU Excel add-in fails to load after Office update from Version 2607 to 2608
Our Excel add-in, Process Runner GLSU , fails to load after Microsoft Office updates from Version 2607 to Version 2608. This started August 17, 2026 and is actively growing in scope. Error messages: Excel: Cannot run the macro 'onLoad' VBA: System Error &H80004005 (-2147467259). Unspecified error VBA: Compile error in hidden module: ThisWorkbook Has anyone encountered similar issue with their own custom add-on. If yes, any pointers to fix it. We are seeking help on priority. Thanks, Vrushali Pawale, Sr. Manager, Insightsoftware.1.1KViews0likes1CommentFree course: Unlocking AI for Nonprofits
With support from Microsoft, NetHope has launched a new free, CPD-certified course series - Unlocking AI for Nonprofits - designed specifically for nonprofit professionals. The series will help nonprofit teams build practical and responsible AI skills, no technical background required. The four learning pathways include: AI Basics – Learn what AI is and why it matters for nonprofits Applications of Generative AI – Explore time-saving tools for content, reporting, and data Advanced Applications: Microsoft Copilot and Beyond – Help your team adopt AI with clarity and confidence Responsible Use of AI – Understand ethics, inclusion, and organizational safeguards We’ve had more than 1,000 enrollments across the series to date – don't miss out! Courses are free and available through August 31, 2025. https://nethope.org/programs/unlocking-ai-for-nonprofits-enroll-in-our-new-ai-skills-course-for-nonprofits/?utm_medium=forum&utm_source=microsoftnonprofit&utm_campaign=msaiskillsjul&utm_content=unlockingai867Views3likes3CommentsLevel Up Your Security Skills This August with the Microsoft Defender Challenge and Learn Live
Security teams face an increasingly complex landscape. Threats span identities, endpoints, email, cloud workloads, and emerging AI environments. The best defenders aren't just reacting to threats—they're continuously building the skills needed to stay ahead. That's why we're inviting security practitioners to build practical security operations expertise while working toward their next certification goal. Running from July 20 through August 21, 2026, and focused on skills across Microsoft Defender XDR, Microsoft Sentinel, and Microsoft Defender for Cloud, this hands-on learning experience is the Microsoft Defender Challenge. Build Skills That Matter to the Modern SOC The Microsoft Defender Challenge isn't about memorizing content for an exam. It's designed to help you develop real-world security skills you can apply immediately in your organization. Through curated Microsoft Learn content, you'll strengthen your ability to: Detect, investigate, and respond to threats across Microsoft Defender XDR Manage incidents and automate workflows with Microsoft Sentinel Triage and remediate security alerts in Microsoft Defender for Cloud Secure cloud and AI workloads using modern security practices Improve operational readiness for today's evolving threat landscape Whether you're a SOC analyst, security engineer, cloud security practitioner, or IT professional looking to expand your security expertise, the challenge is an opportunity to sharpen skills that map directly to modern security operations. Complete the Challenge and Enter the Sweepstakes Learning is the real reward, but there's an added incentive. Participants who complete the Microsoft Defender Challenge and submit the official sweepstakes entry form by August 21, 2026 will have the opportunity to win one of 500 certification exam vouchers worth 50% off one of the following Microsoft Certifications: SC-200: Microsoft Security Operations Analyst SC-500: Microsoft Cloud and AI Security Engineer How to Enter Complete the Microsoft Defender Challenge on Microsoft Learn. Before the entry period closes, submit the official sweepstakes entry form. If selected, you'll receive instructions for redeeming your certification discount voucher. Challenge window: July 20 – August 21, 2026. Sweepstakes entry deadline: August 21, 2026 at 11:59 PM UTC. No purchase necessary. See official rules for eligibility and sweepstakes details. Join Learn Live: Remediating Threats Using Microsoft Defender Want a guided walkthrough of the skills featured in the challenge? Join a live, interactive event where you can learn directly from Microsoft experts, ask questions in real time, and explore security operations scenarios together. Save your spot for our August Learn Live session. Date: Wednesday, August 19, 2026 | Time: 12:00 PM PT / 3:00 PM ET You'll be guided by Scott Landry, Microsoft Security Customer Experience Engineering, as you explore practical approaches to investigating security incidents, managing and remediating threats across the Microsoft Defender ecosystem, automating investigations and response actions, strengthening security operations processes, and applying Microsoft Defender capabilities to real-world scenarios. Start Building Your Skills Today Ready to level up? Sign up today to take the Microsoft Defender Challenge, then join us for the Learn Live session on August 19. Your skilling journey doesn't end here—keep learning, keep growing, and keep building beyond August at the Security Hub on Microsoft Learn.