outlook on the web
132 Topics
Microsoft Sign In Loop
I am trying to sing into Microsoft 365, but every time I do, it takes me back to the login screen. I sing in with my outlook account, but I can't reach the applications. I can sign in on the browser, but not the applications on my computer. I have tried uninstalling and reinstalling M365, but the issue still persists237Views0likes1Comment
How to Recover Data from a Damaged or Corrupted OST File When Outlook Cannot Open It
Hi everyone, I have seen several cases where users still have an old OST file but cannot access the mailbox data inside it. This usually happens after an Outlook profile is removed, a Microsoft 365 or Exchange account is changed, a mailbox is no longer available, or the OST file becomes damaged or corrupted. One common misunderstanding is that an OST file can be opened on another computer in the same way as a PST file. However, an OST file is linked to the Outlook profile and mailbox that created it. If that connection is no longer available, Outlook may not be able to open the file normally. Before trying to recover the OST data, it is worth checking a few things: Is the original Microsoft 365 or Exchange mailbox still available? Can the Outlook profile be recreated and synchronized again? Is the issue related to the OST file itself or only the Outlook profile? Do you need the complete mailbox data or only specific folders/items? If the mailbox is still available, rebuilding the Outlook profile and allowing Outlook to create a new OST may be the better approach. However, if the mailbox no longer exists, the Outlook profile has been deleted, or the OST file is damaged and contains the only available copy of the mailbox data, recovery becomes a different process. In these situations, it is important to first check what information is still readable from the OST file. Scanning and previewing the mailbox data before export can help identify available folders, emails, attachments, contacts, and calendar items before creating a new PST file. A practical OST recovery workflow usually involves: Keeping a copy of the original OST file before making any changes. Checking whether the original mailbox can still be synchronized. Scanning the OST file to identify available mailbox items. Reviewing important folders and messages. Exporting the required data to PST. Validating the resulting PST in Outlook. A detailed overview of the OST to PST conversion process, including scanning, previewing, selecting mailbox items, and exporting recoverable data, is available here: https://www.edbmails.com/pages/ost-to-pst-converter.html One important point to remember is that recovery results depend on the condition and readability of the OST file. A conversion tool can help extract available mailbox information, but it cannot recreate data that is no longer present or readable inside the source file.323Views0likes1Comment
Prevent Microsoft 365 meeting invites from automatically appearing in users’ calendars
Hi All, We are trying to prevent Microsoft 365 meeting invites from automatically appearing in users’ calendars as Tentative until the user explicitly accepts the invite. Setting for Outlook Classic, New Outlook and Windows or Outlook Web. Need Microsoft recommendation on this one.1.4KViews1like4Comments
How much of your Microsoft 365 environment can you actually see at once?
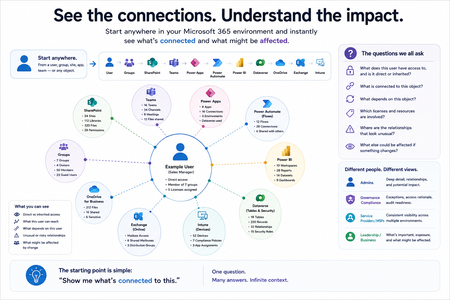
Not how many users you have. Not how many sites, teams, apps or flows you have. How much of it can you actually see connected together? I've been working across Microsoft 365 environments for a while, and I kept running into the same thing. There is no shortage of information. If anything, there is probably too much of it. Users, groups, permissions, SharePoint, Teams, Power Apps, Power Automate, Power BI, Dataverse, OneDrive, Exchange, Intune, licensing, configuration... It's all there. But when you're actually trying to understand how everything fits together, it can be a different story. You open one blade. Find something. Open another. Cross-check it. Go back. Open something else. Before long, you're jumping between different parts of the tenant trying to build the bigger picture in your head. And if you're working with larger environments, that gets difficult pretty quickly. The information isn't necessarily missing. The relationships between the information are what can be difficult to see. That got me thinking about a slightly different question: Instead of "where do I find this information?" "Show me what's connected to this." That's where VisibleState started. Start anywhere. Follow the connections. Imagine starting with a single user. Instead of seeing that user simply as a record with a list of properties, imagine being able to explore the relationships around them: User → Groups → SharePoint → Teams → Power Apps → Power Automate → Power BI → Dataverse → OneDrive → Exchange → Intune Then the questions become different: What does this user have access to? Is that access direct or coming through a group? What resources are connected to them? What depends on something they're associated with? Which licenses are involved? Are there relationships that look unusual? If something changes, what else might be affected? Those questions aren't necessarily about finding another piece of information. They're about putting information that already exists into context. A report can tell you that something exists. A connected view helps you understand what it is connected to. Illustrative example below — not a real customer environment. I'm not suggesting Microsoft 365 doesn't already give us this information Quite the opposite. Microsoft 365 already gives administrators an incredible amount of information and tooling. The thing I've been thinking about is what happens when you want to look across those boundaries. Sometimes I don't want another export. I don't want another list. I don't necessarily want another dashboard. I want to start with something I'm looking at and ask: "What's connected to this?" And then keep following the trail. That's the idea I'm exploring with VisibleState. The interesting part is what happens when you change the viewpoint The same relationships can be useful for completely different reasons. For example: Administrators may want to understand access, permissions and dependencies. Security and governance teams may want to find unusual relationships or exceptions. Compliance teams may need to understand who can access something and why. People managing multiple environments may want a consistent way to understand what's there without rebuilding the picture manually every time. Leadership may not need to see the graph at all. They may simply want to know what's important, what's exposed and what could be affected. It's still the same underlying environment. You're just looking at it from a different angle. And that's where I think things get interesting. Where I'm at with it VisibleState started as something I was building to make my own work easier. I was spending a lot of time investigating environments, tracing access and putting information together for reports. The individual tasks weren't necessarily difficult. It was the jumping between different places and reconstructing the bigger picture that took the time. So I started building something that would let me approach the environment through the relationships instead. It's grown quite a bit from where it started, and I'm continuing to build it. I'm not posting this as a product launch, and I'm not looking for people to sign up. I'm genuinely interested in whether the problem I'm seeing is familiar to other people working with Microsoft 365. So I'm curious... If you could start with any object in your Microsoft 365 environment and immediately see what it's connected to, where would you start? Would it be: Users and access Groups and permissions SharePoint and Teams Power Apps, Power Automate, Power BI and Dataverse Licensing and resources Governance and unusual relationships Something completely different Maybe you've already got a good way of doing this. Maybe you still find yourself jumping between different services and piecing things together manually. Or maybe I'm looking at the problem from the wrong direction. What's the one relationship in your Microsoft 365 environment that you wish you could see instantly?236Views0likes0Comments
Outlook Inbox not updating
Hello, when using the Mail & Calender App on Win 10, everything works fine. But now Windows forces me to use the new Outlook App. When using Outlook my Inbox is not updating, it shows me 2 months old mails on top of the list. Same goes for using the web version outlook.com. My inbox is not updating even though I get new mails everyday. I have to search new mails by using the search bar. I tried to do some research and found blog and forum posts about deleting the Outlook cache. I tried it, I could't find the folder so I went and deinstalled Outlook and installed the old Mail App. Everything worked fine for 2 days. I received new mails like I should. But then again I got forced to move to the new Outlook App. Now it shows me my 2 months old Mails again. What confuses me is why the web version is not working correctly too? My local cache files shouldn't have any influence on the web version. Anybody here that can help me? Thanks in advance.Solved242KViews1like14CommentsNeed suggestions for managing email signatures organization-wide
Hi everyone, I'm looking for advice on managing email signatures organization-wide in Office 365. Right now, every user creates their own signature in Outlook. This has led to inconsistent branding and outdated contact details across the company. I explored a few built-in options, but nothing seems to give proper centralized control, and manually asking every user to update their signature isn't practical. I'm wondering if there's a better way to handle this natively within Microsoft 365, or if most organizations end up going with a third-party tool for this. If you've dealt with something similar, I'd love to hear how you approached it and what worked for you. Any suggestions or experiences would be really helpful. Thanks in advance!359Views0likes6CommentsSwitching Data Loss Prevention Client-Side Checks for OWA
Purview Data Loss Prevention (DLP) rule checks can happen client-side and server-side. This change updates the Exchange Online organization configuration to instruct OWA to stop using Exchange Online to detect potential DLP rule violations before users send email. Instead, OWA will use the workload-neutral Data Classification Services (DCS). Using a workload-neutral service comes with some consequences in terms of OWA being unable to evaluate Exchange-specific predicates. https://office365itpros.com/2026/05/22/data-loss-prevention-dcs/89Views1like0Comments