mobile application management (mam)
857 Topics
New MD-102 : Weird departure from course traditional design
The first slide deck is tremendously long. It takes me 5 hours of lecture to get students into the first lab. The slide decks are very repetitive and could often be replaced with Instructor Demonstration slides. The topics are far-ranging: it mixes identity administration, Intune RBAC, Android enrollment, LAPS, Windows enrollment, and Autopilot before students have a stable mental model of the fundamentals of: Device enrollment > Policy/app creation > Targeting assignment. The first lab is disjointed, with many configurations, such as Creating Administrative units, Assigning Scope tags, and Custom Intune Roles, not implemented until later in the week in Exercise 5. The delegation model, administrative-unit work, and Android restrictions obscure the basics students should understand first. The course design seems to be a big departure from most, if not all, Microsoft courses I have ever taught. No Entra Connect Lab and no real Autopilot lab are a disappointment to some students as well22Views0likes0CommentsMultiple Tenants on One Device
Hello, I have a scenario that I am not sure if it would work or not and wanted to get some clarification: 2 companies, each setup with Intune and MAM policies for mobile. Would I be able to setup both emails on a BYOD device? I don't think it is possible, because the device will need to be registered in Intune Company Portal app to retrieve the policies and check security etc. When you try to add the other address, it will require you to register in Company Portal again, but as far as I know, you can only have 1 company registered at a time?Solved142KViews1like13Comments[New Blog Post] Selective Wipe Corporate Data on unmanagmed devices (iOS/iPadOS and Android)
1. Introduction This blog aims to detail the Mobile Application Management for un-managed iOS/iPadOS devices and un-managed Android devices. This blog is intended to demonstrate how to utilize selective wipe corporate data. When a device is stolen, or lost or an employee leaves the company, you want to be sure there is no corporate data left on the device. This can be achieved by performing a selective wipe. After the selective wipe is requested, the corporate data will be removed from the app. This will be performed the next time the app is started. This guide will touch on three aspects as follow: Conditional Launch Device based wipe request (Stolen/Lost device) User based wipe request (Employee leave the company) How to initiate a wipe There are two ways to initiate a selective wipe. The selective wipe can be performed as part of the Conditional Launch in the App protection policy or by manually initiating a wipe request (Device based wipe and User base wipe). 2.1. Conditional launch When you configure an app protection policy a selective wipe will be configured. This is part of the https://docs.microsoft.com/en-us/mem/intune/apps/app-protection-policy-settings-android#conditional-launch. One of the default settings is “Offline grace period -> 180 days”. After 180 days offline you need to reconnect to the network and successfully authenticate. If the user successfully authenticates nothing will happen, but if the user fails, a selective wipe will be performed. 2.2. Manually initiate a wipe request Here are two ways to manually initiate a wipe request. There is a device based wipe request and a user based wipe request. To initiate a wipe select in the MEM admin center “Apps” -> “App selective wipe” or press https://endpoint.microsoft.com/#blade/Microsoft_Intune_DeviceSettings/AppsMenu/appSelectiveWipe. In the top of the app selective wipe blade, you can select “Wipe request” (device based wipe) or “User-Level Wipe” (user based wipe). 2.2.1. Device based wipe request With a device based wipe request a wipe can be initiated for each user device registered with an app protection policy. If a user has lost the device and a new device is in use. Then a device based wipe can be used to only wipe the previous device. Press the button “Create wipe request” in top of the page. 2. Press “Select user” to select the user of which you want to wipe a device. After the user has been selected the devices belonging to the user will be displayed. Select the device you want to wipe and press “Create”. 3. The wipe request will be sent to the device to remove corporate data from applications protected with an app protection policy. You will return to the app selective wipe blade where you can monitor the removal process of the user. Pending requests can be deleted by right-clicking the request and selecting “Delete wipe request”. 4. After successfully performing a wipe, the device will be removed from the device overview that was display on step 2. Important: The user must open the app for the wipe to occur, and the wipe may take up to 30 minutes after the request has been made. 2.2.2. User based wipe request When performing a user-based wipe request a wipe request will be sent to all apps on all the devices. This wipe you may want to perform when a user leaves the company and you want to be sure that all data is removed from all devices associated with the user. In the app selective wipe page select “User-level wipe” and press “add” to select the user for which you want to perform a user-level wipe. 2. Now the user has been selected wipe requests will be sent to all the devices of the user. As long as the user is on the list. The user will continue to get wipe commands at every check-in from all devices. To allow sign-in on a device you first need to remove the user from the list. 1. The wipe action can be monitored using the https://endpoint.microsoft.com/#blade/Microsoft_Intune/ReportingMenuBlade/userReportSettingKey (“Apps” -> “Monitor” -> “Reports”) or click https://endpoint.microsoft.com/#blade/Microsoft_Intune/ReportingMenuBlade/userReportSettingKey. Important: The user must open the app for the wipe to occur, and the wipe may take up to 30 minutes after the request was made. Author https://www.linkedin.com/in/shady-khorshed-19277723/ is a Microsoft enthusiast. He loves writing on iOS/Android, Windows 11, Windows 365 and related Microsoft Intune. He is here to share quick tips and tricks for all young professionals.7KViews2likes6Comments
Intune App Protection Policy Still Allows Access to iOS Files App
I'm testing a very restrictive Intune App Protection Policy for Microsoft Word on iOS. The policy successfully blocks actions such as saving company data to unmanaged locations, copy/paste, screenshots, printing, and data transfer to other apps. However, users can still open Word, browse the native iOS Files app, open personal/local documents, and modify them. Is this expected behavior? In other words, do App Protection Policies only protect organizational data, while still allowing access to personal files stored on the device? Has anyone found a way to prevent Word from browsing or opening local files through the iOS Files app, either with App Protection Policies, App Configuration Policies, or MDM restrictions? Thanks in advance for any insight.426Views0likes2CommentsHow to Manually Sync the Compliance Policies
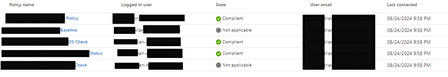
Hi All, We have come across an incident where we need to exclude a device from a device compliance policy after the device got non-compliant according as per the policy. We have exclude the specific user from the compliance policy to meet the requirement (we have assigned the policy to user groups). However, the issue is that the device not get back to the compliant state event after passed 4 days. I would appreciate if anyone could help me here to manually get the device into the compliant state. Please note that, when we go to specific device > device compliance policies, we are not able to see the compliance policy anymore and other applied policies in complaint state (refer image01). However, the device is still showing as non-compliant in devices in Intune (refer image 02). Last checking time is continuously updating as well. Further, We have tried below troubleshooting but there is no luck yet. We are not still take a remote session to the device yet as we have some challenges to get a remote session from the end user. Sync the device from Intune Portal. remotely login into the PowerShell of the device and run below command. Start-Process -FilePath "C:\Program Files (x86)\Microsoft Intune Management Extension\Microsoft.Management.Services.IntuneWindowsAgent.exe" -ArgumentList "intunemanagementextension://synccompliance" Image01 We are not able to see the excluded compliance policy under policy name anymore and the all the applied policies are in complaint state as below. Image02 Thanks in advance Dilan2.8KViews0likes3Comments
Microsoft Teams not working when Company Intune Portal is installed
Hello can someone help me why MS Teams force to closed the app when the company intune portal is installed. I need the company portal to sign in on teams because of policy in our company. But when I installed it crashed the MS team app Using android 13.12KViews0likes3Comments
Android 12 Sign-In Issue with HP Corporate Accounts via Intune Company Portal
Since yesterday, HP employees using older mobile operating systems (Ex. Android 12) have been unable to access Microsoft Outlook and Microsoft Teams on their smart devices. When launching Outlook or Teams, users are prompted to install the Microsoft Intune Company Portal app for authentication and device compliance. However, the latest version of this app appears to require a newer operating system version and is not supported on older devices. As a result, users with devices running Android 12 or earlier cannot complete the authentication process and are unable to use Outlook or Teams. ■ Please provide additional details 1) The issue started yesterday and affects employees using older Android and iOS versions. 2) On iOS devices, users can typically resolve the issue by upgrading to a newer iOS version. 3) However, some Android devices cannot be upgraded further due to manufacturer limitations. 4) For example, Samsung Galaxy Note 10 officially supports Android 12 as its final OS version and cannot be upgraded to Android 13 or later. 5) Because of this limitation, affected Android users are unable to install or use the required Microsoft Intune Company Portal app, which prevents access to Microsoft Outlook and Microsoft Teams. 6) This issue may impact multiple HP employees who are using Android devices that do not support Android 13 or later. Example affected device: Samsung Galaxy Note 10 (Android 12) Affected applications: Microsoft Outlook, Microsoft Teams, and Microsoft Intune Company Portal Business impact: Users cannot access corporate email, messaging, and collaboration services from their mobile devices. I have already posted this issue on the Microsoft Feedback Portal: https://feedbackportal.microsoft.com/feedback/idea/7bba2697-a2a2-f111-85ce-7c1e529382f4 However, this issue cannot be reproduced when using a personal Microsoft account. It only occurs when using an HP corporate email account because HP requires the use of the Microsoft Intune Company Portal app for authentication and device compliance. Since the problem appears to be related to the Intune Company Portal rather than Outlook or Teams themselves, I would like to post this issue here and seek guidance on resolving the Intune Company Portal authentication and compatibility issue affecting Android 12 devices.629Views0likes2Comments