mobile application management (mam)
855 Topics
Intune App Protection Policy Still Allows Access to iOS Files App
I'm testing a very restrictive Intune App Protection Policy for Microsoft Word on iOS. The policy successfully blocks actions such as saving company data to unmanaged locations, copy/paste, screenshots, printing, and data transfer to other apps. However, users can still open Word, browse the native iOS Files app, open personal/local documents, and modify them. Is this expected behavior? In other words, do App Protection Policies only protect organizational data, while still allowing access to personal files stored on the device? Has anyone found a way to prevent Word from browsing or opening local files through the iOS Files app, either with App Protection Policies, App Configuration Policies, or MDM restrictions? Thanks in advance for any insight.209Views0likes2CommentsHow to Manually Sync the Compliance Policies
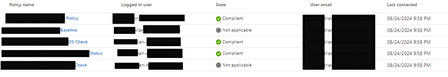
Hi All, We have come across an incident where we need to exclude a device from a device compliance policy after the device got non-compliant according as per the policy. We have exclude the specific user from the compliance policy to meet the requirement (we have assigned the policy to user groups). However, the issue is that the device not get back to the compliant state event after passed 4 days. I would appreciate if anyone could help me here to manually get the device into the compliant state. Please note that, when we go to specific device > device compliance policies, we are not able to see the compliance policy anymore and other applied policies in complaint state (refer image01). However, the device is still showing as non-compliant in devices in Intune (refer image 02). Last checking time is continuously updating as well. Further, We have tried below troubleshooting but there is no luck yet. We are not still take a remote session to the device yet as we have some challenges to get a remote session from the end user. Sync the device from Intune Portal. remotely login into the PowerShell of the device and run below command. Start-Process -FilePath "C:\Program Files (x86)\Microsoft Intune Management Extension\Microsoft.Management.Services.IntuneWindowsAgent.exe" -ArgumentList "intunemanagementextension://synccompliance" Image01 We are not able to see the excluded compliance policy under policy name anymore and the all the applied policies are in complaint state as below. Image02 Thanks in advance Dilan2.6KViews0likes3Comments
Microsoft Teams not working when Company Intune Portal is installed
Hello can someone help me why MS Teams force to closed the app when the company intune portal is installed. I need the company portal to sign in on teams because of policy in our company. But when I installed it crashed the MS team app Using android 13.12KViews0likes3Comments
Android 12 Sign-In Issue with HP Corporate Accounts via Intune Company Portal
Since yesterday, HP employees using older mobile operating systems (Ex. Android 12) have been unable to access Microsoft Outlook and Microsoft Teams on their smart devices. When launching Outlook or Teams, users are prompted to install the Microsoft Intune Company Portal app for authentication and device compliance. However, the latest version of this app appears to require a newer operating system version and is not supported on older devices. As a result, users with devices running Android 12 or earlier cannot complete the authentication process and are unable to use Outlook or Teams. ■ Please provide additional details 1) The issue started yesterday and affects employees using older Android and iOS versions. 2) On iOS devices, users can typically resolve the issue by upgrading to a newer iOS version. 3) However, some Android devices cannot be upgraded further due to manufacturer limitations. 4) For example, Samsung Galaxy Note 10 officially supports Android 12 as its final OS version and cannot be upgraded to Android 13 or later. 5) Because of this limitation, affected Android users are unable to install or use the required Microsoft Intune Company Portal app, which prevents access to Microsoft Outlook and Microsoft Teams. 6) This issue may impact multiple HP employees who are using Android devices that do not support Android 13 or later. Example affected device: Samsung Galaxy Note 10 (Android 12) Affected applications: Microsoft Outlook, Microsoft Teams, and Microsoft Intune Company Portal Business impact: Users cannot access corporate email, messaging, and collaboration services from their mobile devices. I have already posted this issue on the Microsoft Feedback Portal: https://feedbackportal.microsoft.com/feedback/idea/7bba2697-a2a2-f111-85ce-7c1e529382f4 However, this issue cannot be reproduced when using a personal Microsoft account. It only occurs when using an HP corporate email account because HP requires the use of the Microsoft Intune Company Portal app for authentication and device compliance. Since the problem appears to be related to the Intune Company Portal rather than Outlook or Teams themselves, I would like to post this issue here and seek guidance on resolving the Intune Company Portal authentication and compatibility issue affecting Android 12 devices.485Views0likes2Comments
Problems identifying managed iOS devices when using APP
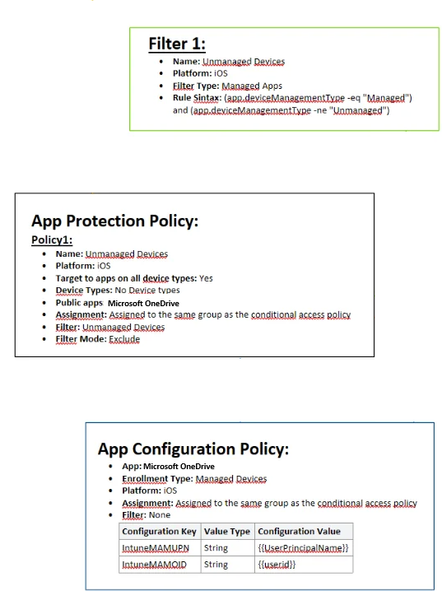
Hello, As the title says i am having a hard time getting this to work. We have been using APP for a long time, but it has not been necessary for us to have different policies for managed (we only use iOS) and unmanaged devices (all mobile device types). Now i want to remove APP from managed devices all together, and only enforce this on unmanaged devices (BYOD) Please see attached image of how it is configured today. I also have an CA policy which requires APP when using MS apps, where i have added and "Filter for devices" exclude with following syntax: device.enrollmentProfileName -contains "iOS standard profile" (which cover our enrollment profiles, both are fully managed) When enrolling a managed device, APP still is enforced. Does anyone have any tips? I wanted to try here before submitting a ticket to MS. As far as i have found out , the app.devicemanagmenttype is the only rule that can be used to filter managed devices when used with APP.500Views0likes1CommentEntra Shared Mode - Force App Stop
Hi All I hope you are well. Anyway, I was asked this yesterday and think I already might know the answer, but here goes. We had an instance of Microsoft Excel stuck in "getting things ready" on an Android Entra Shared Mode Device. Technical Support wondered if there was a way to Force Stop Excel or clear the app data. We had a look in Exit Kiosk Mode, Android Settings, and the Force Stop of Excel said "Action not allowed" and the clear the app data said "Unable to delete data for app" So, my question(s) would be, is going into Exit Kiosk Mode and even trying to force stop / clear data on apps even a valid option, or is this by design? Would adding Excel to this setting help? Any help or confirmation would be greatly appreciated. Stuart595Views0likes3Comments
iOS Enrollment and Conditional Access
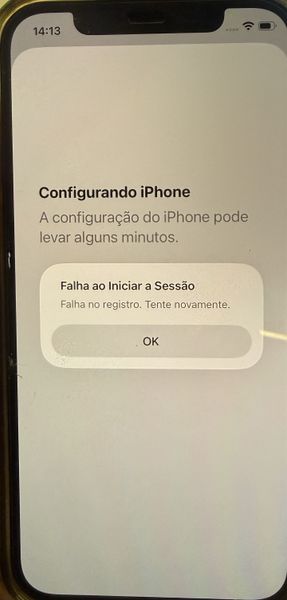
Hello everyone, I need some help! We are configuring Intune to allow BYOD on iOS devices using the Account Driven User Enrollment method. In this scenario, the user enrolls the device by following the path: Settings > General > VPN & Device Management > Sign in to your Work or School Account The enrollment process was working correctly until we configured a Conditional Access policy to ensure that only BYOD-managed devices can access company resources. In other words, only devices that have successfully completed enrollment and are marked as Compliant in Intune should be allowed to use corporate applications. However, after applying the policy, we are no longer able to complete the enrollment process. During one of the enrollment steps, the device displays the following message: Translate English "Setting Up iPhone iPhone setup may take a few minutes. Sign-In Failed Enrollment failed. Please try again. OK" 1. Target resources (Include) 2. Target resources (Exclude) 3. Device Platform: iOS 4. Filter for devices: device.mdmAppId -notIn ["0000000a-0000-0000-c000-000000000000"] 5. Grant: Require device to be marked as compliant This is our current Conditional Access policy configuration. Has anyone encountered this behavior before, or can identify whether there is any setting that might be blocking the enrollment process during the compliance validation stage?259Views0likes1Comment
Windows App Application Protection Policy
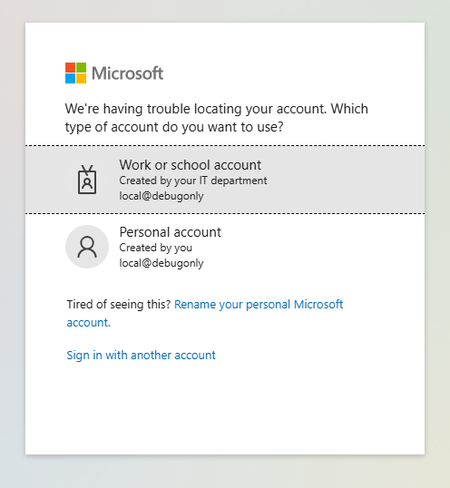
I have been testing out an Intune MAM policy to restrict copy/paste and drive redirection to AVD session hosts based on the link here: https://learn.microsoft.com/en-us/windows-app/require-device-security-compliance-intune?tabs=web#related-contentHowever, I've run into problems (in two separate tenants) that have halted me from being able to test. Setup Intune App Protection Policy targeting Windows Devices & Microsoft Edge\ Conditional Access Policy enforcing App Protection Policy when users access 'Azure Virtual Desktop' target resource via https://windows.cloud.microsoft.com Results First When signing into a user account targeted by the policy, they are prompted to Switch Edge Profile which signs in the user to a new Edge profile for 'Work or School Account'. The account has to sign in again. The account can access Windows App resources When launching a desktop session, this authentication page pops up for an account "local@debugonly" Second When signing into a user account targeted by the policy, they are prompted to Switch Edge Profile which signs in the user to a new Edge profile for 'Work or School Account'. The account has to sign in again. After sign in, the account loops with 'Switch Edge Profile' and gets stuck here I'm curious if anyone has gotten this to work and what was your setup? Or if Microsoft or provide some assistance or if this is in the wrong forum, any help would be appreciated.467Views0likes2CommentsHave OneDrive or SharePoint files/folders on home screen of iPad without internet connection?
This. I'm on a big iOS project. We have several users who need files on an ipad when traveling, and be able to open them when there is no internet connectivity. These files aren't intended to be edited, just 'read only.' These files do not contain any sensitive corporate data. The content lives in SharePoint online and I'm using OneDrive as a bridge to their sharepoint site. BUT the files can only be viewed on the ipad within the OneDrive app without internet access. These are devices using user affinity enrollment. Initially, the solution for users was to use the 'Mark Offline' feature within the OneDrive iOS app. I used Power Automate to have it fetch new files found in OneDrive and move them to the teams SharePoint site. These shared devices are locked down (an understatement). These will be used by the least computer savy/literate people and so having them dive through OneDrive folder after folder, even offline, is a tall order to ask. I totally get it and don't want them doing that either. So now I have to move onto plan B. How can we put the files that live within OneDrive/Sharepoint onto the home screen without an internet connection when the ipad is 'out in the field.?' This would make it infinitely easier for them. The key here is to not have end users manually moving files around. We don't want them to even have to go into OneDrive and mark folders/files offline, if possible. We don't have the SharePoint app on them. I tried the SP app a while back, and it is a hot mess of garbage. I could revisit it. Whatever I can get to work of course we'll have to modify our Intune polices. Thoughts?319Views0likes1Comment