identity
142 Topics
No acces to local Office365 apps with an account which differs from the current windows account
Hi, guys! I'm working with Windows 11 Pro using the Microsoft account ABC. Today I bought a Office 365 Family License - by using another Microsoft account XYZ. I downloaded the local apps successfully... ...but when I start the local app and tried to sign in using the XYZ account, I'm asked for the Windows Hello Pin for the XYZ account - but there is no PIN for that, because the account doesn't exist as a Windows account at this computer at all. Copilot says: "You can sign in to Windows 11 with one Microsoft account and use a different Microsoft 365/Office account for Office applications. Microsoft supports this setup." What did I wrong - what can I do? Kind regards! Sebastian91Views0likes1Comment
Sketchy behaviour from Microsoft on MFA - what gives?
Recently, Microsoft has overwritten our Authentication Method Registration campaign settings, from 'Disabled' to 'Microsoft Managed' for dozens of tenants. Thanks guys. That's not super sketchy at all. /s This was ostensibly done for the Retiring of Voice and SMS based MFA or, as the article puts it 'To help enterprises adopt AI at scale,'.... what? Not because they're garbage MFA methods? But so Microsoft can market-capture MFA? Regardless of that bizarre statement, this article is sub par - like most Microsoft 'help' docs, it appears to have been written by someone in Marketing, with no technical experience. My chief concern is that the term 'OTP' doesn't appear ANYWHERE in here. So, for us and our customers - who block Voice/SMS already - this is alarming. Microsoft's Passkey flow is confusing af to people - and since it includes SYNCED passkeys by default, it faces the same risks as OTP. We specifically HAVEN'T rolled out passkeys because everytime we do, people get confused and frustrated - because they'll have 3-4 different things pop-up, offering to take a sync'd passkey. Really concerned with my 'do not allow microsoft to manage' setting, being explicitly set to 'Microsoft managed', and whatever decisions they're NOT publicly addressing at this point. We've spent years teaching people to use Microsoft Authenticator and password vault-based OTP. Now, Microsoft is pushing everyone to keep using those same tools, but to go through the mess that is the passkey setup interface?79Views0likes0CommentsHacked Microsoft Account Recovery with Semi Access
I'm at a complete loss and it is infuriatingly ridiculous. I am entirely unable to get a hold of a human being at Microsoft and am being turned down by automated responses nonstop. So here's what's happening: My Microsoft account has been hijacked (obviously not this one) for its valuable Minecraft account and has now been sold. I am logged into my account via my PC, have full access of the main email address, but I have been locked out of my account using the alias email. Whenever I want to log in to my account, it wants to instead send a code to an email address I do not own and can't access. I have tried the Sign-In Helper, the Recovery Form, the hotline, the support email without any result, let alone a non-automated response. I sadly don't have the Recovery Code of my 15 year old-ish account. Since I still have full access of my email address I get updates of security info being changed and what not. Last month a stranger sent me screenshots of someone trying to sell my Minecraft account, for which I myself have received multiple buying offers, and voila yesterday I received notification of my alias mail address changing followed by Minecraft server apps being added to my Microsoft account. While I had already given up retrieving my account, whenever I get notifications my heart sinks a new while some hope sparks up again. Do you people have any idea of what I could do? I don't even rule out legal actions at this point. While I do of course have the email address of the hijacker and the buyer, I fear that contacting them results in me being locked out permanently. I'm just begging to catch the attention of anyone involved with Microsoft. This being walled out with automated responses is killing me.134Views1like1Comment
Project Lifeline: Biometric Security Ecosystem for Lock-Screen Password Recovery
Title: Project Lifeline: Biometric Security Ecosystem for Lock-Screen Password Recovery Overview The Lifeline application is a proactive biological and digital security ecosystem specifically designed to protect smartphone users from data loss and the erasure of personal memories caused by forgetting the screen lock code (PIN/Password). How it Works • Secure Registration: While the phone is unlocked, the user registers their name, phone number, and email, and securely saves their screen lock code in an encrypted format within the isolated system vault (SecureStore). • Persistent Notification: This immediately generates a persistent, silent notification in the notification drawer that functions even when the screen is locked with a password and automatically restarts upon device boot. • Emergency Rescue: In the event of an emergency when the code is forgotten, the user simply pulls down the notification drawer from the lock screen and taps the rescue button. Identity Verification & Decryption The application invokes the phone’s biometric security system (face scan or fingerprint) or the "System Credential Fallback" (such as a backup code or a secret security question) to ensure maximum privacy protection and block intruders. Once identity verification succeeds, the app decrypts the code and displays it instantly on the screen inside the app, allowing the user to unlock their device in seconds, at zero material cost, and without the need for an enforced factory reset or losing any files
Microsoft Authenticator backup not recognized by the same recovery account
My old Android phone has completely failed, so I can no longer access Microsoft Authenticator on that device. I had previously enabled Cloud Backup in Microsoft Authenticator, and I am certain that I am signing in with the same Microsoft personal account that was originally used as the recovery account. On my new Android phone, I reinstalled Microsoft Authenticator and selected “Restore from backup / Begin recovery” before adding any accounts. I then signed in with the same Microsoft personal account. However, Authenticator says that the backup is not stored under this account and asks me to try another personal Microsoft account. I am certain that this is the correct recovery account. Both the old phone and the new phone are Android devices, so this is not a cross-platform restore issue. I would like to know: Could this be a problem with the association between the cloud backup and the recovery account? Is there any way for the Microsoft Authenticator team to verify whether a backup still exists? Is there any supported way to recover the original backup instead of manually resetting and re-enrolling every third-party 2FA account? My old device is completely inaccessible, so I cannot open Authenticator there or create a new backup. Any guidance from the Microsoft Authenticator or Identity team would be appreciated.184Views0likes1CommentHelp me recover my account.
Hi, My other Microsoft account was recently compromised but it was compromised before as well. When it was compromised before, the hacker added a recovery email for verification and to remove that I added my another email and the request was sent and it was supposed to change in October and I was not able to change the password or use other features of Microsoft because at some point it keep redirecting me to the page that I have sent a request but during that time period, my account was compromised again and I keep receiving emails of unusual sign-in activity by the hacker and I wanted to change the password but I couldn't because of that request so I was being patient. Now I received an email that someone accessed my Microsoft account and now I have to verify my identity to log in and to log in it ask me to type the email that the hacker set up because it's not changed and since I don't know what that is it takes me to the account recovery page where I put all the information that I know, I write in my postal code, my old and current passwords, date of birth etc. I have never used skype, Hotmail or outlook and Xbox so I just uncheck those boxes and then it asks me if I have ever bought any product but since I didn't so I uncheck that as well but then I just receive the email that the information I provided is nonsufficient even thou I provided all the information that is correct. Unfortunately Sign-in helper didn't work. Kindly help me resolve the issue. Looking forward to your positive response. Yours sincerely.68Views0likes0Comments
Minha conta Microsoft foi comprometida e o e-mail original deixou de ser reconhecido
Olá, preciso de ajuda para recuperar minha conta Microsoft. Minha conta originalmente usava o endereço email address removed for privacy reasons. Recentemente perdi o acesso e, quando tento entrar ou usar o formulário de recuperação com esse endereço, aparece a mensagem de que “a conta Microsoft inserida não existe”. Acredito que o endereço de e-mail e as informações de segurança da conta tenham sido alterados sem minha autorização. O endereço email address removed for privacy reasons ainda aparece no meu Microsoft Authenticator. Ainda tenho o Authenticator associado à conta antiga, mas o código de verificação não é aceito. Durante uma tentativa de recuperação apareceu o endereço email address removed for privacy reasons, que não reconheço. A conta também ainda aparece associada ao meu perfil de administrador do Windows e ainda consigo acessar minha conta do Minecraft pelo site. Já tentei o Assistente de Entrada e o formulário de recuperação, mas o endereço original não é mais reconhecido. Gostaria de saber qual é o procedimento correto para recuperar a conta ou entrar em contato com o suporte responsável por contas Microsoft comprometidas. Obrigado pela ajuda!121Views0likes0Comments
Microsoft Account connected apps management
Why is there no visible “Connected apps” management page in Microsoft Account? I noticed that third-party applications connected to a personal Microsoft account can be managed at: https://account.live.com/consent/Manage However, I cannot find any obvious navigation path to this page from the main Microsoft Account portal: https://account.microsoft.com/ The main account portal provides sections such as Security, Privacy, Devices, Subscriptions, and Your info, but there does not appear to be a visible “Connected apps”, “Apps and services”, or “App permissions” entry. I only discovered the consent management page after receiving a Microsoft security notification that a new application had been granted access to my Microsoft account. The “Manage your apps” button in that email links to the older account.live.com consent page. This creates two usability and security concerns: Users may not know where to review or revoke third-party OAuth permissions unless they still have the original security notification email. Microsoft Account management currently uses both microsoft.com and live.com domains, which can be confusing for users trying to verify whether an account-management page is an official Microsoft page. Would it be possible to add a visible “Connected apps”, “Apps and services”, or “App permissions” entry under Security or Privacy in account.microsoft.com? This would not require redesigning the existing consent system. Even a simple link from account.microsoft.com to the existing account.live.com/consent/Manage page would make third-party permission management much easier to discover. Is there currently an official navigation path to this page that I may have missed?418Views0likes2CommentsWho Can Access What? Designing RBAC and Identity in Azure
Who should be allowed to access an Azure resource? Azure makes it easy to create resources. The harder question comes afterwards: who should be allowed to access them? A Function App may need to read secrets from Key Vault. A Logic App may need to call APIs through API Management. A developer may need to deploy to Dev but have no access to Production. A CI/CD pipeline may need to deploy infrastructure without becoming an Owner of the entire subscription. This is where Azure Role-Based Access Control (RBAC) and Managed Identity become critical. In this article, I look at how to design access around people, applications and deployment pipelines, while keeping permissions as narrow as practical. The article covers: Azure RBAC and access scopes Least-privilege access Managed Identities Developer vs Production access boundaries Application identities CI/CD deployment permissions RBAC vs API authentication Privileged access and PIM Common RBAC design mistakes One of the key principles is simple: Give an identity only the permissions it actually needs. For example, if a Function App only needs to read secrets from Key Vault, giving it Contributor access to the entire Resource Group solves the problem with a much broader permission than necessary. Good RBAC design is not about assigning more permissions. It is about understanding: Who needs access? Why do they need it? What exactly do they need to do? At what scope should access be granted? How can that access be managed securely over time? I would be interested to hear how others approach RBAC and identity design in enterprise Azure environments. Full article: https://www.linkedin.com/pulse/who-can-access-what-designing-rbac-identity-azure-chethan-raj-ud6gc/221Views0likes0Comments
How much of your Microsoft 365 environment can you actually see at once?
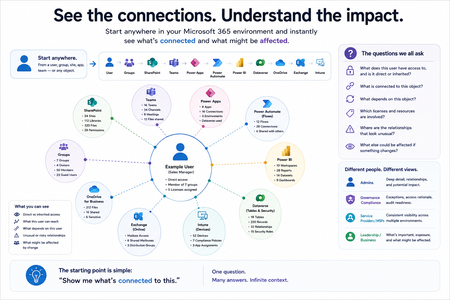
Not how many users you have. Not how many sites, teams, apps or flows you have. How much of it can you actually see connected together? I've been working across Microsoft 365 environments for a while, and I kept running into the same thing. There is no shortage of information. If anything, there is probably too much of it. Users, groups, permissions, SharePoint, Teams, Power Apps, Power Automate, Power BI, Dataverse, OneDrive, Exchange, Intune, licensing, configuration... It's all there. But when you're actually trying to understand how everything fits together, it can be a different story. You open one blade. Find something. Open another. Cross-check it. Go back. Open something else. Before long, you're jumping between different parts of the tenant trying to build the bigger picture in your head. And if you're working with larger environments, that gets difficult pretty quickly. The information isn't necessarily missing. The relationships between the information are what can be difficult to see. That got me thinking about a slightly different question: Instead of "where do I find this information?" "Show me what's connected to this." That's where VisibleState started. Start anywhere. Follow the connections. Imagine starting with a single user. Instead of seeing that user simply as a record with a list of properties, imagine being able to explore the relationships around them: User → Groups → SharePoint → Teams → Power Apps → Power Automate → Power BI → Dataverse → OneDrive → Exchange → Intune Then the questions become different: What does this user have access to? Is that access direct or coming through a group? What resources are connected to them? What depends on something they're associated with? Which licenses are involved? Are there relationships that look unusual? If something changes, what else might be affected? Those questions aren't necessarily about finding another piece of information. They're about putting information that already exists into context. A report can tell you that something exists. A connected view helps you understand what it is connected to. Illustrative example below — not a real customer environment. I'm not suggesting Microsoft 365 doesn't already give us this information Quite the opposite. Microsoft 365 already gives administrators an incredible amount of information and tooling. The thing I've been thinking about is what happens when you want to look across those boundaries. Sometimes I don't want another export. I don't want another list. I don't necessarily want another dashboard. I want to start with something I'm looking at and ask: "What's connected to this?" And then keep following the trail. That's the idea I'm exploring with VisibleState. The interesting part is what happens when you change the viewpoint The same relationships can be useful for completely different reasons. For example: Administrators may want to understand access, permissions and dependencies. Security and governance teams may want to find unusual relationships or exceptions. Compliance teams may need to understand who can access something and why. People managing multiple environments may want a consistent way to understand what's there without rebuilding the picture manually every time. Leadership may not need to see the graph at all. They may simply want to know what's important, what's exposed and what could be affected. It's still the same underlying environment. You're just looking at it from a different angle. And that's where I think things get interesting. Where I'm at with it VisibleState started as something I was building to make my own work easier. I was spending a lot of time investigating environments, tracing access and putting information together for reports. The individual tasks weren't necessarily difficult. It was the jumping between different places and reconstructing the bigger picture that took the time. So I started building something that would let me approach the environment through the relationships instead. It's grown quite a bit from where it started, and I'm continuing to build it. I'm not posting this as a product launch, and I'm not looking for people to sign up. I'm genuinely interested in whether the problem I'm seeing is familiar to other people working with Microsoft 365. So I'm curious... If you could start with any object in your Microsoft 365 environment and immediately see what it's connected to, where would you start? Would it be: Users and access Groups and permissions SharePoint and Teams Power Apps, Power Automate, Power BI and Dataverse Licensing and resources Governance and unusual relationships Something completely different Maybe you've already got a good way of doing this. Maybe you still find yourself jumping between different services and piecing things together manually. Or maybe I'm looking at the problem from the wrong direction. What's the one relationship in your Microsoft 365 environment that you wish you could see instantly?234Views0likes0Comments