exchange
3435 TopicsThe Great Exchange Online Meltdown of November 2026
November 12 was a bad day for Microsoft 365. A massive Exchange Online outage reduced servers to quivering wrecks and affected many other Microsoft 365 services. I was out of the office in France, peacefully researching wine, when all hell broke loose. One thing we learned is that Exchange Online is extremely well connected with other Microsoft 365 services. The other is that putting all an organization’s eggs into one cloud basket might not be such a great plan after all. Now that Microsoft has published its preliminary Post-Incident Report, the guesswork about what happened can fade and tenants can concentrate on what they should do in the future, including the potential to file a claim for service credits to cover the incident period. In this article, I cover: Why Exchange Online rather than Outlook was the center of the story. Why Exchange Online has such a large dependency blast radius across Microsoft 365. How the SLA calculations work and how the calculated outage flows into service credits. What this says about single-provider operational concentration. The future question of millions of agents adding workload to services originally built around human users. ... and more... https://office365itpros.com/2026/11/16/exchange-online-outage-nov26/2.9KViews0likes0Comments
Outlook still down in India – EX1550543 / MO1550821
Still affected here in India as of 10:45 UTC, 13 Nov 2026 (EX1550543 / MO1550821). Outlook on the web and Outlook desktop are both unable to connect. Sign-in to Microsoft 365 works, but Outlook isn't loading. We've ruled out local network issues on our side, so it looks like the fix hasn't reached our region yet. Is anyone else in India still affected, or seeing recovery?287Views0likes1CommentThe CISO Cheat Sheet to Microsoft Digital Defense Report 2026
I know we’re all busy, so I’ve pulled the most important data from this year’s Microsoft Digital Defense Report into one short read. The full report is well worth exploring, but this article focuses on the numbers and trends most relevant to security leaders. This year’s edition shows that AI is lowering the time, expertise and cost required to discover and exploit weaknesses, enabling attackers to operate with greater speed, scale and autonomy. The report describes this as AI “changing the physics of cybersecurity”: attack timelines are compressing and agentic systems are beginning to automate more of the attack lifecycle. Trend 1: Time has collapsed The clearest finding is about speed. Vulnerability discovery is increasingly running ahead of remediation, while the time from discovery to weaponisation is shrinking. In the AI era, weaponisation can follow in hours. Vulnerability discovery and weaponisation now often needs only a well-written prompt. The median time from discovery in the wild to weaponisation is below 24 hours. Vulnerabilities were on track for a record estimated 72,000 CVEs in 2026. The report expects a multi-year period in which the number of known but unpatched vulnerabilities rises sharply before eventually declining. The median time from container start to first exploit attempt is 5.3 hours. The ransomware actor Storm-1175 moved from web-facing exploitation to deploying Medusa ransomware in as little as 24 hours. CISA added over 110 CVEs to its Known Exploited Vulnerabilities catalogue between November 2025 and May 2026, most within a week of disclosure. The mismatch with enterprise reality is the uncomfortable part. The report says the disclosure-to-exploitation window has shrunk to single-digit days. Between November 2025 and May 2026, CISA added more than 110 vulnerabilities to its Known Exploited Vulnerabilities catalogue, most within a week of disclosure. In one example, Storm-1175 moved from exploiting a web-facing vulnerability to deploying Medusa ransomware in as little as 24 hours. Microsoft’s Red Team makes an important point: a patch is also a disclosure. Every fix points attackers towards the flaw it closes. As AI-assisted analysis makes reversing patches faster and more reliable, the report argues that patch velocity, not simply patch availability, becomes the control that matters. Trend 2: Attack chains are gaining autonomy The report charts a clear progression: September–November 2025: AI assists in orchestrating a campaign, as in the Anthropic-reported espionage case. April–June 2026: Full-chain autonomy is demonstrated in labs. July 2026: Real-world autonomous attacks of increasing complexity appear. Two frontier models, Mythos and GPT-5.5, completed a 32-step attack chain against an emulated enterprise with no human help. The test environment had no defenders. The UK AI Security Institute reached a similar finding independently. GPT-5.5 was the second model to solve its end-to-end corporate network attack simulation, a task AISI estimates would take a human about 20 hours. Open-weight models lag closed models at orchestrating attacks by about seven months. In the wild, early July 2026 saw the first documented automated ransomware extortion attack, named JADEPUFFER by Sysdig. Microsoft has seen AI-orchestrated intrusions that share elements with it. Initial access consistently came from internet-exposed services running known-vulnerable software. The report is measured on this point. Volumes of AI-orchestrated activity remain low. In most observed real-world operations, complex end-to-end intrusions still retain meaningful human direction. The Red Team's framing is the most useful one: AI doesn't create a new class of attack, it collapses the effort needed to find and exploit existing attack paths. Trend 3: AI has become an attack surface The report's second takeaway is that attackers are already targeting AI itself. The adoption numbers explain why. 88% of enterprises are experimenting with agents, and 82% of leaders plan broader rollouts within 12–18 months. The report cites industry projections of roughly 1.3 billion agents in production by 2028. What attackers are doing to AI systems: Four techniques accounted for roughly 90% of observed attack activity in telemetry from Azure AI workloads: malicious link injection (52%), jailbreaks (16%), tool and agent abuse (12%), and identity and credential abuse (10%). Memory poisoning: An attacker who can place content anywhere an agent reads can often place it where the agent remembers. Email is the dominant pathway the Red Team has observed. Human-in-the-loop isn't a complete control: Red team testing saw approval prompts ignored, or bypassed by a policy stored in poisoned memory. Developer tools turned against their owners: The "s1ngularity" malware hijacked locally installed AI command-line tools to hunt for secrets. It leaked about 2,000 secrets and 20,000 files across 225 victims. AI browsers: In daily use at more than 40% of organisations in Microsoft's dataset, they were the initial infection vector in incidents involving 57 malware families in a May 2026 analysis. Chat histories as a target: Malicious AI-assistant extensions reached nearly 900,000 installs and more than 20,000 enterprise tenants, harvesting AI chat histories that often contain code, architecture and credentials. The identity implications are direct. Each agent needs its own identity, not one borrowed from an employee, and a named human sponsor. The report also treats revocation latency, the time to cut off a compromised agent, as a measured outcome. Trend 4: The front door is still identity AI changes the speed and personalisation of social engineering. It hasn't changed where attacks start. Initial access in Defender Experts data: User execution: 30% Valid accounts: 20% Malicious copy-and-paste: 13% Phishing: 11% Together, user execution and valid accounts account for over half of observed activity. In incident response engagements, phishing as an initial access vector jumped from 7% to 23% year on year. The standout numbers: ClickFix: Defender saw user-pasted malicious commands on more than 1.1 million unique devices between February and early May 2026, roughly an 8x increase. AiTM: URLs accounted for 45% of the identified phishing techniques in the report’s breakdown. Separately, the share of AiTM phishing and token-theft attacks more than doubled during the first six months of 2026, although the report notes that their overall share remained comparatively small. Teams vishing: Weekly confirmed malicious volume increased 502% year on year. Per attempt, 48% of vishing calls kept the victim engaged for more than 20 seconds, and 30% lasted more than one minute. When a call succeeds, attackers can persuade the victim to install a remote-management tool and complete reconnaissance in two minutes or less. Business contact impersonation (BCI): The report introduces this term for conversations that start with a trusted-looking contact. Microsoft detected more than 46 million attacks in 12 months, with a 121% spike in April 2026. The share of first-contact messages that explicitly asked for money or documents fell from 17% to 3%. The first message is deliberately bland, like "Are you at your desk?" Password attacks declined 26% year on year, which the report describes as strong evidence that MFA and passkeys are forcing attackers to pivot. That pivot includes techniques such as fatigue attacks, AiTM phishing and token theft designed to circumvent conventional MFA. Trend 5: Attackers are inheriting trust rather than breaking in The report's headline theme is that risk is increasingly interconnected. Threats travel through the trusted relationships between identities, software supply chains, partners and cloud platforms. The numbers: Supply chain: Major open-source ecosystems saw attacks roughly every ten days, accelerating through Q2 2026. Shai-Hulud 2.0 affected 25,000 repositories. Megalodon backdoored 5,561 GitHub repositories in under six hours. Trusted signing: In May 2026, Microsoft disrupted Fox Tempest, a "malware-signing-as-a-service" operation that obtained genuine certificates for ransomware loaders and infostealers. Microsoft revoked over a thousand fraudulent code-signing certificates. Legitimate access: An unsanctioned remote monitoring tool is now one of the most reliable mid-stage indicators of a human-operated intrusion. Cloud identity: Cloud identity abuse was the most observed technique against critical infrastructure, representing 78% of the technique mix in Microsoft’s data for March to June 2026. Hybrid intrusions: The Storm-2885 case showed an attacker using a privileged cloud identity to close and downgrade security alerts. The report says identity governance and alert-handling workflows deserve Tier 0 treatment. Dwell time: DART data shows a statistically significant increase in dwell time year on year, meaning organisations took longer to detect intrusions. Ransomware shows the same ecosystem pattern. Qilin led leak-site data with 16.4% of victims, up 386%. Defender detections tell a different story, with Akira at 22%. Trend 6: Defence works best when it's connected The report is not only a catalogue of threats. The strongest defensive evidence: Disruption works. Following the March 2026 disruption, Tycoon2FA activity had fallen 95% from its November 2025 peak by June. Its share of CAPTCHA-gated phishing declined from 76% in December 2025 to 12% in June 2026. Correlation is the highest-leverage variable. The report argues that how well defenders share and correlate signals across endpoint, identity, cloud, email and network is one of the highest-leverage strategic variables under their control. AI is also changing defensive operations. The report describes AI-assisted triage, incident summarisation, hunting-query generation and detection engineering as ways to accelerate investigations and allow analysts to concentrate on higher-value work. Automated disruption can compress response time. The report says that when a correlated incident reaches a defined confidence threshold, defensive systems can automatically isolate devices, disable compromised accounts, revoke sessions or quarantine affected cloud resources. It also stresses the importance of appropriate governance and human oversight for high-risk AI actions. The report also recommends changing what leaders measure. It suggests moving from patches deployed to exposure reduced, detection coverage increased and time-to-mitigate compressed. What the MDDR recommends: ten security priorities The report starts its recommendations with the foundations: Secure by Design, Secure by Default and Secure Operations, applied through identity-centric Zero Trust. Microsoft says these keep the priorities below durable as AI adds more identities, applications, agents and dependencies to govern. Govern cyber risk at leadership level. Report identity exposure, patch latency, agent permissions, critical dependencies, dwell time and recovery readiness to the board. Defend identity as the primary control plane. Deploy passkeys and phishing-resistant MFA, reduce privilege and govern human and non-human identities. Invalidate and rotate tokens and session credentials quickly. Establish governance, visibility and data controls for AI. Keep visibility of approved AI tools, services and agents, and monitor for unauthorised or unmanaged use. Apply sensitivity-aware access and data protection to the data those systems can reach. Reduce exposure and edge risk. Continuously discover internet-facing assets and patch edge devices quickly. Centralise high-fidelity logging, enforce strong authentication and combine network visibility with threat intelligence. Focus on cross-signal correlation. Correlate endpoint, identity, cloud, application, email and network signals to detect intrusions earlier. Correlation also helps defenders anticipate attack paths and likely targets. Enact a continuous threat and vulnerability management model. Combine asset visibility, vulnerability identification, threat detection and AI-accelerated insight into a single continuous programme. Validate exposure through proactive testing. Run assume-breach exercises on cloud services, SaaS platforms, APIs and workflow automation. Prioritise them by where your highest-value data is stored, accessed or aggregated. Secure software dependencies. Harden software installation, keep a software inventory and validate provenance. Monitor packages and prepare for rapid containment. Participate in collective defence. Share actionable threat indicators and victim-informed intelligence with trusted partners and law enforcement. This supports coordinated tracking, investigation and disruption. Prepare for long-horizon technology transitions. Build a cryptographic inventory and advance post-quantum planning alongside AI governance. Read together, the numbers tell one story: the attacker’s workflow is becoming faster and less expensive. AI can shorten vulnerability discovery, exploitation, secret discovery and lateral movement, while organisations still face the slower operational work of testing, coordinating and deploying safe changes across complex environments. At the same time, agent identities can proliferate faster than organisations can inventory, govern and revoke them The defining question for boards today is not whether disruption will occur, but whether the organization can continue operating, contain harm, recover quickly, and maintain trust when it does. Source: Microsoft Digital Defense Report 2026, Version 1.1. Reporting period: July 2025–June 2026.Shared Calendars No Longer Visible
For years, I've shared Outlook calendars between my Outlook accounts and with my husband's, without any issues. However, since mid-June the shared calendars have disappeared for no apparent reason. The sharing permissions are still in place, but the calendars are no longer visible or available to add on Android, in the Outlook desktop app, or on Outlook on the web. I've spent hours Googling and tried all the usual troubleshooting steps, but nothing has worked! As a workaround, I now have to invite all @outlook.com accounts to calendar events just so everyone can see them and avoid double bookings. Has anyone come across this before and found a fix that isn't one of the standard "how-to" suggestions? Note: these are personal paid Microsoft accounts.3KViews0likes5CommentsM365 Admin Center Global Administrator Lockout
Hello Microsoft Community, I am seeking urgent assistance and guidance regarding a critical Microsoft 365 tenant lockout that has been ongoing for several days without a resolution or proper communication from the support team. Our organization manages Microsoft 365 services for a business with more than 200 active users who depend on Microsoft 365 for their daily operations. Issue Description We have been locked out of our Microsoft 365 tenant's administrator account. This prevents us from properly managing our Microsoft 365 environment and restoring normal access to essential business services. Our business-critical data, including important documents and operational information, is stored in SharePoint. The inability to access and manage these services has significantly disrupted our business operations. Microsoft Support Ticket References We have raised multiple support tickets and followed up repeatedly, but the issue remains unresolved. Tracking ID: 2610050040001149 Tracking ID: 2610090010001066 Tracking ID: 2610050040001222 Despite these support cases and repeated follow-ups, we have not received a satisfactory resolution or a clear recovery timeline. Support Experience So Far Following a discussion with the support team, we were expecting a call to assist with unlocking the administrator account and providing a temporary password through the appropriate recovery process. However, we have not received the expected call or a meaningful update. Our main concerns are: Complete loss of access to the Microsoft 365 tenant administrator account. More than 200 users affected by the ongoing incident. Critical business data and documents stored in SharePoint. Multiple support tickets without a concrete resolution. Lack of clear communication regarding the root cause and recovery timeline. No clear escalation path or confirmation of the next recovery steps. Our Concerns We understand that technical issues can occur, but leaving a business-critical environment inaccessible for an extended period without meaningful updates is extremely concerning. We purchase Microsoft 365 licenses through a partner and expect appropriate technical support and escalation assistance when critical incidents occur. Our organization previously used Google Workspace and recommended migrating to Microsoft 365 because of its enterprise capabilities. This incident has seriously affected user confidence and business continuity. If access cannot be restored promptly, we may have to consider alternative email hosting arrangements to minimize further disruption. Request for Assistance I would appreciate guidance from Microsoft engineers, Microsoft 365 administrators, and community members who have experienced similar situations. What is the appropriate escalation process when all available tenant administrator accounts are inaccessible? How can we expedite tenant ownership verification and administrator account recovery? Is there a dedicated Microsoft team that handles critical tenant lockout incidents affecting business operations? What is the recommended recovery process when the administrator cannot access the Microsoft 365 Admin Center? How can we obtain urgent assistance when multiple support tickets and repeated follow-ups have not resulted in a clear resolution? Can the three referenced support tickets be escalated for urgent review by the appropriate Microsoft support team? We are not looking for workarounds that compromise tenant security. We need Microsoft's official recovery process to restore authorized administrative access safely. Microsoft Support Team: If any Microsoft support representatives are monitoring this community, we would appreciate your guidance on the appropriate escalation channel for this incident. We can provide additional information privately through the appropriate official channels. Thank you for your time and assistance. Any guidance that helps us restore our services and protect business continuity would be greatly appreciated. Best regards, Microsoft 365 Tenant Administrator344Views0likes1Comment15 productivity features in the new Outlook for Windows
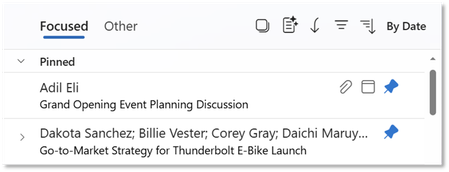
Hello, Outlook community. I’m Vicki Milton, a Principal Product Manager on the Outlook team. Over the last year, we’ve added important capabilities across areas such as offline support, shared mailboxes, and PST files. Alongside those milestones, we've continued to deliver smaller improvements that help people work more efficiently throughout the day. This article highlights 15 productivity features in the new Outlook for Windows that can help you stay organized, reduce routine effort, and keep important work moving. Mail features Email remains central to how many people manage communications, priorities, and follow-up. Outlook includes familiar tools for composing and organizing messages, along with newer capabilities that can help reduce friction and make inbox management more efficient. Pin a mail: Keep important messages easy to find. The Pin feature keeps a selected email at the top of your inbox so it remains visible as new messages arrive. This can be useful for items you need to reference often or do not want to lose track of, such as travel details, approvals, or active requests. By keeping priority messages in view, Pin can reduce time spent searching and help you stay focused on current work. Snooze a mail: Return messages when they are relevant again. Snooze lets you temporarily remove an email from your inbox and have it reappear at a time you choose. This can help keep your inbox focused on messages you can act on now while ensuring follow-up items come back when they are timely. It is particularly useful for requests that depend on additional information, scheduled tasks, or work you plan to handle during dedicated focus time. Add multiple categories at the same time: Organize messages with fewer steps. If you use categories to manage incoming mail, Outlook makes it possible to apply more than one category in a single action. This can help when you need to capture multiple types of context, such as project, priority, or follow-up status, without reopening menus repeatedly. It is especially useful when processing a large number of messages. Sweep: Reduce repetitive inbox cleanup. Sweep lets you create automatic actions for messages from a specific sender. For example, you can delete promotional mail after a set period, keep only the latest message in a thread, or move recurring updates to a folder. This can help reduce manual cleanup and keep your inbox more focused on items that need attention. Schedule Send: Write on your schedule and deliver at the right time. Schedule Send lets you prepare messages when it is convenient for you and send them later at a time that works better for the recipient. This can improve visibility, support more intentional communication, and reduce the need to rely on reminders or leave messages in Drafts. Simplified folder sharing: Share folders more simply. Sharing a mail folder has traditionally required extra permission steps, especially for nested folders. Now, when you share a folder, Outlook can automatically apply the visibility permissions needed for its parent folders. This can reduce setup effort, help avoid access issues for recipients, and make folder sharing easier to complete with confidence. Calendar and meeting features For many people, the workday is shaped by meetings, schedule changes, and the need to stay aligned on what comes next. Outlook includes calendar and meeting capabilities that can help simplify planning, reduce coordination overhead, and make follow-up easier. Follow a meeting: Stay informed without attending live. The Follow RSVP option lets you indicate that you will not attend a meeting but still want access to the recap. This can be helpful when schedules overlap or when a meeting is useful to monitor without joining in real time. It can help you stay connected to outcomes and shared materials while keeping your calendar more manageable. Save calendar views: Return to the calendar setup you need more quickly. Saved Views let you store specific calendar combinations and switch back to them without rebuilding the same view each time. This can save time for people who move frequently between personal, team, and project schedules. It also can make it easier to review the right set of calendars for different planning tasks. Improved meeting tracking: Work with meeting responses more efficiently. Outlook includes tools that make it easier for organizers to review and manage meeting responses. You can sort attendee lists, search for names in the Tracking view, and copy or download response details when needed. These capabilities can be especially useful for larger meetings where attendance information needs to be reviewed quickly. Meeting recap: Find follow-up materials in one place. After a Teams meeting, the calendar event in Outlook can surface a Meeting recap with links to the recording, transcript, and shared files. This can make it easier to review what was discussed, confirm details, or catch up afterward. By keeping these materials together, Meeting recap can reduce the time it takes to get oriented after a meeting. Filtered views: Reduce visual clutter in your calendar. Filters let you hide meetings you are not attending and limit the distraction of declined or informational events. This can make it easier to scan your schedule, identify conflicts, and focus on the meetings that need your attention. For people with full calendars, it can help make planning more straightforward. Change a recurring event: Update future meetings while preserving earlier ones. When plans change, Outlook lets you edit the current event and all following events in a recurring series. This can make it easier to adjust details such as time, location, or agenda going forward without changing the record of past meetings. It can simplify updates for organizers and reduce disruption for attendees. Personalization and settings Settings can play a practical role in day-to-day productivity. A few adjustments can make it easier to focus, move between accounts and calendars, and work in a way that fits your preferences. Here are several settings-related features that can help make Outlook feel more streamlined and manageable. Rename your email accounts: Make the right inbox easier to recognize. If you use multiple accounts in Outlook, you can assign each one a custom name. This can help you tell accounts apart more quickly, reduce the chance of sending from the wrong inbox, and make navigation simpler as you move between accounts during the day. Modern themes: Choose a look that supports comfort and clarity. Outlook includes theme and color options that let you tailor the experience to your preferences. Visual settings can influence readability and comfort, especially for people who spend much of the day in email and calendar. Options such as Dark Mode and color customization can help make the interface feel easier to use over time. Keyboard shortcuts: Keep familiar ways of working. In Outlook, you can choose the shortcut style you prefer in Settings. This can help you maintain existing habits, reduce adjustment time, and complete common tasks with fewer steps. For people moving from classic Outlook or Outlook on the web, shortcut flexibility can make the transition more consistent. These features reflect a broader effort to help people work more efficiently in the new Outlook for Windows. Whether you are managing a high volume of email, coordinating a full calendar, or tailoring the experience to match your workflow, these updates are designed to reduce effort and improve day-to-day productivity. For more information and step-by-step guidance, see the Microsoft Support articles and the Learning Path.8.9KViews2likes9Comments
Classic Outlook "EMAIL FORWARDING IS ON" bar: how to keep forwarding and remove the bar
Since around August 2026, classic Outlook (Microsoft 365) has shown a brown bar across the message list: "EMAIL FORWARDING IS ON — You are forwarding your email to …" with a Manage Rules button. There's no setting or registry key to dismiss it. The usual advice is to turn the forwarding off, which doesn't help if the forwarding is deliberate. This behavior disappeared for a while but has recently returned. I have several Inbox rules that forward mail from specific senders to a family member. They have to run server-side, because some must work while my PC is off, and I need to keep my own copy. Here's what I tried: - Change the rules to "on this computer only": bar stays - Change the rules from Forward to Redirect: bar stays - Disable the forwarding rules: bar goes, but so does the forwarding - Replace the Inbox rules with an Exchange mail flow (transport) rule: !!! bar goes, forwarding still works !!! The bar appears for any Inbox rule that forwards or redirects mail. A mail flow rule runs in Exchange Online before the message reaches my mailbox, and the bar trigger apparently doesn't look at it. Requirement: you need Exchange admin rights on your Microsoft 365 tenant. That's typically the case for small-business or custom-domain subscriptions where you're the admin. Home and Outlook.com accounts don't have mail flow rules. Steps (Exchange Online PowerShell) 1. Connect: Connect-ExchangeOnline -UserPrincipalName <your-address> 2. List your forwarding rules and their conditions: Get-InboxRule | ? {$_.ForwardTo -or $_.RedirectTo -or $_.ForwardAsAttachmentTo} | fl Name,Enabled,From,FromAddressContainsWords,SubjectContainsWords,RedirectTo,ForwardTo 3. Create one mail flow rule that covers them. Here the conditions are by sender, using regex patterns, and all patterns in the list are OR'd: New-TransportRule -Name 'Copy to Family' ` -SentTo '<your-address>' -FromAddressMatchesPatterns '@sender1\.com$','^alerts@sender2\.com$' ` -BlindCopyTo '<recipient-address>' -SentTo limits the rule to mail addressed to you. -BlindCopyTo delivers a copy that shows the original sender, like a redirect, and you keep the original. The Exchange admin center also has a GUI for this, under Mail flow → Rules. 4. Check the rule order: Get-TransportRule | ft Name,Priority,State,StopRuleProcessing If an existing rule above yours has StopRuleProcessing = True, yours will never run. A common example is a "bypass spam filtering" rule with no conditions. New rules are added at the bottom, so move yours up: Set-TransportRule 'Copy to Family' -Priority 0 5. Wait up to 30 minutes. A new or changed mail flow rule doesn't take effect right away. Then test by adding a temporary sender pattern, such as a personal address you can send from, and check the trace: Get-MessageTraceV2 -RecipientAddress '<recipient-address>' -StartDate (Get-Date).AddHours(-1) -EndDate (Get-Date) | ft Received,SenderAddress,Subject,Status -EndDate is required whenever you use -StartDate. Times are shown in UTC. Remove the test pattern afterwards with Set-TransportRule … -FromAddressMatchesPatterns …. 6. In classic Outlook, go to File → Manage Rules & Alerts, untick the old forwarding/redirect rules, click Apply, and restart Outlook. After the above, the bar was gone, the forwarding kept working, and my other rules, including "run a script" rules, were not affected. Tips - Before you change anything, back up your rules: Manage Rules & Alerts → Options → Export Rules. - Edit the Inbox rules in classic Outlook rather than Outlook on the web or PowerShell. Editing them elsewhere can remove client-only rules. - From now on, add or remove senders on the mail flow rule. Any new forwarding or redirect Inbox rule brings the bar back.464Views0likes0Comments