endpoint security
1127 TopicsIgnite 2026: What’s new in endpoint security
As more work happens in the browser, the browser has become a prime target for attackers. A fake CAPTCHA or a convincing error message persuades users to take an action that seems harmless, like running a command or approving a request. In these attacks, the user unknowingly carries the threat from the browser to the operating system. Once that happens, the attacker can install malware, steal credentials, or establish a foothold on the device. This sequence creates a practical challenge for defenders. Preventing breach at the time of execution is key, and at the same time security teams need confidence that protection is deployed, communicating, current, and functioning across all endpoints in the environment. At Microsoft Ignite 2026, Microsoft Defender is introducing protection designed to block some of the most prevalent browser-based attacks, and new capabilities to better and more easily manage the endpoint estate itself. Together, these updates connect two responsibilities that security teams often manage separately: stopping an attack when it becomes executable and continuously verifying that the protection layer is ready to respond. Protect against browser-based ClickFix attacks Today’s attacks often begin with a lure in the browser that leads to an attack on the endpoint. These attacks, called ClickFix attacks, accounted for 12.8% of all intrusions observed by Microsoft Defender between June 2025 and June 2026, with a 23x growth in volume seen between December 2025 and May 2026. Figure 1. Chart shows steep increase in unique devices per week running ClickFix attacks (source: 2026 Microsoft Digital Defense Report) Today, ClickFix attacks attempt to evade protection by targeting many different execution surfaces (command terminals, Windows Run, Windows Explorer, Common File dialogs, etc), complicating detection and blocking of attacks. With the introduction of the new clipboard monitor (DefenderSessionHelper.exe) Microsoft Defender now detects malicious commands copied from web content before they can reach Windows execution surfaces. Remediation of detections (clearing the malicious content from the clipboard) will break the attack chain before the lure becomes execution. Remediation is currently rolling out to all devices running Defender Antivirus and is slated to complete by year’s end. For customers who have deployed Microsoft Defender, security teams will be able to see relevant detections in the Defender portal and can further investigate any relevant activity in advanced hunting. Learn more about investigating alerts in the device timeline. Build more resilient endpoint security operations An endpoint can have the right policy on paper and still be exposed in practice. A device may be missing from the inventory, a sensor may have stopped communicating, an engine may be out of date, or an attack may reach an execution surface before the security team can respond. Across a large and varied estate, these conditions create an operational security problem as much as a detection problem. The new capabilities below strengthen that operational foundation. They help teams verify that protection is working, introduce changes safely, and manage devices through the full lifecycle. Monitor the health of every endpoint The new health dashboard in the Defender portal shows the health of your entire endpoint estate at a glance, across Defender components and platforms. It brings health signals into one place so security teams can quickly check that Defender is deployed, connected, up to date, and operating as expected across their endpoints. If they discover devices that need attention, they can move more quickly from visibility to troubleshooting. The dashboard unifies four key views: Inventory: onboarding status and the top operating systems and platforms in the environment Communication: devices that are active, inactive or have impaired communication with the cloud service Antivirus service health: antivirus running mode and quick and full scan outcomes Update status: security intelligence, engine, and platform, each shown as up to date, out of date, or unknown Teams can select any section to understand what a status means, explore a detailed breakdown, and open relevant remediation guidance. They can also view and export a complete list of affected devices. With a shared view of endpoint health, teams can be more confident that protection is deployed and working across the estate. This feature will be rolling out to public preview over the next few weeks. Control how security changes are rolled out Resilient endpoint operations also depend on introducing change safely. Security teams need to move quickly on critical updates and new capabilities while protecting mission-critical systems from avoidable disruption. Customers have asked for greater control over how Defender changes are introduced across their environments. That’s why we’re introducing new safe deployment settings that provide visibility and control over the rollout of security updates and product capabilities across Windows and Linux devices. This new experience allows security teams to validate, manage, and adopt security changes: Roll out updates progressively: New safe deployment channels allow organizations to progressively roll out Defender platform and engine updates. Teams can now validate changes on a smaller set of devices before expanding to production environments. This helps protect mission-critical systems from unexpected disruption. Adopt new security capabilities when the organization is ready: Administrators can selectively enable individual public preview features based on readiness, risk tolerance, and business requirements. Together, these controls help teams keep protection current while managing operational risk. They make continuous security innovation safer, more predictable, and easier to manage at enterprise scale. Learn more about safe deployment controls. Offboard devices easily to close security gaps Resilient operations require control across the full device lifecycle, including retirement. Last year at Ignite, we introduced the Defender deployment tool, a lightweight tool that dynamically adapts to the operating system, delivering healthy endpoint security to a diverse estate. But just as critical as onboarding is offboarding, because attackers often try to use offboarding scripts to switch off defenses, e.g. in Octo Tempest-style intrusions. Devices need to be retired deliberately, in a controlled and traceable way. That’s why we are introducing a new offboarding experience that is embedded in the Defender deployment tool for Windows and Linux. Administrators can generate an offboarding key or download an offboarding package, set a custom expiration, use unique keys, and track the resulting package. With time-bounded artifacts and package traceability, it makes offboarding a defined administrative action. Once the device is retired, teams can return to the health and inventory views with greater confidence that the estate reflects the population they are responsible for protecting. Learn more about simplified offboarding. Extend coverage to shared mobile devices Resilient endpoint security must extend across every device and work model in the estate. Today, we’re expanding Defender to support shared Android and iOS devices. Shared mobile devices are commonly used by frontline workers across industries such as retail, healthcare, logistics, and manufacturing, with multiple workers sharing the same organization owned device across shifts. With Defender, protection remains persistent at the device, independent of the user signed in. Support includes onboarding, risk evaluation, threat protection, and collection of security telemetry. Devices must be configured in Microsoft Entra shared device mode and managed through Microsoft Intune. Learn more about Defender-supported platforms and devices. Collect custom data for Linux file data & Windows registry data Even with strong preventive controls, resilient operations depend on having the evidence required to investigate and respond. Custom data collection in Microsoft Defender lets teams define additional endpoint events directly from the Defender portal without deploying a separate collection agent. This enables use cases including investigating what ran inside a script, monitoring new server-side scripts on web servers, or hunting command and control (C2) communications. Today we are announcing expanded custom data available to Linux file telemetry, including file created, deleted, and renamed. This is helpful for teams that want to watch web folders and scheduled-job folders on Linux servers. We're also adding Windows registry events, including when keys are created, deleted, renamed or queried, and when values are set. These features will be available in Public Preview on December 9, 2026. Learn more about custom data collection. Endpoint resilience depends on prevention and operational control Endpoint attacks and endpoint operations converge on the same question: Is protection present, healthy, and able to act when an attack reaches the device? The new capabilities announced today ensure that organizations have the latest protections in place and provide security teams with insights and controls over managing security on their endpoints effectively. As these capabilities reach your tenant, review your estate health, and define whether a staged deployment path for Defender changes is right for your rollout strategy. See what's new in Microsoft Defender Join us November 17–20 in San Francisco or online for deep dives and practical labs to help you maximize your Microsoft Defender investments and to get more from the Microsoft capabilities you already use. Featured Ignite sessions: KEY01: Microsoft Ignite opening keynote BRK324: The Alert Is Dead. The Blueprint for the Agentic SOC BRK333: How Threat Research Powers Attack Disruption in the AI Era BRK334: Modern Phishing Doesn't End at the Click BRK320: Agentic Security Unfiltered with Allie Mellen: Hype vs. Reality BRK340: A Zero Trust approach to securing AI runtime with Microsoft Defender308Views0likes0CommentsA guide to governing local AI agents with Intune
Local AI agents are becoming part of everyday work. Employees may use them on managed devices to access repositories, analyze files, automate tasks, or interact with external services. IT needs to understand which agents are present, decide how to handle them, and apply controls that match their approved use. Our Ignite 2026 roundup of what's new in Microsoft Intune introduced new controls for agent governance and containment on managed devices. This hands-on follow-up explains how to put them to work. No single control fits every agent or task. Coverage depends on the agent, host app, platform, and available signals. As always, test policies to understand behavior before deploying broadly. Discover local agents and decide what is allowed Microsoft Agent 365 combines available inventory and runtime signals from Microsoft Defender, Intune, and Microsoft Entra to help IT identify supported local AI agents on Windows devices. Intune’s application inventory can help IT identify how and where discovered agents are installed. Admins can create a configuration profile that specifies which app inventory properties to collect and assign it to device or user groups. App inventory collects registered Win32 and Windows Store apps from Windows 10/11 devices that are Intune enrolled and Entra joined. For an unwanted agent or app, note the Platform-specific app ID attribute. This is the MSI product code for Win32 apps or the package full name for Store apps. Admins can use this value to enable restrictions with a software compliance policy. Local AI agents do not always map one-to-one with a host app. Currently, only host apps installed as Win32 or Windows Store apps appear in Intune’s app inventory. Govern agent access to company resources Intune software compliance policy, available in public preview, can help restrict device access to protected company resources when a specified unwanted application is detected and applicable Conditional Access requirements are configured. Software compliance evaluates installed apps by supported identifiers, not agent identifiers directly. Agents with multiple supported host apps may need multiple restricted software entries. Review these relationships before assigning the policy. In this preview, editor extensions, npm packages, and standalone executables aren't available to select. Using the MSI product code or package full name of an unwanted app: Create a software compliance policy in the Intune console Add the app’s identifier as a restricted software entry Assign the policy to a device or user group Ensure a Conditional Access policy is configured to require that devices are compliant to access corporate resources Once deployed, Intune marks targeted devices non-compliant if restricted software is found, allowing Conditional Access to block access to protected corporate resources across the entire device, even while the agent is inactive. After uninstalling the software, employees can immediately request a compliance check; once Intune confirms compliance with applicable requirements, access can be restored according to the organization’s Conditional Access policies. To provide instructions for the employee, admins can create a custom message explaining why the device is out of compliance and how to fix it. The IT team can then use reporting to see which devices still need attention and adjust the policy as needs change. Configure App Protection Policies for supported AI apps on mobile platforms App protection policies help control how work data is accessed and transferred within supported AI apps on iOS/iPadOS and Android, with or without device enrollment. Supported AI applications, including eligible offerings from Microsoft and third-party developers, can integrate with Intune app protection policies through the Intune App SDK. To get started: Check the Microsoft Intune protected apps list, the Apple App Store, or Google Play to confirm which AI apps support Intune app protection policies. Create or update an app protection policy for iOS/iPadOS and Android that includes those apps. Configure data protection settings, such as limiting cut, copy, and paste and saving to personal storage, and access requirements such as a PIN. Add conditional launch checks, then assign the policy to the user groups that use those apps. Set boundaries for what agents can do An agent may be approved for a task without needing access to everything on the device. Set guardrails for approved agents with MXC Microsoft Execution Containers (MXC), now generally available on Windows 11, lets developers run each agent task inside a policy-driven execution boundary. Windows enforces the configured execution boundary independently of the agent, helping prevent supported agents and their generated code from exceeding the permissions established for the container. Developers choose how to contain their agents; IT sets the guardrails through the new agent containment policy in Intune. On managed Windows devices, this policy defines the most an MXC-enabled agent can do. Setting the guardrails takes three steps: Define the ceiling in the Intune admin center under Endpoint security, in Agent containment. Configure folder access as deny, read-only, or read-write. Decide whether the agent gets network access, such as local loopback or external connections. Target the policy to all known MXC-enabled agents, or to a specific supported agent. When an agent asks Windows to create a container, Windows compares the request with the Intune ceiling. Requests within the ceiling are granted. Requests that exceed it are denied, and the agent gets enough information back to adjust. For example, IT might allow an agent to work in a project repository while denying access to a credentials folder. Initial coverage includes process containers and MXC-enabled agents that Microsoft Defender identifies, beginning with GitHub Copilot CLI and OpenAI Codex CLI. Secure Cloud PCs that run agents with the Windows 365 for Agents security baseline The Windows 365 for Agents security baseline provides Microsoft-recommended device security settings for agent Cloud PCs. Protections apply as soon as a Cloud PC is provisioned and enrolled in Intune, before the agent signs in and starts working. The baseline provides Microsoft-recommended settings for Windows 11, Microsoft Edge, and Microsoft Defender for Endpoint, covering Defender Antivirus, Defender Firewall, attack surface reduction, credential protection, browser security, and OS hardening. In the Intune admin center, go to Endpoint security > Security baselines and select Windows 365 for Agents Security Baseline. Review and adjust the default settings. Assign the profile to the device groups that contain the agent Cloud PCs. Restrict unneeded agent runtimes on Windows devices. Limit unused AI runtimes Many local AI agents rely on runtime environments like Node.js or Windows Subsystem for Linux (WSL). On Windows devices where these runtimes aren't needed, the Local AI Agent Baseline - OpenClaw (Preview), introduced in May 2026, can help disable or restrict them. It configures Windows Subsystem for Linux (WSL) settings and adds two firewall rules that block outbound TCP connections from Node.js executables. Test the baseline configuration before deployment. Disabling WSL or blocking Node.js network traffic may impact more than OpenClaw and could be disruptive for employees who use these runtimes. To deploy it in the Intune admin center: Go to Endpoint security > Security baselines, select Local AI Agent Baseline - OpenClaw (Preview), and create a profile. Review each setting and turn off any that would disrupt legitimate work, such as on developer devices that rely on Node.js or WSL. Assign the profile to a pilot group first, then expand. Govern agent runtime Intune can restrict agent execution on supported Macs and enable runtime protections for supported agents on Windows. Govern local agents and block unwanted binaries on macOS devices On supervised Macs running macOS 27 or later, Allowed Binaries and Denied Binaries control which apps and command-line tools can execute. For approved agents that support managed configuration, Intune can deliver policies governing tool permissions, MCP connections, approval requirements, and supported sandbox settings. Applicable macOS privacy controls provide another layer around access to sensitive data and device capabilities. The new app privacy permission defaults streamline consent, but they are not enforced restrictions. For customers using Microsoft Entra Internet Access, Global Secure Access adds outbound network controls. Intune can deploy and configure the Mac client, while Entra policies restrict destinations for traffic routed through the service. Customers should configure traffic acquisition, bypass rules, and connection-failure behavior to match their security requirements. These controls do not create a universal containment boundary around every agent or integration: coverage depends on the agent’s supported policies, its execution environment, and the traffic captured for enforcement. Enable AI agent runtime protections on Windows Use Intune to enable Microsoft Defender AI agent runtime protections on managed Windows devices. For supported agents and event interfaces, such as Claude Code, Codex CLI, and GitHub Copilot CLI, Defender inspects designated interaction points to help identify prompt injection attempts. It can also block certain detected high-risk actions before execution. Before starting, confirm that the organization has a Microsoft Defender for Endpoint Plan 2, Microsoft 365 E5, Microsoft Agent 365, or Microsoft 365 E7 license. Devices need to be onboarded to Defender for Endpoint. Microsoft Defender Antivirus needs to be in active mode, with real-time protection turned on. Admins can follow these steps: In the Intune admin center, go to Endpoint security > Antivirus and select ‘Create policy’. For Platform, select Windows. For Profile, select Microsoft Defender AI agent runtime protection. Set AI Agent Protection to Audit and assign the policy to a small group of devices where supported agents are actively used. Review detections in the Microsoft Defender portal for one to two weeks. In audit mode, informational alerts show what would have been blocked. When the detections look accurate, change the setting to Block for the device groups where enforcement is required. Confirm the effective setting on the device page in the Defender portal, then run the AI agent runtime protection demonstration on a test device. With runtime protection enabled in block mode, employees can continue using supported agents, although certain detected requests or actions may be blocked according to the configured protection settings. When Defender detects a prompt injection attempt inside a prompt or tool response, it can block the request before the agent acts. In Claude Code, the employee sees a Microsoft Defender block message and a Windows notification. The detection appears in Windows Security under Protection history. The security team sees a Suspicious AI prompt injection alert in the Defender portal. Get started in five steps Choose the controls that apply to the devices and agents. This checklist follows the post's structure rather than a required deployment sequence. Use app and local AI agent inventory in Intune, along with Defender and Agent 365 discovery. Use software compliance policies with Conditional Access to block access to company resources until compliance is restored. Protect work data with app protection policies for supported AI apps built with the Intune App SDK. Preview the agent containment policy for MXC-enabled agents. Ask agent vendors to support MXC and expose settings IT can manage. For agents running in Windows 365 for Agents Cloud PCs, deploy the Windows 365 for Agents security baseline. Deploy the Local AI Agent security baseline on Windows devices where agent runtimes aren't needed. On managed macOS devices, use denied binaries to block unwanted agents. Deploy configurations and enable network settings for approved agents. Plan your organizations software compliance pilot With software compliance in preview, start with a small group of Windows devices. Before expanding assignments, validate host-app detection, the resulting compliance state, and how configured Conditional Access policies restrict and restore access. Agree how endpoint and security teams will handle findings and exceptions. For the broader agent security story, read Ignite Security Blog and the Securing the agentic insider blog. Watch these on-demand Microsoft Ignite sessions on the capabilities covered here: Manage and Govern AI Agents on Windows as Your Trusted Execution Layer (BRK391) From AI Pilot to Practice: Scale Securely with Windows (BRK406) Local agents are here. Can you find and secure them? (BRK339) Stay up to date! Bookmark the Microsoft Intune Blog and Intune Customer Success Blog and follow us on LinkedIn or @MSIntune and @IntuneSuppTeam on X to continue the conversation.156Views0likes0Comments
Microsoft Perception helps IT drive outcomes and scale
Attackers now move in hours. The Microsoft Digital Defense Report 2026 notes that new vulnerabilities can be weaponized in under a day, and roughly 40,000 CVEs were published in the first half of 2026 alone, a pace on track to roughly double. Unpatched vulnerabilities can leave organizations exposed, making timely identification, prioritization, and remediation essential to endpoint security. Security teams often focus on identifying and prioritizing risk, while IT teams manage the deployment of fixes across devices. IT teams roll out fixes at scale but need the context for which risks matter most. The workflows between these two teams are often fragmented across tickets and manual handoffs. And yet, IT is increasingly being asked to protect more: more devices, more apps, and now AI agents. As Hayete Gallot, Executive Vice President of Microsoft Security, wrote when introducing Project Perception, "approaches built for a world of human actors cannot keep pace" with AI, agents, and machine-speed attacks. At Microsoft Ignite, we are introducing Microsoft Perception capabilities specifically for IT in Microsoft Intune to help teams scale to meet this expanding set of responsibilities. These capabilities shift IT from chasing tickets and reconciling lists to reviewing plans, approving change, and proving outcomes. What Microsoft Perception means for IT Microsoft Perception is an agentic security system in which red, blue, and green team agents drive security outcomes across the security lifecycle, with humans in the loop. In October, we extended Perception to secure the agentic insider specialized agents. Perception and Microsoft Agent 365 now share a unified agent registry, giving IT and security a consistent view of agents and risk. We now expand the power of Perception to IT. Perception connects critical workflows and closes the gap between security teams that prioritize risk and IT teams that deploy change. For IT pros, Perception brings three connected capabilities into Intune: Plain language exploration converts tenant endpoint data into actionable insights conversationally – no multi-step queries and cross exports needed. The Vulnerability Remediation Agent in Intune turns prioritized risk into exposure reduction plans ready for approval. Custom reports track progress and verify outcomes in a repeatable manner. By bringing shared security context and a path to remediation directly into Intune, these capabilities help IT meet expanding responsibilities, prioritize fixes, and move faster from understanding risk to acting on it. With fewer disconnected steps between security and IT, teams can shift from chasing tickets to reviewing plans, approving change, and proving outcomes. Putting shared security context and a path to remediation directly into Intune helps to move from understanding which risks matter most to acting on them faster, with fewer disconnected steps between security and IT. Get actionable insights: Ask, and get the deeper data story It is now incredibly easy to ask deep questions that would otherwise require hand stitching exports. Just ask, “Which non-compliant devices on each OS version have not checked in during the last 30 days?” or “Which devices are still running a vulnerable app version or are missing the latest security update?” Perception returns a table, shows how it arrived at the results, and flags when results are partial. Simply open Perception in the Intune admin center, begin a new chat, and describe the required outcome. Perception writes and runs the queries, combines results across data sources, and explains each step with citations. Review the queries behind the answer without having to write them or look up an API. To act, add the affected devices or users to a new or existing group and follow through with familiar Intune tools. Data exploration and actions runs as you: you see only the data your role-based permissions allow you to access and act on. Better AI answers also depend on better data. Intune platform improvements are moving device data closer to near real time, with faster app inventory and policy reporting on Windows giving Perception a more current picture of your environment to reason from. More current device data can help to provide insights based on recent information, while timestamps show how current is the underlying data. See risk the way Security sees it In Microsoft Defender, Perception green team agents produce the risk prioritization that tells teams what to fix first. Those rankings and their reasoning aren't locked in another team's console. IT administrators with access to Perception in Microsoft Defender can also review these risk prioritizations and their supporting context. The Posture Prioritization Agent, now generally available, scores each exposure on likelihood, potential impact, asset criticality, exploitability, reachability, and how many resources are affected. It looks for single fixes that reduce risk across several assets, and for each item it explains why it matters and which critical assets are involved. The Risk Reduction Agent, in public preview, puts that analysis into action through the Reduce exposure risk playbook. When a permanent fix is ready, it coordinates patching through Intune while IT keeps control of deployment. When patching isn't immediately possible, it can shield the vulnerability with targeted, temporary protection, then track progress toward closure. Risk scoring now extends to agents, too. Many agents run on endpoints IT manages, contained by controls IT owns, such as execution containers and software compliance policies in Intune. Dynamic Agent Risk combines signals from identity, data, endpoints, cloud, network, runtime, and the agent’s own activity. It scores how securely each agent is configured, what it can reach, its potential impact if something goes wrong, and whether its actions are drifting from the intent of its task. The score updates as behavior changes rather than being set once at onboarding. When an agent’s risk rises, IT can see why and tighten those controls instead of waiting on a ticket from the SOC. Whether the risk is a vulnerable app or a drifting agent, admins arrive in Intune knowing which fix matters most. Act intelligently: the Vulnerability Remediation Agent The Vulnerability Remediation Agent in Intune combines Microsoft Defender vulnerability intelligence with Intune device and app context to build prioritized, tenant-specific remediation plans. For every plan, the agent weighs severity and exploit likelihood, and classifies each fix as either an OS update or an app update. OS updates can be expedited at any time; app updates are matched to managed, catalog, or WinGet apps. The agent ranks plans with reasoning. Rather than handing IT a list of CVEs, it focuses on the most impactful vulnerability reduction recommendations. Each recommendation is centered on an action, and one remediation action may address multiple CVEs across affected devices. One agent, two ways in As a standalone agent in Intune, the vulnerability reduction agent gives IT an independent path to act on risk. Admins can review prioritized Defender recommendations, generate remediation plans, and execute them in a single pane, without waiting for a request from the security team. When a broader initiative flags a critical OS update, that fix surfaces as a priority the next time the admin runs the agent. The agent also works hand in hand with the Risk Reduction Agent from Perception in Defender. When the Risk Reduction Agent identifies an app or OS vulnerability that needs remediation, IT can run the Vulnerability Remediation Agent in Intune. It combines that context and priority with the tenant’s Intune environment to build a specific, actionable plan grounded in the organization’s device state. IT receives the plan ready for review before any action is taken. Agentic, but governed Faster remediation must be balanced with IT oversight. The agent proposes remediation plans, while administrators retain control over deployment decisions. Admins review and can change every target, exclusion, and safeguard, and nothing runs without a human decision. Approved plans roll out through deployment rings, starting with a ring 0 pilot with success thresholds before moving to ring 1. Admins can act only on devices within their role and scope tags. Every run is logged, including agent activity, run results, and when each suggestion was applied. Turn answers into proof with custom reports An answer is useful once. A report is useful every day. When an investigation is worth repeating, it can be saved as a custom report, with data views and advanced visualizations in one place. The report keeps the recipe behind the answer: the queries, API calls, and analysis steps. Each time it is opened from Custom reports in the Perception pane, it automatically reruns that recipe on the latest data and displays the results. Cards can be added to place related views side by side, such as devices by platform and by OS version. That turns one-off investigations into repeatable checkpoints. A Windows upgrade report refreshes and older versions phase out. A remediation rollout report monitors key insights and helps administrators monitor deployment progress, changes in exposure, and understand which devices have received fixes. Custom reports help IT support deceisions with current, traceable data. How Perception in Intune changes IT work IT scales to meet expanding responsibilities. As IT takes responsibility for more devices, apps, agents, and containers, these capabilities connect the work of finding, prioritizing, addressing, and verifying exposure. Data exploration scopes exposure without exports, risk scores identify the most important fix, the Vulnerability Remediation Agent turns that priority into a plan to close CVEs, and shielding covers vulnerabilities that cannot yet be patched. Custom reports confirm that exposure has closed, helping teams extend their reach across the environment. Prioritize remediation with greater context. Prioritized recommendations put the most important fix first, one action can close several CVEs, and tenant-specific plans move straight from insight to deployment. The work itself changes. IT moves from chasing tickets and reconciling lists to reviewing plans, approving change, and proving outcomes. Security and IT share context, scope, and accountability in one connected workflow, while safe ring-based rollouts keep users productive. AI should do more than provide answers. It should help IT teams turn security insights into informed remediation decisions and measurable progress. Get started Microsoft Perception in Intune, including data exploration, custom reports, and the Vulnerability Remediation Agent, is available in public preview for Intune customers onboarded to Microsoft Perception. If you already use Microsoft Perception, reach out to your account representative to connect with the Intune team. If you are not yet a Perception customer, express your interest in the Intune public preview at aka.ms/IntunePerceptionPreview, and we will reach out if we are able to onboard you. To learn more about Microsoft Perception: What's new with Microsoft Perception at Ignite 2026. To see it in action at Microsoft Ignite, join these sessions: Code Session BRK404 What’s New in Intune: Secure, Patch, and Scale BRK328 What’s New in Intune: Trusted device and app foundation for AI BRK322 Stay ahead of endpoint risk with AI-powered discovery and remediation BRK391 Manage and Govern AI Agents on Windows as Your Trusted Execution Layer BRK405 Trust, Enforced: How Windows delivers security for the AI era BRK339 Local agents are here. Can you find and secure them? BRK323 Project Perception Roadmap: New Capabilities, Use Cases & What's Next Stay up to date! Bookmark the Microsoft Intune Blog and Intune Customer Success Blog and follow us on LinkedIn or @MSIntune and @IntuneSuppTeam on X to continue the conversation.120Views0likes0Comments
Defender XDR: Tables not supported for table management
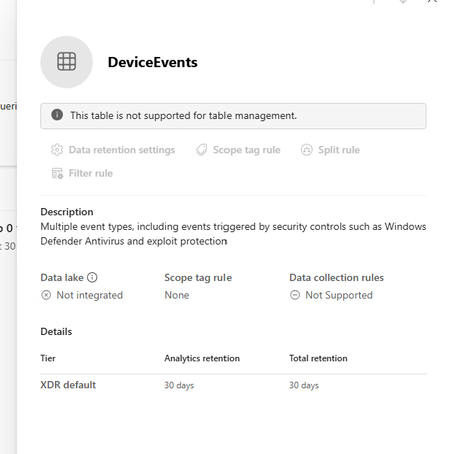
I am trying to extend the table retention of specific tables to allow them to flow to Sentinel Analytics but keep getting the message "This table is not supported for table management" in the Sentinel > Configuration > Tables page. The Sentinel workspace is connected in System > Settings > Microsoft Sentinel. I can see the table type is XDR in the list which seems to be the reason why it can't be managed. Any ideas why this table is not able to be managed.656Views0likes2CommentsThe CISO Cheat Sheet to Microsoft Digital Defense Report 2026
I know we’re all busy, so I’ve pulled the most important data from this year’s Microsoft Digital Defense Report into one short read. The full report is well worth exploring, but this article focuses on the numbers and trends most relevant to security leaders. This year’s edition shows that AI is lowering the time, expertise and cost required to discover and exploit weaknesses, enabling attackers to operate with greater speed, scale and autonomy. The report describes this as AI “changing the physics of cybersecurity”: attack timelines are compressing and agentic systems are beginning to automate more of the attack lifecycle. Trend 1: Time has collapsed The clearest finding is about speed. Vulnerability discovery is increasingly running ahead of remediation, while the time from discovery to weaponisation is shrinking. In the AI era, weaponisation can follow in hours. Vulnerability discovery and weaponisation now often needs only a well-written prompt. The median time from discovery in the wild to weaponisation is below 24 hours. Vulnerabilities were on track for a record estimated 72,000 CVEs in 2026. The report expects a multi-year period in which the number of known but unpatched vulnerabilities rises sharply before eventually declining. The median time from container start to first exploit attempt is 5.3 hours. The ransomware actor Storm-1175 moved from web-facing exploitation to deploying Medusa ransomware in as little as 24 hours. CISA added over 110 CVEs to its Known Exploited Vulnerabilities catalogue between November 2025 and May 2026, most within a week of disclosure. The mismatch with enterprise reality is the uncomfortable part. The report says the disclosure-to-exploitation window has shrunk to single-digit days. Between November 2025 and May 2026, CISA added more than 110 vulnerabilities to its Known Exploited Vulnerabilities catalogue, most within a week of disclosure. In one example, Storm-1175 moved from exploiting a web-facing vulnerability to deploying Medusa ransomware in as little as 24 hours. Microsoft’s Red Team makes an important point: a patch is also a disclosure. Every fix points attackers towards the flaw it closes. As AI-assisted analysis makes reversing patches faster and more reliable, the report argues that patch velocity, not simply patch availability, becomes the control that matters. Trend 2: Attack chains are gaining autonomy The report charts a clear progression: September–November 2025: AI assists in orchestrating a campaign, as in the Anthropic-reported espionage case. April–June 2026: Full-chain autonomy is demonstrated in labs. July 2026: Real-world autonomous attacks of increasing complexity appear. Two frontier models, Mythos and GPT-5.5, completed a 32-step attack chain against an emulated enterprise with no human help. The test environment had no defenders. The UK AI Security Institute reached a similar finding independently. GPT-5.5 was the second model to solve its end-to-end corporate network attack simulation, a task AISI estimates would take a human about 20 hours. Open-weight models lag closed models at orchestrating attacks by about seven months. In the wild, early July 2026 saw the first documented automated ransomware extortion attack, named JADEPUFFER by Sysdig. Microsoft has seen AI-orchestrated intrusions that share elements with it. Initial access consistently came from internet-exposed services running known-vulnerable software. The report is measured on this point. Volumes of AI-orchestrated activity remain low. In most observed real-world operations, complex end-to-end intrusions still retain meaningful human direction. The Red Team's framing is the most useful one: AI doesn't create a new class of attack, it collapses the effort needed to find and exploit existing attack paths. Trend 3: AI has become an attack surface The report's second takeaway is that attackers are already targeting AI itself. The adoption numbers explain why. 88% of enterprises are experimenting with agents, and 82% of leaders plan broader rollouts within 12–18 months. The report cites industry projections of roughly 1.3 billion agents in production by 2028. What attackers are doing to AI systems: Four techniques accounted for roughly 90% of observed attack activity in telemetry from Azure AI workloads: malicious link injection (52%), jailbreaks (16%), tool and agent abuse (12%), and identity and credential abuse (10%). Memory poisoning: An attacker who can place content anywhere an agent reads can often place it where the agent remembers. Email is the dominant pathway the Red Team has observed. Human-in-the-loop isn't a complete control: Red team testing saw approval prompts ignored, or bypassed by a policy stored in poisoned memory. Developer tools turned against their owners: The "s1ngularity" malware hijacked locally installed AI command-line tools to hunt for secrets. It leaked about 2,000 secrets and 20,000 files across 225 victims. AI browsers: In daily use at more than 40% of organisations in Microsoft's dataset, they were the initial infection vector in incidents involving 57 malware families in a May 2026 analysis. Chat histories as a target: Malicious AI-assistant extensions reached nearly 900,000 installs and more than 20,000 enterprise tenants, harvesting AI chat histories that often contain code, architecture and credentials. The identity implications are direct. Each agent needs its own identity, not one borrowed from an employee, and a named human sponsor. The report also treats revocation latency, the time to cut off a compromised agent, as a measured outcome. Trend 4: The front door is still identity AI changes the speed and personalisation of social engineering. It hasn't changed where attacks start. Initial access in Defender Experts data: User execution: 30% Valid accounts: 20% Malicious copy-and-paste: 13% Phishing: 11% Together, user execution and valid accounts account for over half of observed activity. In incident response engagements, phishing as an initial access vector jumped from 7% to 23% year on year. The standout numbers: ClickFix: Defender saw user-pasted malicious commands on more than 1.1 million unique devices between February and early May 2026, roughly an 8x increase. AiTM: URLs accounted for 45% of the identified phishing techniques in the report’s breakdown. Separately, the share of AiTM phishing and token-theft attacks more than doubled during the first six months of 2026, although the report notes that their overall share remained comparatively small. Teams vishing: Weekly confirmed malicious volume increased 502% year on year. Per attempt, 48% of vishing calls kept the victim engaged for more than 20 seconds, and 30% lasted more than one minute. When a call succeeds, attackers can persuade the victim to install a remote-management tool and complete reconnaissance in two minutes or less. Business contact impersonation (BCI): The report introduces this term for conversations that start with a trusted-looking contact. Microsoft detected more than 46 million attacks in 12 months, with a 121% spike in April 2026. The share of first-contact messages that explicitly asked for money or documents fell from 17% to 3%. The first message is deliberately bland, like "Are you at your desk?" Password attacks declined 26% year on year, which the report describes as strong evidence that MFA and passkeys are forcing attackers to pivot. That pivot includes techniques such as fatigue attacks, AiTM phishing and token theft designed to circumvent conventional MFA. Trend 5: Attackers are inheriting trust rather than breaking in The report's headline theme is that risk is increasingly interconnected. Threats travel through the trusted relationships between identities, software supply chains, partners and cloud platforms. The numbers: Supply chain: Major open-source ecosystems saw attacks roughly every ten days, accelerating through Q2 2026. Shai-Hulud 2.0 affected 25,000 repositories. Megalodon backdoored 5,561 GitHub repositories in under six hours. Trusted signing: In May 2026, Microsoft disrupted Fox Tempest, a "malware-signing-as-a-service" operation that obtained genuine certificates for ransomware loaders and infostealers. Microsoft revoked over a thousand fraudulent code-signing certificates. Legitimate access: An unsanctioned remote monitoring tool is now one of the most reliable mid-stage indicators of a human-operated intrusion. Cloud identity: Cloud identity abuse was the most observed technique against critical infrastructure, representing 78% of the technique mix in Microsoft’s data for March to June 2026. Hybrid intrusions: The Storm-2885 case showed an attacker using a privileged cloud identity to close and downgrade security alerts. The report says identity governance and alert-handling workflows deserve Tier 0 treatment. Dwell time: DART data shows a statistically significant increase in dwell time year on year, meaning organisations took longer to detect intrusions. Ransomware shows the same ecosystem pattern. Qilin led leak-site data with 16.4% of victims, up 386%. Defender detections tell a different story, with Akira at 22%. Trend 6: Defence works best when it's connected The report is not only a catalogue of threats. The strongest defensive evidence: Disruption works. Following the March 2026 disruption, Tycoon2FA activity had fallen 95% from its November 2025 peak by June. Its share of CAPTCHA-gated phishing declined from 76% in December 2025 to 12% in June 2026. Correlation is the highest-leverage variable. The report argues that how well defenders share and correlate signals across endpoint, identity, cloud, email and network is one of the highest-leverage strategic variables under their control. AI is also changing defensive operations. The report describes AI-assisted triage, incident summarisation, hunting-query generation and detection engineering as ways to accelerate investigations and allow analysts to concentrate on higher-value work. Automated disruption can compress response time. The report says that when a correlated incident reaches a defined confidence threshold, defensive systems can automatically isolate devices, disable compromised accounts, revoke sessions or quarantine affected cloud resources. It also stresses the importance of appropriate governance and human oversight for high-risk AI actions. The report also recommends changing what leaders measure. It suggests moving from patches deployed to exposure reduced, detection coverage increased and time-to-mitigate compressed. What the MDDR recommends: ten security priorities The report starts its recommendations with the foundations: Secure by Design, Secure by Default and Secure Operations, applied through identity-centric Zero Trust. Microsoft says these keep the priorities below durable as AI adds more identities, applications, agents and dependencies to govern. Govern cyber risk at leadership level. Report identity exposure, patch latency, agent permissions, critical dependencies, dwell time and recovery readiness to the board. Defend identity as the primary control plane. Deploy passkeys and phishing-resistant MFA, reduce privilege and govern human and non-human identities. Invalidate and rotate tokens and session credentials quickly. Establish governance, visibility and data controls for AI. Keep visibility of approved AI tools, services and agents, and monitor for unauthorised or unmanaged use. Apply sensitivity-aware access and data protection to the data those systems can reach. Reduce exposure and edge risk. Continuously discover internet-facing assets and patch edge devices quickly. Centralise high-fidelity logging, enforce strong authentication and combine network visibility with threat intelligence. Focus on cross-signal correlation. Correlate endpoint, identity, cloud, application, email and network signals to detect intrusions earlier. Correlation also helps defenders anticipate attack paths and likely targets. Enact a continuous threat and vulnerability management model. Combine asset visibility, vulnerability identification, threat detection and AI-accelerated insight into a single continuous programme. Validate exposure through proactive testing. Run assume-breach exercises on cloud services, SaaS platforms, APIs and workflow automation. Prioritise them by where your highest-value data is stored, accessed or aggregated. Secure software dependencies. Harden software installation, keep a software inventory and validate provenance. Monitor packages and prepare for rapid containment. Participate in collective defence. Share actionable threat indicators and victim-informed intelligence with trusted partners and law enforcement. This supports coordinated tracking, investigation and disruption. Prepare for long-horizon technology transitions. Build a cryptographic inventory and advance post-quantum planning alongside AI governance. Read together, the numbers tell one story: the attacker’s workflow is becoming faster and less expensive. AI can shorten vulnerability discovery, exploitation, secret discovery and lateral movement, while organisations still face the slower operational work of testing, coordinating and deploying safe changes across complex environments. At the same time, agent identities can proliferate faster than organisations can inventory, govern and revoke them The defining question for boards today is not whether disruption will occur, but whether the organization can continue operating, contain harm, recover quickly, and maintain trust when it does. Source: Microsoft Digital Defense Report 2026, Version 1.1. Reporting period: July 2025–June 2026.
Bitlocker TPM+PIN - Safety only when TPM is safe?
Hello, i habe read the microsoft docs about Bitlocker on Windows 11. At the moment i understand, that the feature TPM+PIN ask for a PIN at startup. From the PIN Bitlocker creates a SHA-256 Hash and use only 160Bit for Authentication with the TPM. Are the PCR Register and the PIN is correct, the TPM give Bitlocker the Authenticationcode free and Bitlocker can unecrypt der Disk. The safety of this require the safety from the TPM. Is the safety of the TPM compromised, than Bitlocker is unsafe, too. Knowledge of the PIN can be unnecessary. Why Bitlocker don’t use the 96bit from the Hash, strechted the 96 Bit with a salt (saved on the unencrypted disk space), use a cryptographic safe hash function (e.g. Argon2id) and use this hash XOR with the TPM set free Authenticationcode as key for the master key? Steps: PIN from user -> SHA-256 -> 160 bit for TPM S1 and 96Bit for the second half of the master key. -> Argon2id( 96bit ) S2 -> S1 XOR S2 -> Master key. Pro: If someone can crack the TPM the attacker has only the half of the Masterkey. Cons: little more calculation steps. This make the safety better, because it need knowledge and hardware security. What do you think about it? Sincerely yours, ElGuy139Views0likes1Comment
Microsoft Defender AMSI false positive — private evidence submission guidance
We're seeking guidance on the official private review process for a suspected Microsoft Defender Antivirus AMSI false-positive detection. Detection: HackTool:PowerShell/ApexToolkit.A The detection occurred during an authorized PowerShell-based .NET development/testing workflow. The original AMSI payload is unavailable. We've collected the official Microsoft Defender diagnostic CAB, but it contains personal and internal system information, along with unrelated security history. Microsoft Support referred us to Tech Community because the consumer support channel could not escalate the investigation directly. Our question: Is there an official private channel for submitting sanitized incident records for initial classification review, or obtaining guidance about secure handling of the full diagnostic CAB? We want to maintain Defender protections and avoid posting sensitive diagnostic evidence publicly. Thank you for any guidance on the appropriate Microsoft review process.210Views0likes1Comment
Defending Linux in the age of AI-operated attacks
Linux supports cloud services, containers, developer environments, business-critical applications, and a growing share of AI infrastructure. That makes Linux both essential to modern enterprises and increasingly attractive to attackers. AI is compressing the time required to research targets, vary payloads, and adapt when an attempt fails. Customers need protection that can recognize modern attacker behavior at runtime, continuously test effectiveness against realistic attacks, and learn and evolve with the threat landscape. That’s why Microsoft Defender is focused on three priorities for Linux: stronger runtime protection for fileless and in-memory attacks, continuous validation that proves protection remains effective, and AI-powered defense that can help security teams simulate attacks, investigate threats, close protection gaps, and reduce exploitable paths before compromise. A new Linux threat model The threat landscape has evolved from AI-assisted attacks, where people use AI to accelerate individual tasks, to AI-operated attacks, where AI coordinates more of the attack chain, and now it is moving to autonomous AI attacks that can adapt and act with limited human direction. Modern Linux attacks rarely depend on one file; they combine exposed services, stolen credentials, legitimate administration tools, scripts, containers, and cloud-native attack paths. As AI helps attackers generate and modify payloads at scale, adapt when an attempt fails, and move through the attack chain faster, defenders can no longer assume that every payload, script, or binary will resemble something they have seen before. Microsoft Security Research recently observed compromises involving a LiteLLM gateway, a RAGFlow deployment, and a Kestra workflow environment. The intrusion paths differed, but the objectives converged around credential theft, persistence, downstream access, and compute monetization. The broader lesson is that AI gateways, retrieval platforms, and orchestration services are becoming high-value control points where data, credentials, model connectivity, and workload execution meet. These examples also highlight a broader shift: attackers increasingly abuse legitimate services, tools, and workflows rather than relying solely on overtly malicious binaries. Viewed one event at a time, Bash, Python, curl, SSH, and network connections can appear legitimate. The security challenge is to understand their sequence, process relationships, destinations, and runtime context. That is why Linux protection in Defender is grounded in recognizing attacker behavior, not just known files. Behavior-based runtime protection for modern attacks Defender brings together next-generation protection, endpoint detection and response (EDR), vulnerability management, advanced hunting, investigation, and response to provide protection and visibility across the attack lifecycle. Behavioral protection evaluates process relationships, command lines, scripts, and runtime activity to identify malicious execution based on what is happening on the device. This is particularly valuable when attackers use legitimate tools or changing payloads that may not appear suspicious in isolation. Targeted memory inspection, now in public preview, extends protection to supported threats that operate in memory and may leave limited evidence on disk. Defender uses runtime behavior to focus inspection on relevant processes and execution activity. By concentrating inspection where suspicious behavior is observed, Defender delivers in-memory protection while minimizing unnecessary scanning and associated performance overhead. Consider an attacker who gains access through an exposed Linux application, executes commands, moves malicious activity into memory, launches additional processes, and connects to attacker-controlled infrastructure. Defender creates opportunities to block the attack, detect suspicious runtime activity, correlate related signals, and disrupt further impact. These are not isolated protection points. Different layers of Defender work together to build one complete picture as an attack progresses. Changing a payload or technique does not remove the behavioral, process, memory, and network signals that can expose malicious activity. From malicious activity to an actionable incident Defender protection on Linux executes a four-step process: block malicious behavior, detect suspicious runtime activity, correlate related signals into an incident, and disrupt the attack before it causes further impact. 1. BLOCK Malicious behaviour stopped. 2. DETECT Suspicious runtime activity surfaced. 3. CORRELATE Related evidence connected into an attack graph. 4. DISRUPT Malicious activity contained to limit impact. In these sample screenshots, you can see how Defender turns runtime activity into a connected incident that security teams can investigate and respond to. Connecting DNS activity to Active Incidents Microsoft Defender now provides DNS visibility on Linux. Network connections are enriched with the domain being contacted, and DNS activity is attributed to the process that requested it. When these domains are correlated with Microsoft Threat Intelligence, Defender can identify Linux servers reaching out to known malicious infrastructure and connect that activity to the process chain behind it. This gives security teams earlier detection and clearer context when investigating a potentially compromised Linux server. In an attack, a compromised Linux server could execute malicious commands, download payloads, and connect to attacker-controlled infrastructure. The example below shows how DNS activity can appear within the incident, helping investigators trace the connection back to the process behind it. Continuous validation and coordinated defense Protection is only meaningful when it performs against real attacks. Customers continuously validate Linux protection across leading breach-and-attack simulation and penetration-testing platforms, including AttackIQ, SafeBreach, Cymulate, Metasploit, and Picus. Repeatable testing helps expose coverage gaps, identify regressions earlier, strengthen behavioral detections, and verify resilience as payloads and attack paths change. Deterministic scenarios remain the foundation because they provide repeatability and measurable coverage. Over time, specialized security models can complement them by helping teams develop controlled tests for their environment, explore alternative attack paths, and continuously validate that protections are effective. Project Perception outlines Microsoft’s direction for connecting signals, context, security models, and specialized agents into a coordinated defense system that continuously learns while keeping people in control of high-impact decisions. Microsoft’s differentiated advantage is the breadth of its security vantage point: more than 100 trillion security signals processed each day provide the threat intelligence and context to continuously improve detection and defense. For Linux, this direction connects attack simulation, investigation, vulnerability context, and protection improvement into a continuous loop—reducing exploitable paths before compromise, limiting attacker movement during incidents, and extending runtime protection to emerging AI workloads. Looking ahead Linux will remain central to cloud services, developer platforms, and AI infrastructure. Our commitment is to help customers identify critical gaps, test protection against changing attack paths, reduce opportunities for exploitation, and strengthen Linux defense continuously as attackers and defenders operate at AI speed.575Views0likes2Comments
Prompted to sign in to Microsoft Defender Platform on W11/W2025 using Entra
Hi Microsoft Defender XDR community, Since around May 18th, our users on devices that are onboarded to Microsoft Defender for Endpoint are being prompted to sign-in to the following application using Entra on login to Windows. Application Microsoft Defender Platform Application ID cab96880-db5b-4e15-90a7-f3f1d62ffe39 Is anyone aware of a change that requires user sign-in to Entra as a requirement for Microsoft Defender for Endpoint? I have tried raising a support topic on this topic. Regards Chris2.1KViews3likes10Comments