ediscovery
180 Topics
How much of your Microsoft 365 environment can you actually see at once?
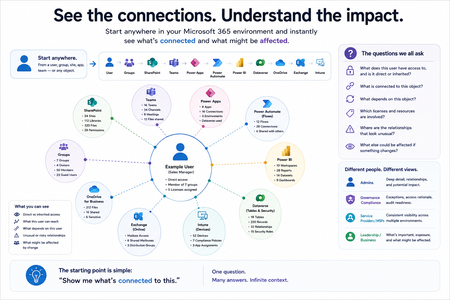
Not how many users you have. Not how many sites, teams, apps or flows you have. How much of it can you actually see connected together? I've been working across Microsoft 365 environments for a while, and I kept running into the same thing. There is no shortage of information. If anything, there is probably too much of it. Users, groups, permissions, SharePoint, Teams, Power Apps, Power Automate, Power BI, Dataverse, OneDrive, Exchange, Intune, licensing, configuration... It's all there. But when you're actually trying to understand how everything fits together, it can be a different story. You open one blade. Find something. Open another. Cross-check it. Go back. Open something else. Before long, you're jumping between different parts of the tenant trying to build the bigger picture in your head. And if you're working with larger environments, that gets difficult pretty quickly. The information isn't necessarily missing. The relationships between the information are what can be difficult to see. That got me thinking about a slightly different question: Instead of "where do I find this information?" "Show me what's connected to this." That's where VisibleState started. Start anywhere. Follow the connections. Imagine starting with a single user. Instead of seeing that user simply as a record with a list of properties, imagine being able to explore the relationships around them: User → Groups → SharePoint → Teams → Power Apps → Power Automate → Power BI → Dataverse → OneDrive → Exchange → Intune Then the questions become different: What does this user have access to? Is that access direct or coming through a group? What resources are connected to them? What depends on something they're associated with? Which licenses are involved? Are there relationships that look unusual? If something changes, what else might be affected? Those questions aren't necessarily about finding another piece of information. They're about putting information that already exists into context. A report can tell you that something exists. A connected view helps you understand what it is connected to. Illustrative example below — not a real customer environment. I'm not suggesting Microsoft 365 doesn't already give us this information Quite the opposite. Microsoft 365 already gives administrators an incredible amount of information and tooling. The thing I've been thinking about is what happens when you want to look across those boundaries. Sometimes I don't want another export. I don't want another list. I don't necessarily want another dashboard. I want to start with something I'm looking at and ask: "What's connected to this?" And then keep following the trail. That's the idea I'm exploring with VisibleState. The interesting part is what happens when you change the viewpoint The same relationships can be useful for completely different reasons. For example: Administrators may want to understand access, permissions and dependencies. Security and governance teams may want to find unusual relationships or exceptions. Compliance teams may need to understand who can access something and why. People managing multiple environments may want a consistent way to understand what's there without rebuilding the picture manually every time. Leadership may not need to see the graph at all. They may simply want to know what's important, what's exposed and what could be affected. It's still the same underlying environment. You're just looking at it from a different angle. And that's where I think things get interesting. Where I'm at with it VisibleState started as something I was building to make my own work easier. I was spending a lot of time investigating environments, tracing access and putting information together for reports. The individual tasks weren't necessarily difficult. It was the jumping between different places and reconstructing the bigger picture that took the time. So I started building something that would let me approach the environment through the relationships instead. It's grown quite a bit from where it started, and I'm continuing to build it. I'm not posting this as a product launch, and I'm not looking for people to sign up. I'm genuinely interested in whether the problem I'm seeing is familiar to other people working with Microsoft 365. So I'm curious... If you could start with any object in your Microsoft 365 environment and immediately see what it's connected to, where would you start? Would it be: Users and access Groups and permissions SharePoint and Teams Power Apps, Power Automate, Power BI and Dataverse Licensing and resources Governance and unusual relationships Something completely different Maybe you've already got a good way of doing this. Maybe you still find yourself jumping between different services and piecing things together manually. Or maybe I'm looking at the problem from the wrong direction. What's the one relationship in your Microsoft 365 environment that you wish you could see instantly?130Views0likes0Comments
Office 365 Mailbox Export to PST - Third Party Tools: What’s Your Experience?
Exporting Office 365 mailboxes to PST is still a common requirement in many Microsoft 365 environments, especially for backup, compliance, and migration scenarios. While Microsoft offers native options like Purview eDiscovery and Outlook export, many administrators also consider third-party tools when dealing with large mailboxes or bulk export requirements. In real-world scenarios, factors like speed, ease of use, permission handling, and consistency of exported data often influence the choice of tool. Some teams prefer native methods for compliance control, while others explore third-party solutions to simplify large-scale or repeated export tasks. For those working with Microsoft 365, what has your experience been with third-party PST export tools? Have they helped in your environment, or do you still rely mainly on Microsoft’s native options?379Views1like3CommentsThe Advantages of Premium Cases in Purview eDiscovery
Capacity & Scale Feature Description Advantage over E3 Enhanced Limits Supports significantly higher limits, including eDiscovery case count and export volume. For example, up to 50,000 cases and 5 TB per search in E5 (versus 10,000 cases and 2 TB in E3). Handles large investigations without splitting into multiple cases or searches. E3’s lower limits would force breaking up big jobs, adding overhead and risk of errors. E5’s higher capacity means fewer workarounds and seamless handling of large-scale litigation. Tenant-Wide eDiscovery Process and Holds Reports (Preview) Provides a central dashboard of all eDiscovery activities and eDiscovery holds across the tenant. Compliance and IT teams get at-a-glance status of ongoing jobs and active holds. Improves oversight and management efficiency for eDiscovery. E3 lacks centralized reporting, making it harder to track many cases. E5’s reporting gives better visibility into operations, which is crucial for heavy workloads and tight deadlines. Expanded Hold Capacity Each legal hold in E5 can encompass up to 2,000 mailboxes and 2,000 sites in one policy. E3 holds are limited to 1,000 mailboxes or 100 sites per policy. Enables placing very large custodian sets on hold with a single action. In E3, exceeding hold limits means juggling multiple policies for one case, increasing complexity. E5 simplifies hold management by consolidating more custodians per hold, reducing admin burden. Search & Collection Feature Description Advantage over E3 Advanced Search Filters Offers richer search criteria beyond keywords. You can filter by sensitive info types (credit cards, SSNs), specific message IDs, or sensitivity labels on documents. This helps pinpoint relevant sensitive content directly. Enables more precise and speedy discovery of critical data. In E3, finding the same info might require complex keyword strings or separate tools (with a higher chance of missing items). E5’s advanced filters mean faster, targeted searches for things like confidential data or GDPR content. Data Source Sync Allows you to refresh custodians’ data sources in a search or hold to catch updates to locations. For example, if a custodian adds a new OneDrive, E5 will detect and prompt you to include it. Ensures no content location is overlooked as the case evolves. E3 has no easy way to know if data moved or new sites were created, potentially leaving gaps. E5’s sync provides complete and defensible collection by keeping holds/searches up-to-date. Cloud Attachment Collection (Hyper-linked Documents) Automatically collects the content of files shared via cloud links (OneDrive/SharePoint) in emails or chats. E5 can retrieve the actual document (and its versions) that was linked, even pulling the specific version that was shared at the time if the version shared feature is enabled. Preserves evidence that E3 would miss. E3 eDiscovery does not fetch linked file content. It would only show a hyperlink, making it difficult to return the associated file. E5 ensures linked documents (with version history) are collected, so the full context of communications is retained. Conversation Threading (Chats & Email) Reconstructs conversations in a threaded view for Microsoft Teams chats and email chains. Reviewers can see messages in context (like a chat transcript or email thread) rather than as isolated items. Greatly improves contextual understanding. E3 exports chats as separate messages with no threading, making it hard to follow the story. E5’s threaded view lets reviewers grasp the full conversation at a glance, reducing confusion and ensuring nothing is interpreted out of context. Custodian & Hold Management Feature Description Advantage over E3 Case-Level Custodian Management Provides a dedicated tab to manage custodians (people) within each case. You add custodians once and can easily apply holds or searches to all their data without re-entering their information each time. Streamlines hold setup and ensures clarity on who is in the case. E3 has no concept of custodians. You must manually input email or site addresses for each search/hold. E5’s approach saves time, reduces errors, and gives a clear view of all people involved in the matter. Bulk Custodian Import Supports importing up to 1,000 custodians at once from a list into a case. Useful for large investigations (e.g., adding an entire department as custodians in one go). Dramatically faster setup for big cases. In E3, adding hundreds of people means typing or pasting each individually, which is time-consuming and error prone. E5’s bulk import means quick, one-time setup for large custodian lists, ensuring no one is missed. “Explore & Add” Custodian Sources Provides an intelligent way to discover related data sources for a given custodian. For example, it can list Teams, SharePoint sites, or groups the person is part of, and let you add those to the case. Helps capture all relevant locations for each person. In E3, you might overlook a Teams channel or group mailbox a custodian was involved in. E5’s explore feature surfaces those connections, improving completeness of your holds and searches by including collaboration spaces that might otherwise be missed. In-Place Review & Analytics Feature Description Advantage over E3 Advanced Indexing and OCR Automatically re-indexes content that was partially indexed or had errors and performs OCR (Optical Character Recognition) on images to extract text. This means files with images or previously unsearchable formats become searchable in E5. Ensures “no stone is left unturned.” E3 would flag such content as “unindexed” (meaning you know a file exists but not what’s inside it). With E5, far more data is searchable, even text inside images or scanned PDFs, reducing the amount of partially indexed content and the chance of missing critical evidence due to format issues. In-Place Review Sets Lets you create a review set of collected data in the cloud. Review sets offer contextual review of conversations, powerful query and filtering capabilities, and query reports for additional insights. Pre-review culling is possible in E5. E3 has no in-product review capability. You must export everything to an outside tool for examination. E5’s review sets allow the team to filter out irrelevant data and focus on what matters before exporting. This reduces the volume (and cost) of data sent for attorney review and keeps data in a secure, auditable environment during analysis. Tagging and Metadata Filters Enables applying tags (labels like “Responsive,” “Privileged,” “Personal Data”) to documents and emails in a review set, and filtering by these tags or other metadata fields. Improves organization and review workflow. E3 cannot tag items in-place, so keeping track of important documents is harder. In E5, tagging allows systematic categorization for quick retrieval (e.g., find all items tagged Highly Relevant instantly). These tags also carry over on export, so any work done during review isn’t lost when handing off to external counsel. Email Threading and Analytics Automatically identifies and stitches together email threads, showing only the last inclusive email that contains the entire conversation. Earlier duplicate emails in the chain are noted and can be skipped. Cuts down review volume and improves context. E3 reviewers would see every single email (even if content repeats across replies). This saves review time and ensures attorneys see the full discussion in one place rather than piecemeal. Conversation View Displays collected Teams (and other chat) messages in a conversation format in a review set, similar to how one would view a chat in the app, instead of individual out-of-context messages. Makes reviewing chat evidence much easier. In E3, chat messages are isolated, forcing reviewers to manually piece together who said what when. E5’s conversational view provides full context at a glance, so nothing is misunderstood or missed in chat-based communications. Near-Duplicate Detection Finds and groups nearly identical documents (e.g. multiple versions of a file or emails with only slight differences). Reviewers are informed which items are alike. Saves time and ensures consistency. E3 requires manually spotting similar files. E5 can let a reviewer examine one version and then quickly tag all its close duplicates the same way. This speeds up review and ensures similar content is handled uniformly (no conflicting judgments on essentially the same document). Themes (Topic Analytics) Uses analytics to cluster documents by themes/topics. For example, it might reveal a group of emails all discussing “Project X” or detect an unusual theme (like frequent mentions of “resignation”). Uncovers hidden patterns that simple keyword searches in E3 might miss. This insight helps investigators spot important threads of discussion or issues they weren’t explicitly searching for, leading to a more thorough understanding of the data set. It adds a layer of proactive insight absent in E3. Global Deduplication Automatically de-duplicates exact copies of emails or files across all custodians using review sets. Each unique item is retained once for review, with duplicates noted. Prevents redundant review work. In E3, the same email stored in five mailboxes would appear five times and could be reviewed and tagged inconsistently by different people. E5’s deduplication means reviewers spend time only on unique content improving efficiency and ensuring consistency in treatment of identical items. Export & Integration Feature Description Advantage over E3 Guest Reviewer Access Allows secure, read-only external access to a review set for outside experts (like outside counsel). Guest reviewers can be invited to review and tag documents in your E5 case via secure Azure AD access (with MFA), without data leaving the tenant. Enables collaboration with outside counsel without exporting data. E3 cannot extend access to external users. You’d have to export files and send them out, which is slower and riskier. E5 keeps the data in-place and governed, letting external reviewers work more efficiently while your organization retains control and visibility. Import External Data Supports ingestion of data from outside M365 into eDiscovery. You can load files like PST emails, PDFs, or documents from file shares into an E5 review set, maintaining custodians’ identity and metadata. Brings all relevant data under one roof. E3 cannot handle content beyond Exchange/SharePoint/Teams, so any non-M365 data would be reviewed separately. E5’s ingestion means even file server or third-party data can be included in the case, making your eDiscovery truly comprehensive and eliminating blind spots between different systems. Rich Export with Metadata Exports include a detailed load file with extensive metadata from the review (custodian info, email thread indices, attachment names, message IDs, tags applied, etc.). This is in addition to the actual content files. Simplifies downstream processing and preserves review decisions. E3’s export is basic (limited metadata), often requiring additional data processing in third-party tools. E5’s comprehensive load file means that all important context (including tags like “Privileged” that your team applied) travels with the exported data, so external reviewers immediately see those cues. This saves time and prevents rework. MIP Search and Decryption Integration Can automatically decrypt protected content (encrypted by Microsoft Information Protection, e.g. with sensitivity labels/Azure RMS) during eDiscovery. Encrypted emails and documents are made readable and searchable when added to a review set. Ensures encrypted files aren’t “invisible” in your investigation. E3 often cannot search or preview MIP-protected emails/docs until they’re manually decrypted after export (if at all). E5 seamlessly includes these encrypted items in search results and review, so you don’t miss evidence that was simply locked behind encryption. Insider Risk Management Escalation Integrates with Microsoft Insider Risk Management (IRM) alerts. With E5, if an insider risk policy flags a user (e.g., for a potential data theft), you can one-click escalate to create an eDiscovery case that automatically targets that user’s content around the incident. Enables a fast, seamless response to insider threats. E3 has no IRM at all, so there’s no such trigger. In E5, the moment a high-risk activity is detected, the legal team can immediately jump into collecting and reviewing the related data. This tight integration means quicker investigations and potentially mitigating issues before they escalate. Communication Compliance Escalation Ties into Communication Compliance (E5’s internal communications monitoring for policy violations). If a serious policy violation is found (e.g., harassment in Teams chats or inappropriate sharing of sensitive info), it can be escalated directly into an eDiscovery case for further investigation. Offers proactive discovery of misconduct. E3 lacks built-in communication monitoring, so issues may go unnoticed until too late. With E5, compliance officers can swiftly pivot from detecting a problem to launching a full eDiscovery inquiry, ensuring faster and more thorough handling of incidents like HR violations or data leaks. Graph API & Automation Fully supports the Microsoft Graph API for eDiscovery. This means eDiscovery tasks (case creation, adding custodians, running searches, exporting data) can be automated or integrated into other applications via scripting/programming without additional cost. While API support is supported for E3, the E3 export API is a metered solution. E5 allows organizations to streamline eDiscovery workflows – for example, auto-create a case and hold when HR flags an employee exit, or integrate with third-party legal management tools without additional cost. Teams and Copilot Interactions Purge Provides an incident response capability to search and purge Teams chats or Microsoft 365 Copilot interactions if sensitive information was shared. Authorized investigators can directly delete up to 100 Teams chat messages (across participant mailboxes) in one go via the eDiscovery interface (leveraging Graph API) when necessary to contain a data leak. Allows quick containment of spills that E3 cannot do. E3’s content search can purge emails but cannot delete Teams messages or Copilot content. With E5, if confidential data pops up in a Teams chat, compliance can not only find it but also bulk-delete those messages from user mailboxes to mitigate further exposure. This capability is crucial for responding to internal data mishandling in real time.Collecting Microsoft 365 Copilot Data with Microsoft Purview eDiscovery
Copilot Data Collection Reference Table Data Type Storage Location Item Class Collection Strategy Copilot Prompts (user questions sent to M365 Copilot) Exchange Online: Hidden folder in the user's mailbox. Compliance copies stored similar to Teams chats, but with unique item classes. IPM.SkypeTeams.Message.Copilot.<AppName> (e.g., .Word, .Excel, .Outlook, .BizChat). Additional AI-related classes may also apply: IPM.SkypeTeams.Message.ConnectedAIApp*, IPM.SkypeTeams.Message.CloudAIApp*, IPM.SkypeTeams.Message.TeamCopilot*, IPM.SkypeTeams.TeamCopilot* 1. Add the user's Exchange mailbox as a data source to the search. 2. In the condition builder you can optionally filter the search to only return Copilot prompts by adding a condition of "Item class contains any of Copilot activity". This automatically applies all relevant M365 Copilot item classes as a condition of the search. 3. Add any further additional conditions such as date range or keywords to narrow results as required. You can also use the Item Class condition to exclude M365 Copilot interactions from your collections when targeting a user’s mailbox. Notes: · Additional item classes may be added. The item class condition will be updated accordingly. Copilot Responses (AI-generated answers) Exchange Online: The same hidden folder in the user's mailbox as prompts. The same IPM.SkypeTeams.Message.Copilot.<AppName> pattern as prompts The same collection strategy used for prompts. Copilot Memories (personalized saved information Copilot "remembers") Exchange Online: Hidden CopilotMemory subfolder within the user's mailbox contacts. Stored as contact entries separate from prompts and responses. IPM.Contact Each memory item appears as a contact card within Exchange, which is distinct from the message-based item classes used for prompts/responses. 1. Add the user's Exchange mailbox as a data source to the search. 2. In the condition builder you can optionally filter the search to only return Contacts by adding a condition of "Item class contains any of Contacts". Notes: · Copilot memories will not be preserved under a legal hold or retention policy. · This will return both Copilot memories stored in contacts as well as traditional contacts from the user’s Exchange mailbox. Copilot Pages (AI-generated, user-editable documents) SharePoint Online: Stored in a user-owned SharePoint embedded container (shared with Loop workspace content and Copilot Notebooks). File format is .page. Not stored in the user's mailbox. N/A These are SharePoint files (not Exchange items), so no item class applies. Identify them in search results by the .page file extension. 1. Add the custodian’s SharePoint embedded site URL as a data source to the search. Alternatively, tenant-wide searches of all SPO sites will include all SharePoint Embedded containers 2. Optionally use the condition builder with conditions such as date range, keywords or file type to further filter results returned Facilitator agent interactions in a Team meeting chat Exchange Online: Hidden folder in all meeting attendees’ mailboxes. Compliance copies stored as Teams chats IPM.SkypeTeams.Message 1. Add the user's Exchange mailbox as a data source to the search. 2. In the condition builder you can optionally filter the search to only return Copilot prompts by adding a condition of "Item class contains any of Instant messages". 3. Add any further additional conditions such as date range or keywords to narrow results as required. Facilitator agent meeting notes (loop) SharePoint Online: Facilitator meeting notes are stored as a .loop file in a OneDrive folder titled Meetings of the user who initiated Facilitator in Teams N/A These are SharePoint files (not Exchange items), so no item class applies. Identify them in search results by the .loop file extension. 1. Add the user's OneDrive URL as a data source to the search. 2. In the condition builder you can optionally filter the search to only return loop files by adding a condition of "File type equals any of loop". 3. Add any further additional conditions such as date range or keywords to narrow results as required. Notes: · With eDiscovery premium enabled cases you can follow the standard workflow for collecting Team meeting messages and select to include cloud attachments in your collection. This will automatically pull into the export or review set any Facilitator agent meeting notes. Facilitator created word/loop documents SharePoint Online: When the facilitator agent is asked to create a word or loop document during a meeting they are stored in the requesters OneDrive in a folder called N/A These are SharePoint files (not Exchange items), so no item class applies. Identify them in search results by the .loop file extension. 1. Add the user's OneDrive URL as a data source to the search. 2. In the condition builder you can optionally filter the search to only return loop and doc files by adding a condition of "File type equals any of loop, docx". 3. Add any further additional conditions such as date range or keywords to narrow results as required. Notes: · With eDiscovery premium enabled cases you can follow the standard workflow for collecting Team meeting messages and select to include cloud attachments in your collection. This will automatically pull into the export or review set any Facilitator generated loop or word documents. Facilitator generated and assigned tasks Exchange Online: When the facilitator agent creates and assigns a task to an individual, it is created as a to-do item in the assigned individual's Exchange Mailbox IPM.Task 1. Add the user's Exchange mailbox as a data source to the search. 2. In the condition builder you can optionally filter the search to only return Tasks by adding a condition of "Item class contains any of Tasks". 3. Add any further additional conditions such as date range or keywords to narrow results as required. Application-Specific Item Classes for Prompts & Responses For more granular filtering by Copilot application, the following item class values can be used in KQL queries: Application Context Item Class Value Microsoft Copilot Chat (BizChat / Teams) IPM.SkypeTeams.Message.Copilot.BizChat Copilot in Excel IPM.SkypeTeams.Message.Copilot.Excel Copilot in Loop IPM.SkypeTeams.Message.Copilot.Loop Copilot in Outlook IPM.SkypeTeams.Message.Copilot.Outlook Copilot in PowerPoint IPM.SkypeTeams.Message.Copilot.PowerPoint Copilot in Teams IPM.SkypeTeams.Message.Copilot.Teams Copilot in Whiteboard IPM.SkypeTeams.Message.Copilot.Whiteboard Copilot in Word IPM.SkypeTeams.Message.Copilot.Word To target all Copilot applications at once, use the wildcard query ItemClass:IPM.SkypeTeams.Message.Copilot.*. For a wider list of AI data sources, see the following link: https://learn.microsoft.com/en-us/purview/edisc-search-copilot-data#data-sources-for-ai-data Important Notes for eDiscovery Practitioners Excluding Copilot Data from Broader Searches Because Copilot prompts and responses reside in the same Exchange mailbox as emails and Teams chats, they will appear in broad mailbox searches unless explicitly filtered out. To exclude Copilot items, use the condition "Item Class Contains none of Copilot activity" in the condition builder, or add (-ItemClass:IPM.SkypeTeams.Message.Copilot.*) in KQL. Some eDiscovery managers run separate searches, one for Copilot data and one for other communications, to keep collections distinct. Copilot Memories: Retention & Hold Limitations Purview retention policies and eDiscovery holds do not currently apply to Copilot memory items. Memory items remain until a user deletes them or an admin explicitly removes them via eDiscovery or Graph API. Additionally, deleting a Copilot prompt and response does not delete any memory derived from that conversation. Memories must be removed separately if required. Copilot Pages: Do Not Treat Like Prompts/Responses Copilot Pages are not stored in Exchange mailboxes. Searching only a custodian’s mailbox will not return Copilot Pages. Treat Copilot Pages the same way as you do for SharePoint content in your existing eDiscovery workflow. For collections, keyword searches will generate hits on text content within the .page file if either the SharePoint Embedded URL is included in the search or the search is a tenant-wide search of all SharePoint sites Be aware that full-text search within .page files in Purview eDiscovery review sets is not currently available. Instead you can use filters such as Subject/Title or Native File Type to locate Copilot Pages in your review set and review the content. When an eDiscovery hold is placed on a custodian’s mailbox, it does not automatically extend to the SharePoint Embedded site where the Copilot Pages are stored. Instead, ensure the hold policy includes the URL for the user-owned SharePoint Embedded site that contains the Copilot Page(s) that must be preserved. Audit Logs vs. eDiscovery for Copilot Content Audit logs record that a Copilot interaction occurred (time, user, workload context) but do not include the actual prompt or response text. To retrieve the substance of Copilot interactions, use Purview eDiscovery searches against the mailbox. Copilot Prompts and Responses: HTML Transcription Copilot prompts and responses are stored as individual messages within the user’s mailbox. When collecting Copilot interactions, enabling the “Organize conversations into HTML transcripts” premium option will convert these individual messages into HTML transcripts making for easier review and linkage between the user’s original prompt and the Copilot responses. Copilot Prompts and Responses: Contextual prompts and responses When using the Keywords condition as part of your collection in eDiscovery, it will only return items that match the keywords included in the query. This means that you may only return a part of the Copilot interaction. If using keywords in your collection query you can enable the “Include full conversation for Copilot, Teams and Viva Engage messages” premium option. This will include in the export or review set any prompts or responses from the Copilot interaction within a 12-hour window before and after each responsive item. This means that you are able to see the full context of the prompt or response that was responsive to search. Collecting Referenced Documents (Cloud Attachments) Copilot responses may reference or summarize SharePoint/OneDrive files. When collecting Copilot interactions, enabling the "Access links (cloud attachments) in messages" premium option will additionally collect the files referenced in the prompt or response and include them in the export package. This provides full evidentiary context but can significantly increase export size and processing time so consider if collecting these artifacts are relevant to the investigation. If so, look to use additional conditions such as date to effectively manage volumes or reduce the number of custodians in the collection. Facilitator agent in Microsoft Teams Meetings The Facilitator agent in Microsoft Teams is an AI-powered assistant (included with Microsoft 365 Copilot) that enhances meeting productivity by generating real-time notes, summarizing key decisions, and managing action items. It acts as an active participant, allowing for collaborative editing of notes and answering chat questions during calls. As the Facilitator works within the context of Microsoft Teams meetings (scheduled private meetings only) your existing workflows for collecting Microsoft Teams meetings chat should be used. In addition, enabling the "Access links (cloud attachments) in messages" premium setting will automatically collect any meeting note (loop) or loop or word documents created by the Facilitator agent. Copilot Retention Reference Table Data Type Microsoft Purview Retention Policy Location/Scope Copilot prompts and responses Microsoft Copilot experiences Copilot Memories (personalized saved information Copilot "remembers") Not supported Copilot Pages (AI-generated, user-editable documents) SharePoint classic and communications sites (Static Scopes only) Facilitator interactions in a Team meeting Teams chats Facilitator meeting notes (loop) OneDrive Accounts Facilitator created word/loop documents OneDrive Accounts Facilitator generated and assigned tasks Exchange mailboxes (Tasks with end dates only)4.6KViews4likes0CommentsRegistration Open: Community-Led Purview Lightning Talks
Get ready for an electrifying event! The Microsoft Security Community proudly presents Purview Lightning Talks; an action-packed series featuring your fellow Microsoft users, partners and passionate Microsoft Security community members of all sorts. Each 3-12 minute talk cuts straight to the chase, delivering expert insights, real-world use cases, and even a few game-changing tips and tricks. Don’t miss this opportunity to learn, connect, and be inspired! Secure your spot now for the big day: April 30th at 8am Redmond Time. See agenda details below and follow this blog post (sign in and click the "follow" heart in the upper right) to receive notifications. ❗UPDATE❗This event is expected to last around 2 hours and 15 minutes, due to the incredible number of community sessions that were submitted! 💖 Please see the timing table below broken out into sections of four talks each, and plan to arrive 10 minutes before the section that interests you, OR stay for the whole time! Speakers will be available in the chat to answer your questions; please ask your questions during their session. Spillover Q&A forum links will also be shared. The full session recording will be indexed and posted to Microsoft Security Community YouTube within 24 hours after the event. Bookmark this page or follow this blog post for updates! Agenda Legend ↩️ Data Lifecycle Management 🔐 Information Protection 🚫 Data Loss Prevention (DLP) 🦾 Data Security Posture Management (DSPM) for AI 🤖 Purview for AI 👁️ Insider Risk Management (IRM) 🔍 eDiscovery 📊 Governance 🗒️ Compliance Manager 🛡️ Data Security All times are listed in US Pacific/Redmond Time. Session lengths are rounded to the nearest minute. AGENDA Section 1 - approximately 8:00 am - 8:43 am ↩️ The Day Offboarding Exposed Infinite Retention — Nikki Chapple Length: 10 minutes | Topic: Data Lifecycle Management A routine Purview request led to an unexpected discovery: more than 9,000 orphaned OneDrives and thousands of inactive mailboxes still storing content long after employees had left. This talk explains how a retain-only policy created hidden retention debt and how Adaptive Scopes can help organisations separate active users from leavers to avoid similar pitfalls. 🔐 The Purview Label Engine: Automated Classification, Translation, and co-Documentation for Enterprise Tenants — Michael Kirst-Neshva Length: 12 minutes | Topic: Information Protection Global enterprises face the challenge of implementing uniform data protection standards across borders and languages. In this talk, I’ll present a framework that makes Microsoft Purview labels truly scalable. Discover how to roll out parent and child label logics automatically, manage priorities with a single click, and generate instant compliance documentation for every business unit. 🗒️ What's In My Compliance Manager Toolbox: A Cloud Security Architect's Perspective — Jerrad Dahlager Length: 8 minutes | Topic: Compliance Manager A practical walkthrough of how I use Compliance Manager across real client engagements to map controls, track improvement actions, and simplify multi-framework compliance. No theory, just what works in the field. 🛡️ Stop, Think, Protect: Data Security in Real Life with Purview — Oliver Sahlmann Length: 8 minutes | Topic: Data Security With simple labels and matching DLP policies, Purview offers a practical and accessible way to approach data security. This lightning talk uses a real-life traffic light concept to show how a low barrier to adoption can still drive meaningful protection and awareness. Section 2 - approximately 8:44 am - 9:15 am 🔐 Using Purview to prevent oversharing with AI services — Viktor Hedberg Length: 10 minutes | Topic: Information Protection In this day and age, AI is the big thing. However, Copilot has access to everything you can access, including potentially sensitive data. In this session we will look at how to prevent Copilot to access highly sensitive data, using Information Protection. 🦾 How I Helped My Customers Understand their AI Usage (and protect their sensitive data) — Bram de Jager Length: 5 minutes | Topic: Data Security Posture Management (DSPM) for AI As AI tools explode across the web, many organizations still have no idea what’s actually happening in the browser—where employees type prompts, paste sensitive data, or visit public AI sites outside corporate governance. In this lightning talk, I’ll share how I helped customers shine a light on this issue. We’ll explore how Purview Data Security Posture Management (DSPM) can reveal which AI tools employees use, what types of data they input, and where sensitive information may leak through prompts. I’ll walk through real customer scenario where we detected risky AI usage patterns—such as employees pasting confidential documents into public chatbots. 🔐 Four Labels Max for Daily Use: Which Ones & Why? — Romain Dalle Length: 8 minutes | Topic: Information Protection Sensitivity labels are one of the most critical parts of a Purview Risk and compliance deployment, if not the most critical, because it directly impacts how end-users and business units should allow or restrict themselves to share their business data, internally and externally, on a daily basis. Labels have not other options than being precise, meaningful, and balanced in terms of embedded data security. Setting the right taxonomy is core to success, and is everything but a one-time project. 🚫 Data-driven Endpoint DLP Solution with Advanced Hunting — Tatu Seppälä Length: 8 minutes | Topic: Data Loss Prevention (DLP) This lightning talk shows you how to use KQL queries in advanced hunting to easily build initial sensitive service domain groups for authorized and unauthorized domains based on your organization's usage patterns. The same approach can be used for numerous other similar solution refinement and design purposes. Section 3 - approximately 9:16 am - 9:46 am 🔐 The Purview Hack No One Talks About: Container Sensitivity Labels That Fix Oversharing Fast — Nikki Chapple Length: 10 minutes | Topic: Information Protection Most organizations tackle oversharing with manual fixes, but the fastest solution is often overlooked. In this lightning talk, I show how container sensitivity labels automatically apply the right sharing and collaboration controls, ensuring every new Group, Team or SharePoint site starts secure by default. 🔍 Does M365 Support eDiscovery? — Julian Kusenberg Length: 11 minutes | Topic: eDiscovery A myth-busting session that separates perception from reality when it comes to Microsoft 365 eDiscovery capabilities. 📊 Improving Discovery, Trust, and Reuse of Analytics with Purview Data Products — Craig Wyndowe Length: 5 minutes | Topic: Governance This talk shows how bringing Power BI and Fabric assets into Microsoft Purview Governance Domains and Data Products creates a single, trusted view of enterprise analytics. By connecting reports, semantic models, and underlying data with shared metadata, ownership, and business context, organizations can make existing assets easy to discover and safe to reuse. 🔐 Why You Should Create Your Own Sensitive Information Types (SITs) — Niels Jakobsen Length: 5 minutes | Topic: Information Protection An in depth analysis of why Microsoft SITs are not one-size-fits-all, and how to create your own using what Microsoft has already built for you. Section 4 - approximately 9:47 am-10:30 am 👁️ From Zero to First Signal: Insider Risk Management Prerequisites That Actually Matter — Sathish Veerapandian Length: 8 minutes | Topic: Insider Risk Management (IRM) A focused live demo showing the real world prerequisites required for Microsoft Purview Insider Risk Management to work effectively. This session highlights the critical Entra ID, Intune, Microsoft Defender for Endpoint, and Purview DLP configurations that must be in place before creating IRM policies. 🤖 Securing data in the age of AI — Júlio César Gonçalves Vasconcelos Length: 11 minutes | Topic: Purview for AI AI will transform business as we know it; but without proper governance, it can introduce serious risks. We’ll show you how Microsoft Purview enables organizations to accelerate AI adoption while maintaining security, compliance, and transparency. 🔍 Beyond eDiscovery - Purview DSI for Security Investigation — Susantha Silva Length: 11 minutes | Topic: eDiscovery Most people hear “Microsoft Purview” and immediately think compliance, eDiscovery, or legal holds. But this session highlights Data Security Investigations, showing how DSI lets you take a DLP alert or insider risk signal and turn it into a structured investigation. 🚫 Elevating Purview DLP with a real world use case — Victor Wingsing Length: 14 minutes | Topic: Data Loss Prevention (DLP) Learn how I hardened Microsoft Purview DLP beyond out of the box defaults—closing real world data loss gaps, tuning policies to actual user behavior, and turning noisy alerts into protection that really blocks exfiltration. - Quick Closing/ Resource Sharing2.5KViews7likes2Comments
eDiscovery - Issues exploring groups & users related to a hybrid data source
Hi all, first time posting - unusually I could find nothing out there that helped. I work in an organisation has an on-premises domain which syncs to our tenant. I don't manage the domain or the sync, but I'm assured that the settings are vanilla and there are no errors being logged. 99% of our users are hybrid. The tenant is shared across multiple legal entities, so I'm using eDiscovery to fulfil our GDPR subject access requests The issue I am hitting is straightforward. in eDiscovery searches with hybrid users as the data source, I cannot add related objects (manager, direct reports, groups the user is in). The properties are present in Entra, but not visible to Purview, so I'm not investigating sync errors at the moment. For cloud objects, I can see manager, teams, etc. and it works fine. Does anyone have any insights they can share on the "explore and add" mechanics in eDiscovery search data sources? I'm drawing a complete blank on this one. Where should I be looking?314Views0likes2CommentsGeneral Availability of Microsoft Purview eDiscovery Graph API for E3 Customers
As of December 1 st , 2025, the Microsoft Purview eDiscovery Graph API Standard hit General Availability (GA). It provides a programmatic way to manage eDiscovery cases, searches, holds, and exports for organizations that have only M365 E3 licenses. It extends capabilities that were previously exclusive to eDiscovery Premium customers with M365 E5 (or equivalent add-on SKU) licenses. With the eDiscovery Graph APIs, organisations can realise efficiency savings by interacting programmatically with the following elements of their eDiscovery workflow: Case management – create new cases, list or get case details, update cases, and close or reopen cases. Hold management – place content locations on hold (or remove holds) within a case and list hold policies. Search management – create new searches, list existing searches, update search parameters, delete searches, and run a statistics job on a search. View progress of eDiscovery jobs – view lists of all jobs run in the case, including their status and run times. Export operations – trigger an export job from a search, generate an export report, and download the export packages programmatically. Execute Search and Purge operations - ability to purge email messages from mailboxes identified in a modern UX search. For existing customers utilizing the legacy eDiscovery PowerShell cmdlets it presents an opportunity to enrich and enhance any existing script based processes. eDiscovery Investigators, and teams supporting them, can benefit from the Microsoft Graph-based PowerShell cmdlets to also realize efficiency savings without implementing full end-to-end automation. Why use Graph APIs instead of eDiscovery PowerShell cmdlets? Moving from the old Exchange/Compliance PowerShell cmdlets to Graph API might seem like a significant change. The Graph API is aligned with the latest Purview eDiscovery (modern) experience, unlocking organizations to scale their workflows to benefit fully from its new features and improvements. Searches created and run through the APIs can be viewed and managed from the Purview Portal. Microsoft continues to update and enhance the Graph APIs as Microsoft Purview eDiscovery continues to evolve Where as the legacy Cmdlets are tied to the older eDiscovery (Classic) model with limitations in the eDiscovery activities you can perform. There are no new capabilities or enhancements to the legacy cmdlets planned. What do I need to do to start using the APIs? For customers with only E3 licenses in their tenant, before you can start using the APIs you must enable Microsoft Purview pay-as-you-go features as per the following article: Enable Microsoft Purview pay-as-you-go features via subscription | Microsoft Learn If today, your eDiscovery Investigators and supporting operational teams are connecting to Security & Compliance PowerShell using the Exchange Online PowerShell module and are authenticating as themselves then the delegated permission model would be the equivalent model with the APIs. Investigators using the Microsoft Graph PowerShell module eDiscovery cmdlets: Can only work with cases they have created or have been granted access to Limits their actions based on the eDiscovery Purview roles assigned to them To enable investigators to authenticate and use the eDiscovery cmdlets from the Microsoft Graph API PowerShell module; the Microsoft Graph Command Line Tools enterprise app must be added to Entra ID and the appropriate Graph API permissions consented to. There are two eDiscovery related Microsoft Graph Permissions and organizations should select the appropriate permissions based on their requirements. They are as follows: eDiscovery.Read.All: Allows the app to read eDiscovery objects such as cases, searches, holds and other related objects (link) eDiscovery.ReadWrite.All: Allows the app to read and write eDiscovery objects such as cases, searches, holds and other related objects (link) You can check if these permissions are already granted to the Microsoft Graph Command Line Tools by searching for and reviewing the enterprise app in Microsoft Entra. If they have not been granted then an administrator with either the Application Administrator, Cloud Application Administrator or Privileged Role Administrator Entra roles assign can use the following steps to grant the permissions and provide admin consent for all users in the tenant. As delegate permissions are being used in this scenario, even though the consent applies to all users. The signed in user must also be assigned the relevant eDiscovery Purview Roles to make use of the APIs. Install the Microsoft Graph PowerShell Module (link) Connect to Microsoft Graph using the following PowerShell cmdlet Connect-MgGraph -scopes "eDiscovery.ReadWrite.All" -TenantId "<tenant id>" On the permissions screen select “Consent on behalf of your organization” and select accept Now that this has been configured, eDiscovery Investigators will require the Microsoft Graph PowerShell module to connect and make use of the Microsoft Graph PowerShell modules eDiscovery cmdlets. Frequently asked questions Where can I find details on what APIs are available and what they can do? Documentation for the Microsoft Purview eDiscovery Graph APIs can be found here: Use the Microsoft Purview eDiscovery API in Microsoft Graph - Microsoft Graph v1.0 | Microsoft Learn The documentation provides information on what the API call does, what properties are supported and examples of the request and responses. Is there costs associated with using the Microsoft Purview eDiscovery Graph API Standard? Currently, usage of all APIs except the Export API does not contribute towards billing. ediscoverySearch: exportResult - Microsoft Graph v1.0 | Microsoft Learn Usage of the Export API is billed based on the volume of data exported. Each organization receives an included amount of free storage per month (50GB), with additional usage billed at a set price per GB ($10). More information can be found here: Billing in eDiscovery | Microsoft Learn What happens if I have a mix of E3 and E5 licenses? When triggering an export using the Export API for a Microsoft Purview eDiscovery case with the premium features enabled, no costs will be incurred. When triggering an export using the Export API for a Microsoft Purview eDiscovery case with the premium features disabled, it will contribute towards billing. Can I still use PowerShell to work with eDiscovery Cases? Yes, you can use PowerShell cmdlets to work with Microsoft Purview eDiscovery via the APIs. Within the Microsoft Graph PowerShell module there are eDiscovery cmdlets available. When reviewing the API documentation the appropriate PowerShell cmdlets are listed within the examples section. Take, for instance, creating a new case, when reviewing the documentation (link), we can see the New-MgSecurityCaseEdiscoveryCase is available. Can I integrate the APIs into a custom-developed application? Yes, you can install the Microsoft Graph SDK and it is available for the following languages: .NET Go Java JavaScript PHP PowerShell Python More information on installing the Microsoft Graph SDK can be found here: Install a Microsoft Graph SDK - Microsoft Graph | Microsoft Learn Can I use Microsoft Graph application permissions if I am an E3 customers? For E3 customers you can only make use of Microsoft Graph delegate permissions when working with eDiscovery cases without Premium features. The use of application permissions requires E5 licenses and eDiscovery Premium cases. Do third-party applications integrate with the Microsoft Purview eDiscovery APIs? Please check with your third-party vendor for their support for the Microsoft Purview eDiscovery APIs. Is this available in GCC, GCC High, and DoD tenants? Yes, it is available across these environments. Is there any scenario-based guidance for me with examples on how to use the Graph API? There will be soon! We will be releasing further scenario-based guidance to help both Microsoft 365 E3 and E5 organizations adopt and benefit from the Microsoft Purview eDiscovery Graph APIs.Building Secure, Enterprise Ready AI Agents with Purview SDK and Agent Framework
At Microsoft Ignite, we announced the public preview of Purview integration with the Agent Framework SDK—making it easier to build AI agents that are secure, compliant, and enterprise‑ready from day one. AI agents are quickly moving from demos to production. They reason over enterprise data, collaborate with other agents, and take real actions. As that happens, one thing becomes non‑negotiable: Governance has to be built in. That’s where Purview SDK comes in. Agentic AI Changes the Security Model Traditional apps expose risks at the UI or API layer. AI agents are different. Agents can: Process sensitive enterprise data in prompts and responses Collaborate with other agents across workflows Act autonomously on behalf of users Without built‑in controls, even a well‑designed agent can create compliance gaps. Purview SDK brings Microsoft’s enterprise data security and compliance directly into the agent runtime, so governance travels with the agent—not after it. What You Get with Purview SDK + Agent Framework This integration delivers a few key things developers and enterprises care about most: Inline Data Protection Evaluate prompts and responses against Data Loss Prevention (DLP) policies in real time. Content can be allowed or blocked automatically. Built‑In Governance Send AI interactions to Purview for audit, eDiscovery, communication compliance, and lifecycle management—without custom plumbing. Enterprise‑Ready by Design Ship agents that meet enterprise security expectations from the start, not as a follow‑up project. All of this is done natively through Agent Framework middleware, so governance feels like part of the platform—not an add‑on. How Enforcement Works (Quickly) When an agent runs: Prompts and responses flow through the Agent Framework pipeline Purview SDK evaluates content against configured policies A decision is returned: allow, redact, or block Governance signals are logged for audit and compliance This same model works for: User‑to‑agent interactions Agent‑to‑agent communication Multi‑agent workflows Try It: Add Purview SDK in Minutes Here’s a minimal Python example using Agent Framework: That’s it! From that point on: Prompts and responses are evaluated against Purview policies setup within the enterprise tenant Sensitive data can be automatically blocked Interactions are logged for governance and audit Designed for Real Agent Systems Most production AI apps aren’t single‑agent systems. Purview SDK supports: Agent‑level enforcement for fine‑grained control Workflow‑level enforcement across orchestration steps Agent‑to‑agent governance to protect data as agents collaborate This makes it a natural fit for enterprise‑scale, multi‑agent architectures. Get Started Today You can start experimenting right away: Try the Purview SDK with Agent Framework Follow the Microsoft Learn docs to configure Purview SDK with Agent Framework. Explore the GitHub samples See examples of policy‑enforced agents in Python and .NET. Secure AI, Without Slowing It Down AI agents are quickly becoming production systems—not experiments. By integrating Purview SDK directly into the Agent Framework, Microsoft is making governance a default capability, not a deployment blocker. Build intelligent agents. Protect sensitive data. Scale with confidence.
Securing the Browser Era - From Cloud to AI: A blog series on protecting the modern workspace
Browser has transformed how enterprises operate, but it has also created new opportunities for attackers. As we’ve seen in Part 1, as browsers have become indispensable with Cloud and SaaS adoption, browser native threats and attacks have also increased. Despite their central role in daily work, browsers often lack the layered security controls we expect for networks, endpoints, or applications. This post unpacks how organizations can build defense-in-depth strategies to provide browser centric protection. Part 2 - From Neglected to Necessary: Building Defense in Depth for Browsers To protect against browser-specific threats like phishing, malicious extensions, data exfiltration, session hijacking, and drive-by downloads, organizations must apply the zero trust principles to browsers. A secure browser environment with multiple layers of defense that includes explicit verification of identity, device health enforcement, browser hardening, threat intelligence, and data protection is crucial to defend against sophisticated browser threats. Below are the multi-layered controls, defenses, and best practices an organization can implement to combat the risk from browser threats. Leverage an Enterprise Secure Browser Standardizing and adopting an enterprise grade secure browser for corporate access helps in reducing the attack surface. An enterprise browser such as Microsoft Edge for Business is designed to meet the security, management, and productivity needs of organizations. Microsoft Edge for Business is independently recognized by Forrester, IDC, and industry analysts as a secure enterprise browser, delivering measurable economic value, strong Zero Trust alignment, and enterprise‑grade security. Below are some of the security features and benefits of deploying an enterprise secure browser - Microsoft Edge for Business: Separation of Work and Personal Data- Microsoft Edge’s automatic profile separation of work and personal uses separate caches and storage and a visual enterprise-branded icon. This allows organizations to consolidate on one browser for both work and personal needs across platforms and reduce variance, bring consistency and eliminate management overhead of separate browsers. Edge for Business requires minimal user effort on BYOD and silently applies protection with security solutions integrations. Centralized Manageability: All settings in an enterprise browser can be centrally configured and locked down whether the organization is cloud only, hybrid, or on premises. Enterprise browsers allow organizations to enforce consistent security controls and reduce attack surface. Features like SmartScreen in Edge protect users from threats, but enterprise versions go further by letting IT turn on additional safeguards (e.g. Edge’s JIT hardening, forced VPN, strict site isolation modes, extensions) via policy. Centralized management also makes it possible to consistently apply settings across the organization for UI elements (Ex: homepage, favorites) and deploy updates to patch vulnerabilities and install new enhancements. Security and Threat Protection Features: Phishing and Malware Defense: Edge for Business leverages Defender SmartScreen to block malicious sites/downloads and integrates with Microsoft Threat Intelligence and Windows Security Center for enterprise visibility. SmartScreen protection is native to the browser – no extensions needed – and forms the first line of defense against web threats. Process Isolation and sandboxing: Multi-process architecture, which sandboxes web content in isolated renderer processes that have limited access to the operating system. This containment means if a malicious site manages to run code, it’s much harder for it to escape the browser or infect the device, ensuring robust containment of web content. Enhanced Security Mode: Disables the Just-In-Time (JIT) JavaScript compiler and enables additional OS-hardening like Hardware-enforced Stack Protection and Arbitrary Code Guard (ACG) for the browser process. By removing JIT, which is often exploited in drive-by attacks and using hardware-level safeguards, Edge greatly reduces the risk of memory corruption exploits on those sites. Network and Attack Surface Protections: Microsoft Edge also incorporates various other built-in security features for safe browsing. For example, typosquatting protection thwarts phishing that relies on mistyped addresses. Automatic HTTPs feature upgrades certain HTTP connections to HTTPS, when possible, to ensure encrypted transit. The browser also monitors extension installations and detects and auto-removes malicious sideloaded extensions. In addition, Edge has a built-in password manager with password monitor that scans and alerts leaked credentials on dark web. Continuous Threat Intelligence Updates: Edge benefits from Microsoft’s threat intelligence feeds. SmartScreen’s cloud service is continually updated with newly reported phishing URLs and malware sources. Scareware\scam detector in Edge provides protection from tech support scam pages such as a fake virus alert that locks the browser. Edge will immediately break out of full-screen mode, mute audio, and display a prominent warning – even before SmartScreen has a signature for it. This client-side ML sensor also signals the SmartScreen cloud to block new scam sites faster for all users. Integration with Enterprise Systems: Edge for Business’s out of the box integration with Entra ID, Intune, and Defender helps secure browser with same tools that organizations leverage for protecting applications and networks. It can leverage existing solutions and features like conditional access, single sign-on, MDM/MAM to provide a smoother, more secure experience, and provides visibility of browser threats in enterprise security tools. Enterprise versions ensure that the browser can be made to fit into login flows, proxy configurations, certification environments, and other enterprise needs. This tight integration not only significantly boosts security, but it also simplifies user experience. Implement Layered Controls Use multiple reinforcing defenses across identity, device, browser, network, data to provide comprehensive protection. Edge for Business natively integrates with Microsoft Security solutions and can also be integrated with third party security solutions. Below are some layered controls and best practices that can be implemented to protect from browser-based attacks. Require Strong Authentication: Every access request in a browser must be explicitly authenticated and authorized based on context before any corporate data is exposed. Edge for Business is natively aware of Entra ID and provides seamless Single Sign-On and supports strong conditional access rules. For managed PCs, require they are Entra joined or Intune compliant to get access; for BYOD or unmanaged devices, require MFA at minimum – and consider using “allow browser access but with limited sessions” controls to reduce what unmanaged sessions can do. Leverage risk-based policies such as - block TOR/VPN anonymity or unfamiliar countries automatically and enable new features like Token binding for high-value apps to neutralize pass-the-cookie attacks. Harden Endpoint & Browser: At the device level, organizations should harden both the browser application and the operating system environment in which it runs. Microsoft Defender for Endpoint fortifies the device environment in which the browser runs. It provides both preventive defenses (blocking bad sites, files, and behavior) and detective controls (alerting on anomalies, stopping post-breach actions). On enterprise-managed devices, admins can configure security baseline policies for the OS and the browser via Intune baseline policies, leverage Defender for Endpoint security features such as network filtering to block traffic to malicious domains, categorize and block web content via web filtering, detect drive-by download attacks and anomalous behavior with Defender antivirus. Defender for Endpoint’s Attack Surface Reduction (ASR) rules can be utilized to effectively shore up the OS against actions that malware from a compromised browser might attempt. Defender for Endpoint also provides the device risk signals and Intune provides device compliance status to Entra to continuously verify device health to enforce adaptive access. Microsoft Defender for Endpoint’s device inventory lists installed browser extensions and potentially unwanted apps – leverage these to audit and remove dangerous add-ons enterprise-wide. Intune can also enforce secure browser settings on enterprise managed devices. For a BYO or unmanaged device where OS cannot be controlled, requiring the user to use Edge for Business utilizes SmartScreen, Intune App Protection to containerize that session. Keeping browsers up to date is also crucial to patch vulnerabilities in both managed and unmanaged device scenarios. Enforce Secure Application Access: Treat every browser session and web application as a potential entry point for attackers. Conduct regular risk assessments and maintain an inventory of all web apps accessed by users by leveraging Defender for Cloud Apps for discovery and control. Apply granular access policies using Conditional Access, Defender for Cloud Apps, and Global Secure Access to restrict sensitive actions based on user, device, and risk context. Monitor network interactions and pre-empt threats: Defender SmartScreen and Network Protection in Defender for Endpoint help leverage the vast Microsoft threat intelligence to block threats. Defender for Office 365 Safe Links works in conjunction with browser security by catching phishing at the email source. Ensure web application firewalls (WAFs) are protecting any self-hosted web services. For Wi-Fi, use WPA3 enterprise to prevent local sniffing that could steal session cookies. Secure the networks (on-prem or cloud) that connect browsers to apps through micro-segmentation. Data Protection & Compliance: Edge for Business integrates with native Endpoint DLP enforcement and the ability to prevent data exfiltration through the browser. With a managed browser, companies can ensure that uploads, downloads, copy-paste, printing, watermarking, and other actions adhere to policy – crucial for compliance with regulations like GDPR, HIPAA, etc. Enable a layered approach to prevent data leaks via the browser by leveraging Purview DLP on the endpoint and in Edge, along with Defender for Cloud Apps for in-session control. On a managed device, endpoint DLP policies in Edge will directly block prohibited actions. On an unmanaged device, Conditional Access and Defender for Cloud Apps can enforce restrictions. Logging and SecOps: Collect telemetry from everywhere (Edge, proxies, endpoints, identity) in a centralized SIEM such as Sentinel and set up alerts for example - multiple SmartScreen blocks which could mean a user is repeatedly trying to bypass warnings. Leverage automation to respond to browser-based incidents for instance - if a browser exploit is detected, isolating the machine quickly. Use Microsoft 365 Defender’s hunting queries for proactive threat detection such as identifying any suspicious PowerShell spawned by browsers or abnormal data transfer events. A secure browser, coupled with defense in depth and Zero Trust offer a powerful playbook for managing today’s browser risks and becomes a powerful first line of defense for the cloud-first, work-anywhere world. Yet, just as organizations start to catch up, a new frontier is emerging — AI-powered browsers. In Part 3, final post, we’ll look ahead at the next evolution: AI browsers. They promise new levels of productivity and insight but also open doors to sensitive data leakage, model manipulation, and other novel risks and how enterprises can strike the right balance between risk and innovation.1.2KViews0likes0Comments