compliance
25 Topics
M365 Admin Center Global Administrator Lockout
Hello Microsoft Community, I am seeking urgent assistance and guidance regarding a critical Microsoft 365 tenant lockout that has been ongoing for several days without a resolution or proper communication from the support team. Our organization manages Microsoft 365 services for a business with more than 200 active users who depend on Microsoft 365 for their daily operations. Issue Description We have been locked out of our Microsoft 365 tenant's administrator account. This prevents us from properly managing our Microsoft 365 environment and restoring normal access to essential business services. Our business-critical data, including important documents and operational information, is stored in SharePoint. The inability to access and manage these services has significantly disrupted our business operations. Microsoft Support Ticket References We have raised multiple support tickets and followed up repeatedly, but the issue remains unresolved. Tracking ID: 2610050040001149 Tracking ID: 2610090010001066 Tracking ID: 2610050040001222 Despite these support cases and repeated follow-ups, we have not received a satisfactory resolution or a clear recovery timeline. Support Experience So Far Following a discussion with the support team, we were expecting a call to assist with unlocking the administrator account and providing a temporary password through the appropriate recovery process. However, we have not received the expected call or a meaningful update. Our main concerns are: Complete loss of access to the Microsoft 365 tenant administrator account. More than 200 users affected by the ongoing incident. Critical business data and documents stored in SharePoint. Multiple support tickets without a concrete resolution. Lack of clear communication regarding the root cause and recovery timeline. No clear escalation path or confirmation of the next recovery steps. Our Concerns We understand that technical issues can occur, but leaving a business-critical environment inaccessible for an extended period without meaningful updates is extremely concerning. We purchase Microsoft 365 licenses through a partner and expect appropriate technical support and escalation assistance when critical incidents occur. Our organization previously used Google Workspace and recommended migrating to Microsoft 365 because of its enterprise capabilities. This incident has seriously affected user confidence and business continuity. If access cannot be restored promptly, we may have to consider alternative email hosting arrangements to minimize further disruption. Request for Assistance I would appreciate guidance from Microsoft engineers, Microsoft 365 administrators, and community members who have experienced similar situations. What is the appropriate escalation process when all available tenant administrator accounts are inaccessible? How can we expedite tenant ownership verification and administrator account recovery? Is there a dedicated Microsoft team that handles critical tenant lockout incidents affecting business operations? What is the recommended recovery process when the administrator cannot access the Microsoft 365 Admin Center? How can we obtain urgent assistance when multiple support tickets and repeated follow-ups have not resulted in a clear resolution? Can the three referenced support tickets be escalated for urgent review by the appropriate Microsoft support team? We are not looking for workarounds that compromise tenant security. We need Microsoft's official recovery process to restore authorized administrative access safely. Microsoft Support Team: If any Microsoft support representatives are monitoring this community, we would appreciate your guidance on the appropriate escalation channel for this incident. We can provide additional information privately through the appropriate official channels. Thank you for your time and assistance. Any guidance that helps us restore our services and protect business continuity would be greatly appreciated. Best regards, Microsoft 365 Tenant Administrator7Views0likes0Comments
Language defaults audit for everything M365
We are struggling to find where and how the wrong language is being used for various parts of the M365 platform. We have Swedish set as default, but still English is used for a number of places which often are only realized as a consequence by a user. For example, in Viva Engage language is set to Swedish, and for the SharePoint as well. But: When a new user logs on VE is in English While the SharePoint web part is in Swedish, the link text have for some time ended with "- Home" (English) instead of as it was when we started 2+ years ago " - Startsida" (Swedish) Then when creating a VE group Event (Teams-meeting) default language is also English Tracking down what and where is making the wrong language being used is hard. I would be very grateful if pointed to a resource that give an as complete as possible overview of everything in M365 that we need to look over for making sure that the correct language is default everywhere it should be.528Views0likes4Comments
Partner lockout of Microsoft 365 tenant – looking for advice on next steps
Hello all, I’d appreciate some guidance from the community on a serious situation we are facing. On 12 September 2025, our Microsoft partner unilaterally locked us out of our Microsoft 365 tenant. They retained exclusive Global Administrator / Partner Delegated Admin rights, which means: All staff and directors are unable to access email, Teams, SharePoint/OneDrive, or even log into their Azure AD-authenticated workstations. Our corporate and staff personal data is now inaccessible to us as the controller. Access restoration has been explicitly conditioned on payment of a disputed invoice (not related to Microsoft licence pass-through). This raises several concerns: Operational: we are effectively paralysed. Security/IP: the partner still has exclusive access to proprietary source code and other confidential business data. Compliance: we cannot meet our GDPR/UK DPA obligations on availability of personal data while locked out. We contacted Microsoft Business Conduct on Friday evening with full details of the incident, but so far no human response has been received to those emails. Questions for the community From a Microsoft tenancy perspective – what’s the fastest/most effective way to remove a partner’s delegated admin access if they refuse to release it voluntarily? Has anyone experienced or seen a similar scenario where access was conditioned on disputed payments? Are there formal Microsoft Partner Code of Conduct provisions that directly address this type of misuse of delegated admin rights? Any practical lessons on balancing the technical fix (regaining control of the tenant) with the legal approach (injunction, regulatory notifications)? My focus is on regaining secure access, protecting data/IP, and ensuring compliance. Any experience, insight, or links to Microsoft policy/resources would be greatly appreciated.667Views0likes1Comment
Unable to whitelist quarantined emails
We have an email that is being constantly quarantined from a webform. The email comes from the email of the web form server, but is spoofing an internal address in our tenant by design. The email keeps getting blocked, and nothing we've tried as far as transport rules, whitelist additions, etc has been able to discernably affect this. There is a option to create a tenant allow list entry but the maximum duration is 45 days. We need a way to reliably whitelist an email indefinitely.263Views0likes1Comment
Adding Outlook add-ins and permissions
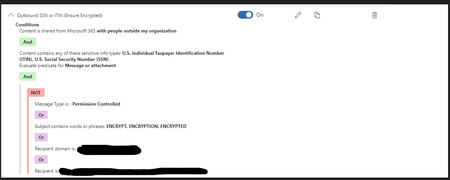
Wonderoig if someone can answer a question for me. I'll use the process in this link as context https://help.draftable.com/hc/en-us/articles/46382047949977-Configuring-Redline-in-Email-Outlook-with-Draftable In short when adding an Outlook Addin and selecting a group to assign the add-in too and the accepting the permission requests does this: Apply the permissions to ONLY those nominated users' mailboxes; or Applies the permissions to ALL mailboxes and applies "security" by limiting the users who can see the add-in I assume it does one of the two. Any ideas?395Views0likes2CommentsDLP Exception for "Permission Controlled" Not Working (Microsoft Purview | RMS Template | Encrypt)
Hello, We are in the process of moving some of our mail-flow / transport rules over to Microsoft Purview. We don't want the DLP policy to apply when people click their "Encrypt" or "Do not Forward" buttons (RMS templates; OME encryption.) Putting "Permission Controlled" in the exceptions group should theoretically let the emails go through. The exception we have for when people put "Encrypt" in the subject line works (we have a mail-flow rule that encrypts those emails.) But actually clicking "Options" > "Set permissions on this item" > "Encrypt" doesn't remove the policy tip on an email draft, and people are unable to send the emails. Can someone verify that this rule is constructed properly? If so, we may have to reach out to Microsoft Support. Thank you so much for your time and help!Solved914Views1like6Comments
Disable OneDrive Retention Policy for One User Account
We have one OneDrive default retention policy for all staff in M365. We have one user, because of the work they do, has one file that is rewritten many times during the day which creates an incredibly huge version history. I can't delete the version history because of the retention policy. I don't need more than a day or two retention. It looks like I can create an exclusion by going to Admin portal --> Compliance --> Data Lifecycle Mgmt --> Microsoft 365 --> Retention Polices --> I keep clicking Next till I get to "Choose Where to Apply This Policy" then I select OneDrive accounts. Under Included we have "All user accounts". Under Excluded we currently have "None". In order to exclude someone I need "remove all the included ones". In order to include someone it looks like I have to remove all the excluded ones. Clearly I am either misreading this or just not understanding. I need to exclude this one user or be able to delete the many 100's of versions of this one file. Your help is appreciated.8.4KViews0likes6Commentspasscode expiry on personal devices
My work has enabled enforcement of minimum password security requirements for personal mobile devices accessing work email. Unfortunately, this imposes a requirement to frequently change the device pin code which is annoying everyone. Our IT admin wants to remove this requirement while still enforcing a minimum requirement that devices must have a pin code but doesn't know where to find the relevant setting in Azure AD. We don't have any devices enrolled in Intune as that requires a P2 licence which we don't have. Any guidance that I could pass on would be appreciated.464Views0likes1CommentData Retention, Compliance, and Litigation Holds
We recently revamped our data retention policies and now I need to set up everything in M365. In the past, we would enable litigation hold under the user's account. Since that only does email, that is not enough. We are now drastically shortening our retention policy and it's critical that all data for a user is accessible if they were brought into a litigation issue. So if we were subpoenaed, I would "freeze" the users data and then it would be possible to search if we were required 1/2/3 months down the road. Is the best way to do this by starting an eDiscovery search and placing everything on hold but not searching for anything? Then, if we were required to search the account, I would edit that eDiscovery hold to include specific queries? Or maybe I would create a "Litigation Hold" retention policy outside of the new default one that would hold their data indefinitely? That seems like a pain to exclude the user and then add them to the other and probably not efficient. Looking for advice from anyone who does this a lot as Microsoft gives a ton of options.. which is great, but it makes it difficult to know the best way when handling critical data.825Views0likes2Comments