compliance
984 Topics
CSP Program enrollment was DEACTIVATED
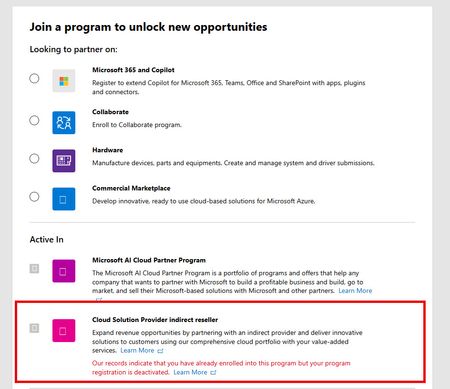
We are an active Microsoft reseller in the AI Cloud Partner Program. We were also enrolled in the CSP Indirect Reseller Program. Last year, our CSP enrollment was DEACTIVATED (not SUSPENDED and not TERMINATED). Of course, we got the typical response on our tickets when asking WHY we were deactivated stating that MS can walk away with no explanation. We BELIEVE it is because we had not sold at least $1000 in the previous 12 month period. Everything I read states that we can re-enroll 12 months after our "onboarding date" which I am not sure what that date is. We were deactivated around October 2025. The "Learn More" link doesn't really help, and focuses mostly on SUSPENSIONS which I believe is different. Even using that link, none of the reasons for a suspension apply to us other than the "program requirements" which is where the $1000 minimum comes from. Can anyone offer some additional guidance here? Thanks!
Poor Partner Center Support
I'm trying to register for the Hardware Program and it shows account suspended (we have not subscribed before), because we simply need a driver to be signed. But after many frustrating weeks this is the final answer we got (8+ weeks, TrackingID#2609140040004120): "Thank you so much for your patience while we reviewed the account. During the reinstatement review, it was confirmed that the account was never registered in the Hardware Program and therefore was never active. Because of this, the existing account cannot be reinstated. To move forward, you will need to start a new Hardware Program enrollment using a new tenant. I understand this may not be the outcome you were expecting, but this will allow you to proceed with a new registration rather than continuing with the previous account. As we have now received the final outcome of the reinstatement review and the required next step has been provided, I will proceed with closing this support ticket." How it the world is this a possible solution since it did not work in the first place. We have a our whole company tied to this tenant, and now I have to register a new one, most likely incur some costs again, just because of some buggy software that cannot resolve the issue??
M365 Admin Center Global Administrator Lockout
Hello Microsoft Community, I am seeking urgent assistance and guidance regarding a critical Microsoft 365 tenant lockout that has been ongoing for several days without a resolution or proper communication from the support team. Our organization manages Microsoft 365 services for a business with more than 200 active users who depend on Microsoft 365 for their daily operations. Issue Description We have been locked out of our Microsoft 365 tenant's administrator account. This prevents us from properly managing our Microsoft 365 environment and restoring normal access to essential business services. Our business-critical data, including important documents and operational information, is stored in SharePoint. The inability to access and manage these services has significantly disrupted our business operations. Microsoft Support Ticket References We have raised multiple support tickets and followed up repeatedly, but the issue remains unresolved. Tracking ID: 2610050040001149 Tracking ID: 2610090010001066 Tracking ID: 2610050040001222 Despite these support cases and repeated follow-ups, we have not received a satisfactory resolution or a clear recovery timeline. Support Experience So Far Following a discussion with the support team, we were expecting a call to assist with unlocking the administrator account and providing a temporary password through the appropriate recovery process. However, we have not received the expected call or a meaningful update. Our main concerns are: Complete loss of access to the Microsoft 365 tenant administrator account. More than 200 users affected by the ongoing incident. Critical business data and documents stored in SharePoint. Multiple support tickets without a concrete resolution. Lack of clear communication regarding the root cause and recovery timeline. No clear escalation path or confirmation of the next recovery steps. Our Concerns We understand that technical issues can occur, but leaving a business-critical environment inaccessible for an extended period without meaningful updates is extremely concerning. We purchase Microsoft 365 licenses through a partner and expect appropriate technical support and escalation assistance when critical incidents occur. Our organization previously used Google Workspace and recommended migrating to Microsoft 365 because of its enterprise capabilities. This incident has seriously affected user confidence and business continuity. If access cannot be restored promptly, we may have to consider alternative email hosting arrangements to minimize further disruption. Request for Assistance I would appreciate guidance from Microsoft engineers, Microsoft 365 administrators, and community members who have experienced similar situations. What is the appropriate escalation process when all available tenant administrator accounts are inaccessible? How can we expedite tenant ownership verification and administrator account recovery? Is there a dedicated Microsoft team that handles critical tenant lockout incidents affecting business operations? What is the recommended recovery process when the administrator cannot access the Microsoft 365 Admin Center? How can we obtain urgent assistance when multiple support tickets and repeated follow-ups have not resulted in a clear resolution? Can the three referenced support tickets be escalated for urgent review by the appropriate Microsoft support team? We are not looking for workarounds that compromise tenant security. We need Microsoft's official recovery process to restore authorized administrative access safely. Microsoft Support Team: If any Microsoft support representatives are monitoring this community, we would appreciate your guidance on the appropriate escalation channel for this incident. We can provide additional information privately through the appropriate official channels. Thank you for your time and assistance. Any guidance that helps us restore our services and protect business continuity would be greatly appreciated. Best regards, Microsoft 365 Tenant Administrator18Views0likes0Comments
Store company account: employment verification closed after appeal limit
I’m the sole owner of a single-member US LLC (Clumsy’s Lab LLC, Missouri) and I’m trying to open a company account through the new Microsoft Store developer onboarding at storedeveloper.microsoft.com. Status: Email verification: ✅ Verified (on our company domain.) Business verification: ✅ Verified via D-U-N-S Employment verification: ❌ “Verification could not be completed. You’ve reached the limit for verification appeals.” The vetting team’s note says our organization “does not currently meet the requirements to pass verification” and the request is closed. No specific reason was given. What I’ve done since: Updated our Dun & Bradstreet record to list me as owner and contact, with the company email Updated the domain registration so the registrant organization is the LLC, with the company email and business address Emailed mailto:email address removed for privacy reasons with documentation The problem: every “Contact support” and “create a ticket” link sends me to partner.microsoft.com, which requires an existing Partner Center account, so I can’t open a ticket. I’m stuck in a loop. I can provide Articles of Organization (naming me as organizer), our IRS EIN letter, and domain ownership records going back to 2024. Could a moderator help reopen the employment verification, or point me to the right team? For a one-person company, I’m not sure what more “employment” proof is possible. I am the company. Thank you!WHY is microsoft support so useless???
I give up at this point. How is it possible for one of the biggest companies in the world to have the worst and most useless support system ever. I'm just trying to get my account back after it got hacked so I can play minecraft. So how is in after sending a paragraph of information about the account and screenshots of receipts and email I received of someone changes the email of the account, it's still not enough information??? The selfhelp system is somehow the worst one I've ever seen and the AI chatbot doesn't even work.59Views0likes0CommentsSecurity Review for Microsoft Edge version 152
We have reviewed the new settings in Microsoft Edge version 152 and determined that there are no additional security settings that require enforcement. The Microsoft Edge version 151 security baseline continues to be our recommended configuration which can be downloaded from the Microsoft Security Compliance Toolkit. Microsoft Edge version 152 introduced 4 new Computer and User settings; we have included a spreadsheet listing the new settings to make it easier for you to find. Starting with version 152 Microsoft Edge is moving to a more frequent release cycle. To better align with the needs of the enterprise customers, the Microsoft Edge security baseline is expected to align with the Extended Stable Channel, which provides major feature updates on an eight-week cadence while continuing to receive security and quality updates between releases. This approach provides organizations with additional time to evaluate and deploy feature changes while ensuring security protections remain current. Why the change? Security baselines are intended to provide guidance for managing security relevant configuration settings, not to track every feature introduced in a browser release. With the move to a two-week release cadence, publishing baseline updates for every release would increase operational overhead while providing limited security benefit. The Extended Stable cadence offers a more practical balance for enterprise customers by allowing additional time for testing and evaluation, while continuing to receive security and critical fixes between major feature releases. By aligning with Extended Stable, we can update the baselines less frequently and focus on publishing them earlier in the release cycle, giving IT administrators more time to review and plan for upcoming changes. Our goal is to make security baseline adoption more predictable and easier to manage while continuing to provide timely security guidance. As a friendly reminder, all available settings for Microsoft Edge are documented here, and all available settings for Microsoft Edge Update are documented here. Please continue to give us feedback through the Security Baselines Discussion site or this post.1.6KViews0likes6CommentsWindows 11, version 26H2 security baseline
Update: The Windows 11, version 26H2 security baseline has been updated to reflect the general availability of Administrator protection. An updated v2 package is now available, and organizations should review and test the existing Administrator protection configuration as appropriate for their environment. You can download the baseline package from the Microsoft Security Compliance Toolkit, test the recommended configurations in your environment, and customize / implement them as appropriate. Summary of Changes This release includes several changes since the Security baseline for Windows 11, version 25H2 to further strengthen enterprise security and align the baseline with current platform capabilities and industry standards. Security Policy Change Summary Printer\Configure Windows Ready Print driver ranking Configured as “Enabled” to reduce reliance on third-party print drivers in the stack, narrowing the overall print driver attack surface. Internet Explorer\Internet Control Panel\Advanced Page\Turn off encryption support Updated from TLS 1.1 and TLS 1.2 to TLS 1.2 and TLS 1.3 to align with current security standards. User Account Control: Configure type of Admin Approval Mode (updated) Configured as “Admin Approval Mode with Administrator protection” to enable Administrator protection. User Account Control: Behavior of the elevation prompt for administrators running with Administrator protection (updated) Configured as “Prompt for credentials on the secure desktop” to require credential verification for administrative elevation. Windows Ready Print driver ranking Configure Windows Ready Print driver ranking" is the newly added setting under Administrative Templates\Printers to control whether Windows prefers the modern inbox IPP class driver over third-party OEM drivers when installing new printers. We recommend enabling this policy to reduce reliance on third-party print drivers in the stack, narrowing the overall print driver attack surface. Note that driver ranking applies when printers are installed via a connection method that supports IPP, such as USB or network multicast discovery. In those cases, if the printer supports IPP, Windows will install using the class driver even if a vendor V3/V4 driver is available. If the printer doesn't support IPP, or is installed directly as a TCP/IP printer, there's no change in behavior. Encryption Support We have updated the policy "Turn off encryption support" to allow only TLS 1.2 and TLS 1.3. Previous baseline releases permitted TLS 1.1 and TLS 1.2; however, TLS 1.1 is now considered obsolete and is no longer recommended for enterprise environments. This change aligns the security baseline with modern cryptographic standards while maintaining compatibility with widely deployed services that support current TLS versions. Administrator Protection (update) Administrator protection is now generally available. Organizations can enable it through Microsoft Intune or Group Policy. Important: Organizations should review and test their existing configuration and adjust these settings as appropriate for their environment. The security baselines for Windows 11, versions 24H2, 25H2, and 26H2 include settings that enable Administrator protection. The following policies are part of the security baseline: User Account Control: Configure type of Admin Approval Mode User Account Control: Behavior of the elevation prompt for administrators running with Administrator protection An updated v2 package has been published for Windows 11, version 26H2, to reflect this change. Please let us know your thoughts by commenting on this post or through the Security Baseline Community.Verification "Authorized" but Partner Center remains deactivated. No support channel reachable.
We are a company seeking help with a Partner Center account state inconsistency (Seller ID available by direct message to a Community Manager or Microsoft employee). Timeline: - Our Windows Hardware Developer Program enrollment was rejected at the Employment Verification stage. - Microsoft Vetting Operations instructed us in writing to update our profile to a company-owned domain and provide domain registration documentation. We complied fully and same-day: registered and verified a company domain on the enrolling tenant, updated the seller contact and company approver to an address on that domain, and supplied registrar documentation. - The verification pipeline re-ran: Email, Identity, and ultimately all stages completed. Legal Info now shows Verification Status: AUTHORIZED. - However, the Partner Center account itself returns "your Partner Center account has been deactivated" on every workspace — Hardware, Programs, and the support wizard — so we cannot file an in-portal support case from the deactivated account. - Email follow-ups to the Vetting Operations thread and to an assigned Dev Center support engineer have gone unanswered for over a week. We hold multiple correlation IDs (most recent: f4fd02fd-d21f-462f-8765-1ea3d6132ad2, 02 Oct 2026). Our read: the account object was deactivated when the earlier application was closed, and was never re-activated when the verification subsequently authorized — a state inconsistency between the vetting record and the account. Ask: could a Community Manager or Microsoft employee escalate this to the team that can re-activate a verified account? The verification work is complete; only the deactivation flag remains, and it is blocking a driver-signing deliverable. We can provide the Seller ID, case numbers, correlation IDs, and full documentation through any private channel indicated. Thank you. Access restricted We're sorry, you don't have permission to access this page because your Partner Center account has been deactivated. For assistance, please contact your Partner Center administrator or support. Correlation ID: f4fd02fd-d21f-462f-8765-1ea3d6132ad2 Correlation vector: leO3sWI4S0K2fExK.4 Time: 02 Oct 2026 22:36:07 +00:00I built a free, open-source M365 security assessment tool - looking for feedback
I work as an IT consultant, and a good chunk of my time is spent assessing Microsoft 365 environments for small and mid-sized businesses. Every engagement started the same way: connect to five different PowerShell modules, run dozens of commands across Entra ID, Exchange Online, Defender, SharePoint, and Teams, manually compare each setting against CIS benchmarks, then spend hours assembling everything into a report the client could actually read. The tools that automate this either cost thousands per year, require standing up Azure infrastructure just to run, or only cover one service area. I wanted something simpler: one command that connects, assesses, and produces a client-ready deliverable. So I built it. What M365 Assess does https://github.com/Daren9m/M365-Assess is a PowerShell-based security assessment tool that runs against a Microsoft 365 tenant and produces a comprehensive set of reports. Here is what you get from a single run: 57 automated security checks aligned to the CIS Microsoft 365 Foundations Benchmark v6.0.1, covering Entra ID, Exchange Online, Defender for Office 365, SharePoint Online, and Teams 12 compliance frameworks mapped simultaneously -- every finding is cross-referenced against NIST 800-53, NIST CSF 2.0, ISO 27001:2022, SOC 2, HIPAA, PCI DSS v4.0.1, CMMC 2.0, CISA SCuBA, and DISA STIG (plus CIS profiles for E3 L1/L2 and E5 L1/L2) 20+ CSV exports covering users, mailboxes, MFA status, admin roles, conditional access policies, mail flow rules, device compliance, and more A self-contained HTML report with an executive summary, severity badges, sortable tables, and a compliance overview dashboard -- no external dependencies, fully base64-encoded, just open it in any browser or email it directly The entire assessment is read-only. It never modifies tenant settings. Only Get-* cmdlets are used. A few things I'm proud of Real-time progress in the console. As the assessment runs, you see each check complete with live status indicators and timing. No staring at a blank terminal wondering if it hung. The HTML report is a single file. Logos, backgrounds, fonts -- everything is embedded. You can email the report as an attachment and it renders perfectly. It supports dark mode (auto-detects system preference), and all tables are sortable by clicking column headers. Compliance framework mapping. This was the feature that took the most work. The compliance overview shows coverage percentages across all 12 frameworks, with drill-down to individual controls. Each finding links back to its CIS control ID and maps to every applicable framework control. Pass/Fail detail tables. Each security check shows the CIS control reference, what was checked, what the expected value is, what the actual value is, and a clear Pass/Fail/Warning status. Findings include remediation descriptions to help prioritize fixes. Quick start If you want to try it out, it takes about 5 minutes to get running: # Install prerequisites (if you don't have them already) Install-Module Microsoft.Graph, ExchangeOnlineManagement -Scope CurrentUser Clone and run git clone https://github.com/Daren9m/M365-Assess.git cd M365-Assess .\Invoke-M365Assessment.ps1 The interactive wizard walks you through selecting assessment sections, entering your tenant ID, and choosing an authentication method (interactive browser login, certificate-based, or pre-existing connections). Results land in a timestamped folder with all CSVs and the HTML report. Requires PowerShell 7.x and runs on Windows (macOS and Linux are experimental -- I would love help testing those platforms). Cloud support M365 Assess works with: Commercial (global) tenants GCC, GCC High, and DoD environments If you work in government cloud, the tool handles the different endpoint URIs automatically. What is next This is actively maintained and I have a roadmap of improvements: More automated checks -- 140 CIS v6.0.1 controls are tracked in the registry, with 57 automated today. Expanding coverage is the top priority. Remediation commands -- PowerShell snippets and portal steps for each finding, so you can fix issues directly from the report. XLSX compliance matrix -- A spreadsheet export for audit teams who need to work in Excel. Standalone report regeneration -- Re-run the report from existing CSV data without re-assessing the tenant. I would love your feedback I have been building this for my own consulting work, but I think it could be useful to the broader community. If you try it, I would genuinely appreciate hearing: What checks should I prioritize next? Which security controls matter most in your environment? What compliance frameworks are most requested by your clients or auditors? How does the report land with non-technical stakeholders? Is the executive summary useful, or does it need work? macOS/Linux users -- does it run? What breaks? I have tested it on macOS, but not extensively. Bug reports, feature requests, and contributions are all welcome on GitHub. Repository: https://github.com/Daren9m/M365-Assess License: MIT (free for commercial and personal use) Runtime: PowerShell 7.x Thanks for reading. Happy to answer any questions in the comments.5.5KViews2likes4Comments