alerts
330 Topics
Hacked Microsoft Account Recovery with Semi Access
I'm at a complete loss and it is infuriatingly ridiculous. I am entirely unable to get a hold of a human being at Microsoft and am being turned down by automated responses nonstop. So here's what's happening: My Microsoft account has been hijacked (obviously not this one) for its valuable Minecraft account and has now been sold. I am logged into my account via my PC, have full access of the main email address, but I have been locked out of my account using the alias email. Whenever I want to log in to my account, it wants to instead send a code to an email address I do not own and can't access. I have tried the Sign-In Helper, the Recovery Form, the hotline, the support email without any result, let alone a non-automated response. I sadly don't have the Recovery Code of my 15 year old-ish account. Since I still have full access of my email address I get updates of security info being changed and what not. Last month a stranger sent me screenshots of someone trying to sell my Minecraft account, for which I myself have received multiple buying offers, and voila yesterday I received notification of my alias mail address changing followed by Minecraft server apps being added to my Microsoft account. While I had already given up retrieving my account, whenever I get notifications my heart sinks a new while some hope sparks up again. Do you people have any idea of what I could do? I don't even rule out legal actions at this point. While I do of course have the email address of the hijacker and the buyer, I fear that contacting them results in me being locked out permanently. I'm just begging to catch the attention of anyone involved with Microsoft. This being walled out with automated responses is killing me.298Views1like3Comments
Is the Security Graph ever going to be brought back?
Over six years ago, Microsoft explored the concept of a Security Graph, with the vision of bringing together insights from across the security ecosystem into a unified relationship-driven platform. The goal was to connect security data, signals, and intelligence from multiple vendors to provide deeper visibility, context, and understanding of complex security environments. Over time, much of this effort was consolidated into the broader Microsoft Graph strategy, which emphasized centralized data access and integration. While that approach delivered significant benefits, the emergence of AI and graph-based intelligence highlights the value of domain-specific models where relationships are intentionally defined, preserved, and analyzed rather than inferred after the fact. I believe the time has come for Microsoft to revisit and revive the concept of the Security Graph. While I understand the rationale behind consolidating security data into centralized platforms to simplify implementation and improve accessibility, the rapid advancement of AI has demonstrated the value of specialized models with purpose-built relationships and context. A dedicated Security Graph would provide significant advantages by explicitly defining relationships between security entities, events, controls, assets, identities, and findings rather than relying solely on correlation and inference. This approach would enable deeper analytics, more accurate investigations, enhanced threat detection, and improved decision-making across the security ecosystem. However, the framework should evolve beyond traditional log aggregation and align with the operational data that security vendors already generate. Each security assessment, validation, or monitoring submission should include structured metadata describing: The objective of the capability or validation being performed. The methodology used, including specific tests executed and the environments, controls, and assets evaluated. The toolset details, including product name, version, identity or service account used, supporting datasets, and systems interacted with during testing. Findings and observed results. Coverage gaps, including tests not completed, areas not evaluated, and data not analyzed. The underlying raw logs and telemetry currently generated and submitted by the tool. To ensure integrity and accountability, all submissions should be cryptographically signed, providing verifiable evidence of who performed the assessment, when it was performed, and what data was collected. With this richer, evidence-based data model, a Security Graph could be constructed that not only enables security teams to trace activities, relationships, and attack paths with greater confidence, but also provides substantial value for risk management, governance, compliance, and audit functions. The resulting graph would move beyond simple event correlation to become a trusted system of record for continuous security validation, assurance, and accountability. Thoughts???169Views0likes1Comment
Microsoft Defender: Problems with correlations in Azure Sentinel
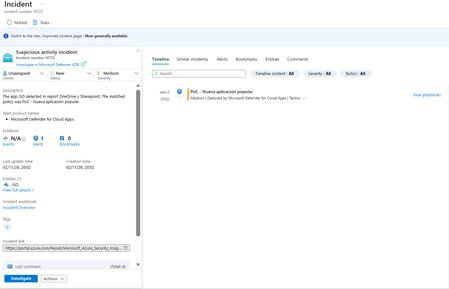
Hi community! Sharing something we've noticed this week, in case anyone else is running into the same thing. Since around October 31, several of our environments have been generating more incidents than before. Many of the automation rules we have deployed are based on the incident title, and they're now "failing" because the alert that creates the incident is being correlated and the incident is getting a different title. On top of that, I can't base these automation rules on the analytics rule name instead, because the alert comes from Defender and that condition isn't available for it in the automation rule. In addition, some incidents from Sentinel analytics rules now show Defender-generated titles, even though they contain only a single alert. For example, the rule "Office365 Sharepoint File transfer Folders above threshold" now generates an incident called "Exfiltration incident involving one user", and "PoC - Nueva aplicación popular" now generates "Suspicious activity incident". .178Views0likes2Comments
How to get alerted on pending items in the Action Center
Good morning all! Part of my daily duties is to ensure that items in the Action Center are acted upon in a timely manner. I have been trying to find ways to be able to be alerted on new items, but there is nothing in Microsoft documentation, or anything that is obvious. I have scoured the internet, where I stumbled upon an old post about having to use a PS script, but there has to be some sort of notification Microsoft can send out on these items?! Since these items are time sensitive, I am having to check constantly for any new soft/hard delete emails.630Views1like1Comment
Windows Forwarded Events connector with Windows Security Events NRT rules
Hello, We are testing Microsoft Sentinel using the official Windows Forwarded Events connector. Environment - Windows Server WEC - Windows Event Forwarding - Azure Arc - Azure Monitor Agent - Windows Forwarded Events connector Everything works correctly. Forwarded security events are successfully ingested into the WindowsEvent table. For example: - Event ID 1102 - Event ID 4732 However, the built-in Windows Security Events NRT Analytics Rules (Content Hub version 1.0.1) query only the SecurityEvent table. Example: NRT Security Event log cleared SecurityEvent | where EventID == 1102 As a result, forwarded events received through the Windows Forwarded Events connector never trigger these NRT rules. Question: Is this expected behavior? Should Windows Forwarded Events customers use a different set of analytics rules (ASIM or other templates), or should these built-in NRT rules also support WindowsEvent? Thank you.1KViews0likes4CommentsYour Sentinel AMA Logs & Queries Are Public by Default - AMPLS Architectures to Fix That
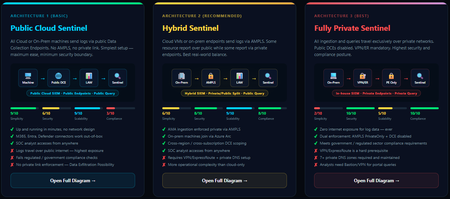
When you deploy Microsoft Sentinel, security log ingestion travels over public Azure Data Collection Endpoints by default. The connection is encrypted, and the data arrives correctly — but the endpoint is publicly reachable, and so is the workspace itself, queryable from any browser on any network. For many organisations, that trade-off is fine. For others — regulated industries, healthcare, financial services, critical infrastructure — it is the exact problem they need to solve. Azure Monitor Private Link Scope (AMPLS) is how you solve it. What AMPLS Actually Does AMPLS is a single Azure resource that wraps your monitoring pipeline and controls two settings: Where logs are allowed to go (ingestion mode: Open or PrivateOnly) Where analysts are allowed to query from (query mode: Open or PrivateOnly) Change those two settings and you fundamentally change the security posture — not as a policy recommendation, but as a hard platform enforcement. Set ingestion to PrivateOnly and the public endpoint stops working. It does not fall back gracefully. It returns an error. That is the point. It is not a firewall rule someone can bypass or a policy someone can override. Control is baked in at the infrastructure level. Three Patterns — One Spectrum There is no universally correct answer. The right architecture depends on your organisation's risk appetite, existing network infrastructure, and how much operational complexity your team can realistically manage. These three patterns cover the full range: Architecture 1 — Open / Public (Basic) No AMPLS. Logs travel to public Data Collection Endpoints over the internet. The workspace is open to queries from anywhere. This is the default — operational in minutes with zero network setup. Cloud service connectors (Microsoft 365, Defender, third-party) work immediately because they are server-side/API/Graph pulls and are unaffected by AMPLS. Azure Monitor Agents and Azure Arc agents handle ingestion from cloud or on-prem machines via public network. Simplicity: 9/10 | Security: 6/10 Good for: Dev environments, teams getting started, low-sensitivity workloads Architecture 2 — Hybrid: Private Ingestion, Open Queries (Recommended for most) AMPLS is in place. Ingestion is locked to PrivateOnly — logs from virtual machines travel through a Private Endpoint inside your own network, never touching a public route. On-premises or hybrid machines connect through Azure Arc over VPN or a dedicated circuit and feed into the same private pipeline. Query access stays open, so analysts can work from anywhere without needing a VPN/Jumpbox to reach the Sentinel portal — the investigation workflow stays flexible, but the log ingestion path is fully ring-fenced. You can also split ingestion mode per DCE if you need some sources public and some private. This is the architecture most organisations land on as their steady state. Simplicity: 6/10 | Security: 8/10 Good for: Organisations with mixed cloud and on-premises estates that need private ingestion without restricting analyst access Architecture 3 — Fully Private (Maximum Control) Infrastructure is essentially identical to Architecture 2 — AMPLS, Private Endpoints, Private DNS zones, VPN or dedicated circuit, Azure Arc for on-premises machines. The single difference: query mode is also set to PrivateOnly. Analysts can only reach Sentinel from inside the private network. VPN or Jumpbox required to access the portal. Both the pipe that carries logs in and the channel analysts use to read them are fully contained within the defined boundary. This is the right choice when your organisation needs to demonstrate — not just claim — that security data never moves outside a defined network perimeter. Simplicity: 2/10 | Security: 10/10 Good for: Organisations with strict data boundary requirements (regulated industries, audit, compliance mandates) Quick Reference — Which Pattern Fits? Scenario Architecture Getting started / low-sensitivity workloads Arch 1 — No network setup, public endpoints accepted Private log ingestion, analysts work anywhere Arch 2 — AMPLS PrivateOnly ingestion, query mode open Both ingestion and queries must be fully private Arch 3 — Same as Arch 2 + query mode set to PrivateOnly One thing all three share: Microsoft 365, Entra ID, and Defender connectors work in every pattern — they are server-side pulls by Sentinel and are not affected by your network posture. Please feel free to reach out if you have any questions regarding the information provided.1.2KViews3likes2CommentsSentinel Foundry - MCP Server (Github Community Release)
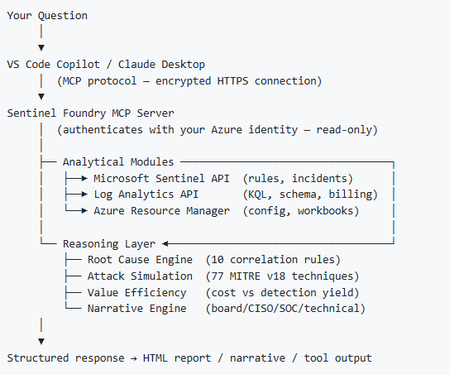
I’ve been cooking something that a lot of people in SOC have been struggling with — especially on the engineering side of Microsoft Sentinel. Thanks to the Microsoft Security team for shaping the capabilities of Sentinel even better with Sentinel Data Lake & Modern SecOps. Today’s the day I can finally share it. Note: This is not an official Microsoft product, but it is designed to make the Sentinel Build even better (complement) with much more intelligence. 🚀 Sentinel Foundry is now in public preview with 43 tools. (Sentinel Foundry - MCP Server) It’s an MCP server built to act like the brain of a strong Sentinel engineer — helping make building, improving, and operating Sentinel far more practical, faster, and honestly more enjoyable. For a lot of teams, the challenge is not understanding what Sentinel can do. The hard part is the engineering work around it: -> Deciding what data should actually be ingested -> Building a clean, scalable Sentinel foundation -> Writing useful detections instead of noisy ones -> Balancing security value with cost -> Turning ideas into deployable engineering outputs That is exactly why I built Sentinel Foundry to help communities grow stronger. It helps with the real engineering tasks behind Sentinel — from architecture thinking to detection design, deployment planning, ingestion strategy, automation ideas, and many of the workflows outlined in the GitHub project. How does it work? Here’s one of the flagship prompts I ran with it: “Give me a complete security posture report for our workspace. Score each pillar and tell me what to prioritise.” And within seconds, it produced a structured engineering blueprint that would normally take a lot longer to pull together manually. You can see the example prompts here in what it can do: https://github.com/prabhukiranveesam/Sentinel-Foundry#what-can-it-do I want building Sentinel to feel less like repetitive engineering overhead — and more like real security engineering that is fast, creative, and enjoyable. If you work with Sentinel as a SOC L2 analyst, engineer, detection engineer, consultant, or architect, I’d genuinely love for you to try it and tell me what you think. 🔗 Public Preview: https://github.com/prabhukiranveesam/Sentinel-Foundry This is just the start of an AI era — and I’m excited to keep shaping it with more powerful features over the coming days. This is very easy to set up and will be available to all of you at no cost during this month as part of the public preview, and your feedback is extremely valuable to shape this as a powerful solution.1.4KViews0likes2CommentsAre you getting the most out of your Azure Log Analytics Workspace (LAW) investment?
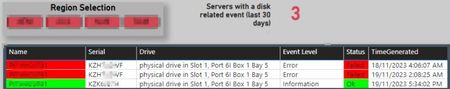
Using a LAW is a great way to consolidate various types of data (performance, events, security, etc.) and signals from multiple sources. That's the easy part - mining this data for actionable insights is often the real challenge. One way we did this was by surfacing events related to disks across our physical server estate. We were already sending event data to our LAW; it was just a matter of parsing it with KQL and adding to a Power Bi dashboard for additional visibility. The snippet from the Power Bi dashboard shows when the alert was first triggered and when the disk was eventually replaced. Here's the KQL query we came up with. let start_time=ago(30d); let end_time=now(); Event | where TimeGenerated > start_time and TimeGenerated < end_time | where EventLog contains 'System' | where Source contains 'Storage Agents' | where RenderedDescription contains 'Drive Array Physical Drive Status Change' | parse kind=relaxed RenderedDescription with * 'Drive Array Physical Drive Status Change. The ' Drive ' with serial number ""' Serial '"", has a new status of ' Status '. (Drive status values:'* | project Computer, Drive, Serial, Status, TimeGenerated, EventLevelName You can of course set up alerting with Alerts for Azure Monitor. I hope this example helps you get more value from your LAW.1KViews2likes5CommentsSentinel - Defender XDR KQL Queries Library
Hello all, I’ve been building something over the past few weeks that I think the security community might find useful. https://goxdr.fyi is a searchable KQL query library for Microsoft Sentinel and Defender XDR. The name comes from a nickname my colleagues gave me (GoX) combined with XDR. I also picked up https://goxdr.fyi as a short and easy to remember domain for it. You can check it out here: https://goxdr.fyi The idea came from my own day to day work as someone working in IAM and SOC operations. I constantly find myself writing and refining KQL queries for threat hunting, detection engineering and incident investigation. Over time I realized I had a growing collection of queries that I kept going back to and I thought why not make these available to others? It currently has 117 queries covering identity security, BEC/AiTM detection, NTLM and LDAP attack hunting, OAuth governance, AI/Copilot security, Sentinel alert trending, SOC performance metrics and more. Some of these queries are ones I wrote from scratch based on real scenarios I encountered in production environments. Others are community queries I tested and validated in my own setup. Only the ones I found genuinely useful and that actually worked against real data made it in. Each query comes with a description explaining what it detects and why it matters, along with severity levels, platform tags (Sentinel, XDR or both) and a copy button so you can paste it directly into Advanced Hunting or use it as the basis for an Analytics Rule. The site is open source, hosted on GitHub Pages and licensed under CC BY 4.0. No sign-up, no paywall, no tracking. The source is available. I’ll keep adding queries as new scenarios come up. If there’s enough interest I’m also considering adding Cortex XQL queries for Palo Alto environments. Suggestions, feedback or ideas for new detections are always welcome. Feel free to reach out. Thanks404Views1like0CommentsVaihdoit uuteen puhelimeen. Authenticator ongelma
Vaihdoit uuteen puhelimeen. Microsoft Authenticator ei ole enää saatavilla vanhalla laitteellasi. Et voi kirjautua Microsoft 365 -työtilillesi, koska MFA-vahvistus vaaditaan. Sinulla ei ole pääsyä mihinkään vaihtoehtoiseen todennusmenetelmään. Tarvitset apua suomeksi, jos mahdollista.551Views0likes1Comment