tpm
8 Topics
Windows 11 Pluton TPM AIK Enrollment Fails with HTTP 404 — The authority does not exist
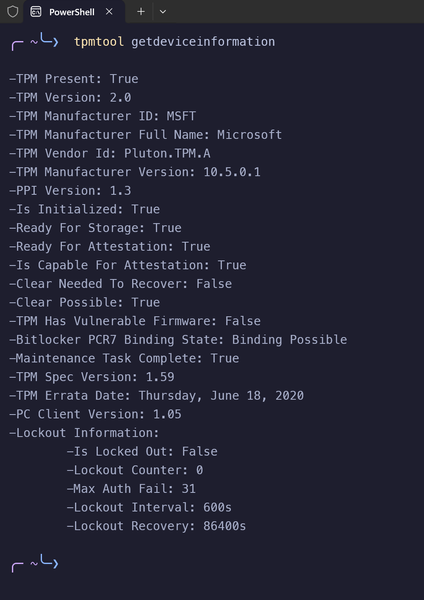
Hello everyone, I'm experiencing a Windows TPM/AIK certificate enrollment issue on my ASUS TUF Gaming A14 (FA401WV), and I'm looking for guidance from someone familiar with Windows TPM attestation. System information Laptop: ASUS TUF Gaming A14 FA401WV CPU: AMD Ryzen AI 9 HX 370 OS: Windows 11 Home Single Language, 64-bit, build 26300.9711 BIOS: Version 322, confirmed by ASUS as the latest available for my model TPM: Microsoft Pluton TPM 2.0 Secure Boot: Enabled and active Problem Call of Duty's Secure Attestation Wizard passes the TPM 2.0 and Secure Boot checks but fails to generate the required attestation key. It reports a BIOS firmware update requirement even though my BIOS is already up to date. To investigate the underlying issue, I ran the Windows command below from an elevated Command Prompt: certreq -enrollaik -config "" The request fails during GetCACaps with: HTTP status: 404 Not Found Windows error: 0x80190194 Message: "The authority does not exist." The request is directed to a device-specific Microsoft AIK enrollment endpoint under microsoftaik.azure.net. The failure happens before certificate enrollment completes. Troubleshooting already performed Verified that Windows detects the TPM and reports it as ready. Confirmed that Secure Boot is enabled and active. Checked with ASUS and confirmed that BIOS version 322 is the latest available. Retried AIK enrollment using my phone's mobile hotspot; the same HTTP 404 error persists. Tried the game's enrollment utility, which also produced 0x80072EFD (WinHTTP cannot connect) on a separate attempt. Another laptop using a Microsoft Pluton TPM successfully completed the same certreq -enrollaik -config "" command. I understand that this comparison does not establish the root cause, but I am including it as potentially useful context. Questions Is this a known issue with Windows AIK certificate enrollment for Microsoft Pluton TPMs? What supported diagnostics can help determine why the device-specific AIK enrollment authority returns HTTP 404? Is there an official Microsoft support or Feedback Hub route for getting this investigated by the appropriate Windows TPM/AIK enrollment engineering team? The laptop manufacturer confirmed that BIOS version 322 is the latest available for my device. I can provide the full command output and diagnostic logs through an appropriate support channel. I have intentionally left out device-specific identifiers from this public post. Thank you for any guidance.177Views2likes2Comments
Found an odd hang that leaves no record on host when triggered.
I have a really old system, and I bought a TPM 2.0 module to use on it. I hadn't realized all the details of using it (like needing to reinstall fresh to change secure boot mode). I assumed I could just leave it installed until I wanted to go through the full effort of activating it. And hoped it might be useful even if full secure boot mode wasn't being used. Now I've realized my host will start to hang for no reason with that module installed. With some odd symptoms/details too. I'll outline those later. I'm guessing this is a "not supported" or "don't care" from Microsoft, but figured I should mention it in case I'm wrong. And they see their own part in the bug as bad enough to do something about. Since there isn't any obvious explanation of what happens in the OS (event log explanation, etc), beyond that the system didn't shutdown properly and/or a bugcheck I couldn't decode anything from (system just hangs, doesn't reboot as it should, no debug dmp, etc). ------------ I can physically install the module and not see a hang for a while (days/weeks?) which makes it hard to connect the result to the cause. Then after using my computer for 8-10 hours already (around midnight or 1am at least a couple times now), it'll decide to hang. Then every reboot after that will hang after 1-3 minutes from login to desktop (unless in safe mode then sits indefinitely, or it lasted slightly longer in normal boot mode after I disabled all non-Microsoft services). I can do nothing except log in (or try to use it to open a bunch of stuff, no difference) then it'll hang. No obvious pointer in event log to what sub-system or event or a reason the issue happened. System is from circa 2017. i7-4790k CPU, z97 motherboard that only had a TPM header back then. Bought a semi-recent TPM 2.0 module off Amazon a couple/three years ago that matched the Gigabyte module type I couldn't buy direct anymore (Gigabyte had 3 different things that looked very similar). OS installed a long time ago, using mostly default BIOS options from before I knew anything about what they meant ("Other OS" not Windows 8 mode, etc). If module is installed then the BIOS says secure boot enabled, even when I disabled the TPM setting I could manually adjust. OS says secure boot was not enabled (followed directions online to look for some particular mode, like SC6?). I spent a lot of time trying to fix various oddities, like how Intel's XTU overclocking/BIOS settings tool left behind a service after I'd uninstalled it (pretty sure is connected to a "watchdog" to reset BIOS and reboot). Turning off Samsung's Optune cache performance feature. And tweaking various BIOS settings to see if they impacted anything, like disabling power saving modes, or various boot options (UEFI only vs Legacy only vs ...). Sadly managed to truly break my hardware in that debug/tweaking process. But this hanging issue was happening BEFORE that damage was done. Basically I've rarely used the hardware jumpers to clear CMOS before (removing the battery instead usually, or clear from inside BIOS), and I tried to do both but had it plugged in to AC power still accidentally. Saw a spark and it turned itself on when I shorted the pins. After that it was too late to do anything. Now only the CPU attached PCIe lanes seem to work. Meaning the 2 x 16x slots that'll run at 8x or above (GPU in one, and NIC or wifi in the other). I had to disable the onboard NIC and XHCI in BIOS to let my keyboard and mouse work after booting (outside BIOS). They wouldn't even light up (Logitech things I've had for ages now). And now the boot options include 3 boxes with odd, mostly white, hash marks covering the whole width of the screen. And there was some weirdness with duplicate names there (two Microsoft boot loaders pointing at the same drive entry, one at top and another much further down... below those cross hatched options). But my 5 internal SATA drives all seem to work still (2 SSD, 3 HDD). I don't expect Microsoft to pay for anything, but they're the only ones who could improve this situation for future users. The whole TPM/secure boot feature feels ugly and hard to understand. And anything that hangs the computer should be obvious/explicit in the log entries beforehand (save them with a flush and pause a little). That was another area I wasted time on (adjusting page file sizes manually, changing dump types, etc). Yes, I have the free ESL additional updates enabled for this system (1 year more of security only patches), and installed.230Views0likes5CommentsBitLocker Network Unlock Question
I set up network unlock for two servers in our network as a test for a future deployment of BitLocker. Both HP's. One is a DL 360 Gen9 server with aftermarket TPM, the other is a DL360 Gen11 with onboard/HP TPM. Configured first NIC on both boxes for DHCP. Just to test things, I unplugged NIC1 but kept NIC2 plugged in on the Gen11 server and rebooted. It prompted for a PIN on boot up (expected behavior). Did the same test on the Gen9 server and it boots straight into the OS (unexpected behavior). As a further test, I kept NIC1 unplugged and then unplugged NIC2, rebooted and got prompted for a PIN (as expected since box was completely off network). Does anyone have any ideas why this is happening? Could it have something to do with the aftermarket TPM? From what I've read network unlock requires the first NIC to be DHCP so it can communicate with the WDS server and allow network unlock to work. Could it be something with the NIC's on the Gen9 server? I'm at a loss to explain this behavior. Hoping someone may have some insight. TIA556Views0likes3Comments
FSLogix Problem with Microsoft.AADPluginBroker
We have a few on prem windows 2022 RDS farms using fslogix and outlook. We are bashing our heads against the wall because of the this 58tm1 problem. Every once in a while (5 times a day) a user will get a 58tm1 error while trying to open outlook, we usually fix the problem by deleting the Microsoft.AAD.BrokerPlugin which would fix things for a short while, because we've tried everything else out there, nothing works. Every possible settings combination, registry fixes etc... Newest fslogix versions (hello 25.09) do not fix anything but break everything (this entire branch has a nasty bug which would create temporary profiles and fill every storage space available). Let me know any possiblity to fix this =)1.4KViews1like5CommentsTPM Warning Message during Device Wipe
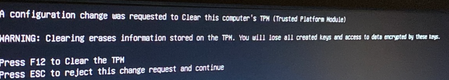
Dear all, When we initiate Intune device wipe (not Autopilot reset) on the Dell PC, it prompts a TPM clear message on the reboot. Usually we will just hit F12 to proceed with the device wipe and Autopilot. However, sometimes we need a fully unattended workflow for our Kiosk PC setup. This prompt is preventing us to achieve a 100% zero touch experience. Is there a way to fix this via Intune? Thanks,9KViews0likes3Comments