security and compliance
53 Topics
Microsoft Copilot 365 Personal Premium limits
In my Copilot Notebook, I deliberately loaded 20 PDF files in order to test Copilot’s grounding behavior across the full set of available references. At the time this testing setup was created, 20 references represented the effective grounding limit described for Copilot Notebooks, meaning that these references were expected to form the source base used by Copilot when generating grounded responses. The references consisted of fully functional, original academic textbooks containing relevant and up-to-date scientific information, mostly published within the last ten years. Importantly, the sources do not differ from one another in terms of accessibility, file type, availability, or how they were added to the notebook. They are all PDF files, they are all available in the same environment, and there is no obvious difference in access conditions that would explain why some are consistently used while others are repeatedly treated as inaccessible, unavailable, summarized, or skipped. The purpose of the test was therefore not simply to see whether Copilot could access 20 files, but whether it could actually ground its answers in the complete reference set when explicitly instructed to analyze all available sources. Despite this, in approximately 99.9% of my tests, Copilot appears to ground its responses in only 3 to 5 of the 20 available references, often repeatedly using the same documents. When I ask what happened to the remaining sources, Copilot gives different explanations. Sometimes it says that it does not have access to certain files. Sometimes it says that it only received a summary of the file. Sometimes it says that a step involved in retrieving or processing the information failed. The way Copilot explains this often makes it sound as if access to the uploaded files depends on some external or intermediate system, rather than being something Copilot itself can directly control. This is difficult to understand from a user perspective because the files are already uploaded into the Copilot environment and were specifically provided as source material for analysis. The practical result is that a task explicitly requesting analysis of 20 sources often produces an answer based on only 3 to 5 of them. For academic or research use, this is a serious limitation. If 15 to 17 out of 20 carefully selected sources are not actually examined, then the final synthesis cannot realistically represent the full source base. This also creates uncertainty about what Copilot means when it claims to have used the provided materials. My question to Microsoft is: Is there a technical limit on how much information Copilot can actually retrieve, open, and analyze from uploaded files during a single task or session? If such a limit exists, what is that limit? And why, when 20 valid PDF sources are uploaded and Copilot is explicitly instructed to analyze all of them, does it so often appear to open only 3 to 5 files, while describing the others as inaccessible, summarized, or unavailable because some retrieval step failed?52Views0likes0CommentsMicrosoft Copilot 365
To Microsoft: Serious Concerns Regarding the Actual Capabilities of Microsoft Copilot Microsoft, After 12 consecutive days of intensive testing of Microsoft Copilot, for approximately eight hours per day — around 96 hours of practical use in total — I have serious concerns about the accuracy of the way Copilot's functions and capabilities are described and presented by Microsoft. What I have observed in actual use is repeatedly and substantially different from what the product is presented as being capable of doing. This conclusion is not based on a single unsuccessful prompt, an isolated error, or a short test. It is based on repeated testing over many days, involving continuous academic, analytical, document-based, and multi-step tasks. One of the most serious problems is Copilot's inability to reliably maintain and use conversational context even within the same active session. For example, Copilot can generate a substantial piece of text and, in the immediately following interaction, claim that it cannot see or access that same text. It may ask the user to provide again information or content that Copilot itself generated only one response earlier. This makes it impossible to rely on the system for genuine sequential work. During testing, the same general problem has appeared in different forms: Copilot fails to return reliably to earlier tasks, loses access to information already established within the conversation, fails to connect consecutive instructions, and sometimes behaves as though previous parts of the same active session do not exist. This is particularly serious when Copilot is used for academic or research work. A workflow may require the system first to generate or analyse material, then classify it, compare it with another part of the work, identify its sources, reorganise it, and finally continue developing it. If Copilot cannot reliably access the result of the immediately preceding step, such a workflow becomes fundamentally unreliable. After approximately 96 hours of direct testing, it is increasingly difficult to regard these problems simply as occasional technical limitations. The discrepancy between Microsoft's descriptions of Copilot and the behaviour actually observed during sustained use is substantial enough to raise a much more serious question: whether the functions and capabilities attributed to Copilot in Microsoft's product descriptions accurately represent what the system can actually and reliably do in normal use. From the user's perspective, the current experience creates the impression that Microsoft's claims about Copilot's capabilities are misleading. A capability should not be considered a genuine product capability merely because the system can occasionally perform it under favourable conditions. If a feature is presented to users as part of the product's functionality, users should reasonably be able to expect that functionality to operate consistently enough to be relied upon. After 12 days of testing, that has not been my experience. The difference between the advertised or described capabilities and the actual behaviour of Copilot is not minor. In several fundamental areas — particularly conversational continuity, access to previous work within the same session, multi-step task execution, and reliable reuse of previously generated content — the practical experience does not correspond to the expectations created by Microsoft's descriptions of the product. After nearly 100 hours of testing, I am therefore questioning not simply the quality of Copilot, but the accuracy and transparency of Microsoft's representation of what Copilot is actually capable of doing. If Microsoft describes Copilot as possessing capabilities that repeatedly cannot be reproduced in sustained real-world use, then the issue is no longer merely whether Copilot occasionally makes mistakes. The issue is whether users are being given an accurate representation of the product they are being asked to use and pay for.62Views0likes0Comments
Bitlocker key requested on the boot, but I don’t have any key
My laptop (Windows 10, version 22H2, build 19045), that I have been using more than 6 years already, suddenly started asking for the BitLocker recovery key at startup, which is blocking access to the system entirely. What I've already checked/tried: - Checked account.microsoft.com/devices/recoverykey while signed in with my Microsoft account, no key appears for this device. - Contacted Microsoft Support directly, they said they can no longer assist with Windows 10 issues and suggested posting here instead. Is there any way to recover access to this drive?420Views0likes3CommentsWhat it looks like: Trusted, compliant AI systems at scale
As AI systems move into production, the risk landscape expands beyond traditional app security. Examine emerging threats like prompt injection, data leakage, and autonomous tool misuse—and hear ways to mitigate threats using a defense-in-depth strategy. Find out how to apply layered controls across identity, data protection, orchestration, and runtime environments to keep AI systems secure and controllable. AI security and observability are essential for building trusted, compliant AI systems at scale. That's why we'll also cover how traceability, safety monitoring, and auditability help you maintain trust, prove compliance, and operate with confidence in real-world conditions. How do I participate? Select Add to Calendar to save the date, then click the Attend button to save your spot, receive event reminders, and participate in the Q&A. Not able to attend live? This session will be recorded and available on demand shortly after airing. Just announced! Live Q&A will also be available July 29 from 9:00-10:00 AM SGT (UTC+8) to support attendees in Asia and western Australia. Don't see Attend or Add to Calendar? Sign in to the Tech Community to join the conversation. Organizational policies preventing you from signing in to the Tech Community? Use a personal account or tune in on LinkedIn. This session is part of Path to production for agents: a Microsoft Azure AI Tech Accelerator. View the full agenda for more actionable strategies to help you deliver secure, compliant, and high-performing AI solutions across your organization.789Views0likes4CommentsSCCM PXE Boot Deep Dive – Backend Flow & DP Migration
SCCM PXE Boot Deep Dive – Backend Flow & DP Migration I recently worked on a Distribution Point migration and noticed PXE requests were still routing to the old DP due to DHCP/IP helper configuration. I put together a deep dive explaining: PXE flow (DHCP and TFTP sequence) Role of Distribution Points What changes during DP migration Common failure points One key takeaway: PXE issues are almost always network and routing related, not SCCM itself. Curious how others are handling PXE in large environments. Are you standardizing on IP helpers or still using DHCP options? Full article: http://SCCM%20PXE%20Boot%20Deep%20Dive%20–%20Backend%20Flow%20&%20DP%20Migration268Views0likes1CommentIn Case You Missed It: Frontier Transformation and Wave 3 of Microsoft 365 Copilot Announcements
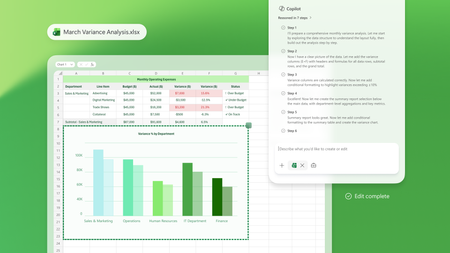
March brought a major set of Frontier Transformation and wave 3 of Microsoft 365 Copilot announcements across Microsoft 365 Copilot, Copilot Chat, and agents—all focused on helping people move faster from intent to action and helping organizations scale AI responsibly. If you missed any of the updates, here’s a quick recap of what’s new and why it matters. Copilot Transforms Knowledge Work These updates deepen how Copilot shows up inside the flow of work—grounded in your content, context, and tools. Word, Excel, and PowerPoint Agents From Copilot Chat, users can ask Word, Excel, or PowerPoint agents to create content, take next steps, or execute tasks, helping them move from intent to action without copying and pasting or switching contexts. 👉 Learn more Edit with Copilot in Word, Excel, and PowerPoint Copilot now creates, edits, and refines content directly inside Word, Excel, and PowerPoint, grounded in the context of a user’s work through Work IQ, so people can iterate and improve content without leaving the app they’re working in. 👉 Learn more Sequences shortened for demonstration purposes. Copilot Chat in Outlook Copilot Chat in Outlook enables users to draft and refine emails, manage calendars and RSVPs, and use the Outlook email widget to take action directly from chat, streamlining everyday communication and scheduling tasks. 👉 Learn more Outlook customer calendar instructions & proactive RSVPs Copilot finds available meeting times, sends invites, and keeps calendars up to date based on custom instructions, notifying users of changes directly in chat to reduce manual coordination. 👉 Learn more Copilot Cowork Built with Anthropic, Copilot Cowork brings a multimodel approach to Microsoft 365 Copilot—so your work isn’t tied to a single model. Cowork moves Copilot beyond prompts into long‑running, multi‑step work. With full awareness of your work context through Work IQ, it lets you delegate meaningful work and stay informed as it progresses. 👉 Learn more Claude Sonnet available in Copilot Chat Users can select Claude models directly in Copilot Chat, alongside next‑generation OpenAI models, bringing leading models from multiple providers into a single Copilot experience. 👉 Learn more Dataverse in Work IQ Work IQ connects signals from Microsoft 365—including documents, meetings, email, and chat—and will soon access operational data in Dataverse through Copilot in Dynamics 365 and Power Apps, bringing work context and business data closer together. 👉 Learn more Work IQ Memory (Chat History) Work IQ Memory enables more relevant, personalized Copilot responses shaped by a user’s work and Copilot chat history over time. 👉 Learn more Extensibility: Work IQ API / MCP Work IQ APIs provide access to production‑ready AI capabilities that work directly with enterprise work context, enabling extensibility through APIs and MCP. 👉 Learn more Launch Demo Copilot in Dynamics 365 & Power Apps Microsoft 365 Copilot is accessible directly within Dynamics 365 Sales, Customer Service, and Power Apps, extending Copilot experiences into business applications where operational work happens. 👉 Learn more Agents That Help Run the Business These announcements focus on building, deploying, and scaling agents across the enterprise. Apps SDK The Apps SDK provides tools to build ChatGPT apps based on the MCP Apps standard, with additional ChatGPT functionality to support agent and Copilot experiences. 👉 Learn more Model Context Protocol (MCP) Apps MCP Apps turn Copilot from a text interface into a governed, interactive execution layer by surfacing interactive app experiences directly in Copilot Chat. 👉 Learn more Apps in Agents: Outlook, Dynamics 365, and Power Apps Agents can bring Outlook, Dynamics 365, and Power Apps directly into chat, allowing users to review information and take action without leaving the conversation. 👉 Learn more Agent Recommendations in Microsoft 365 Copilot When users prompt Microsoft 365 Copilot, the system analyzes intent and recommends an installed, IT‑approved agent directly in the flow of work, making agents easier to discover and use at scale. 👉 Learn more Evaluate agents in Copilot Studio Copilot Studio provides structured, repeatable testing to help catch issues early, reduce the risk of bad answers, and maintain agent quality as agents evolve. 👉 Learn more Visibility, Governance, and Control at Scale As agent usage grows, these updates help organizations move from experimentation to enterprise readiness. Agent 365 Agent 365 serves as the control plane for agents, helping organizations move from experimentation to enterprise‑scale operations by enabling them to observe, govern, and secure agents. 👉 Learn more Microsoft 365 E7: The Frontier Suite Microsoft 365 E7 unifies Microsoft 365 E5, Microsoft 365 Copilot and Agent 365 into a single solution powered by Work IQ and integrated with the productivity apps and security stack customers already rely on. It includes Microsoft Entra Suite and advanced Defender, Intune and Purview security capabilities, delivering comprehensive protection across agents and employees. 👉 Learn more To explore what’s available now—and what’s coming next—visit the Microsoft 365 roadmap and related announcement blogs. 👉 Explore the roadmap8.4KViews3likes1CommentSYSTEM CENTER IMPLEMENTATION & LICENSING Guide
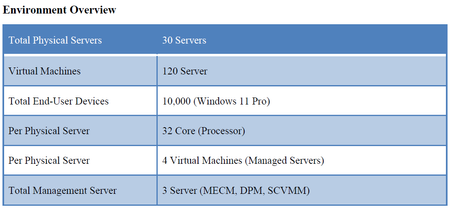
Dear Microsoft Community, Our organization is planning to deploy a comprehensive IT management solution using the Microsoft System Center Suite. The goal is to streamline infrastructure operations, enhance backup and recovery, manage both virtual and physical resources, oversee endpoints, and maintain security and compliance. We need guidance regarding the number and type of licenses required, specifically Client Management Licenses (CML), Server Management Licenses (ML), and System Center Suite licenses.1.1KViews0likes5CommentsSecurity and governance innovations for Microsoft 365 Copilot and agents from Ignite 2025
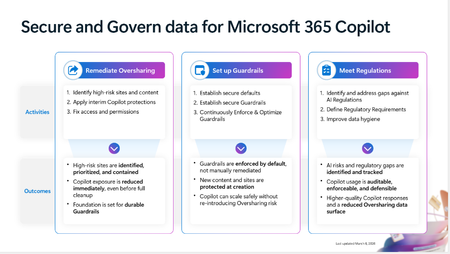
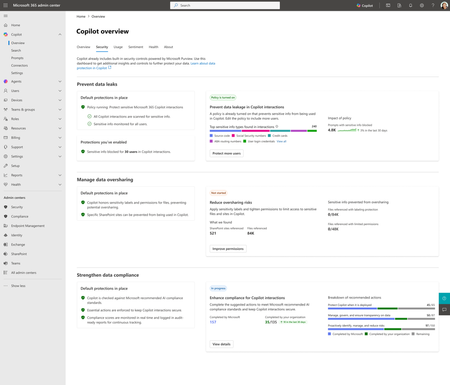
Microsoft 365 Copilot is built on a foundation of trust established through our commitments to protect customer data and the controls we make available directly to customers. We’re excited to share the latest updates to these security and governance tools, designed to help you: Gain a unified view of key security and governance features as a Copilot/IT admin Block sensitive data from Copilot processing or sent as web queries Address oversharing through automation and greater visibility The latest security and governance updates introduce the following tools and features: Purview value integrated in the Microsoft 365 admin center Purview Data Loss Prevention for Microsoft 365 Copilot to safeguard prompts Purview Data security posture management Data risk assessments: item-level investigation and remediation SharePoint Advanced Management (SAM) Content management assessment SAM Permission report for a given user SAM Agent insight report SAM Catalog management SAM Delegating control to site administrators allows site admins to manage Restricted access control (RAC) and Restricted content discovery (RCD) SharePoint Admin Agent Microsoft Baseline security mode Be sure to watch the Ignite session BRK 293 - From oversharing to oversight for more details and demos of many of these new capabilities! Unified view of key security features As a Copilot and IT admin managing the security and governance of Copilot, you need a unified view to see key security and governance features and take actions. At Ignite 2025, we announced that Microsoft Purview value is now integrated directly into the Microsoft 365 admin center (MAC). Now available in Public Preview. The Copilot overview page now offers a Security tab, where you can click on cards to prevent data leakage, manage data oversharing, and strengthen data compliance, directly in the MAC. Block sensitive data from processing Many of you have expressed concerns about sensitive data being processed by Copilot or sent as web queries through a web search. Last year, we announced Microsoft Purview Data Loss Prevention (DLP) for Microsoft 365 Copilot (now Generally Available) to block Copilot from processing files and email with specific sensitivity label. This year, we are thrilled to extend the capability of DLP for Copilot to safeguard prompts that contain sensitive data. Now available in Public Preview. We are also excited to share that Purview DLP for Copilot prompt is available to all users of Microsoft 365 Copilot and Copilot chat! Purview DLP for Copilot prompt provides real-time control to help you mitigate data leakage and oversharing risks. It prevents Microsoft 365 Copilot, including pre-built agents in Microsoft 365 Copilot, and Microsoft 365 Copilot Chat, from returning a response when the prompt contains sensitive data. This feature helps to ensure sensitive data is not used for internal grounding or sent through web searches. Microsoft Purview Data Loss Prevention for Microsoft 365 Copilot to safeguard prompts blocking responses to questions around Project Wingtip, as Project Wingtip is on the organization’s sensitive information block list Automation and visibility to address oversharing As part of Microsoft’s commitments and controls, Copilot responses only contain data the user has permission to access, but oversharing can still happen regardless of Copilot use. Oversharing happens when an employee has been granted access to information and files that aren’t necessary for them to do their job. It’s generally an accidental oversight occurring when users share files too broadly, or when files aren’t protected in a way that persists regardless of location. To help customers address oversharing for a Microsoft 365 Copilot deployment, we published the Oversharing blueprint, powered by two powerful tools: Microsoft Purview, and SharePoint Advanced Management - included in your Microsoft 365 Copilot license. Last year we introduced Microsoft Purview Data security posture management for AI Data risk assessment to address oversharing concerns. This year, we expanded Data risk assessments to include item-level investigation and remediation. Now, in addition to identifying sharing links across SharePoint sites, this enhanced capability enables bulk remediation by allowing admins to remediate or disable overshared links at scale. This helps organizations proactively reduce data exposure, strengthen compliance posture, and ensure sensitive files are only accessible to the right people. Now available in Public preview. SharePoint Advanced Management (SAM), included in your Microsoft 365 Copilot license, concentrates on helping you manage content sprawl and clutter, control permissions and content access, and automate housecleaning chores like making sure all your sites have owners, content is attested on a continuous basis, and provides targeted audit capabilities by tracking changes in the tenant configurations. We’re excited to share these new SAM features: Content management assessment evaluates and improves content management with a single click to identify content risks, ensure compliance, and maintain data integrity. Generally Available. Permission report for a given user provides a detailed overview of all SharePoint and OneDrive access points, highlights oversharing risks, and enables admins to quickly identify and fix risky permissions across the organization for a given user. Generally Available. Agent insight report shows how agents interact and access SharePoint sites and OneDrive accounts, and allow admins take governance actions to manage these agents. Generally Available. Catalog management defines organizational content clusters for targeted actions and automatically groups SharePoint sites using existing sites and user properties to enable governance with precision and at scale. Available in Public Preview. Delegating control to site administrators allows site admins to manage Restricted access control (RAC) and Restricted content discovery (RCD). Available in Public Preview. We’ve also heard many of you request support in working with the breadth of admin tools, reports and capabilities available in SharePoint—so we were especially excited to announce SharePoint Admin Agent, designed for administrators that are tasked with the responsibility of insuring that their organizational content is governed properly in the AI era, with the help of AI. Now available in public preview. The SharePoint Admin Agent removes the need for you to know what SAM reports to trigger, how to read the reports, what actions to take. Now all you need to know is what problem you are trying to solve. The SharePoint Admin Agent will be equipped with skills to help you manage permissions, storage, lifecycle and access to start with, but we have much more planned for the future. Baseline security mode The adoption of AI can accelerate the ability for malicious actors to exploit configuration gaps, specifically legacy configurations that can be the most vulnerable, in your enterprise environment. To support security administrators with this challenge, we introduced Baseline security mode, which applies Microsoft-recommended security settings across Office, SharePoint, and Teams to standardize protections across your deployments, so you can more easily identify gaps and reduce risk. Baseline security mode, included with your existing Microsoft 365 license, is Generally Available for Microsoft 365 and Entra. It allows you to: Act on tailored recommendations with preconfigured defaults that protect against known vulnerabilities from legacy configurations and emerging AI risks exploiting them, helping you keep pace with the rapidly evolving threat landscape and helps to ensure that security protections are current. Adopt changes safely and test configurations safely in simulation mode before rollout, making adoption straightforward, mitigating the risk of misconfiguration and helping organizations stay ahead of evolving threats. Take advantage of built-in protection and benefit from purpose-built integration, as BSM is optimized for Microsoft 365, and updated regularly to help deliver ongoing security enhancements. To learn more on how to get started with Microsoft Baseline security mode, read our Insider Track blog and Learn doc. Closing As we continue to enhance security and governance capabilities, Microsoft is committed to building trust with you, our customers, by equipping you with robust tools to effectively manage Copilot and agents. By delivering security and governance capabilities in Microsoft 365 Admin Center, Microsoft Purview, and SharePoint Advanced Management, we empower administrators to maintain transparency, security, and compliance in your Microsoft 365 environments. These innovations ensure your most valuable data is protected and provide your organization with the confidence to collaborate securely in an AI-powered workplace. Related Copilot control system: aka.ms/CopilotControlSystem Ignite 2025: Copilot Control System and related updates for IT and Security Teams: aka.ms/CCSIgnite2025 Learn more about Copilot Control System’s Security and Governance pillar: aka.ms/CCS/SecureGovern Blueprint guidance to help you enable Agent in Microsoft 365 Copilot: https://aka.ms/Copilot/Microsoft365AgentsBlueprint Microsoft Security for AI Ignite news: https://aka.ms/S4AI_IgniteNews2025 Copilot readiness and resiliency with Microsoft 365: Copilot readiness and resiliency with Microsoft 365: Ignite 2025 Edition | Microsoft Community Hub Microsoft Baseline security mode: https://aka.ms/MicrosoftBaselineSecurityMode3.4KViews2likes1Comment