microsoft graph
479 Topics
Duplicate subscriptions for a specific resource
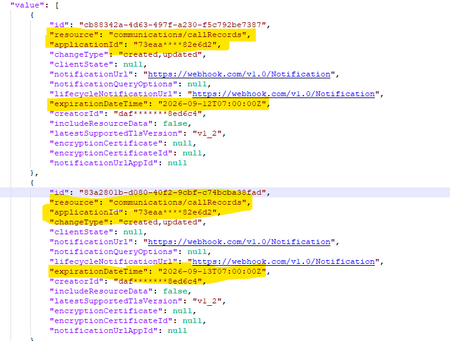
Hello, Previously, we were not allowed to create duplicate subscriptions for the same resource. But now we can create duplicate subscriptions for a specific resource. Could you please confirm whether this functionality has been newly enabled or supported? Why duplicate subscriptions are now allowed for the same resource like (/users, /groups & communications/callRecords). Whether this is a change or a bug. We would appreciate clarification on the expected behavior and the supported use cases.235Views0likes2CommentsWhy Some Purview DLP Policies Need Days to Start Working
While testing the new DLP capabilities to block sharing to users and domains and stop Copilot from using external email, it was noticeable how long it took before policies became active. DLP policy synchronization to workloads is reasonably work (and getting faster), but these policies have a new retrospective effect that requires workloads to process files and messages to stop them being available. It’s a new twist to the DLP story. https://office365itpros.com/2026/09/11/dlp-policies-take-time/68Views1like0CommentsWhy Microsoft Graph Does Not Support Group Mailboxes
A reader asked why the Outlook Mail Graph API doesn’t support access to group mailboxes. The basic reason is that a group mailbox doesn’t have an account and the Outlook Mail API only supports mailboxes that are linked to an account. When you look at the current usage of group mailboxes, it doesn’t seem like there’s much data to mine. Maybe the need for Graph API support for group mailboxes isn’t such a big thing? https://office365itpros.com/2026/09/09/group-mailbox-graph-api/65Views0likes0CommentsWho's Performing Microsoft 365 License Audits For Their Clients?
If you’re an MSP or IT leader and aren't running these regularly, you might be leaving money on the table or letting your clients overpay by over 20% on average. Common quick wins we see all the time: Disabled user accounts that still hold active paid licenses. Inactive or dormant users that could easily be converted to free shared mailboxes. Over-licensed users who only need OWA/web access instead of full desktop suites. Paying for unassigned licenses sitting idle in the tenant. Doing a full, manual audit can feel tedious, but following a structured process makes it painless. If you want to run a complete audit via the Admin Center, PowerShell, or free automated tools, check out this comprehensive guide: https://www.gitbit.org/docs/microsoft-365-license-audit63Views0likes0CommentsRevoking Access Tokens for Risky Service Principals
A Technical Community post discusses the topic of using the Entra ID continuous access evaluation (CAE) feature to revoke access for service principals when apps become risky or potentially compromised. The Microsoft Graph Command Line Tools app is a good example of a service principal in common use, so we examine the access tokens issued for interactive Graph sessions to discover if they are CAE-enabled. Just for fun! https://office365itpros.com/2026/09/03/cae-service-principals/79Views0likes0Comments
How much of your Microsoft 365 environment can you actually see at once?
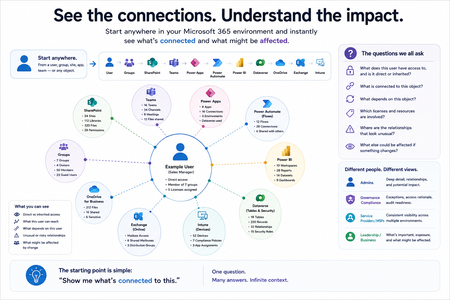
Not how many users you have. Not how many sites, teams, apps or flows you have. How much of it can you actually see connected together? I've been working across Microsoft 365 environments for a while, and I kept running into the same thing. There is no shortage of information. If anything, there is probably too much of it. Users, groups, permissions, SharePoint, Teams, Power Apps, Power Automate, Power BI, Dataverse, OneDrive, Exchange, Intune, licensing, configuration... It's all there. But when you're actually trying to understand how everything fits together, it can be a different story. You open one blade. Find something. Open another. Cross-check it. Go back. Open something else. Before long, you're jumping between different parts of the tenant trying to build the bigger picture in your head. And if you're working with larger environments, that gets difficult pretty quickly. The information isn't necessarily missing. The relationships between the information are what can be difficult to see. That got me thinking about a slightly different question: Instead of "where do I find this information?" "Show me what's connected to this." That's where VisibleState started. Start anywhere. Follow the connections. Imagine starting with a single user. Instead of seeing that user simply as a record with a list of properties, imagine being able to explore the relationships around them: User → Groups → SharePoint → Teams → Power Apps → Power Automate → Power BI → Dataverse → OneDrive → Exchange → Intune Then the questions become different: What does this user have access to? Is that access direct or coming through a group? What resources are connected to them? What depends on something they're associated with? Which licenses are involved? Are there relationships that look unusual? If something changes, what else might be affected? Those questions aren't necessarily about finding another piece of information. They're about putting information that already exists into context. A report can tell you that something exists. A connected view helps you understand what it is connected to. Illustrative example below — not a real customer environment. I'm not suggesting Microsoft 365 doesn't already give us this information Quite the opposite. Microsoft 365 already gives administrators an incredible amount of information and tooling. The thing I've been thinking about is what happens when you want to look across those boundaries. Sometimes I don't want another export. I don't want another list. I don't necessarily want another dashboard. I want to start with something I'm looking at and ask: "What's connected to this?" And then keep following the trail. That's the idea I'm exploring with VisibleState. The interesting part is what happens when you change the viewpoint The same relationships can be useful for completely different reasons. For example: Administrators may want to understand access, permissions and dependencies. Security and governance teams may want to find unusual relationships or exceptions. Compliance teams may need to understand who can access something and why. People managing multiple environments may want a consistent way to understand what's there without rebuilding the picture manually every time. Leadership may not need to see the graph at all. They may simply want to know what's important, what's exposed and what could be affected. It's still the same underlying environment. You're just looking at it from a different angle. And that's where I think things get interesting. Where I'm at with it VisibleState started as something I was building to make my own work easier. I was spending a lot of time investigating environments, tracing access and putting information together for reports. The individual tasks weren't necessarily difficult. It was the jumping between different places and reconstructing the bigger picture that took the time. So I started building something that would let me approach the environment through the relationships instead. It's grown quite a bit from where it started, and I'm continuing to build it. I'm not posting this as a product launch, and I'm not looking for people to sign up. I'm genuinely interested in whether the problem I'm seeing is familiar to other people working with Microsoft 365. So I'm curious... If you could start with any object in your Microsoft 365 environment and immediately see what it's connected to, where would you start? Would it be: Users and access Groups and permissions SharePoint and Teams Power Apps, Power Automate, Power BI and Dataverse Licensing and resources Governance and unusual relationships Something completely different Maybe you've already got a good way of doing this. Maybe you still find yourself jumping between different services and piecing things together manually. Or maybe I'm looking at the problem from the wrong direction. What's the one relationship in your Microsoft 365 environment that you wish you could see instantly?160Views0likes0CommentsRunning a Regular Check for New Graph Permissions
Use PowerShell to Check for New Graph Permissions with a View to Updating Permissions Used by Apps. After Microsoft released some new Graph permissions, thoughts turned to how to discover new permissions after they are released. Code is the best way to perform automatic checks, and this article explains how to use PowerShell to check a last known set (stored in SharePoint Online) against the current set. Any variations are reported to administrators via email. https://office365itpros.com/2026/08/31/new-graph-permissions-check/84Views0likes0CommentsBackout Plan for EWS to MS Graph API upgrade for SharePoint|sapiens
Microsoft has announced the retirement of Exchange Web Services (EWS) in Exchange Online, effective October 1, 2026. After this date, EWS-based integrations will no longer be supported. To ensure uninterrupted email functionality, all affected SharePoint|sapiens solutions must be upgraded to use the Microsoft Graph API. My question is this - if we upgrade to Graph and our SharePoint|sapiens solution goes sideways somehow, is backout / rollback to EWS an option? I realize we could only roll back until 10/1 since that's the EWS retirement date, but our leadership may request that we make our solution functional temporarily (if the upgrade causes a problem) by rolling back.249Views0likes2CommentsMicrosoft To Enforce WAM for Delegated Interactive Graph Sessions
In a GitHub post, Microsoft says that interactive Graph sessions using the default Microsoft Graph Command Line Tools app will use the Web Account Manager (WAM) in the future. Some administrators use older versions of the Microsoft Graph PowerShell SDK for continued access to browser-based authentication, but this won’t be possible once Microsoft makes the server-side change to enforce WAM on an undefined future date. Teams and Exchange Online also use WAM, apparently for better security. https://office365itpros.com/2026/08/28/interactive-graph-sessions-wam/72Views0likes0Comments