microsoft entra
110 Topics
Free, offline tool: see each user's real passkey policy in Entra ID and who SMS retirement blocks
Entra combines passkey profiles as a union (any profile that allows a passkey type wins), while Conditional Access works as an intersection. So a Global Admin in a strict "security keys only" profile who is also in an All Users profile can still register a synced iCloud or Google passkey, and the portal never shows you that per user. I built EffectivePasskey to answer three questions for every user and admin: 1. What passkey can this person actually register? 2. What can this admin actually sign in with after Conditional Access? 3. Who gets blocked when SMS and voice MFA retire (1 Feb 2027, and 1 Jul 2027 for Global Admins)? It runs entirely on your machine from read-only JSON exports. It never signs in to your tenant and never changes anything. No telemetry. MIT licensed and completely free. Try it with the included demo tenants: pip install effective-passkey GitHub: https://github.com/xsignon-secure/EffectivePasskey Feedback and issues are very welcome, especially from anyone mid-rollout.16Views0likes0Comments
Microsoft Entra provisioning Agent Error
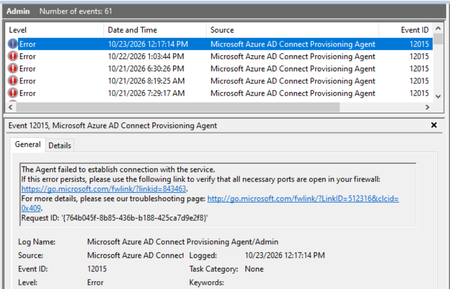
Hello, I have deployed the Microsoft Entra provisioning agent in my organization, with synchronization configured from AD to Microsoft Entra ID. I am encountering an issue on the server where the Cloud Sync agent is installed: when connecting to Microsoft endpoints via a Squid proxy, I receive the error shown in the screenshot. The synchronization itself works perfectly, and the configuration status in the cloud is "Healthy." I frequently see the error shown in the screenshot (error code 12015), and I also occasionally encounter error code 12011. Has anyone experienced a similar issue? Could you please advise on how to resolve it? Thanks.14Views0likes0CommentsBulk Enrollment suddently stopped working?
We've been generating BPRT tokens for Entra ID enrollment via provisioning package (WCD) for a long time. This started out of the blue, tried from three different tenants, these two error messages: AADSTS90202: A transient error has occurred. Please try again. AADSTS240001: User is not authorized to register devices in Azure AD I know its not authorization because the same user was working the day before and because I even tired removing the enrollment restriction from the tenant altogether.155Views2likes4Comments
Passkey/FIDO2 for users in mainland China – recommended approach?
Hi, We are currently evaluating the adoption of Passkey/FIDO2 in Microsoft Entra ID as part of our strategy to move users away from traditional authentication methods such as SMS and voice and towards phishing-resistant authentication. Our Microsoft Entra ID tenant is a global tenant (not Azure China operated by 21Vianet), but we have a group of users who are physically located in mainland China. For users in other regions, we are evaluating Passkeys in Microsoft Authenticator and FIDO2 security keys. However, before defining the approach for our users in China, we would like to better understand the supported and recommended architecture for this particular scenario. We have reviewed the Microsoft documentation and understand that: Passkeys are not available for Microsoft Azure operated by 21Vianet. On iOS, Microsoft Authenticator Passkeys can be used to sign in to global organizations while the user is in China. On Android, Passkey authentication has dependencies such as Google Play Services, which raises questions for devices operating in mainland China. Our main questions are: For users physically located in mainland China but authenticating against a global Microsoft Entra ID tenant, what is Microsoft's recommended approach for deploying phishing-resistant authentication with Passkey/FIDO2? Is Microsoft Authenticator Passkey on iOS considered a fully supported option for users permanently located in mainland China, rather than only users temporarily traveling there? For Android users in mainland China, what is the recommended approach considering the dependency on Google Play Services? Is Passkey in Microsoft Authenticator a realistic supported option in this scenario? Would physical FIDO2 security keys be the preferred or more consistent alternative for users in China when mobile Passkeys cannot be reliably used? Are there any other Microsoft-supported Passkey providers or authentication approaches that should be considered specifically for mainland China? From an enrollment perspective, what would be the recommended bootstrap process for these users? For example, would Temporary Access Pass (TAP) be the recommended method to allow users to register their Passkey/FIDO2 credential before SMS/Voice is removed? Are there any additional regional, connectivity, mobile OS, or application compatibility considerations that should be taken into account before enforcing a phishing-resistant Authentication Strength through Conditional Access? Our objective is not simply to enable Passkey in the tenant, but to define a supported and sustainable authentication model for users located in mainland China before starting a broader rollout. Any experience, Microsoft guidance, or recommended architecture for this type of scenario would be greatly appreciated. Thanks in advance.221Views0likes2CommentsEntra-issued agent identities, verified offline by a party with no Microsoft credential
I am Toshikatsu Oga, representative director of The HORIZONs Co., Ltd. in Tokyo. We build NENRIN, an open record format and verifier for what AI agents authorize and execute, built so that a third party can recheck the records without trusting us and without access to the systems that produced them. On 2026-10-15 we ran this against a real Microsoft Entra ID tenant: Two agent app registrations obtained v2.0 access tokens with the client credentials flow (RS256). Each agent bound its own signing key to its token, inside the token's lifetime (record format idp-bind-v0). Agent A signed a grant authorizing one action. Agent B signed a receipt for executing exactly that action, committing to the grant by hash. A reader holding only four files (the two bindings, the tenant's JWKS pinned by SHA-256, and the grant and receipt), with no network access and no Microsoft credential, verified all four records in two independent runtimes (JavaScript and Python). It printed which Entra subject authorized what, and which one executed it. We ran the same thing with Google service-account ID tokens the same day, with the same reader. Since 2026-10-16 we also record the Entra and Google signing keys every day and anchor them to Bitcoin, so a reader can check later that a pinned JWKS is the one the issuer was serving at the time. Code and records (MIT): github.com/ogasurfproject-jpg/horizon-shield (folder workers/hs-ledger/nenrin/idp-bind-v0/real-issuers) (run node check.mjs). For the Entra run, the grant, receipt and JWKS are public. The two bindings are pinned by SHA-256 but withheld, because GitHub push protection treats Entra access tokens as secrets even after expiry. They are available to the Entra team on request. What this does not establish: that the action happened in the world (a signature proves who asserted it), or possession of the identity beyond holding a live token, because the tokens carry no cnf claim (RFC 7800). The verifier already supports a cnf claim naming the agent's key, which would upgrade the result from bearer_only to cnf_bound. Two questions for the Entra Agent ID team: Is there a supported way to obtain a proof-of-possession (cnf) token for an agent identity, so the binding can be possession-proven rather than bearer? Would an offline-verifiable record of what agent identities authorized and executed be useful to your customers? It is meant for auditors, counterparties or regulators who cannot sign in to the tenant. Toshikatsu Oga, The HORIZONs Co., Ltd. (email address removed for privacy reasons, ORCID 0009-0000-9180-903X)83Views0likes0Comments
Sole Global Administrator locked out — no working MFA method — need account recovery
I'm the sole Global Administrator of my Microsoft Entra ID tenant and I'm completely locked out due to losing access to my MFA device, with no other admin and no working alternate verification method. Account details: - User (UPN): email address removed for privacy reasons - Custom verified domain: apip.dk - Tenant ID: can be provided - Azure Subscription ID: can be provided What happened: My phone (with Microsoft Authenticator installed — my only registered MFA method) was destroyed. I know my password and secondary email, but: - Phone-call verification during sign-in does not connect. - I have a FIDO2 security key, but it is not currently enabled/registered as a sign-in method on this account. - There is no other Global Administrator in this tenant and no other active session I can use to self-recover. What I need: An MFA/authentication-method reset on my account so I can sign back in and register a new MFA method, or guidance on an alternative recovery path. Proof of ownership I can provide: - I own the custom domain apip.dk and can add/modify a DNS TXT (or CNAME) record to verify tenant ownership. - I can provide billing details for the subscription (card on file, recent invoice amounts, billing address) if needed for verification. Additional context: I recently updated the payment method on this subscription, so I'm concerned about a billing failure at the next payment date while this recovery is pending — I'd appreciate the account being flagged so it isn't suspended during this process. Please let me know what verification steps you need from me to proceed. Thank you, Andreas199Views0likes1CommentSynced iCloud Keychain passkey registration succeeds despite Device-Bound-only passkey profile
a { text-decoration: none; color: #464feb; } tr th, tr td { border: 1px solid #e6e6e6; } tr th { background-color: #f5f5f5; } We have Microsoft Entra passkeys enabled only for a pilot group. The assigned Default Passkey Profile is configured as: Passkey Type = Device-bound Key Restrictions enabled Microsoft Authenticator iOS and Android AAGUIDs only Despite this, a pilot account successfully registered a synced iCloud Keychain passkey. The Security Info page explicitly shows: "Passkey (Synced) - iCloud Keychain" The tenant also displays a warning banner stating: "All users enabled for SMS or voice authentication are in scope for passkey auto-enablement and will be assigned to a system-managed passkey profile that allows all passkey types without restrictions." Can Microsoft explain how tenant-managed passkey profiles interact with the system-managed passkey auto-enablement profile? Is the system-managed profile overriding or supplementing tenant-defined passkey restrictions?278Views0likes4Comments
Entra ID 53003: How to identify primary authentication when Authentication Details are empty?
We are investigating repeated interactive Microsoft Entra ID sign-ins with the following pattern: - ErrorCode: 53003 (BlockedByConditionalAccess) - isInteractive: true - AppDisplayName: OfficeHome - Authentication requirement: Multifactor authentication Conditional Access correctly blocks these requests because they originate outside our trusted locations. We have already confirmed through controlled testing that the authentication flow can reach 53003 after the correct credentials are provided. Our current problem is different: We need to determine what mechanism satisfied the primary/first authentication factor for the observed 53003 events. For these events, Authentication Details are empty: - Authentication method: empty - Authentication method detail: empty - Result detail: empty Therefore, we cannot determine whether primary authentication was performed using a password, an existing token/session claim, PHS, PTA, federation, Seamless SSO, or another mechanism. Our questions are: 1. Is there any tenant-visible telemetry that can identify the primary authentication mechanism when AuthenticationDetails is empty? 2. Can fields such as AuthenticationProcessingDetails, AuthenticationProtocol, IncomingTokenType, OriginalTransferMethod, or AuthenticationMethodsUsed reliably distinguish between password validation and reuse of an existing authentication/token? 3. If additional authentication infrastructure is used: - can PTA Authentication Agent logs be correlated using RequestId or CorrelationId? - should Seamless SSO generate a corresponding Kerberos 4769 event for AZUREADSSOACC$? - should federated authentication be traceable in AD FS logs? 4. For Password Hash Synchronization, is there any tenant-visible telemetry confirming that Entra ID actually validated the password for a specific sign-in request? 5. If this information is not exposed to the tenant, can Microsoft Support retrieve backend authentication telemetry for a specific Sign-in ID / RequestId / CorrelationId and determine how primary authentication was satisfied? Our goal is not to determine why Conditional Access generated 53003 — that part is already understood. We specifically need to identify what satisfied primary authentication before the Conditional Access evaluation.148Views0likes0CommentsSingle group for TEAM AND Lighthouse (Security Group + 'Unified' group)
Trying to simplify our groups, since we are a 20+ year old firm, the variety of groups we have has bloated over the years. I'm trying to clean these up, but I've met a hitch. Our Service Desk dept has their own Internal team. Aka a 365 Group. Aka a 'unified' group. We use Lighthouse, which only takes Security Groups - it can't take the above 365 Group. First instinct is to create a Security group that can be used for both. But I can't seem to find a way to do this. The 365 Group is unable to nest a Security group. The Security group is unable to nest a 365 Group. So there's no single source of truth. I thought I could use Dynamic Grouping as a workaround - using the MemberOf property. But according to this, this Preview Feature is being abandoned and disabled. Anyone have workarounds/advice? Here's the output I get, when trying to do this via EOM PS C:\Users\lmtpo\Downloads> New-MgGroupMember -GroupID (team) -DirectoryObjectId (sec) New-MgGroupMember : Non-Unified Security Groups cannot be added to Unified Groups. paramName: Members, paramValue... PS C:\Users\lmtpo\Downloads> New-MgGroupMember -GroupID (sec) -DirectoryObjectId (team) New-MgGroupMember : A Unified Group cannot be added as a member of a Distribution List or Security Group or Elevated Group. paramName: Members, paramValue: , objectType: Microsoft.Online.DirectoryServices.Group132Views0likes0CommentsEntra External ID email OTP send event requestType always set to "signIn" regardless of user action
Hi, In a recent workload, I'm assisting a client with implementation of Entra External ID for identity management and app authentication, which includes sending OTP codes with customized email templates. To accomplish this, a custom authentication extension has been created that authorizes the request and then communicates with an email service via an event-driven, loosely coupled architecture. While implementing and testing this feature together with the client, we noticed that it seems like the different modes or states in the user flows are not reflected in the requestType property in the request payload posted to the OnOtpSend auth extension configured. E.g., if a user tries to sign in but has forgotten their password and navigates to the password reset view and requests to send the OTP code to their email address to reset the password, the following payload is sent to the auth extension endpoint (the original payload below was logged with Application Insights, with identifiers below then redacted and formatted, otherwise intact): { "type": "microsoft.graph.authenticationEvent.emailOtpSend", "source": "/tenants/aaaaaaaa-bbbb-cccc-dddd-eeeeeeeeeeee/applications/11111111-2222-3333-4444-555555555555", "data": { "@odata.type": "microsoft.graph.onOtpSendCalloutData", "otpContext": { "identifier": "email address removed for privacy reasons", "oneTimeCode": "<REDACTED>" }, "tenantId": "aaaaaaaa-bbbb-cccc-dddd-eeeeeeeeeeee", "authenticationEventListenerId": "22222222-3333-4444-5555-666666666666", "customAuthenticationExtensionId": "33333333-4444-5555-6666-777777777777", "authenticationContext": { "correlationId": "44444444-5555-6666-7777-888888888888", "client": { "ip": "192.0.2.10", "locale": "en-gb", "market": "en-gb" }, "protocol": "UNDEFINED", "requestType": "signIn", "clientServicePrincipal": { "id": "55555555-6666-7777-8888-999999999999", "appId": "11111111-2222-3333-4444-555555555555", "appDisplayName": "Example Web App", "displayName": "Example Web App" }, "resourceServicePrincipal": { "id": "55555555-6666-7777-8888-999999999999", "appId": "11111111-2222-3333-4444-555555555555", "appDisplayName": "<client-app-name>-Web", "displayName": "<client-app-name>-Web" } } } } The above payload was captured using browser-based authentication (native auth is not used), with the below parameters passed (identifiers, tenant name etc. redacted, otherwise intact): https://example.ciamlogin.com/ aaaaaaaa-bbbb-cccc-dddd-eeeeeeeeeeee/oauth2/v2.0/authorize ?response_type=code &client_id=11111111-2222-3333-4444-555555555555 &redirect_uri=https%3A%2F%2Fexample.com%2Fsignin%2Fcallback%2F &scope=openid+profile+email &state=<REDACTED> &prompt=login &ui_locales=de-DE &mkt=de-DE &nonce=<REDACTED> &code_challenge=<REDACTED> &code_challenge_method=S256 Following having navigated to the authorize endpoint above, the issue can be reproduced by entering an email address or an existing user identity, then on the password entry view, press the “Forgot Password?” link under the password input field, and then press the button/element “Email code to <user-email>”. I have looked at using the requestType in the email OTP send event payload to determine which email template and email content are used as per client requirement, but noted that the requestType seemingly always contains the value "signIn" even if the OTP code was sent as part of a password reset operation. At first glance, it would seem like this property indicates which step in the UI the user is currently at, even though I’m not certain whether that is what the property is actually meant to represent or indicate or not. However, for the above scenario and requirement, some identifier or value indicating the action would be needed in order to tailor the email content. The alternatives to having a reliable context property in the payload to indicate user action would require more or less significant additional components and infrastructure, thus increasing the complexity of the solution. Based on its name and values, it would seem like the requestType property appears be a good candidate to carry a user action context identifier. A suitable alternative solution has been adopted currently, using a generalized OTP template, which works well, but the requirement that it would be preferable to tailor the content based on user context and intent, e.g., whether the request was triggered as part of a password reset action or for another authentication scenario, is still present, ideally via the event payload sent from Entra External ID to the auth extension. If there would be any further/follow-up questions on the above, e.g., to clarify the requirement, or further explain the reproduction steps and behaviour observed, or anything else, please tell, and I'll ensure to get back as soon as possible. Also, would someone have some input on potential other/additional ways to make the requestType include a context identifier, that would be much appreciated as well, thanks! Regards Kristoffer168Views0likes0Comments