exchange server
2408 Topics
Could Adaptive, Capacity-Aware Recovery Orchestration Improve Exchange Online Resilience?
Sentinel AI – Adaptive Infrastructure Recovery & Traffic Intelligence Hello Microsoft Exchange Community, Following the publicly communicated Microsoft 365 and Exchange Online service disruptions in November 2026, I began examining the reliability challenges associated with large-scale cloud service recovery, traffic redistribution, infrastructure capacity, and secure connection establishment. Based on this technical analysis, I have developed an independent engineering proposal titled Sentinel AI – Adaptive Infrastructure Recovery & Traffic Intelligence. 1. Problem Context Large-scale cloud service disruptions can create complex recovery challenges, particularly when service availability decreases, traffic shifts toward remaining infrastructure, and recovery activities need to be coordinated under changing capacity conditions. Some key engineering challenges worth exploring include: Infrastructure overload during traffic redistribution. Uneven capacity utilization across available service instances. Retry amplification and uncontrolled request concurrency. Health-check signals that may not accurately represent service readiness. Recovery operations that risk introducing additional instability. Limited correlation of operational signals during complex incidents. These are general distributed-systems reliability challenges and are not assertions about Microsoft's internal implementation or the confirmed root cause of any particular incident. 2. Proposed Solution: Sentinel AI Sentinel AI is a proposed adaptive infrastructure recovery and traffic intelligence architecture designed to support cloud service resilience. Its objective is to combine intelligent monitoring, capacity-aware traffic management, controlled recovery orchestration, and evidence-based AI recommendations. The proposed architecture explores the following capabilities: A. Capacity-Aware Adaptive Traffic Management Continuously evaluate available infrastructure capacity. Distribute traffic according to service health and resource availability. Reduce the risk of overwhelming already-constrained infrastructure. Support controlled traffic redistribution during degraded conditions. B. Intelligent Health-Check and Readiness Evaluation Distinguish basic process availability from actual service readiness. Evaluate multiple operational signals before considering an instance healthy. Reduce the possibility of routing traffic toward services that are technically running but unable to handle requests reliably. C. Retry and Concurrency Intelligence Apply bounded concurrency and queue management. Introduce retry budgets and exponential backoff with jitter. Prevent uncontrolled retry amplification. Maintain predictable request handling under elevated load. D. Controlled Recovery Orchestration Gradually restore traffic using canary-based recovery. Monitor service health and capacity during each recovery stage. Define automatic rollback conditions. Require appropriate safeguards before expanding traffic to additional infrastructure. E. AI-Powered Incident Intelligence Correlate monitoring signals, logs, and service metrics. Identify abnormal patterns and potential cascading failure indicators. Generate evidence-linked diagnostic recommendations. Provide human operators with contextual incident insights. F. Human Oversight and Operational Governance Maintain human approval for high-impact recovery decisions. Record operational decisions and recovery actions. Provide auditability, rollback controls, and policy-based execution safeguards. 3. Proposed Architectural Objective The proposed Sentinel AI architecture follows a continuous operational feedback loop: Observe → Analyze → Decide → Validate → Recover → Learn The system is intended to help infrastructure teams make more informed recovery decisions while maintaining capacity constraints, service stability, and operational control. Importantly, AI recommendations would support engineering teams rather than independently control critical production infrastructure without authorization and safeguards. 4. Expected Engineering Benefits If implemented and validated successfully, the proposed approach could help explore improvements in: More controlled traffic redistribution. Reduced retry amplification during degraded conditions. Better visibility into service readiness. Safer and more gradual infrastructure recovery. Faster correlation of operational signals. Improved incident decision support. More predictable recovery behavior under changing capacity conditions. These are proposed outcomes, not measured or demonstrated results. 5. Validation and Implementation Approach The proposal recommends validating the architecture through an isolated test environment using synthetic services, simulated infrastructure constraints, and controlled fault-injection scenarios. Potential evaluation metrics include: Service recovery time. Request success and error rates. Queue depth and request latency. Infrastructure utilization. Retry amplification. Traffic distribution stability. Rollback effectiveness. The architecture has not been implemented or validated in Microsoft's production environment. Any practical evaluation involving Microsoft infrastructure would require explicit authorization. 6. Full Technical Proposal I have prepared a detailed technical document covering the problem analysis, proposed architecture, component-level design, decision logic, recovery workflows, security considerations, validation strategy, risks, and implementation roadmap. Read the complete technical proposal (PDF): https://drive.google.com/file/d/1y-A2rRdasBRpObSpSuW_6iU2miftkkL-/view?usp=sharing 7. Feedback and Technical Discussion I would genuinely appreciate feedback from Microsoft Exchange administrators, cloud infrastructure engineers, SRE professionals, and distributed-systems specialists. In particular, I would welcome technical perspectives on: The feasibility of capacity-aware recovery orchestration in large-scale cloud environments. Approaches to preventing retry amplification during infrastructure degradation. The effectiveness of readiness-based health checks and gradual traffic restoration. The practical role of AI-assisted incident intelligence in production reliability workflows. My intention is to contribute an independent engineering perspective and encourage constructive technical discussion around cloud infrastructure resilience. 8. Author Information Anurag Rajak AI Developer | Independent Engineering Research B.Tech in Information Technology Bansal Institute of Science and Technology (BIST) , Bhopal GitHub: https://github.com/anuragraja LinkedIn: https://www.linkedin.com/in/anurag-rajak-it/ Thank you for your time and consideration. Best regards, Anurag Rajak62Views0likes0Comments
Ip exchange on spamlist
Have noticed that a range of Microsoft IP's are on blacklists. Examples (there is a whole range of them): 52.101.66.97 Listed on spamcop. 52.101.66.97 Listed on: 0SPAM Sender Score Reputation Network SORBS SPAM Emails from Exchange Online systems or those using Outlook Protection are being delayed to us by several hours. https://0spam.org/request?ip=52.101.66.97151Views0likes1CommentMigration from Exchange on prem to Exchange online
Will migration from on-premise Exchange to Exchange Online stop working as of October 2026? You can see this error in the logs:"Error: The job encountered too many transient failures (61) and is quitting. The most common failure is CommunicationErrorTransientException with the hit count 60." And in IIS you see error 401 The solution is to recreate the migration endpoint using the UPN (email address removed for privacy reasons) instead of "Domain\user". Simply modifying the existing endpoint will not work.267Views0likes1CommentMicrosoft Defender for Office 365: New “Move to Quarantine” Feature Coming Soon
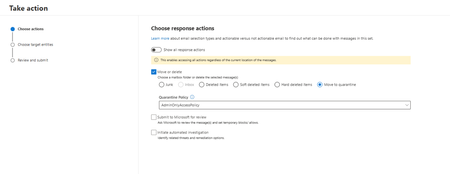
Microsoft introducing Move to Quarantine, a new remediation action in Microsoft Defender for Office 365. It enables security teams to move potentially malicious email messages from users' mailboxes directly to Microsoft Defender quarantine. This provides a safer and more flexible way to contain suspicious messages that bypassed initial detection while preserving the ability to investigate, release, or permanently delete them later. This capability is available with Microsoft Defender for Office 365 Plan 2, including eligible Microsoft 365 subscriptions that include Plan 2. Rollout schedule General Availability (Worldwide): Beginning in early November 2026 and expected to complete by mid-December 2026 Remediate malicious email that was delivered in Office 365 - Microsoft Defender for Office 365 | Microsoft Learn320Views0likes0CommentsBackdoor.MSIL.Webshell.gen
Hello ; My antivirus detected Trojan -------------------- Probably infected object detected: Trojan HEUR:Backdoor.MSIL.Webshell.gen. Object name: C:\Windows\Microsoft.NET\Framework64\v4.0.30319\Temporary ASP.NET Files\owa\8e05b027\e164d61b\App_Web_z1qruv0b.dll MD5 file hash: fd34b27c2ea1a4702e265f6d1f05fe16 File SHA256 hash: a4f7b4261a9f70bd5247f497ff384012a71d75010765cc7174724ed04ed9b047 ---------------------- and w3wp.exe I alreday upgraded that to CU22 before this atttack and also installed the last Security patch for CU22. I ran the MSERT tool and other Security Script for Exchange . But has been removed but the mystery of the re-infections continues . Could you help me3.2KViews0likes1Comment
Access old Exchage after migration to 365
Hi all So I have migrated from Exchange OnPrem to Exchange Online. Before migration I have taken a snapshot from the Exchange server, just in case. Now, there is a user who claims that some of her contacts vanished during the migration. So I booted up the backup Exchange and tried logging into the OWA to see if I can find some cantacts there. However, when trying the OWA, using the localhost url I get redirected to the online Outlook. Obviously the Exchange server recognizes soemwhere in the AD that we have migrated. So my question: How do I access the old information on the OnPrem Exchange Server if I did not think of keeping a backup of the DC?4.4KViews0likes9CommentsWhy do Apple macOS and Ubuntu clients display Exchange meeting times one hour earlier than scheduled
If a meeting is generated from Apple macOS and Ubuntu clients showing the meeting time as one hour earlier than the actual scheduled time email solution is exchange server 2019, what will be the issue.323Views0likes1Comment
Teams calendar for exchange on prem users not working
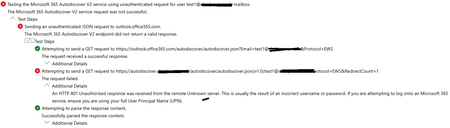
Hello I am having issues to make Exchange On prem users use Calendar on teams. Initially Client autodiscover was blocked externally but they added a cname and open flows but I am still having issues to makecalendar on teams work HCW as passed and new hybrid dedicated app was used any help is welcome972Views0likes3Comments
Cross-Tenant Mailbox Migration - HTTP 401 Unauthenticated during Test-MigrationServerAvailability
We are performing a Cross-Tenant Exchange Online mailbox migration between two Microsoft 365 tenants. The migration endpoint is configured with ApplicationId authentication and validates successfully. When running: Test-MigrationServerAvailability -Endpoint "MexicoToPortugal" -TestMailbox "<user>" the test consistently fails with: StatusCode="Unauthenticated" HTTP Status Code: 401 We reproduced the issue with two different users. We have already validated: - MailUser configuration - ExchangeGuid - LegacyExchangeDN (X500) - ExternalEmailAddress - Accepted Domains - Organization Relationships - Migration Endpoint - Enterprise Application - Mailbox.Migration permission - Admin Consent - Cross-Tenant Migration licensing The same HTTP 401 error occurs for multiple mailboxes after all configuration issues are corrected. Has anyone experienced a similar Cross-Tenant Mailbox Migration scenario where Test-MigrationServerAvailability returns HTTP 401 Unauthenticated even though the Enterprise Application, Mailbox.Migration permission and Admin Consent are correctly configured?218Views0likes0CommentsRetirement of Azure Communication Services
Microsoft has announced several retirement and breaking changes in September 2026. One notable change is the retirement of Azure Communication Services as a standalone offering, scheduled to take effect on September 30, 2028. Organizations currently using Azure Communication Services should review the announcement, assess the potential impact on their environments, and begin planning accordingly. https://learn.microsoft.com/en-us/azure/communication-services/acs-retirement-and-breaking-changes-guide1.1KViews0likes1Comment