events
871 Topics
The designs we didn't ship: How user feedback shaped the new Teams meeting controls
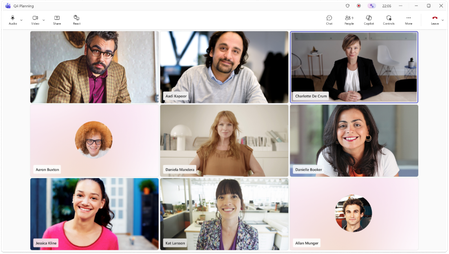
Some of the most important product decisions we've made weren't about what to ship. They were about what not to ship. When we began rethinking the meeting controls in Microsoft Teams, the challenge was clear. Meetings had become more capable, and the interface had grown along with them. As Teams meetings became more capable, we saw an opportunity to make controls simpler to navigate and easier to adapt to different meeting needs. And simply adding another button every time Teams gained a capability wasn’t the experience we wanted to carry forward. So we started with a question: Could we make meeting controls simpler today while creating room for Teams to become more capable tomorrow? It took more than one attempt to answer it. First idea: Spread things out An early concept divided the controls across more of the meeting window. The idea made sense on paper: reduce crowding, establish clearer groups, and create additional separation between actions such as Share and Leave. Initial research gave us reasons to keep exploring it. Participants responded positively to aspects of the cleaner layout and clearer grouping. But repeated use revealed tradeoffs. In our first longitudinal study, supplemented by feedback from early users and customer sessions, we identified tradeoffs in control placement, discoverability, and Leave separation that informed the next iteration. It looked cleaner. But looking cleaner wasn't enough. A meeting toolbar isn't something people simply look at. It's something they operate quickly while concentrating on a conversation, presentation, or task. So we kept going. Next, we tested very different answers Instead of debating design philosophies, we decided to test them. We developed three approaches: All centered: Put controls together in one predictable place. Three columns: Separate families of controls and use more of the available screen. Cleaned-up current: Reduce clutter while preserving more of the familiar structure. We gave those experiences to for a large cohort for a month, with participants responding to surveys twice a week. We looked at signals including findability, efficiency, confidence, effort, satisfaction, and perceived value. Just as importantly, we looked at how participants' reactions developed as they became familiar with each design. The findings exposed an important tradeoff. The lesson wasn't simply that one design had "won." It was that visual simplicity and operational simplicity aren't necessarily the same thing. Then users challenged the idea of a perfect toolbar We had been approaching the toolbar partly as an optimization problem: determine which controls belong there, identify the best order, and create the right default. What we learned from participants led us to reconsider that assumption. People use Teams differently. A presenter may have different priorities from someone participating in a large group discussion. Someone who records frequently may want Record immediately accessible. Another person may prioritize Notes, Copilot, People, reactions, or something else. Across the research, we heard a clear desire for more control over that experience. Let me customize it. That changed our thinking. Instead of trying to create one perfect toolbar, we focused on creating a system people could adapt. Pin. Unpin. Rearrange. Bring forward the controls that matter to you. The goal became a simpler starting point without assuming that everyone's definition of "simple" is the same. Finding the problems that still remained By early 2026, the design had converged substantially. But before expanding the rollout, we conducted a structured review around nine meeting tasks. Could participants mute? Add and remove controls? Take notes? Raise their hand? Record? Start transcription without recording? That final task exposed an issue we needed to fix. The capability existed, but some participants weren't reliably finding or understanding it. That's an important distinction in product design: A capability delivers the most value when people can easily discover and use it. The review surfaced other opportunities too. Relying on right-click wasn't enough to make customization discoverable for everyone, and the difference between temporary and permanently pinned controls needed to be clearer. So we iterated again. Listening to more than one signal There wasn't a single metric that could tell us whether we had the design right. We combined what people told us through research and surveys with aggregated product usage insights. We looked at questions such as whether participants could find what they needed, how confident they felt, and how they perceived different designs. We also examined how early users interacted with controls and menus, and we listened closely to people who chose to return to the previous experience during testing. When someone told us a control was difficult to find, an interaction took too long, or a change disrupted something familiar, that feedback helped us understand where the design still needed work. Predictability matters As more people tried the experience, their preferences weren't always the same. Some participants wanted Raise hand visible at all times. Others liked its association with reactions. Some preferred fewer visible controls. Others wanted to make fuller use of a large display. Some appreciated additional separation between Leave and Share. Others noticed even small changes to locations they knew well. One particularly useful lesson came from feedback about dynamic controls. A toolbar can become harder to operate when controls move unexpectedly during an interaction. That reinforced a design principle that stayed with us: Simplicity isn't only about reducing clutter. It's also about predictability. People in meetings have better things to think about than where their interface went. Where we landed After the prototypes, longitudinal research, surveys, experience reviews, telemetry, card sorting, diary studies, and a lot of iteration, the principles behind the final direction became relatively straightforward: Keep frequently needed actions accessible. Separate Leave from common controls. Make the broader toolbox easier to navigate. Let people personalize their controls. And build an information architecture with room to evolve. The finished experience can make those decisions seem obvious. What you don't see are the designs that didn't survive the research. That's the part of this work I'm most proud of. We didn't need to have the right answer on the first try because we built a process that allowed users to help us find a better one. Shipping is another beginning The new Microsoft Teams meeting controls are becoming broadly available. Learn more about how to set up and use. That gives us something our prototypes and studies couldn't: feedback from a much broader range of real-world meetings and ways of working. So if you've tried the new controls, tell us what you think in the blog comments. What did we get right? What could we make even better? And what's the next thing we should simplify? Some of the most valuable moments in this journey began when user feedback challenged our assumptions. We're still listening.381Views0likes0CommentsWindows Server 2028: A trusted foundation for an evolving enterprise
Enterprise infrastructure has evolved in response to changing and increasing business demands. Windows Server helped connect the enterprise by bringing people and resources together with Active Directory. As more business processes moved into software, it became a place to run business-critical applications. And when those applications multiplied, Hyper-V helped customers host the infrastructure they depend on more flexibly. Windows Server has evolved and grown with customers through each shift. Now customers are asking where AI should run when it needs to work with those applications and data. The cloud is part of the answer, but so is the local infrastructure they operate themselves. With Windows Server 2028, we’re strengthening the platform across the work it already does—and beginning to enable enterprise hybrid intelligence. Today, we’re introducing Windows Server 2028, in public preview now. This major release raises the security and access bar, accelerates enterprise infrastructure, and simplifies management at scale. It also begins our long term investments extending Microsoft Foundry to bring AI inference to fleets of local token factories, giving customers more choices to put the right intelligence in the right place with the right cost structure. For customers interested in early access to Windows Server 2028 features and direct engagement with Windows Server engineering, consider applying to Windows Server Technology Adoption Program (TAP) at aka.ms/WSTAP Enable enterprise hybrid intelligence AI raises an infrastructure question: where should inference run? A cloud service may be the right choice for one application. Another may need inference close to its data, near a physical operation, or within an environment the customer controls. Customers need to make that choice without building and operating a separate AI stack for every location, and want to scale their local inference servers on the same trusted platform delivering storage, compute, networking, and databases across their enterprise today. With Windows Server 2028, we’re investing across the stack needed to run inference on enterprise infrastructure. At the hardware layer, we’re introducing powerful new AI accelerators with Windows Server 2028. We’re excited to share that AMD’s Instinct MI350P card is in preview starting H1 2027 for in-market supported Windows Servers and Windows Server 2028. At the platform layer, we’re developing capabilities to deploy and configure inference environments, manage accelerated hardware, and direct model requests to the right environment. At the runtime layer, we’re working to support open-weight and custom models across technologies including Foundry Local, Windows ML, vLLM, and Llama.cpp. Running inference in an enterprise also means protecting and governing it. Windows Servers benefit from broad Windows investment in agent security and management, including Microsoft eXecution Containers for isolation, integration with Microsoft Foundry for model catalogs, and Agent 365 for agent identity and governance. Together, these capabilities are intended to help customers run AI close to their applications and data while connecting that work to a broader hybrid AI architecture. Raising the security and access bar The more an organization relies on its servers, the more important it is to keep them secure. Administrators need to protect the operating system and the virtual machines it hosts, maintain the certificates that secure connections, and prepare for threats that will change over the life of the infrastructure. Doing that well should not depend on every team starting from scratch. Windows Server 2028 is designed to give customers a stronger starting point. A hardened Server Core configuration by default and a new security baseline help reduce the work of establishing a secure baseline from day 1. Trusted Launch extends protection to virtual machines, guaranteeing boot integrity across your VM fleet, and Confidential VM support begins a journey to support integrity-protected runtimes on supported CVM hardware. We’re also investing in automatic certificate management and post-quantum cryptography, addressing both the day-to-day task of maintaining secure connections and the longer-term need to modernize them against the threats of tomorrow. Accelerate enterprise infrastructure Applications and data keep placing new demands on the systems beneath them. Customers are adopting faster storage and moving larger volumes of data, but the value of that hardware depends on whether the rest of the infrastructure can keep up. For organizations running critical workloads on Windows Server, performance improvements need to reach the applications they already operate. Windows Server 2028 adds native NVMe storage enabled by default and NVMe over TCP and RDMA transports, along with the ability to boot from ReFS. These technology ingredients combine to deliver high-performance, scalable, resilient storage solutions for Windows Server customers and help customers make better use of modern hardware to give demanding workloads more room to grow. Simplify administration and management at scale Managing a server and managing a server estate are different jobs. Across datacenters, clouds, and remote sites, teams need ways to apply policy, manage updates, and see what is running across the estate across an extraordinary diversity of Windows workloads. We hear regularly from customers who want to use proven Windows management processes and manage Clients and Servers as one fleet. We are proud to build on our recognition as a leader in Server Virtualization to help customers manage Windows Servers at scale. For teams that already manage Windows clients with Microsoft Intune, we are excited to announce Intune management for Windows Servers is now in Preview. Intune support for Windows Server brings familiar endpoint-management workflows including configuration, compliance, applications, and updates to eligible, persistent servers. Azure and Azure Arc continue to provide cloud-native management workflows for production and business-critical servers wherever they run. When a workload needs attention or a virtualization host needs troubleshooting, administrators need to get close to the machine and understand what is happening. Enterprise customers around the world run Windows Server VM fleets at scale, and need modern management tools to keep up. Windows Admin Center Virtualization Mode gives administrators the depth to work with individual servers and virtualized infrastructure as one fabric, and we are pleased to announce that WAC vMode is now in GA. These Cloud and On-Premises approaches complement one another. Customers can start with the workflows that fit their environment today, and grow into tomorrow with a consistent toolset that meets them where they are with the best of Azure and Windows management all together. Bringing Windows Server 2028 to enterprise infrastructure Bringing this vision to life takes an ecosystem spanning software, silicon, and systems integrators. We’re working closely with hardware partners to bring accelerated computing to the enterprise infrastructure customers already rely on. The strength of Windows and the strength of our ecosystem go hand in hand, and we thank our fantastic partners for their work scaling with us to support the needs of today’s enterprises. “Windows Server 2028’s advancements in security, virtualization, and modern infrastructure align naturally with AMD’s technology investments. Together, these technologies can help organizations protect data in use, modernize virtualized estates, and build efficient platforms for the next generation of mission-critical and AI-enabled workloads.” Kumaran Siva, Corporate Vice President of Business Development, AMD "Security for the AI era must be engineered across the platform—from firmware and the operating system through the full server lifecycle. Dell and Microsoft are working together so Dell PowerEdge customers can maximize the value of Windows Server 2028, including advances supporting the transition to post-quantum cryptography, with the reliability, automated protection and operational confidence they expect for their most critical workloads.” Anita Henry, Vice President of Infrastructure Solutions Group Engineering, Dell Technologies “As customers modernize distributed IT estates, they need security rooted in the server, reliability and simpler operations across edge, datacenter, and cloud. HPE ProLiant Compute, supported by Windows Server 2028’s security and hybrid-management, creates a strong foundation for resilient infrastructure that can adapt as business-critical workloads evolve.” Lauren Engebretson, Head of Compute Solutions and Enablement, Hewlett Packard Enterprise “The transition to post quantum cryptography is a major initiative for governments and enterprises. Intel’s PQC transition is well underway and, through deep co-engineering with Microsoft, we anticipate the Intel Xeon platform and Windows Server 2028 together will offer a strong PQC-capable foundation for our customers to build upon.” Srini Krishna, Distinguished Engineer, GM of Data Center Products, Intel Corporation “Customers want to bring AI closer to their data and decisions while building on the enterprise infrastructure they already rely on. Windows Server 2028, together with Lenovo Hybrid AI Advantage™ and Lenovo ThinkSystem and ThinkEdge servers, can help customers extend that foundation for trusted AI—from the edge to the data center and cloud—with greater choice, control and speed.” Scott Patti, Vice President of Infrastructure Solutions Group, Lenovo Going forward Windows Server 2028 is part of a bigger picture: intelligence across the cloud, enterprise infrastructure, and personal devices. As AI-accelerated workloads diffuse across the enterprise, different workloads have different needs. Some call for the breadth and scale of the cloud. Others need to run close to business-critical applications and data, on infrastructure customers control. Still others belong on the devices people use every day. Cost, latency, IP protection, data residency, and regulatory requirements all shape that decision. Our vision is to extend Microsoft Foundry across these environments, so teams can build with familiar tools and run each workload where it makes the most sense, from client, to cloud, to powerful Windows Server token factories running in corporate datacenters. As we move toward general availability, we’ll keep working with customers to learn where running inference on their own infrastructure makes the greatest difference—and to shape how Windows Server fits into a broader hybrid AI architecture. We’re excited about what Windows Server 2028 makes possible, and we look forward to sharing more as these capabilities develop. Explore Windows Server 2028 Security, performance, and management features are available in preview through the Windows Server Insider Program, and the Server team is looking forward to your feedback on the Windows Server Insiders Forum. Hybrid intelligence capabilities are available to a limited number of customers through an early access program, and hardware requirements apply. Thank you for the trust you’ve placed in Windows Server. Windows Server 2028 is our commitment to keep earning it: by strengthening the foundation you rely on and helping you put it to work in new ways.Secure Data at Microsoft Ignite 2026: Plan Your Experience
We're excited for you to join us at Microsoft Ignite 2026, our biggest event of the year! As organizations scale Microsoft Copilot, Cowork, and AI agents, one question keeps coming up: is our data ready? This post is your one-stop Ignite guide to sessions on data security and activities we have planned, so you can learn how Microsoft Purview helps prepare, manage, and protect data as you scale AI adoption. Visit Microsoft Ignite homepage to learn more, register, and build your agenda. When: November 17–20, 2026 Where: Moscone Center in San Francisco, plus a digital event experience online Types of sessions Here’s a quick overview of what types of sessions there are so you can decide which ones to join that will get you to the next step in your data security journey: Keynotes: The opening keynote is on Tuesday, November 17, from 10:00 AM to 12:00 PM PT, live from the Chase Center in San Francisco and online. Hear Microsoft's latest announcements and get a preview of what's coming across AI, cloud, security, and data. Breakout sessions: Expert led L200–L400 sessions with best practices, tips, and deep technical information, open to both in-person and online attendees. Labs: Expert led sessions that give you hands-on experience with our technology in a virtual environment. You'll need to reserve a seat. Late night labs run Tuesday and Thursday evenings, from 6:15 to 7:30 PM PT. Theater sessions: 25-minute technical deep dives with demos of product features, held inside the Hub. Lightning talks: Informal 15-minute sessions designed to spark conversation, questions, and discussion. Table talks: Small-group technical conversations that extend and deepen what you learn in the formal sessions. Microsoft Purview breakout sessions Day / time (PT) Session What you'll learn Wed, Nov 18 | 11:30 AM–12:15 PM BRK346: Protect data and accelerate AI adoption with Microsoft Purview Learn how Microsoft Purview provides unified data security and compliance to help you identify risk, protect sensitive data across Microsoft 365 and Copilot, and accelerate investigations — so you can scale AI securely and confidently. Wed, Nov 18 | 4:15–5:00 PM BRK348: From understanding sensitive data to protecting it Secure AI starts with understanding your data. Discover how Microsoft Purview uses AI-powered classification and sensitivity labels to identify sensitive content, automate protection, and help organizations confidently scale Copilot adoption. Thu, Nov 19 | 9:00–9:45 AM BRK342: Secure data and manage AI risk for Microsoft Copilot Chat and Cowork Confidently deploy and scale Microsoft Copilot Chat and Cowork. Explore how Microsoft Purview helps you understand and protect sensitive data, reduce oversharing risk, govern permissions and investigate incidents, to secure your AI-powered workplace. Thu, Nov 19 | 11:30 AM–12:15 PM BRK211: Secure and govern Microsoft Copilot Chat and Cowork Microsoft Copilot and Cowork are transforming how employees and agents work together, creating new opportunities and new governance challenges. Learn how to secure, govern, and manage Copilot & Cowork across your organization using Microsoft's integrated security, compliance, and governance capabilities. We'll cover protecting sensitive data, reducing oversharing risks, meeting regulatory requirements, and gaining visibility into usage so you can confidently scale Copilot & Cowork adoption. Thu, Nov 19 | 4:00–4:45 PM BRK329: Get your data AI-ready: Discover and mitigate sensitive data exposure risks As AI accelerates access to information, organizations need stronger protections for sensitive data. Learn how Microsoft Purview combines classification, permissions insights, and controls to reduce oversharing and secure data across AI. Thu, Nov 19 | 4:00–4:45 PM BRK335: Insights from Microsoft's journey to prepare its data for AI adoption Before deploying Copilot broadly, Microsoft focused on the fundamentals: understanding sensitive data, managing access, reducing oversharing risks, and establishing governance. Learn the strategies and lessons from our AI readiness journey. Fri, Nov 20 | 10:15–11:00 AM BRK338: Protect and govern data to scale your AI agents with Microsoft Purview AI agents can access data and automate work at unprecedented scale. Learn how Microsoft Purview helps discover agent activity, protect sensitive information, detect risk, and meet compliance requirements for a growing landscape of AI agents. Fri, Nov 20 | 11:30 AM–12:15 PM BRK347: Microsoft Purview: Scale data protection with sensitivity labels As data grows and AI accelerates how quickly it’s accessed, shared, and used, organizations need a scalable way to protect sensitive information. Microsoft Purview sensitivity labels provide persistent protection and context that travels with your data. Learn how to build an effective labeling strategy and use auto-labeling to automate protection and prevent oversharing in Microsoft 365 Copilot interactions. Microsoft Purview lab and theatre sessions Day / time (PT) Session What you'll learn Tue, Nov 17 | 6:15–7:30 PM; Wed, Nov 18 | 8:30–9:45 AM; Wed, Nov 18 | 12:00–1:15 PM; Fri, Nov 20 | 9:00–10:15 AM LAB685: Deploy Copilot with confidence: Find and protect exposed sensitive data Prepare your organization for secure AI adoption. In this hands-on lab, assess oversharing risks, identify exposed sensitive data, apply labels and policy controls, and validate that Microsoft Copilot can scale without exposing critical information. Wed, Nov 18 | 10:10–10:35 AM THR878: Secure exfiltration gaps with Microsoft Purview Data Loss Prevention Learn how Microsoft Purview provides unified data security and compliance to help you identify risk, protect sensitive data across Microsoft 365 and Copilot, and accelerate investigations — so you can scale AI securely and confidently. Microsoft Purview Lighting Talks Day / time (PT) Session What you'll learn Tue, Nov 17 | 4:25–4:40 PM LTG1234: Beyond data classification: Understanding human and data interactions Data security goes beyond knowing what's sensitive. It's understanding how people interact with data, where insider risk may emerge, and whether that activity fits the business need. Learn why user-data interactions are critical to reducing risk and securing AI. Thu, Nov 19 | 11:00–11:15 PM LTG1243: Turn global regulations into operating control with Microsoft Purview Regulatory demands are outpacing evidence. Understand how Microsoft Purview turns global AI and data requirements into assigned actions, operating protections, and reviewable records across data security, insider risk, and compliance management. Thu, Nov 19 | 12:15–12:30 PM LTG1241: Stay audit-ready for every AI interaction with Microsoft Purview Effective governance requires visibility. Learn how Microsoft Purview helps organizations track agent activity, support investigations, and maintain the auditability and evidence needed to satisfy compliance requirements. Microsoft Purview Table Talks Day / time (PT) Session What you'll learn Wed, Nov 18 | 1:20–2:05 PM TT2531: Protecting AI in real time: Ask the experts Effective governance requires visibility. Learn how Microsoft Purview, Defender, and Entra help organizations track agent activity, understand data access, support investigations, and maintain the auditability and evidence needed to satisfy compliance requirements Wed, Nov 18 | 3:30–4:15 PM TT2533: What's next for Microsoft Purview? Join this interactive community table talk to explore what’s next for Microsoft Purview. Share your feedback on protecting data across Microsoft 365, Copilot, and AI agents—and help shape the future of integrated data security and compliance. Thu, Nov 19 | 9:00–9:45 AM TT2534: Microsoft Purview AMA: Preparing your data for secure AI Bring your questions and join the conversation. In this interactive table talk, discuss real-world challenges, best practices, and lessons learned for classification and labeling. Explore how organizations are building the data foundation needed for secure AI adoption. More ways to connect at Ignite Visit the Hub: Stop by the Hub at the Moscone Center campus (November 17–19) to explore booths, catch theater sessions, and connect with Microsoft experts. Visit the booth area during Hub drop-in hours to ask questions, see live demos firsthand, and get practical guidance to make the most of your Ignite experience. Attendee Hours Mon Nov 16 – Tue Nov 17 12:00 PM – 6:00 PM Wed Nov 18 8:30 AM – 5:00 PM Thu Nov 19 8:30 AM – 6:00 PM Pre-day sessions and labs: Get a head start on Monday, November 16 with hands-on pre-day training designed to help you build skills you can put into action right away. Get certified: Eligible in-person attendees can take one Microsoft or GitHub certification exam at no cost, subject to the offer terms. Registration is required, so reserve your slot early. Can't make it in person? Register for the digital pass to stream keynotes and sessions online and catch up on demand after the event. Build your agenda We can't wait to see you at Ignite! Head to the homepage to register, add the Microsoft Purview sessions above to your schedule, and reserve your seat for LAB685 before it fills up. Learn more about Microsoft Purview Discover Microsoft Purview: Explore how Microsoft Purview helps you secure and govern data and manage compliance. Explore Microsoft Purview Explore technical documentation: Find guidance and resources to get started with Microsoft Purview. Browse Microsoft Learn Stay up to date with the latest innovations: Discover the latest Microsoft Purview announcements and innovations from Ignite 2026. Read the blog1.3KViews0likes0CommentsPlan your Microsoft Ignite 2026 experience
Build your Microsoft Ignite agenda around product insights, partner sessions, and connections that can move your business forward. Microsoft Ignite 2026 is coming November 17–20, and it’s time to get ready. Whether you join in person or digitally, Microsoft Ignite is where you can build connections, accelerate customer conversations, and get early product access to shape your 2027 plans. If you’re attending in person, register now to access exclusive partner programming and experiences, including the Microsoft AI Cloud Partner Program booth, exclusive networking areas, and dedicated partner sessions. If you’re attending online, access livestreamed and on-demand keynote and breakout sessions. Access the session catalog and sponsor directory to plan your experience and connect with other attendees, along with online-exclusive experiences. Use the session catalog to identify the dedicated partner sessions, product insights, and networking opportunities that can give you practical ways to scale your business and lead with AI. Register today and start planning your Microsoft Ignite experience. Plus: Exciting benefits news! Buy or renew your partner benefits package today and get even more AI value at Microsoft Ignite. New AI products will automatically unlock at launch—including Microsoft 365 Copilot Business across all three packages—with no increase to your package price. Starting at $350 a year, packages include discounted licenses, Azure credits, and one-on-one support so partners can save, innovate, and grow. Buy today and visit the Microsoft AI Cloud Partner Program booth to learn more.424Views0likes0CommentsFrom Silicon to Service: Bringing AMD Helios™ to Azure
Article contributed by: Yash Bhamare and Anna Daly Azure’s ND MI455X v7 brings a rack-scale approach to AI inference, powered by AMD Helios. Each liquid-cooled compute rack combines 72 MI455X GPUs, 18 AMD EPYC “Venice” CPUs, and 31 TB of HBM4 memory, with a two-tier Ethernet backend connecting racks into larger clusters. Designed for reasoning, long-context inference, search, and multi-agent services, the platform brings compute, memory, and networking together to support demanding AI workloads. In the Azure context, “silicon to service” describes the engineering around that hardware foundation and deploying the hardware at scale. Start with the user’s needs Consider a user who asks a trained AI model a question and receives a response. For that user, the response is the result that matters. Microsoft provides the infrastructure behind that experience as a cluster product, including GPU capacity and a commitment to its availability and reliability. Users need confidence that their GPUs will be available when needed, that the next job will run reliably, that updates will leave the system usable, and that faults will leave enough evidence for diagnosis. Reliability lets model teams and engineers focus on their models rather than rediscovering machine state. It requires infrastructure that can be deployed, observed, updated, and recovered predictably. Datacenter requirements At Microsoft, we deliver AI supercomputing clusters as a product. With AMD, we design from the rack up to meet customer workload requirements. We account for power, cooling, and physical fit so each rack can be deployed, operated, and maintained in the datacenter throughout its lifetime. A Microsoft-owned, two-tier back-end network connects racks for high-bandwidth communication. Our job is to bring compute, networking, software, and physical infrastructure together into a system customers can use reliably. Hardware availability shapes how we get there, and a standalone rack lets us advance software enablement and rack-local testing, but validating the cluster requires connected racks and the back-end network operating together under load. That is why we include power delivery, cooling, cabling, and software versions in the test configuration rather than treating them as separate concerns. The same principle applies after maintenance. We confirm that a replacement component responds and works within the connected system. Establish a repeatable software foundation System firmware, the operating-system kernel and device drivers must work together to initialize and manage hardware. Testing each layer alone cannot establish how the stack behaves. A versioned baseline recipe of all firmware components, the operating-system image, GPU and network drivers, and diagnostic tools are tested together. This supports reproducible installation in cloud-scale datacenters and helps distinguish hardware faults from configuration or integration issues. Secure boot and driver signing also belong in that baseline and repeatability must preserve Microsoft’s trust requirements. When expected behavior changes, the baseline provides a traceable starting point for investigation. Bring cloud management into the lab early Our work starts when the first systems power on in the lab, and since early hardware is limited and still evolving, we focus on iterating quickly by testing whatever we can, fixing what we find, and testing again. The first milestone is a stable foundation, where each system reliably boots the target operating system, discovers and initializes its devices, and reports their health. Getting there often exposes subtle interactions between firmware, drivers, and the operating system that we need to resolve before more advanced testing can begin. Once the system is stable, we turn to performance, starting with microbenchmarks for GPU compute, memory bandwidth, and GPU-to-GPU and network transfers, and using tools such as TransferBench and RCCL tests to characterize how accelerators communicate. These simple tests are especially valuable during bring-up because an unexpected result can point to a firmware defect, a driver issue, or a configuration problem. From there, we step up to distributed training and inference workloads to see how compute, memory, and networking behave together under sustained load and where the software stack needs tuning. Alongside this work, we validate how device inventory and configuration integrate with Azure for health reporting, updates, and recovery, so the tests, tooling, and management workflows we refine in the lab are ready to scale in the datacenter. Burn-In – Make readiness an engineering outcome Burn-in is where we take the same kinds of tests we ran in the lab and automate them at scale in the datacenter. Before a cluster reaches customers, we lock in an approved hardware and software configuration and use SuperBench to orchestrate sustained workloads across the whole system. Running these workloads for extended periods across thousands of GPUs surfaces intermittent hardware failures, thermal problems, and performance anomalies that shorter lab runs can miss. The communication tests from the lab also expand to cover the full network, both within racks (scale-up) and across racks (scale-out), where RCCL collectives such as AllReduce and AllGather expose bandwidth bottlenecks, topology misconfigurations, and failures that only appear at scale. After any faulty components are repaired or replaced and retested, the cluster enters production with data showing it can sustain demanding distributed AI workloads at expected performance and run reliably as one system. Exercise recovery as normal operation Once GPU racks enter production and begin running customer workloads, hardware failures are inevitable over time. These failures may manifest as workload performance degradation, unexpected errors, or device failures that must be traced to specific hardware components across one or more systems. To maintain cluster capacity, healthy spare nodes replace affected systems, while faulty nodes are moved to dedicated quarantine racks for further investigation. There, we run extensive diagnostics to isolate the underlying issues and repair or replace faulty components. Repair alone, however, is not sufficient to return a system to production. While still in quarantine, the repaired node undergoes another round of validation, running representative workloads against established performance and reliability baselines. This ensures that the original issue has been resolved and that the system performs as expected under realistic operating conditions. Once the node passes these checks, it becomes a healthy spare, ready to replace the next system requiring maintenance. This creates a continuous cycle of detection, isolation, repair, validation, and reuse, allowing Azure to maintain reliable GPU capacity as hardware ages and individual components fail. We apply the same rigor to system updates, looking across the GPU, firmware, operating system, and network layers to verify that the system remains healthy and workloads can continue or recover predictably after a change. Come and See it at SC26 This is what we mean by Microsoft delivering AI Supercomputing Clusters. Yash Bhamare and Anna Daly will share more in their session at the Microsoft booth (#3411) at SC26, on Wednesday 18 November at 10:00am CT.Plan your Ignite agenda: Join sessions that help you secure agentic insiders at scale.
AI agents are transforming how businesses operate—writing code, processing expenses, and taking action across enterprise systems. But that autonomy introduces a new security challenge: agents are becoming a new kind of insider. Agents can make mistakes, be manipulated or compromised, all while operating at machine speed. The answer isn't blanket blocking or unrestricted access. Organizations need security that can keep pace with the agents they’re deploying. Recently, Microsoft Security announced the expansion of Project Perception with new purpose-built capabilities to help organizations secure the agentic insider. Customers can now build on their existing investment in Microsoft 365 E7, including Agent 365, to know more of their agents, contain what agents can access and do, and adapt protections as risks change. Read the blog here. At Microsoft Ignite, we'll show you how these capabilities work in practice and how you can apply them in your own environment. Join us from November 17–20, 2026, at Moscone Center in San Francisco and online. Register here. Your guide to Secure Agentic Insiders sessions, from strategy to hands-on labs Join us at Ignite to explore what's new and see how Microsoft is bringing these capabilities to life—from agent discovery and identity to dynamic access controls, real-time risk protection, and AI-powered defense. Start with Microsoft Security Pre-Day on Monday, November 16, 2026, from 1:00-5:00 pm PT, where you can explore what’s next in cybersecurity through live demos, hands-on experiences, and conversations with the experts building these capabilities. Tuesday, November 17 Time Session Key takeaway 2–2:45pm BRK336: When AI acts, security has to answer: Microsoft Security for AI Strategy to accelerate AI innovation with confidence through unified security that protects AI apps, agents, access, and data across the lifecycle. 3:15–3:30pm LTG1240: Build AI on identities you can trust Learn how silicon-based credential protection helps prevent device impersonation and build a stronger foundation of trust for AI agents, devices, and services. 3:15–4pm BRK337: Prioritize and remediate your riskiest agents with Project Perception Learn how to continuously identify, prioritize, and remediate evolving AI agent risks across your environment with Project Perception. 4:05–4:30 pm THR877: AI agents: access granted. Trust not included Securely connect AI agents to apps and data, enforce least-privilege access, and reduce risk with Microsoft Entra Agent ID. 6:15–7:30pm LAB682: Can’t secure what you can’t see. Find every AI agent in your org Hands-on practice discovering agents, governing their identities and controlling access Wednesday, November 18 Time Session Key takeaway 8:30–9:45am LAB683: Secure local AI agents with end-to-end threat protection Hands-on practice investigating local agent attacks and responding to incidents 9:25–9:40am LTG1237: Govern & protect local agents for safe access to enterprise resources Discover, monitor, and secure local AI agents with Windows and Microsoft Security by enforcing least-privilege access and responding to risky agent behavior. 9:50–10:05am LTG1242: AI agents need access. Your network needs controls Gain visibility into AI agent network connections, enforce access controls, and contain risky activity while enabling secure, uninterrupted productivity. 10:15–11am BRK 343: AI is changing access. See how Microsoft Entra helps you stay ahead Learn about the latest identity and network access innovations to securely scale AI with Agent 365, protect people and agents, and use AI to detect and disrupt attacks. 12:15–1pm TT2530: AI Agents Are Scaling. Are Your Access Controls Ready? Govern Microsoft and non-Microsoft AI agents at scale with effective discovery, access controls, monitoring, and lifecycle management without slowing innovation. 1:20–2:05pm TT2531: Protecting AI in real time: Ask the experts Learn how Microsoft Purview, Defender, and Entra help track AI agent activity, monitor data access, support investigations, and maintain auditability to meet governance and compliance requirements. 2:00-3:30pm INV642: Observability at every layer of the stack Turn AI visibility into action to manage risk, build trust, and scale AI and agents with confidence. 2:15–3:30pm LAB683: Secure local AI agents with end-to-end threat protection Hands-on practice investigating local agent attacks and responding to incidents 2:25–3:10pm TT2532: Securing AI Agents: A candid conversation with the experts Practical strategies from Microsoft experts to identify and mitigate AI agent risks, strengthen security across data, identity, and runtime, and enable secure AI innovation. 4–5:15pm LAB682: Can’t secure what you can’t see. Find every AI agent in your org Hands-on practice discovering agents, governing their identities and controlling access 4:15–5pm BRK344: Build, secure, and govern agents across platforms with A365 and Entra Securely manage AI agent identities, automate lifecycle management, and govern access across Microsoft and third party apps using Agent 365 and Microsoft Entra. Thursday, November 19 Time Session Key takeaway 9–9:15am LTG1239: Dive into new intent-based playbooks that accelerate agent risk defense Prioritize and reduce AI agent risks with continuous risk assessment, intelligent recommendations, and guided playbooks to protect, govern, investigate, and remediate agents. 9–10:15am LAB682: Can’t secure what you can’t see. Find every AI agent in your org Hands-on practice discovering agents, governing their identities and controlling access 10:15–11am BRK 342: Secure data and manage AI risk across Microsoft Copilot and Cowork Protect sensitive data, reduce oversharing risks, and strengthen security and governance with Microsoft Purview to confidently scale Microsoft Copilot Chat and Cowork. 11–11:15am LTG1238: Agent 365 in Action: Managing MCP Servers, Plugins, and Skills for AI Agents Discover, register, and govern AI agent tools with Microsoft Agent 365, blocking unsanctioned tools while enabling granular access controls for approved users and functionality. 11:30am–12:15pm BRK341: Inside Look at Agent 365: Lessons from Microsoft's Office of the CISO Best practices and lessons from Microsoft's Office of the CISO on using Agent 365 to strengthen AI agent security and governance while enabling responsible innovation at scale. 12:15–12:30pm LTG1241: Stay audit-ready for every AI interaction with Microsoft Purview Learn how to track AI agent activity, support investigations, and maintain auditability to meet governance and compliance requirements with Microsoft Purview. 1-2:15pm LAB683: Secure local AI agents with end-to-end threat protection Hands-on practice investigating local agent attacks and responding to incidents 4–4:45pm BRK339: Local agents are here. Can you find and secure them? Gain visibility into local AI agents, reduce security risks, and enable trusted agent adoption without slowing innovation. 4:30–5:45pm LAB683: Secure local AI agents with end-to-end threat protection Hands-on practice investigating local agent attacks and responding to incidents 5:15–6pm BRK340: A Zero Trust approach to securing AI runtime with Microsoft Defender Secure AI agents with Microsoft Defender, apply Zero Trust principles, and protect against emerging AI threats like prompt injection, tool misuse, and identity abuse. 5:15–6pm BRK345: Master agent governance with Agent 365 Confidently govern, manage, and secure AI agents at scale with centralized visibility, policy enforcement, and lifecycle management using Agent 365. Friday, November 20 Time Session Key takeaway 10:15–11am BRK338: Secure data as you scale your agents with Microsoft Purview and A365 Discover and monitor AI agent activity, protect sensitive data, manage risks, and maintain compliance with Microsoft Purview. *Lightning talks (LTG), Table Talks (TT), and Labs (LAB) are only available to in person attendees. Breakout (BRK) and Theater (THR) sessions will be streamed online during the event and available on demand after the event at https://ignite.microsoft.com/. Expert Meetup Station Have questions about securing AI and agents in your organization? Come to the Secure Agentic Insider Expert Meetup Station in the Microsoft Security neighborhood at Moscone Center. Talk one-on-one with the engineers and product experts building Microsoft Security for AI. Bring your questions about agent discovery, identity and access, data protection and runtime defense, and get practical guidance you can apply in your own environment. While you're there, pick up a custom patch for your Ignite hat. Hours (PT): Tuesday, November 17: 11:00 AM–6:00 PM Wednesday, November 18: 8:30 AM–5:00 PM Thursday, November 19: 8:30 AM–6:00 PM See you at Ignite For organizations to adopt agents at scale, they need to be able to trust them. Come see how Microsoft Security helps you know every agent, contain it before it acts and adapt protections as fast as risks change. You shouldn't have to choose between moving quickly with AI and keeping your organization secure. Learn how to secure your agentic estate at speed and scale with the Microsoft Security for AI solution. For more on what’s happening in security, bookmark the Microsoft Security Community blog and follow Microsoft Security on LinkedIn (Microsoft Security) and X (@MSFTSecurity) for the latest news and updates on cybersecurity. Resources: View the Microsoft Security Ignite guide Browse the Ignite session catalog Learn more about Microsoft Security for AI solution Learn more about Microsoft Agent 365 Check out more Microsoft Agent 365 sessions at Ignite, 2026The CISO Cheat Sheet to Microsoft Digital Defense Report 2026
I know we’re all busy, so I’ve pulled the most important data from this year’s Microsoft Digital Defense Report into one short read. The full report is well worth exploring, but this article focuses on the numbers and trends most relevant to security leaders. This year’s edition shows that AI is lowering the time, expertise and cost required to discover and exploit weaknesses, enabling attackers to operate with greater speed, scale and autonomy. The report describes this as AI “changing the physics of cybersecurity”: attack timelines are compressing and agentic systems are beginning to automate more of the attack lifecycle. Trend 1: Time has collapsed The clearest finding is about speed. Vulnerability discovery is increasingly running ahead of remediation, while the time from discovery to weaponisation is shrinking. In the AI era, weaponisation can follow in hours. Vulnerability discovery and weaponisation now often needs only a well-written prompt. The median time from discovery in the wild to weaponisation is below 24 hours. Vulnerabilities were on track for a record estimated 72,000 CVEs in 2026. The report expects a multi-year period in which the number of known but unpatched vulnerabilities rises sharply before eventually declining. The median time from container start to first exploit attempt is 5.3 hours. The ransomware actor Storm-1175 moved from web-facing exploitation to deploying Medusa ransomware in as little as 24 hours. CISA added over 110 CVEs to its Known Exploited Vulnerabilities catalogue between November 2025 and May 2026, most within a week of disclosure. The mismatch with enterprise reality is the uncomfortable part. The report says the disclosure-to-exploitation window has shrunk to single-digit days. Between November 2025 and May 2026, CISA added more than 110 vulnerabilities to its Known Exploited Vulnerabilities catalogue, most within a week of disclosure. In one example, Storm-1175 moved from exploiting a web-facing vulnerability to deploying Medusa ransomware in as little as 24 hours. Microsoft’s Red Team makes an important point: a patch is also a disclosure. Every fix points attackers towards the flaw it closes. As AI-assisted analysis makes reversing patches faster and more reliable, the report argues that patch velocity, not simply patch availability, becomes the control that matters. Trend 2: Attack chains are gaining autonomy The report charts a clear progression: September–November 2025: AI assists in orchestrating a campaign, as in the Anthropic-reported espionage case. April–June 2026: Full-chain autonomy is demonstrated in labs. July 2026: Real-world autonomous attacks of increasing complexity appear. Two frontier models, Mythos and GPT-5.5, completed a 32-step attack chain against an emulated enterprise with no human help. The test environment had no defenders. The UK AI Security Institute reached a similar finding independently. GPT-5.5 was the second model to solve its end-to-end corporate network attack simulation, a task AISI estimates would take a human about 20 hours. Open-weight models lag closed models at orchestrating attacks by about seven months. In the wild, early July 2026 saw the first documented automated ransomware extortion attack, named JADEPUFFER by Sysdig. Microsoft has seen AI-orchestrated intrusions that share elements with it. Initial access consistently came from internet-exposed services running known-vulnerable software. The report is measured on this point. Volumes of AI-orchestrated activity remain low. In most observed real-world operations, complex end-to-end intrusions still retain meaningful human direction. The Red Team's framing is the most useful one: AI doesn't create a new class of attack, it collapses the effort needed to find and exploit existing attack paths. Trend 3: AI has become an attack surface The report's second takeaway is that attackers are already targeting AI itself. The adoption numbers explain why. 88% of enterprises are experimenting with agents, and 82% of leaders plan broader rollouts within 12–18 months. The report cites industry projections of roughly 1.3 billion agents in production by 2028. What attackers are doing to AI systems: Four techniques accounted for roughly 90% of observed attack activity in telemetry from Azure AI workloads: malicious link injection (52%), jailbreaks (16%), tool and agent abuse (12%), and identity and credential abuse (10%). Memory poisoning: An attacker who can place content anywhere an agent reads can often place it where the agent remembers. Email is the dominant pathway the Red Team has observed. Human-in-the-loop isn't a complete control: Red team testing saw approval prompts ignored, or bypassed by a policy stored in poisoned memory. Developer tools turned against their owners: The "s1ngularity" malware hijacked locally installed AI command-line tools to hunt for secrets. It leaked about 2,000 secrets and 20,000 files across 225 victims. AI browsers: In daily use at more than 40% of organisations in Microsoft's dataset, they were the initial infection vector in incidents involving 57 malware families in a May 2026 analysis. Chat histories as a target: Malicious AI-assistant extensions reached nearly 900,000 installs and more than 20,000 enterprise tenants, harvesting AI chat histories that often contain code, architecture and credentials. The identity implications are direct. Each agent needs its own identity, not one borrowed from an employee, and a named human sponsor. The report also treats revocation latency, the time to cut off a compromised agent, as a measured outcome. Trend 4: The front door is still identity AI changes the speed and personalisation of social engineering. It hasn't changed where attacks start. Initial access in Defender Experts data: User execution: 30% Valid accounts: 20% Malicious copy-and-paste: 13% Phishing: 11% Together, user execution and valid accounts account for over half of observed activity. In incident response engagements, phishing as an initial access vector jumped from 7% to 23% year on year. The standout numbers: ClickFix: Defender saw user-pasted malicious commands on more than 1.1 million unique devices between February and early May 2026, roughly an 8x increase. AiTM: URLs accounted for 45% of the identified phishing techniques in the report’s breakdown. Separately, the share of AiTM phishing and token-theft attacks more than doubled during the first six months of 2026, although the report notes that their overall share remained comparatively small. Teams vishing: Weekly confirmed malicious volume increased 502% year on year. Per attempt, 48% of vishing calls kept the victim engaged for more than 20 seconds, and 30% lasted more than one minute. When a call succeeds, attackers can persuade the victim to install a remote-management tool and complete reconnaissance in two minutes or less. Business contact impersonation (BCI): The report introduces this term for conversations that start with a trusted-looking contact. Microsoft detected more than 46 million attacks in 12 months, with a 121% spike in April 2026. The share of first-contact messages that explicitly asked for money or documents fell from 17% to 3%. The first message is deliberately bland, like "Are you at your desk?" Password attacks declined 26% year on year, which the report describes as strong evidence that MFA and passkeys are forcing attackers to pivot. That pivot includes techniques such as fatigue attacks, AiTM phishing and token theft designed to circumvent conventional MFA. Trend 5: Attackers are inheriting trust rather than breaking in The report's headline theme is that risk is increasingly interconnected. Threats travel through the trusted relationships between identities, software supply chains, partners and cloud platforms. The numbers: Supply chain: Major open-source ecosystems saw attacks roughly every ten days, accelerating through Q2 2026. Shai-Hulud 2.0 affected 25,000 repositories. Megalodon backdoored 5,561 GitHub repositories in under six hours. Trusted signing: In May 2026, Microsoft disrupted Fox Tempest, a "malware-signing-as-a-service" operation that obtained genuine certificates for ransomware loaders and infostealers. Microsoft revoked over a thousand fraudulent code-signing certificates. Legitimate access: An unsanctioned remote monitoring tool is now one of the most reliable mid-stage indicators of a human-operated intrusion. Cloud identity: Cloud identity abuse was the most observed technique against critical infrastructure, representing 78% of the technique mix in Microsoft’s data for March to June 2026. Hybrid intrusions: The Storm-2885 case showed an attacker using a privileged cloud identity to close and downgrade security alerts. The report says identity governance and alert-handling workflows deserve Tier 0 treatment. Dwell time: DART data shows a statistically significant increase in dwell time year on year, meaning organisations took longer to detect intrusions. Ransomware shows the same ecosystem pattern. Qilin led leak-site data with 16.4% of victims, up 386%. Defender detections tell a different story, with Akira at 22%. Trend 6: Defence works best when it's connected The report is not only a catalogue of threats. The strongest defensive evidence: Disruption works. Following the March 2026 disruption, Tycoon2FA activity had fallen 95% from its November 2025 peak by June. Its share of CAPTCHA-gated phishing declined from 76% in December 2025 to 12% in June 2026. Correlation is the highest-leverage variable. The report argues that how well defenders share and correlate signals across endpoint, identity, cloud, email and network is one of the highest-leverage strategic variables under their control. AI is also changing defensive operations. The report describes AI-assisted triage, incident summarisation, hunting-query generation and detection engineering as ways to accelerate investigations and allow analysts to concentrate on higher-value work. Automated disruption can compress response time. The report says that when a correlated incident reaches a defined confidence threshold, defensive systems can automatically isolate devices, disable compromised accounts, revoke sessions or quarantine affected cloud resources. It also stresses the importance of appropriate governance and human oversight for high-risk AI actions. The report also recommends changing what leaders measure. It suggests moving from patches deployed to exposure reduced, detection coverage increased and time-to-mitigate compressed. What the MDDR recommends: ten security priorities The report starts its recommendations with the foundations: Secure by Design, Secure by Default and Secure Operations, applied through identity-centric Zero Trust. Microsoft says these keep the priorities below durable as AI adds more identities, applications, agents and dependencies to govern. Govern cyber risk at leadership level. Report identity exposure, patch latency, agent permissions, critical dependencies, dwell time and recovery readiness to the board. Defend identity as the primary control plane. Deploy passkeys and phishing-resistant MFA, reduce privilege and govern human and non-human identities. Invalidate and rotate tokens and session credentials quickly. Establish governance, visibility and data controls for AI. Keep visibility of approved AI tools, services and agents, and monitor for unauthorised or unmanaged use. Apply sensitivity-aware access and data protection to the data those systems can reach. Reduce exposure and edge risk. Continuously discover internet-facing assets and patch edge devices quickly. Centralise high-fidelity logging, enforce strong authentication and combine network visibility with threat intelligence. Focus on cross-signal correlation. Correlate endpoint, identity, cloud, application, email and network signals to detect intrusions earlier. Correlation also helps defenders anticipate attack paths and likely targets. Enact a continuous threat and vulnerability management model. Combine asset visibility, vulnerability identification, threat detection and AI-accelerated insight into a single continuous programme. Validate exposure through proactive testing. Run assume-breach exercises on cloud services, SaaS platforms, APIs and workflow automation. Prioritise them by where your highest-value data is stored, accessed or aggregated. Secure software dependencies. Harden software installation, keep a software inventory and validate provenance. Monitor packages and prepare for rapid containment. Participate in collective defence. Share actionable threat indicators and victim-informed intelligence with trusted partners and law enforcement. This supports coordinated tracking, investigation and disruption. Prepare for long-horizon technology transitions. Build a cryptographic inventory and advance post-quantum planning alongside AI governance. Read together, the numbers tell one story: the attacker’s workflow is becoming faster and less expensive. AI can shorten vulnerability discovery, exploitation, secret discovery and lateral movement, while organisations still face the slower operational work of testing, coordinating and deploying safe changes across complex environments. At the same time, agent identities can proliferate faster than organisations can inventory, govern and revoke them The defining question for boards today is not whether disruption will occur, but whether the organization can continue operating, contain harm, recover quickly, and maintain trust when it does. Source: Microsoft Digital Defense Report 2026, Version 1.1. Reporting period: July 2025–June 2026.ESPC Microsoft 365 and AI 2026 Event Guide
Event at a Glance ESPC is Europe's premier Microsoft 365 and AI conference. It brings together IT professionals, business leaders, developers, architects, partners, MVPs, community leaders, and Microsoft experts to learn, connect, and explore the latest innovations across Microsoft 365, Copilot, Teams, SharePoint, and more. Microsoft is a lead partner and headline sponsor, using ESPC as a key opportunity to engage with customers, partners, and the Microsoft community. Dates: November 30 - December 3, 2026 Location: RAI Amsterdam, Netherlands Venue: RAI Amsterdam, Europaplein 24, 1078 GZ Amsterdam, Netherlands (Entrance C) Hashtag: #ESPC26 Microsoft Role: Headline Sponsor Sessions: 35+ Microsoft-led Speakers: 100+ (MVPs, RDs, Microsoft and community members) Why Attend ESPC 2026? ESPC is where the Microsoft community comes together to learn, connect, and shape what’s next. From Microsoft keynotes and product-maker sessions to hands-on demos, community meetups, and networking opportunities, attendees gain direct access to the people building the technologies they use every day. ESPC is known for its welcoming community atmosphere, making it easy to learn from peers, share ideas, and build meaningful professional relationships. Learn from Microsoft - Hear directly from Microsoft leaders, engineers, product makers, and customer experience experts as they share the latest developments across Microsoft 365, Copilot, Teams, SharePoint, Power Platform, Security, Fabric, Azure, and AI. Explore What's New in AI and Copilot - Discover how organizations are adopting AI, deploying Copilot, building agents, and transforming productivity. Gain practical guidance, real-world insights, and technical knowledge you can take back to your team. Get Hands-On with Innovation - Visit the Microsoft Innovation Hub to experience live demos, engage with product experts, explore new capabilities, and participate in interactive experiences designed to help you learn by doing. Connect with the Community - Meet MVPs, partners, customers, developers, architects, IT professionals, and community leaders from around the world. Whether in a session, the Community Lounge, a meetup, or a networking event, ESPC creates opportunities to build lasting connections. Return with Actionable Ideas - Beyond inspiration, ESPC focuses on practical learning. Attendees leave with new skills, proven approaches, and fresh perspectives they can immediately apply to modernize collaboration, accelerate adoption, strengthen governance, and drive AI-powered transformation within their organizations Microsoft Presence Microsoft will have a significant presence throughout the conference, including: Microsoft keynotes and product announcements Product makers, engineers, and customer experience leaders Microsoft-led breakout sessions Innovation Hub experience on the expo floor Innovation Stage lightning talks Ask the Expert opportunities Executive engagement activities Women in Tech & Allies programming Community meetups and networking experiences Meet the Microsoft Keynote speakers Jeff Teper, Executive Vice President, Microsoft Apps & Agents Karuana Gatimu, Director, Microsoft SCALE Experience Group, AI & Collaboration Vesa Juvonen, Principal Product Manager Keynotes Microsoft Opening Keynote | Tuesday, December 1 | 9:00 AM The AI-Powered Enterprise Speaker: Jeff Teper, Executive Vice President, Microsoft Apps & Agents Microsoft's opening keynote will explore how the biggest AI value gains extend beyond individual applications and personal productivity gains. They emerge when organizations connect people, knowledge, business processes, data, workflows, and agents into a unified operating model. You can expect valuable insights into business transformation trends, product innovation, and demos to show how everyday work is evolving. Whether you're a decision maker, business leader, or technology professional, this session will offer practical perspectives on navigating the next wave of digital transformation. Demonstrations Miceile Barrett, Principal Group Product Manager, Michel Bouman, Senior Program Manager, Kendra Springer, Principal Group PM Manager Microsoft Product Keynote | Wednesday, December 2 | 9:00 AM Leading Through Change: Fireside Conversations on AI and Business Transformation Speaker: Karuana Gatimu, Director of the Microsoft SCALE Experience Group, AI & Collaboration A product-focused keynote highlighting customer adoption, community innovation, and practical approaches for leveraging Microsoft 365 Copilot, agents, and modern workplace technologies. Known for translating complex technology into actionable guidance, Karuana will share practical insights, real-world examples, and best practices that you can take back to your teams. From collaboration and productivity to AI-powered innovation, this keynote will provide valuable inspiration for organizations looking to maximize their Microsoft investments. Closing Keynote | Thursday, December 3 | 9:00 AM Crafting the Next Era of Work with AI and Empathy Speaker: Vesa Juvonen, Principal Product Manager, Microsoft As organizations continue to embrace AI, one question becomes increasingly important: how do we balance technological advancement with human connection? In this keynote, Vesa Juvonen will explore how innovation and empathy can work together to shape the future workplace. Through practical examples and relatable insights, Vesa will share ideas for embracing new technologies while keeping people at the center of transformation efforts. Whether you're leading organizational change, building solutions, supporting users, or exploring ways to work smarter, this session will provide actionable ideas to help you navigate the evolving world of work. Microsoft sessions Tuesday: 10:15-11:15 - Frontier transformation with Microsoft Copilot and Work IQ with John Mighell, Microsoft / Shanna Bosmans, Microsoft 10:15-11:15 - Microsoft Teams: Harnessing agents where work gets done with Matt Slomka, Microsoft 11:45-12:45 - Agent 365: Securing, Governing, and Managing the Agentic Enterprise with Sesha Mani, Microsoft / Vinod Kurpad, Microsoft 11:45-12:45 - Extending Microsoft Copilot: Understanding Your Options with Vesa Juvonen, Microsoft / Paolo Pialorsi, Microsoft 11:45-12:45 - OneDrive: Your Hub for Productivity and Collaboration Excellence (Product Team Overview) with Arjun Tomar, Microsoft / Lincoln DeMaris, Microsoft 14:00-15:00 - Harnessing Connectors to Power Intelligent Agents in Microsoft 365 with Manas Biswas, Microsoft 15:15-16:15 - Modernize Legacy Systems for the Copilot Era with SharePoint Embedded with Marc Windle, Microsoft / James Eccles, Microsoft 15:15-16:15 - Copilot Cowork in Action: What It Is, How to Get It & What You Can Do With It with Melissa Hale, Kerv / Daniel Laskewitz, Microsoft 16:45-17:45 - Giving your office eyes, ears and a brain with Michel Bouman, Microsoft / Matt Slomka, Microsoft 16:45-17:45 - Build Once, Ground Everywhere: Developing Agents with the WorkIQ API with Shyam Narayan, Microsoft / Yogesh Ratnaparkhi, Microsoft Wednesday: 10:15-11:15 - SharePoint: The Knowledge Platform for Copilot & Agents (Product Team Overview) with Zach Rosenfield, Microsoft / Miceile Barrett, Microsoft 11:45-12:45 - OneDrive: Your Hub for Productivity and Collaboration Excellence (Product Team Overview) with Arjun Tomar, Microsoft / Lincoln DeMaris, Microsoft 14:00-15:00 - Secure your Copilot Era: 3Rs you should care: Readiness-Relevancy-Resiliency with Brad Gussin, Microsoft / Kartik Pullabhotla, Microsoft 15:15-16:15 - Unlocking Business Value with Copilot, Agents, and Content Automation with Bryan Wofford, Microsoft / Karuana Gatimu, Microsoft 16:45-17:45 - Digital Me: Meet Your Microsoft Scout with TBA, Microsoft 16:45-17:45 - M365 Content Governing Agent powered by SAM. Governing Content at the Speed of AI with Sanjoyan Mustafi, Microsoft / Jill McClenahan, Microsoft Thursday: 11:45-12:45 - How to avoid “(fin)Ooops” in AI: practical tokenomics for Copilot agents with Hanna Engel, Microsoft 11:45-12:45 - MCP in Power Platform: One Year Later – Building Custom MCP Servers with Low Code with Daniel Laskewitz, Microsoft / Mats Necker, MVP, dhino 15:15-16:15 - From Conversation to Action: Building Copilot Apps That Transform Work with Vesa Juvonen, Microsoft / Bert Jansen, Microsoft Community Sessions There are over 100 sessions presented by the Microsoft Community – Microsoft Most Valuable Professionals (MVPs), Regional Directors, Microsoft Global Community Initiative Board Members and Regional Leads, Microsoft Partners and more. ESPC also has a Programme Team that curates all of the content for the event. Thank you Luise Freese, Maarten Eekels, Rik Hepworth, and Chris O’Brien for your curation, partnership and working so hard to architect a fabulous programme for 2026. Learn more about the team here: European SharePoint Conference 2026 | ESPC 2026 Microsoft Innovation Hub The Innovation Hub serves as Microsoft's home on the ESPC expo floor and gives attendees opportunities to interact directly with product teams through demos, conversations, and hands-on experiences. We are excited to announce that Dona Sarkar, Principal CX Program Manager, Microsoft will be leading a learning promptahon workshop in the Ideation Lab. More info and a few other activations with names you know to be announced. Innovation Hub Zones Innovation Stage Lightning talks Live demos Product-maker presentations Demo Stations Microsoft Copilot Copilot Studio and Agents OneDrive & SharePoint AI Adoption Surface + AI Skilling Bar Surface devices with AI integration AI skilling experiences Practical learning scenarios Ideation Lab Interactive workshops Community collaboration Future-of-work discussions Planned Hours Tuesday: 10:00 AM - 7:00 PM Wednesday: 10:15 AM - 6:00 PM Thursday: 10:00 AM - 3:00 PM Community Activities Microsoft is partnering closely with the broader Microsoft community to deliver: Community Lounge meetups Ask the Expert activities Microsoft Most Valuable Professional (MVP) engagement Microsoft Global Community Initiative (MGCI) engagement Innovation Stage presentations Community networking opportunities Community activities are integrated directly into the Innovation Hub and Community Lounge experience, creating opportunities for attendees to engage with Microsoft leaders, MVPs, partners, and community organizers. Women in Tech & Allies Activities WIT Community Lounge Meetup Calling all Women in Tech and Allies! Join us during lunch on the first day of ESPC to say hello, make new connections, and perhaps find an ESPC show buddy. This is a casual meetup with no formal agenda. Simply pick up your lunch and join us at the tables marked with WITA signs. Date: Tuesday, December 1 Time: 12:45 –2:00 PM CET Location: Community Lounge Inspire Stage breakout Leading with Allyship: Building Inclusive Communities in the Age of AI Date: Wednesday, December 2 Time: 10:15–11:15 AM CET Location: Inspire Stage Hosts: Heather Cook, Principal Customer Experience Manager, Microsoft and Femke Cornelissen, Chief AI Transformation Officer, Wortell Panelists: Jayshree Ostwal, MVP, Manager, AI Solution Architect, Avanade, Lindsay Shelton, MVP, Digital Workplace Advisor, Epiq, Merethe Stave, MVP, Chief Customer Officer and Senior Cloud Architect, CloudWay, Onyinye Madubuko,MVP, Senior M365 Consultant, Ergo, Reshmee Auckloo, MVP, Modern Workplace Associate Manager, Avanade Women in Tech & Allies Lunch Shaping the Future Together: Women in Tech and Allies Driving Change Date: Wednesday, December 2 Time: 12:45-2:00 PM CET Location: Elicium 1 Host: Heather Cook, Principal Customer Experience Manager, Microsoft Panelists: Danielle Moon, Sr. Specialist – AI Business Process, Women in Power Platform, Microsoft, Karuana Gatimu, Director of the Microsoft SCALE Experience Group, AI & Collaboration, Microsoft, Jessie Hwang, Customer Experience Product Manager, Microsoft, Hanna Engel, Cloud Solution Architect | Azure & AI, Microsoft, Dona Sarkar, Chief Troublemaker | Enterprise AI Advocacy, Microsoft, Ioana-Cristina Sbiera, Field Integrated Marketing Manager, Microsoft Microsoft Event Team Executive Producer - Heather Cook, Principal Customer Experience Manager, Microsoft Content Narrative Lead – Bryan Wofford, Principal Customer Experience Manager, Microsoft Community & Innovation Hub Lead – Jonathan Jones, Customer Experience Program Manager, Microsoft ESPC Organizers Thank you to our event producers: Bridgette Robertson, Partnership Development & Programme Executive, Ella Murphy, Marketing Manager, Joanne Mangan, Product & Partner Manager, John Carroll, Business Development Lead, Katie Boland, Events Administrator, Kevin Monahan, General Manager, Sarah Grech, Events Coordinator, Sean Colleran, Marketing Executive Links and Social Event Resources - ESPC Website Social Media Hashtag – #ESPC26 X/Twitter – ESPC Community LinkedIn – ESPC LinkedIn Instagram – ESPC_Community See you there! ESPC 2026 represents an important opportunity to connect product makers, customers, partners, MVPs, and the broader Microsoft community in one of the most engaged Microsoft ecosystems in the world. Across four days of learning, networking, hands-on experiences, and community-led conversations, Microsoft will showcase the latest innovations in Microsoft 365, Copilot, AI, Teams, SharePoint, Power Platform, Fabric, Security, and Azure while creating meaningful opportunities for attendees to learn, connect, and share what’s next. We look forward to welcoming the community to Amsterdam and making ESPC 2026 a memorable, inclusive, and impactful experience for everyone involved. See you at ESPC 2026. #ESPC26618Views0likes0Comments