document processing
7 TopicsIgnite’26 Spotlight: Announcing Microsoft Baseline security mode 2026 General Availability
Security is Microsoft’s top priority At Microsoft, security is our top priority. Through the Secure Future Initiative (SFI), we're turning lessons learned into stronger security across everything we build and deliver. Customers consistently ask three questions: What is Microsoft’s secure-by-default benchmark for Microsoft 365, Windows, and Azure? How does SFI translate into better security for customers? Is my tenant’s security posture hardened per Microsoft’s recommendations? Microsoft Baseline security mode (BSM) is designed to help answer these questions. It brings Microsoft's recommended security controls, directly to customers out of the box available to the administrators directly in the Microsoft 365 admin center. First introduced at Ignite 2025, BSM takes another major step forward today. Today at Microsoft Ignite 2026, we're announcing that Microsoft Baseline security mode (BSM) 2026 is now generally available, with a phased rollout across all supported Microsoft 365 cloud environments worldwide. Microsoft Baseline Security Mode marks a significant step forward in making security the default, helping organizations move from fragmented security configurations to a more consistent, integrated approach. It is built on Microsoft’s experience operating secure cloud services, responding to incidents, and applying lessons from the Secure Future Initiative (SFI). BSM combines ease of use with advanced capabilities to help harden your Microsoft cloud services’ security posture, every day, week, and year, with minimal effort. BSM is a Continuous Journey Microsoft Baseline security mode is not a one-time feature; it is an evolving standard. We continue to regularly strengthen the baseline with additional configurations across Microsoft cloud services. BSM 2025 marked the first milestone, starting with Microsoft 365 and Entra. BSM 2026 expands coverage to Purview, Intune, and Dynamics 365, with Azure and Windows in private preview. Future releases are expected to expand the baseline across Microsoft cloud services. Here’s what’s new in BSM 2026 compared with BSM 2025: Expanded with more workloads: BSM 2026 extends protection beyond the original five BSM 2025 workloads (Office, SharePoint, Teams, Exchange, and Entra) to include: o Microsoft Intune o Microsoft Purview o Dynamics 365 o Azure (in Private Preview), and o Windows (in Private Preview). New Applications category: In addition to the three categories that BSM already has, BSM 2026 now covers what applications can do, how they access data, and which permissions they hold. With Applications added, Baseline security mode 2026 spans four categories: o Applications o Authentication o Devices & Endpoints o Files Expanded coverage within the existing categories: New recommendations include stronger macro security and blocking native COM add-ins in Office, requiring multifactor authentication (MFA) for guest users, requiring dual admin consent for critical Intune operations, disabling classic SharePoint page creation and more. Enable Baseline security mode in the Microsoft 365 admin center As Global Administrator, you can navigate to: Microsoft 365 admin center → Org Settings → Security & Privacy → Baseline security mode to get started with BSM. BSM 2026 introduces 24 new settings. Administrators can apply each setting or run them in simulation mode to evaluate potential impact within their tenant. BSM provides flexibility and control, enabling administrators to manage each setting independently. This phased approach is designed to help administrators transition to secure-by-default configurations. Let’s deep dive into some of the BSM 2026 settings. Microsoft Baseline security mode 2026 settings Applications The Applications category in BSM 2026 addresses what apps can do, how they access data, and the permissions they hold. In BSM 2026 we are making generally available 16 applications settings. Highlights are below. For the full list see the Microsoft baseline security mode – Learn article New apps require assignment of the tenants allowed to access them (Entra) Allowing applications to span multiple tenants is a security risk. With this Entra setting, admins are empowered to control the tenants that a given app is allowed to be instantiated. Block COM add-ins that aren't on the admin allow list (Office) In the same fashion as Apps, admins can control the list of COM add-ins that are allowed in their organization. Require external users to wait in the lobby before joining meetings (Teams) Security risk increases when external users are brought into the workforce as the policy drift might happen for them. Much like there are controls for secure collaboration, for secure Teams meetings admins can now require externals users to wait in the lobby before joining meetings. Disable guest users from having eDiscovery roles (Purview) Purview eDiscovery roles are highly privileged, allowing users to search a broad range of Microsoft 365 content and export the results. Assigning these roles to external guests poses a significant risk unless those guests have been vetted and explicitly authorized for this access. This BSM 2026 setting blocks external guests from holding eDiscovery roles by default. Block creation and editing of classic pages in SharePoint sites (SharePoint) This setting prevents users from creating new classic SharePoint pages or editing existing ones, including publishing, wiki, and web part pages. Existing published pages remain viewable the setting does not delete them. It helps reduce risks from harmful script injection and unsupported legacy customizations while encouraging adoption of modern SharePoint experiences. Report applications without Exchange App RBAC permissions (Exchange) This setting identifies applications accessing Exchange without Exchange App RBAC (role-based access control) permissions, giving administrators visibility into apps that may have overly broad access. These insights help administrators prioritize permission reviews and identify opportunities to limit app access to the mailboxes they need. Require scoped access to files and sites for High Privileged Applications (HPA) (SharePoint) This setting requires highly privileged applications to use a defined, limited scope when accessing OneDrive and SharePoint files and sites, rather than relying on unrestricted, organization-wide access. It helps reduce the risk of unauthorized access and data leakage from broadly permissioned apps. Authentication The Authentication category in BSM strengthens how users and apps sign in, helping reduce credential theft, account takeover, and access through outdated authentication methods. In BSM 2026 we are making generally available 4 authentication settings: Don't allow Microsoft 365 trial tenants to federate with your organization (Teams) Block external apps from using pre-authenticated tokens to access OneDrive and SharePoint content (SharePoint) Enable Continuous Access Evaluation (CAE) (Dynamics 365) Require MFA (multi-factor-authentication) for guests and external users (Entra) BSM 2025 we brought in MFA for admin accounts and upleveling that baseline for external users. This setting is designed to significantly reduce the risk from external access across Microsoft 365 services, including Exchange, SharePoint, OneDrive, Teams, and Microsoft 365 apps. To strengthen your security posture, we strongly recommend requiring MFA for external users. Devices & Endpoints Stronger device security starts with hardening through a device management soluion like Intune. The Devices & Endpoints category introduces four critical Intune security settings to strengthen device protection: Alert users when a new device is enrolled (Intune) Require a device compliance policy (Intune) Restrict the number of devices a user can enroll (Intune) Require a second admin to approve sensitive actions (Intune) The key safeguard: Two admins, one critical action. Sensitive Intune changes require a second administrator's approval, helping prevent unauthorized or accidental changes. Azure – now part of Microsoft Baseline security mode (Private Preview) Microsoft Baseline security mode expands to include seven settings across Azure Storage and Azure Key Vault, now available in Private Preview. The Azure Storage settings require secure transfer, prevent anonymous public access, enforce a minimum TLS version, and prevent Shared Key authorization; the Azure Key Vault settings restrict public network access and require purge protection and soft delete. Together, these settings provide an Azure Policy-based foundation that gives administrators visibility into security posture and workload impact before enrolling ready scopes for enforcement. Learn more about Azure settings -part of Microsoft Baseline security mode. Enroll in the preview https://aka.ms/M365BaselineSecurityModeEnroll Windows – now part of Microsoft Baseline security mode (Private Preview) Microsoft Baseline security mode expands to include three Windows settings, enable virtualization-based security (VBS), enable secure boot, and enable the security processor, now available in Private Preview. The VBS setting isolates security-sensitive operations from the main operating system; the secure boot setting helps prevent malicious software from loading at startup; and the security processor setting uses dedicated hardware to help protect sensitive data, including credentials and keys. Together, these settings provide a foundation that gives administrators visibility into Windows security posture and helps strengthen device protections. Learn more about Windows baseline protection – part of Microsoft Baseline security mode. Enroll in the preview https://aka.ms/M365BaselineSecurityModeEnroll BSM enhancements to support your security journey (Private Preview) In response to your feedback, BSM introduces four new features in private preview to help administrators review security posture, share progress, and put configurations in context. Preview features are available to a limited set of customers and may change before general availability. Action oriented dashboard. Review your BSM security posture through a dashboard focused on the settings that need attention. Downloadable security and compliance reports. Download reports to support security reviews and compliance discussions, and share a view of your BSM posture with stakeholders. Regulatory framework mapping. View BSM settings in the context of regulatory frameworks to support compliance and audit conversations. BSM does not guarantee compliance with any law or regulatory framework. Customers remain responsible for their own compliance obligations. Geo locations (for Multi-Geo tenants). Bring geographic context into your review of BSM posture across Multi-Geo environments. Enroll in the preview https://aka.ms/M365BaselineSecurityModeEnroll Figure 7. Baseline security mode dashboard showing posture summaries, category progress, and regulatory framework coverage. On the roadmap: BSM 2025 as the default for all new Microsoft 365 tenants As part of strengthening our customers’ secure-by-default posture, BSM 2025 will become the default configuration for all new Microsoft 365 tenants. Following its announcement at Ignite 2025, we strongly encourage existing Microsoft 365 and Entra customers to opt in to all BSM 2025 settings. On-Premises Baseline security mode As outlined in early November 2026 here, we are making new investments to reduce On-Premises security risks. Within the Secure pillar of the on-premises security initiative, we’re hardening the products themselves through On-Premises Baseline Security Mode, starting with supported Exchange Server, SharePoint Server, and Skype for Business Server workloads. On-Premises Baseline Security Mode is designed to make the default security posture stronger, reducing the number of recommended security settings administrators must configure and maintain manually. For supported on-premises server workloads, it starts with a validated and tested secure-by-default configuration from initial deployment, while preserving administrator control. To learn more, check out: New Investments to Reduce On-Premises Security Risk | Microsoft Community Hub Get started To get started with Microsoft Baseline security mode 2026, as it rolls out, sign in with your global admin account to Microsoft 365 admin portal and open Baseline security mode settings. If you are new to Microsoft 365, learn how to try or buy a Microsoft 365 subscription. With built-in dashboards and telemetry, BSM provides visibility into security configurations and a predictable, secure-by-default foundation to help organizations of all sizes reduce legacy risks, strengthen protection, and support compliance and audit readiness References: Microsoft baseline security mode – Learn article Microsoft Secure Future Initiative Azure Baseline security mode – Learn more Windows baseline protection – Ignite announcement Microsoft Corporate adopts BSM - https://aka.ms/msd-baselinesecuritymode Need help. Engage with FastTrack – https://aka.ms/BSMFastTrack Join us at Ignite in our sessions: LTG1168: The foundation of Trusted AI: SharePoint security and resiliency, Thurs 11/19, 9:00-9:15 AM, Moscone South | The Hub, Lightning Talk 2 BRK211 - Secure and Govern Microsoft Copilot and Cowork, Thurs 11/19, 11:30 AM - 12:15 PM, Marriott Marquis | Lower B2, Yerba Buena Salon 9 Thank you!2.2KViews0likes0Comments
Unlocking Microsoft 365 Adoption in Engineering, Manufacturing, and Regulated Industries
Executive Feedback to Microsoft Leadership: Expanding the Value of Microsoft 365 Beyond Cloud-First Workflows Executive Summary Microsoft has successfully built the industry's leading cloud collaboration ecosystem around Microsoft 365, OneDrive, and SharePoint. The strategy has delivered substantial value for information workers, distributed teams, and organizations pursuing cloud-first operating models. However, there is a significant and often overlooked customer segment that remains underserved: engineering, manufacturing, healthcare, medical device, industrial, laboratory, defense, and other regulated organizations whose primary workflows are intentionally built around file-based repositories, network shares, PDM/PLM systems, and controlled document environments. The challenge is not opposition to cloud technology. The challenge is that many of these organizations prioritize data integrity, traceability, predictability, and workflow continuity above all else. As a result, they often perceive modern Microsoft productivity capabilities such as AutoSave, coauthoring, and version history as being unnecessarily coupled to OneDrive and SharePoint. This creates an important business opportunity. Microsoft could unlock substantial additional Microsoft 365 adoption and customer goodwill by extending modern document protection and collaboration capabilities to local, network-hosted, and hybrid file environments without requiring a complete migration to OneDrive or SharePoint. This is not a request to replace cloud services. It is a request to recognize that cloud-first and file-based workflows can coexist. The Opportunity Is Larger Than It Appears Many of Microsoft's largest enterprise customers operate in environments where files are not simply documents. They are: Design history files Manufacturing records Engineering drawings Validation reports Device master records Controlled procedures Laboratory data Regulatory submissions Quality records For these organizations, file location, revision control, ownership, auditability, and retention are operational requirements rather than convenience features. Microsoft itself acknowledges that Office AutoSave currently requires files to be stored in OneDrive or SharePoint. Files opened from traditional file-system locations do not receive the same experience. As a result, many organizations feel they must choose between: Maintaining proven operational workflows. Accessing Microsoft's most advanced productivity features. That is a business decision many organizations simply refuse to make. The Real Barrier Is Not Technology. It Is Trust. Discussions around cloud adoption are often framed as a resistance-to-change problem. Research consistently suggests otherwise. Studies examining enterprise cloud adoption repeatedly identify security concerns, data privacy concerns, and control over organizational information as major barriers to adoption. One study found security concerns dramatically increased the likelihood that organizations would reject cloud adoption. Similarly, KPMG's cloud transformation research notes that concerns about data loss, audit findings, compliance issues, and operational risk can slow or limit cloud initiatives. The lesson is important: Organizations rarely reject technology because it is new. They reject technology because they do not trust it with critical business information. Once users experience: unexpected file overwrites, synchronization ambiguity, permission confusion, data residency uncertainty, conflicting document versions, trust declines rapidly. Trust, not functionality, is often the limiting factor. Engineering Users Experience the World Differently Microsoft's cloud ecosystem was largely designed around information-worker collaboration. Engineering organizations frequently operate under different assumptions: Information Worker Priority Engineering Priority Seamless sharing Data integrity Anywhere access Traceability Real-time collaboration Configuration control Ease of use Auditability Cloud accessibility Revision certainty Neither approach is wrong. The challenge is that Microsoft increasingly optimizes for one while under-serving the other. An Example: AutoSave AutoSave is one of the most valuable additions Microsoft has made to Office. The value proposition is obvious: Reduced data loss Improved productivity Lower cognitive burden Better user confidence Microsoft's own documentation describes AutoSave as continuously saving changes while users work, but only when documents reside in OneDrive or SharePoint. From Microsoft's perspective, this design is understandable. From the customer perspective, the message often becomes: "Modern document protection is available, but only if you adopt Microsoft's preferred storage architecture." Many customers view this not as a technical limitation, but as product segmentation. Microsoft Could Learn from Version Control Systems Modern software development solved multi-user document conflicts decades ago. Git was specifically designed around realities such as: multiple devices, multiple contributors, offline work, concurrent editing, conflicting changes. Critically, Git assumes conflicts are inevitable. Rather than hiding them, Git exposes conflicts and provides mechanisms to resolve them. Many engineers trust Git precisely because its behavior is transparent. By comparison, file synchronization systems often attempt to abstract away complexity. When synchronization fails, users can no longer determine: which version is authoritative, which edits are newer, what happened, who changed what. The engineering mindset is frequently: Show me the conflict. rather than Hide the conflict and make a decision on my behalf. The Untapped Hybrid Customer Much discussion around Microsoft 365 assumes organizations are either: Cloud-first, or Legacy. In reality, many enterprises are neither. Many operate as hybrid organizations and intentionally will continue to do so. Research from industry and security organizations continues to show persistent adoption of hybrid and multi-cloud architectures driven by governance, security, compliance, and operational requirements. These customers are not rejecting Microsoft. They are already paying customers. They often purchase: Microsoft 365 Windows Azure Teams Active Directory SQL Server Yet many would immediately purchase additional capabilities if Microsoft offered: Local AutoSave Office AutoSave functionality for: NTFS local storage SMB file shares NAS systems PDM-managed documents Local Version History Built-in document time travel without cloud dependence. Hybrid Collaboration Coauthoring capabilities that operate through enterprise file infrastructure. Enterprise Conflict Resolution Visualization and reconciliation of competing document changes. Network-Aware Document Protection The same confidence users experience in OneDrive without requiring migration to OneDrive. The Revenue Opportunity This is not merely a product-improvement request. It is a business opportunity. A significant portion of engineering and regulated industries remain hesitant to migrate entirely into cloud-centric document ecosystems because the perceived operational risks exceed the perceived benefits. Rather than forcing an all-or-nothing decision, Microsoft could monetize a middle path: Microsoft 365 Hybrid Collaboration A premium offering delivering: AutoSave Version History Recovery Conflict Resolution Audit Visibility for enterprise-controlled file infrastructure. Organizations that decline OneDrive adoption today may still eagerly purchase these capabilities. In effect, Microsoft could create incremental revenue from customers who are already committed to the Microsoft ecosystem but currently feel underserved by a cloud-only feature strategy. Recommendation Microsoft should stop treating file-server and network-share users as transitional users waiting to migrate. Many are not transitioning. Many have intentionally chosen architectures optimized for regulatory compliance, engineering rigor, operational control, and data governance. The future should not require choosing between: modern productivity features, and trusted enterprise workflows. The organizations building medical devices, industrial equipment, aerospace systems, manufacturing infrastructure, energy systems, and critical technologies represent some of Microsoft's most technically sophisticated and commercially valuable customers. They deserve first-class support for the workflows they intentionally operate. The opportunity is not to move every customer to the cloud. The opportunity is to bring Microsoft's best innovations to every customer, regardless of where their files live.113Views0likes0Comments
Disable incessant nagware popups
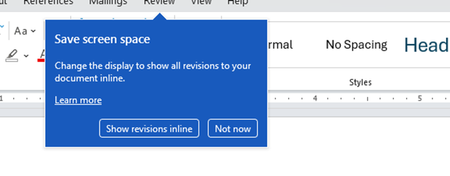
I don't know about everyone else, but I am sick and tired of the nagware pop ups in Word, Excel, PowerPoint, Outlook, etc. Every single product harasses me with pop ups trying to tell me "hey, did you know this feature was here?", "you can do this if you click that", "let me hold your hand through using products you've used for decades even though you don't want daddy Microslop to do that". This is a prime example. I keep getting the same ones again and again and again and everything I've read indicates they should only appear once. But they don't. They keep coming back like a psychotic stalker ex who wants alimony even though you were never married. How do I get this nagware to stop?!678Views1like2Comments
Microsoft Word - Footnote remains on the original page after moving the original reference up
Issue I encountered an issue in Microsoft Word where moving the original footnote reference to an earlier location in the document did not move the footnote itself. The footnote remained on its original page even though the reference had been moved. This was particularly problematic because the same footnote was referenced multiple times throughout the document using cross-references. Cause The footnote is anchored to the original footnote reference in the main text. In my case, Word had somehow lost track of that original anchor, so the footnote stayed on its original page while all cross-references continued to point to it. Solution Hold Ctrl and click the misplaced footnote reference. Word jumps to the original footnote reference in the main text. Cut the original footnote reference (Ctrl+X). Paste it in the correct location using Keep Source Formatting. Press Ctrl+A, then F9 to update all fields. Verify that: the footnote has moved to the correct page, the numbering has updated correctly, all cross-references still work. In my document, one footnote had previously lost its connection to the original reference, so its numbering did not update automatically. That one had to be repaired manually. Important Do not create a new footnote or copy the footnote text itself. Move the original footnote reference in the main text. This preserves the existing footnote, its numbering, and every cross-reference that points to it. I hope this helps someone else. It took me quite a while to figure out what was happening.316Views0likes1CommentWord/PowerPoint are not suitable replacements for Publisher
I’m writing following the guidance that Word and PowerPoint can be used as replacements for Publisher. This feedback is based on completing a real production document, not theoretical use Having just completed a fairly complex, layout-heavy technical document, I thought it only fair to share how that works in practice. In theory, I can see the logic: Word handles documents PowerPoint handles layouts Therefore, between the two, everything should be covered Unfortunately, in reality, this appears to be more of a theoretical exercise than a practical solution. Publisher was clearly designed for: Fixed, page-based layouts Precise positioning of objects Efficient alignment of mixed content (text, images, tables) Producing consistent, professional multi-page documents By comparison: Word is admirably committed to reminding you that it would prefer everything to flow freely, regardless of whether you want it to or not PowerPoint, while better behaved, does seem to assume every page is a standalone slide rather than part of a structured document Both tools can, with enough persistence, be persuaded into doing the job. However, this involves a level of manual intervention, workaround, and general negotiation with the software that feels somewhat at odds with modern productivity software. To put it simply: They are not replacements in any meaningful, real-world sense. The end result can be achieved, but the process is unnecessarily time-consuming, fragile, and prone to unexpected layout changes—particularly when precision actually matters. Replacing a purpose-built publishing tool with two applications that were never designed for that role gives the impression that this use case has been… optimistically simplified. I would strongly encourage Microsoft to either: Provide a genuine page-layout solution within the Office suite, or Enhance existing applications so they can support fixed-layout publishing without constant workarounds At present, the gap left by Publisher is very noticeable for anyone producing structured documents beyond basic text. I appreciate the direction of Microsoft 365 overall, but in this particular area, the experience feels less like an evolution and more like working around a missing tool. Regards Andy699Views1like2Comments
How to restore a single file deleted 6 months ago - using M365 Backup?
My friend's company uses Sharepoint Online, but relevant folders are synced to their OneDrive so they manage everything in File Explorer. I have Microsoft 365 Backup enabled on their Sharepoint site. This company has all the parent folders in "Site Contents". These folders include Sales, HR, Clients, etc. I need to restore a single file out of Sales but it appears I need to restore the entire site first, sync the Sales folder from the site ending in /R0 to my OneDrive, then copy/paste from my File Explorer. Yes, I am a NOOB in Sharepoint. What's the right way to grab this file? And if it's ditching M365 Backup, then that's what I'll do, but I still need to get this file.126Views0likes1Comment