data loss prevention
464 TopicsSecure the data that fuels AI with Microsoft Purview
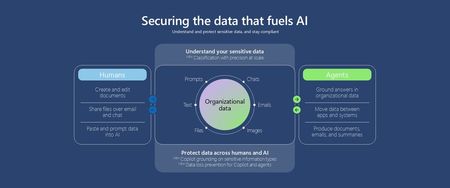
Agents in Microsoft 365 grew 15x year-over-year, and every one of them can reach your organization's sensitive data. AI accesses, creates, and updates data, faster than current classification and labeling can keep up. At the same time, AI apps and agents introduce new surface areas for sensitive data to be exposed such as grounding data, prompts, responses, tool calls and more. Without the right controls, that data exposure can erode customer trust and create regulatory, legal, competitive, and financial consequences. Microsoft Purview helps organizations secure the data that fuels AI. To act quickly and confidently, data security teams need a precise, current understanding of their sensitive data, without extra manual work, and controls that enforce protection across humans, apps, and agents. Purview helps teams understand their sensitive data, protect data across humans and AI, and stay ahead of compliance with the auditability that evolving regulations demand. At Ignite, we're announcing enhanced classification and labeling at scale to help teams get to data protection faster, and new data loss prevention (DLP) controls that protect the data Microsoft Copilot and local agents use. Ignite announcements at a glance Get to data protection faster Stay current with recurring classification refresh (public preview January 2027): Automatically re-classify data that hasn’t been touched in years when classifiers are updated or improved. Deploy faster with enhanced built-in sensitive information types (SITs) (available starting January 2027): Get precise detection out of the box with less manual tuning and customization, starting with the 100+ most widely used SITs, such as credit card and U.S. Social Security numbers, and extending to all built-in SITs over time. Simplify workflows with a unified classification management experience (public preview): Find and manage all your classifiers in one place, with improved search and filtering. Accelerate data protection with auto-labeling scalability improvements (generally available): Now label up to 500,000 files per day, match 20M items in simulation, target sites by attribute instead of hand-picking with adaptive scopes; and apply default library labels to SharePoint libraries for data-at-rest (public preview). Protect data across humans and AI Protect the sensitive data that Copilot uses (public preview January 2027): Apply DLP policies that prevent Copilot from processing files with sensitive data, even when those files aren't labeled. Additionally, Copilot will not process prompts with attached or linked files containing sensitive data. Protect the sensitive data local agents use (public preview January 2027): Gain visibility into local agent activity and apply DLP policies that prevent local agents from processing sensitive data, whether it comes from a prompt or from the files and tools the agent accesses. Additionally, data protection policies can be scoped to specific agents for more granular controls tailored to each agent’s role. Integrate agent activity signals into Unified Agent Risk score (public preview): Purview agent activity and interaction with sensitive data signals now feed into Unified Agent Risk score in Agent 365, so security teams can spot higher-risk agents, prioritize investigations, and apply the right controls. Get to data protection faster AI creates large volumes of new data. More than 2 billion files are uploaded to SharePoint every day, and SharePoint is now the top grounding source for Microsoft 365 Copilot. At that volume, admins can't pause to manually tune and validate classification before enforcing auto-labeling and DLP policies. That's why we're enhancing our built-in sensitive information types (SITs) for precise detection out of the box, so admins can move confidently from detecting sensitive data to enforcing protection. We're starting with the 100+ most widely used SITs, such as credit card and U.S. Social Security numbers, and will extend these enhancements to all built-in SITs over time. To secure data effectively, classification must keep pace as your data estate grows and your definition of what's sensitive evolves. Purview classifies content as it is accessed, created, and shared, but AI tools can also access and process older files that no one has opened in years. If those files were never classified, protection policies have nothing to act on, leaving the sensitive data inside them exposed to AI. Last year, we introduced on-demand classification to scan and classify that older content, so organizations can identify and protect sensitive data in older files before AI accesses it. Now, we're evolving it from a point-in-time scan into a recurring classification refresh. After a baseline scan, Purview will automatically re-classify existing content when an enhanced built-in sensitive information type (SIT) rolls out or your organization adds or updates custom SITs, so protection reflects the latest understanding of what's sensitive. For example, when the enhanced built-in credit card number SIT rolls out, the next refresh can identify card numbers in a years-old customer contract, so DLP can prevent Copilot from processing it, even if no one has opened or edited the file. The baseline scan and two recurring classification refreshes will be included in Microsoft 365 E5 licenses in the coming months. Getting to protection faster also means making classification easier to manage. The new unified classification management experience brings all classifiers, including sensitive information types, exact data match, trainable classifiers, and document fingerprinting, into one place, with improved search and filtering. Once Purview classifies sensitive data at scale, new auto-labeling scalability improvements help admins apply sensitivity labels at scale, up to 500,000 SharePoint and OneDrive files per tenant per day (up from 100,000) and preview up to 20 million matched items in simulation mode before turning a policy on (up from 4 million). Admins can now apply auto-labeling policies to every SharePoint site that matches a rule, such as all sites with “Finance” in the URL, and with no cap on matching sites, one policy keeps covering new sites as the organization grows. Finally, admins can extend a SharePoint library's default sensitivity label, previously applied to new and modified files, to data-at-rest, without anyone opening or editing the files. This helps organizations scale baseline protection across high-priority sites. Admins can now extend a SharePoint library's default sensitivity label to all files in the library, including data-at-rest. Protect data across humans and AI Sensitive data can be exposed in Copilot in three ways: text typed into prompts, files attached or linked in prompts, and content retrieved as grounding data. Organizations need to protect all three without getting in the way of productive AI use. Admins can already use Purview sensitivity labels and DLP policies to restrict Copilot from processing labeled files and emails, as well as prompts containing sensitive information. Today, we're taking that further: admins can protect the data Copilot uses, even when files aren't labeled. When Copilot retrieves content to ground a response, Purview can detect sensitive data such as financial information or personal ID numbers, and DLP can block Copilot from using it. This helps organizations deploy Copilot more quickly, with confidence. DLP policy to prevent Copilot from grounding responses on files containing sensitive information, even if the file is not labeled. Protection also extends to the prompt itself: admins can now protect sensitive data in Copilot prompt attachments and linked files, in addition to typed text, so sensitive data is covered as it flows into and through Copilot. For example, an employee might ask Copilot to analyze a linked financial planning document that hasn’t been labeled. Without a label, Purview can still identify a SIT, such as an ABA routing number, and apply the organization’s DLP policy to prevent it from grounding the response. The same protection extends to prompts and attachments. With protection integrated into Copilot, organizations can confidently turn AI innovation into everyday impact. In addition to protecting Copilot, Purview currently provides visibility into agent activity and audit records for agents built on Microsoft Copilot Studio and Foundry, helping organizations understand how AI is being used. We are now extending that visibility and bringing new data protection capabilities across agents running locally on Windows devices, including Claude Code, GitHub CLI, the GitHub Copilot app, Claude Desktop, and the Claude Code and GitHub Copilot extensions for Visual Studio Code. Admins can now safeguard the sensitive data local agents use at runtime by blocking prompts and tool calls that contain sensitive information in text, files, and links. Data protection policies can also be scoped to specific agents for more granular controls tailored to each agent’s role. Security teams need a consistent way to identify higher-risk agents, prioritize investigation and scope the right controls. To address that, Purview agent activity and sensitive data interaction signals are now integrated into the Unified Agent Risk score, surfaced in Agent 365. Local agent access to sensitive information is blocked by DLP policy. A local AI coding agent illustrates how interaction-level protection and broader risk-based controls work together. For example, a developer might use Claude Code on a corporate laptop to debug an application. Purview provides visibility into the agent’s activity and interactions with organizational data. As the agent accesses local files and invokes tools, it may attempt to send proprietary source code, API keys, or connection strings to an external AI service or connected tool through a prompt or tool call. A Purview DLP policy scoped specifically for Claude Code agents can identify the sensitive content and block the interaction before the data is exposed at runtime. To evaluate agent behavior, the security and IT teams can also leverage the Unified Agent Risk score to refine policies over time. By extending consistent data protection across a rapidly growing agent ecosystem, Purview helps organizations embrace the next wave of AI innovation with greater confidence. Secure the data that fuels AI Data security admins need to keep pace with AI adoption without compromising protection. With more precise, up-to-date classification and expanded protections for Copilot and agents, Microsoft Purview helps teams get to data protection faster and protect data across AI — turning an understanding of sensitive data into protections built into the workflows people and agents use. Explore these enhancements at Ignite. Browse the Microsoft Ignite 2026 guide to Microsoft Purview to discover sessions, hands-on learning, and one-on-one time with experts.Microsoft Purview: Data Loss Prevention (DLP) vs. Insider Risk Management (IRM)
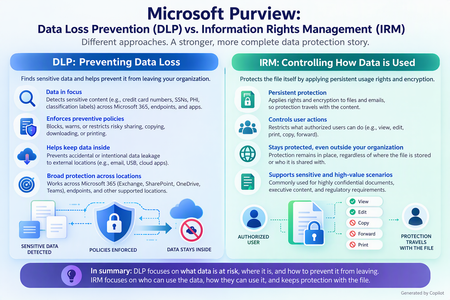
Navigating the Microsoft Purview compliance suite often leads to a common question: what sets Data Loss Prevention (DLP) apart from Insider Risk Management (IRM)? Although these two solutions frequently overlap in organizational security strategies, they address entirely different challenges. In this article, we will explore the core distinctions between them, highlighting how DLP safeguards your sensitive data, while IRM detects and manages risky user behavior before it leads to an incident. The fundamental difference is that DLP focuses on protecting sensitive data, while Insider Risk Management focuses on identifying and managing risky user behavior. Both are Microsoft Purview security and compliance capabilities, but they address different dimensions of data security. Data Loss Prevention (DLP): Determines whether sensitive information is being shared, transferred, or used in ways that violate organizational policies and can automatically prevent those actions. Insider Risk Management (IRM): Analyzes patterns of user activity and contextual signals to identify potential insider threats, including accidental data exposure, intellectual property theft, and other security violations. Side-by-side comparison Capability Purview DLP Purview Insider Risk Management Primary objective Prevent unauthorized disclosure of sensitive data Detect, investigate, and mitigate insider risks Primary focus Data and how it is handled User activities, behavioral patterns, and risk context Key question Is sensitive information leaving the organization or being shared inappropriately? Is a user exhibiting potentially risky behavior? Detection approach Content inspection, sensitivity labels, sensitive information types, and policy conditions Correlation of user activities, risk indicators, and contextual signals Typical triggers Sensitive data emailed externally, copied to USB, uploaded to unauthorized destinations Unusual downloads, repeated data exfiltration activities, or risky actions associated with departing employees Prevention capabilities Directly blocks, restricts, audits, or warns about policy violations Primarily detects and investigates; can initiate mitigation and integrate with DLP for preventive controls Risk analysis Evaluates data and activities against configured policies Correlates activities and indicators to identify potential insider risk Investigation DLP alerts, activity details, and incident reports Risk alerts, user activity timelines, investigation cases, and escalation workflows User awareness Policy tips, warnings, and notifications Primarily analyst-facing; privacy-preserving investigation workflows Privacy controls Role-based access and compliance controls Pseudonymization by default, role-based access, and auditing Typical stakeholders Security, compliance, and data protection teams Insider risk, security investigations, compliance, and authorized HR/legal stakeholders Practical example: An employee downloading confidential customer information Consider a financial services organization where an employee downloads confidential customer records and attempts to transfer them to a personal cloud storage account. Scenario A: Using Purview DLP The organization has configured DLP policies to protect customer information. What happens? An employee accesses an Excel file containing customer financial information. The employee attempts to upload the file to an unauthorized cloud storage service. DLP evaluates the content and activity against the configured policies. If the file contains protected information and the policy conditions match, DLP can block the upload. A policy notification or alert may be generated. Outcome: Sensitive customer information is prevented from leaving through the restricted channel. Important: DLP does not need to determine whether the employee has malicious intentions. It enforces the configured data protection policy. Scenario B: Using Purview Insider Risk Management Now consider the same employee, but with additional activities: Downloads unusually large amounts of confidential information. Copies files from multiple sensitive SharePoint locations. Attempts to transfer information to personal storage. Repeatedly performs activities associated with potential data exfiltration. What happens? IRM collects relevant activity signals from supported sources. It correlates those signals using configured insider risk policies. It identifies potentially risky patterns across activities. It generates risk alerts when the configured detection criteria are met. Authorized investigators can review the activity context, investigate, and determine appropriate next steps. Outcome: The organization can investigate whether the employee's behavior represents a potential insider threat. Important: IRM identifies potential risk, not proven malicious intent. An alert is not evidence that an employee has committed wrongdoing. IRM supports risk investigation and escalation workflows, including integration with Microsoft Purview eDiscovery. The biggest architectural difference: Data-centric vs. user-centric security This is probably the most important distinction when explaining these capabilities to enterprise customers. Purview DLP: Data-centric protection DLP essentially evaluates: Data sensitivity + Activity + Destination + Policy = Enforcement decision For example: Is the document classified as confidential? Does it contain credit card numbers? Is it being shared externally? Is the destination permitted? Should the activity be allowed, audited, or blocked? DLP focuses on whether a particular action involving data violates a protection policy. Purview IRM: User-centric risk detection IRM evaluates: User activities + Risk indicators + Context + Correlation = Potential insider risk For example: Is the user performing multiple potentially risky activities? Are there unusual patterns of sensitive data access or transfer? Are activities associated with a configured risk scenario? Does the combination of signals warrant investigation? IRM provides broader context around potential insider risk rather than evaluating only an individual data-sharing transaction. Can DLP and Insider Risk Management work together? Absolutely. In fact, Microsoft provides an integration called Adaptive Protection that combines their strengths. Adaptive Protection uses Insider Risk Management signals to dynamically adjust DLP enforcement based on the risk level associated with a user. This is particularly valuable because traditional DLP policies can apply consistent restrictions, while Adaptive Protection enables more context-aware enforcement. Example: Adaptive Protection Imagine an organization with three insider risk levels. User risk level IRM assessment Example DLP enforcement Minor Limited indicators of potential risk Monitor activity and generate alerts Moderate More significant indicators of potential risk Increase monitoring and notify users Elevated Significant indicators warranting stronger controls Block specified external sharing activities These are illustrative policy choices, not mandatory Microsoft defaults. How it works: IRM evaluates relevant user activity and assigns a risk level. Adaptive Protection makes that risk level available to supported enforcement policies. DLP evaluates the risk level alongside its other policy conditions. DLP applies the configured controls. As the risk level changes, applicable enforcement can change dynamically. For example, an employee at an elevated insider risk level could be prevented from sharing certain content externally, while users at lower risk levels continue working with fewer restrictions. This is where the two solutions become particularly powerful together. Does Insider Risk Management replace DLP? No. They are complementary, not competing solutions. Consider these customer requirements: Customer requirement Recommended capability Prevent employees from emailing credit card numbers externally DLP Block confidential files from being copied to USB drives DLP Prevent sensitive information from being uploaded to unauthorized cloud applications DLP Identify potential intellectual property theft IRM Investigate suspicious patterns of employee data access and transfer IRM Identify potential data exfiltration associated with departing employees IRM Apply stricter DLP restrictions to users exhibiting elevated insider risk IRM + DLP with Adaptive Protection Protect sensitive data while investigating suspicious user activity DLP + IRM One important nuance: DLP can detect and report risky activities, and IRM can contribute to mitigation. The distinction is their primary purpose and operating model, not an absolute separation between detection and prevention. Which capability should customers implement first? For customers beginning their Microsoft Purview data security journey, I would generally recommend the following sequence. Phase 1: Establish data protection with DLP Start by identifying sensitive information and understanding where it resides. Define sensitive information types and classification requirements. Implement sensitivity labels where appropriate. Configure DLP policies for Microsoft 365 workloads. Extend protection to endpoints and other supported locations. Initially use audit or simulation capabilities to assess impact before enabling blocking. Business outcome: Reduce accidental and unauthorized sensitive data exposure. Phase 2: Introduce Insider Risk Management Once the organization has foundational visibility and protection, introduce insider risk detection. Identify relevant insider risk scenarios. Establish investigation ownership and privacy safeguards. Configure appropriate risk indicators and policies. Develop alert triage and investigation workflows. Integrate with existing security and compliance processes. Business outcome: Improve the ability to detect and investigate potentially harmful insider activities. Phase 3: Enable Adaptive Protection Connect the two capabilities to establish risk-based enforcement. Configure insider risk levels. Map risk levels to DLP policy conditions. Apply proportionate restrictions based on risk. Continuously tune detection and enforcement. Business outcome: Stronger security controls where risk is elevated, with less disruption for lower-risk users. The actual deployment order should depend on the customer's highest-priority risks, licensing, regulatory obligations, and organizational readiness. How I would position this to a customer For your CAIP and Security cross-solution conversations, I would use this positioning: Microsoft Purview DLP protects sensitive information from inappropriate sharing or movement, while Microsoft Purview Insider Risk Management identifies potentially risky user activities that could lead to data loss, intellectual property theft, or security incidents. Together, through Adaptive Protection, they enable organizations to move from static data protection policies toward dynamic, risk-aware security controls. Executive-level analogy Think of these solutions as two different security mechanisms: DLP is the security checkpoint: It examines what information is moving and determines whether that movement should be permitted. IRM is the security intelligence function: It analyzes patterns of activity to identify potential insider threats that warrant investigation. Adaptive Protection connects them: It enables the checkpoint to adjust restrictions based on the risk intelligence available. My recommendation When discussing Microsoft Purview with enterprise customers, I would avoid positioning DLP and IRM as alternative products. Instead, position them as three layers of a comprehensive data security strategy: Understand the data: Discover, classify, and label sensitive information. Protect the data: Use DLP to prevent unauthorized exposure. Understand and respond to insider risk: Use IRM and Adaptive Protection to identify potential threats and dynamically strengthen enforcement. Bottom line: DLP answers, "How do we prevent sensitive data from leaking?" IRM answers, "How do we identify potentially risky insider activity?" Adaptive Protection answers, "How do we automatically adjust protection based on that risk?" References: https://learn.microsoft.com/en-us/purview/dlp-learn-about-dlp https://learn.microsoft.com/en-us/purview/insider-risk-management https://learn.microsoft.com/en-us/purview/insider-risk-management-adaptive-protection https://learn.microsoft.com/en-us/purview/insider-risk-management-adaptive-protection-guideThe CISO Cheat Sheet to Microsoft Digital Defense Report 2026
I know we’re all busy, so I’ve pulled the most important data from this year’s Microsoft Digital Defense Report into one short read. The full report is well worth exploring, but this article focuses on the numbers and trends most relevant to security leaders. This year’s edition shows that AI is lowering the time, expertise and cost required to discover and exploit weaknesses, enabling attackers to operate with greater speed, scale and autonomy. The report describes this as AI “changing the physics of cybersecurity”: attack timelines are compressing and agentic systems are beginning to automate more of the attack lifecycle. Trend 1: Time has collapsed The clearest finding is about speed. Vulnerability discovery is increasingly running ahead of remediation, while the time from discovery to weaponisation is shrinking. In the AI era, weaponisation can follow in hours. Vulnerability discovery and weaponisation now often needs only a well-written prompt. The median time from discovery in the wild to weaponisation is below 24 hours. Vulnerabilities were on track for a record estimated 72,000 CVEs in 2026. The report expects a multi-year period in which the number of known but unpatched vulnerabilities rises sharply before eventually declining. The median time from container start to first exploit attempt is 5.3 hours. The ransomware actor Storm-1175 moved from web-facing exploitation to deploying Medusa ransomware in as little as 24 hours. CISA added over 110 CVEs to its Known Exploited Vulnerabilities catalogue between November 2025 and May 2026, most within a week of disclosure. The mismatch with enterprise reality is the uncomfortable part. The report says the disclosure-to-exploitation window has shrunk to single-digit days. Between November 2025 and May 2026, CISA added more than 110 vulnerabilities to its Known Exploited Vulnerabilities catalogue, most within a week of disclosure. In one example, Storm-1175 moved from exploiting a web-facing vulnerability to deploying Medusa ransomware in as little as 24 hours. Microsoft’s Red Team makes an important point: a patch is also a disclosure. Every fix points attackers towards the flaw it closes. As AI-assisted analysis makes reversing patches faster and more reliable, the report argues that patch velocity, not simply patch availability, becomes the control that matters. Trend 2: Attack chains are gaining autonomy The report charts a clear progression: September–November 2025: AI assists in orchestrating a campaign, as in the Anthropic-reported espionage case. April–June 2026: Full-chain autonomy is demonstrated in labs. July 2026: Real-world autonomous attacks of increasing complexity appear. Two frontier models, Mythos and GPT-5.5, completed a 32-step attack chain against an emulated enterprise with no human help. The test environment had no defenders. The UK AI Security Institute reached a similar finding independently. GPT-5.5 was the second model to solve its end-to-end corporate network attack simulation, a task AISI estimates would take a human about 20 hours. Open-weight models lag closed models at orchestrating attacks by about seven months. In the wild, early July 2026 saw the first documented automated ransomware extortion attack, named JADEPUFFER by Sysdig. Microsoft has seen AI-orchestrated intrusions that share elements with it. Initial access consistently came from internet-exposed services running known-vulnerable software. The report is measured on this point. Volumes of AI-orchestrated activity remain low. In most observed real-world operations, complex end-to-end intrusions still retain meaningful human direction. The Red Team's framing is the most useful one: AI doesn't create a new class of attack, it collapses the effort needed to find and exploit existing attack paths. Trend 3: AI has become an attack surface The report's second takeaway is that attackers are already targeting AI itself. The adoption numbers explain why. 88% of enterprises are experimenting with agents, and 82% of leaders plan broader rollouts within 12–18 months. The report cites industry projections of roughly 1.3 billion agents in production by 2028. What attackers are doing to AI systems: Four techniques accounted for roughly 90% of observed attack activity in telemetry from Azure AI workloads: malicious link injection (52%), jailbreaks (16%), tool and agent abuse (12%), and identity and credential abuse (10%). Memory poisoning: An attacker who can place content anywhere an agent reads can often place it where the agent remembers. Email is the dominant pathway the Red Team has observed. Human-in-the-loop isn't a complete control: Red team testing saw approval prompts ignored, or bypassed by a policy stored in poisoned memory. Developer tools turned against their owners: The "s1ngularity" malware hijacked locally installed AI command-line tools to hunt for secrets. It leaked about 2,000 secrets and 20,000 files across 225 victims. AI browsers: In daily use at more than 40% of organisations in Microsoft's dataset, they were the initial infection vector in incidents involving 57 malware families in a May 2026 analysis. Chat histories as a target: Malicious AI-assistant extensions reached nearly 900,000 installs and more than 20,000 enterprise tenants, harvesting AI chat histories that often contain code, architecture and credentials. The identity implications are direct. Each agent needs its own identity, not one borrowed from an employee, and a named human sponsor. The report also treats revocation latency, the time to cut off a compromised agent, as a measured outcome. Trend 4: The front door is still identity AI changes the speed and personalisation of social engineering. It hasn't changed where attacks start. Initial access in Defender Experts data: User execution: 30% Valid accounts: 20% Malicious copy-and-paste: 13% Phishing: 11% Together, user execution and valid accounts account for over half of observed activity. In incident response engagements, phishing as an initial access vector jumped from 7% to 23% year on year. The standout numbers: ClickFix: Defender saw user-pasted malicious commands on more than 1.1 million unique devices between February and early May 2026, roughly an 8x increase. AiTM: URLs accounted for 45% of the identified phishing techniques in the report’s breakdown. Separately, the share of AiTM phishing and token-theft attacks more than doubled during the first six months of 2026, although the report notes that their overall share remained comparatively small. Teams vishing: Weekly confirmed malicious volume increased 502% year on year. Per attempt, 48% of vishing calls kept the victim engaged for more than 20 seconds, and 30% lasted more than one minute. When a call succeeds, attackers can persuade the victim to install a remote-management tool and complete reconnaissance in two minutes or less. Business contact impersonation (BCI): The report introduces this term for conversations that start with a trusted-looking contact. Microsoft detected more than 46 million attacks in 12 months, with a 121% spike in April 2026. The share of first-contact messages that explicitly asked for money or documents fell from 17% to 3%. The first message is deliberately bland, like "Are you at your desk?" Password attacks declined 26% year on year, which the report describes as strong evidence that MFA and passkeys are forcing attackers to pivot. That pivot includes techniques such as fatigue attacks, AiTM phishing and token theft designed to circumvent conventional MFA. Trend 5: Attackers are inheriting trust rather than breaking in The report's headline theme is that risk is increasingly interconnected. Threats travel through the trusted relationships between identities, software supply chains, partners and cloud platforms. The numbers: Supply chain: Major open-source ecosystems saw attacks roughly every ten days, accelerating through Q2 2026. Shai-Hulud 2.0 affected 25,000 repositories. Megalodon backdoored 5,561 GitHub repositories in under six hours. Trusted signing: In May 2026, Microsoft disrupted Fox Tempest, a "malware-signing-as-a-service" operation that obtained genuine certificates for ransomware loaders and infostealers. Microsoft revoked over a thousand fraudulent code-signing certificates. Legitimate access: An unsanctioned remote monitoring tool is now one of the most reliable mid-stage indicators of a human-operated intrusion. Cloud identity: Cloud identity abuse was the most observed technique against critical infrastructure, representing 78% of the technique mix in Microsoft’s data for March to June 2026. Hybrid intrusions: The Storm-2885 case showed an attacker using a privileged cloud identity to close and downgrade security alerts. The report says identity governance and alert-handling workflows deserve Tier 0 treatment. Dwell time: DART data shows a statistically significant increase in dwell time year on year, meaning organisations took longer to detect intrusions. Ransomware shows the same ecosystem pattern. Qilin led leak-site data with 16.4% of victims, up 386%. Defender detections tell a different story, with Akira at 22%. Trend 6: Defence works best when it's connected The report is not only a catalogue of threats. The strongest defensive evidence: Disruption works. Following the March 2026 disruption, Tycoon2FA activity had fallen 95% from its November 2025 peak by June. Its share of CAPTCHA-gated phishing declined from 76% in December 2025 to 12% in June 2026. Correlation is the highest-leverage variable. The report argues that how well defenders share and correlate signals across endpoint, identity, cloud, email and network is one of the highest-leverage strategic variables under their control. AI is also changing defensive operations. The report describes AI-assisted triage, incident summarisation, hunting-query generation and detection engineering as ways to accelerate investigations and allow analysts to concentrate on higher-value work. Automated disruption can compress response time. The report says that when a correlated incident reaches a defined confidence threshold, defensive systems can automatically isolate devices, disable compromised accounts, revoke sessions or quarantine affected cloud resources. It also stresses the importance of appropriate governance and human oversight for high-risk AI actions. The report also recommends changing what leaders measure. It suggests moving from patches deployed to exposure reduced, detection coverage increased and time-to-mitigate compressed. What the MDDR recommends: ten security priorities The report starts its recommendations with the foundations: Secure by Design, Secure by Default and Secure Operations, applied through identity-centric Zero Trust. Microsoft says these keep the priorities below durable as AI adds more identities, applications, agents and dependencies to govern. Govern cyber risk at leadership level. Report identity exposure, patch latency, agent permissions, critical dependencies, dwell time and recovery readiness to the board. Defend identity as the primary control plane. Deploy passkeys and phishing-resistant MFA, reduce privilege and govern human and non-human identities. Invalidate and rotate tokens and session credentials quickly. Establish governance, visibility and data controls for AI. Keep visibility of approved AI tools, services and agents, and monitor for unauthorised or unmanaged use. Apply sensitivity-aware access and data protection to the data those systems can reach. Reduce exposure and edge risk. Continuously discover internet-facing assets and patch edge devices quickly. Centralise high-fidelity logging, enforce strong authentication and combine network visibility with threat intelligence. Focus on cross-signal correlation. Correlate endpoint, identity, cloud, application, email and network signals to detect intrusions earlier. Correlation also helps defenders anticipate attack paths and likely targets. Enact a continuous threat and vulnerability management model. Combine asset visibility, vulnerability identification, threat detection and AI-accelerated insight into a single continuous programme. Validate exposure through proactive testing. Run assume-breach exercises on cloud services, SaaS platforms, APIs and workflow automation. Prioritise them by where your highest-value data is stored, accessed or aggregated. Secure software dependencies. Harden software installation, keep a software inventory and validate provenance. Monitor packages and prepare for rapid containment. Participate in collective defence. Share actionable threat indicators and victim-informed intelligence with trusted partners and law enforcement. This supports coordinated tracking, investigation and disruption. Prepare for long-horizon technology transitions. Build a cryptographic inventory and advance post-quantum planning alongside AI governance. Read together, the numbers tell one story: the attacker’s workflow is becoming faster and less expensive. AI can shorten vulnerability discovery, exploitation, secret discovery and lateral movement, while organisations still face the slower operational work of testing, coordinating and deploying safe changes across complex environments. At the same time, agent identities can proliferate faster than organisations can inventory, govern and revoke them The defining question for boards today is not whether disruption will occur, but whether the organization can continue operating, contain harm, recover quickly, and maintain trust when it does. Source: Microsoft Digital Defense Report 2026, Version 1.1. Reporting period: July 2025–June 2026.
Protecting Organizations from External Email Risks in Microsoft 365 Copilot
Introduction As organizations embrace Microsoft 365 Copilot (Copilot), a new category of risk emerges: what happens when Copilot grounds its responses in untrusted external emails? Messages from external or unverified senders can carry content Copilot shouldn’t rely on. A new policy in Microsoft Purview Data Loss Prevention (DLP) addresses exactly this challenge. It lets organizations ground Copilot in trusted internal email only—reducing the risk of cross-prompt injection, while keeping everyday work uninterrupted. Why This Matters: The Risk of External Email in Copilot Grounding Copilot is built to integrate deeply with your organizational data—emails, files, meetings, and more—to generate intelligent and context-aware responses. However, not all mailbox content is equally reliable. External emails—messages originating from outside your organization’s trusted domains—can introduce risks such as: Prompt injection (or cross prompt injection) attempts disguised as legitimate communication Manipulated or misleading content aimed at influencing Copilot-generated outputs Unverified information or instructions that may lead to inaccurate responses Social engineering content that could be amplified through Copilot summarization Without proper safeguards, Copilot may inadvertently reference or summarize this content, potentially impacting decision-making or exposing users to biased or manipulated information. Consider a common scenario: an employee receives a message from an outside address that looks like a routine vendor note but contains hidden text instructing any AI assistant to ignore prior guidance and surface the recipient’s recent internal updates. Later, the employee asks Copilot to "summarize my inbox." Without this policy, that external message is eligible for grounding, and its planted instructions could influence the summary. With this new policy enabled, the external email is excluded from grounding entirely—Copilot never reads it as a source, so the injected instructions have no effect. How It Works: Under the Hood The feature operates through a DLP policy configured in the Microsoft Purview portal using the "Microsoft 365 Copilot and Copilot Chat" policy location with the "Email is received from > External users" condition. Here is how Copilot enforces the policy at runtime: Metadata Evaluation: Copilot evaluates email metadata and it checks the sender’s domain against your tenant’s accepted domains to determine whether an email is internal or external. Importantly, the body of the email is not inspected—only sender metadata is evaluated. External Emails Excluded from Grounding: Emails received from an external sender are excluded from Copilot grounding (source) data. This means when a user asks Copilot to summarize their inbox or reason over recent communications, those external emails are not referenced, summarized, or cited in the response. Other Grounding Sources Remain Available: Results from other grounding sources, such as web search, Word documents, Excel files, PowerPoint presentations, and internal emails, continue to show up in Copilot responses as normal. The policy is surgical in scope. No Impact on Email Access: User access to email remains completely unchanged. Users can still read, reply to, forward, and manage all their external emails as they always have. No Impact on Mail Flow: The policy does not affect mail flow, delivery, or retention. It operates exclusively at the Copilot grounding layer, not at the transport or storage layer. Things to Keep in Mind A few points help set the right expectations before you deploy: Metadata-only evaluation: The policy evaluates sender metadata, not message content. It does not scan or analyze the body of any email. Scoped to the grounding layer: The policy affects only what Copilot can use as a grounding source. It does not change mail flow, delivery, retention, or a user’s ability to access their email. Other sources are unaffected: Internal emails, files, and web results remain available to Copilot, so most everyday scenarios are unchanged. Validate before enforcing: Assess where external email is important to business workflows, then use simulation mode to validate impact and apply the protection only where it is relevant and needed. Key Benefits for Your Organization Mitigates Cross-Prompt Injection Risk: By excluding untrusted external email from Copilot’s grounding data, organizations significantly reduce the attack surface for prompt injection attempts embedded in incoming email. Applies protection where it is needed: Organizations can use the policy when external email presents a meaningful risk to Copilot grounding, while leaving external email available in scenarios where it is relevant and trusted. Ensures Copilot Responses Are Grounded in Trusted Data: Copilot responses reflect only your organization’s internal, verified communications, building greater confidence in Copilot generated insights. Minimal Disruption to Productivity: The feature keeps everyday work uninterrupted. Users retain full access to all their emails, and Copilot continues to function using all other permitted data sources. Simple Policy-Based Administration: Configured through familiar Microsoft Purview DLP policy workflows, making it easy for compliance and security teams to deploy and manage. Transparent User Experience: Users receive clear notifications when organizational policies restrict content, maintaining trust and transparency in the Copilot experience. Prerequisites Before you begin, make sure you have: Permissions: An account with the Compliance Administrator or Data Loss Prevention administrator role, or equivalent permissions to create DLP policies in the Microsoft Purview portal. Accepted domains: Your tenant’s accepted (internal) domains configured correctly, since these determine which senders are treated as internal versus external. How to Set It Up Setting up this protection is straightforward: Sign in to the Microsoft Purview portal (https://purview.microsoft.com). Navigate to Data Loss Prevention > Policies and select + Create policy. Choose the Custom template, then Custom policy. On the Locations page, enable the Microsoft 365 Copilot and Copilot Chat location. Add a rule with the condition "Email is received from," and set the value to External users. Set the action to "Prevent Copilot from processing content". Deploy the policy in simulation (test) mode first, and review the impact to confirm only the intended external email is affected. Once validated, save and activate (enforce) the policy. Conclusion As M365 Copilot becomes central to enterprise productivity, organizations must control what data feeds its responses. This new policy features adds a critical layer of defense, grounding M365 Copilot in trusted internal data while keeping the door open to seamless collaboration. By deploying this DLP policy, you protect more than data—you protect the integrity and trustworthiness of every Copilot-generated insight your organization relies on. Ready to get started? Create the policy in simulation mode today, validate the impact, and enforce it once you’re confident—so every Copilot response your organization relies on is grounded in data you trust. Learn more: https://learn.microsoft.com/en-us/purview/dlp-microsoft365-copilot-location-learn-aboutDLP for Copilot Customizes Data Access Messages
A small but important change gives DLP for Copilot the ability to include custom compliance links in error messages when DLP blocks Copilot from accessing content. It sounds like something administrators could ignore. They can, and DLP for Copilot will continue to work perfectly well. However, directing users to a chosen web page when Copilot cannot access data creates an opportunity to deliver trusted information, and that’s always a good thing. https://office365itpros.com/2026/11/06/dlp-for-copilot-links/59Views0likes0CommentsWhy DLP for External Web Search in Microsoft 365 Copilot Matters?
Introduction Microsoft 365 Copilot (Copilot) grounds its responses in your organizational data—emails, files, chats—and, optionally, the public web. With web search enabled, Copilot fetches real-time information from the Bing search service to deliver richer, more current answers. But what happens when a user’s prompt contains sensitive data such as credit card numbers, passport numbers, or Social Security numbers? That’s where a new feature in Microsoft Purview Data Loss Prevention (DLP) becomes essential: it keeps sensitive information from reaching external web search during Copilot’s query generation, preventing inadvertent data leakage while preserving the productivity benefits of AI. At a Glance In short: admin and user toggles decide whether Copilot can search the web; Microsoft Purview DLP decides what data may leave when it does. . Admin and user toggles are binary on/off controls—they aren’t aware of sensitive data. Prevents Copilot from using external web search as a grounding source for that prompt. It does not block the prompt itself or prevent Copilot from generating a response using permitted sources. It works regardless of your web search configuration,even as a safety net if web search is disabled. The Web Search Landscape in Copilot Before diving into the DLP feature, it’s important to understand the web search controls already available in Copilot and how they interact with this DLP feature. How Web Search Works in Copilot When web search is enabled, Copilot parses user prompts and generates search queries sent to the Bing search service. These generated queries are different from the user’s original prompt—they consist of a few words informed by the prompt. Importantly: The user’s entire prompt is NOT sent to Bing (unless it’s very short) Entire Microsoft 365 files (emails, documents) are NOT included in the search query User and tenant identifiers are removed before queries reach Bing Web search queries are not used to improve Bing, create advertising profiles, or train AI models Queries are treated as customer confidential information Admin Controls for Web Search IT administrators have several options to manage web search through the "Allow web search in Copilot" policy in Cloud Policy service for Microsoft 365: Enabled in Microsoft 365 Copilot and Microsoft 365 Copilot Chat: Web search is available across all Copilot experiences. Users get the Web content toggle to control it personally. Disabled in Microsoft 365 Copilot and Microsoft 365 Copilot Chat: Web search is completely turned off. The Web content toggle is dimmed and unavailable to users. Disabled in Work mode; Enabled in Web mode and Copilot Chat: A hybrid approach where web search is blocked in Work mode (where organizational data is accessed) but available in Web mode and Copilot Chat. User-Level Control: The Web Content Toggle When the admin enables web search, users in Copilot (Work chat) have a "Web content" toggle that is ON by default. Users can turn it off to exclude web content from their Copilot responses. This toggle is NOT available in Copilot Chat. The Gap: Why Admin Controls and User Toggles Are Not Enough Here’s the critical question: What if your organization has web search enabled (for good reasons—better answers, real-time data, improved productivity) but a user inadvertently includes sensitive information in their prompt? Consider these scenarios: A user asks Copilot: "What are the compliance requirements for processing credit card number 4532-XXXX-XXXX-1234?" An employee types: "Find regulations related to passport number AB1234567 for our international transfer." A prompt includes a customer’s Social Security number while asking about tax filing procedures. In each case, if web search is enabled, Copilot might generate a search query informed by the sensitive data in the prompt. Even though Copilot doesn’t send the entire prompt to Bing, the generated search query could still be influenced by or contain fragments of sensitive information. This is the gap that DLP for external web search fills—and it works regardless of which web search configuration option your admin has chosen. The Solution: DLP Policy to Restrict Web Search When Prompts Contain Sensitive Data Microsoft Purview DLP allows you to create a policy that detects when a user’s prompt contains sensitive information types (SITs)—such as credit card numbers, passport numbers, Social Security numbers, or custom SITs defined by your organization—and automatically prevents Copilot from using external web search as a grounding source for that specific prompt. How It Works Real-Time Detection: The DLP policy evaluates each prompt in real time, checking for configured sensitive information types before Copilot generates any web search query. Surgical Blocking: Only the web search component is prevented for that specific prompt. Copilot continues to generate responses using permitted internal Microsoft 365 data sources (emails, files, chats) where applicable. Per-Prompt Enforcement: The restriction applies only to prompts that actually contain sensitive data. The next prompt from the same user (without sensitive data) will use web search normally. Supports various available SIT Types: Works with Microsoft-provided SITs (credit cards, passports, SSNs, etc.) and custom SITs defined by your organization. Clear User Notification: Users are informed that web search was restricted for their prompt due to organizational policy, maintaining transparency. Why This Feature Is Critical, Regardless of Your Web Search Configuration This is the key insight that every security and compliance team must understand: The DLP policy for external web search provides a fundamentally different layer of protection than the admin toggle or user toggle for web search. Scenario 1: Web Search Fully Enabled With web search enabled across all Copilot experiences—the most common setup—the DLP policy acts as a safety net. Normal prompts get full web-grounded answers, but the moment a prompt contains sensitive data, web search is blocked for that prompt alone. External web grounding is prevented for that prompt when the policy detects configured sensitive content. Scenario 2: Web Search Disabled in Work Mode, Enabled in Web Mode Even here, users in Web mode and Copilot Chat still have web search active. The mode-level toggle is binary (on/off) and can’t tell safe prompts from sensitive ones—so if a prompt in these modes contains sensitive data, DLP adds prompt-level, data-aware protection beyond binary web-search controls.. Scenario 3: Web Search Enabled with User Toggle Available Expecting users to toggle off web search before every sensitive prompt is unrealistic—they don’t always know when content counts as sensitive by compliance standards. The DLP policy removes that human error, detecting and blocking automatically on a per-prompt basis. Scenario 4: Even When Web Search Is Fully Disabled Even with web search disabled entirely, the DLP policy adds defense-in-depth. Configurations change, policies get modified, and new users join groups with different settings. If web search is ever re-enabled—intentionally or not—the policy keeps sensitive data protected. Comparing the Controls: A Side-by-Side View Control Scope Granularity Sensitive Data Aware? Admin Policy (Allow web search) Tenant/User Group Binary: On or Off per mode No User Web Content Toggle Individual User Binary: On or Off No DLP: Block Web Search for SITs (Recommended) Per Prompt (Real-Time) Layered defense-in-depth; Conditional Block: Only when SITs detected Yes Key Takeaway: The admin toggle and user toggle control whether web search is available. The DLP policy controls what data can be sent when web search is available. These are complementary, not overlapping controls. Prerequisites Before you configure the policy, make sure you have: Licensing: Microsoft 365 Copilot licenses for your users, plus Microsoft Purview Data Loss Prevention (included with Microsoft 365 E5 or E5 Compliance, or an equivalent plan). Permissions: An account with a role that can create DLP policies for the Copilot location, e.g. Compliance Administrator or the Purview Data Security AI Admin role. Sensitive information types: The Microsoft-provided or custom SITs you want to detect (credit card numbers, passport numbers, SSNs, and so on) identified ahead of time. How to Configure the DLP Policy Follow these steps to set up the protection in Microsoft Purview: Sign in to the Microsoft Purview portal (https://purview.microsoft.com). Go to Data Loss Prevention > Policies and select + Create policy. Select the Custom template, then Custom policy. On the Locations page, set the Microsoft 365 Copilot and Copilot Chat location to On. Add a rule with the "Content contains" > "Sensitive information types" condition and choose the SITs you want to detect (e.g., Credit Card Number, Passport Number, SSN, or custom SITs). In the same rule, set the action to "Prevent Copilot from processing content" > "Performing Web Searches". Save and turn on the policy. Policy Design note: Conditions based on sensitive information types and sensitivity labels must be configured in separate rules within the same policy. Note: DLP policy changes can take up to 4-8 hours to take effect in Copilot. Deploy in simulation (test) mode first to review the impact before you enforce the policy. Real-World Use Case: Contoso Contoso wants employees to use Copilot for productivity and has web search enabled to provide the best possible responses. However, they don’t want sensitive customer data—such as credit card numbers or national identification numbers—to be sent to external web search when Copilot grounds responses on the web. They configure a DLP policy targeting the Microsoft 365 Copilot and Copilot Chat location with a rule that detects their relevant SITs and sets the action to "Prevent Copilot from processing content" > "Performing Web Searches". Result: When a user submits a prompt containing those SITs, Copilot does not send the prompt to external web search. Copilot still returns a response grounded in internal Microsoft 365 data sources where the user has access. For all other prompts, web search works normally. Other prompts can continue to use web search, subject to applicable settings and policies Best Practices Deploy the DLP web search policy alongside your existing web search admin controls for defense-in-depth. Include both Microsoft-provided and custom SITs relevant to your industry and data classification. Use simulation mode first to understand the impact before enforcing the policy. Combine with the "Prevent sensitive information types in prompts" DLP action for comprehensive protection (note: these must be separate rules within the same policy). Regularly review DLP alerts to identify patterns of sensitive data in prompts that may indicate user training needs. Document your layered approach: admin toggle for broad control, DLP for data-aware conditional control. Conclusion The “Restrict Microsoft 365 Copilot from using external web search when prompts contain sensitive data” DLP capability fills a critical gap. Admin policies and user toggles give broad on/off control over web search availability, but they can’t tell a prompt that’s safe to ground on the web from one carrying sensitive information that must never leave your Microsoft 365 boundary. This DLP feature adds intelligent, real-time, per-prompt protection that works regardless of your web search configuration. Users keep the productivity benefits of web-grounded Copilot responses without compromising data security—a clear example of security enabling productivity rather than restricting it. Bottom line: If your organization uses M365 Copilot with web search in any capacity, this DLP policy isn’t optional—it’s essential. References DLP for Microsoft 365 Copilot, Copilot Chat and Cowork: https://learn.microsoft.com/en-us/purview/dlp-microsoft365-copilot-location-learn-about Data, Privacy, and Security for Web Search in Copilot: https://learn.microsoft.com/en-us/microsoft-365/copilot/manage-public-web-access
Unlocking Microsoft 365 Adoption in Engineering, Manufacturing, and Regulated Industries
Executive Feedback to Microsoft Leadership: Expanding the Value of Microsoft 365 Beyond Cloud-First Workflows Executive Summary Microsoft has successfully built the industry's leading cloud collaboration ecosystem around Microsoft 365, OneDrive, and SharePoint. The strategy has delivered substantial value for information workers, distributed teams, and organizations pursuing cloud-first operating models. However, there is a significant and often overlooked customer segment that remains underserved: engineering, manufacturing, healthcare, medical device, industrial, laboratory, defense, and other regulated organizations whose primary workflows are intentionally built around file-based repositories, network shares, PDM/PLM systems, and controlled document environments. The challenge is not opposition to cloud technology. The challenge is that many of these organizations prioritize data integrity, traceability, predictability, and workflow continuity above all else. As a result, they often perceive modern Microsoft productivity capabilities such as AutoSave, coauthoring, and version history as being unnecessarily coupled to OneDrive and SharePoint. This creates an important business opportunity. Microsoft could unlock substantial additional Microsoft 365 adoption and customer goodwill by extending modern document protection and collaboration capabilities to local, network-hosted, and hybrid file environments without requiring a complete migration to OneDrive or SharePoint. This is not a request to replace cloud services. It is a request to recognize that cloud-first and file-based workflows can coexist. The Opportunity Is Larger Than It Appears Many of Microsoft's largest enterprise customers operate in environments where files are not simply documents. They are: Design history files Manufacturing records Engineering drawings Validation reports Device master records Controlled procedures Laboratory data Regulatory submissions Quality records For these organizations, file location, revision control, ownership, auditability, and retention are operational requirements rather than convenience features. Microsoft itself acknowledges that Office AutoSave currently requires files to be stored in OneDrive or SharePoint. Files opened from traditional file-system locations do not receive the same experience. As a result, many organizations feel they must choose between: Maintaining proven operational workflows. Accessing Microsoft's most advanced productivity features. That is a business decision many organizations simply refuse to make. The Real Barrier Is Not Technology. It Is Trust. Discussions around cloud adoption are often framed as a resistance-to-change problem. Research consistently suggests otherwise. Studies examining enterprise cloud adoption repeatedly identify security concerns, data privacy concerns, and control over organizational information as major barriers to adoption. One study found security concerns dramatically increased the likelihood that organizations would reject cloud adoption. Similarly, KPMG's cloud transformation research notes that concerns about data loss, audit findings, compliance issues, and operational risk can slow or limit cloud initiatives. The lesson is important: Organizations rarely reject technology because it is new. They reject technology because they do not trust it with critical business information. Once users experience: unexpected file overwrites, synchronization ambiguity, permission confusion, data residency uncertainty, conflicting document versions, trust declines rapidly. Trust, not functionality, is often the limiting factor. Engineering Users Experience the World Differently Microsoft's cloud ecosystem was largely designed around information-worker collaboration. Engineering organizations frequently operate under different assumptions: Information Worker Priority Engineering Priority Seamless sharing Data integrity Anywhere access Traceability Real-time collaboration Configuration control Ease of use Auditability Cloud accessibility Revision certainty Neither approach is wrong. The challenge is that Microsoft increasingly optimizes for one while under-serving the other. An Example: AutoSave AutoSave is one of the most valuable additions Microsoft has made to Office. The value proposition is obvious: Reduced data loss Improved productivity Lower cognitive burden Better user confidence Microsoft's own documentation describes AutoSave as continuously saving changes while users work, but only when documents reside in OneDrive or SharePoint. From Microsoft's perspective, this design is understandable. From the customer perspective, the message often becomes: "Modern document protection is available, but only if you adopt Microsoft's preferred storage architecture." Many customers view this not as a technical limitation, but as product segmentation. Microsoft Could Learn from Version Control Systems Modern software development solved multi-user document conflicts decades ago. Git was specifically designed around realities such as: multiple devices, multiple contributors, offline work, concurrent editing, conflicting changes. Critically, Git assumes conflicts are inevitable. Rather than hiding them, Git exposes conflicts and provides mechanisms to resolve them. Many engineers trust Git precisely because its behavior is transparent. By comparison, file synchronization systems often attempt to abstract away complexity. When synchronization fails, users can no longer determine: which version is authoritative, which edits are newer, what happened, who changed what. The engineering mindset is frequently: Show me the conflict. rather than Hide the conflict and make a decision on my behalf. The Untapped Hybrid Customer Much discussion around Microsoft 365 assumes organizations are either: Cloud-first, or Legacy. In reality, many enterprises are neither. Many operate as hybrid organizations and intentionally will continue to do so. Research from industry and security organizations continues to show persistent adoption of hybrid and multi-cloud architectures driven by governance, security, compliance, and operational requirements. These customers are not rejecting Microsoft. They are already paying customers. They often purchase: Microsoft 365 Windows Azure Teams Active Directory SQL Server Yet many would immediately purchase additional capabilities if Microsoft offered: Local AutoSave Office AutoSave functionality for: NTFS local storage SMB file shares NAS systems PDM-managed documents Local Version History Built-in document time travel without cloud dependence. Hybrid Collaboration Coauthoring capabilities that operate through enterprise file infrastructure. Enterprise Conflict Resolution Visualization and reconciliation of competing document changes. Network-Aware Document Protection The same confidence users experience in OneDrive without requiring migration to OneDrive. The Revenue Opportunity This is not merely a product-improvement request. It is a business opportunity. A significant portion of engineering and regulated industries remain hesitant to migrate entirely into cloud-centric document ecosystems because the perceived operational risks exceed the perceived benefits. Rather than forcing an all-or-nothing decision, Microsoft could monetize a middle path: Microsoft 365 Hybrid Collaboration A premium offering delivering: AutoSave Version History Recovery Conflict Resolution Audit Visibility for enterprise-controlled file infrastructure. Organizations that decline OneDrive adoption today may still eagerly purchase these capabilities. In effect, Microsoft could create incremental revenue from customers who are already committed to the Microsoft ecosystem but currently feel underserved by a cloud-only feature strategy. Recommendation Microsoft should stop treating file-server and network-share users as transitional users waiting to migrate. Many are not transitioning. Many have intentionally chosen architectures optimized for regulatory compliance, engineering rigor, operational control, and data governance. The future should not require choosing between: modern productivity features, and trusted enterprise workflows. The organizations building medical devices, industrial equipment, aerospace systems, manufacturing infrastructure, energy systems, and critical technologies represent some of Microsoft's most technically sophisticated and commercially valuable customers. They deserve first-class support for the workflows they intentionally operate. The opportunity is not to move every customer to the cloud. The opportunity is to bring Microsoft's best innovations to every customer, regardless of where their files live.110Views0likes0Comments
Excel Pivot Missing
Power Pivot is unavailable. I have already checked COM Add-ins and Disabled Items and completed Microsoft 365 repair without success. Please do not restart the standard troubleshooting script. I have a project due tomorrow and need advanced diagnosis or a remote-support session.183Views0likes1CommentHow to Recover Data from a Damaged or Corrupted OST File When Outlook Cannot Open It
Hi everyone, I have seen several cases where users still have an old OST file but cannot access the mailbox data inside it. This usually happens after an Outlook profile is removed, a Microsoft 365 or Exchange account is changed, a mailbox is no longer available, or the OST file becomes damaged or corrupted. One common misunderstanding is that an OST file can be opened on another computer in the same way as a PST file. However, an OST file is linked to the Outlook profile and mailbox that created it. If that connection is no longer available, Outlook may not be able to open the file normally. Before trying to recover the OST data, it is worth checking a few things: Is the original Microsoft 365 or Exchange mailbox still available? Can the Outlook profile be recreated and synchronized again? Is the issue related to the OST file itself or only the Outlook profile? Do you need the complete mailbox data or only specific folders/items? If the mailbox is still available, rebuilding the Outlook profile and allowing Outlook to create a new OST may be the better approach. However, if the mailbox no longer exists, the Outlook profile has been deleted, or the OST file is damaged and contains the only available copy of the mailbox data, recovery becomes a different process. In these situations, it is important to first check what information is still readable from the OST file. Scanning and previewing the mailbox data before export can help identify available folders, emails, attachments, contacts, and calendar items before creating a new PST file. A practical OST recovery workflow usually involves: Keeping a copy of the original OST file before making any changes. Checking whether the original mailbox can still be synchronized. Scanning the OST file to identify available mailbox items. Reviewing important folders and messages. Exporting the required data to PST. Validating the resulting PST in Outlook. A detailed overview of the OST to PST conversion process, including scanning, previewing, selecting mailbox items, and exporting recoverable data, is available here: https://www.edbmails.com/pages/ost-to-pst-converter.html One important point to remember is that recovery results depend on the condition and readability of the OST file. A conversion tool can help extract available mailbox information, but it cannot recreate data that is no longer present or readable inside the source file.467Views0likes1Comment