azure ad
558 Topics
Add custom attributes to users (or devices) to map hardware peripherals
Hello everyone, I am seeking some help, guidance or suggestions with the following situation. We are looking for a solution that could map peripherals (such as monitors) to a user or a device. Once we have that info, we will utilize an additional tool to extend our visibility over the assets & assignments. I reviewed a few documentations and videos about potential solutions, and I just want to know if that's possible or I should not invest time on it any longer. The scope is the following: 1. We've collected information about connected monitors using Intune Script detection. That's perfect. It already maps devices with monitor's serial numbers and other details. 2. Export in CSV is fine (although, the data is not a 100% accurate, we have an internal data base that we can compare). 3. Now, how can we properly map that data to the cloud objects? What the best approach is? Logically, the monitors should be added to the devices, but Intune Custom Attributes are not easily populated/managed (?). On the other hand, Entra AD is capable of managing such expressions and overall has better capabilities (or am I wrong?) when it comes to operating with cloud objects. I am really looking for a human response; more of a knowledge share. I'd appreciate if someone shares their experience with similar scenarios. :) I apologise in advance if my question is not in the right section. Docs: https://learn.microsoft.com/en-us/graph/extensibility-overview?tabs=http https://www.reddit.com/r/AZURE/comments/1e5z3kv/add_customextension_attribute_in_entra_id/ https://www.reddit.com/r/AZURE/comments/1dz4cru/comment/lcdf2ev/?context=3&share_id=UqZR0m9s-9SWiHOiVwwAM&utm_content=1&utm_medium=ios_app&utm_name=ioscss&utm_source=share&utm_term=1 https://www.youtube.com/watch?v=kBm-fjqg0PU https://www.youtube.com/watch?v=LHXfFoygiOA Thanks :)20Views0likes0CommentsMicrosoft Launches Preview for Entra ID Conditional Access Policy Plans
Conditional access policy plans are now available in preview. The idea is to define common rules, conditions like breakglass accounts and have the details inherited by CA policies. Microsoft provides a migration facility to move existing policies to plans, but it’s probably going to take some time for tenants to inventory their current CA policies, understand points of commonality, and slowing move towards rationalization. https://office365itpros.com/2026/10/29/conditional-access-policy-plans/38Views0likes0CommentsMicrosoft Plans to Allow Users to Create Agent Blueprints
The Entra admin center will soon get a new user role permission to control whether users can create agent blueprints. The control will be enabled by default. I think this is a terrible idea. Outside the hallowed walls of Microsoft, does the need really exist to allow average users to create agent blueprints? I don’t think so. Agents are like apps. They need to be controlled and managed by people who know what they are doing. https://office365itpros.com/2026/10/15/agent-blueprint-option/461Views0likes0CommentsWhy Entra Administrators Cannot Disable Their Own Accounts
When attempting to disable a user account in an interactive Graph session, I was told that the command failed because the accountEnabled property was invalid. The error is obviously incorrect because it’s very possible to update the property to disable or enable an account. However, different rules apply when the account is holds a privileged role, like Global Administrator. Entra imposes some reasonable blocks, even if the error messages are not good. https://office365itpros.com/2026/09/14/strange-accountenabled-error/200Views1like1Comment
Partner Entra lockout for more than 2 months
Sole Global Administrator Locked Out (60+ Days) Following MAICPP Partner Launch Benefits Activation — Case #2607300040011056 Hello Microsoft Partner Community and Microsoft Community Managers, I been a partner for several decades, previously a higher capacity MAICPP I am posting from my active Developer account because my primary organization tenant has been completely locked out for over two months.. MAICPP Partner Launch Benefits Activation The activation of Entra subscription failed and a delay in partner tech support resulting in an administrative lockout across our tenant spnode.io The Issue & Support Bottleneck Attempts to authenticate or initiate self-service password recovery result in an explicit account lockout message The ticket has stalled across various support queues for over two months Initially routed to Microsoft Defender for Cloud Apps, where engineers confirmed it was outside their scope Re-routed toward the Azure / M365 Data Protection queue A communication delay occurred when I temporarily lost phone access and was in the hospital. I require intervention from a Community Manager or Partner Operations Escalation Lead to help route this stalled case directly to an active Duty Manager in the Partner Support for immediate identity verification Direct Callback Phone: 628-309-6705 Thank you for your assistance in restoring access to our partner tenant.Entra ID Continuous Access Evaluation and Microsoft 365
Continuous Access Evaluation (CAE) is supported by core Microsoft 365 workloads like Exchange Online, SharePoint Online, and Teams, and the reach of CAE is gradually spreading throughout the Microsoft cloud ecosystem. However, security researchers report inconsistent coverage across first-party apps and clients that take a little gloss off the promise of instant access revocation when critical events like user password changes happen. https://office365itpros.com/2026/09/08/continuous-access-evaluation-cae/270Views0likes1CommentRevoking Access Tokens for Risky Service Principals
A Technical Community post discusses the topic of using the Entra ID continuous access evaluation (CAE) feature to revoke access for service principals when apps become risky or potentially compromised. The Microsoft Graph Command Line Tools app is a good example of a service principal in common use, so we examine the access tokens issued for interactive Graph sessions to discover if they are CAE-enabled. Just for fun! https://office365itpros.com/2026/09/03/cae-service-principals/155Views0likes0Comments
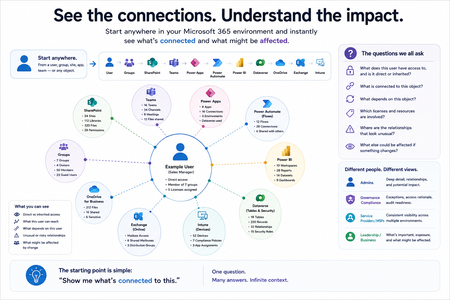
How much of your Microsoft 365 environment can you actually see at once?
Not how many users you have. Not how many sites, teams, apps or flows you have. How much of it can you actually see connected together? I've been working across Microsoft 365 environments for a while, and I kept running into the same thing. There is no shortage of information. If anything, there is probably too much of it. Users, groups, permissions, SharePoint, Teams, Power Apps, Power Automate, Power BI, Dataverse, OneDrive, Exchange, Intune, licensing, configuration... It's all there. But when you're actually trying to understand how everything fits together, it can be a different story. You open one blade. Find something. Open another. Cross-check it. Go back. Open something else. Before long, you're jumping between different parts of the tenant trying to build the bigger picture in your head. And if you're working with larger environments, that gets difficult pretty quickly. The information isn't necessarily missing. The relationships between the information are what can be difficult to see. That got me thinking about a slightly different question: Instead of "where do I find this information?" "Show me what's connected to this." That's where VisibleState started. Start anywhere. Follow the connections. Imagine starting with a single user. Instead of seeing that user simply as a record with a list of properties, imagine being able to explore the relationships around them: User → Groups → SharePoint → Teams → Power Apps → Power Automate → Power BI → Dataverse → OneDrive → Exchange → Intune Then the questions become different: What does this user have access to? Is that access direct or coming through a group? What resources are connected to them? What depends on something they're associated with? Which licenses are involved? Are there relationships that look unusual? If something changes, what else might be affected? Those questions aren't necessarily about finding another piece of information. They're about putting information that already exists into context. A report can tell you that something exists. A connected view helps you understand what it is connected to. Illustrative example below — not a real customer environment. I'm not suggesting Microsoft 365 doesn't already give us this information Quite the opposite. Microsoft 365 already gives administrators an incredible amount of information and tooling. The thing I've been thinking about is what happens when you want to look across those boundaries. Sometimes I don't want another export. I don't want another list. I don't necessarily want another dashboard. I want to start with something I'm looking at and ask: "What's connected to this?" And then keep following the trail. That's the idea I'm exploring with VisibleState. The interesting part is what happens when you change the viewpoint The same relationships can be useful for completely different reasons. For example: Administrators may want to understand access, permissions and dependencies. Security and governance teams may want to find unusual relationships or exceptions. Compliance teams may need to understand who can access something and why. People managing multiple environments may want a consistent way to understand what's there without rebuilding the picture manually every time. Leadership may not need to see the graph at all. They may simply want to know what's important, what's exposed and what could be affected. It's still the same underlying environment. You're just looking at it from a different angle. And that's where I think things get interesting. Where I'm at with it VisibleState started as something I was building to make my own work easier. I was spending a lot of time investigating environments, tracing access and putting information together for reports. The individual tasks weren't necessarily difficult. It was the jumping between different places and reconstructing the bigger picture that took the time. So I started building something that would let me approach the environment through the relationships instead. It's grown quite a bit from where it started, and I'm continuing to build it. I'm not posting this as a product launch, and I'm not looking for people to sign up. I'm genuinely interested in whether the problem I'm seeing is familiar to other people working with Microsoft 365. So I'm curious... If you could start with any object in your Microsoft 365 environment and immediately see what it's connected to, where would you start? Would it be: Users and access Groups and permissions SharePoint and Teams Power Apps, Power Automate, Power BI and Dataverse Licensing and resources Governance and unusual relationships Something completely different Maybe you've already got a good way of doing this. Maybe you still find yourself jumping between different services and piecing things together manually. Or maybe I'm looking at the problem from the wrong direction. What's the one relationship in your Microsoft 365 environment that you wish you could see instantly?240Views0likes0CommentsRunning a Regular Check for New Graph Permissions
Use PowerShell to Check for New Graph Permissions with a View to Updating Permissions Used by Apps. After Microsoft released some new Graph permissions, thoughts turned to how to discover new permissions after they are released. Code is the best way to perform automatic checks, and this article explains how to use PowerShell to check a last known set (stored in SharePoint Online) against the current set. Any variations are reported to administrators via email. https://office365itpros.com/2026/08/31/new-graph-permissions-check/125Views0likes0CommentsCalculating the Licensing Requirement for Entra Conditional Access Policies
After the discussion about the licensing gap prompts shown in the Entra admin center, here’s a PowerShell script to compute the set of user accounts that should have Entra P1 licenses. The information comes from the conditions property of conditional access policies with group and directory role membership expanded to find individual accounts. The set is checked against the set of users licensed for Entra P1 to find the accounts that need to be licensed. https://office365itpros.com/2026/08/18/find-entra-p1-accounts-to-license/155Views0likes0Comments