
Forum Widgets
Latest Discussions

Proposal: Applying DCWL to Copilot and Windows Client for Local Text‑Processing Efficiency
# Proposal: Applying DCWL to Copilot and Windows Client for Local Text‑Processing Efficiency # Proposal: Data Center WordCode Layer (DCWL) **Author:** Satoshi Kubota (Araha Planning) **Date:** September 15, 2026 --- ## 1. Introduction This proposal explores how the Data Center WordCode Layer (DCWL), originally designed for Azure text‑processing workloads, can be applied to Copilot and Windows client environments. If the DCWL Proof of Concept (PoC) demonstrates significant efficiency improvements in Azure, the same architecture can be extended to local text‑processing pipelines on Windows PCs. Copilot for Windows increasingly relies on local natural‑language processing, including prompt parsing, context generation, semantic search, and log analysis. These workloads share structural similarities with Azure RAG, Search, and Observability pipelines—making DCWL a natural fit for client‑side optimization. --- ## 2. Background: DCWL Concept DCWL encodes frequently used words, technical terms, and domain‑specific concepts into fixed‑length 32‑bit codes. This reduces: - String parsing overhead - Memory bandwidth consumption - CPU cycles for tokenization - I/O load during text ingestion - Energy usage for repeated text operations DCWL also supports fallback to Unicode, enabling compatibility with existing UTF‑8/UTF‑16 systems. --- ## 3. Why DCWL Fits Copilot and Windows Client Copilot for Windows performs substantial text processing locally: - Prompt interpretation - Local RAG (Recall‑Augmented Generation) - File and email summarization - Settings and system log analysis - Natural‑language command execution - Context building for multi‑turn interactions These operations involve repeated parsing of large volumes of text. DCWL can reduce the cost of these operations by providing a compact, fixed‑length representation for common words and concepts. ### Benefits for Copilot: - Faster prompt parsing - Reduced latency for local RAG - Lower CPU usage during context generation - More efficient semantic search over local files - Improved responsiveness on low‑power devices ### Benefits for Windows Client: - Reduced overhead in system log analysis - Faster text‑based indexing - Lower memory pressure during NLP tasks - Potential battery‑life improvements - More predictable performance on ARM‑based devices --- ## 4. Alignment with Windows Architecture Windows internally uses a mix of UTF‑16 (Win32 APIs) and UTF‑8 (modern subsystems). This hybrid model introduces overhead during conversions and string operations. DCWL’s fixed‑length 32‑bit encoding aligns well with: - Windows Runtime (WinRT) - Copilot local processing pipeline - Windows Search indexing - File system metadata analysis - Event Viewer and system logs - Power‑efficient processing on mobile PCs DCWL can serve as a lightweight, optional layer for text‑heavy operations without requiring changes to existing APIs. --- ## 5. Potential Implementation Approaches ### 5.1 Local DCWL Dictionary A client‑side dictionary containing: - Frequent English words - Windows terminology - Copilot command vocabulary - Common system log tokens - Application‑specific terms This dictionary can be updated via Windows Update or Copilot service updates. ### 5.2 Hybrid Processing Mode Copilot and Windows components can choose between: - **DCWL mode** (for known words) - **Unicode fallback mode** (for unknown words) This ensures compatibility while improving efficiency. ### 5.3 Integration Points - Copilot local RAG engine - Windows Search indexer - File summarization pipeline - Event log parser - Power‑optimized NLP tasks - On‑device AI acceleration paths --- ## 6. Expected Impact If DCWL’s Azure PoC shows measurable gains, similar improvements are expected on Windows PCs: - Faster Copilot responses - Reduced CPU usage during NLP tasks - Lower energy consumption - Improved performance on ARM devices - More efficient local semantic search - Enhanced user experience for natural‑language interactions These benefits align with Microsoft’s goals for Windows AI experiences and power‑efficient client computing. --- ## 7. Conclusion DCWL has the potential to enhance both cloud and client environments. Applying DCWL to Copilot and Windows client systems could provide meaningful improvements in performance, responsiveness, and energy efficiency—especially as local AI workloads continue to grow. I welcome feedback from the community regarding potential integration points, architectural considerations, and additional use cases for DCWL in client‑side environments.SatoshiKubotaSep 15, 2026Copper Contributor18Views0likes0CommentsProposal: Data Center WordCode Layer (DCWL) for Azure Text‑Processing Efficiency
# Proposal: Data Center WordCode Layer (DCWL) **Author:** Satoshi Kubota (Araha Planning) **Date:** September 7, 2026 --- ## 1. Overview This document presents **DCWL (Data Center WordCode Layer)**, a proposed external software layer designed to improve text‑processing efficiency and reduce energy consumption in Azure data centers. DCWL extends the concept of **GlobalWordCode (GWC)**—encoding not only characters but also words—into large‑scale cloud environments. The goal is to optimize workloads such as **RAG pipelines, search, log processing, and text preprocessing**, where variable‑length UTF‑8 text introduces significant overhead. A key design principle of DCWL is **prioritizing English** with the largest and most comprehensive word‑coding region. Because English represents: - the **largest volume of documents worldwide**, - the **largest share of AI training corpora**, - and the **dominant language in cloud‑based enterprise systems**, it receives **the widest and most densely allocated 32‑bit word‑coding space** to maximize performance impact. DCWL encodes frequent words, technical terms, proper nouns, and multilingual concepts as **fixed‑length 32‑bit codes**, reducing: - data‑transfer volume - string‑parsing overhead - storage I/O - CPU/GPU load - joules per query This post publicly records the DCWL concept under my name and invites technical discussion from Azure engineers, architects, and community members. --- ## 2. Motivation: Why Fixed-Length 32-bit Codes? Azure’s text‑processing stack relies heavily on variable‑length UTF‑8 strings. This creates bottlenecks such as: - boundary detection - repeated normalization/tokenization - large index scans - high memory‑transfer volume A fixed‑length representation for high‑frequency text units simplifies parsing and reduces CPU cycles. ### Alignment with UTF‑32 DCWL aligns naturally with **UTF‑32**, which uses 21 bits for Unicode code points. The remaining 11 bits allow room for structured extensions, enabling DCWL to coexist with Unicode while providing deterministic fixed‑length processing. --- ## 3. Technical Structure Each DCWL code consists of: - **Language ID (8 bits)** - **Group ID (8 bits)** - **Word ID (16 bits)** Unknown or unregistered text falls back to standard Unicode, ensuring compatibility with existing Azure systems. ### English Priority Allocation Because English dominates global digital content and AI training data, DCWL assigns: - **the largest Language ID block**, - **the widest Group ID ranges**, - **and the densest Word ID mapping** to English vocabulary, technical terminology, and enterprise‑related expressions. This design maximizes real‑world performance impact in Azure workloads. --- ## 4. Expected Impact ### Text‑processing layer (PoC target) - **15–30% reduction in energy consumption** ### Data‑center‑wide (estimated) - **1.5–5% reduction in total energy usage** Even a 1% reduction is significant at Azure’s global scale. --- ## 5. PoC Concept for Azure A simple A/B test could be performed: | Pipeline | Description | |---------|-------------| | Baseline | Standard UTF‑8 processing | | DCWL | Frequent words encoded as 32‑bit fixed‑length codes | ### Target workloads - Azure Cognitive Search - Azure AI Search - Azure Monitor Logs - RAG preprocessing and retrieval ### Metrics - processing time - memory‑transfer volume - storage I/O - CPU/GPU utilization - joules per query - throughput (queries/sec) --- ## 6. Questions for the Community I would appreciate feedback from Azure engineers, architects, and MVPs: 1. **Which Azure components would benefit most from fixed‑length word encoding?** 2. **Is UTF‑32 extension a viable approach for Azure’s internal text pipelines?** 3. **Would this concept be suitable for Cognitive Search or RAG preprocessing?** 4. **Are there existing Azure features that already approximate this idea?** --- ## 7. Purpose of This Post This post serves two goals: 1. **To publicly document DCWL under my name, Satoshi Kubota (Araha Planning), as the original proposer of the concept.** 2. **To gather technical feedback from the Azure community before discussing PoC possibilities with Microsoft Japan.** Thank you for reading.SatoshiKubotaSep 08, 2026Copper Contributor63Views0likes0CommentsWho Can Access What? Designing RBAC and Identity in Azure
Who should be allowed to access an Azure resource? Azure makes it easy to create resources. The harder question comes afterwards: who should be allowed to access them? A Function App may need to read secrets from Key Vault. A Logic App may need to call APIs through API Management. A developer may need to deploy to Dev but have no access to Production. A CI/CD pipeline may need to deploy infrastructure without becoming an Owner of the entire subscription. This is where Azure Role-Based Access Control (RBAC) and Managed Identity become critical. In this article, I look at how to design access around people, applications and deployment pipelines, while keeping permissions as narrow as practical. The article covers: Azure RBAC and access scopes Least-privilege access Managed Identities Developer vs Production access boundaries Application identities CI/CD deployment permissions RBAC vs API authentication Privileged access and PIM Common RBAC design mistakes One of the key principles is simple: Give an identity only the permissions it actually needs. For example, if a Function App only needs to read secrets from Key Vault, giving it Contributor access to the entire Resource Group solves the problem with a much broader permission than necessary. Good RBAC design is not about assigning more permissions. It is about understanding: Who needs access? Why do they need it? What exactly do they need to do? At what scope should access be granted? How can that access be managed securely over time? I would be interested to hear how others approach RBAC and identity design in enterprise Azure environments. Full article: https://www.linkedin.com/pulse/who-can-access-what-designing-rbac-identity-azure-chethan-raj-ud6gc/ChethanRajSep 02, 2026Copper Contributor95Views0likes0CommentsHow Should You Structure Dev, UAT, Staging and Prod in Azure?
This is one of those decisions that can look simple at the beginning of a project and become increasingly important as the environment grows. Should each environment have its own Resource Group? Should Production have a separate Subscription? Where should shared services live? How should naming, tagging and CI/CD fit into the design? There isn't one universal answer. The right structure depends on factors such as security boundaries, ownership, lifecycle, deployment processes and operational requirements. In this article, I look at: Dev, UAT, Staging and Production environment boundaries Resource Groups vs Azure Subscriptions Production isolation Naming conventions Azure tagging CI/CD considerations Blue/Green deployment considerations Common environment architecture mistakes The main idea is that environment architecture should be designed around clear operational and security boundaries rather than simply creating more Resource Groups. I would be interested to hear how others structure Dev, UAT, Staging and Production in enterprise Azure environments. Full article: https://www.linkedin.com/pulse/how-should-you-structure-dev-uat-staging-prod-azure-chethan-raj-ktfac/ChethanRajSep 02, 2026Copper Contributor75Views0likes0CommentsHow to Build a Self-Improving AI Agent on Azure: A Practical Technical Guide
A traditional chatbot answers a question. A more advanced AI agent can reason about a task, use tools, retrieve information, interact with APIs, and complete multiple steps on behalf of a user. Link to the post88Views1like0CommentsHow do you decide what belongs in an Azure Resource Group?
One of the Azure design decisions that looks simple at first but becomes surprisingly important in production is how we structure Resource Groups. The common approach is to group related Azure resources together. But in enterprise environments, I have found that a more useful question is: Should a Resource Group represent technology, application, workload ownership, or resource lifecycle? For example, consider an integration platform containing API Management, Azure Functions, Service Bus, Key Vault and networking. Would you put everything into one Resource Group? Or would you separate shared infrastructure from workload-specific resources? In my experience, ownership, lifecycle and operational responsibility are often better boundaries than simply grouping resources by Azure service type. I recently explored this topic in more detail in the first article of a new series I am writing on Azure architecture: Are Azure Resource Groups Just Folders? The article covers workload-based Resource Group design, environment boundaries, shared infrastructure, RBAC and some production lessons learned. I would be interested to hear how others approach Resource Group design in production Azure environments. Article: https://www.linkedin.com/pulse/azure-resource-groups-just-folders-chethan-raj-fakacChethanRajAug 13, 2026Copper Contributor105Views0likes0Comments
Leverage Azure PIM with DataBricks with Contributor role privilege
We are trying to leverage Azure PIM. This works great for most things, however; we've run into a snag. We want to limit the contributor role to a group and only at the resource group level, not subscription. We wish to elevate via PIM. This will then allow the user access within DataBricks. #1 issue - We have to enable PIM at the group level as it doesn't show up for group members within PIM and can't assign a contributor level group within the PIM application in Azure. So an admin has to enable PIM for the user to activate at the group level. We've also tried to do this scenario leveraging the Managed Application Contributor role as well. #2 - Delay - We are using the SCIM connector for User Provisioning leveraging Azure AD Groups. This connects to the unity catalog and are able to assign the groups within the Workspace. The issue - after you elevate the users permission in the contributor group at the resource level, you have to wait for 40 minutes for user provisioning to run or stop/start it. Until then, the user remains in an 'inactive' state within DataBricks. We feel we are missing a more fluid way to grant these rights and leverage PIM. Suggestions? Thanks in advance.SmileyvilleRocksAug 13, 2026Copper Contributor1.1KViews0likes1CommentFinOps for AI: Cost Optimization Strategies for High-Volume Azure AI Workloads
AI has moved from experimentation to production surprisingly quickly. Teams are now using Azure AI workloads for everything from customer support and document processing to content generation, data extraction, search, and intelligent automation. But as AI usage grows, so does a problem that many engineering teams discover the hard way: AI costs can scale much faster than expected. Link to the Blog110Views0likes0Comments
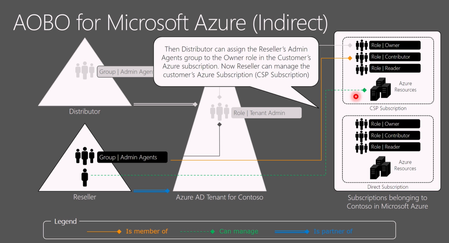
Admin‑On‑Behalf‑Of issue when purchasing subscription
Hello everyone! I want to reach out to you on the internet and ask if anyone has the same issue as we do when creating PAYG Azure subscriptions in a customer's tenant, in which we have delegated access via GDAP through PartnerCenter. It is a bit AI formatted question. When an Azure NCE subscription is created for a customer via an Indirect Provider portal, the CSP Admin Agent (foreign principal) is not automatically assigned Owner on the subscription. As a result: AOBO (Admin‑On‑Behalf‑Of) does not activate The subscription is invisible to the partner when accessing Azure via Partner Center service links The partner cannot manage and deploy to a subscription they just provided This breaks the expected delegated administration flow. Expected Behavior For CSP‑created Azure subscriptions: The CSP Admin Agent group should automatically receive Owner (or equivalent) on the subscription AOBO should work immediately, without customer involvement The partner should be able to see the subscription in Azure Portal and deploy resources Actual Behavior Observed For Azure NCE subscriptions created via an Indirect Provider: No RBAC assignment is created for the foreign AdminAgent group The subscription is visible only to users inside the customer tenant Partner Center role (Admin Agent foreign group) is present, but without Azure RBAC. Required Customer Workaround For each new Azure NCE subscription, the customer must: Sign in as Global Admin Use “Elevate access to manage all Azure subscriptions and management groups” Assign themselves Owner on the subscription Manually assign Owner to the partner’s foreign AdminAgent group Only after this does AOBO start working. Example Partner tries to access the subscription: https://portal.azure.com/#@customer.onmicrosoft.com/resource/subscriptions/<subscription-id>/overview But there is no subscription visible "None of the entries matched the given filter" https://learn.microsoft.com/en-us/azure/role-based-access-control/elevate-access-global-admin?tabs=azure-portal%2Centra-audit-logs#step-1-elevate-access-for-a-global-administrator from the customer's global admin. and manual RBAC fix in Cloud console: az role assignment create \ --assignee-object-id "<AdminAgent-Foreign-Group-ObjectId>" \ --role "Owner" \ --scope "/subscriptions/<subscription-id>" \ --assignee-principal-type "ForeignGroup" After this, AOBO works as expected for delegated administrators (foreign user accounts). Why This Is a Problem Partners sell Azure subscriptions that they cannot access Forces resources from customers to involvement from customers Breaks delegated administration principles For Indirect CSPs managing many tenants, this is a decent operational blocker. Key Question to Microsoft / Community Does anyone else struggle with this? Is this behavior by design for Azure NCE + Indirect CSP? Am I missing some point of view on why not to do it in the suggested way?ivokoJul 25, 2026Copper Contributor370Views0likes2Comments


Tags
- azure16 Topics
- Architecture10 Topics
- application gateway3 Topics
- Site Recovery2 Topics
- AGIC2 Topics
- cloud2 Topics
- RBAC2 Topics
- security2 Topics
- nsg1 Topic
- best practices1 Topic