windows server
2929 Topics
Your experience matters: help shape what’s next for Windows Server
Windows Server powers the workloads and services organizations rely on every day. As those environments evolve, so do the priorities behind them—from strengthening security and improving resiliency to making operations more consistent across on-premises, cloud, and edge deployments. Every organization brings a different perspective shaped by its people, workloads, and operating needs. We want to learn from those experiences and build lasting connections with the customers who rely on Windows Server. The Windows Server Technology Adoption Program (TAP) brings customers and the Windows Server product team together to validate preview capabilities and releases before they ship. Through the Windows Server TAP, customers can share their perspectives directly with the Windows Server team, explore areas of mutual interest, and help inform how we build and improve the product. We see TAP as an ongoing conversation: listening to your needs, learning from your feedback, and working together to make Windows Server better for the organizations that depend on it. What is Windows Server TAP? TAP is a structured partnership focused on testing and feedback. Participating customers validate defined scenarios in a test or lab environment isolated from production, share their findings, and work with the product team to identify issues and assess readiness. Depending on the engagement, validation may focus on a particular capability or on broader release-readiness scenarios, such as upgrades and workload compatibility. TAP is a two-way partnership: your team can explore upcoming capabilities in a test environment, share what you learn, and engage directly with the Windows Server product team. Your real-world perspective helps us understand how Windows Server is used across different environments and focus validation on the scenarios that matter to customers. Is your organization a good fit for Windows Server TAP? We're interested in hearing from Windows Server customers who can dedicate technical resources to hands-on validation and regular feedback. You must have a non-production environment where your team can deploy preview builds and run test scenarios from Windows Server features. TAP engagements are focused and selective. The team matches customer interests and environments to available validation opportunities, then discusses participation requirements and next steps. Expressing interest does not enroll your organization or guarantee a place in the program. Learn more about Windows Server TAP Attending Microsoft Ignite? Meet the team at the Windows Server Booth in the Hub (open November 17th – 19th) to learn more about TAP and discuss whether it could be a fit for your organization. Prefer to connect virtually? Fill out the Windows Server TAP interest form and let's chat over Microsoft Teams about your organization's interests and whether TAP could be a fit. Questions? Feel free to reach out to the TAP team at windowsserver-engage@microsoft.com.
Windows Server License with Software Assurance (SA) – Renewal Options
I purchased a Windows Server 2022 Standard license with 3 years of Software Assurance (SA), which is expiring next month. I would like to know how the renewal process works. I understand that Windows Server 2025 Standard with 3 years of SA is available. Do I need to upgrade to Windows Server 2025, or can I continue using Windows Server 2022 while renewing SA through the Windows Server 2025 offering? Are there any other options to renew or extend the existing SA coverage? Also, is there any option to extend the Extended Support End Date? Appreciate any advice from those familiar with Microsoft Windows Server licensing.74Views0likes2Comments
0x139 in wcifs!WcRemoveInMemoryTombstoneAfterRenameLink on Server 2019 RDS hosts with new Teams
We run a Remote Desktop Services farm on Windows Server 2019 (build 17763.9376, October 2026 cumulative update) with local user profiles (no FSLogix) and the new Teams client (MSIX). Since late October 2026 the session hosts bugcheck with KERNEL_SECURITY_CHECK_FAILURE (0x139), parameter 1 = 3 (LIST_ENTRY corruption, double remove). Four crashes in two weeks, on three different hosts, with a different user each time. Stack, identical in the two complete kernel dumps we have: nt!KeBugCheckEx nt!RtlRemoveEntryHashTable wcifs!WcRemoveInMemoryTombstoneAfterRenameLink+0x2d8 wcifs!WcPostSetInformation FLTMGR!... Ntfs!NtfsCommonSetInformation (status c0000022) FLTMGR!FltCompletePendedPreOperation cldflt!HsmiInfoRenameNotificationCallback cldflt!HsmFltPreSetRenameInformation nt!NtSetInformationFile (from user mode) - Process: ms-teams.exe, MSTeams 26288.2003.5258.9616. - Operation: IRP_MJ_SET_INFORMATION, FileRenameInformationEx, Flags = 0x5 (REPLACE_IF_EXISTS | SUPPRESS_PIN_STATE_INHERITANCE). - Target: %LOCALAPPDATA%\Packages\MSTeams_8wekyb3d8bbwe\LocalCache\Local\Microsoft\OneAuth\accounts\<guid>, renamed onto itself, in a local user profile. - No third-party filter driver in the stack. !analyze buckets one dump as MEMORY_CORRUPTION_LARGE, but that comes from !chkimg differences in nt (normal runtime patching), not real corruption. Our reading: Teams renames the OneAuth account entry onto itself, cldflt pends the operation, and when it completes wcifs removes its in-memory tombstone twice. One more data point: the only host in the farm running Windows Server 2022 (build 20348.5761, with FSLogix profile containers) has had the same Teams builds and has not crashed. All crashes are on Server 2019. It differs in both OS and profile type, so we cannot tell which one matters. Questions: - Is this wcifs/cldflt double remove a known issue, and is a fix planned for Windows Server 2019? - Has anyone else seen 0x139 with this stack on Server 2019 RDS hosts? We can share the dumps privately with Microsoft.24Views0likes0Comments
Bug in RDS Web Client - Copied text in RD session improperly encoded
As the title describes, there appears to be a bug in the HTML5 web client for Remote Desktop Services. This bug is present in both 2.1.85.0 and 2.1.87.0, and possibly earlier. When text is copied to the clipboard within a remote session (tested via a published RemoteApp), the text will occasionally be stored into the clipboard of the local machine encoded in UTF-8 instead of UTF-16 as it is supposed to be. When pasted into an application on the client machine, the UTF-8 encoded text (stored as CF_UNICODETEXT) is interpreted as UTF-16 (as that's how it's supposed to be encoded in memory as that's what Windows uses internally), resulting in meaningless output/mojibake. As an example, the text "Given" is copied from a Remote Desktop session (via the web client). The endpoint has these formats on the clipboard: Copied text CF_UNICODETEXT hex (padded) CF_TEXT hex Decoded text - UTF-8 Decoded text - UTF-16LE Given 47 69 76 65 6E 00 00 00 3F 3F 6E 00 Given 楇敶n The behavior is seemingly random. Most of the time, text is copied without issue. Once out of every 5-10 times, however, the UTF-8 encoded text is incorrectly written to the clipboard. Some additional information about this behavior: It only happens when using the RDS web client. The native RDP client does not exhibit this behavior. This has only been observed on Windows clients. It hasn't been observed on other client platforms, but testing has been minimal. The client browser does not appear to factor into the bug. It has been observed in Edge, Chrome, and Firefox. The issue is unrelated to the text copied. The same text, from the same application, can produce both outcomes when copied. The application being pasted into seems to be irrelevant. Has anyone else seen this behavior?51Views0likes2CommentsHyper-V Ubuntu VM: Memory Demand Different at Hyper-V and OS Level
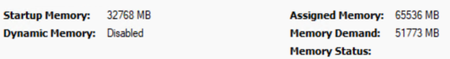
Hello all, Looking for advice and insight for a strange problem we are experiencing. We have a cluster of Windows Server 2025 hosts, on which we are using Hyper-V manager to run mostly Windows VMs. To access these VMs, we are using Apache Guacamole which is hosted on a Ubuntu VM on our cluster. We originally assigned 32GB memory to this VM. Recently, we have noticed an increased memory demand for this VM at the Hyper-V level which prompted us to increase the assigned memory of the VM to 64GB. Despite this, the memory demand has continued rising despite no apparent change in the usage of Guacamole. When logging into the VM and observing the memory usage here, the VM is using no where near the amount that is assigned. As shown in the attached images which were taken at the same time: Memory Demand Hyper-V Level (And seems to be continuing to increase...): Memory Demand OS Level: This morning, the memory demand spiked to 95GB on Hyper-V but at OS level was only 12GB and we were forced to restart the VM. The biggest concern is where this discrepancy is coming from and the potential unnecessary disruptions that will be caused from having to restart/rebuild the VM. Has anyone experienced this sort of issue before and found a fix? Can anyone suggest how to debug this issue? TIA221Views0likes2Comments
Server 2016 Domain member server Policy in effect prevents connecting to print queue
I have server 2016 member server (terminal server). Cannot add shared printers, get "A policy is in effect on your computer which prevents you from connecting to this print queue" I have check added changed the Point and print ect policies, no change...This is a new issue in the last few months but not sure exactly when it started.61Views0likes2CommentsKB5122882 and Intel SATA RAID boot problem
There is a bigger issue on Supermicro motherboards when Intel SATA RAID is configured: the system fails to boot after an update. I have verified this on three different boards; X9SCL-F, X11SCW-F, X11SSL-F, after a second restart : A disk read error occurred The array is functioning correctly; I can see it when running the system from an ISO, and I have tested all possible boot repair options.267Views0likes3Comments
Windows server 2022 is not updating with latest patch KB5126655
Windows server 2022 is not updating with latest patch KB5126655. However, successfully installed 2026-10 Cumulative update for .Net framework. Last successful Cumulative update for the operating system version 21H2 is 2026-06. Try to update the latest patch manually, the server is rolling back the patch.1.1KViews0likes4CommentsAnnouncing Native NVMe in Windows Server 2025: Ushering in a New Era of Storage Performance
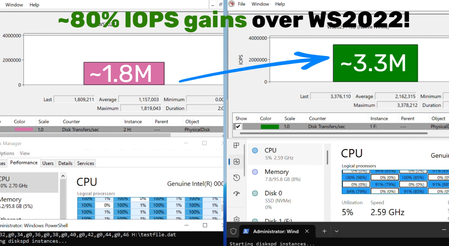
We’re thrilled to announce the arrival of Native NVMe support in Windows Server 2025—a leap forward in storage innovation that will redefine what’s possible for your most demanding workloads. Modern NVMe (Non-Volatile Memory Express) SSDs now operate more efficiently with Windows Server. This improvement comes from a redesigned Windows storage stack that no longer treats all storage devices as SCSI (Small Computer System Interface) devices—a method traditionally used for older, slower drives. By eliminating the need to convert NVMe commands into SCSI commands, Windows Server reduces processing overhead and latency. Additionally, the whole I/O processing workflow is redesigned for extreme performance. This release is the result of close collaboration between our engineering teams and hardware partners, and it serves as a cornerstone in modernizing our storage stack. Native NVMe is now generally available (GA) with an opt-in model (disabled by default as of October’s latest cumulative update for WS2025). Switch onto Native NVMe as soon as possible or you are leaving performance gains on the table! Stay tuned for more updates from our team as we transition to a dramatically faster, more efficient storage future. Why Native NVMe and why now? Modern NVMe devices—like PCIe Gen5 enterprise SSDs capable of 3.3 million IOPS, or HBAs delivering over 10 million IOPS on a single disk—are pushing the boundaries of what storage can do. SCSI-based I/O processing can’t keep up because it uses a single-queue model, originally designed for rotational disks, where protocols like SATA support just one queue with up to 32 commands. In contrast, NVMe was designed from the ground up for flash storage and supports up to 64,000 queues, with each queue capable of handling up to 64,000 commands simultaneously. With Native NVMe in Windows Server 2025, the storage stack is purpose-built for modern hardware—eliminating translation layers and legacy constraints. Here’s what that means for you: Massive IOPS Gains: Direct, multi-queue access to NVMe devices means you can finally reach the true limits of your hardware. Lower Latency: Traditional SCSI-based stacks rely on shared locks and synchronization mechanisms in the kernel I/O path to manage resources. Native NVMe enables streamlined, lock-free I/O paths that slash round-trip times for every operation. CPU Efficiency: A leaner, optimized stack frees up compute for your workloads instead of storage overhead. Future-Ready Features: Native support for advanced NVMe capabilities like multi-queue and direct submission ensures you’re ready for next-gen storage innovation. Performance Data Using DiskSpd.exe, basic performance testing shows that with Native NVMe enabled, WS2025 systems can deliver up to ~80% more IOPS and a ~45% savings in CPU cycles per I/O on 4K random read workloads on NTFS volumes when compared to WS2022. This test ran on a host with Intel Dual Socket CPU (208 logical processors, 128GB RAM) and a Solidigm SB5PH27X038T 3.5TB NVMe device. The test can be recreated by running "diskspd.exe -b4k -r -Su -t8 -L -o32 -W10 -d30 testfile1.dat > output.dat" and modifying the parameters as desired. Results may vary. Top Use Cases: Where You’ll See the Difference Try Native NVMe on servers running your enterprise applications. These gains are not just for synthetic benchmarks—they translate directly to faster database transactions, quicker VM operations, and more responsive file and analytics workloads. SQL Server and OLTP: Shorter transaction times, higher IOPS, and lower tail latency under mixed read/write workloads. Hyper‑V and virtualization: Faster VM boot, checkpoint operations, and live migration with reduced storage contention. High‑performance file servers: Faster large‑file reads/writes and quicker metadata operations (copy, backup, restore). AI/ML and analytics: Low‑latency access to large datasets and faster ETL, shuffle, and cache/scratch I/O. How to Get Started Check your hardware: Ensure you have NVMe-capable devices that are currently using the Windows NVMe driver (StorNVMe.sys). Note that some NVMe device vendors provide their own drivers, so unless using the in-box Windows NVMe driver, you will not notice any differences. Enable Native NVMe: After applying the 2510-B Latest Cumulative Update (or most recent), add the registry key with the following PowerShell command: reg add HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Policies\Microsoft\FeatureManagement\Overrides /v 1176759950 /t REG_DWORD /d 1 /f Alternatively, use this Group Policy MSI to add the policy that controls the feature then run the local Group Policy Editor to enable the policy (found under Local Computer Policy > Computer Configuration > Administrative Templates > KB5066835 251014_21251 Feature Preview > Windows 11, version 24H2, 25H2). Once Native NVMe is enabled, open Device Manager and ensure that all attached NVMe devices are displayed under the “Storage disks” section. Monitor and Validate: Use Performance Monitor and Windows Admin Center to see the gains for yourself. Or try DiskSpd.exe yourself to measure microbenchmarks in your own environment! A quick way to measure IOPS in Performance Monitor is to set up a histogram chart and add a counter for Physical Disk>Disk Transfers/sec (where the selected instance is a drive that corresponds to one of your attached NVMe devices) then run a synthetic workload with DiskSpd. Compare the numbers before and after enabling Native NVMe to see the realized difference in your real environment! Join the Storage Revolution This is more than just a feature—it’s a new foundation for Windows Server storage, built for the future. We can’t wait for you to experience the difference. Share your feedback, ask questions, and join the conversation. Let’s build the future of high-performance Windows Server storage together. Send us your feedback or questions at nativenvme@microsoft.com! — Yash Shekar (and the Windows Server team)116KViews16likes101CommentsWindows Server at Microsoft Ignite 2026: Sessions, our booth, and how to join the pre-day
Start early with the Windows Server pre-day Windows Server: Secure, manage, and accelerate with AI (PREB20) Monday, November 16 | 1:00–5:00 PM PT | Moscone Center This is a demo-filled, deep-dive workshop built for Windows Server professionals and led by the engineers and product team who build Windows Server. You'll see how to manage your servers across Azure, hybrid cloud, and on-premises environments, and get an early look at what's coming in the next version of Windows Server, including local AI, security, Hyper-V, Active Directory, networking, and storage. Expect practical tips you can take back to optimize, modernize, and get the most out of your Windows Server fleet. How to sign up The pre-day was added after Ignite registration opened, and it's a paid add-on that you select during registration. That means it doesn't show up when you search the session catalog, and many people who registered early never saw it. Here's how to get a seat. If you haven't registered for Ignite yet: Visit the Microsoft Ignite registration website and select Register. Choose the in-person Conference pass. When you reach the pre-day options, add Windows Server: Secure, manage, and accelerate with AI (PREB20). The pre-day has an additional fee of $325. Finish registration. The pre-day will appear in your confirmation. Already registered for the in-person event? Sign in to your registration using the same account you used to register. Open your registration page and select "Add a Pre-Day pass". Add Windows Server: Secure, manage, and accelerate with AI (PREB20) and complete checkout; additional fee of $325 applies. Watch for an updated confirmation email. If it doesn't arrive, check your junk folder. Seats are limited, and the Windows Server pre-day has sold out in past years, so we recommend adding it soon. Windows Server sessions on Thursday, November 19 All four of our sessions are on Thursday in the Moscone Center area. The venues are close together with 30 to 45 minutes between sessions, so you can catch all of them. Add them to your schedule from the session catalog. Session Speakers What you'll see When and where BRK418 (Breakout): What's new and what's next for Windows Server Neil Hinnant, Elden Christensen The latest release news and a preview of the next version of Windows Server, covering Hyper-V, Active Directory, storage, and networking, and how the next release raises the bar for security, performance, and AI. Thursday, Nov 19 10:15 AM – 11:00 AM BRK419 (Breakout): From VMware to Hyper-V: Hyperscale virtualization in your datacenter Jeff Woolsey, Davanna White How Windows Admin Center Virtualization Mode helps you build cost-effective, cloud-connected on-premises virtualization with Hyper-V in Windows Server. Thursday, Nov 19 1:30 PM – 2:15 PM THR897 (Theater): Cloud management for every Windows Server Theo Tran, Cindy Wan Consistent management with Azure Arc wherever your servers run, plus lower ESU costs, free hotpatching, and SQL Server optimization. Thursday, Nov 19 10:45 AM – 11:10 AM TT1701 (Table talk): On-prem inferencing with Windows Server Dan Cuomo A small-group conversation on running AI workloads on-premises: planning AI-ready server hardware, and thinking through performance, security, and operational consistency. Thursday, Nov 19 9:00 AM – 9:45 AM Come find us at the Windows Server booth Windows Server has its own booth in the Hub, open November 17 to 19. Stop by to see demos, ask the product team your toughest questions, and tell us what you need from Windows Server. Bring your upgrade plans, your hotpatching questions, and your AI ideas. Can't be there in person? The digital pass is free and includes keynotes and a wide range of sessions. Breakouts and Theater sessions will be streamed or available on demand. Table talks and the pre-day are in-person only. Get hands-on before you arrive Want a head start? Join the Windows Server Insider Program to try preview builds of the next version of Windows Server and share feedback with the team. Several features you'll hear about at Ignite are already in Insider builds, and we've covered them here on Tech Community, including Trusted Launch for virtual machines, ReFS boot, and Windows NVMe-over-Fabrics initiator preview. We can't wait to see you in San Francisco. If you have questions about our sessions or the pre-day, refer to the Ignite event page for more information or leave us a comment below.