virtual machines
18 TopicsMore EDA Job Sets per Volume: Azure NetApp Files Raises the Performance Bar
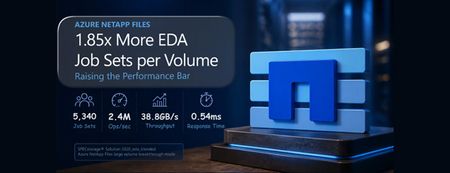
Azure NetApp Files raises the performance ceiling for cloud-based electronic design automation (EDA) with a new independently published SPECstorage® Solution 2020 EDA_BLENDED result for a single large volume in breakthrough mode: 5,340 job sets, 2.4 million operations per second, 38,776 MB/s peak throughput, and 0.54 ms overall response time. Delivering 1.85 times the job sets, operations, and throughput of the previous single-volume result while preserving sub-millisecond latency through most load points, the result enables more concurrent simulations, shorter regression cycles, and better utilization of compute and tool licenses without dataset sharding. Combined with proven linear scale-out and generally available Azure NetApp Files cache volumes that provide on-demand access to on-premises data, it gives EDA teams a practical foundation for high-performance cloud deployment and bursting.122Views0likes0CommentsBoost performance with NFS nconnect on Azure NetApp Files datastores for Azure VMware Solution
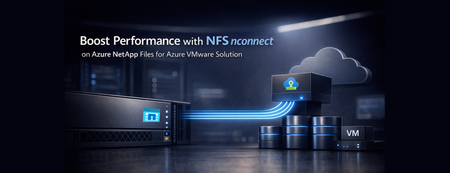
Azure VMware Solution now supports nconnect=4 with Azure NetApp Files datastores each ESXi host opens up to four parallel TCP connections to a single NFS datastore, raising throughput and lowering latency under load. Supported on both Gen 1 and Gen 2 private clouds, it makes Azure VMware Solution with Azure NetApp Files an even stronger home for databases and other storage‑intensive workloads.454Views0likes0CommentsFrom Scale to Breakthrough: Azure NetApp Files Sets a New Cloud Benchmark for EDA Performance
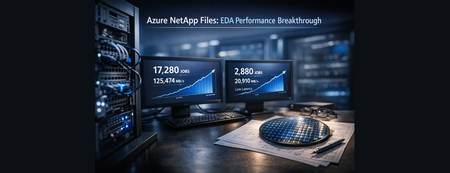
This article spotlights the newest leap in Azure NetApp Files: large volume breakthrough mode performance – independently validated by SPECstorage® Solution 2020 benchmarks. Azure NetApp Files is setting a new record for enterprise-scale Electronic Design Automation (EDA) workloads in the cloud. Backed by benchmark results at enterprise scale, it further reduces the traditional tradeoff between massive scale and uncompromising storage performance. For EDA teams, this means storage can keep pace with design cycles – enabling faster iteration, supporting cloud-first workflows, and reducing time spent waiting on infrastructure.512Views0likes0CommentsSecure, Keyless Application Access with Managed Identities - Now GA in Azure Files SMB
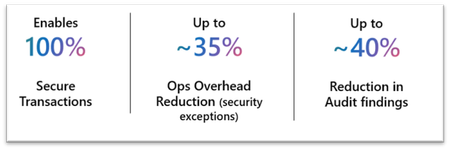
As enterprises modernize applications and strengthen their security posture, identity is central to how applications access shared storage. Traditional identity models relying on account keys, stored credentials, or domain‑joined infrastructure add operational overhead and introduce security risks such as credential leakage, lack of identity attribution, and excessive privilege if shared keys are compromised. Today, we are excited to announce the General Availability (GA) of Managed Identity support for Azure Files over SMB, enabling applications and virtual machines to securely access Azure Files without secrets, passwords, or key distribution. Managed Identity support enables customers to meet modern enterprise security standards without reliance on storage account keys, streamlining how organizations securely enable file‑based application access and reducing the operational overhead of filing internal exceptions. New storage accounts can support secure, identity‑based SMB access out of the box, while existing deployments can get secure by enabling Managed Identity authentication. From web application workloads such as WordPress, to databases on Azure Kubernetes Service (AKS), to CI/CD pipelines, applications require secure access. In a world where security is foundational, continued reliance on key-based access conflicts with Zero Trust principles and least privilege access. What’s New In GA AKS Workload Identity Support AKS Workload Identity (preview) extends the traditional managed identity model for Kubernetes by shifting the identity from the node to pods. Instead of inheriting the identity of the underlying cluster, each Kubernetes pod can use its own federated identity, mapped directly to a Microsoft Entra ID principal. This feature enables: Pod-level identity isolation, rather than cluster-level Least-privilege access with secure RBAC Seamless scaling and redeployment, without identity reconfiguration No secrets, no key rotation, no credential injection When combined with Azure Files over SMB, Workload Identity allows AKS workloads to access shared file storage securely and natively per pod, using the same identity-driven model as cluster level managed identities. Now available with AKS 1.35, for customers specifically in the financial services industries, AKS Workload Identity enables per‑application, least‑privilege access to Azure Files without credentials, improving isolation and auditability. This allows regulated, stateful workloads to run securely on AKS while meeting strict compliance and regulatory requirements. Co-existence of Application Identities and end-user identity access Azure Files now enables both Managed Identity and end‑user access on the same storage account, with users and applications independently authenticated via Entra ID and authorized through a shared permissions model. This unified access model eliminates the need for duplicate storage or credentials, enabling secure collaboration, troubleshooting, and automation on shared data without compromising governance or compliance. This supports scenarios such as: Developers accessing the same file share as an application for debugging Admins managing content used by automated workflows Hybrid environments with user-driven and app-driven access Simplified Storage Account enablement via the Azure portal We have now added a dedicated Managed Identity property that makes enabling identity‑based SMB access simple and transparent via the Azure portal for new as well as existing storage accounts. With a single configuration at the storage account level, customers can allow applications to authenticate to Azure Files using Managed Identities. This portal experience supports incremental adoption, making it easy to modernize authentication while maintaining compatibility with existing user access and governance models. Get Started with Managed Identities with SMB Azure Files Start using Managed Identities with Azure Files today at no additional cost. This feature is supported on HDD and SSD SMB shares across all billing models. Refer to our documentation for complete set-up guidance. Whether provisioning new storage or enhancing existing deployments, this capability provides secure, enterprise‑grade access with a streamlined configuration experience. For any questions, reach out to the team at azurefiles@microsoft.com.1.1KViews0likes0Comments
Pure Storage Cloud, Azure Native evolves at Microsoft Ignite!
In September, we were pleased to announce the General Availability of Pure Storage Cloud, Azure Native. A co-developed Azure Native Integration enabling more customers to migrate to Azure easily and benefit from Pure’s industry-leading storage platform – now supporting more customer workloads!560Views0likes0Comments
Take Data Management to the next level with Silk Software-Defined Azure Storage
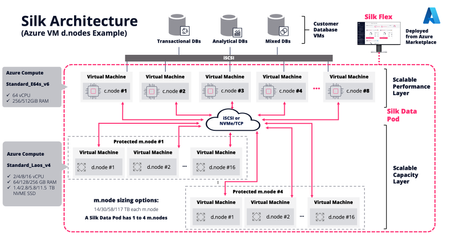
Note: This article is co-authored by our partner Silk. In today’s data-driven world, every enterprise is under pressure to make smarter decisions faster. Whether you're running production databases, training machine learning models, running advanced analytics, or building customer-facing applications, your data needs to be more agile, secure, and readily accessible than ever before. That’s where Silk’s software-defined cloud storage platform on Microsoft Azure comes into play — bringing performance, resiliency, and intelligence to data management across the cloud. With the recent addition of Silk Echo, you can now supercharge your Copy Data Management (CDM) strategy to ensure your data isn’t just protected, it’s available instantly for any purpose — a true strategic asset. Transforming Azure IaaS with Silk's Platform Microsoft Azure offers a rich ecosystem of services to support every stage of your cloud journey, and when paired with Silk, customers gain a game-changing storage and data-services layer purpose-built for performance-intensive workloads. Silk’s software-defined storage platform runs on Azure infrastructure as a high-performance data layer between Azure compute and native storage. It works by orchestrating redundant sets of resources, as close to the DB compute as possible. Aggregating and accelerating the native capabilities of Azure, enabling databases to reach the maximum physical limits of the underlying hardware. Silk makes use of the excellent L-series of storage optimized VMs and NVME media, ensuring the data is always quickly available and able to withstand multiple failures using erasure coding. Silk is designed to address common challenges customers face when migrating relational databases — such as SQL Server, Oracle, and DB2 — to the cloud: Performance Bottlenecks: On-prem workloads often rely on ultra-low latency, high-throughput storage systems with features that are difficult to replicate in the cloud. Data Copy Sprawl: Multiple non-production environments (dev, test, QA, analytics) mean many redundant data copies, leading to storage inefficiencies. Operational Overhead: Managing snapshots, backups, and refreshes across environments consumes time and resources. Silk changes the game with: Extreme performance in the Azure cloud. Up to 34GB/s of throughput from a single VM. The combination of Silk and Azure provide a unique cost/performance balance, through the combination of a very low latency software defined cloud storage platform and sharing of Azure resources. Inline data deduplication and compression for optimized resource utilization. Autonomous, fully integrated, non-disruptive, zero cost snapshots and clones for effortless environment refreshes. Multi-zone resilience and no single point of failure. This makes it easier than ever to lift and shift critical applications to Azure, with the confidence of consistent performance, uptime, and flexibility. Elevating CDM with Silk Echo for AI While Silk’s core platform solves performance and efficiency challenges, Silk Echo for AI introduces an intelligent, AI-powered layer that revolutionizes how organizations manage and leverage their data across the enterprise. At its core, Silk Echo for AI offers next generation Copy Data Management capabilities that empower IT teams to accelerate digital initiatives, reduce costs, and maximize the value of every data copy. Key Benefits of Silk Echo for AI Smarter Data Copying and Cloning Silk Echo leverages AI to understand data access patterns and recommends the optimal strategy for creating and managing data copies. Instead of manually managing snapshots, you can automate the entire workflow — ensuring the right data is in the right place at the right time. Instant, Space-Efficient Clones Using Silk’s advanced snapshot and cloning engine, Echo creates fully functional clones in seconds, consuming minimal additional storage resources. Teams can spin up dev/test environments instantly, accelerating release cycles and experimentation. Cross-Environment Data Consistency Echo ensures consistency across copies — whether you're cloning for testing, backup, or analytics — and with AI-driven monitoring, it can detect drift between environments and recommend synchronizations. Policy-Based Lifecycle Management Define policies for how long data copies should live, when to refresh them, and who has access. Echo automates the enforcement of these policies, reducing human error and ensuring compliance. Optimized Resource Consumption Silk Echo minimizes redundant data storage through smart deduplication, compression, and AI-driven provisioning — resulting in cost savings of 50% or more across large-scale environments. Enablement for AI/ML Workflows For data science teams, Silk Echo provides curated, up-to-date data clones without impacting production environments — essential for model training, experimentation, and validation. Real-World Use Case: Streamlining Dev/Test and AI Pipelines Consider Sentara Health, a healthcare provider migrating their EHR and SQL Server workloads to Azure. Before Silk, environment refreshes were time-consuming, often taking days or even weeks. With Silk Echo for AI, the same tasks will be completed in minutes. Now, development teams have self-service access to fresh clones of production data — enabling faster iteration and better testing outcomes. Meanwhile, their data science team leverages Echo’s snapshot automation to feed AI models with real-time, production-grade data clones without risking downtime or data corruption. All of this runs seamlessly on Azure, with Silk ensuring high performance and resilience at every step. Joint Value of Silk and Microsoft Together, Silk and Microsoft are unlocking a new level of agility and intelligence for enterprise data management: Data-as-a-Service: Give every team — DevOps, DataOps, AI/ML — access to the data they need, when they need it. Free snapshots democratize data so up-to-date copies can be made quickly for any team member who can benefit from it. AI-Ready Database Infrastructure: Your infrastructure evolves from a reactive model which is addressing problems as they arise (i.e. triggering responses on alerts), to a predictive model that utilizes AI/ML to forecast issues and mitigate them before they occur by learning patterns of behavior. Silk enables real-time AI inferencing, for business-critical agents that require access to up-to-date operational data. Reduced Costs, Improved ROI: Storage optimization, reduced manual overhead, and faster time to value — backed by Azure’s scalability and Silk’s performance. Accelerated Cloud Migrations: Achieve the enhanced scalability and flexibility of a cloud migration for your Tier 1 databases without refactoring. Get Started Ready to take your data management strategy to the next level? Explore how Silk’s software-defined storage and Silk Echo for AI can accelerate your transformation on Microsoft Azure. Whether you're modernizing legacy systems, building AI-driven applications, or simply trying to get more value from your cloud investments, Silk and Microsoft are here to help. By embracing the power of Silk’s software-defined storage and Silk Echo, organizations can finally make their data in the cloud work smarter, not harder. Contact Alliances@silk.us for a deeper dive on Silk!695Views2likes0CommentsAzure Native Pure Storage Cloud brings the best of Pure and Azure to our customers
Pure Storage Cloud is the result of a tightly coupled integration effort between the Pure and Azure teams that brings Pure’s industry-leading advanced data services to our customers. Built on rock solid Azure infrastructure, Pure makes Azure even better!535Views0likes0CommentsEnhance Your Linux Workloads with Azure Files NFS v4.1: Secure, Scalable, and Flexible
Enhance your Linux workloads with Azure Files NFS v4.1, enterprise-grade solution. With new support for in-transit encryption and RESTful access, it delivers robust security and flexible data access for mission-critical and data-intensive applications.1.3KViews0likes0Comments