security
654 Topics
My hotmail account got hijacked.
My old hotmail account got hijacked - I tried to log this weekend and got the message that "We couldn't find an account with that username". I understand that the hacker did an alias change. I ultimately was able to get a support chat, and the agent had me fill out a recover your account form, which I did, and gave them an alternative email address. After that, I got an email from Microsoft to the alternative email with a longer list of items to verify, which I filled out and submitted. I waited a few days with no response, so I replied to that Microsoft email asking for a status update, and got an automated response: "This case was previously closed as it was either resolved or closed due to non-response after multiple contact attempts. In both situations, a closure email explaining the reason would have been sent to you." But no contact attempt was made, nor a closure email sent to me. I got back on the support chat, and explained the situation and the agent said to reply to that Microsoft email asking for an update. I told him that I did so, but would do it again if it helped. After sending it again, I received the same automated message that the case was closed. The agent suggested that I go through the process again, which I have done. As I'm not expecting great results, I'm here to ask if I'm doing anything wrong, or if I can go through a different channel?38Views0likes1CommentI built a free, open-source M365 security assessment tool - looking for feedback
I work as an IT consultant, and a good chunk of my time is spent assessing Microsoft 365 environments for small and mid-sized businesses. Every engagement started the same way: connect to five different PowerShell modules, run dozens of commands across Entra ID, Exchange Online, Defender, SharePoint, and Teams, manually compare each setting against CIS benchmarks, then spend hours assembling everything into a report the client could actually read. The tools that automate this either cost thousands per year, require standing up Azure infrastructure just to run, or only cover one service area. I wanted something simpler: one command that connects, assesses, and produces a client-ready deliverable. So I built it. What M365 Assess does https://github.com/Daren9m/M365-Assess is a PowerShell-based security assessment tool that runs against a Microsoft 365 tenant and produces a comprehensive set of reports. Here is what you get from a single run: 57 automated security checks aligned to the CIS Microsoft 365 Foundations Benchmark v6.0.1, covering Entra ID, Exchange Online, Defender for Office 365, SharePoint Online, and Teams 12 compliance frameworks mapped simultaneously -- every finding is cross-referenced against NIST 800-53, NIST CSF 2.0, ISO 27001:2022, SOC 2, HIPAA, PCI DSS v4.0.1, CMMC 2.0, CISA SCuBA, and DISA STIG (plus CIS profiles for E3 L1/L2 and E5 L1/L2) 20+ CSV exports covering users, mailboxes, MFA status, admin roles, conditional access policies, mail flow rules, device compliance, and more A self-contained HTML report with an executive summary, severity badges, sortable tables, and a compliance overview dashboard -- no external dependencies, fully base64-encoded, just open it in any browser or email it directly The entire assessment is read-only. It never modifies tenant settings. Only Get-* cmdlets are used. A few things I'm proud of Real-time progress in the console. As the assessment runs, you see each check complete with live status indicators and timing. No staring at a blank terminal wondering if it hung. The HTML report is a single file. Logos, backgrounds, fonts -- everything is embedded. You can email the report as an attachment and it renders perfectly. It supports dark mode (auto-detects system preference), and all tables are sortable by clicking column headers. Compliance framework mapping. This was the feature that took the most work. The compliance overview shows coverage percentages across all 12 frameworks, with drill-down to individual controls. Each finding links back to its CIS control ID and maps to every applicable framework control. Pass/Fail detail tables. Each security check shows the CIS control reference, what was checked, what the expected value is, what the actual value is, and a clear Pass/Fail/Warning status. Findings include remediation descriptions to help prioritize fixes. Quick start If you want to try it out, it takes about 5 minutes to get running: # Install prerequisites (if you don't have them already) Install-Module Microsoft.Graph, ExchangeOnlineManagement -Scope CurrentUser Clone and run git clone https://github.com/Daren9m/M365-Assess.git cd M365-Assess .\Invoke-M365Assessment.ps1 The interactive wizard walks you through selecting assessment sections, entering your tenant ID, and choosing an authentication method (interactive browser login, certificate-based, or pre-existing connections). Results land in a timestamped folder with all CSVs and the HTML report. Requires PowerShell 7.x and runs on Windows (macOS and Linux are experimental -- I would love help testing those platforms). Cloud support M365 Assess works with: Commercial (global) tenants GCC, GCC High, and DoD environments If you work in government cloud, the tool handles the different endpoint URIs automatically. What is next This is actively maintained and I have a roadmap of improvements: More automated checks -- 140 CIS v6.0.1 controls are tracked in the registry, with 57 automated today. Expanding coverage is the top priority. Remediation commands -- PowerShell snippets and portal steps for each finding, so you can fix issues directly from the report. XLSX compliance matrix -- A spreadsheet export for audit teams who need to work in Excel. Standalone report regeneration -- Re-run the report from existing CSV data without re-assessing the tenant. I would love your feedback I have been building this for my own consulting work, but I think it could be useful to the broader community. If you try it, I would genuinely appreciate hearing: What checks should I prioritize next? Which security controls matter most in your environment? What compliance frameworks are most requested by your clients or auditors? How does the report land with non-technical stakeholders? Is the executive summary useful, or does it need work? macOS/Linux users -- does it run? What breaks? I have tested it on macOS, but not extensively. Bug reports, feature requests, and contributions are all welcome on GitHub. Repository: https://github.com/Daren9m/M365-Assess License: MIT (free for commercial and personal use) Runtime: PowerShell 7.x Thanks for reading. Happy to answer any questions in the comments.5.4KViews2likes4Comments
How to properly redact a PDF?
I need to share a PDF that contains names, email addresses, and other confidential details that must be removed first. Simply placing black boxes over the text does not seem secure, since the original content may still be searchable, selectable, or recoverable, so I need a way to permanently redact a PDF. Because the document contains sensitive information, I would prefer not to upload it to an online tool. I’m looking for either a built-in option or professional third-party desktop software that can permanently redact both text and images while processing the file locally. It would also be useful to remove hidden information from a PDF before sharing, including comments, document metadata, and any other embedded details. What is the safest way to handle this, and how can I verify that a PDF is properly redacted before I send it?Solved658Views0likes7CommentsHelp me recover my account.
Hi, My other Microsoft account was recently compromised but it was compromised before as well. When it was compromised before, the hacker added a recovery email for verification and to remove that I added my another email and the request was sent and it was supposed to change in October and I was not able to change the password or use other features of Microsoft because at some point it keep redirecting me to the page that I have sent a request but during that time period, my account was compromised again and I keep receiving emails of unusual sign-in activity by the hacker and I wanted to change the password but I couldn't because of that request so I was being patient. Now I received an email that someone accessed my Microsoft account and now I have to verify my identity to log in and to log in it ask me to type the email that the hacker set up because it's not changed and since I don't know what that is it takes me to the account recovery page where I put all the information that I know, I write in my postal code, my old and current passwords, date of birth etc. I have never used skype, Hotmail or outlook and Xbox so I just uncheck those boxes and then it asks me if I have ever bought any product but since I didn't so I uncheck that as well but then I just receive the email that the information I provided is nonsufficient even thou I provided all the information that is correct. Unfortunately Sign-in helper didn't work. Kindly help me resolve the issue. Looking forward to your positive response. Yours sincerely.45Views0likes0CommentsRevoking Access Tokens for Risky Service Principals
A Technical Community post discusses the topic of using the Entra ID continuous access evaluation (CAE) feature to revoke access for service principals when apps become risky or potentially compromised. The Microsoft Graph Command Line Tools app is a good example of a service principal in common use, so we examine the access tokens issued for interactive Graph sessions to discover if they are CAE-enabled. Just for fun! https://office365itpros.com/2026/09/03/cae-service-principals/118Views0likes0Comments
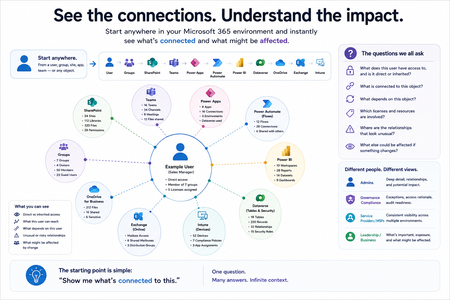
How much of your Microsoft 365 environment can you actually see at once?
Not how many users you have. Not how many sites, teams, apps or flows you have. How much of it can you actually see connected together? I've been working across Microsoft 365 environments for a while, and I kept running into the same thing. There is no shortage of information. If anything, there is probably too much of it. Users, groups, permissions, SharePoint, Teams, Power Apps, Power Automate, Power BI, Dataverse, OneDrive, Exchange, Intune, licensing, configuration... It's all there. But when you're actually trying to understand how everything fits together, it can be a different story. You open one blade. Find something. Open another. Cross-check it. Go back. Open something else. Before long, you're jumping between different parts of the tenant trying to build the bigger picture in your head. And if you're working with larger environments, that gets difficult pretty quickly. The information isn't necessarily missing. The relationships between the information are what can be difficult to see. That got me thinking about a slightly different question: Instead of "where do I find this information?" "Show me what's connected to this." That's where VisibleState started. Start anywhere. Follow the connections. Imagine starting with a single user. Instead of seeing that user simply as a record with a list of properties, imagine being able to explore the relationships around them: User → Groups → SharePoint → Teams → Power Apps → Power Automate → Power BI → Dataverse → OneDrive → Exchange → Intune Then the questions become different: What does this user have access to? Is that access direct or coming through a group? What resources are connected to them? What depends on something they're associated with? Which licenses are involved? Are there relationships that look unusual? If something changes, what else might be affected? Those questions aren't necessarily about finding another piece of information. They're about putting information that already exists into context. A report can tell you that something exists. A connected view helps you understand what it is connected to. Illustrative example below — not a real customer environment. I'm not suggesting Microsoft 365 doesn't already give us this information Quite the opposite. Microsoft 365 already gives administrators an incredible amount of information and tooling. The thing I've been thinking about is what happens when you want to look across those boundaries. Sometimes I don't want another export. I don't want another list. I don't necessarily want another dashboard. I want to start with something I'm looking at and ask: "What's connected to this?" And then keep following the trail. That's the idea I'm exploring with VisibleState. The interesting part is what happens when you change the viewpoint The same relationships can be useful for completely different reasons. For example: Administrators may want to understand access, permissions and dependencies. Security and governance teams may want to find unusual relationships or exceptions. Compliance teams may need to understand who can access something and why. People managing multiple environments may want a consistent way to understand what's there without rebuilding the picture manually every time. Leadership may not need to see the graph at all. They may simply want to know what's important, what's exposed and what could be affected. It's still the same underlying environment. You're just looking at it from a different angle. And that's where I think things get interesting. Where I'm at with it VisibleState started as something I was building to make my own work easier. I was spending a lot of time investigating environments, tracing access and putting information together for reports. The individual tasks weren't necessarily difficult. It was the jumping between different places and reconstructing the bigger picture that took the time. So I started building something that would let me approach the environment through the relationships instead. It's grown quite a bit from where it started, and I'm continuing to build it. I'm not posting this as a product launch, and I'm not looking for people to sign up. I'm genuinely interested in whether the problem I'm seeing is familiar to other people working with Microsoft 365. So I'm curious... If you could start with any object in your Microsoft 365 environment and immediately see what it's connected to, where would you start? Would it be: Users and access Groups and permissions SharePoint and Teams Power Apps, Power Automate, Power BI and Dataverse Licensing and resources Governance and unusual relationships Something completely different Maybe you've already got a good way of doing this. Maybe you still find yourself jumping between different services and piecing things together manually. Or maybe I'm looking at the problem from the wrong direction. What's the one relationship in your Microsoft 365 environment that you wish you could see instantly?206Views0likes0Comments
Why is Microsoft being a bully in regard to security defaults?
Hi, I received this email today: The security defaults setting for your domain.com tenant will be turned on by May 11, 2023 You’re receiving this email because you’re a global administrator for domain.com. To help protect your organization, we’re always working to improve the security of Microsoft cloud services. As part of this, we’re enabling the security defaults setting in your tenant that includes multifactor authentication, which can block more than 99.9 percent of identity attacks that attempt to compromise your accounts. When you log in to your account between April 27, 2023, and May 11, 2023, you’ll see a message prompting you to proactively enable security defaults. If you haven’t logged in or enabled this setting when that timeframe ends, we’ll enable it for you automatically. This is my subscription, I pay for it and Microsoft has no right to tell me what to do!!!! Angry I already disabled my security defaults in Azure admin centre a long time ago and do not want security defaults on because there may be situations where my mobile is unavailable, there is no signal or the battery is flat. Microsoft can suggest this, but cannot force their clients to enable this if they don't want to. There are many of my clients that don't want to authenticate a second time because it would cause a nightmare with their employees. Forcing someone is dictatorship. In a democratic society people get to choose what they want to do. I read that I can use conditional access policies but Microsoft is going to hit you with an additional Azure AD Premium subscription on top of what you are already paying. Many of my clients are small businesses who try to keep their costs down. Currently inflation is rampant and many small businesses are going bust. Thanks Microsoft for increasing our cost of living and running a business. This is my 2 cents worth on this subject.2.7KViews1like4CommentsMicrosoft Tightens Security for Self-Service Password Reset
Microsoft plans to improve the security of the Self-Service Password Reset (SSPR) facility in September 2026 by requiring users to register at least one authentication method. SSPR will then use the registered authentication method to verify user accounts when changing passwords. The change aligns SSPR with user sign-ins and improves security by removing fallback on directory attributes, which might be altered by attackers. https://office365itpros.com/2026/06/17/sspr-authentication-methods/468Views0likes0CommentsOffice 365 Mailbox Export to PST - Third Party Tools: What’s Your Experience?
Exporting Office 365 mailboxes to PST is still a common requirement in many Microsoft 365 environments, especially for backup, compliance, and migration scenarios. While Microsoft offers native options like Purview eDiscovery and Outlook export, many administrators also consider third-party tools when dealing with large mailboxes or bulk export requirements. In real-world scenarios, factors like speed, ease of use, permission handling, and consistency of exported data often influence the choice of tool. Some teams prefer native methods for compliance control, while others explore third-party solutions to simplify large-scale or repeated export tasks. For those working with Microsoft 365, what has your experience been with third-party PST export tools? Have they helped in your environment, or do you still rely mainly on Microsoft’s native options?498Views1like3Comments