networking
335 Topics
Hyper-v Ubuntu 26.04LTS Multiple DHCP entries
Good evening, am running windows server 2022 datacenter edition, which is running multiple hyper-v machines. I have been installing a new instance of ubuntu 26.04.1LTS but have noticed something weird. Maybe you could assist. Issue: When fresh install Ubuntu 26.04.1 into a VM using hyper-v, I notice 2 IP addresses appear in windows DHCP (192.168.40.20, 192.168.40.21). When I shut down the instance only one disappears (192.168.40.21). If I delete 192.168.40.20 and restart the VM instance both Ip addresses reappear in DHCP. Points to note: Image was downloaded direct off the website with no changes (have redownloaded to make sure image is not broken) Have tried using a different name for the server Have noticed the ubuntu instance only picks up one address (192.168.40.21) for the adaptor. Am unable to ping 192.168.40.20 or connect to that address via ssh. Would anyone have any idea, where the second IP address would be coming from in DHCP?6Views0likes0Comments
Hyper-V Cluster Failover Event viewer log showing SMB traffic connect to quorum disk network share
Hi, To tweak my SIEM, I need to correlate smb network traffic between Hyper-V servers and witness disk stored on a network share on another server. I'm searching a log who tell me the Hyper-V is connecting to the witness disk (on network shared drive) for doing something ... probably I will be able to correlate and put exception when this happens and the SMB traffic between Hyper-V and the other server to stop always receive this alert. Any cues would be appreciated! Thanks448Views0likes1Comment
NPS network policy with multiple Client ip4 addesses
I have a wireless policy on my NPS server with the primary wireless controller added using a Client IPv4 address entry in the policy. I want to add the backup controller as well but it seems it is adding it as a and condition. I need it to be added as an or condition when the primary controller is unreachable. How can I add multiple Client ip4 addessess in a Network policy with an or condition? An and condition would require both to be reachable. thanks.139Views0likes1CommentAssign IP Address for Windows Server 2025 VM on Hyper-V
I have built my first Windows Server 2025 VM on HyperV and trying to assign an IP address. I want the VM's to be like an actual server so I Created an external vswitch. The HyperV server IP is 172.16.1.41 with a physical gateway of 172.16.1.5. I have tried to assign the new VM with 172.16.1.42/255.255.255.0 and the Gateway is 172.16.1.5 also. However, I cannot get a positive ping. Do I need another VSWITCH configured or what am I missing?363Views0likes5Comments
Hyper-V Converged Networking for VEEAM Backups
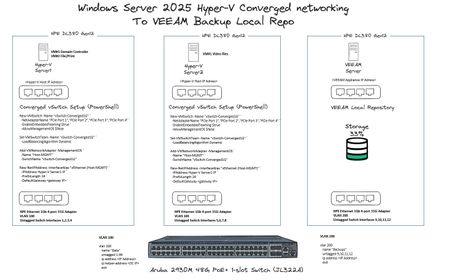
Hi All, As per the image below, I have 3 x HPE DL380 Gen 12 Servers, Server1 and Server2 are ADDS domain joined, VEEAM Local Repo is not. For the converged networking to work, is there anything else I need to perform in terms of additional power-shell commands, VLAN tagging etc? Thanks!328Views0likes2Comments
Unable to Build Switchless Storage using Network ATC
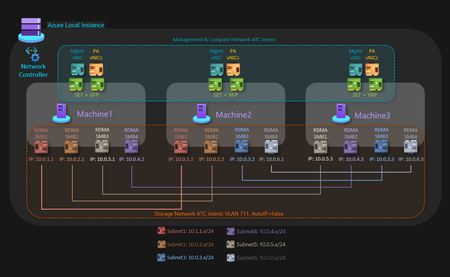
3-Node HV/S2D Cluster using Switchless Storage and Network ATC getting Network HUD Error I have a Dell 3-node server cluster being used to host Hyper-V with S2D. Each node is identical and certified to pass S2D requirements. The networking consists of 2 onboard 1 Gbps and 2 quad-port PCI(e) NICs at 10/25 Gbps. The 2 onboard ports are being used for the management intent, 2 ports from each of those NICs are being connected to 2 top-of-rack switches for the compute intent at a total of 12 10 Gbps connections, and the other 2 ports from each of those NICs are being connected directly to the other nodes in a dual mesh method for the storage intent at a total of 6 25 Gbps connections. Very similar to the Microsoft diagram for a three-node storage switchless, dual TOR, dual link deployment network reference pattern for Azure Local, but I am using Windows Server 2025 Datacenter, not Azure Local. The problem I am encountering is when I attempt to create the switchless storage intent, I get an error (shown below) that reads "Failed to fetch physical NIC mapping from the Network HUD service. Please diagnose..." If I leave off the switchless option, it builds without issue. The error only occurs when I attempt to use the switchless option. I tried without configuring the NIC IP addresses first, as well as trying configuring the NIC IP addresses beforehand. I tried without having a cluster built first, as well as building a failover cluster without storage before running the network intent command. The error I posted below shows my last attempt after having the NICs configured with IP addresses and having a failover cluster established before running the command. The error has remained the same throughout the process. Has anyone else run into an issue like this with switchless storage? It seems like everything that I am trying to do is within scope and should be a supported solution. My fallback plan is to use my existing switches, but that drops my connection speeds down from 25 Gbps to 10 Gbps due to hardware limitations.485Views0likes4CommentsBLOG: CVE-2024-38063 - Disabling IPv6 binding = fix - or not?
Dear community, in today's LinkedIn Stream and other social media you might have noticed a recent CVE and the recommendation to disable IPv6 in Windows Server and Windows Client. We are talking about this one: https://msrc.microsoft.com/update-guide/vulnerability/CVE-2024-38063 Reading the advisory carefully, Microsoft, strictly speaking, does not directly recommend disabling (technically remove binding) of IPv6. Citing: "Mitigation refers to a setting, common configuration, or general best-practice, existing in a default state, that could reduce the severity of exploitation of a vulnerability. The following mitigating factors might be helpful in your situation: Systems are not affected if IPv6 is disabled on the target machine." Maybe I am a bit nitpicking here about old experiences and would greatly appreciate a refreshed Microsoft statement on the disablement (unbinding) of IPv6 and the side-effects in 2024. What we have learned in the past - do no disable IPv6 easily. - yes, you can face issues with IPv6 being on by default and unexpected or misconfiguration. Often caused by DHCPv6, especially in the combination of critical domain controllers, Dual Stack ISPs and SoHo routers messing up your DNS. What's the fuss about IPv6? I am not actively using it in corporate / at home. IPv6 is being used in Windows. More specifically non-routable fe80 addresses and loopback ::1 for internal purposes of Windows or other software. One may complain use cases are - unrightfully - not well and transparent documented. Have a read in the past Here are some references that Copilot brings up. Trust my memory, I've read more like this. https://techcommunity.microsoft.com/t5/core-infrastructure-and-security/ipv6-for-the-windows-administrator-why-you-need-to-care-about/ba-p/256251 https://community.spiceworks.com/t/is-it-a-bad-practice-to-disabe-ipv6/781811/9 https://learn.microsoft.com/en-us/troubleshoot/windows-server/networking/configure-ipv6-in-windows My personal conclusion Hold on, we need patches for this CVE, but we should not disable IPv6 easily. Please disable IPv6 temporarily, when you cannot patch this CVE immediately / in time. Take notes which system you have had to disable and consider re-enabling once patches have been tested and applied. If you are using IPv6 knowingly, note the NIC configs. They will be lost when using static settings rather DHCPv6. I am sad to see that NetSec people, undoubtedly experts in their area, jump on the bandwaggon esp. on Social Media to easily disgrace the IPv6 by default enablement of Windows Client and Windows Server, telling you the easier story: "Disable IPv6 and you are good / if you do not need it." Let me counter: You might not know you're "needing it" it in the first place. Whenever you are changing system defaults in Windows, mind that Microsoft and other software vendors may not consider these changes in their testing. And the Crowdstrike Black Friday showed us clearly how outlier system configs and unwell testing goes along. Not very well. IPv6 usage and defaults today One of the most recent example that Microsoft is using IPv6 can be found in the Azure Arc Agent (Connected Machine Agent) changelog: "Better handling when IPv6 local loopback is disabled" source: https://learn.microsoft.com/en-us/azure/azure-arc/servers/agent-release-notes How can I disable IPv6, if required? Many roads led to Rome. Windows + X > Terminal / PowerShell (Admin) #save current NIC config into a simple text file Get-NetAdapterBinding -ComponentID "ms_tcpip6" | where Enabled -eq $true | Out-File $env:temp\original-ipv6-config.txt #disable IPv6 on all adapters Get-NetAdapterBinding -ComponentID "ms_tcpip6" | where Enabled -eq $true | Disable-NetAdapterBinding And how to revert the change? Windows + X > Terminal / PowerShell (Admin) #enable IPv6 on all adapters (mind the text file) Get-NetAdapterBinding -ComponentID "ms_tcpip6" | where Enabled -eq $true | Enable-NetAdapterBinding TL:DR Microsoft is using fe80 addresses and loopback ::1 addresses for internal reasons. IPv6 is preferrably used over IPv4 when it is bound to a network adapter, including said special non- routable addresses. Please disable IPv6 temporarily, when you cannot patch this CVE immediately / in time. Take notes of current config. Please share the word and mind that disabling IPv6 can turn your OS into an outlier system, causing immediate or later issue due lack of testing by Microsoft or other software vendors, assuming the defaults, which is IPv6 being turned on.8.3KViews2likes2Comments
Did Microsoft make a mistake? WinServer 2022 Standard and up.
Microsoft removed functionality of Windows Deployment Service. I know their are ways to to get around this but they either are hackjobs or deploying your own windows with PE. as far as i know of writing this. I know I could go linux. they have a simple cd to follow. Or Mac has their own version for macs. but not microsoft. They THREW it away for some stupid reason. Do I really have to do a VM or worse ditch DNS & DHCP?175Views0likes1CommentSCCM- Upgrade from 2409 to 2509 WSUS timeout issue
Had a working task sequence on 2409 that performed software updates at the end of the task sequence. Upgraded to 2509 - I get a timeout issue when getting to that point on the task sequence. Ive performed maintenance on the WSUS Server, (obsolete, expired etc) I removed the Software Update Point - and re installed it selected the Products of Server 2016,2019, server operating system 21h2 , Windows 10 1903 or later and Windows 11. rebooted both the SCCM and SQL Server. after doing the above but the HRESULT 0x80244010 still persists. "Exceeded max server round trips" — client couldn't retrieve all updates in one cycle. Software centre updates in the OS seem to be unaffected or unknown if clients are affected, only in a task sequence this occurs. Blog posts refer to older items, what would cause this to fail after a upgrade from 2409 to 2509? AI help repeats about reducing metadata and updates but for weird reason i keep getting 700+ updates for the above categories!530Views0likes2Comments