incident response
11 Topics
CDOC Contact Information - Responses Failing to Reach CDOC Team
Good afternoon, I'm not sure if this is the correct forum to post this but I thought it might be the best place to start. I have been unsuccessfully trying to recover my child's compromised account for almost a month. Each of the 5 times I have followed the same steps, which eventually lead me to receiving an email with and SIR number, and telling me I need to provide more information to verify ownership of the account. When I reply to the email (from email address removed for privacy reasons and email address removed for privacy reasons ) it's like my response are black-holed somewhere. Eventually I get an email saying the following: This is NAME with Microsoft Customer Support again. I hope your day is going well. I wanted to touch base as I have not heard back from you. We want to be able to assist you with your request, but I still need the information that I requested to be able to consider moving forward with a resolution. I apologize in advance for the length of this email, but I wanted to be sure that I included everything. and then : Hello, This is NAME again with Microsoft Support. I initially e-mailed you on DATE with a request for the information required to confirm what your previous [recovery e-mail] was yours. your previous [recovery e-mail] is required before we can assist with your request. As no response was received, we have closed your case and any further replies will go to an unmonitored mailbox. If you still need assistance, please open a new case with us at Recover your Microsoft account | XBOX Support. You will receive an automated e-mail with confirmation that we have received your ticket. Please respond to that e-mail and reference this ticket number. Or Hello, Thank you for reaching out. This case was previously closed as it was either resolved or closed due to non-response after multiple contact attempts. In both situations, a closure email explaining the reason would have been sent to you. If you require further assistance, please open a new case by visiting hxxps://support.microsoft.com/. No matter what I tell the online chat agent, they tell me to be patient and submit the form. There seems to be no way to escalate the fact that my emails are not reaching the CDOC Team. Is there a workaround to reach them so they can receive the information that I'm providing and recover my child account? J24Views0likes0Comments
Microsoft confirmed my account was hacked, but says it cannot be recovered
I am looking for guidance from the Microsoft Community or anyone who has experienced a similar account-takeover situation. Microsoft Support investigated my case and confirmed that there was unauthorized access to my Microsoft account. During the takeover, the third party changed the account's security information and enabled 2FA. Microsoft has now told me that because the security information was changed, Customer Support is unable to recover the account. The account has instead been permanently suspended. What I find difficult to understand is that the very security changes made during the confirmed unauthorized takeover now appear to prevent the legitimate account owner from recovering the account. I have already provided evidence supporting my ownership, including: Original Minecraft purchase information/invoice Billing information associated with the purchase My original account details Confirmation that the email address subsequently added to the account does not belong to me Microsoft Support's own investigation confirming unauthorized access I am not asking Microsoft to bypass account-security procedures. I am asking whether there is an escalation or verification process specifically for cases where Microsoft has already determined that an account was compromised. My questions to the community/Microsoft moderators are: Is there a senior Microsoft Account Security, Fraud, or Account Takeover team to which a confirmed-compromise case can be escalated? Can historical account information, previous security information, billing records, purchase history, device/account history, or original game entitlements be used to establish ownership? If the account itself genuinely cannot be restored, is there any process to restore or transfer a legitimately purchased Minecraft entitlement to a new Microsoft account after ownership has been independently verified? Is there any formal review or appeal mechanism available after Support has classified an account as unrecoverable? Has anyone successfully resolved a similar situation where an attacker changed the security information/2FA before the legitimate owner could regain control? I fully appreciate the need for strict account-security controls. However, I would like to exhaust the legitimate escalation and ownership-verification options before accepting that both the account and a legitimately purchased product are permanently lost because of security changes made by an unauthorized third party. Any guidance from Microsoft moderators or community members on the correct escalation channel would be greatly appreciated. Thank you.28Views0likes0Comments
Microsoft defender is not catching threats before they are put into download folder.
Before I post this, please note that I’m a security researcher trained to investigate malware and other application bugs. my complaint is the following and it's a serious one that should be fixed by Microsoft as soon as possible. When I downloaded several malicious EXE files, Microsoft Defender didn't block or quarantine them during the download. Instead, Defender only detected them after I actually ran or executed the files. I also noticed that online platforms showed Microsoft Defender detecting the threats, so the files were clearly being recognized as malicious by Defender's engine. Has Microsoft changed the way Defender detects malware? Does it now require a malicious file to be executed before it detects it, similar to how some behavioral detection works in Malwarebytes? Or should Defender still be detecting and blocking known malicious EXE files before they are executed/downloaded because it's not at this current time and this is a clean installed system. My system is clean, and I even performed a clean installation of Windows. I also used ConfigureDefender with the settings configured to High, and all of the relevant protection settings appeared to be enabled.I'm trying to understand whether this is normal behavior with the current version of Microsoft Defender or if something might be misconfigured on my system. Before, Microsoft Defender would detect and block malicious files while they were being downloaded, before I had a chance to run or execute them. Now, however, it seems like Defender is allowing the files to finish downloading and only detects them after I execute them. Windows Defender isn't detecting EICAR test files? Mine doesn’t seem to detect them automatically, as shown in my proof. It only detects the file when I right-click it and select “Scan with Microsoft Defender.” Is this normal? It seems pretty crazy that it doesn’t detect the file immediately. it allowed them all to download. It's not even blocking Eicar test files when i bypass edges warning to download it just allows it to download no problem. edge detects it but Microsoft security does not. Please have Microsoft’s threat team investigate why Windows Defender isn’t detecting malicious files when downloaded through Microsoft Edge. When Edge warns about a malicious or suspicious download and those warnings are bypassed, the files aren’t caught or blocked by Defender and end up being saved to the system. This is extremely dangerous and needs to be replicated to confirm the issue.101Views0likes0CommentsAutomating Defender Alerts with CISA KEV and n8n – Has anyone tried similar workflows?
Hi everyone, I’ve been experimenting with n8n automation to improve vulnerability management. I created a workflow that cross-references Microsoft Defender for Endpoint vulnerabilities with the CISA Known Exploited Vulnerabilities (KEV) catalog, and then automatically creates Jira tickets for remediation. The flow takes about 16 seconds to run and prioritizes only the CVEs that are both present in the environment and listed in KEV. Has anyone here built similar automation (maybe with Logic Apps, Power Automate, or Sentinel playbooks)? Would love to hear how others handle vulnerability prioritization or ticket creation!540Views0likes0CommentsAutomação de Alertas do Defender com o Catálogo KEV da CISA usando n8n
Overview Recently, I decided to explore how automation could help simplify daily security operations, especially in vulnerability management. While studying n8n, an open-source automation platform, I saw the opportunity to connect it with Microsoft Defender for Endpoint and the CISA Known Exploited Vulnerabilities (KEV) Catalog. The goal was simple: build an automated workflow that identifies which vulnerabilities detected in Defender are actively exploited in the wild, and then create actionable tickets in Jira for remediation teams — automatically and with full context. Why I Built This Most security teams deal with thousands of vulnerabilities every week, but only a small portion are actually being exploited. I wanted to find a way to prioritize what truly matters without adding more manual work. Defender for Endpoint already provides strong vulnerability data, but by combining it with the CISA KEV catalog, we can instantly highlight high-risk CVEs that need urgent attention. This project was also a great opportunity to test n8n’s flexibility and API-handling capabilities in a real-world cybersecurity scenario.211Views0likes0Comments
EDR logs explanation
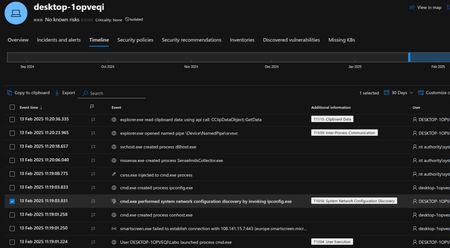
Hello, would it be possible for an expert from this forum to analyze the EDR logs? Could you also explain to me in detail what happened? Furthermore, can you tell me if it is clearly established that the deleted files were deleted by someone physically present on the machine, or if there are other possible explanations? Thanks in advance.203Views0likes0CommentsMy laptop has been blocked by BitLocker.
However, there is no BitLocker recovery keys on my Microsoft account. I have tried to call Microsoft support, but I only get bot messages that take me to sites that asks me to go and check my Microsoft account. Is there any way I can chat with a human that can actually help me how to get around this BitLocker? thanks495Views0likes1Commentmultiple Login tries from different places
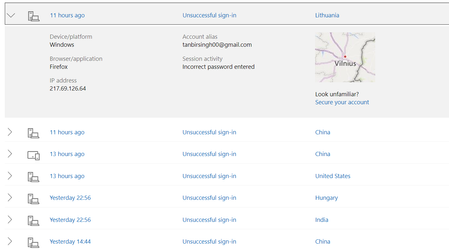
hi, from a long time I'm facing a really threatening issue of SOMEONE trying to login to my account. my sign in history shows that after like every 2 hours a new guy from new place is trying to log into my account but unable to do it coz of wrong password. Now this is really scary coz in a way someone is just keep on trying to use different passwords until he got the right one. I'm not getting what to do right now instead just waiting when he logs in and then log out from there. otherwise, I have used almost kind of Secuity measures like using authenticator app and two step verification. If anyone know anything that i can do right now from stop this then please help634Views0likes1Comment