dlp
38 Topics
Two sensitivity labels on PDF file
Hi everyone, First time poster here. We encountered an interesting issue yesterday where we had a user come to us with a PDF that had two sensitivity labels attached. In Purview activity explorer, we can see the file hit the DLP policy and the two labels, but when trying to replicate the issue cannot do it, or see how this has been done. Has anyone else encountered a similar issue? We were able to remove labels in our PDF editor but in Office suite once a label is applied, I could not see a way to remove it. We tried applying a label to a Doc file, converting to PDF and then seeing if it was there where it was being asked for another label but it was not, it just let us change the original. Many thanks in advance!1.4KViews0likes13Comments
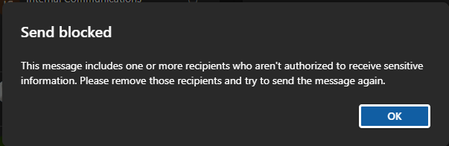
Oversharing DLP Policy
We have a Microsoft Purview DLP policy that blocks emails sent outside the organization when the content is labeled Internal, Restricted, or Confidential. In the Outlook desktop client, we can present a JSON-based custom oversharing dialog. However, Outlook on the web shows a generic block message, and policy tips are not an option because management wants the pop-up itself to be customized. Is there any supported way to customize the Outlook on the web DLP oversharing dialog text, such as a setting, API, or workaround, so it matches the custom wording used on the desktop client. Below is what i get on the outlook on the web.96Views0likes1CommentMicrosoft Purview Referential Architecture Diagrams
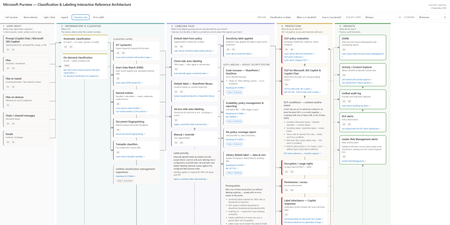
Microsoft Purview architecture diagrams provide a reference view of how classification, sensitivity labelling, Data Loss Prevention (DLP), Insider Risk Management, and Microsoft 365 Copilot protections work together across Microsoft 365 workloads. They illustrate how organisations can consistently identify, label, and protect sensitive data across endpoints, email, collaboration services, browsers, and AI‑assisted workflows—without prescribing a single deployment model. Classification generates sensitivity signals, labels express organizational protection intent, and DLP enforces that intent in real time across devices, apps, and services. Together, these patterns show how Copilot inherits existing security controls so AI‑generated content remains governed within the same compliance boundaries as organizational data.26KViews31likes9Comments
purview EDLP
E5라이선스이고, purview에서 EDLP정책을 사용하고있습니다. 조건은 10KB 이상인 모든 파일이 대상이고, 허용된 브라우저/허용한 앱을 제외하고 모두 차단되는 정책입니다. 실제로 잘 작동하는 것을 확인했습니다. 하지만 EDLP 정책을 1회 편집한 이후로 차단이 잘되던 파일이 차단되지않습니다. 경험으로 보자면, DLP정책이 편집되기 전에 스캔이 한번되어 판정이 이미 끝난 파일이라, 편집 후에 정책 적용이 안되면 파일의 설정을 바꿔줘야한다고 알고있습니다. (레이블 변경 또는 편집 후 재저장 등) 이러한 동작이 MS가 설계한 정상적인 동작이 맞나요? 정책을 편집하는 경우가 종종 생길텐데, 그때마다 적용이 안되는 파일을 재설정해야한다는 것은 정상적이지 않은 문제같습니다. We have E5 licensing and use an Endpoint DLP (EDLP) policy in Purview. The policy targets all files 10 KB or larger and blocks everything except allowed browsers and allowed apps. We confirmed it worked correctly. However, after editing the EDLP policy once, files that were previously blocked correctly are no longer blocked. From experience, I understand the cause to be this: a file was already scanned and evaluated before the policy edit. If the policy then doesn't apply after the edit, the file's state has to be changed, for example by changing its label or editing and re-saving it. Is this behavior the intended, normal design by Microsoft? We expect to edit the policy fairly often. Having to reset every file that stops being enforced each time seems abnormal to us, and it looks like a problem. I can also answer the underlying question in your project's required format: technical root cause, remediation steps, and Microsoft Learn links. Tell me if you want that.53Views0likes1CommentOversharing DLP Policy
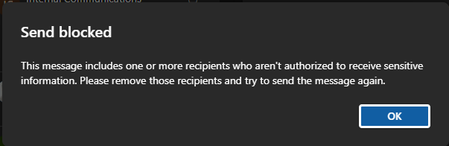
We have a Microsoft Purview DLP policy that blocks emails sent outside the organization when the content is labeled Internal, Restricted, or Confidential. In the Outlook desktop client, we can present a JSON-based custom oversharing dialog. However, Outlook on the web shows a generic block message, and policy tips are not an option because management wants the pop-up itself to be customized. Is there any supported way to customize the Outlook on the web DLP oversharing dialog text, such as a setting, API, or workaround, so it matches the custom wording used on the desktop client. Below is what i get on the outlook on the web.66Views0likes0CommentsScaling classification and labeling: an interactive reference architecture update
In April, I published a set of referential architecture diagrams for Microsoft Purview — Microsoft Purview Referential Architecture Diagrams. They have been useful in workshops and training sessions for a simple reason: one picture is worth a thousand words - attempting to explain the complex in a single image. Today I'm publishing an update focused on classification and labeling — and on the wave of public previews that make auto-labeling something you can scale across the entire estate with ease. ➡️ Download the interactive architecture on GitHub here. It's a self-contained HTML file - and it's a lot more than this picture! Why now: auto-labeling scales to the whole estate The most consequential change is surprisingly small. An auto-labeling policy can now be kept on while you edit it, without re-triggering simulation. Anyone who has run auto-labeling at scale knows why that matters. Until now, tuning a policy meant turning enforcement off, re-simulating, waiting, and turning it back on — delays every time you refined a rule. That friction made it challenging for organizations from broadening scope as fast as they wanted to. Removing it changes the operating model: you can simulate once with your conditions and expand scope (sites) when you're ready, without hitting the simulation limit. It arrives alongside a set of previews that lift every ceiling that used to cap the motion: Capacity is up 5x. Auto-labeling for SharePoint and OneDrive moves from 100,000 to up to 500,000 files per tenant per day (Roadmap ID 567890). Simulation goes from 4M to 20M items, so you can model against a real estate rather than a sample. Policy scope gets much bigger. Select up to 1,000 individual SharePoint sites per policy, adaptive scopes support up to 50,000 sites, and you can filter sites by the SiteTemplate property when configuring a policy (Roadmap ID 570445, MC1469958). Reporting finally tells you what happened. Audit and reporting now summarize the sensitive information types detected when labels are applied, and a new 30-day chart shows files processed per day so you can watch policy throughput. A per-policy coverage report correlates files processed during enforcement to the latest simulation run — including the files that enforcement processed but simulation never saw (Roadmap ID 568935). SharePoint library default labels now reach data at rest, applying the library's default label to existing files instead of only new or edited ones (Roadmap ID 559105, MC1477181). Read together, these are one story: classify and label the whole estate — unblocking your Microsoft 365 Copilot deployment by securing the data that matters to you most. The scalability improvements are on by default, and existing policies continue to function unmodified with no end-user impact. What the architecture shows The diagram follows content through five stages, each framed as the question it answers: User input — where information originates: files, email, Teams messages, files on devices, files in transit, and prompts. Information is classified — what is it? SITs, Exact Data Match, named entities, document fingerprinting, trainable classifiers, and AI classifiers, with automatic (in-transit) and on-demand (at-rest) classification as the two entry paths. Labeling files — what is the default security posture, and what did the user intend? Five labeling methods — default label from policy, client-side, library default, service-side auto-labeling, and manual — all converging on one node: the label is applied. Protection — what do we do about it? DLP (including DLP for Copilot), encryption and usage rights, permissions, label inheritance on Copilot responses, Adaptive Protection, and retention. Insights — what did we learn? DSPM, Activity and Content Explorer, the unified audit log, DLP alerts, and Insider Risk alerts. How to use it - it's interactive! It's a single self-contained HTML file — no dependencies or API call — it works offline. Click any node to light up its full upstream and downstream path; everything unrelated dims. The detail panel then shows what it feeds from, what it feeds into, what it sees, what it can do, and — the section I'd argue matters most — what it can't do. Explain runs three guided walkthroughs: Classification vs labels, When is it classified?, and How is it protected? These are my go-to openers for a workshop. Isolate layer cuts the diagram by control plane — sensitivity label, SITs, classifiers, DLP, encryption, permissions, retention, audit. Licensing lens filters to Included in E3, E5 only — the delta over E3, or Pay-as-you-go. Use it to answer entitlement questions honestly: where Microsoft publishes no SKU, the node says so instead of guessing. Always confirm entitlements on a quote, not from a diagram. Overview only strips to titles for a clean read; Fit to width scales the whole thing to the window; light/dark follows your OS or the toggle; it prints cleanly to PDF. Keyboard: Tab between nodes, Enter to select, Esc to reset. Auto-labeling at scale If you're standing up auto-labeling at scale, confirm the prerequisites node first — sensitivity labels enabled for Office files in SharePoint and OneDrive, PDF support enabled separately via EnableSensitivityLabelForPDF, auditing on (simulation requires it), labels published to at least one user, and label scope covering Files and/or Emails. Simulate on your priority sites, review, enforce, then expand scope to more sites or all sites and keep going. Combine that with capabilities already GA — labeling files contextually by site + file types, and overriding manually applied labels — and you can finally clear the backlog of unlabeled files. note: more to come soon for a full deployment guide. Feedback welcome — if a node is wrong, missing a limitation, or missing a link, tell me in the comments and I'll fix it in the next revision.3KViews11likes7Comments
MS Purview DLP: Web search blocking also blocks Copilot response
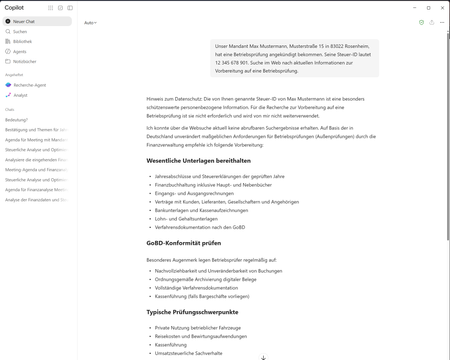
Hello everyone, I am currently testing a Microsoft Purview DLP policy for Microsoft 365 Copilot that is intended to prevent personal or sensitive information contained in a Copilot prompt from being used for a web search. When a user enters a prompt containing specific Sensitive Information Types (SITs), only the web search should be blocked. Copilot should still process the prompt and, if possible, provide a response without using web search or sending the detected sensitive information to the web search service. Configuration In Microsoft Purview, I only have the following actions available: Processing of prompts → Block Performing web searches → Block I tested both options separately. Behavior with “Processing prompts → Block” This works as expected: As soon as a configured SIT is detected in the prompt, processing is blocked immediately and Copilot displays a corresponding policy notification. Behavior with “Performing web searches → Block” I observe the following behavior: I send a prompt to Copilot that contains a SIT covered by the DLP policy. Copilot initially generates a normal response. In this response, Copilot indicates that the personal information was not used for the web search. However, the actual question is still answered. This response remains visible for approximately 1–2 seconds. The entire Copilot response then disappears. Instead, the following message is displayed: “Due to your organization’s policies, none of the requested files or resources are available.” The previously generated response, which was briefly visible, can no longer be accessed afterwards. Expected behavior Since I would like to use “Performing web searches → Block” in the DLP policy, I would expect that: the web search is blocked, sensitive information is not used for the web search, Copilot can still process the prompt, and the response generated by Copilot remains visible. Question Is this behavior expected when using the DLP action “Performing web searches → Block”? In particular, I would like to understand why Copilot initially generates and displays a response without using the sensitive information for the web search, but then completely removes this response a few seconds later and replaces it with the policy notification. Is it possible to configure additional actions in the DLP policy, or to select an option other than “Block”? I only have the two actions mentioned above available. I have attached the relevant screenshots. Please note that the attached screenshots are in German. Thank you in advance!353Views1like4CommentsMeet the New Microsoft Purview Classifiers Experience: Your Admin Playbook for Public Preview
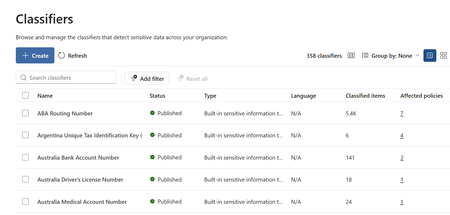
Microsoft Purview Unified Classification Management Experience Feature overview and administrator playbook Overview The new Classifiers experience brings supported Microsoft Purview classification types into one place where administrators can discover, create, inspect, and manage classifiers. It adds practical visibility into classified-item counts and policy dependencies so administrators can make more informed, lower-risk changes. Why this experience is important Classification underpins data protection, data loss prevention, and data security. As classifier inventories grow, administrators need a consistent way to understand what exists, where it is used, and what could be affected by a change. Centralized visibility Search and filter supported classifiers from a unified inventory instead of navigating separate management locations. Safer change decisions Review classified-item counts and affected policies before editing or deleting a classifier. Stronger governance Establish clear ownership, testing, approval, validation, and review expectations. Better coverage analysis Use matched-item information and Data Explorer to understand where classifications occur and where gaps may exist. What administrators can do Discover supported classifier types and understand what the organization already uses. Create classifiers from a single entry point with type-specific preparation guidance. Review classified-item counts and inspect policies that depend on a classifier. Validate matched items across supported data sources and investigate unexpected coverage. Access Classifiers through Information Protection, Data Loss Prevention, or Data Security Posture Management, depending on tenant availability. Supported classification capabilities include sensitive information types, named entities, Exact Data Match, trainable classifiers, credentials, document fingerprinting, optical character recognition, and on-demand classification. How the experience can help Reduce context switching: Use one inventory to find and inspect supported classifiers. Understand impact earlier: Identify policy dependencies before a change reaches enforcement. Improve accountability: Connect classifiers to business owners, policy owners, and reviewers. Standardize operations: Apply the same lifecycle to routine maintenance, quality improvements, and retirement decisions. How the admin playbook helps The companion playbook turns the preview into a practical operating guide. It is designed to be the first place an administrator goes to understand the value of the experience and apply it safely. Explains the administrator value of unified classifier management. Provides a continuous Inventory Offers a decision guide for selecting an appropriate classification method. Shows how to review policy impact and validate matched items. Includes customer scenarios and answers to common licensing, permissions, and coexistence questions. INVENTORY → ASSESS → TEST → APPROVE → CHANGE → VALIDATE → REVIEW Resources Public documentation Current availability, permissions, supported classification capabilities, and product guidance. Administrator playbook A self-contained, interactive guide with workflows, screenshots, scenarios, and FAQs.2.2KViews2likes0CommentsMicrosoft Purview | Share block at external users
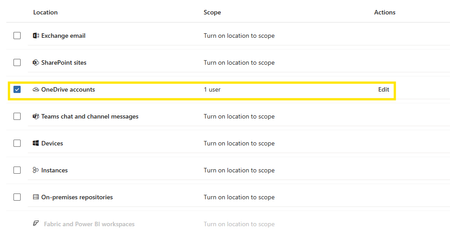
Hello community. I have an issue with Microsoft Purview DLP policies. I am trying to create a policy that prevents documents from being shared through OneDrive with external users, while allowing certain exceptions. However, when I select the option "Block Access to external domains and users" and assign a specific email address to be blocked, it does not work. The configured email address is not being blocked. I was reviewing this with Copilot, and it mentioned that if the external user you are sharing with already exists in Entra ID, the tenant may treat the user differently (not necessarily as an external user). My external user exists in Entra ID as a Guest account. The external user is registered as follows: Displayname: User Name Userprincipalname: user.name_external.domain#EXT#@company.onmicrosoft.com User Type: Guest Has anyone else experienced this issue? I am sharing evidence of the policy configuration.1.3KViews0likes7CommentsClose the gaps: layered data protection with Microsoft Purview across endpoint, browser, and network
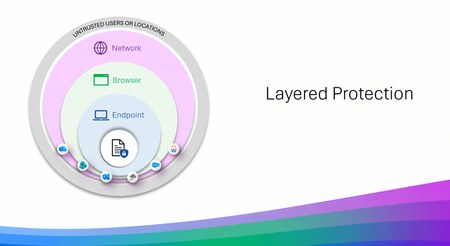
Three layers that work like a good team and slides to show it Data Loss Prevention (DLP) is not new, many use it daily without ever even knowing it, but with AI bringing faster results for productivity so does the risk of data leakage. That is where we take a layered approach, meeting the end user exactly where they are working, on a device, or in a browser, or through that cute cat Office add-in that had to be installed. But don't think of layered protection as three products but more as three specialists who are each excellent at their own job and have the good sense not to try doing everyone else's. Endpoint DLP lives on the device. USB and removable media, clipboard, print, restricted apps. It carries the deepest classification support, EDM, fingerprinting, OCR, and it works offline, which turns out to be more useful than it sounds at 30,000 feet. Browser Data Security lives in the session, inline in Edge for Business, checking content before an upload or a form submission. It is the most precise layer for AI prompts and for activity happening inside a managed web app, where nothing else is standing close enough to help. Network Data Security lives on the wire, via Entra Global Secure Access or a third-party SASE. It handles traffic that never touches a browser at all, desktop apps, Office add-ins quietly phoning a friend, and it is the layer that supports inbound classification of content coming back from cloud and AI apps. Each one has natural technical boundaries, and those are a design decision rather than an oversight. A network proxy is never going to have strong opinions about a USB stick. An endpoint agent is not positioned to unwrap an encrypted API call from a third-party add-in. Ask any one of them to cover all three domains and you would end up with something slower and less capable at each. Deployed together, though, the edges line up rather nicely. That is the entire premise of layered protection, and it is what I built this asset to show. What is actually in the slides A coverage view across all three layers. Common activities — removable media, RDP sessions, add-in API calls, in-session copy and paste, inbound AI content, classification depth, inline prompt inspection — matched to the layer best positioned for each. Six scenario walkthroughs. Realistic situations traced attempt by attempt, including one determined individual who tries three separate routes to get the same file to a consumer AI service. A departing employee and a USB drive. A contractor on a personal laptop. Files headed to personal cloud storage. Each shows which layer engages, and why. Deployment flows you can follow. Prerequisites, permissions, policy names, conditions, actions. Both browser patterns (managed device with unmanaged apps, unmanaged device with managed apps) and both network paths (Entra GSA, and third-party SASE including Netskope and iBoss). Four reference architectures. Traffic flow diagrams for each browser and network model — what gets evaluated, where the Purview verdict comes from, where enforcement lands. Collection policies explained thoroughly. The unsung plumbing underneath all of it. Anatomy, the full flow from event source to Activity Explorer, Insider Risk Management, eDiscovery, and Data Security Posture Management (DSPM), plus the operational details that are much nicer to learn about in a deck than in production. The parts people keep coming back to The coverage view is usually where planning conversations start. It gives everyone a shared picture of what is deployed today and what a sensible next step looks like; adding the browser layer to an existing Endpoint DLP footprint, say, or bringing in the network layer to extend coverage to add-ins and desktop apps. The scenario walkthroughs are where it tends to click for a wider audience. Following one situation through several routes and watching a different layer step in at each turn, does more for the story than any static diagram I have drawn. And the deployment flows are genuinely meant to be executed. Everyone is written to run against a pilot group first, with Conditional Access in report-only mode in production until you have confirmed the behavior. Please do that part. Your future self will appreciate it. Who it is for Architects scoping a deployment. Partners running workshops. Admins with Endpoint DLP already humming along who are working out what comes next. Anyone who would like a single starting point instead of a browser window that has stopped showing page titles. Take whatever is useful. Pull individual slides into your own narrative or run the whole thing end to end it was built to be borrowed. Things to keep in mind Several capabilities in here are in preview or Pay-As-You-Go backed, and network-layer coverage depends on supported SASE/SSE integrations and how traffic is routed. The deck flags this as it goes. Check current availability on Microsoft Learn, and with your SASE provider for the network layer. Now the fun The full slide set is at https://aka.ms/purviewlayeredprotection. It is a living reference, and it will keep evolving with the product. If it helps you plan something, or if there is a scenario you would like to see in the next version, I would love to hear about it.2.2KViews5likes0Comments