azure
81 Topics
Enhanced data protection for Azure Files
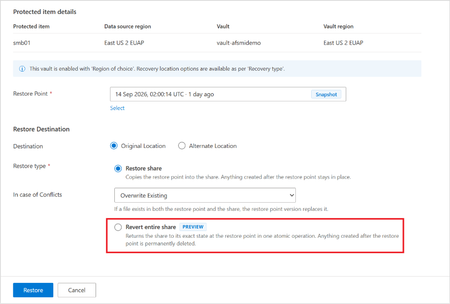
Organizations rely on Azure Files for business-critical workloads such as VDI, SAP, and general-purpose file shares that hold their enterprise data. For these workloads, backup and disaster recovery are day-one requirements. Customers need a simple, scalable way to recover from an accidental change to production data, a regional disruption or a ransomware attack, both within a region and across regions. Today, we’re announcing new capabilities, in Public Preview, that expand business continuity and disaster recovery (BCDR) capabilities for Azure Files. They help customers recover from operational issues, strengthen regional resilience and protect critical file data from cyber threats: Vaulted backup for NFS shares: Protect NFS file shares with isolated recovery points through Azure Backup for protected, trusted recovery from cyber incidents. Revert snapshot: Roll an existing file share back to a known-good point in time, in place, without changing the endpoint or mount path for fast. This gives you fast recovery from operational issues. Azure Files-to-Azure Files copy and sync with Storage Mover: Use Azure Storage Mover to maintain a secondary copy of your SMB file share data in the Azure region of your choice, with scheduled incremental transfers to keep it current for disaster recovery. Together, these capabilities let customers build Azure Files resiliency in layers: roll back quickly, maintain secondary copies and recover from protected backups. Vaulted backup for Azure Files NFS shares Cyber recovery introduces another dimension to resiliency: When ransomware or another security incident compromises the production environment, organizations need protected recovery points and may need to validate recovered data before reconnecting it to production. Azure Files already supports vaulted backup for SMB shares. With this preview, that protection extends to NFS shares. Vaulted backup for Azure Files NFS shares adds an additional protection layer through Azure Backup. Recovery points are maintained separately from the production file share and managed through backup policies designed to support long-term retention, immutability, and cyber recovery objectives. Vaulted backup helps customers protect critical file data when: Recovery points need protection separate from production: Maintain protected recovery points separately from the production file share, adding another layer of protection for critical file data. Backup strategies require immutability: Support immutable backup strategies as part of the broader approach to protecting recovery points and meeting cyber recovery objectives. Data must be retained long term: Manage recovery points through backup policies designed to support long-term retention and meet the organization’s retention requirements. Ransomware resilience is a priority: Strengthen resilience with protected recovery points for recovery when ransomware or another security incident compromises the production environment. To participate in the Vaulted backup for NFS shares preview, sign up here. Roll back quickly with Revert snapshot Operational mistakes are among the most common reasons applications need data recovery. A deployment can modify the wrong files, a configuration rollout can affect an entire namespace, or an administrator can accidentally overwrite critical content. Azure Files Revert Snapshot initially provides in-place recovery for data and applications hosted on SMB file shares, with NFS support coming next. Customers can select a point-in-time snapshot and restore the existing file share to that state while applications continue using the same file share, endpoint, and mount path. Common scenarios include: Failed application deployments: Roll back after a deployment modifies the wrong files. Incorrect configuration changes: Restore the share after a configuration rollout affects the namespace. Accidental mass modifications: Return to a point-in-time snapshot after unintended changes or overwrites. Development and test environment resets: Reset the file share to a selected snapshot. Azure Backup offers an integrated experience in the Azure portal restore blade to revert snapshots it manages. To participate in the Revert Snapshot preview, sign up here. Azure Files-to-Azure Files copy and sync with Storage Mover From disaster readiness and regional expansion to workload relocation and storage consolidation, customers need a simple, scalable way to copy and sync file data across storage accounts and Azure regions. Common use cases include Virtual Desktop Infrastructure (VDI) users maintaining secondary copies of FSLogix profiles and user data to support regional continuity, SAP and enterprise applications moving application data during regional expansion, organizations consolidating distributed content to simplify administration, and AI workflows placing datasets closer to AI and analytics compute to support distributed development and processing. Azure Files-to-Azure Files copy and synchronization with Azure Storage Mover gives customers a fully managed Azure service to copy data between SMB file shares across storage accounts, regions, and subscriptions (within the same tenant). They can also schedule incremental transfers to keep destination shares up to date. Customers can: Maintain secondary copies for business-critical workloads to an Azure region of choice. Schedule incremental synchronization of application data, user profiles, and shared content to another Azure region, helping organizations strengthen business-continuity and recovery planning. Copy or migrate file share data between regions: Copy data for regional expansion, datacenter transitions, or workload relocation. Consolidate file shares: Bring data together across storage accounts and regions to simplify management. Operate at scale with less overhead: Centrally schedule, monitor, and audit transfers instead of maintaining scripts or copy infrastructure. Azure Storage Mover reduces operational overhead with centralized scheduling, monitoring, auditing, metadata preservation, and orchestration for recurring file transfers. Figure: Storage Mover (West Central US) copies File share 1 in East US to File share 2 in West Central US. Preview support for Azure Files to Azure Files data copy is now available for SMB shares, with NFS support coming soon. To participate in the preview program, sign up here. Together, these capabilities help customers protect critical file data, recover quickly from operational issues and strengthen continuity across regions. Vaulted backup for NFS shares, Revert Snapshot and Azure Files copy and synchronization with Storage Mover provide complementary layers for a more resilient BCDR strategy. Learn more About Azure Files backup - Azure Backup | Microsoft Learn Use Azure Files Share Snapshots | Microsoft Learn Get started with Azure Files-to-Azure Files data copy in Azure Storage Mover (preview) | Microsoft Learn For questions or feedback, please reach out to the team at azurefiles@microsoft.com.238Views0likes1Comment
Discover and assess on-premises Network Attached Storage (NAS) shares using Azure Migrate
Network-attached storage (NAS) holds much of an enterprise’s data; home directories, project shares, media libraries, application data, and analytics datasets, often spanning tens or hundreds of terabytes across protocols and administrative boundaries. Moving this estate to Azure starts not with copying data, but with understanding what you have, where each share should go, and what it will cost. Building on the file share assessment capability we announced in May, today we’re announcing the public preview of NAS share discovery and assessment in Azure Migrate. It connects directly to Dell PowerScale/Isilon and NetApp ONTAP clusters, inventories every SMB, NFS, and S3 share, and assesses each against Azure Files, Azure Blob Storage, and Azure NetApp Files—providing readiness, right-sized configurations, cost estimates, and migration tooling guidance. Your NAS assets now join servers, applications, and databases in the same Azure Migrate project, inventory, and business case. Why does this matter NAS planning has historically been done with spreadsheets, vendor-specific tools, and a lot of manual reconciliation. Storage ends up being assessed separately from the servers and applications that depend on it, which makes it hard to sequence a migration or defend a budget. This capability is designed to help you: Replace manual inventory with automated discoveries across Dell and NetApp platforms, so you can go from "we think we have a few thousand shares" to a verified, per-share inventory. Effectively plan your NAS shares alongside everything else. NAS clusters and their shares appear in the same Azure Migrate inventory as your VMware, Hyper-V, and physical servers, databases, and web apps. Make your informed decision before you migrate. Each share gets a readiness verdict, a recommended Azure service and SKU, and a monthly cost estimate. What's available in public preview Add Dell or NetApp NAS clusters: Discover Dell PowerScale / Isilon (OneFS) and NetApp ONTAP AFF / FAS clusters, and inventory every SMB, NFS, and S3 shares they host — including shares exposed through more than one protocol. Explore and review on-prem shares and workloads: Review cluster and share details in the portal: model, nodes, total and used capacity, protocol versions, volume, and estimated size. Group and filter shares by tag — by business unit, cost center, or application — so related workloads can be planned together. Suitable Azure storage targets: Assess each share against Azure Files, Azure Blob Storage, and Azure NetApp Files, with control over target region, sizing criteria, comfort factor, redundancy, media type, access frequency, and workload type. Alternative migration paths: Compare various migration paths side by side — a recommended mixed path that sends each share to its best-fit service, alongside single-service alternatives — with readiness, monthly cost, and estimated emissions for each. Business case: Build a business case for a NAS-only estate or for a mixed estate of VMs and NAS, comparing a modernization approach against lift-and-shift. End-to-end experience The experience follows the same guided workflow you already know from Azure Migrate. 1. Enable the feature Install the latest Azure Migrate appliance or turn on auto-update, so your existing appliance picks up the new capability. Unlike file shares hosted on Windows and Linux servers, NAS clusters need to be added explicitly: in the appliance configuration manager, add a credential of source type NAS Server, then add a discovery source of type NAS Server with your cluster's FQDN and port. The account needs read-only permission at cluster level — Azure Migrate only reads metadata and never writes to your storage. 2. Discover your NAS estate Create an Azure Migrate project, deploy the appliance on VMware, Hyper-V, or a physical server, and point it at your clusters. The appliance connects to each cluster's management endpoint and collects system and share metadata, vendor, product and model, operating system version, cluster nodes, total and used capacity, share and bucket paths, protocols and protocol versions; followed by performance signals such as IOPS and throughput. Discovered clusters and their shares appear as first-class inventory objects, listed alongside the Windows and Linux file servers the appliance already finds. Filter by type, search, tag, and export the inventory at whatever scale your estate demands. Discovery runs a daily cycle and updates existing items as new metadata arrives, so the picture improves over time rather than being a one-shot snapshot. 3. Create an assessment Select the shares you care about — individually, by tag, or a whole cluster at a time — and create an assessment. The share is the unit of assessment, so every SMB, NFS, or S3 share receives its own verdict rather than inheriting one from its host. Assessment settings let you shape the recommendation to your environment: choose the target Azure region, pick as-is or performance-based sizing, set a comfort factor for headroom, and configure redundancy, Azure Files media preferences, and Azure Blob access frequency. A workload type setting from general purpose file shares through to AI/ML and mission-critical, helps Azure Migrate recommend an appropriate performance level. Azure NetApp Files is added to the evaluation automatically when the source share is detected on NetApp NAS. Settings can be changed, and the assessment recalculated at any time. 4. Review results and build the business case Results are organized as migration paths. The recommended path routes each share to its best-fit Azure service and is shown next to single-service alternatives, so you can compare readiness and cost on the same basis. Key insights include: Readiness for every share — Ready, Ready with conditions, or Not ready — with the warnings that need attention before you move. A recommended Azure configuration per share. For example, a multi-protocol NetApp volume is recommended for Azure NetApp Files, while a general-purpose SMB share is recommended for Azure Files with a specific media type and redundancy. Provisioned size, IOPS, and throughput behind the recommendation, plus the reasoning Azure Migrate used to select the SKU and access tier. Monthly cost estimates per share and per path, an on-premises versus Azure TCO comparison, and estimated carbon savings. Next, you can generate a wave plan to sequence the migration or build a business case that helps you with cost modernizing Azure storage services. Assessment results showing the recommended path, source-to-target mappings, estimated Azure TCO, and carbon savings. Note: All screenshots in this post are from a sample environment. Cluster and share names, capacity values, readiness distributions, cost and TCO estimates, and emissions figures are illustrative and shown for reference and indicative purposes only. They are not a price quote. Your own results depend on your discovered environment, the assessment settings you choose, your target Azure region, and the pricing and offers that apply to your subscription. Prepare for migration with the right tool Assessment tells you where each share should go; Azure Migrate then points you at the tool to get it there. Azure Storage Mover is the recommended path for moving shares to Azure Files and Azure Blob Storage. For ONTAP volumes heading to Azure NetApp Files, the Azure NetApp Files migration assistant is recommended, and Azure File Sync remains the option for active sync and hybrid scenarios with Windows file servers. To learn more about our recommendations for unstructured data migration, visit https://aka.ms/migratemydata. Get started Update your Azure Migrate appliance, add your first NAS cluster, and let a discovery cycle run. Within a few hours you'll start to see a per-share picture of your NAS estate; you can then create an assessment to view the right target service to migrate to Azure. Learn more in our documentation. Connect and discover your NAS appliance Review discovered NAS resources Create a fileshare assessment of NAS shares Review NAS File share assessment recommendations Write to us at azurestoragemigrations@microsoft.com with questions or feedback, or to suggest additional NAS systems you’d like this capability to support. We look forward to hearing from you!217Views0likes0CommentsAzure Storage Discovery now offers advanced capacity insights
Azure Storage Discovery is introducing advanced capacity insights to help customers gain deeper visibility into their data estate, identify inactive or inefficiently stored data, understand storage composition and retention considerations, and pinpoint resources for further investigation and optimization.711Views0likes1Comment
TLS 1.0 and 1.1 support will be removed for new & existing Azure storage accounts starting Feb 2026
Update on October 13, 2026: Starting on October 14, 2026, changes will start rolling out to block existing storage accounts from downgrading their minimum TLS version to 1.0 or 1.1. Update in September 2025: This post was edited to reflect the retirement date change from November 1, 2025 to February 3, 2026. To meet evolving technology and regulatory needs and align with security best practices, we are removing support for Transport Layer Security (TLS) 1.0 and 1.1 for both existing and new storage accounts in all clouds. TLS 1.2 will be the minimum supported TLS version for Azure Storage starting February 3, 2026. Azure Storage currently supports TLS 1.0 and 1.1 (for backward compatibility) and TLS 1.2 on public HTTPS endpoints. TLS 1.2 is more secure and faster than older TLS versions. TLS 1.0 and 1.1 do not support modern cryptographic algorithms and cipher suites. Many of the Azure storage customers are already using TLS 1.2 and we are sharing this guidance to expedite the transition for customers currently on TLS 1.0 and 1.1. Customers must secure their infrastructure by using TLS 1.2+ with Azure Storage by February 2, 2026. The older TLS versions (1.0 and 1.1) are being deprecated and removed to meet evolving standards (FedRAMP, NIST), and provide improved security for our customers. This change will impact both existing and new storage accounts using TLS 1.0 and 1.1. To avoid disruptions to your applications connecting to Azure Storage, you must migrate to TLS 1.2 and remove dependencies on TLS version 1.0 and 1.1, by February 2, 2026. Learn more about how to migrate to TLS1.2. As best practice, we also recommend using Azure policy to enforce a minimum TLS version. Learn more here about how to enforce a minimum TLS version for all incoming requests. If you already use Azure Policy to enforce TLS version, minimum supported version after this change rolls out will be TLS 1.2. Help and Support If you have questions, get answers from community experts in Microsoft Q&A. If you have a support plan and you need technical help, create a support request: For Issue type, select Technical. For Subscription, select your subscription. For Service, select My services. For Service type, select Blob Storage. For Resource, select the Azure resource you are creating a support request for. For Summary, type a description of your issue. For Problem type, select Connectivity For Problem subtype, select Issues using TLS.125KViews3likes5CommentsMore EDA Job Sets per Volume: Azure NetApp Files Raises the Performance Bar
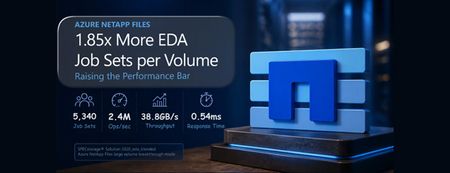
Azure NetApp Files raises the performance ceiling for cloud-based electronic design automation (EDA) with a new independently published SPECstorage® Solution 2020 EDA_BLENDED result for a single large volume in breakthrough mode: 5,340 job sets, 2.4 million operations per second, 38,776 MB/s peak throughput, and 0.54 ms overall response time. Delivering 1.85 times the job sets, operations, and throughput of the previous single-volume result while preserving sub-millisecond latency through most load points, the result enables more concurrent simulations, shorter regression cycles, and better utilization of compute and tool licenses without dataset sharding. Combined with proven linear scale-out and generally available Azure NetApp Files cache volumes that provide on-demand access to on-premises data, it gives EDA teams a practical foundation for high-performance cloud deployment and bursting.333Views0likes0CommentsBoost performance with NFS nconnect on Azure NetApp Files datastores for Azure VMware Solution
Azure VMware Solution now supports nconnect=4 with Azure NetApp Files datastores each ESXi host opens up to four parallel TCP connections to a single NFS datastore, raising throughput and lowering latency under load. Supported on both Gen 1 and Gen 2 private clouds, it makes Azure VMware Solution with Azure NetApp Files an even stronger home for databases and other storage‑intensive workloads.555Views0likes0CommentsEnterprise Identity Meets Secure File Transfer: Entra ID Public Preview on Azure Blob Storage SFTP
Updated on June 23 2026: Microsoft Entra ID-based access for Azure Blob Storage SFTP is now Generally Available. GA enhancements: Improved ABAC by resolving inconsistencies with the Storage Blob Data Owner role (eliminating timeout issues) while adding support for sub-operations to enable more granular access control. Learn more here. We are excited to announce the public preview of Entra ID-based access for Azure Blob Storage SFTP. This new capability enables you to use Microsoft Entra ID (formerly Azure Active Directory) identities (including guest users via Entra External Identities) to securely connect to Azure Blob Storage via SFTP without needing local users. This feature eliminates the operational overhead of managing local SFTP users and passwords by introducing enterprise-grade identity management powered by Microsoft Entra ID. For IT administrators and security teams, this means no more creating, tracking, rotating, or decommissioning local SFTP credentials. For developers and architects, it means seamless integration with your existing identity infrastructure. For business users, it means faster, more secure access to the data they need, all while maintaining compliance with enterprise security policies. Azure Blob Storage SFTP Azure Blob Storage SFTP natively enables secure file access and management without third-party solutions. This simplifies operations for customers and removes the need for complex, custom SFTP solutions. Until this Public Preview, Azure Blob Storage SFTP utilized a form of identity management called local users as the only authorization mechanism. Local users must use either a password or a Secure Shell (SSH) private key credential for authentication. Learn more about local users here. The Challenge: SFTP Local User Management Organizations currently face challenges when managing SFTP access at scale with Azure Storage SFTP Local Users. Local User based SFTP access require IT teams to: Manually create and provision local user accounts for each SFTP user Generate, distribute, and securely store SSH keys or passwords Implement custom workflows for lifecycle management Manage offboarding processes to ensure departed users lose access immediately Audit and track access across disconnected identity silos Handle external partner and vendor access through ad-hoc, often insecure methods The Solution: Enterprise Identity Meets Secure File Transfer With Entra ID-based access for Azure Blob Storage SFTP, you can now leverage your organization's centralized identity platform to authenticate and authorize SFTP users. This integration brings the full power of Microsoft Entra ID to your file transfer workflows, delivering the following benefits: 1. Eliminate Local User Management Simplify SFTP management by assigning access with Entra ID—no separate SFTP accounts needed. No local credential generation or distribution—users authenticate with their existing corporate credentials No orphaned accounts when users change roles or leave the organization Reduced attack surface by eliminating static, long-lived local credentials Centralized user lifecycle management through your existing identity platform 2. Enterprise-Grade Identity and Security Leverage the full security capabilities of Microsoft Entra ID for your SFTP infrastructure: Multi-Factor Authentication (MFA): Require additional verification factors beyond passwords, significantly reducing the risk of account compromise Conditional Access: Define policies that grant or block access based on user location, device compliance, sign-in risk, and other conditions Identity Protection: Benefit from Microsoft threat intelligence and risk detection to identify and respond to compromised accounts Privileged Identity Management (PIM): Provide just-in-time elevated access for administrative operations 3. Native Azure RBAC, ABAC, and ACL Integration Your SFTP access control seamlessly integrates with Azure comprehensive authorization framework: Role-Based Access Control (RBAC): Assign built-in or custom roles at the storage account, container, or even blob level Attribute-Based Access Control (ABAC): Create sophisticated access policies based on resource tags, user attributes, and environmental conditions Access Control Lists (ACLs): Apply fine-grained permissions at the directory and file level for hierarchical namespace-enabled accounts Unified Permission Model: SFTP access respects the same permissions as REST API, Azure CLI, and other access methods—no separate permission system to manage 4. Faster SFTP Onboarding and Time-to-Value Onboard new SFTP users or partners in minutes instead of hours or days, saving significant time and boosting business agility. 5. Secure External Collaboration with Entra External Identities Seamlessly enable secure external SFTP access by allowing partners to authenticate with their own credentials using Entra External Identities (Azure AD B2B). External users authenticate with credentials they already manage Full audit trail of external user activity Ability to apply Conditional Access policies to external users Automatic access revocation when B2B relationships end Real World Scenarios Financial Services: A bank receives daily transaction files from merchants via SFTP. Merchants authenticate with their own Entra ID credentials (B2B collaboration), MFA is enforced, and access is restricted to assigned directories. Access is instantly revoked when a merchant is removed from the B2B directory. Healthcare: A hospital exchanges patient data with insurers and labs. Entra ID authentication ensures only authorized staff access sensitive PII, with full audit logs for HIPAA compliance. Conditional Access restricts connections to approved locations and devices. Media & Entertainment: A production company enables freelance editors and agencies to transfer large media files. Entra External Identities provide time-limited access and automatic revocation when projects end—no need for local SFTP accounts. Manufacturing: A manufacturer receives CAD files and orders from suppliers using SFTP. With Entra ID, suppliers use unified credentials and access policies across all systems, streamlining supply chain management. How It Works Entra ID simplifies SFTP access to Azure Blob Storage by authenticating users with their corporate credentials. After authentication, users receive a short-lived Open SSH certificate to connect. The service verifies certificate validity and user permissions, enabling secure file operations and automatic access revocation in line with current identity policies. Learn more here. Getting started with the Public Preview We encourage you to try Entra ID-based access for Azure Blob Storage SFTP in your non-production environments today. Learn more about how to register for the preview and get started with the detailed ms docs learn guide here. This preview gives you an opportunity to shape the feature development by providing feedback on what works well and what could be improved. Note: Local user accounts for SFTP access are still supported, but we strongly recommend switching to Entra ID-based access for greater security, simpler management, and automatic access control. Questions or feedback? We would love to hear from you! Reach out to our team at blobsftp@microsoft.com We are excited to bring enterprise-grade identity management to Azure Blob Storage SFTP, and we cannot wait to see how you use this capability to simplify operations, enhance security, and enable new collaboration scenarios. Happy transferring!2.3KViews0likes0CommentsBringing Enterprise File Data to Users with Azure NetApp Files, Microsoft Foundry, and M365 Copilot
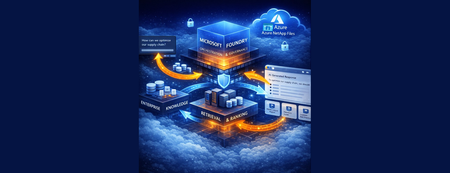
This is Part 3 of a 3-part series on extending AI to enterprise file data, showing how the knowledge pipeline is surfaced through enterprise AI agents and user experiences including Microsoft 365 Copilot.687Views0likes0CommentsFrom Enterprise File Storage to an AI-Ready Data Foundation using Azure NetApp Files and OneLake
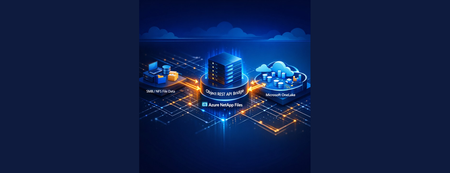
This 3-part series shows how to extend AI to enterprise file data – without migration – by combining Azure NetApp Files, OneLake, and a RAG-based architecture that surfaces grounded insights through enterprise AI agents. This is Part 1 of a 3-part series covering the data foundation, knowledge pipeline, and user experience layers.691Views0likes0Comments