azure ad
555 TopicsMicrosoft to Stop Providing Telephony-Based Authentication Methods for MFA in February 2027
In an important announcement for all tenants, Microsoft revealed that Entra ID will no longer provide SMS one-time codes or voice calls for MFA challenges after February 1, 2027. Tenants can continue to use telephony-based authentication methods after that date, but only by purchasing a service from a telecom provider. This is arguably the biggest change in Entra ID authentication since mandatory MFA for administrative interfaces – and we have a PowerShell script to help identify the affected accounts. https://office365itpros.com/2026/07/14/entra-sms-one-time-code/4.2KViews0likes3CommentsWhy Entra Administrators Cannot Disable Their Own Accounts
When attempting to disable a user account in an interactive Graph session, I was told that the command failed because the accountEnabled property was invalid. The error is obviously incorrect because it’s very possible to update the property to disable or enable an account. However, different rules apply when the account is holds a privileged role, like Global Administrator. Entra imposes some reasonable blocks, even if the error messages are not good. https://office365itpros.com/2026/09/14/strange-accountenabled-error/72Views1like1Comment
Partner Entra lockout for more than 2 months
Sole Global Administrator Locked Out (60+ Days) Following MAICPP Partner Launch Benefits Activation — Case #2607300040011056 Hello Microsoft Partner Community and Microsoft Community Managers, I been a partner for several decades, previously a higher capacity MAICPP I am posting from my active Developer account because my primary organization tenant has been completely locked out for over two months.. MAICPP Partner Launch Benefits Activation The activation of Entra subscription failed and a delay in partner tech support resulting in an administrative lockout across our tenant spnode.io The Issue & Support Bottleneck Attempts to authenticate or initiate self-service password recovery result in an explicit account lockout message The ticket has stalled across various support queues for over two months Initially routed to Microsoft Defender for Cloud Apps, where engineers confirmed it was outside their scope Re-routed toward the Azure / M365 Data Protection queue A communication delay occurred when I temporarily lost phone access and was in the hospital. I require intervention from a Community Manager or Partner Operations Escalation Lead to help route this stalled case directly to an active Duty Manager in the Partner Support for immediate identity verification Direct Callback Phone: 628-309-6705 Thank you for your assistance in restoring access to our partner tenant.Entra ID Continuous Access Evaluation and Microsoft 365
Continuous Access Evaluation (CAE) is supported by core Microsoft 365 workloads like Exchange Online, SharePoint Online, and Teams, and the reach of CAE is gradually spreading throughout the Microsoft cloud ecosystem. However, security researchers report inconsistent coverage across first-party apps and clients that take a little gloss off the promise of instant access revocation when critical events like user password changes happen. https://office365itpros.com/2026/09/08/continuous-access-evaluation-cae/141Views0likes1CommentRevoking Access Tokens for Risky Service Principals
A Technical Community post discusses the topic of using the Entra ID continuous access evaluation (CAE) feature to revoke access for service principals when apps become risky or potentially compromised. The Microsoft Graph Command Line Tools app is a good example of a service principal in common use, so we examine the access tokens issued for interactive Graph sessions to discover if they are CAE-enabled. Just for fun! https://office365itpros.com/2026/09/03/cae-service-principals/79Views0likes0Comments
How much of your Microsoft 365 environment can you actually see at once?
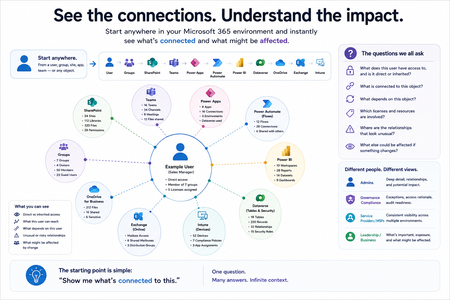
Not how many users you have. Not how many sites, teams, apps or flows you have. How much of it can you actually see connected together? I've been working across Microsoft 365 environments for a while, and I kept running into the same thing. There is no shortage of information. If anything, there is probably too much of it. Users, groups, permissions, SharePoint, Teams, Power Apps, Power Automate, Power BI, Dataverse, OneDrive, Exchange, Intune, licensing, configuration... It's all there. But when you're actually trying to understand how everything fits together, it can be a different story. You open one blade. Find something. Open another. Cross-check it. Go back. Open something else. Before long, you're jumping between different parts of the tenant trying to build the bigger picture in your head. And if you're working with larger environments, that gets difficult pretty quickly. The information isn't necessarily missing. The relationships between the information are what can be difficult to see. That got me thinking about a slightly different question: Instead of "where do I find this information?" "Show me what's connected to this." That's where VisibleState started. Start anywhere. Follow the connections. Imagine starting with a single user. Instead of seeing that user simply as a record with a list of properties, imagine being able to explore the relationships around them: User → Groups → SharePoint → Teams → Power Apps → Power Automate → Power BI → Dataverse → OneDrive → Exchange → Intune Then the questions become different: What does this user have access to? Is that access direct or coming through a group? What resources are connected to them? What depends on something they're associated with? Which licenses are involved? Are there relationships that look unusual? If something changes, what else might be affected? Those questions aren't necessarily about finding another piece of information. They're about putting information that already exists into context. A report can tell you that something exists. A connected view helps you understand what it is connected to. Illustrative example below — not a real customer environment. I'm not suggesting Microsoft 365 doesn't already give us this information Quite the opposite. Microsoft 365 already gives administrators an incredible amount of information and tooling. The thing I've been thinking about is what happens when you want to look across those boundaries. Sometimes I don't want another export. I don't want another list. I don't necessarily want another dashboard. I want to start with something I'm looking at and ask: "What's connected to this?" And then keep following the trail. That's the idea I'm exploring with VisibleState. The interesting part is what happens when you change the viewpoint The same relationships can be useful for completely different reasons. For example: Administrators may want to understand access, permissions and dependencies. Security and governance teams may want to find unusual relationships or exceptions. Compliance teams may need to understand who can access something and why. People managing multiple environments may want a consistent way to understand what's there without rebuilding the picture manually every time. Leadership may not need to see the graph at all. They may simply want to know what's important, what's exposed and what could be affected. It's still the same underlying environment. You're just looking at it from a different angle. And that's where I think things get interesting. Where I'm at with it VisibleState started as something I was building to make my own work easier. I was spending a lot of time investigating environments, tracing access and putting information together for reports. The individual tasks weren't necessarily difficult. It was the jumping between different places and reconstructing the bigger picture that took the time. So I started building something that would let me approach the environment through the relationships instead. It's grown quite a bit from where it started, and I'm continuing to build it. I'm not posting this as a product launch, and I'm not looking for people to sign up. I'm genuinely interested in whether the problem I'm seeing is familiar to other people working with Microsoft 365. So I'm curious... If you could start with any object in your Microsoft 365 environment and immediately see what it's connected to, where would you start? Would it be: Users and access Groups and permissions SharePoint and Teams Power Apps, Power Automate, Power BI and Dataverse Licensing and resources Governance and unusual relationships Something completely different Maybe you've already got a good way of doing this. Maybe you still find yourself jumping between different services and piecing things together manually. Or maybe I'm looking at the problem from the wrong direction. What's the one relationship in your Microsoft 365 environment that you wish you could see instantly?160Views0likes0CommentsRunning a Regular Check for New Graph Permissions
Use PowerShell to Check for New Graph Permissions with a View to Updating Permissions Used by Apps. After Microsoft released some new Graph permissions, thoughts turned to how to discover new permissions after they are released. Code is the best way to perform automatic checks, and this article explains how to use PowerShell to check a last known set (stored in SharePoint Online) against the current set. Any variations are reported to administrators via email. https://office365itpros.com/2026/08/31/new-graph-permissions-check/84Views0likes0CommentsCalculating the Licensing Requirement for Entra Conditional Access Policies
After the discussion about the licensing gap prompts shown in the Entra admin center, here’s a PowerShell script to compute the set of user accounts that should have Entra P1 licenses. The information comes from the conditions property of conditional access policies with group and directory role membership expanded to find individual accounts. The set is checked against the set of users licensed for Entra P1 to find the accounts that need to be licensed. https://office365itpros.com/2026/08/18/find-entra-p1-accounts-to-license/99Views0likes0CommentsEntra Admin Center Flags Licensing Problems with Conditional Access
The Entra admin center is flagging licensing gaps for conditional access. The messages are informational, not the beginning of a new automated billing procedure to charge tenants when Entra ID notices that some accounts use conditional access policies when they don’t have a license. In this article, we discuss the product license insight and how Microsoft measures conditional access usage, and show how to use PowerShell to find who’s using conditional access. https://office365itpros.com/2026/08/13/licensing-gaps-entra-id/293Views0likes0CommentsEmpower Your Cloud Identity: How to Convert User SOA from AD to Entra ID
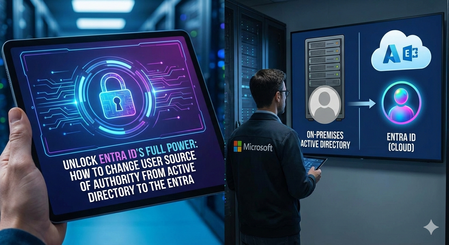
For years, hybrid identity has been the standard. We synchronize users from on-premises Active Directory (AD) to Microsoft Entra ID (formerly Azure AD), giving our people one set of credentials for both cloud and local resources. But this setup comes with a hidden limitation: Active Directory remains the Source of Authority (SOA). This traditional model limits your ability to leverage modern security, governance, and management tools available in the cloud. The good news? Microsoft has introduced the capability to shift the SOA for your users entirely to Entra ID. Here’s a deep dive into why this shift is essential, how simple the change is, and the critical implications you need to plan for. The Hybrid Dilemma: Why AD SOA is Limiting: In a typical hybrid setup, every synced user object in Entra ID has properties that are permanently locked down or "grayed out." This is because the object has an underlying attribute, isCloudManaged, set to false. This status means: Limited Lifecycle Management: You can’t fully leverage cloud-based identity governance or lifecycle features. HR Provisioning Complexity: If your Human Resources (HR) system is the true source of truth for new employees, updates must flow: HR → AD → Entra ID. This creates latency and points of failure. Increased Attack Surface: If you are primarily cloud-focused, maintaining an AD object for synchronization creates an unnecessary on-premises attack surface that you must continually protect. No Cloud Editing: You are forced to make all major attribute changes in AD, even if the user only interacts with cloud services. By making Entra ID the Source of Authority, you break this dependency and unlock a truly cloud-first identity posture. The Core Mechanism: A Single Attribute Flip: The actual technical process of changing the SOA is surprisingly simple, it boils down to flipping a single attribute. The change is made using the Microsoft Graph API (or PowerShell) with a PATCH command against the user's onPremisesSyncBehavior endpoint. Action Method Endpoint Body Change SOA PATCH /beta/users/{user-id}/onPremisesSyncBehavior { "isCloudManaged": true } Once this change is made, two immediate things happen: Synchronization Stops: Entra Connect or Cloud Sync immediately recognize the change and stop synchronizing any updates from the on-premises AD object to the Entra ID object. Properties Unlocked: The user's properties in the Entra ID portal are instantly un-grayed, allowing cloud administrators to manage the user's identity directly. Critical Warning: No Write-Back Before you perform this change, you must understand the most critical implication: There is no user write-back capability from Entra ID to AD today. Once you shift the SOA, the connection is unidirectional and then effectively severed. Changes made to the cloud object will not be reflected in the on-premises AD object. Post-Migration Scenarios: Planning the Cutover: After flipping the SOA, you must plan what happens to the on-premises AD object. There are two main scenarios: Scenario 1: Full Cloud Cutover (The Ideal) If your user no longer requires any legacy Kerberos or AD-dependent services: Action in AD: Disable the user account in Active Directory immediately. After a period of validation, the account can be safely deleted. Benefit: This achieves the goal of minimizing your AD footprint, reducing attack surface, and simplifying your HR flow to HR → Entra ID. Scenario 2: Maintaining On-Premises Kerberos Access Many organizations still rely on Kerberos for resources like file shares, legacy applications, or Remote Desktop (RDP) access. Fortunately, you can still access these resources with an Entra ID-managed user, but it requires a few key technical components: Keep the AD Object: You must keep the on-premises AD user account (though it should no longer be managed by AD tools). Passwordless Authentication: The user must utilize a modern passwordless method (like Windows Hello for Business or FIDO2 keys). Cloud Kerberos Trust: Your environment must be configured with a Cloud Kerberos Trust. How it works: The cloud-managed user authenticates with Entra ID using passwordless methods. Entra ID, acting as a pseudo Read-Only Domain Controller, issues a partial Kerberos Ticket Granting Ticket (TGT). This partial TGT is used with your domain controllers to acquire a full Kerberos service ticket, which then grants access to the on-premises resource (e.g., the file share). Final Planning Checklist: While the Graph API command is easy, the preparation is everything. Plan your deployment carefully: Step Action Why 1. Migrate Groups First Shift the SOA for all security groups the user belongs to before shifting the user's SOA. Groups are often a logical first step for moving access controls. 2. Retire Exchange Hybrid Ensure all user mailboxes have been moved to Exchange Online. Entra ID SOA users are incompatible with the on-premises Exchange Hybrid configuration. 3. Plan for HR Flow Update your HR provisioning to target Entra ID directly, bypassing AD, for the affected users. This ensures the user's identity lifecycle is entirely cloud-managed going forward. 4. Automate Write a robust PowerShell script to manage the process, allowing for staged rollouts based on Organizational Units (OUs) or security groups. Avoid making changes one-by-one in the portal for scale and consistency. Moving the Source of Authority to Microsoft Entra ID is a major step toward a modern, highly secure, and simplified identity environment. Understand the implications, plan your path for Kerberos access, and start unlocking the full potential of the cloud.