apps
260 Topics
Whiteboard migration
Hi! Before MS Whiteboard for personal accounts shuts down, I want to say a huge thank you to the developers for the wonderful product I’ve been using constantly since 2020. It became my primary tool—especially due to remote learning in our region since 2022—and it worked reliably even with a very poor internet connection. It is a real shame that support for it is ending. Best regards.12Views0likes0Comments
Word friert ständig ein
Hallo, bei mir friert seit einer Woche immer wieder die Word App ein und ich weiß nicht, was ich tun soll. Ich habe alles geupdated, automatisches Speichern abgestellt, mein IPad neugestartet, das Internet immer wieder aus und angemacht und ich weiß einfach nicht weiter. Ich schreibe nicht mal einen ganzen Satz und schon friert alles ein und ich darf es schließen und erneut öffnen, nur damit dasselbe wieder geschieht. Ich brauche dringend Hilfe!78Views0likes0Comments
Issues around our administratio email on school.onmiscrosoft.com
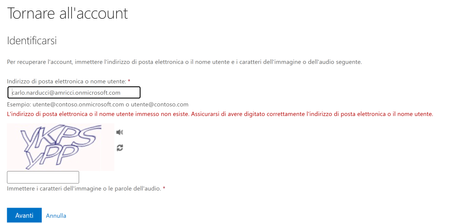
This page collects the issues (and related solutions/workarounds) linked to the administration account of the Microsoft 365 tenant http://school.onmicrosoft.com/. Context Tenant: my.name@myhttp://school.onmicrosoft.com/ Involved account: admin email address (specify which one, if needed) me and my administrator cannot access since jan 2026 Issues encountered Problem description Symptoms: my email amd my administrator email does not access the domani anymore Error message (if any): When it happens (frequency/time): no wayy to access other theachers have not this issue with the same domain Impact Who is blocked / which services are affected (Outlook, Teams, Entra ID, etc.) Urgency: Attempts already made [no way ] Password reset [ no way] Check MFA / sign-in methods [no way ] Try signing in from another browser / incognito [ ] Check Microsoft service status Next steps [ ] Collect screenshots and error codes see upper image [ ] Check sign-in logs (Entra ID) and any blocks (Conditional Access) [ ] Open a Microsoft support ticket (if needed) Notes / references Useful links: Last updated date:328Views0likes1Comment
AADSTS50105 error message is unreadable for end users — UX improvement suggestion
1. What’s wrong with the current error message a. It’s written for administrators, not users The message exposes: Internal system names (AADSTS50105) GUIDs (aaaabbbb-cccc-dddd-eeee-ffff01234567) Identity provider jargon (“direct member of a group with access”) None of this helps the person who sees the error decide what to do next. b. The actual problem is buried in a wall of text The real issue is simply: You don’t have permission to access this app. Instead, the message forces users to: Read a long paragraph Decode domain-specific language Guess which part matters Cognitively, this is high effort for low payoff. c. “Contact your administrator” is vague and unhelpful Users ask: Which administrator? IT? Security? App owner? Their manager? What should they say? Without context, users either: Ignore the error Forward screenshots randomly Open the wrong support ticket d. Error codes without guidance increase support load AADSTS50105 may be meaningful internally, but: Users don’t know whether to Google it Support teams receive unclear tickets (“it doesn’t work”) This paradoxically raises support cost instead of lowering it. 2. What a better error message should do A good error message answers four questions in order: What happened? Why did it happen (in plain language)? What can the user do next? Who specifically can help? And it does so in under 30 seconds of reading time. 3. Example of a much better error message You don’t have access to [APPLICATION] Your account (email address removed for privacy reasons) isn’t currently authorized to use [APPLICATION]. This usually means: You haven’t been added to the required security group, or Access hasn’t been requested or approved yet. What to do next If you believe you should have access, contact IT Service Desk or your [APPLICATION] owner and request access. Helpful details to include in your request Application name: [APPLICATION] Your email: email address removed for privacy reasons Error reference: Access not assigned (Error ID: AADSTS50105 — for IT use) 4. Optional but high-impact improvement: Add a “Request Access” button or link One-click takes users to: ServiceNow / Jira / internal form Auto-populates app name and user email Administrators configure support link when configuring the application656Views0likes1CommentRequest to enable preview feature - Face Check with CAP
Dear Microsoft, I am on a business premium plan for my home test tenant. I cannot raise ticket nor do I have an account manager. I know this is in private preview. I would like my tenant to be enabled to test this new Verified ID feature to have "Face Check" in CAP as one of the Grant conditions. tenant id: bc85b508-0107-4472-a49c-fc8cefd4f0d7 Thank you.346Views0likes1Comment
Made a self-hosted Entra ID governance portal for app/identity sprawl (open source)
Our tenant ended up with hundreds of app registrations and enterprise apps, and the native portal makes you dig through a separate blade for every basic question. Who owns this app? Which secrets die next month? What hasn't been signed into in a year? Which ones have scary Graph permissions? There's no single view for any of it, and half the ownership info was missing anyway. Entra ID Governance, access reviews, PIM all exist, but they felt heavy (and licensed) for what I actually wanted, which was just a fast list I could scan for routine cleanup. So I built one. Lightweight portal that runs entirely in your own subscription: One grid for App Registrations, Enterprise Apps, Managed Identities and Privileged Users Risk flags per identity: expiring/expired creds, high-risk permissions, no owner, stale sign-in, no CA coverage Ownership tracking, review and owner-change workflow, CSV export Tenant health score and a consent posture dashboard Optional expiry email notifications (needs a SendGrid key) Reads Graph through a managed identity, so no app secrets for data access and nothing leaves your tenant Runs about $26-30/month (one B2 App Service plan). B1 is also supported, but it's noticeably slower. It's not a replacement for Entra ID Governance or PIM, more of a cheap everyday hygiene thing. Full disclosure, I used AI building this and writing this up. I designed the architecture and functionality, tested it and ran it against my own tenant. It's open source and deployable with Azure DevOps or an Azure CLI script. Data never leaves your own tenant. Repo (screenshots + setup): https://github.com/nicolaibaralmueller/entra-identity-governance-portal Would love feedback, especially what you'd want it to flag that it doesn't, or where the risk scoring feels off. Been building it on and off for a few months with a lot of iteration. Hopefully this could be useful for others as well.518Views0likes2Comments
Ingesting Logs through Azure Private Link
Hi, We are currently using Azure Private Link within our environment and we are attempting to ingest logs into Log Analytics. When I reached out to Microsoft Support, it appears that the CCF connectors will not work using Private Link and the Azure Functions connectors are becoming depricated. Has anyone else run into this issue and what is the solution for getting logs into Sentinel through the Private Link, specifically API log sources? Did this require a custom app for each of these log sources or some sort of custom script that lives on an AMA host within the Private Link to ingest the logs? Any advice here would be greatly appeciated. Thank you,495Views0likes4Comments