Recent Blogs
Co-author: Vivek Kokkengada
Microsoft Ignite 2026 is here, and we're excited to share what's new in Microsoft Sentinel. We’re making it easier for security teams to unify operations, connect and us...
Nov 17, 20261.3KViews
0likes
0Comments
5 MIN READ
Inside Track | Microsoft Digital
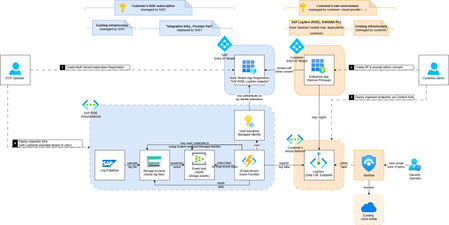
When infrastructure operations shift, security visibility must evolve with the operating model
Four years ago, we told the story of how Microsoft became Customer ...
Nov 16, 2026264Views
0likes
0Comments
Agentic security is only as effective as the security data it can access. That is why Microsoft Sentinel is a core part of the integrated SOC (ISOC), where SIEM and XDR work together with Microsoft D...
Nov 11, 2026480Views
0likes
1Comment
Microsoft Sentinel helps organizations detect, investigate, and respond to threats across increasingly complex environments. As AI transforms security operations, bringing together the right data and...
Nov 11, 20261.7KViews
0likes
1Comment
Welcome back to What's new in Microsoft Sentinel. In October, cross-tenant delegated access reaches general availability so you can run security operations across tenants with least privilege, the Ad...
Oct 30, 2026912Views
3likes
0Comments
Connecting the modern security environment
Having spent years working across Microsoft's cloud, AI, and customer-facing organizations. I have seen that technology delivers the greatest value when...
Oct 28, 2026660Views
0likes
1Comment
4 MIN READ
As security teams bring in more data from more sources and use it across SIEM and XDR workflows, decisions about connector health, ingestion volume, and cost optimization get harder.
Today, we’re a...
Oct 20, 20261.4KViews
1like
0Comments
Security operations rarely stop at a single tenant boundary. Managed security service providers (MSSPs) protect many customer environments, and central security teams often operate across a tenant es...
Oct 20, 20262.5KViews
1like
0Comments
Email remains one of the most common entry points for security threats. Yet email products often describe the same activity with different table names, fields, and values. This makes it harder to bui...
Oct 07, 2026919Views
1like
0Comments
Welcome back to What's new in Microsoft Sentinel. In September, Case Management brings investigation and collaboration together in Microsoft Defender, with a shared workspace to track work through re...
Sep 30, 20261.3KViews
2likes
1Comment
Tags
- siem334 Topics
- what's new114 Topics
- investigation110 Topics
- security96 Topics
- detection94 Topics
- hunting64 Topics
- soar52 Topics
- threat hunting & ti47 Topics
- data collection47 Topics
- security operations44 Topics