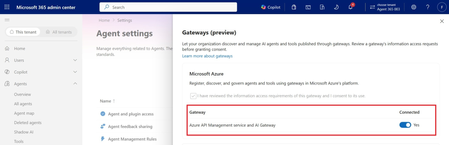
The integration connects centralized governance in Agent 365 with runtime enforcement for MCP servers and tools through Azure API Management for V2 and AI Gateway tiers.
Updated Oct 09, 2026
Version 2.0
santiagxf Microsoft
 MicrosoftMicrosoft

Hi santiagxf,
This is a massive step forward for enterprise AI governance.
What is great about this:
• Centralized vs. Runtime Balance: Separating governance in Agent 365 from gateway enforcement in Azure APIM is the exact right architectural move. No performance bottlenecks.
• Granular Tool-Level Blocking: Being able to block a specific tool on the AI Gateway tier without shutting down the entire MCP server is incredibly useful.
• Pre & Post-Invocation Checks: Using Defender and Purview to evaluate data before it leaves and before it returns solves a major compliance headache.
One real-world suggestion for the future:
Static blocking is an excellent start, but Dynamic, Context-Aware Governance would be a game-changer.
For example, instead of blocking a tool completely, the gateway could read the agent's intent in real-time. If an agent uses a finance tool for public market data, it's allowed. If it tries to fetch restricted HR data, the gateway dynamically blocks or redacts it based on the user's session context.
Adding this semantic layer would make this the ultimate tool for zero-trust AI.
Looking forward to testing the preview!!!
Thanks
Shivanna Gundanavar
 Microsoft
You are on point in context-aware governance and that's why AI Gateway, along with other products like Microsoft Entra, pushes observability data into Agent 365 to give it the context needed to take an action. The job of the AI Gateway is to be a policy enforcement point for agentic traffic that extends sight of Agent 365 into any agentic runtime.