threat intelligence
29 TopicsThe CISO Cheat Sheet to Microsoft Digital Defense Report 2026
I know we’re all busy, so I’ve pulled the most important data from this year’s Microsoft Digital Defense Report into one short read. The full report is well worth exploring, but this article focuses on the numbers and trends most relevant to security leaders. This year’s edition shows that AI is lowering the time, expertise and cost required to discover and exploit weaknesses, enabling attackers to operate with greater speed, scale and autonomy. The report describes this as AI “changing the physics of cybersecurity”: attack timelines are compressing and agentic systems are beginning to automate more of the attack lifecycle. Trend 1: Time has collapsed The clearest finding is about speed. Vulnerability discovery is increasingly running ahead of remediation, while the time from discovery to weaponisation is shrinking. In the AI era, weaponisation can follow in hours. Vulnerability discovery and weaponisation now often needs only a well-written prompt. The median time from discovery in the wild to weaponisation is below 24 hours. Vulnerabilities were on track for a record estimated 72,000 CVEs in 2026. The report expects a multi-year period in which the number of known but unpatched vulnerabilities rises sharply before eventually declining. The median time from container start to first exploit attempt is 5.3 hours. The ransomware actor Storm-1175 moved from web-facing exploitation to deploying Medusa ransomware in as little as 24 hours. CISA added over 110 CVEs to its Known Exploited Vulnerabilities catalogue between November 2025 and May 2026, most within a week of disclosure. The mismatch with enterprise reality is the uncomfortable part. The report says the disclosure-to-exploitation window has shrunk to single-digit days. Between November 2025 and May 2026, CISA added more than 110 vulnerabilities to its Known Exploited Vulnerabilities catalogue, most within a week of disclosure. In one example, Storm-1175 moved from exploiting a web-facing vulnerability to deploying Medusa ransomware in as little as 24 hours. Microsoft’s Red Team makes an important point: a patch is also a disclosure. Every fix points attackers towards the flaw it closes. As AI-assisted analysis makes reversing patches faster and more reliable, the report argues that patch velocity, not simply patch availability, becomes the control that matters. Trend 2: Attack chains are gaining autonomy The report charts a clear progression: September–November 2025: AI assists in orchestrating a campaign, as in the Anthropic-reported espionage case. April–June 2026: Full-chain autonomy is demonstrated in labs. July 2026: Real-world autonomous attacks of increasing complexity appear. Two frontier models, Mythos and GPT-5.5, completed a 32-step attack chain against an emulated enterprise with no human help. The test environment had no defenders. The UK AI Security Institute reached a similar finding independently. GPT-5.5 was the second model to solve its end-to-end corporate network attack simulation, a task AISI estimates would take a human about 20 hours. Open-weight models lag closed models at orchestrating attacks by about seven months. In the wild, early July 2026 saw the first documented automated ransomware extortion attack, named JADEPUFFER by Sysdig. Microsoft has seen AI-orchestrated intrusions that share elements with it. Initial access consistently came from internet-exposed services running known-vulnerable software. The report is measured on this point. Volumes of AI-orchestrated activity remain low. In most observed real-world operations, complex end-to-end intrusions still retain meaningful human direction. The Red Team's framing is the most useful one: AI doesn't create a new class of attack, it collapses the effort needed to find and exploit existing attack paths. Trend 3: AI has become an attack surface The report's second takeaway is that attackers are already targeting AI itself. The adoption numbers explain why. 88% of enterprises are experimenting with agents, and 82% of leaders plan broader rollouts within 12–18 months. The report cites industry projections of roughly 1.3 billion agents in production by 2028. What attackers are doing to AI systems: Four techniques accounted for roughly 90% of observed attack activity in telemetry from Azure AI workloads: malicious link injection (52%), jailbreaks (16%), tool and agent abuse (12%), and identity and credential abuse (10%). Memory poisoning: An attacker who can place content anywhere an agent reads can often place it where the agent remembers. Email is the dominant pathway the Red Team has observed. Human-in-the-loop isn't a complete control: Red team testing saw approval prompts ignored, or bypassed by a policy stored in poisoned memory. Developer tools turned against their owners: The "s1ngularity" malware hijacked locally installed AI command-line tools to hunt for secrets. It leaked about 2,000 secrets and 20,000 files across 225 victims. AI browsers: In daily use at more than 40% of organisations in Microsoft's dataset, they were the initial infection vector in incidents involving 57 malware families in a May 2026 analysis. Chat histories as a target: Malicious AI-assistant extensions reached nearly 900,000 installs and more than 20,000 enterprise tenants, harvesting AI chat histories that often contain code, architecture and credentials. The identity implications are direct. Each agent needs its own identity, not one borrowed from an employee, and a named human sponsor. The report also treats revocation latency, the time to cut off a compromised agent, as a measured outcome. Trend 4: The front door is still identity AI changes the speed and personalisation of social engineering. It hasn't changed where attacks start. Initial access in Defender Experts data: User execution: 30% Valid accounts: 20% Malicious copy-and-paste: 13% Phishing: 11% Together, user execution and valid accounts account for over half of observed activity. In incident response engagements, phishing as an initial access vector jumped from 7% to 23% year on year. The standout numbers: ClickFix: Defender saw user-pasted malicious commands on more than 1.1 million unique devices between February and early May 2026, roughly an 8x increase. AiTM: URLs accounted for 45% of the identified phishing techniques in the report’s breakdown. Separately, the share of AiTM phishing and token-theft attacks more than doubled during the first six months of 2026, although the report notes that their overall share remained comparatively small. Teams vishing: Weekly confirmed malicious volume increased 502% year on year. Per attempt, 48% of vishing calls kept the victim engaged for more than 20 seconds, and 30% lasted more than one minute. When a call succeeds, attackers can persuade the victim to install a remote-management tool and complete reconnaissance in two minutes or less. Business contact impersonation (BCI): The report introduces this term for conversations that start with a trusted-looking contact. Microsoft detected more than 46 million attacks in 12 months, with a 121% spike in April 2026. The share of first-contact messages that explicitly asked for money or documents fell from 17% to 3%. The first message is deliberately bland, like "Are you at your desk?" Password attacks declined 26% year on year, which the report describes as strong evidence that MFA and passkeys are forcing attackers to pivot. That pivot includes techniques such as fatigue attacks, AiTM phishing and token theft designed to circumvent conventional MFA. Trend 5: Attackers are inheriting trust rather than breaking in The report's headline theme is that risk is increasingly interconnected. Threats travel through the trusted relationships between identities, software supply chains, partners and cloud platforms. The numbers: Supply chain: Major open-source ecosystems saw attacks roughly every ten days, accelerating through Q2 2026. Shai-Hulud 2.0 affected 25,000 repositories. Megalodon backdoored 5,561 GitHub repositories in under six hours. Trusted signing: In May 2026, Microsoft disrupted Fox Tempest, a "malware-signing-as-a-service" operation that obtained genuine certificates for ransomware loaders and infostealers. Microsoft revoked over a thousand fraudulent code-signing certificates. Legitimate access: An unsanctioned remote monitoring tool is now one of the most reliable mid-stage indicators of a human-operated intrusion. Cloud identity: Cloud identity abuse was the most observed technique against critical infrastructure, representing 78% of the technique mix in Microsoft’s data for March to June 2026. Hybrid intrusions: The Storm-2885 case showed an attacker using a privileged cloud identity to close and downgrade security alerts. The report says identity governance and alert-handling workflows deserve Tier 0 treatment. Dwell time: DART data shows a statistically significant increase in dwell time year on year, meaning organisations took longer to detect intrusions. Ransomware shows the same ecosystem pattern. Qilin led leak-site data with 16.4% of victims, up 386%. Defender detections tell a different story, with Akira at 22%. Trend 6: Defence works best when it's connected The report is not only a catalogue of threats. The strongest defensive evidence: Disruption works. Following the March 2026 disruption, Tycoon2FA activity had fallen 95% from its November 2025 peak by June. Its share of CAPTCHA-gated phishing declined from 76% in December 2025 to 12% in June 2026. Correlation is the highest-leverage variable. The report argues that how well defenders share and correlate signals across endpoint, identity, cloud, email and network is one of the highest-leverage strategic variables under their control. AI is also changing defensive operations. The report describes AI-assisted triage, incident summarisation, hunting-query generation and detection engineering as ways to accelerate investigations and allow analysts to concentrate on higher-value work. Automated disruption can compress response time. The report says that when a correlated incident reaches a defined confidence threshold, defensive systems can automatically isolate devices, disable compromised accounts, revoke sessions or quarantine affected cloud resources. It also stresses the importance of appropriate governance and human oversight for high-risk AI actions. The report also recommends changing what leaders measure. It suggests moving from patches deployed to exposure reduced, detection coverage increased and time-to-mitigate compressed. What the MDDR recommends: ten security priorities The report starts its recommendations with the foundations: Secure by Design, Secure by Default and Secure Operations, applied through identity-centric Zero Trust. Microsoft says these keep the priorities below durable as AI adds more identities, applications, agents and dependencies to govern. Govern cyber risk at leadership level. Report identity exposure, patch latency, agent permissions, critical dependencies, dwell time and recovery readiness to the board. Defend identity as the primary control plane. Deploy passkeys and phishing-resistant MFA, reduce privilege and govern human and non-human identities. Invalidate and rotate tokens and session credentials quickly. Establish governance, visibility and data controls for AI. Keep visibility of approved AI tools, services and agents, and monitor for unauthorised or unmanaged use. Apply sensitivity-aware access and data protection to the data those systems can reach. Reduce exposure and edge risk. Continuously discover internet-facing assets and patch edge devices quickly. Centralise high-fidelity logging, enforce strong authentication and combine network visibility with threat intelligence. Focus on cross-signal correlation. Correlate endpoint, identity, cloud, application, email and network signals to detect intrusions earlier. Correlation also helps defenders anticipate attack paths and likely targets. Enact a continuous threat and vulnerability management model. Combine asset visibility, vulnerability identification, threat detection and AI-accelerated insight into a single continuous programme. Validate exposure through proactive testing. Run assume-breach exercises on cloud services, SaaS platforms, APIs and workflow automation. Prioritise them by where your highest-value data is stored, accessed or aggregated. Secure software dependencies. Harden software installation, keep a software inventory and validate provenance. Monitor packages and prepare for rapid containment. Participate in collective defence. Share actionable threat indicators and victim-informed intelligence with trusted partners and law enforcement. This supports coordinated tracking, investigation and disruption. Prepare for long-horizon technology transitions. Build a cryptographic inventory and advance post-quantum planning alongside AI governance. Read together, the numbers tell one story: the attacker’s workflow is becoming faster and less expensive. AI can shorten vulnerability discovery, exploitation, secret discovery and lateral movement, while organisations still face the slower operational work of testing, coordinating and deploying safe changes across complex environments. At the same time, agent identities can proliferate faster than organisations can inventory, govern and revoke them The defining question for boards today is not whether disruption will occur, but whether the organization can continue operating, contain harm, recover quickly, and maintain trust when it does. Source: Microsoft Digital Defense Report 2026, Version 1.1. Reporting period: July 2025–June 2026.Planning your move to Microsoft Defender portal for all Microsoft Sentinel customers
In November 2023, Microsoft announced our strategy to unify security operations by bringing the best of XDR and SIEM together. Our first step was bringing Microsoft Sentinel into the Microsoft Defender portal, giving teams a single, comprehensive view of incidents, reducing queue management, enriching threat intel, streamlining response and enabling SOC teams to take advantage of Gen AI in their day-to-day workflow. Since then, considerable progress has been made with thousands of customers using this new unified experience; to enhance the value customers gain when using Sentinel in the Defender portal, multi-tenancy and multi-workspace support was added to help customers with more sophisticated deployments. Our mission is to unify security operations by bringing all your data, workflows, and people together to unlock new capabilities and drive better security outcomes. As a strong example of this, last year we added extended posture management, delivering powerful posture insights to the SOC team. This integration helps build a closed-loop feedback system between your pre- and post-breach efforts. Exposure Management is just one example. By bringing everything together, we can take full advantage of AI and automation to shift from a reactive to predictive SOC that anticipates threats and proactively takes action to defend against them. Beyond Exposure Management, Microsoft has been constantly innovating in the Defender experience, adding not just SIEM but also Security Copilot. The Sentinel experience within the Defender portal is the focus of our innovation energy and where we will continue to add advanced Sentinel capabilities going forward. Onboarding to the new unified experience is easy and doesn’t require a typical migration. Just a few clicks and permissions. Customers can continue to use Sentinel in the Azure portal while it is available even after choosing to transition. Today, we’re announcing that we are moving to the next phase of the transition with a target to retire the Azure portal for Microsoft Sentinel by July 1, 2026. Customers not yet using the Defender portal should plan their transition accordingly. “Really amazing to see that coming, because cross querying with tables in one UI is really cool! Amazing, big step forward to the unified [Defender] portal.” Glueckkanja AG “The biggest benefit of a unified security operations solution (Microsoft Sentinel + Microsoft Defender XDR) has been the ability to combine data in Defender XDR with logs from third party security tools. Another advantage developed has been to eliminate the need to switch between Defender XDR and Microsoft Sentinel portals, now having a single pane of glass, which the team has been wanting for some years.” Robel Kidane, Group Information Security Manager, Renishaw PLC Delivering the SOC of the future Unifying threat protection, exposure management and security analytics capabilities in one pane of glass not only streamlines the user experience, but also enables Sentinel customers to realize security outcomes more efficiently: Analyst efficiency: A single portal reduces context switching, simplifies workflows, reduces training overhead, and improves team agility. Integrated insights: SOC-focused case management, threat intelligence, incident correlation, advanced hunting, exposure management, and a prioritized incident queue enriched with business and sensitivity context—enabling faster, more informed detection and response across all products. SOC optimization: Security controls that can be adjusted as threats and business priorities change to control costs and provide better coverage and utilization of data, thus maximizing ROI from the SIEM. Accelerated response: AI-driven detection and response which reduces mean time to respond (MTTR) by 30%, increases security response efficiency by 60%, and enables embedded Gen AI and agentic workflows. What’s next: Preparing for the retirement of the Sentinel Experience in the Azure Portal Microsoft is committed to supporting every single customer in making that transition over the next 12 months. Beginning July 1, 2026, Sentinel users will be automatically redirected to the Defender portal. After helping thousands of customers smoothly make the transition, we recommend that security teams begin planning their migration and change management now to ensure continuity and avoid disruption. While the technical process is very straightforward, we have found that early preparation allows time for workflow validation, training, and process alignment to take full advantage of the new capabilities and experience. Tips for a Successful Migration to Microsoft Defender 1. Leverage Microsoft’s help: Leverage Microsoft documentation, instructional videos, guidance, and in-product support to help you be successful. A good starting point is the documentation on Microsoft Learn. 2. Plan early: Engage stakeholders early including SOC and IT Security leads, MSSPs, and compliance teams to align on timing, training and organizational needs. Make sure you have an actionable timeline and agreement in the organization around when you can prioritize this transition to ensure access to the full potential of the new experience. 3. Prepare your environment: Plan and design your environment thoroughly. This includes understanding the prerequisites for onboarding Microsoft Sentinel workspaces, reviewing and deciding on access controls, and planning the architecture of your tenant and workspace. Proper planning will ensure a smooth transition and help avoid any disruptions to your security operations. 4. Leverage Advanced Threat Detection: The Defender portal offers enhanced threat detection capabilities with advanced AI and machine learning for Microsoft Sentinel. Make sure to leverage these features for faster and more accurate threat detection and response. This will help you identify and address critical threats promptly, improving your overall security posture. 5. Utilize Unified Hunting and Incident Management: Take advantage of the enhanced hunting, incident, and investigation capabilities in Microsoft Defender. This provides a comprehensive view for more efficient threat detection and response. By consolidating all security incidents, alerts, and investigations into a single unified interface, you can streamline your operations and improve efficiency. 6. Optimize Cost and Data Management The Defender portal offers cost and data optimization features, such as SOC Optimization and Summary Rules. Make sure to utilize these features to optimize your data management, reduce costs, and increase coverage and SIEM ROI. This will help you manage your security operations more effectively and efficiently. Unleash the full potential of your Security team The unified SecOps experience available in the Defender portal is designed to support the evolving needs of modern SOCs. The Defender portal is not just a new home for Microsoft Sentinel - it’s a foundation for integrated, AI-driven security operations. We’re committed to helping you make this transition smoothly and confidently. If you haven’t already joined the thousands of security organizations that have done so, now is the time to begin. Resources AI-Powered Security Operations Platform | Microsoft Security Microsoft Sentinel in the Microsoft Defender portal | Microsoft Learn Shifting your Microsoft Sentinel Environment to the Defender Portal | Microsoft Learn Microsoft Sentinel is now in Defender | YouTube49KViews9likes22CommentsWhy UK Enterprise Cybersecurity Is Failing in 2026 (And What Leaders Must Change)
Enterprise cybersecurity in large organisations has always been an asymmetric game. But with the rise of AI‑enabled cyber attacks, that imbalance has widened dramatically - particularly for UK and EMEA enterprises operating complex cloud, SaaS, and identity‑driven environments. Microsoft Threat Intelligence and Microsoft Defender Security Research have publicly reported a clear shift in how attackers operate: AI is now embedded across the entire attack lifecycle. Threat actors use AI to accelerate reconnaissance, generate highly targeted phishing at scale, automate infrastructure, and adapt tactics in real time - dramatically reducing the time required to move from initial access to business impact. In recent months, Microsoft has documented AI‑enabled phishing campaigns abusing legitimate authentication mechanisms, including OAuth and device‑code flows, to compromise enterprise accounts at scale. These attacks rely on automation, dynamic code generation, and highly personalised lures - not on exploiting traditional vulnerabilities or stealing passwords. The Reality Gap: Adaptive Attackers vs. Static Enterprise Defences Meanwhile, many UK enterprises still rely on legacy cybersecurity controls designed for a very different threat model - one rooted in a far more predictable world. This creates a dangerous "Resilience Gap." Here is why your current stack is failing- and the C-Suite strategy required to fix it. 1. The Failure of Traditional Antivirus in the AI Era Traditional antivirus (AV) relies on static signatures and hashes. It assumes malicious code remains identical across different targets. AI has rendered this assumption obsolete. Modern malware now uses automated mutation to generate unique code variants at execution time, and adapts behaviour based on its environment. Microsoft Threat Intelligence has observed threat actors using AI‑assisted tooling to rapidly rewrite payload components, ensuring that every deployment looks subtly different. In this model, there is no reliable signature to detect. By the time a pattern exists, the attacker has already moved on. Signature‑based detection is not just slow - it is structurally misaligned with AI‑driven attacks. The Risk: If your security relies on "recognising" a threat, you are already breached. By the time a signature exists, the attacker has evolved. The C-Suite Pivot: Shift investment from artifact detection to EDR/XDR (Extended Detection and Response). We must prioritise behavioural analytics and machine learning models that identify intent rather than file names. 2. Why Perimeter Firewalls Fail in a Cloud-First World Many UK enterprise still rely on firewalls enforcing static allow/deny rules based on IP addresses and ports. This model worked when applications were predictable and networks clearly segmented. Today, enterprise traffic is encrypted, cloud‑hosted, API‑driven, and deeply integrated with SaaS and identity services. AI‑assisted phishing campaigns abusing OAuth and device‑code flows demonstrate this clearly. From a network perspective, everything looks legitimate: HTTPS traffic to trusted identity providers. No suspicious port. No malicious domain. Yet the attacker successfully compromises identity. The Risk: Traditional firewalls are "blind" to identity-based breaches in cloud environments. The C-Suite Pivot: Move to Identity-First Security. Treat Identity as the new Control Plane, integrating signals like user risk, device health, and geolocation into every access decision. 3. The Critical Weakness of Single-Factor Authentication Despite clear NCSC guidance, single-factor passwords remain a common vulnerability in legacy applications and VPNs. AI-driven credential abuse has changed the economics of these attacks. Threat actors now deploy adaptive phishing campaigns that evolve in real-time. Microsoft has observed attackers using AI to hyper-target high-value UK identities- specifically CEOs, Finance Directors, and Procurement leads. The Risk: Static passwords are now the primary weak link in UK supply chain security. The C-Suite Pivot: Mandate Phishing‑resistant MFA (Passkeys or hardware security keys). Implement Conditional Access policies that evaluate risk dynamically at the moment of access, not just at login. Legacy Security vs. AI‑Era Reality 4. The Inherent Risk of VPN-Centric Security VPNs were built on a flawed assumption: that anyone "inside" the network is trustworthy. In 2026, this logic is a liability. AI-assisted attackers now use automation to map internal networks and identify escalation paths the moment they gain VPN access. Furthermore, Microsoft has tracked nation-state actors using AI to create synthetic employee identities- complete with fake resumes and deepfake communication. In these scenarios, VPN access isn't "hacked"; it is legally granted to a fraudster. The Risk: A compromised VPN gives an attacker the "keys to the kingdom." The C-Suite Pivot: Transition to Zero Trust Architecture (ZTA). Access must be explicit, scoped to the specific application, and continuously re‑evaluated using behavioural signals. 5. Data: The High-Velocity Target Sensitive data sitting unencrypted in legacy databases or backups is a ticking time bomb. In the AI era, data discovery is no longer a slow, manual process for a hacker. Attackers now use AI to instantly analyse your directory structures, classify your files, and prioritise high-value data for theft. Unencrypted data significantly increases your "blast radius," turning a containable incident into a catastrophic board-level crisis. The Risk: Beyond the technical breach, unencrypted data leads to massive UK GDPR fines and irreparable brand damage. The C-Suite Pivot: Adopt Data-Centric Security. Implement encryption by default, classify data while adding sensitivity labels and start board-level discussions regarding post‑quantum cryptography (PQC) to future-proof your most sensitive assets. 6. The Failure of Static IDS Traditional Intrusion Detection Systems (IDS) rely on known indicators of compromise - assuming attackers reuse the same tools and techniques. AI‑driven attacks deliberately avoid that assumption. Threat actors are now using Large Language Models (LLMs) to weaponize newly disclosed vulnerabilities within hours. While your team waits for a "known pattern" to be updated in your system, the attacker is already using a custom, AI-generated exploit. The Risk: Your team is defending against yesterday's news while the attacker is moving at machine speed. The C-Suite Pivot: Invest in Adaptive Threat Detection. Move toward Graph‑based XDR platforms that correlate signals across email, endpoint, and cloud to automate investigation and response before the damage spreads. From Static Security to Continuous Security Closing Thought: Security Is a Journey, Not a Destination For UK enterprises, the shift toward adaptive cybersecurity is no longer optional - it is increasingly driven by regulatory expectation, board oversight, and accountability for operational resilience. Recent UK cyber resilience reforms and evolving regulatory frameworks signal a clear direction of travel: cybersecurity is now a board‑level responsibility, not a back‑office technical concern. Directors and executive leaders are expected to demonstrate effective governance, risk ownership, and preparedness for cyber disruption - particularly as AI reshapes the threat landscape. AI is not a future cybersecurity problem. It is a current force multiplier for attackers, exposing the limits of legacy enterprise security architectures faster than many organisations are willing to admit. The uncomfortable truth for boards in 2026 is that no enterprise is 100% secure. Intrusions are inevitable. Credentials will be compromised. Controls will be tested. The difference between a resilient enterprise and a vulnerable one is not the absence of incidents, but how risk is managed when they occur. In mature organisations, this means assuming breach and designing for containment: Access controls that limit blast radius Least privilege and conditional access restricting attackers to the smallest possible scope if an identity is compromised Data‑centric security using automated classification and encryption, ensuring that even when access is misused, sensitive data cannot be freely exfiltrated As a Senior Enterprise Cybersecurity Architect, I see this moment as a unique opportunity. AI adoption does not have to repeat the mistakes of earlier technology waves, where innovation moved fast and security followed years later. We now have a rare chance to embed security from day one - designing identity controls, data boundaries, automated monitoring, and governance before AI systems become business‑critical. When security is built in upfront, enterprises don’t just reduce risk - they gain the confidence to move faster and unlock AI’s value safely. Security is no longer a “department”. In the age of AI, it is a continuous business function - essential to preserving trust and maintaining operational continuity as attackers move at machine speed. References: Inside an AI‑enabled device code phishing campaign | Microsoft Security Blog AI as tradecraft: How threat actors operationalize AI | Microsoft Security Blog Detecting and analyzing prompt abuse in AI tools | Microsoft Security Blog Post-Quantum Cryptography | CSRC Microsoft Digital Defense Report 2025 | Microsoft https://www.ncsc.gov.uk/news/government-adopt-passkey-technology-digital-servicesAnnouncing public preview of custom graphs in Microsoft Sentinel
Security attacks span identities, devices, resources, and activity, making it critical to understand how these elements connect to expose real risk. In November, we shared how Sentinel graph brings these signals together into a relationship-aware view to help uncover hidden security risks. We’re excited to announce the public preview of custom graphs in Sentinel, available starting April 1 st . Custom graphs let defenders model relationships that are unique to their organization, then run graph analytics to surface blast radius, attack paths, privilege chains, chokepoints, and anomalies that are difficult to spot in tables alone. In this post, we’ll cover what custom graphs are, how they work, and how to get started so the entire team can use them. Custom graphs Security data is inherently connected: a sign-in leads to a token, a token touches a workload, a workload accesses data, and data movement triggers new activity. Graphs represent these relationships as nodes (entities) and edges (relationships), helping you answer questions like: “Who received the phishing email, who clicked, and which clicks were allowed by the proxy?” or “Show me users who exported notebooks, staged files in storage, then uploaded data to personal cloud storage- the full, three‑phase exfiltration chain through one identity.” With custom graphs, security teams can build, query, and visualize tailored security graphs using data from the Sentinel data lake and non-Microsoft sources, powered by Fabric. By uncovering hidden patterns and attack paths, graphs provide the relationship context needed to surface real risk. This context strengthens AI‑powered agent experiences, speeds investigations, clarifies blast radius, and helps teams move from noisy, disconnected alerts to confident decisions. In the words of our preview customers: “We ingested our Databricks management-plane telemetry into the Sentinel data lake and built a custom security graph. Without writing a single detection rule, the graph surfaced unusual patterns of activity and overprivileged access that we escalated for investigation. We didn't know what we were looking for, the graph surfaced the risk for us by revealing anomalous activity patterns and unusual access combinations driven by relationships, not alerts.” – SVP, Security Solutions | Financial Services organization Use cases Sentinel graph offers embedded, Microsoft managed, security graphs in Defender and Microsoft Purview experiences to help you at every stage of defense, from pre-breach to post-breach and across assets, activities, and threat intelligence. See here for more details. The new custom graph capability gives you full control to create your own graphs combining data from Microsoft sources, non-Microsoft sources, and federated sources in the Sentinel data lake. With custom graphs you can: Understand blast radius – Trace phishing campaigns, malware spread, OAuth abuse, or privilege escalation paths across identities, devices, apps, and data, without stitching together dozens of tables. Reconstruct real attack chains – Model multi-step attacker behavior (MITRE techniques, lateral movement, before/after malware) as connected sequences so investigations are complete and explainable, not a set of partial pivots. Reconstruct these chains from historical data in the Sentinel data lake. Figure 2: Drill into which specific MITRE techniques each IP is executing and in which tactic category Spot hidden risks and anomalies – Detect structural outliers like users with unusually broad access, anomalous email exfiltration, or dangerous permission combinations that are invisible in flat logs. Figure 3: OAuth consent chain – a single compromised user consented four dangerous permissions Creating custom graph Using the Sentinel VS Code extension, you can generate graphs to validate hunting hypotheses, such as understanding attack paths and blast radius of a phishing campaign, reconstructing multi‑step attack chains, and identifying structurally unusual or high‑risk behavior, making it accessible to your team and AI agents. Once persisted via a schedule job, you can access these custom graphs from the ready-to-use section in the graphs section in the Defender portal. Figure 4: Use AI-assisted vibe coding in Visual Studio Code to create tailored security graphs powered by Sentinel data lake and Fabric Graphs experience in the Microsoft Defender portal After creating your custom graphs, you can access them in the Graphs section of the Microsoft Defender portal under Sentinel. From there, you can perform interactive, graph-based investigations, for example, using a graph built for phishing analysis to quickly evaluate the impact of a recent incident, profile the attacker, and trace paths across Microsoft telemetry and third-party data. The graph experience lets you run Graph Query Language (GQL) queries, view the graph schema, visualize results, see results in a table, and interactively traverse to the next hop with a single click. Figure 5: Query, visualize, and traverse custom graphs with the new graph experience in Sentinel Billing Custom graph API usage for creating graph and querying graph is billed according to the Sentinel graph meter. Get started To use custom graphs, you’ll need Microsoft Sentinel data lake enabled in your tenant, since the lake provides the scalable, open-format foundation that custom graphs build on. Use the Sentinel data lake onboarding flow to provision the data lake if it isn’t already enabled. Ensure the required connectors are configured to populate your data lake. See Manage data tiers and retention in Microsoft Sentinel | Microsoft Learn. Create and persist a custom graph. See Get started with custom graphs in Microsoft Sentinel (preview) | Microsoft Learn. Run adhoc graph queries and visualize graph results. See Visualize custom graphs in Microsoft Sentinel graph (preview) | Microsoft Learn. [Optional] Schedule jobs to write graph query results to the lake tier and analytics tier using notebooks. See Exploring and interacting with lake data using Jupyter Notebooks - Microsoft Security | Microsoft Learn. Learn more Earlier posts (Sentinel graph general availability) RSAC 2026 announcement roundup Custom graphs documentation Custom graph billingAccelerate connectors development using AI agent in Microsoft Sentinel
Today, we’re excited to announce the public preview of a Sentinel connector builder agent, via VS code extension, that helps developers build Microsoft Sentinel codeless connectors faster with low-code and AI-assisted prompts. This new capability brings guided workflows directly into the tooling developers already use, helping accelerate time to value as the Sentinel ecosystem continues to grow. Learn more at Create custom connectors using Sentinel connector AI agent Why this matters As the Microsoft Sentinel ecosystem continues to expand, developers are increasingly tasked with delivering high‑quality, production‑ready connectors at a faster pace, often while working across different cloud platforms and development environments. Building these integrations involves coordinating schemas, configuration artifacts, Azure deployment concepts, and validation steps that provide flexibility and control, but can span multiple tools and workflows. As connector development scales across more partners and scenarios, there is a clear opportunity to better integrate these capabilities into the developer environments teams already rely on. The new Sentinel connector builder agent, using GitHub Copilot in the Sentinel VS code extension, brings more of the connector development lifecycle -- authoring, validation, testing, and deployment into a single, cohesive workflow. By consolidating these common steps, it helps developers move more easily from design to validation and deployment without disrupting established processes. A guided, AI‑assisted workflow inside VS Code The Sentinel connector builder agent for Visual Studio Code is designed to help developers move from API documentation to a working codeless connector more efficiently. The experience begins with an ISVs API documentation. Using GitHub Copilot chat inside VS Code, developers can describe the connector they want to build and point the extension to their API docs, either by URL or inline content. From there, the AI‑guided workflow reads and extracts the relevant details needed to begin building the connector. Open the VS Code chat and set the chat to Agent mode. Prompt the agent using sentinel. When prompted, select /create-connector and select any supported API. For example in Contoso API, enter the prompt as: @sentinel /create-connector Create a connector for Contoso. Here are the API docs: https://contoso-security-api.azurewebsites.net/v0101/api-doc Next, the agent generates the required artifacts such as polling configurations, data collection rules (DCRs), table schemas, and connector definitions, using guided prompts with built‑in validation. This step‑by‑step experience helps ensure configurations remain consistent and aligned as they’re created. Note: During agent evaluation, select Allow responses once to approve changes, or select the option Bypass Approvals in the chat. It might take up to several minutes for the evaluations to finish. As the connector takes shape, developers can validate and test configurations directly within VS Code, including testing API interactions before deployment. Validation of the API data source and polling configuration are surfaced in context, supporting faster iteration without leaving the development environment. When ready, connectors can be deployed directly from VS Code to accessible Microsoft Sentinel workspaces, streamlining the path from development to deployment without requiring manual navigation of the Azure portal. Key capabilities The VS Code connector builder experience includes: AI‑guided connector creation to generate codeless connectors from API documentation using natural language prompts. Support for common authentication methods, including Basic authentication, OAuth 2.0, and API keys. Automated validation to check schemas, cross‑file consistency, and configuration correctness as you build. Built‑in testing to validate polling configurations and API interactions before deployment. One‑click deployment that allows publishing connectors directly to accessible Microsoft Sentinel workspaces from within VS Code. Together, these capabilities support a more efficient path from API documentation to a working Microsoft Sentinel connector. Testimonials As partners begin using the Sentinel connector builder agent, feedback from the community will help shape future enhancements and refinements. Here is what some of our early adopters have to say about the experience: “The connector builder agent accelerated our initial exploration of the codeless connector framework and helped guide our connector design decisions.” -- Rodrigo Rodrigues, Technology Alliance Director “The connector builder agent helped us quickly explore and validate connector options on the codeless connector framework while developing our Sentinel integration.” --Chris Nicosia, Head of Cloud and Tech Partnerships Start building This public preview represents an important step toward simplifying how ISVs build and maintain integrations with Microsoft Sentinel. If you’re ready to get started, the Sentinel connector builder agent is available in public preview for all participants. In the unlikely event that an ISV encounters any issues in building or updating a CCF connector, App Assure is here to help. Reach out to us here.From Manual Vetting to Continuous Trust: Automating Publisher Screening with AI
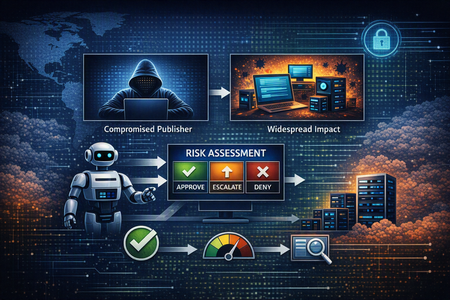
Publisher screening is a software supply-chain reality: if a publisher account is compromised, a single update can reach thousands of machines—and recovery is costly. Microsoft Trust & Security Services applies AI to automate screening at onboarding and keep reassessing publishers as new signals appear. Multiple “checker” agents evaluate identity, reputation, and post-approval behavior, then combine evidence into a consistent risk score and an approve/deny/escalate decision, with an evidence-backed explanation that supports auditability and appeals while reducing operational toil.Strengthening your Security Posture with Microsoft Security Store Innovations at RSAC 2026
Security teams are facing more threats, more complexity, and more pressure to act quickly - without increasing risk or operational overhead. What matters is being able to find the right capability, deploy it safely, and use it where security work already happens. Microsoft Security Store was built with that goal in mind. It provides a single, trusted place to discover, purchase, and deploy Microsoft and partner-built security agents and solutions that extend Microsoft Security - helping you improve protection across SOC, identity, and data protection workflows. Today, the Security Store includes 75+ security agents and 115+ solutions from Microsoft and trusted partners - each designed to integrate directly into Microsoft Security experiences and meet enterprise security requirements. At RSAC 2026, we’re announcing capabilities that make it easier to turn security intent into action- by improving how you discover agents, how quickly you can put them to use, and how effectively you can apply them across workflows to achieve your security outcomes. Meet the Next Generation of Security Agents Security agents are becoming part of day-to-day operations for many teams - helping automate investigations, enrich signals, and reduce manual effort across common security tasks. Since Security Store became generally available, Microsoft and our partners have continued to expand the set of agents that integrate directly with Microsoft Defender, Sentinel, Entra, Purview, Intune and Security Copilot. Some of the notable partner-built agents available through Security Store include: XBOW Continuous Penetration Testing Agent XBOW’s penetration testing agents perform pen-tests, analyzes findings, and correlates those findings with a customer’s Microsoft Defender detections. XBOW integrates offensive security directly into Microsoft Security workflows by streaming validated, exploitable AppSec findings into Microsoft Sentinel and enabling investigation through XBOW's Copilot agents in Microsoft Defender. With XBOW’s pen-testing agents, offensive security can run continuously to identify which vulnerabilities are actually exploitable, and how to improve posture and detections. Tanium Incident Scoping Agent The Tanium Incident Scoping Agent (In Preview) is bringing real-time endpoint intelligence directly into Microsoft Defender and Microsoft Security Copilot workflows. The agent automatically scopes incidents, identifies impacted devices, and surfaces actionable context in minutes-helping teams move faster from detection to containment. By combining Tanium’s real-time intelligence with Microsoft Security investigations, you can reduce manual effort, accelerate response, and maintain enterprise-grade governance and control. Zscaler In Microsoft Sentinel, the Zscaler ZIA–ZPA Correlation Agent correlates ZIA and ZPA activity for a given user to speed malsite/malware investigations. It highlights suspicious patterns and recommends ZIA/ZPA policy changes to reduce repeat exposure. These agents build on a growing ecosystem of Microsoft and partner capabilities designed to work together, allowing you to extend Microsoft Security with specialized expertise where it has the most impact. Discover and Deploy Agents and Solutions in the Flow of Security Work Security teams work best when they don’t have to switch tools to make decisions. That’s why Security Store is embedded directly into Microsoft Security experiences - so you can discover and evaluate trusted agents and solutions in context, while working in the tools you already use. When Security Store became generally available, we embedded it into Microsoft Defender, allowing SOC teams to discover and deploy trusted Microsoft and partner‑built agents and solutions in the middle of active investigations. Analysts can now automate response, enrich investigations, and resolve threats all within the Defender portal. At RSAC, we’re expanding this approach across identity and data security. Strengthening Identity Security with Security Store in Microsoft Entra Identity has become a primary attack surface - from fraud and automated abuse to privileged access misuse and posture gaps. Security Store is now embedded in Microsoft Entra, allowing identity and security teams to discover and deploy partner solutions and agents directly within identity workflows. For external and verified identity scenarios, Security Store includes partner solutions that integrate with Entra External ID and Entra Verified ID to help protect against fraud, DDoS attacks, and intelligent bot abuse. These solutions, built by partners such as IDEMIA, AU10TIX, TrueCredential, HUMAN Security, Akamai and Arkose Labs help strengthen trust while preserving seamless user experiences. For enterprise identity security, more than 15 agents available through the Entra Security Store provide visibility into privileged activity and identity risk, posture health and trends, and actionable recommendations to improve identity security and overall security score. These agents are built by partners such as glueckkanja, adaQuest, Ontinue, BlueVoyant, Invoke, and Performanta. This allows you to extend Entra with specialized identity security capabilities, without leaving the identity control plane. Extending Data Protection with Security Store in Microsoft Purview Protecting sensitive data requires consistent controls across where data lives and how it moves. Security Store is now embedded in Microsoft Purview, enabling teams responsible for data protection and compliance to discover partner solutions directly within Purview DLP workflows. Through this experience, you can extend Microsoft Purview DLP with partner data security solutions that help protect sensitive data across cloud applications, enterprise browsers, and networks. These include solutions from Microsoft Entra Global Secure Access and partners such as Netskope, Island, iBoss, and Palo Alto Networks. This experience will be available to customers later this month, as reflected on the M365 roadmap. By discovering solutions in context, teams can strengthen data protection without disrupting established compliance workflows. Across Defender, Entra, and Purview, purchases continue to be completed through the Security Store website, ensuring a consistent, secure, and governed transaction experience - while discovery and evaluation happen exactly where teams already work. Outcome-Driven Discovery, with Security Store Advisor As the number of agents and solutions in the Store grow, finding the right fit for your security scenario quickly becomes more important. That’s why we’re introducing the AI‑guided Security Store Advisor, now generally available. You can describe your goal in natural language - such as “investigate suspicious network activity” and receive recommendations aligned to that outcome. Advisor also includes side-by-side comparison views for agents and solutions, helping you review capabilities, integrated services, and deployment requirements more quickly and reduce evaluation time. Security Store Advisor is designed with Responsible AI principles in mind, including transparency and explainability. You can learn more about how Responsible AI is applied in this experience in the Security Store Advisor Responsible AI FAQ. Overall, this outcome‑driven approach reduces time to value, improves solution fit, and helps your team move faster from intent to action. Learning from the Security Community with Ratings and Reviews Security decisions are strongest when informed by real world use cases. This is why we are introducing Security Store ratings and reviews from security professionals who have deployed and used agents and solutions in production environments. These reviews focus on practical considerations such as integration quality, operational impact, and ease of use, helping you learn from peers facing similar security challenges. By sharing feedback, the security community helps raise the bar for quality and enables faster, more informed decisions, so teams can adopt agents and solutions with greater confidence and reduce time to value. Making agents easier to use post deployment Once you’ve deployed your agents, we’re introducing several new capabilities that make it easier to work with your agents in your daily workflows. These updates help you operationalize agents faster and apply automation where it delivers real value. Interactive chat with agents in Microsoft Defender lets SOC analysts ask questions to agents with specialized expertise, such as understanding impacted devices or understanding what vulnerabilities to prioritize directly in the Defender portal. By bringing a conversational experience with agents into the place where analysts do most of their investigation work, analysts can seamlessly work in collaboration with agents to improve security. Logic App triggers for agents enables security teams to include security agents in their automated, repeatable workflows. With this update, organizations can apply agentic automation to a wider variety of security tasks while integrating with their existing tools and workflows to perform tasks like incident triage and access reviews. Product combinations in Security Store make it easier to deploy complete security solutions from a single streamlined flow - whether that includes connectors, SaaS tools, or multiple agents that need to work together. Increasingly, partners are building agents that are adept at using your SaaS security tools and security data to provide intelligent recommendations - this feature helps you deploy them faster with ease. A Growing Ecosystem Focused on Security Outcomes As the Security Store ecosystem continues to expand, you gain access to a broader set of specialized agents and solutions that work together to help defend your environment - extending Microsoft Security with partner innovation in a governed and integrated way. At the same time, Security Store provides partners a clear path to deliver differentiated capabilities directly into Microsoft Security workflows, aligned to how customers evaluate, adopt, and use security solutions. Get Started Visit https://securitystore.microsoft.com/ to discover security agents and solutions that meet your needs and extend your Microsoft Security investments. If you’re a partner, visit https://securitystore.microsoft.com/partners to learn how to list your solution or agent and reach customers where security decisions are made. Where to find us at RSAC 2026? Security Reborn in the Era of AI workshop Get hands‑on guidance on building and deploying Security Copilot agents and publishing them to the Security Store. March 23 | 8:00 AM | The Palace Hotel Register: Security Reborn in the Era of AI | Microsoft Corporate Microsoft Security Store: An Inside Look Join us for a live theater session exploring what’s coming next for Security Store March 26 | 1:00 PM | Microsoft Security Booth #5744 | North Expo Hall Visit us at the Booth Experience Security Store firsthand - test the experience and connect with experts. Microsoft Booth #1843The Changing Role of Low-Fidelity (LoFi) Signals in the AI Era
Introduction Low-fidelity signals—heuristics that are cheap to compute but often ambiguous—have traditionally been viewed as a necessary annoyance in security operations. In high-volume pipelines, even a modest false-positive rate can translate into operational disruption: unnecessary blocks, costly recoveries, customer frustration, and analyst burnout from constant triage. In the supply chain scanning service, operated by the Trust and Security Services group in Microsoft, LoFi signals include URL and certificate reputation, obfuscation and packer detection, multiple YARA rule families, high-impact API usage (for example, TerminateProcess), and vulnerability detections. Any one of these may be noisy—or may correctly flag perfectly legitimate behavior. The key shift in the AI era is to stop treating LoFi hits as verdicts and start using them as decision points: triggers for deeper, contextual analysis. Two case studies: LoFi signals as routing, not verdicts Case study 1: URL reputation + LLMs—turning noisy signals into zero-day detections Our supply-chain scanning pipeline processes billions of files each day across public package registries. About 150 million files are routed through a URL reputation stage that extracts embedded URLs and evaluates them using threat intelligence plus heuristic rules. At this scale, small error rates become unmanageable: “a little noisy” turns into tens of thousands of daily alerts. Before: Signal overload Heuristic-only URL reputation produced roughly 40,000 blocking detections per day. Although many were genuine threats, the volume made it difficult to distinguish confirmed malware from false positives with confidence. Multiple heuristic layers provided partial signals, but none reliably produced a high-confidence verdict. As a result, analysts spent substantial time triaging files and tuning detection logic, weighing stricter blocking against the risk of disrupting legitimate packages and missing true malware. After: LLM-assisted signal refinement Adding LLM-based contextual analysis on top of URL reputation changed the signal-to-noise ratio. Instead of judging a URL in isolation, the model evaluates how it is used in surrounding code—an install script versus a documentation link, an obfuscated payload download versus a legitimate API call. Outcome: ~2,000× reduction in alerts—down to about 20 high-confidence blocking detections per day—saving substantial analyst time. More importantly, the remaining alerts skew toward true zero-days that other engines in the pipeline were missing. Case study 2: Windows Device Driver scanning pipelines—scaling LoFi signals into actionable detections Beyond supply-chain package scanning, LoFi-driven routing patterns also show up in third-party device driver scanning used for the Windows certification program and post publishing rescan workflows. The pipeline operates at high volume under strict performance and reliability constraints, making “scan everything deeply” unrealistic. The device driver pipeline receives about 70,000 submissions per month (January 2026 reference). From these submissions, roughly 1 million individual files are extracted and scanned. At this scale, even moderately noisy heuristics become unmanageable if treated as high-confidence detections. Before: high-volume, low-confidence heuristics Several LoFi heuristic detectors (primarily YARA rule-based) run in audit (aka telemetry-only) mode in the driver pipeline, including: Presence of network routing/manipulation (for example, network filter drivers): ~19,000 files/month Use of a process-termination API by a driver: ~5,000 files/month Obfuscated or packed driver: ~500 files/month These detectors are fast and inexpensive, but inherently imprecise. Many flagged files reflect legitimate driver behavior (packing, process termination, filtering logic), so turning every hit into enforcement would create an unacceptable volume of false positives. Without refinement, LoFi hits function best as indicators of potential risk—not actionable verdicts. After: selective escalation and targeted analysis Instead of treating every LoFi hit equally, the pipeline escalates only the top 4% of results for deeper inspection. Those samples get additional correlation and malware analyst review, which enables the creation of concrete, high-confidence signatures that can be safely enforced at scale. With this targeted escalation model: An average of ~5 new blocking detections are added per month Each detection typically identifies 10–100 malicious files Confirmed malware is blocked without broadly impacting legitimate driver submissions This approach preserves throughput while focusing scarce expert time on the most suspicious artifacts. In other words, LoFi signals stop being “detections” and become efficient filters that route the right samples into high-cost analysis—where you can then generate durable, high-confidence blocking rules. Key takeaways LoFi is a routing layer. In AI era pipelines, the goal is not to make every cheap heuristic perfectly precise—it is to use it to decide where to spend expensive compute and analyst time. Context beats indicators. LLMs can turn ambiguous URL signals into high-confidence decisions by reasoning about usage and intent, not just matching patterns. Escalate a small fraction, learn continuously. Selecting the top few percent for deeper analysis keeps throughput high and creates a feedback loop that produces enforceable signatures. Measure success by outcomes. The win is reduced alert volume and improved catch quality (for example, zero-days and durable blocking rules) rather than “more detections.” Conclusion As threat actors move faster and zero-days become more common, security systems have to make better decisions under tighter latency and cost constraints. The answer is not to replace LoFi signals with AI everywhere; it is to combine them. Cheap heuristics can cover the full surface area, while AI (and human expertise) is reserved for the small subset of events that truly deserve deeper reasoning. Both case studies illustrate the same pattern. In supply-chain scanning, LLMs transformed a 40,000-per-day alert stream into ~20 high-confidence blocks—surfacing zero-days that were previously lost in the noise. In device driver scanning, selective escalation of the top LoFi hits converts “interesting but unenforceable” heuristics into a steady stream of high-confidence blocking signatures. In practice, the most scalable security posture is a tiered one: LoFi for breadth, AI for context, and analysts for the hardest calls.Action Required: Transition from HTTP Data Collector API in Microsoft Sentinel
Microsoft Sentinel continues to evolve to provide more secure, scalable, and reliable data ingestion experiences. As part of this evolution, we want to remind customers and partners of an important upcoming change that may impact custom data ingestion and integrations like detection rules, playbooks etc. HTTP Data Collector API will no longer be eligible for Incident Support after September 2026 Starting September 14, 2026, connectors and tables that rely on the legacy HTTP Data Collector API will no longer be eligible for incident support in Microsoft Sentinel, consistent with Azure’s 2024 announcement. Any data sources, custom integrations, or connectors that continue to rely on the HTTP Data Collector API beyond this date may experience ingestion issues. We highly recommend customers transition to a supported ingestion alternative before this deadline, to avoid any service interruptions. Who is impacted? You may be impacted by this change if you are using: Custom-built scripts or applications that ingest data using the HTTP Data Collector API. Any custom data connectors (likely built as Azure Functions) with HTTP Collector API. Any data connector from the in-product Content Hub, provided by Microsoft or one of our partner ISVs, that will be rewritten prior to the API deprecation date. Classic custom log tables (usually marked type: Classic) created using HTTP Data Collector API. Recommended migration paths We recommend transitioning to supported, DCR‑based ingestion methods. The appropriate path depends on how data is currently ingested. 1. Update to the latest connector version in Content Hub (Recommended for most customers): For customers using Microsoft or partner‑provided connectors: Many existing connectors have been released with new versions using modern ingestion and are available as updated versions in the Content Hub. These newer versions use DCR‑based ingestion and are fully supported. 1.1 Identify the Connector Go to Microsoft Defender portal Navigate to Content Hub Search for the connector you are currently using, If your existing connector mentions HTTP Data Collector API. 1.2 Install the New CCF Connector Navigate to Content Hub Search for the same connector name Select the version labeled “(via Codeless Connector Framework)” Click Install/Update the CCF connector and complete the setup wizard (authentication, configuration, polling schedule, etc.) Note: As Microsoft Sentinel transitions to the Codeless Connector Framework (CCF), customers migrating from Azure Functions–based connectors should expect intentional architectural changes. These include new or updated table names and schemas using the Log Ingestion API, and a move to Data Collection Rules (DCRs) and Data Collection Endpoints (DCEs) for modern, governed ingestion. Both connectors may coexist temporarily; installing the CCF connector does not automatically remove the Azure Function connector. 1.3 Validate Data Ingestion Confirm new data is flowing into CCF backed tables. Monitor ingestion for a stabilization period (typically several days). Validate that Logs are flowing as expected, there are no ingestion errors and expected log volume is observed. 1.4 Migrate Dependent Content Update any workloads out of Microsoft provided content types that depend on the old Azure Function–based tables: Analytics rules Hunting queries Workbooks Playbooks / automations Parsers or custom queries 2. Logs Ingestion API (for custom applications and direct ingestion) For customers or ISV partners that ingest data directly into Sentinel tables using custom applications: The Azure Monitor Logs Ingestion API is the supported replacement for the legacy HTTP Data Collector API. Key benefits: Secure, OAuth‑based authentication Data Collection Rules (DCRs) for schema control Improved reliability, scalability, and governance Long‑term platform support Customers using custom ingestion pipelines should plan to migrate their applications to the Logs Ingestion API prior to the deprecation date. Migration Benefits (Azure Function → CCF) Lower Total Cost of Ownership (TCO) , no infra: saves compute cost and eliminates infrastructure maintenance. One‑time modernization: clean queries (no type suffixes) and one‑time migration with no ongoing API churn. Built‑in data shaping & quality gates: transformations (filter/modify during ingestion) plus schema validation to enforce ingestion quality. Flexible routing & modern tables: multiple destinations (route to multiple tables) with modern table format for better performance/features. Governed & future‑proof ingestion: granular RBAC (DCR + identity control), Sentinel data lake mirroring / lake‑only ingestion, and Microsoft’s supported API going forward. Summary The transition from the HTTP Data Collector API to the Azure Monitor Logs Ingestion API is essential to ensure continued data ingestion and improved security. The new API provides key benefits such as OAuth‑based authentication, data filtering and transformation during ingestion, and fine‑grained RBAC. Organizations are strongly encouraged to migrate to the new API ahead of the September 14, 2026 retirement date. Support Resources: If you are an Independent Software Vendor (ISV) and you encounter any difficulty building your Microsoft Sentinel data connector, Microsoft Security's App Assure program is available to assist. Contact us at AzureSentinelPartner@microsoft.com.