threat hunting & ti
25 TopicsIndicators enhancements: Allow/Block by certificates & more
We’re excited to share that you can now set an indicator to prevent and exclude entities based on certificate information. In addition, the alert and block action on files can now be applied on files signed by trusted publishers. We have also increased the number of custom indicators you can create from 5,000 to 15,000.
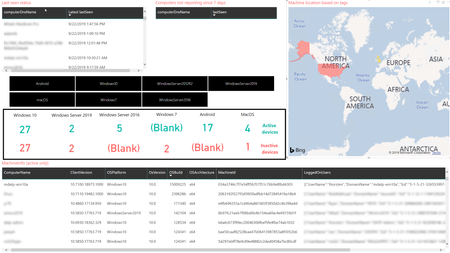
Create custom reports using Microsoft Defender ATP APIs and Power BI
Typical enterprise security operation teams often rely on dependable reporting visualisations to make critical security decisions. While Microsoft Defender ATP provides extensive visibility on the security posture of your organization through built-in dashboards, custom reporting can help you turn security data from multiple sources into insights to meet your analytical needs.How insights from system attestation and advanced hunting can improve enterprise security
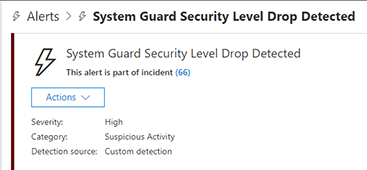
With System Guard runtime attestation and advanced hunting capabilities in Microsoft Defender ATP, defenders can identify and investigate firmware-level threats and other activities attempting to tamper with security technologiesHunting for reconnaissance activities using LDAP search filters
Attackers are known to use LDAP to gather information about users, machines, and the domain structure. Attackers can then take over high-privileged accounts by finding the shortest path to sensitive assets. Spotting these reconnaissance activities, especially from patient zero machines, is critical in detecting and containing cyberattacks.