security
430 TopicsSecuring the Non-Human Identity Attack Surface
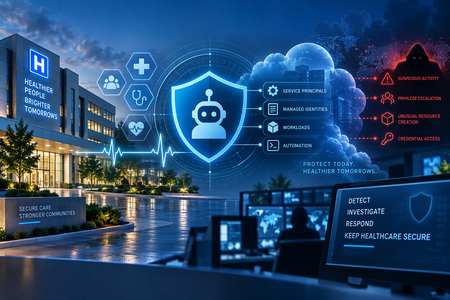
Cybersecurity teams often spend most of their efforts on securing and governing human identities: enforcing Multi-Factor Authentication (MFA), monitoring phishing campaigns, and tightening joiner-mover-leaver processes. Yet, lurking quietly inside every information technology environment is an entirely different population that frequently outnumbers employees: Non-Human Identities (NHI). These workload identities—which encompass applications, service principals, managed identities, CI/CD runners, and automated AI agents—are the connective tissue powering modern IT operations. They run deployment pipelines, automate resource provisioning, and pull data from cloud APIs. Unlike human users, however, they cannot complete an MFA prompt. When an attacker gets their hands on a service principal’s credentials, there is no push notification or phone call standing in the way. The Core Problem: Security & Governance Asymmetry Organizations routinely hold human users to rigorous security standards while letting NHIs operate with sprawling, unmonitored privileges. This disparity turns machine accounts into a high-value attack surface. Once compromised, an identity with broad infrastructure and application permissions grants immediate, high-speed execution capabilities. With AI agents proliferating, automated attacks are evolving. In late 2026, Microsoft published threat intelligence on “Storm-3168: Agentic-driven cloud attacks using compromised service principals” [1]. The immediate danger isn't a science-fiction swarm of sentient rogue AIs. Rather, it is machine-speed execution: scripts and agents performing rapid credential stuffing, instant permission discovery, and automated API reconnaissance through identities that bypass human friction. These modern threats need a modern and comprehensive solution for advanced cyber warfare. The Solution: Microsoft’s multi-layer defense mode: Entra Workload ID Premium + Defender for Cloud (Defender for Resource Manager) + Agent 365 Defending NHIs requires stopping unauthorized access at authentication and monitoring what the identity does once inside. Microsoft tackles this through a multi-layer defense strategy. Layer 1 | Control the Front Door with Microsoft Entra Workload ID Microsoft Entra Workload ID is designed specifically for non-human identities, it focuses on who gets a token and under what conditions: Conditional Access for workload identities — Restricts token issuance to specific public IP ranges and blocks requests when risk thresholds are crossed. Identity Protection for workloads — Detects risky service principals, including leaked credentials, and lets you investigate, confirm compromise, or disable the identity. App Health Recommendations — Flags stale, inactive service principals and expiring secrets before attackers exploit them. Access reviews — Forces scheduled recertification for service principals holding privileged directory roles. Layer 2 | Detect what Non-Human Identities do with Defender for Resource Manager Even with strict front-door checks, a legitimate secret can still be abused. Microsoft Defender for Resource Manager provides a behavioral detection layer for the Azure management plane, analyzing Azure Resource Manager (ARM) operations for suspicious activity that may indicate an identity has been compromised. For Non-Human Identities, Microsoft provides dedicated service-principal behavioral detections that look for suspicious use of high-risk Azure management operations. These detections span the attack lifecycle, including initial access, credential access, execution, persistence, privilege escalation, defense evasion, lateral movement, collection, and impact. This allows Defender to identify scenarios where a service principal may have valid credentials and legitimate Azure RBAC permissions, but begins using those permissions in ways consistent with an attacker. When suspicious behavior is detected, it is surfaced as a Defender for Cloud security alert, providing security teams with information about the detected activity, severity, and associated attack technique. Defender for Resource Manager can also detect surrounding indicators such as activity from suspicious IP addresses or TOR infrastructure, unusual privilege or role changes, abnormal resource creation, persistence activity, and known Azure exploitation techniques. Together, these signals help the SOC move beyond “Was this Non-Human Identity allowed to authenticate?” to the more important question: “After authentication, is this identity behaving like the expected workload or like an attacker?” A full list of the alerts provided by Microsoft Defender for Resource Manager is on the Defender for Cloud alerts reference page. [2] Layer 3 | Give AI agents an identity, governance, and security plane with Microsoft Agent 365 Unlike a traditional application that executes a relatively predictable workflow, an agent can reason, invoke tools, access corporate data, interact with other services, and take actions on behalf of a user or itself. Organizations therefore need controls that extend beyond simply authenticating the underlying application. Microsoft Agent 365 provides a control plane for discovering, governing, and securing agents across the organization: Agent registry and inventory: Establishes centralized visibility into registered agents so security and IT teams can identify agents operating across the environment rather than relying on individual development teams to track them. Connected platforms and the Agent 365 SDK extend visibility and management to agents built outside Microsoft's native agent platforms. Purpose-built agent identity with Microsoft Entra Agent ID: Gives agents a distinct identity foundation instead of treating every agent as an indistinguishable application or service principal. This allows security teams to apply controls to the agent itself and better understand which agent is requesting access. Agent ownership and sponsorship: Associates agents with accountable human sponsors. This creates an ownership model for non-human identities so an agent can be reviewed, governed, and ultimately disabled or removed when its sponsor, business purpose, or lifecycle changes. Lifecycle governance: Applies identity governance controls to agents so access does not have to become permanent simply because an agent was deployed. Organizations can govern the lifecycle from onboarding and access assignment through review and eventual removal. Governed resource access: Microsoft Entra governance capabilities such as access packages can be used to define which resources an agent should receive access to, who can request or approve that access, and how long the entitlement should remain. Conditional Access for agents: Agent-specific Conditional Access gives organizations another policy enforcement point for controlling how agent identities access protected resources. This helps move agent security away from implicit trust toward policy-based access. Agent-aware protection across Microsoft security: Agent 365 integrates the agent into Microsoft's broader security and compliance ecosystem, including Microsoft Defender and Microsoft Purview, so organizations can investigate agent-related threats, apply data security controls, and incorporate agents into existing security operations rather than creating a separate security program for AI. Activity and observability: Centralized agent visibility helps security and operations teams understand which agents exist, who sponsors them, what resources they can reach, and how they are interacting with the enterprise environment. This is critical when autonomous actions occur without a person directly initiating every transaction. Beyond outlining Microsoft's multi-layer defense controls that organizations can implement to protect their NHIs from modern threats, I also want to provide below practical principles and actionable steps, alongside Microsoft's official mitigation and protection guidance for Storm-3168. Core Principles to Harden Non-Human Identities: Prefer secretless authentication — Use managed identities for Azure workloads, and Workload Identity Federation (OIDC) to swap short-lived tokens instead of storing static credentials. Apply least privilege — Give service principals only the specific roles and scopes they need. Avoid broad Owner or Contributor assignments. Own and review them — Assign clear owners. Regularly review privileged service principals and clean up unused apps and credentials. Watch for risk signals — Use Entra Workload ID Identity Protection features to detect leaked credentials and risky sign-in behavior, and pair that with monitoring of Azure resource operations. Treat them like privileged accounts — Even though they’re not people, high-privilege workload identities deserve the same rigor you apply to admin accounts: inventory, review, and rapid response. Practical Steps to Harden Entra Workload Identities: Secure access with adaptive policies: Apply Conditional Access policies to service principals using Conditional Access for workload identities. Enable real-time enforcement of Conditional Access location and risk policies using Continuous access evaluation for workload identities. Manage custom security attributes for an app Intelligently detect compromised identities: Detect risks (like leaked credentials), contain threats, and reduce risk to workload identities and agents using Microsoft Entra ID Protection. Simplify lifecycle management: Access Microsoft Entra protected resources without needing to manage secrets for workloads that run on Azure using managed identities. Access Microsoft Entra protected resources without needing to manage secrets using workload identity federation for supported scenarios such as GitHub Actions, workloads running on Kubernetes, or workloads running in compute platforms outside of Azure. Review service principals and applications that are assigned to privileged directory roles in Microsoft Entra ID using access reviews for service principals. Mitigation and Protection Guidance for Storm-3168: “Agentic-driven cloud attacks using compromised service principals” Enable appropriate Microsoft Defender for Cloud plans for critical Azure workloads. Consider enabling workload protections relevant to the resources in your environment, including Defender for Resource Manager, Defender for Storage, Defender for Key Vault, Defender for App Service and Defender for Databases. Learn more in the Microsoft Defender for Cloud overview. Protect and continuously assess application credentials and secrets. Avoid storing service principal credentials, storage keys, connection strings, and other secrets in source code, configuration files, public repositories, issues, or other locations where they might be inadvertently exposed. Learn more in the Microsoft Entra Workload ID documentation. Rotate compromised or exposed credentials immediately and establish credential lifecycle practices. Treat credentials that have been publicly exposed as compromised, even if the original location has subsequently been edited or deleted. Removing the content does not invalidate the credential or eliminate copies retained in edit history, caches, archives, logs, or other systems. Immediately revoke or rotate the affected credentials and investigate their historical use. Where supported, organizations should favor mechanisms that reduce reliance on long-lived credentials. Learn more about protecting secrets with Defender for Cloud. Apply least privilege to service principals and other workload identities. Review the Azure RBAC permissions assigned to service principals and restrict their privileges to the resources and operations required by their applications. Learn more about best practices for Azure RBAC. Protect backup and recovery infrastructure as part of ransomware resilience. Restrict access to backup and recovery resources and closely monitor attempts to modify or remove their protection controls. Learn more about Azure Backup security best practices. Scale investigation and response with agentic defenses. Use Project Perception to help defenders deploy AI agents that investigate and respond across large, complex environments at machine speed. Strengthen security posture for AI applications and agentic systems. Use Microsoft Defender for AI Security (codename MDASH) to discover AI assets, identify vulnerabilities and misconfigurations, and reduce exposure to AI-related attack paths. The Bottom Line Non-Human Identities are no longer just “service accounts.” They are first-class identities that attackers actively target. Because they can’t use MFA and often lack strong lifecycle management, a single leaked secret or compromised pipeline can give an attacker lasting, high-impact access. Microsoft provides tools to inventory, review, risk-assess, and restrict these NHIs. Combined with least-privilege access, secretless authentication, and monitoring of what they actually do in Azure, organizations can significantly reduce their risk to modern threats. For additional details or assistance, please reach out to your Microsoft Representative. Learn More: For the latest security research from the Microsoft Threat Intelligence community, check out the Microsoft Threat Intelligence Blog. Review our documentation to learn how to prevent identity attacks, ensure least privilege access, unify access controls, and see how to enable them within your organization. Learn more about securing Copilot Studio agents with Microsoft Defender Evaluate your AI readiness with our latest Zero Trust for AI workshop. Microsoft 365 Copilot AI security documentation How Microsoft discovers and mitigates evolving attacks against AI guardrails Prompt injection protection in Microsoft Defender for Office 365 – official documentation of the prompt injection protection in Microsoft Defender for Office 365. How Microsoft discovers and mitigates evolving attacks against AI guardrails | Microsoft Security Blog Manipulating AI memory for profit: The rise of AI Recommendation Poisoning | Microsoft Security Blog – a related example of an AI-era technique observed in email traffic Defending the inbox against prompt injection attacks | Microsoft Defender for Office 365 Blog – feature announcement introducing prompt injection protection in Microsoft Defender for Office 365. Learn how Microsoft is reimagining the SOC for the agentic era with ISOC in Microsoft Defender Microsoft Entra News and Insights | Microsoft Security Blog Microsoft Entra documentation | Microsoft Learn References: [1] Microsoft Corporation. Storm-3168: Agentic-driven cloud attacks using compromised service principals | Microsoft Security Blog 2 Microsoft Corporation. Alerts for Resource Manager - Microsoft Defender for Cloud | Microsoft Learn
Introducing Windows Ready Print and Modernized Driver Selection
Windows Ready Print: A clearer path to modern printing on Windows Printing on Windows is evolving. As printing environments modernize, customers and partners are asking for solutions that are reliable, secure, and easy to manage across today’s devices. To reflect this shift and make the value of our platform clearer, we are evolving the Modern Print Platform under a new name: Windows Ready Print. Windows Ready Print highlights what matters most: a streamlined, dependable printing experience built for modern Windows environments. It represents our commitment to simplifying printing, aligning modern standards, and delivering consistent, forward-looking experiences for users, IT admins, and partners. Driving the transition to Windows Ready Print with driver selection controls At the core of Windows Ready Print is a transition away from legacy, third party drive-based workflows toward modern, standards-based printing with IPP (Internet Printing Protocol) using the Windows inbox IPP printer driver. Starting in July 2026, new printer installations will default to Windows Ready Print where supported, enabling a simpler and more reliable setup experience. This change reduces the need for traditional driver management and lays the foundation for a more scalable and predictable print experience. However, we recognize that not all environments can move to Windows Ready Print immediately. To ensure a smooth and flexible transition, we are introducing the ability for users to configure Windows to install their printers using Windows Ready Print (if supported) or the OEM printer driver during installation. You can find this setting under Settings > Bluetooth & Devices > Printers & Scanners > Default install printer using Windows Ready Print. This feature enables users and IT admins to control how Windows selects drivers when installing printers: When “Default install printers using Windows Ready Print” is enabled, Windows Ready Print installation is preferred When “Default install printers using Windows Ready Print” is disabled, default driver selection is used The configuration applies to new printer installations only, without affecting existing devices. To enable/disable this feature via group policy, go to: Launch Group Policy Editor Navigate to Local Computer Policy -> Administrative Templates -> Printers Find and select 'Configure Windows Ready Print driver ranking' -> double click to open it Select 'Enabled' (if you wish to enable Windows Ready Print driver selection) or 'Disabled' (if you wish to explicitly disable Windows Ready Print driver selection). Select Apply Select OK How driver selection configuration works with Windows protected print mode When you enable "Default install printers using Windows Ready Print”, new printer installations will default to Windows inbox IPP printer driver when supported. When you enable Windows protected print mode, printers are exclusively installed with Windows Ready Print. Devices that do not support Windows Ready Print cannot be installed. Note: When you’ve enabled Windows protected print mode, you cannot disable "Default install printers using Windows Ready Print".13KViews1like4CommentsPartner Blog | Make each Microsoft 365 Business Premium opportunity a security conversation
Small and medium-sized businesses (SMBs) want to put cloud and AI to work while protecting their people, data, and operations. Cybersecurity Awareness Month brings those priorities into focus each October, but building a secure foundation for productive, AI-ready work is a year-round business need. For Microsoft partners, that makes each Microsoft 365 Business Premium opportunity a security conversation and a path to recurring managed services. Lead with the outcomes customers need: adopt AI with confidence, strengthen protection against advanced cyberattacks, and secure sensitive data while addressing compliance requirements. Microsoft 365 Business Premium brings productivity and foundational security together. Microsoft Defender Suite for Business Premium and Microsoft Purview Suite for Business Premium extend that foundation with advanced threat protection, data security, and compliance capabilities. Together, they give you a connected Microsoft platform to assess, deploy, manage, and expand as customer needs evolve. The opportunity continues well after the initial sale. By guiding adoption, maintaining security posture, and strengthening governance, you can build repeatable managed security services that deepen customer relationships and create opportunities for recurring revenue. Security is the foundation for productive, AI-ready work Security is now a priority across the partner ecosystem and a prerequisite for nearly every customer initiative. Secure identities, protected data, threat protection, and clear governance create the foundation for productive work today and for governed AI adoption over time. That’s the thinking behind the FY27 SMB sales plays, including the “Run your business securely” security sales play. Rather than leading with a product list, start with the business outcome the customer is trying to achieve and the risk that could get in the way. The FY27 SMB partner resources provide conversation guides, pitch materials, and discovery questions you can use to turn that framing into a business case. The FY27 SMB Channel Partner Playbook extends that guidance across customer conversations, readiness, and go-to-market execution. This secure foundation also matters as customers move from isolated AI use to repeatable, governed ways of working, a core part of Frontier Transformation. For SMBs with lean IT teams, or who rely on their Managed Service Provider (MSP), an integrated approach can simplify the environment while improving visibility across identity, endpoints, data, and compliance. Partners can guide that progression by keeping security, productivity, and AI readiness connected throughout the customer relationship. Continue reading here192Views0likes0Comments
Getting first customers after publishing what actually worked for you?
I published two transactable SaaS offers earlier this month (Microsoft 365 security and compliance assessment). The technical side went fine, with good support from the ISV team. Getting the offers in front of customers is where I'm stuck. So far I've reached Rewards Tier 3 and activated the listing optimisation benefit. I understand customer references are the gate to co-sell readiness, which feels like a chicken-and-egg problem when you have none yet. For publishers further along than me: what actually produced your first few customers? Was it private offers to targeted tenants, co-sell once you had references, the Marketplace Rewards activities, or something outside the marketplace entirely? I'd rather spend my limited time on what works than keep guessing.Earn the Digital Sovereignty specialization and stand out in a growing market
Customers are raising digital sovereignty requirements earlier in the sales cycle as they navigate AI adoption, evolving regulations, cybersecurity risks, and operational resilience concerns. Microsoft partners who can confidently address these challenges can position themselves to serve as trusted advisors and capture emerging opportunities. The Digital Sovereignty specialization validates your capabilities delivering secure, compliant, and locally governed cloud solutions using Microsoft Sovereign Cloud. Demonstrate your expertise to customers seeking guidance on data control, governance, sovereign AI, cloud resilience, and regulatory requirements. As demand for sovereignty expertise grows across regulated and public sector industries, now is the time to differentiate your practice and showcase your proven capabilities. Learn how digital sovereignty is reshaping customer priorities in the blog and explore the requirements, benefits, and business opportunities associated with earning the Digital Sovereignty specialization.166Views2likes0Comments
Cracking the Code to Secure Productivity: How to Work Smarter Without Compromising Security
For years, organizations were forced to choose between productivity and security. More protection often meant more friction, while greater flexibility increased risk. Today’s digital environment demands a different model—one where security and productivity reinforce each other rather than compete. This is the idea behind secure productivity: empowering employees to work the way they need to while data, identities, devices, and systems are protected seamlessly in the background. As work becomes more distributed and threats become more advanced, organizations can no longer afford a tradeoff between speed and safety—they need both. A modern secure productivity strategy relies on AI‑powered, intelligent security that adapts to real‑world behavior. By detecting anomalies, stopping threats early, and automating routine protection, AI reduces burden on IT teams while allowing employees to stay focused. Combined with a Zero Trust approach—where every access request is continuously verified—security becomes stronger without slowing people down. Secure productivity ultimately: Reduces organizational risk Improves employee experience and confidence Supports remote, hybrid, and AI‑enabled work Accelerates innovation while protecting what matters most As AI reshapes how work gets done, a strong, intelligent security foundation ensures organizations can move forward confidently instead of cautiously. 👉 For the complete explanation, deeper insights, and supporting context, refer to: https://aka.ms/CrackingtheCodetoSecureProductivity234Views1like1CommentStrengthening Cybersecurity for Education‑Focused Nonprofits and Education Institutions
Cybersecurity is one of the most urgent priorities facing education‑focused nonprofits and education institutions today. Whether you’re a nonprofit delivering tutoring, literacy, STEM, or adult learning programs — or a school, district, or learning organization — you’re managing growing threat complexity with lean IT teams, rising ransomware risk, and sensitive learner and staff data to protect. Leaders across the education ecosystem need practical strategies that strengthen security without slowing down their mission. The Microsoft Elevate Education team is bringing you two powerful Signature Series webinars this spring to help education‑focused nonprofits and education institutions strengthen their cybersecurity posture from the inside out. Pick the topic and time that fits your day — or register for both. Webinar 1 | May 19, 2026 Preventing the Next Organization‑Wide Incident: Identity, Access, and Ransomware for Education‑Focused Nonprofits & Education Institutions Choose your session: 8:00 – 9:00 AM PT: https://msevents.microsoft.com/event?id=2868688952 4:00 – 5:00 PM PT: https://msevents.microsoft.com/event?id=1182185119 Webinar 2 | June 23, 2026 Self-Healing Security for Education‑Serving Organizations: Automated Investigation & Response with Microsoft Defender XDR Choose your session: 8:00 – 9:00 AM PT: https://msevents.microsoft.com/event?id=237608052 4:00 – 5:00 PM PT: https://msevents.microsoft.com/event?id=2738526889 Across both sessions, you'll learn how to: Reduce risk from over‑permissioned admin accounts and always‑on access Limit your organization’s blast radius through modern identity segmentation and access controls Automate threat investigation and response to contain incidents faster — even with a lean team Manage and approve remediation actions through a unified Action center Strengthen ransomware readiness using tools many organizations already own How This Benefits Education‑Focused Nonprofits Education‑focused nonprofits and education institutions face many of the same cybersecurity pressures — rising ransomware activity, increasingly sophisticated identity attacks, and the responsibility to protect sensitive learner, staff, and organizational data — often with limited resources and little room for disruption. These sessions tell the full cybersecurity story for organizations that teach, support, and deliver education: securing who has access and automating how you respond when threats occur. Together, they help nonprofits and education institutions move toward containment‑ready, resilient security operations that protect staff, volunteers, and the learners they serve. We hope to see you there. Microsoft Elevate EDU419Views0likes1Comment