phishing
79 Topics
MS Account Blocked due to OAuth Emails
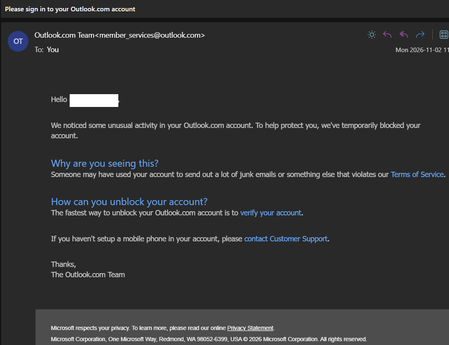
Hi! I am writing in this community forum in the event my account gets blocked again due to false positive flagging and to ensure it never happens again. Lately I've been noticing that my MS account has been constantly getting flagged for suspicious activity. Based on the patterns, it seems to be flagged when my TrueNAS server sends OAuth email alert to my own email. Specifcally, my email was blocked after 5 emails were sent in a single day, or it could be from 3 emails being sent in a single minute. This issue only started occuring recently and has never happened before during my time using TrueNAS OAuth emails, so I am not sure what may have changed to cause this. For the time being, I have disabled Outlook OAuth email alerts from TrueNAS for the time being until this bug or whatever the root cause for this has been determined. More importantly I want to discuss potential flaws during the account recovery process that may require the attention of Microsoft employee. During the attempt to recover my account and prove that I am not a bot, I had to click and hold a button. This button is not visible if MSEdge's tracking prevention is set to strict. I refreshed the page multiple times before figuring out I had to add https://account.live.com:443 as an exception. Due to the page refreshing multiple times, the account recovery itself ended up getting blocked. Possibily due to the servers mistakening this as a brute force attempt. This made the recovery process more difficult. Whenever my account is flagged, I get an email from email address removed for privacy reasons to unlock my verify my account. However, many sources indicate that this email is fraudulent and is a form of an AiTM phishing attack (sources: https://learn.microsoft.com/en-us/answers/questions/4583915/i-received-a-email-form-the-email-member-services, https://learn.microsoft.com/en-us/answers/questions/4670819/is-member-services-@-outlook-safe ) This is of course quite ironic since instead of this suspicious email address being flagged for phishing, my own legitimate account gets flagged which triggers some sort of bot reply from the suspicious email that would actually compromise my account. The email also correctly identifies my name, which I have censored. Also, if you copy the link on "verify your account", you will see https://go.microsoft.com/fwlink/?linkid=xxxxxxx. With a phishing mail like this, users who are also affected by false positive flagging for suspicious activity for using OAuth emails are at high risk for falling victim to this scam. So going back to the purpose of this post. Is there any possible way to continue using TrueNAS Outlook OAuth notifications without getting my account falsely flagged as suspicious?59Views0likes1Comment
Attack Simulation Training – Any update on Microsoft Teams phishing simulations (GA timeline)?
Hi everyone, We run Attack Simulation Training for several customers, and we're getting more and more questions about phishing simulations delivered through Microsoft Teams. As far as we know, this feature has been in private preview for quite a while now. In some tenants the Teams option is visible in the simulation wizard but greyed out. Does anyone have recent information on: General availability: is there a public preview or GA date, or a Microsoft 365 Roadmap ID we can follow? Access to the preview: is it still possible to join the private preview, and if so, how? Scope: which social engineering techniques will be supported in Teams (Credential Harvest, Link to Malware, etc.)? Will Teams payloads work with simulation automations and reporting the same way email does? Any feedback from people already in the preview, or any official update from the product team, would be much appreciated. Thanks in advance ! Julien
Proofpoint’s Core Email Protection API solution joins the Microsoft Defender ICES vendor ecosystem
Email remains the most exploited gateway for cyberattacks, as the threat landscape continues to get more sophisticated with attackers using AI to scale phishing, malware, and business email compromise. Microsoft Defender is a leading email security solution, helping organizations stay ahead of these threats with a modern, cloud-native approach. At the same time, many organizations choose to layer additional email security solutions to meet compliance requirements or align to an existing defense-in-depth strategy. This approach can strengthen resilience, but it can also add operational complexity for SOC teams. That’s why one year ago, we introduced the Microsoft Defender Integrated Cloud Email Security (ICES) vendor ecosystem, which is designed to simplify that complexity by integrating partner protections into Microsoft Defender. Today, we’re continuing to expand the ICES vendor ecosystem by adding Proofpoint Core Email Protection API. Proofpoint joins existing members Darktrace, KnowBe4, Cisco, and VIPRE Security Group. How joint customers benefit from a streamlined SOC experience in Microsoft Defender The ICES ecosystem brings trusted third-party email security verdicts and telemetry into the Defender portal through an API-based integration model. This allows Microsoft Defender to acknowledge partner verdicts on messages, apply the highest-severity determination, and surface that information in the same investigation and response workflows security teams already use. The integration with Proofpoint Core Email Protection API is designed specifically for customers who have already chosen to deploy Proofpoint’s ICES solution alongside Microsoft Defender. It supports environments where customers run both solutions and want to reduce friction for their SOC teams. By integrating Proofpoint into the ICES ecosystem, customers can now preserve their existing security strategy while improving how investigations and response are carried out day to day. "Organizations rely on both Microsoft and Proofpoint to protect their most critical communications and data. By extending Proofpoint’s interoperability across ICES, we’re delivering a more unified security experience that strengthens defense-in-depth and simplifies operations for our shared customers. This milestone reflects our commitment to joint customers worldwide.” - Tom Corn, EVP and GM, Threat Protection Group at Proofpoint Below we have outlined how Proofpoint’s ICES solution now integrates within Microsoft Defender: Unified quarantine: Quarantine is the central place where suspicious, unwanted, or malicious messages are held so they do not remain in users’ mailboxes while analysts review them. With unified quarantine, teams can view and manage quarantined email from both Defender and supported ICES vendors in one experience. The benefit is less context switching, faster triage, and a more consistent response workflow because analysts do not need to jump between separate admin consoles to understand what was held and why. In Figure 1, you can see that in the column “detection technology” ThirdPartyFiltering is listed, indicating to you that this was directly contributed by Proofpoint’s Core Email Protection API solution. Emails quarantined by Proofpoint Core Email Protection API show up in the quarantine experience in Defender, alongside Defender-quarantined emails. Streamlined operations: ICES integrations make Defender more actionable for SOC teams by extending familiar investigation experiences across Microsoft and partner-detected email. In Threat Explorer, analysts can review messages actioned by Defender and integrated partners in one place, making it easier to correlate verdicts and understand which layer acted on a message. 2 and 3: Shows how you can review emails actioned by Proofpoint by using ‘ThirdPartyFiltering’ in Threat Explorer. Click on a particular row and dive deeper into delivery and email details. In Advanced Hunting, teams can query email events that include third-party detections to investigate patterns, validate coverage, and hunt for missed or emerging threats. And on the Email entity page, analysts can see message-level details and action history, including which product took action and what verdict was assigned. Together, these experiences give teams a more complete investigation workflow without forcing them to jump between separate consoles. Reinforcing Our Commitment to Customer Choice The continued expansion of the ICES vendor ecosystem reinforces Microsoft’s commitment to supporting customers who strategically layer email security solutions. The goal of our ecosystem is making multiple solutions operationally effective together with Microsoft Defender as the shared Security Operations experience. By integrating partner signals directly into the Defender portal, customers can reduce analyst fatigue, improve consistency across email threat response, and scale their security posture while reducing the operational complexity of managing layered solutions. Learn more Get started by checking out the Defender for Office 365 ICES Vendor Ecosystem Integration Guide Read our blog: Ensure your ICES solution works seamlessly alongside Microsoft DefenderYou may be right after all! Disputing Submission Responses in Microsoft Defender for Office 365
Introduction As a Microsoft MVP (Most Valuable Professional) specializing in SIEM, XDR, and Cloud Security, I have witnessed the rapid evolution of cybersecurity technologies, especially those designed to protect organizations from sophisticated threats targeting email and collaboration tools. Microsoft Defender for Office 365 introduced an LLM-based engine to help better classify phishing emails that, these days, are mostly written using AI anyways about a year ago. Today, I'm excited to spotlight a new place AI has been inserted into a workflow to make it better…a feature that elevates the transparency and responsiveness of threat management: the ability to dispute a submission response directly within Microsoft Defender for Office 365. Understanding the Challenge While the automated and human-driven analyses are robust in Defender for Office 365, there are occasions where the response—be it a verdict of "benign" or "malicious"— doesn’t fully align with the security team's context or threat intelligence. If you are a Microsoft 365 organization with Exchange Online mailboxes, you’re probably familiar with how admins can use the Submissions page in the Microsoft Defender portal to submit messages, URLs, and attachments to Microsoft for analysis. As a recent enhancement, now all the admin submissions use LLM based response for better explainability. In the past, disputing such verdicts required separate support channels, using Community support, or manual email processes, often delaying resolution and impacting the speed of cyber operations. Introducing the Dispute Submission Response Feature With the new dispute submission response feature, Microsoft Defender for Office 365 bridges a critical gap in the incident response workflow. Now, when a security analyst or administrator receives a verdict on a submitted item, they have the option to dispute the response directly within the Microsoft 365 Defender portal. This feature streamlines feedback, allowing teams to quickly flag disagreements and provide additional context for review at the speed of operations. How It Works Upon submission of a suspicious item, Microsoft Defender for Office 365 provides a response indicating its assessment—malicious, benign, or other categorizations. If the security team disagrees with the verdict, they can select the "Dispute" option and submit their rationale, including supporting evidence and threat intelligence. The disputed case is escalated directly to Microsoft’s threat research team for further review, and the team is notified of progress and outcomes. This direct feedback loop not only empowers security teams to advocate for their organization's unique context, but also enables Microsoft to continually refine detection algorithms and verdict accuracy based on real-world input, because security is a team sport. Benefits for Security Operations Faster Resolution: Streamlined dispute submission eliminates the need for external support tickets and escalations, reducing turnaround time for critical cases. Greater Transparency: The feature fosters a collaborative relationship between customers and Microsoft, ensuring that verdicts are not final judgments but points in an ongoing dialogue. Continuous Improvement: Feedback from disputes enhances Microsoft’s threat intelligence and improves detection for all Defender for Office 365 users. Empowerment: Security teams gain a stronger voice in the protection of their environment, reinforcing trust in automated defenses. MVP Insights: Real-World Impact Having worked with global enterprises, I’ve seen how nuanced and context-specific threats can be. Sometimes, what appears benign to one organization may be a targeted attack for another, a slight modification to a URL may catch one email, but not others, as slight changes are made as billions of emails are sent. We are only as good as the consortium. The ability to dispute submission responses creates a vital safety net, ensuring that security teams are not forced to accept verdicts that could expose them to risk. It’s a welcome step toward adaptive, user-driven security operations. Conclusion The dispute submission response feature in Microsoft Defender for Office 365 is one of the most exciting features for me, because it focuses on enabling organizations striving for agility and accuracy in threat management. By enabling direct, contextual feedback, Microsoft empowers security teams to play an active role in shaping their defenses. As an MVP, I encourage all users to leverage this feature, provide detailed feedback, and help drive the future of secure collaboration in the cloud. You may be right after all. _________ This blog has been generously and expertly authored by Microsoft Security MVP, Mona Ghadiri with support of the Microsoft Defender for Office 365 product team. Mona Ghadiri Microsoft Security MVP Learn More and Meet the Author 1) December 16th Ask the Experts Webinar: Microsoft Defender for Office 365 | Ask the Experts: Tips and Tricks (REGISTER HERE) DECEMBER 16, 8 AM US Pacific You’ve watched the latest Microsoft Defender for Office 365 best practices videos and read the blog posts by the esteemed Microsoft Most Valuable Professionals (MVPs). Now bring your toughest questions or unique situations straight to the experts. In this interactive panel discussion, Microsoft MVPs will answer your real-world scenarios, clarify best practices, and highlight practical tips surfaced in the recent series. We’ll kick off with a who’s who and recent blog/video series recap, then dedicate most of the time to your questions across migration, SOC optimization, fine-tuning configuration, Teams protection, and even Microsoft community engagement. Come ready with your questions (or pre-submit here) for the expert Security MVPs on camera, or the Microsoft Defender for Office 365 product team in the chat! REGISTER NOW for 12/16. 2) Additional MVP Tips and Tricks Blogs and Videos in this Four-Part Series: 1. Microsoft Defender for Office 365: Migration & Onboarding by Purav Desai 2. Safeguarding Microsoft Teams with Microsoft Defender for Office 365 by Pierre Thoor 3. (This blog post) You may be right after all! Disputing Submission Responses in Microsoft Defender for Office 365 by Mona Ghadiri 4. Microsoft Defender for Office 365: Fine-Tuning | Real-world Defender for Office 365 tuning that closes real attack paths by Joe Stocker Learn and Engage with the Microsoft Security Community Log in and follow this Microsoft Defender for Office 365 blog and follow/post in the Microsoft Defender for Office 365 discussion space. Follow = Click the heart in the upper right when you're logged in 🤍 Learn more about the Microsoft MVP Program. Join the Microsoft Security Community and be notified of upcoming events, product feedback surveys, and more. Get early access to Microsoft Security products and provide feedback to engineers by joining the Microsoft Customer Connection Community. Join the Microsoft Security Community LinkedInDefending the Inbox Against Prompt Injection Attacks
AI assistants are quickly becoming part of everyday work—summarizing emails, drafting responses, triaging requests, and even potentially acting across connected business systems. As email becomes an automated input to AI systems, it can also become a new attack surface. Attackers no longer need to convince a human to click; they can target the AI. This shift changes how email threats operate and why traditional protections aren’t enough on their own. Publicly disclosed research—Morris II, EchoLeak, and a steady stream of indirect prompt injection findings—shows this isn’t theoretical. Email can be the highest-volume, lowest-friction ingress channel into your AI estate, and it needs its own purpose-built control. Today, we’re announcing a new capability in Microsoft Defender that addresses this. Microsoft Defender can now detect and isolate malicious AI instructions embedded in email, commonly referred to as prompt injection, before delivery. This reduces the risk of prompt injection reaching the inbox and activating against AI systems. By detecting these threats, organizations are better protected from prompt injection-driven compromise and unintended data exposure. Rather than responding to attacks after an AI system has already processed them, Defender can remove the threat at the earliest control point: the inbox itself. When attackers stop phishing humans and start targeting AI For decades, email attacks relied on social engineering—convincing a user to click a link, open an attachment, or follow instructions. AI assistants connected to email change that model. For illustrative purposes, an attack chain could look like this: An attacker can send an email containing hidden instructions often invisible to a human because they’re encoded, white-on-white, zero-width Unicode, or embedded in HTML the renderer hides. The recipient, or an autonomous agent, asks Copilot to summarize or process the unread mail or inbox. The AI could unknowingly follow the embedded instructions, which can trigger actions like exposing sensitive data, calling tools, or poisoning downstream context. This emerging class of attack, commonly referred to as indirect prompt injection, represents a clear evolution of email‑borne risk and calls for protections specifically designed for AI‑targeted threats. How Microsoft Defender protects against prompt injection attempts Protection against prompt injection is built into Defender’s existing email security pipeline, allowing organizations to reduce AI-targeted threats without requiring new tools, workflows, or operational complexity. Helps stop attacks before delivery – Malicious AI instructions embedded in emails can be detected and quarantined before they reach the inbox. Reduces downstream AI exploitation – By blocking these messages at ingress, prompt injection attempts are less likely to become available to Copilot, Microsoft 365 agents, or any AI tool grounded in Exchange Online data. Starts working automatically – For eligible customers, protection is enabled by default, allowing security teams to benefit without policy changes or admin opt-in. How to view detections Detections are classified under the existing High Confidence Phish verdict with a new Detection Technology value: Prompt Injection Protection. Analysts will be able to interact with this experience across familiar Defender surfaces: Email Quarantine – Messages containing detected prompt injection are isolated before delivery, with the relevant detection technologies visible as part of the message details. Explorer and email entity pages – Analysts can review the full message context, investigate why it was flagged, and understand how the threat fits within the broader email investigation flow. Securing the AI data perimeter Email can be the first, and highest-volume, entry point into AI systems, making it a critical control plane for preventing AI-driven compromise. But email is only the beginning. As AI systems increasingly interact with documents, collaboration platforms, and third‑party data sources, protecting the AI data perimeter becomes critical. Detecting and blocking prompt injection at the inbox represents an important step toward that future—where Defender can stop AI‑targeted threats wherever untrusted data meets autonomous systems. As the threat landscape continues to evolve, Defender is designed to evolve with the threat landscape, so organizations can deploy AI more securely while helping reduce new attack risks. Get started Prompt injection protection is now in public preview. For eligible customers, protection is enabled automatically without requiring policy changes or additional configuration. To learn more about this feature, visit our documentation.
No way to automate restoring user‑reported emails after “no threats found”
When a user reports an email as phishing in Defender, the message gets moved to Deleted Items. After we triage it, if we mark it as “no threats found,” there’s no way to push it back to the user’s inbox as part of that workflow. That creates a bit of a broken experience: User is told the email is safe with our customized email response, but has to go find it themselves In a lot of cases they don’t (Outlook search won’t find it) We end up with follow‑ups like “where did it go?” Technically we could restore the email as part of our triage process, but that just shifts the effort onto the SOC. It doesn’t scale, and it’s not really the right place for that work. We have tried to create an automation to do this, but we have not been able to create an advanced hunting query based on our triage result that can then trigger an action to restore it to the mailbox. So we end up choosing between: Users having a bad experience, or Analysts doing manual mailbox work Neither is ideal. Other platforms (like Proofpoint) handle this end‑to‑end — once something is confirmed clean, it can be returned to the user automatically. Right now Defender stops at classification instead of completing the workflow. Is there a reason this isn’t wired in, or anything on the roadmap to address it?
Microsoft Defender (GCC) - User Submitted "Mark and Notify" for Third Party Phishing Simulations
Our Microsoft 365 tenant is in the GCC environment, and we use a third party phishing simulation platform along with the built in Outlook Report Message button (not a third party reporting add in). When a user correctly reports one of our simulated phishing emails, the message appears in Microsoft Defender > User Submitted as expected. The problem is what happens next. When we select Mark and notify, the only available options are: Phishing Spam No threat found There is no option to notify the user that the email was actually part of a phishing simulation. This creates a difficult situation: If we choose No threat found, Defender tells the user the message was safe, making it appear they incorrectly reported the email even though they did exactly what we trained them to do. If we choose Phishing, the user receives the correct feedback, but the message is counted as a real phishing event, affecting our Defender metrics and potentially generating false incidents and reporting. It feels like we're stuck in a design loop where neither option provides the desired outcome. My questions are: Is there a supported way in Microsoft Defender (particularly GCC) to notify users that a reported message was a simulated phishing email when using the native Outlook Report Message button? Is this capability available in Commercial tenants but not GCC, or is it unavailable across all environments? If this functionality does not exist, what is the recommended process for submitting a feature request specifically for the GCC version of Microsoft Defender? This seems like a valuable enhancement for organizations that use third party phishing simulation platforms while relying on Microsoft's native reporting experience. Has anyone else found a good workflow for this scenario?Enable per‑user language selection for phishing simulation emails and landing pages
We use Attack Simulation Training to deliver phishing simulations to a global, multilingual user base. While Microsoft Defender supports multi‑language content, phishing simulation emails and landing pages are currently delivered in a single selected language per campaign. We are requesting a feature that allows phishing simulation emails and associated landing pages (including credential‑harvest pages) to automatically render in each user’s preferred language, based on: Outlook mailbox language settings, and/or Microsoft Entra ID user language preferences This capability would: Improve realism and accuracy of phishing simulations Ensure users experience simulations in the same language they normally work in Improve behavioral measurement in global organizations Reduce the need to create and manage multiple parallel simulations by language Providing consistent, per‑user language alignment across simulation emails, landing pages, and follow‑up training would significantly enhance the effectiveness of Attack Simulation Training for large, multilingual enterprises.526Views2likes2CommentsMicrosoft Defender for Office 365: Fine-Tuning
In incident response, most business email compromise doesn’t start with “sophisticated zero-day malware.” It starts with configuration gaps: forwarding mail outside the tenant, users clicking through Safe Links warnings, impersonation policies left at day-one defaults, or post-delivery cleanup still relying on a human analyst at 2:00 AM. Those gaps are what attackers actually exploit. This blog covers our top recommendations for fine-tuning Microsoft Defender for Office 365 configuration from hundreds of deployments and recovery engagements: Core fine-tuning actions every email or security admin should land right now Data-driven bulk mail tuning (BCL and Bulk Mail Insights) Impersonation and anti-phishing policy hygiene for executive protection Automate post-delivery cleanup by enabling Automated Remediation Each section includes a short video and practical guidance you can apply immediately in Microsoft Defender for Office 365. These recommendations align with Microsoft’s “secure by default” direction: applying the Standard and Strict preset security policies to users, using Configuration analyzer to catch configuration drift, and enforcing least-privilege release of high-risk mail. When possible, enable the Preset security policies to give you Microsoft’s recommended settings for Safe Links, Safe Attachments, Anti-Phishing, and Anti-Spam. If you use custom policies (or if you exclude users from the Presets) then use Configuration analyzer regularly to compare custom policies to the Standard/Strict baselines, since those get updated as Microsoft updates the Preset policies. Core Fine-Tuning Checklist for Defender for Office 365 This section highlights six controls we recommend implementing broadly. These are “day one hardening” items we repeatedly validate with customers. Block automatic external forwarding by default Attackers often create hidden inbox rules that quietly forward mail (invoices, purchase orders, wire info) to an external account they control. Use outbound spam policies to block automatic external forwarding for the entire org and then create tightly scoped exceptions only for the handful of mailboxes that legitimately need it. This prevents data leakage and payment fraud scenarios where mail auto-forwards out of your tenant without anyone noticing. Although this setting is on by default (“System Controlled” means that external forwarding is disabled), we’ve found many tenants where this was disabled because the admin didn’t know how to create a custom policy for authorized forwarders. The trick is to order custom outbound policies to run as a higher priority than the default outbound policy which should be set to block auto-forwarded emails. It is a good idea to regularly review the auto forwarded message report (located in the Exchange Admin Center). Use Enhanced Filtering for Connectors (“skip listing”) when necessary If you’re routing inbound mail through a third-party Secure Email Gateway or an on-prem hop before Microsoft 365, Defender will see that intermediary as the source IP instead of the original sending IP, which degrades anti-spoofing effectiveness.Enhanced Filtering for Connectors — also called skip listing — lets Microsoft 365 look past that last hop and evaluate the real sending IP and headers, so SPF / DKIM / DMARC and anti-spam logic work correctly. This setting does not support centralized mail routing (unless the routing is linear; see the Enhanced Filtering for Connectors learn article), so make sure you are not using that before enabling Enhanced Filtering. Centralized routing is sometimes used by organizations running a hybrid Exchange deployment, connecting Exchange Online with an on-premises Exchange Server organization. Important: Do this instead of blanket SCL -1 transport rules that “bypass spam filtering for anything coming from our gateway.” Over-bypassing means phishing that slipped through the third-party filter can sail straight to user inboxes, which Microsoft specifically warns against. Turn on Safe Attachments protection beyond email (SharePoint, OneDrive, Teams) In the Safe Attachments “Global settings,” make sure Defender for Office 365 is set to protect files in SharePoint, OneDrive, and Microsoft Teams. When enabled, if a file is identified as malicious, Defender automatically locks the file in-place so users can’t open it in Teams or OneDrive. This gives you malware detonation and containment in collaboration channels, not just email. This step closes a gap we still see a lot: customers protect mail attachments well, but shared files and Teams chats are wide open. In the 1st part of this blog series, Microsoft MVP Purav Desai describes (here) how to prevent users from downloading malicious files by running a SharePoint PowerShell cmdlet: Set-SPOTenant -DisallowInfectedFileDownload $true Don’t let users click through Safe Links warnings Safe Links rewrites and time-of-click scans URLs in mail, Office apps, and Teams. In the Safe Links policy, clear “Let users click through to the original URL.” That prevents the classic “I know it says it’s malicious, but I really need to see it…” moment. Users get blocked instead of “warned but allowed.” This setting is also enforced in Microsoft’s Standard AND Strict preset security policies where click-through is explicitly disabled. Go beyond the default Common Attachment filter The anti-malware policy’s Common Attachment filter blocks known dangerous file extensions (executable content, scriptable content, etc.). Microsoft ships a default list (historically 50+ high-risk extensions), and you can customize it to block additional file types common in malware delivery, like HTML droppers or password-protected archives. Messages with those file types are treated as malware and quarantined. Do this centrally rather than relying on users to “spot a suspicious attachment.” Automation beats user judgment here. Use custom quarantine policies that require admin approval (instead of self-release) If you are not using the Preset Policies, you can create a quarantine policy to customize the user experience with quarantined messages. For anything phishing-related, I recommend creating a custom policy that allows the user to “request release from admin.” That means users can raise a hand if they think something should not have been quarantined, and an Incident is created for administrators to review before it is released. To me, this strikes the best balance between security and productivity. This keeps containment intact and gives the SOC final say. It also creates an auditable workflow: who asked for release, who approved it, and why. Bulk Mail Insights: Tune BCL using your tenant’s mail Bulk email (“graymail”) is noisy. Payroll alerts and benefits notifications are legitimate, but they look exactly like phishing. At the same time, true marketing email (graymail) are also bulk. The traditional response (“just whitelist the sender so users stop complaining”) often opens the door for attacker-looking mail to get delivered straight to executives. Defender for Office 365 gives you something better: Bulk Mail Insights (a.k.a. Bulk senders insight). This report shows, over the last 60 days, how much mail at each Bulk Complaint Level (BCL 1–9) was delivered vs. blocked, which senders are generating volume, and where users are likely to experience false positives or false negatives. You can interactively simulate raising or lowering the bulk threshold and immediately see, “If we tighten BCL, how many more messages get quarantined? How many of those were probably junk? How many were probably wanted?” Why this matters: You stop tuning bulk mail based on anecdotes and start tuning based on real telemetry from your own tenant. You can justify decisions to leadership and audit (“We set BCL at X because here is the simulation showing false positive/false negative impact”). You avoid blanket allow rules. Instead, you adjust bulk thresholds for legitimate high-volume senders while keeping stricter actions for everyone else. Note: You can modify the BCL threshold in your default or custom anti-spam policy, but you can’t change it inside the Standard (BCL:6) or Strict (BCL:5) preset security policies themselves. Standard and Strict are already aligned to Microsoft’s recommended baselines. Additional Links: https://security.microsoft.com/senderinsights https://learn.microsoft.com/en-us/defender-office-365/anti-spam-bulk-senders-insight https://learn.microsoft.com/en-us/defender-office-365/mdo-deployment-guide#step-2-configure-threat-policies https://learn.microsoft.com/en-us/defender-office-365/preset-security-policies#policy-settings-in-preset-security-policies https://learn.microsoft.com/en-us/defender-office-365/recommended-settings-for-eop-and-office365 https://www.microsoft.com/en-us/security/blog/2025/07/17/transparency-on-microsoft-defender-for-office-365-email-security-effectiveness/ Anti-Phishing / Impersonation Tuning: Protect the people attackers actually spoof Business email compromise very often looks like this: “Hi, can you handle this payment today?” sent from an address that looks like your CFO or CEO. Microsoft Defender for Office 365 includes targeted impersonation protection, but it only really works if you target your most targeted executives. Here are five pitfalls we see over and over: Empty or stale VIP list Populate “users to protect / high value targets” with executives, finance approvers, legal, anyone authorized to move money or data. Review it monthly. Roles change, and you only get a finite number of protected users (for example, ~350 entries). An out-of-date list silently weakens protection for the people attackers actually impersonate. Phishing email threshold stuck at 1 forever We find organizations that are not using the preset policies have left their phishing threshold values at the default “1” because of initial false positives. We recommend raising it to match the Standard Preset (“3”) or Strict (“4”). Weak action If suspicious “CFO” mail just goes to Junk, users can still act on it. High-confidence impersonation of executives should be quarantined with AdminOnly or request-release workflows, not left in end-user control. Tie this back to the custom quarantine policies (discussed later in this article). Common-name overload If your CEO’s name is something extremely common, you’ll get noise. Expect it. Don’t “turn off” protection for that name — add that address to the Trusted Senders otherwise it will be blocked as an impersonation attempt. Use Trusted Senders / Trusted Domains for known-good partners and vendors so you keep protection high without drowning in alerts. Add only legitimate senders/domains to the Trusted Senders or Trusted Domains instead of lowering enforcement. No scheduled review This control can’t be “set and forget.” Put impersonation tuning and spoof intelligence review on a monthly checklist. That lets you catch new vendors pretending to be finance, new “urgent wire” lure patterns, and any drift from Standard / Strict baseline that Configuration analyzer will also call out. When done right, impersonation protection is not just “spam reduction.” It’s payment fraud prevention. Automated Investigation & Response (AIR): Let Defender remove malicious email before your SOC has to! One of the biggest wins you can land quickly is letting Microsoft Defender for Office 365 automatically remove clusters of malicious messages — without waiting for analyst approval on every single item. Here’s how it works. Defender’s Automated Investigation and Response (AIR) groups messages into “clusters” based on shared indicators like the same malicious URL or malicious file hash. If you opt in to automatic remediation for those cluster types, AIR will go find every matching copy of that threat across the tenant and soft-delete those messages, not just the one that triggered the alert. Why this matters: It turns post-delivery cleanup into something that happens immediately instead of “after Tier 1 has time to review.” It removes known-bad messages from user mailboxes (and related collaboration surfaces like Teams) before a target can click. It dramatically cuts the classic “Did anyone else get this?” manual hunt-and-purge work that burns out SOC analysts. When you configure AIR automation settings in the Microsoft Defender portal (Settings > Email & collaboration > MDO automation settings), you’ll see checkboxes for “Similar files” and “Similar URLs.” Selecting those opts you into automatic soft delete for those clusters. Today, soft delete is the default supported action for these automatic remediations, enabling administrators to undo a deletion, if necessary. This is Defender for Office 365 Plan 2 / Microsoft 365 E5 functionality, and it’s exactly the kind of “secure operations by default” Microsoft has been pushing: detect, contain, and clean up automatically, then let humans investigate with context instead of manually chasing every copy of a phish. This automation triggers when malicious clusters are detected. For automating the classification and triage of user-submitted phishing incidents, check out the Security Copilot Phishing Triage Agent (Preview). Additional Links: GA Announcement: https://techcommunity.microsoft.com/blog/-/auto-remediation-of-malicious-messages-in-automated/4418047 Docs: https://learn.microsoft.com/en-us/defender-office-365/air-auto-remediation Final Thoughts Defender for Office 365 is more than “email filtering.” It’s part of your security operations surface. The decisions you make about automated remediation (AIR), bulk mail thresholds, Safe Links/Attachment behavior, outbound forwarding, connector hygiene, quarantine policy, and impersonation tuning directly determine how easy — or how hard — it is for an attacker to penetrate your organization. Microsoft’s current guidance is clear: Apply Standard or Strict preset security policies so users get the recommended protections by default (for example, Safe Links with no click-through). If you must use a custom policy, review the recommendations from the Configuration analyzer monthly for new recommendations, or to catch and correct drift whenever someone weakens a control. Align internal procedures with the excellent Security Operations Guide for Defender for Office 365. Lock down quarantine so only admins can release high-risk messages, with an auditable “request release” path for users. Turn on automated remediation so Defender can remove malicious clusters of messages before anyone clicks. Organizations that land these basics are in a dramatically better position during an incident. Instead of “Who clicked the link?” you can say, “AIR already pulled it, users were blocked from clicking through, outbound forwarding is disabled, and impersonation of the CFO is quarantined for admin review.” That’s what “secure by default” actually looks like in production. ________ This blog was authored by Joe Stocker, Microsoft Security MVP and Founder of Patriot Consulting Technology Group, in partnership with the Microsoft Defender for Office 365 product team, including Paul Newell, Senior Product Manager, Microsoft Defender for Office 365. Joe Stocker Microsoft Security MVP Learn More and Meet the Author 1) December 16th Ask the Experts Webinar: Microsoft Defender for Office 365 | Ask the Experts: Tips and Tricks (REGISTER HERE) DECEMBER 16, 8 AM US Pacific You’ve watched the latest Microsoft Defender for Office 365 best practices videos and read the blog posts by the esteemed Microsoft Most Valuable Professionals (MVPs). Now bring your toughest questions or unique situations straight to the experts. In this interactive panel discussion, Microsoft MVPs will answer your real-world scenarios, clarify best practices, and highlight practical tips surfaced in the recent series. We’ll kick off with a who’s who and recent blog/video series recap, then dedicate most of the time to your questions across migration, SOC optimization, fine-tuning configuration, Teams protection, and even Microsoft community engagement. Come ready with your questions (or pre-submit here) for the expert Security MVPs on camera, or the Microsoft Defender for Office 365 product team in the chat! REGISTER NOW for 12/16. 2) Additional MVP Tips and Tricks Blogs and Videos in this Four-Part Series: Microsoft Defender for Office 365: Migration & Onboarding by Purav Desai Safeguarding Microsoft Teams with Microsoft Defender for Office 365 by Pierre Thoor You may be right after all! Disputing Submission Responses in Microsoft Defender for Office 365 by Mona Ghadiri (This post) "Microsoft Defender for Office 365: Fine-Tuning" by Joe Stocker Learn and Engage with the Microsoft Security Community Log in and follow this Microsoft Defender for Office 365 blog and follow/post in the Microsoft Defender for Office 365 discussion space. Follow = Click the heart in the upper right when you're logged in 🤍 Learn more about the Microsoft MVP Program. Join the Microsoft Security Community and be notified of upcoming events, product feedback surveys, and more. Get early access to Microsoft Security products and provide feedback to engineers by joining the Microsoft Customer Connection Community. Join the Microsoft Security Community LinkedIn