messaging
826 TopicsHow to Validate That Your BizTalk SB-Messaging Adapter Is Really Using AMQP
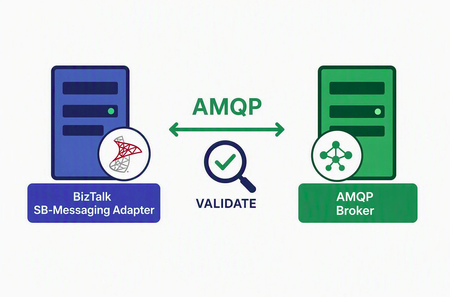
On September 30, 2026, Azure Service Bus stops accepting the Service Bus Messaging Protocol (SBMP) — the protocol the BizTalk SB-Messaging adapter has always used. The failure mode is not a warning in a log file; it is a refused connection. To keep those integrations running, a BizTalk Server 2020 hotfix adds a new Azure.Messaging.ServiceBus AMQP implementation to the adapter in place of the legacy SBMP path. This post walks through how to validate the hotfix was successfully deployed and is using AMQP and not SBMP. Required baseline: BizTalk Server 2020 with Cumulative Update 6 or Cumulative Update 7 installed, plus the SB-Messaging AMQP hotfix — KB5091379, obtained by opening a Microsoft support case. The hotfix is not offered through Windows Update or the regular CU download, and it will not install on a CU5 or earlier baseline. Every node in the BizTalk group needs it. A multi-server group will happily run the affected host instance on an unpatched node, and your test may land on the one server where the fix is not active. Patch and restart host instances everywhere, then record the edition, CU level, hotfix number, and component build per server. Hotfix location: https://1drv.ms/f/c/cac4b5f5988b8228/IgCrzn_KTaZ8T5tuKmcdPgXxARuOLcGHDhxVLgeysj44GWE?e=w5AcpM Once the baseline is confirmed, test in a non-production environment that reproduces production topology, authentication, and the full network path — proxy, firewall, private endpoint, and DNS. And list every materially different configuration you intend to validate: each send port and receive location, queue, topic, and subscription usage, 32-bit versus 64-bit hosts, and features such as sessions, ordered delivery, or transactions. A green result on one port does not validate the others. Method 1: Verify the active connection on port 5671 (recommended) The adapter selects AMQP over TCP, and Azure Service Bus uses TCP port 5671 for AMQP over TLS. Correlating an established 5671 connection with the correct BTSNTSvc or BTSNTSvc64 process demonstrates that the BizTalk host is using the AMQP transport. Run elevated PowerShell while the receive location is enabled and actively polling: $hostProcesses = Get-Process BTSNTSvc, BTSNTSvc64 -ErrorAction SilentlyContinue Get-NetTCPConnection -State Established -RemotePort 5671 | Where-Object OwningProcess -in $hostProcesses.Id | ForEach-Object { $process = Get-Process -Id $_.OwningProcess [pscustomobject]@{ Process = $process.ProcessName ProcessId = $_.OwningProcess LocalAddress = $_.LocalAddress LocalPort = $_.LocalPort RemoteAddress = $_.RemoteAddress RemotePort = $_.RemotePort State = $_.State } } Expected result: Process is BTSNTSvc or BTSNTSvc64. Remote port is 5671. State is Established. The remote address resolves to or corresponds to the Service Bus namespace. What an empty result means: not much, on its own. An empty result is inconclusive, not a failure. Confirm the port or receive location is enabled, the host instance is running, traffic is actually flowing during the check, and that DNS, firewall, or private endpoint rules permit the connection — then repeat. One important exception: if your environment routes AMQP over WebSockets on TCP 443, you should not expect a 5671 connection at all. In that case skip to Method 2. Method 2: Capture adapter traces When the connection view is unavailable or ambiguous, the trace is the more definitive answer, because it shows which code path executed rather than which socket happened to be open. BizTalk adapter tracing uses ETW through BT.Trace.Tracer, and entries containing [SBMessaging-AMQP] confirm that the new AMQP-specific implementation executed. Start BizTalk adapter tracing immediately before the test — not hours earlier. Send or receive a single, uniquely identifiable test message through the target port or receive location. Stop tracing as soon as the message completes. Search the captured output for [SBMessaging-AMQP] entries inside the test window, and match them to the host instance and configuration you were exercising. Method 3: Block the legacy SBMP ports Methods 3 and 4 are corroborating tests, not proof, and belong in an isolated environment. Legacy SBMP commonly uses TCP ports 9350 through 9354. If the isolated AMQP workload continues to operate while those ports are blocked and TCP 5671 remains available, the result corroborates that the workload does not depend on SBMP. Record the original firewall rules before you start and restore them immediately afterwards — this test has a real blast radius if it escapes the test subnet. Method 4: Large message functional test In Basic and Standard tiers, the maximum message size is 256 KB, regardless of SDK or protocol, so this test does not apply there. In Premium, the legacy SBMP path supports messages only up to 1 MB, whereas AMQP supports larger messages up to the entity’s configured maximum of 100 MB. Successfully processing a Premium message larger than 1 MB therefore provides supplementary evidence that the adapter is using AMQP. Read a failure carefully: entity limits, timeouts, and pipeline constraints all produce the same symptom, so a failed large-message test is not by itself evidence that the hotfix did not take. Verify payload integrity and the event log, then remove the test message and restore any temporary entity settings. Do not stop at the protocol Confirming that AMQP is in use answers the transport question. It does not answer whether your solution still behaves the same way. AMQP and SBMP differ in a handful of behavioural details, so before you call the validation complete, run the scenarios your integrations depend on and compare against a pre-change baseline: Send and receive across each representative queue, topic, and subscription path, checking message body and application-property fidelity. Peek-lock completion, abandon, defer, dead-letter, and retry behaviour, plus sessions, ordering, transactions, and duplicate detection where you use them. Authentication renewal, and recovery after a host instance restart or a brief network interruption. Throughput and latency within your accepted baseline, with no new event log errors, suspended instances, duplicates, or lost messages.134Views0likes2Comments
How to receive app mentions only from a channel, while having the consent to read user messages?
We're building a Teams bot (Azure Bot + Entra app) that a customer adds into a standard Teams channel. Members @mention the bot and it replies in the same thread. To make replies useful, when the bot is mentioned we want to read recent messages in that thread for context, including messages where the bot was not mentioned. We have two requirements that appear to be in tension, and we'd like your guidance on the best-supported way to satisfy both: a. Delivery: we want Teams to send our bot only the activities where it is @mentioned (not every channel message), to avoid unnecessary inbound load and Bot Framework rate-limit pressure in busy channels. b. Context read: on those mention turns, we want to read recent thread messages via Microsoft Graph (/teams/{team}/channels/{channel}/messages/{id}/replies). We've identified two approaches, each with their drawbacks: a. RSC (ChannelMessage.Read.Group) - all channel messages; team-scoped & consented by team owner at install (low friction) Concern: RSC forces delivery of every channel message; heavy backend filtering + bot framework rate-limit risk b. App permission (ChannelMessage.Read.All) - @mention-only; tenant-wide consent; tenant-admin consent Concerns: setup friction (admin consent URL, per app per tenant); read grant spans all standard channels, including ones the app isn't a member of Our core question: Option 1 gives the delivery we don't want but the scoping we like; Option 2 gives the delivery we want but a tenant-wide read grant we'd prefer to avoid. Specifically: Is there any supported way to keep @mention-only delivery and a channel-scoped (RSC-style) read grant, i.e. decouple RSC's message delivery from its read authorization? Can the tenant-wide read in Option 2 be narrowed to specific teams/channels (e.g., via a Teams application access policy or any resource-scoping mechanism), so the app can only read where it's intended to operate? Given our two requirements, which approach does Microsoft recommend, and is there any option we've missed? TIA!15Views0likes0CommentsTeams Gets Messaging Reminders
The Teams Remind Me feature is a new action available to allow users to create future reminders for chat and channel messages. When the set time comes around, Teams notifies the user about the marked messages, with the intention that users can pick up a topic discussed in a chat or channel conversation. It’s a good idea that’s similar to the way that email reminders work. The only wonder is why reminders have not appeared in Teams before now. https://office365itpros.com/2026/09/16/remind-me-teams/117Views0likes0Comments
Why someone cannot see/chat after leaving the meeting?
Hi folks, My company has some vendors. I setup the Teams meetings with all of them. They all called in using their company domain emails. After the call ends, one of the vendor always got kicked out and it displays the message saying [Name] no longer has access to the chat. However, other users from other vendors still remain in the chat and can communicate. The settings from that vendor company is as attachment. And I confirmed they use their company email, not a personal email or join as Guest. Does anyone know what the issue is?Solved133KViews5likes34Comments
Teams missing GIF option in messaging
This morning we noticed the GIF option in Teams messaging is missing org wide. Desktop and Web client. Old messages that were sent with a GIF display as a link now instead of the image Our global org policy in the Admin porta is set to On Anyone else seeing this?Solved32KViews16likes39CommentsTeams Clamps Down on MOERA-Only Tenants
The latest restriction on tenants using MOERA (service domain) addresses in production is that Teams will restrict external collaboration from September 2026. At this point, there is zero sense in any organization using a MOERA-only tenant for production purposes. Restrictions in Exchange Online and Teams should drive that point home, and the likelihood is that further clampdowns will follow in the future. https://office365itpros.com/2026/09/02/moera-only-tenants-external-collab/153Views0likes0Comments
Teams Copying text includes persons name
Hello, sometimes at my work we send each other links to files/folders on our internal server. The only problem is in teams when you do that you get the persons name instead of the link. So they sent me a link to a folder, I select the link in the text and copy it. However if past that into windows explorer I just get the time and their name. [15:12] Firstname Lastname Is there a way to get it to not include the Firstname Lastname when you copy a message? kind regards, AndrewSolved48KViews17likes61CommentsWhat if Teams isn’t too complicated — but simply being compared to the wrong product?
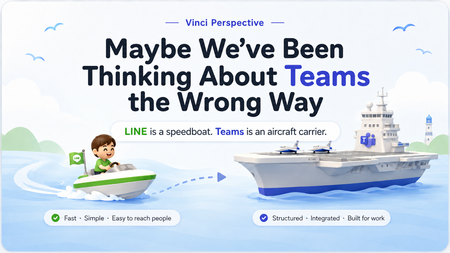
Many users first experience Microsoft Teams through meetings, chat, and file sharing. So it feels natural to compare Teams with messaging apps. But I’ve started to wonder whether that comparison itself shapes how people experience Teams. In markets such as Taiwan, Japan, and Thailand, LINE is deeply embedded in everyday communication. For those unfamiliar with it, LINE is a widely used consumer messaging app in these markets. When users bring that same mental model into Teams, a familiar question appears: “Why does Teams have to be so complicated?” But what if that isn’t quite the right question? I explored the idea in this short interactive page: Maybe We've Been Thinking About Teams the Wrong Way https://teams-vs-line-vinci.vinciwang.chatgpt.site/en/teams-vs-line One analogy sits at the center of it: LINE is like a speedboat. Teams is more like an aircraft carrier. I’m particularly interested in whether people here agree — or think this analogy actually proves the opposite. Is the problem mainly Teams itself, or the mental model we use to judge it?179Views0likes0Comments
Build governed asynchronous APIs with Azure API Management and Azure Service Bus
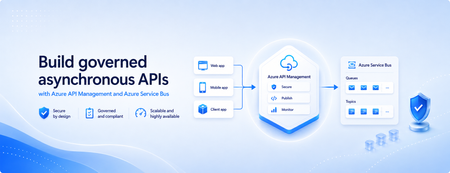
Many applications use Azure Service Bus to decouple services, handle traffic spikes, and process workloads asynchronously. However, securely exposing messaging capabilities to applications, partners, and internal teams can require custom middleware or messaging-specific client implementations. Today, we’re announcing the general availability of native Azure Service Bus integration in Azure API Management. With the send-service-bus-message policy, developers can publish messages directly from an Azure API Management gateway to an Azure Service Bus queue or topic. This provides a secure and governed HTTP interface for Service Bus workloads—without requiring teams to build and operate a separate adapter service. Connect APIs directly to Azure Service Bus Azure API Management can act as the governed entry point for applications that submit work to Azure Service Bus. A client sends a standard HTTP request to API Management. The gateway can authenticate and authorize the caller, validate or transform the request, and apply policies such as rate limits and quotas before publishing the message to a Service Bus queue or topic. Once the message is accepted, API Management can immediately respond to the caller while downstream services process the message asynchronously. Alternatively, message publication can be added to an existing API flow while the request continues to its primary backend. This integration brings together API governance in Azure API Management and reliable asynchronous messaging in Azure Service Bus—without adding another intermediary service. Greater control over Service Bus messages As part of general availability, we’re introducing additional controls for building production messaging workflows. 1. Control how messages are processed Developers can configure the following Service Bus message properties directly in the policy: Message IDs to correlate messages and support duplicate-detection or idempotent processing patterns. Session IDs to group related messages for ordered or stateful processing. Time-to-live to prevent messages from being processed after they are no longer relevant. These values can be generated dynamically using API Management policy expressions, allowing them to reflect request IDs, customer identifiers, transactions, or other application context. 2. Capture the send result The response-variable-name attribute captures information about the Service Bus send operation in an API Management context variable. Subsequent policies can use the result to add correlation information to an API response, emit telemetry, record an operational event, or apply conditional logic when a message cannot be sent. 3. Choose how failures affect the API Different messaging scenarios require different failure behavior. When publishing the message is the primary purpose of an API, a send failure can stop policy execution and invoke the API Management error-handling path. When publishing is secondary—such as sending an audit event or initiating optional downstream processing—the ignore-error option can allow the primary API request to continue. Information about the send operation remains available through the response variable for logging or subsequent policy logic. 4. Secure access with managed identity API Management authenticates to Azure Service Bus using a Microsoft Entra managed identity. Customers can use the system-assigned identity of the API Management service or specify a user-assigned managed identity. The selected identity is granted the Azure Service Bus Data Sender role for the appropriate namespace, queue, or topic. This removes the need to store Service Bus connection strings or shared access keys in API policies and makes it easier to apply least-privilege access using Azure role-based access control. Send a message with an API Management policy The following example sends the incoming request body to an orders queue. It assigns a message ID and expiration time, captures the result of the send operation, and treats successful publication as a required part of the API request. <send-service-bus-message queue-name="orders" namespace="contoso-messaging.servicebus.windows.net" message-id="@(context.RequestId.ToString())" time-to-live="00:10:00" response-variable-name="serviceBusResult" ignore-error="false"> <payload> @(context.Request.Body.As<string>(preserveContent: true)) </payload> </send-service-bus-message> A session ID can also be added when related messages need to be grouped for ordered or stateful processing. For a fully asynchronous API, the policy can be followed by return-response so that API Management acknowledges the request immediately after sending the message. For an existing API, the request can continue to its configured backend after the message is published. Common integration scenarios Create asynchronous APIs: Accept an order, document, or processing request through an HTTP API, publish it to a queue, and return immediately while downstream services complete the work. Govern partner integrations: Provide partners with a managed API contract instead of exposing the underlying Service Bus namespace. API Management can authenticate callers, validate requests, and apply quotas before publishing messages. Publish business events: Publish events to a Service Bus topic so multiple subscriptions and downstream services can process them independently. Handle bursts of incoming traffic: Use Service Bus to buffer messages when incoming API traffic temporarily exceeds the rate at which downstream services can process requests. Add events to existing API operations: Publish audit, notification, analytics, or workflow events while allowing the primary API request to continue to its configured backend. Preserve workflow affinity: Use Service Bus sessions to group related messages for ordered or stateful processing based on a customer, transaction, order, or workflow identifier. Get started To send messages from Azure API Management to Azure Service Bus: Create or select an Azure Service Bus queue or topic. Enable a system-assigned or user-assigned managed identity on the API Management service. Assign the identity the Azure Service Bus Data Sender role. Add the send-service-bus-message policy to an API operation. Configure the message payload, processing properties, output variable, and failure behavior. With native Azure Service Bus integration, Azure API Management provides a secure and governed way to connect HTTP APIs with asynchronous messaging workloads—without requiring additional middleware. Learn more Send Service Bus message policy reference Send messages to Azure Service Bus from Azure API Management Azure API Management June 2026 release notes Azure Service Bus documentation758Views0likes0Comments