infrastructure
58 TopicsBring Azure AI to your private workloads on Azure VMware Solution
Overview A global enterprise has migrated thousands of VMware vSphere virtual machines (VMs) to Microsoft Azure as part of their application modernization strategy. Having exited their on-premises data centers and relocated their legacy application VMs to Azure VMware Solution, the next phase of that strategy is no longer about where the workloads run, but about what the organization can do with the data inside them. Those applications hold the enterprise's most valuable data, yet they sit on private networks that Azure AI services cannot reach by default. What should Azure VMware Solution look like when the goal is to make private workloads AI-accessible in place? Azure VMware Solution is a VMware validated first party Azure service from Microsoft that provides private clouds containing VMware vSphere clusters built from dedicated bare-metal Azure infrastructure. It enables customers to leverage their existing investments in VMware skills and tools, allowing them to focus on developing and running their VMware-based workloads on Azure. That is why organizations move their VMware estates to Azure VMware Solution in the first place: they get to modernize on their own terms, lifting and shifting mission-critical applications into Azure exactly as they run today, with no rewrites, no re-platforming, and no big-bang migration. Azure AI Foundry is the Azure platform for building, deploying, and governing AI agents, providing managed model deployments, an agent runtime, tool integration, and end-to-end tracing under Microsoft Entra identity. Agents in Foundry reach external systems through the Model Context Protocol (MCP), an open standard that describes a system to an agent as a small, explicit set of tools. MCP matters here because it turns "connect the agent to a workload" into a contract rather than a custom integration: the agent learns one way to ask, and each workload is fronted by a server that translates it. But the "leave it as it is" strength of Azure VMware Solution has a quiet side effect. The systems holding your most valuable data, such as core databases, file servers, and line-of-business applications, keep running on private networks inside the private cloud. Meanwhile, Azure's AI services live in the Azure control plane and, by default, reach only public endpoints. When the mandate arrives to "add AI everywhere," your Azure VMware Solution workloads are often the one place AI cannot reach. Not because the data isn't valuable, but because it's private by design. In this post, I will introduce the challenge of reaching private workloads with Azure AI, describe the Azure VMware Solution and Azure AI Foundry architectural components that close the gap, and describe the security and design considerations for doing it safely. The pattern is deliberately workload-agnostic: a managed agent in Azure AI Foundry that reaches private Azure VMware Solution systems through small, purpose-built bridges, one per workload type, while your data stays put, read-only, and inside your network. I will prove it with a working SQL example (two private databases behind a single bridge), then show how the same pattern extends to file shares, APIs, and beyond. The full deployment kit is on GitHub, so you can try it in your own environment. In the next section, I will introduce the architectural components of Azure VMware Solution. Architectural Components The diagram below describes the architectural components of the Azure VMware Solution. Figure 1 – Azure VMware Solution Architectural Components Each Azure VMware Solution architectural component has the following function: Azure Subscription: Used to provide controlled access, budget, and quota management for the Azure VMware Solution. Azure Region: Physical locations around the world where we group data centers into Availability Zones (AZs) and then group AZs into regions. Azure Resource Group: Container used to place Azure services and resources into logical groups. Azure VMware Solution Private Cloud: Uses VMware software, including vCenter Server, NSX-T Data Center software-defined networking, vSAN software-defined storage, and Azure bare-metal ESXi hosts to provide compute, networking, and storage resources. Azure NetApp Files, Azure Elastic SAN, and Pure Cloud Block Store are also supported. Azure VMware Solution Resource Cluster: Uses VMware software, including vSAN software-defined storage, and Azure bare-metal ESXi hosts to provide compute, networking, and storage resources for customer workloads by scaling out the Azure VMware Solution private cloud. Azure NetApp Files, Azure Elastic SAN, and Pure Cloud Block Store are also supported. VMware HCX: Provides mobility, migration, and network extension services. VMware Site Recovery: Provides Disaster Recovery automation and storage replication services with VMware vSphere Replication. Third party Disaster Recovery solutions Zerto Disaster Recovery and JetStream Software Disaster Recovery are also supported. Dedicated Microsoft Enterprise Edge (D-MSEE): Router that provides connectivity between Azure cloud and the Azure VMware Solution private cloud instance. Azure Virtual Network (VNet): Private network used to connect Azure services and resources together. Azure Route Server: Enables network appliances to exchange dynamic route information with Azure networks. Azure Virtual Network Gateway: Cross premises gateway for connecting Azure services and resources to other private networks using IPSec VPN, ExpressRoute, and VNet to VNet. Azure ExpressRoute: Provides high-speed private connections between Azure data centers and on-premises or colocation infrastructure. Azure Virtual WAN (vWAN): Aggregates networking, security, and routing functions together into a single unified Wide Area Network (WAN). Those components describe where your workloads run. In the next section, I will introduce the pattern that makes the data inside them reachable by Azure AI, without changing any of it. The idea in one picture One managed agent in Azure AI Foundry talks to your private Azure VMware Solution workloads through a set of small Model Context Protocol (MCP) servers, one bridge per workload type. SQL databases are live today; a file-share bridge or an API bridge is the same shape with different tools. Figure 2: Solution overview A single managed agent in Azure AI Foundry reaches private Azure VMware Solution workloads through per-workload MCP servers running on VNet-integrated Azure Container Apps, connected to the private cloud over ExpressRoute. Three ideas carry the design: MCP is the universal contract. Every workload is exposed through the same small set of tools. For the SQL bridge, that’s list_sources, get_schema, and run_query. The agent learns one way to ask a question; each bridge translates it for its workload. One lightweight bridge per workload type. Each MCP server is a VNet-integrated Azure Container App that can legitimately see both worlds: Azure on one side, the private Azure VMware Solution network over ExpressRoute on the other. Want to make another workload AI-accessible? Add another bridge. The agent doesn’t change. Managed identity end to end. No passwords in code or config. The agent presents a Microsoft Entra token; each bridge pulls the credentials it needs from Azure Key Vault at runtime. One pattern, every workload The power of the design is that it’s workload-agnostic. The agent, the network path, the Entra identity, and the governance model are built once. Each new workload is just a new MCP server that speaks the same tool contract, so you can light up your estate incrementally, highest-value workloads first, without re-architecting anything. Azure VMware Solution workload MCP bridge Example tools What it unlocks SQL databases (SQL Server, PostgreSQL, Oracle, MySQL) SQL MCP server (live in this post) list_sources, get_schema, run_query Natural-language questions and cross-database corroboration File shares (SMB / NFS, document stores) File MCP server list_dirs, search, read_file Q&A and summarization over contracts, drawings, PDFs, logs Line-of-business apps (REST / SOAP) API MCP server list_operations, call_operation Conversational access to ERP, ticketing, claims, orders NoSQL / message systems Connector MCP server list_collections, query, peek Reasoning over document stores and event streams Mainframe / other systems Adapter MCP server workload-specific Bringing legacy systems into modern AI workflows Every bridge is small, independently deployable, and governed the same way: read-only by default, private over ExpressRoute, and locked to your agent’s managed identity. The pattern is the product; the bridges are how you grow it. To make it concrete, here’s the first proof of the pattern: a secure, read-only agent over two private SQL databases in Azure VMware Solution. Reference architecture The reference deployment runs in a single Azure region, with the Azure resources in one resource group alongside the Azure VMware Solution private cloud. Figure 3: Reference architecture A question from the managed agent in Azure AI Foundry crosses into your virtual network, where the MCP server on Azure Container Apps validates the caller's Entra token, reads the database password from Key Vault with its own managed identity, and runs a single read-only SELECT against the SQL Server VMs inside the Azure VMware Solution private cloud. Component Resource Type Azure VMware Solution private cloud avs-private-cloud Microsoft.AVS/privateClouds MCP server avs-mcp-server Microsoft.App/containerApps Container Apps environment avs-mcp-env Microsoft.App/managedEnvironments AI Foundry account avs-sql-foundry Microsoft.CognitiveServices/accounts Foundry project avs-sql-foundry/avs-sql-agent .../accounts/projects Container registry avssqlacr Microsoft.ContainerRegistry/registries Secrets avs-sql-kv-01 Microsoft.KeyVault/vaults Network avs-hub-vnet (10.40.0.0/16) Microsoft.Network/virtualNetworks ExpressRoute gateway avs-ergw virtualNetworkGateways Foundry private endpoint avs-sql-foundry-pe (+ privatelink DNS zones) privateEndpoints Logs avs-sql-logs OperationalInsights/workspaces The data itself lives on VMs inside the Azure VMware Solution private cloud, on a VMware NSX segment (avs-workload-01, 192.168.131.0/24): VM IP Database SQL VM #1 192.168.131.55 SalesDB (Products, Customers, Orders) SQL VM #2 192.168.131.56 InventoryDB (Products, Stock) The bridge works because the Container Apps subnet routes to the Azure VMware Solution private cloud over ExpressRoute, while Foundry is reachable privately through a private endpoint. Figure 4: Network topology The MCP server runs in a delegated aca-subnet and reaches the workload segment over ExpressRoute. Foundry sits behind a private endpoint with privatelink DNS zones, so the portal and jump host reach it privately. The agent’s tool call to the bridge is a single outbound HTTPS request carrying an Entra token. The data bridge: a small, read-only MCP server The first bridge is the SQL MCP server, a small Python service (FastMCP over streamable HTTP) that exposes three read-only tools. It’s engine-agnostic (SQLAlchemy) and pulls its credentials from Key Vault at runtime: @mcp.tool() def list_sources() -> str: """List the databases across the Azure VMware Solution workloads and what each contains.""" @mcp.tool() def get_schema(source: str) -> str: """Return tables and columns for a source (call list_sources first).""" @mcp.tool() def run_query(source: str, query: str) -> str: """Run ONE read-only SELECT and return up to the source's row cap.""" Guardrails are built in. Only SELECT / WITH statements are allowed, one statement at a time; DML and DDL keywords are blocked; and every result set is row-capped. The agent gets to read and reason, but never to mutate. Onboarding a database is configuration, not code. A single sources.yaml catalog describes each source and its governance: sources: sales: type: mssql connection: { host: 192.168.131.55, port: 1433, database: SalesDB } auth: { kind: sql, username: agentreader, secret: sql-agentreader-password } governance: { allow_schemas: [dbo], max_rows: 200 } inventory: type: mssql connection: { host: 192.168.131.56, port: 1433, database: InventoryDB } auth: { kind: sql, username: agentreader, secret: sql-agentreader-password } governance: { allow_schemas: [dbo], max_rows: 200 } The service is containerized (with the ODBC Driver 18 / msodbcsql18), pushed to the container registry, and run on the VNet-integrated Container Apps environment. It has a system-assigned managed identity with Key Vault Secrets User on the vault, so it can fetch the read-only database credential without ever storing it. The managed agent in Azure AI Foundry The agent lives entirely in Azure AI Foundry (avs-sql-foundry, project avs-sql-agent), running on a small, cost-efficient model deployment. It’s configured with: A schema-first workflow. Discover the available sources, read the schema, write a read-only query, then corroborate the results. An MCP tool pointing at the Container App’s /mcp endpoint, authenticated with Microsoft Entra using the project’s managed identity. Generic, source-agnostic instructions. The agent discovers structure at runtime rather than hard-coding any schema, so the same agent works against any workload behind an MCP server, not just these two databases. Figure 5: The agent in Azure AI Foundry The agent is attached as a tool with the private MCP data server and authenticated via managed identity. Once the tool is attached, answering a question is a single, auditable round trip. The agent discovers the available sources, reads only the schema it needs, issues a read-only query, and corroborates the results, all over private connectivity and with managed-identity authentication end to end. Figure 6: How a question becomes an answer. The agent calls list_sources, validates its managed-identity token, reads each schema, and runs read-only SELECTs over ExpressRoute. Key Vault supplies the credentials, and the corroborated answer flows back to the user. Security and governance, by design Because these are your crown-jewel systems, security is the starting point rather than a layer on top: No secrets in code. Database credentials live in Key Vault; the server fetches them through its managed identity (DefaultAzureCredential to SecretClient). Entra managed-identity auth from the agent to the bridge, with no shared keys and automatically rotating tokens. Private connectivity. The bridge reaches Azure VMware Solution over ExpressRoute; the SQL VMs are never exposed to the internet; Foundry sits behind a private endpoint. Read-only guardrails. Only SELECT is allowed; writes and DDL are blocked; result sets are capped. Least-privilege caller lock. The bridge accepts tokens only from the Foundry project’s managed identity. The payoff: answers no single system can give The value here isn’t “query a table.” It’s corroboration, the kind a single database can’t do on its own. Our two databases share a ProductID, so the agent queries both and joins them itself. Ask a plain-language question about stock health, and you get: Widget A: sold 500, stock 40 (below the reorder point of 50), so REORDER NOW Gizmo C: high stock, low sales, so OVERSTOCKED Contraption E: present in Sales, missing from Inventory, flagged as a DISCREPANCY Figure 7: A natural-language question answered from two private Azure VMware Solution databases, with reorder, overstock, and discrepancy flags surfaced directly in the agent’s reply. Figure 8: The run trace Every tool call and query is visible and auditable (list_sources, then get_schema, then run_query on each source), so you can see exactly how the answer was produced. The same shape generalizes far beyond retail: claims versus policy, orders versus fulfillment, and tickets versus assets. Anywhere the truth is split across silos, the agent can bring it back together. Adding the next workload Coverage grows at two levels: within a bridge, and across bridges. Within the SQL bridge (another database), it’s configuration, not code. SQLAlchemy gives one code path for SQL Server, PostgreSQL, MySQL, and Oracle; the source type selects the dialect. Adding a PostgreSQL VM, for example, takes no changes to the server code: add the driver, a source block (type: postgresql, allow_schemas: [public]), and a Key Vault secret, then rebuild. Across workload types (a file share, an API), you add a new bridge that implements the same tool contract with connectors suited to that workload (read_file / search for a document store, call_operation for a REST or SOAP app), then attach it to the same agent. Nothing about the agent, the network, or the identity model changes. Your estate lights up one bridge at a time. Deploy it yourself The entire bridge is packaged as an open, reusable kit on GitHub, Azure VMware Solution AI Data Agent, with a Bicep template (and a compiled ARM equivalent), a parameters file, and a one-command deploy script. # Build and push the MCP image az acr build --registry <your-acr> --image avs-mcp:v4 . # Deploy to the VNet-integrated Container Apps environment az containerapp update -n avs-mcp-server -g avs-sql-rg \ --image "<your-acr>.azurecr.io/avs-mcp:v4" # Store the read-only SQL credential in Key Vault az keyvault secret set --vault-name avs-sql-kv-01 \ --name sql-agentreader-password --value '<password>' The script provisions the delegated subnet, the container registry, Key Vault (with the read-only secret), the VNet-integrated Container Apps environment and MCP server, and the managed-identity role assignments, optionally including the Azure AI Foundry account and model deployment. You point it at the VNet already connected to your Azure VMware Solution private cloud and supply a read-only database credential. All that’s left is creating the read-only login and attaching the MCP tool to your agent in the Foundry portal. What’s next This SQL example is deliberately just the first bridge. A few directions we’re excited about: Meet users where they are. Surface the agent in Microsoft Teams or Microsoft 365 Copilot, so anyone in the organization can ask questions of Azure VMware Solution workloads in natural language. One agent, every workload. Grow from databases to file shares, REST/SOAP apps, NoSQL, and message systems, each a new bridge behind the same agent. A workload catalog. A library of ready-made bridges, so onboarding a new Azure VMware Solution workload becomes a deploy-and-configure step rather than a project. Bringing it together With a managed agent in Azure AI Foundry, lightweight MCP servers on VNet-integrated Azure Container Apps, and private connectivity over ExpressRoute, workloads that used to be “off-limits to AI” become conversational, while staying inside your network, read-only, and credential-less, using the same identity and governance model you already rely on across Azure. The SQL example is just the beginning. Because every workload is reached the same way, enabling AI across your Azure VMware Solution estate becomes a repeatable motion: pick the next workload, add a small bridge, and it’s live, with no data movement, no re-platforming, and no new trust boundary. For organizations on Azure VMware Solution, that reframes what Azure VMware Solution is for. Not just where your VMware workloads run, but where they become AI-accessible, one bridge at a time, securely and in place. Ready to try it? Grab the Azure VMware Solution AI Data Agent kit on GitHub, point it at your Azure VMware Solution-connected VNet, and stand up your first bridge. We’d love to hear what you connect first. Next Steps Start by identifying which Azure VMware Solution workloads hold the highest-value data, typically core databases, document stores, and line-of-business applications, and pick one as your first bridge. Deploy the kit into the virtual network already connected to your Azure VMware Solution private cloud, create a dedicated read-only login for the agent, and validate the full path end to end in a non-production private cloud before going further. With large enterprise solutions for strategic and major customers, an Azure VMware Solution Solutions Architect from Azure, Broadcom, or a trusted VMware Partner should be engaged to review the network path, the identity model, and the data governance boundaries before a production rollout. This should also include a data classification and application dependency assessment, to establish which sources the agent may read, where data gravity lies, and which traffic flows and latency dependencies the ExpressRoute path must support. Beyond the first bridge, a few directions we are excited about: Meet users where they are. Surface the agent in Microsoft Teams or Microsoft 365 Copilot, so anyone in the organization can ask questions of Azure VMware Solution workloads in natural language. One agent, every workload. Grow from databases to file shares, REST/SOAP apps, NoSQL, and message systems, each a new bridge behind the same agent. A workload catalog. A library of ready-made bridges, so onboarding a new Azure VMware Solution workload becomes a deploy-and-configure step rather than a project. Summary In this post, I took a closer look at the challenge of making private Azure VMware Solution workloads reachable by Azure AI, the architectural building blocks that close the gap (a managed agent in Azure AI Foundry, lightweight per-workload MCP servers on VNet-integrated Azure Container Apps, and private connectivity over ExpressRoute), and the security and governance model that keeps your data read-only, credential-less, and inside your network. I also discussed the next steps to continue enabling Azure AI across an Azure VMware Solution estate. The SQL example is just the beginning. Because every workload is reached the same way, enabling AI across your Azure VMware Solution estate becomes a repeatable motion: pick the next workload, add a small bridge, and it's live, with no data movement, no re-platforming, and no new trust boundary. For organizations on Azure VMware Solution, that reframes what the service is for. Not just where your VMware workloads run, but where they become AI-accessible, one bridge at a time, securely and in place. Ready to try it? Grab the Azure VMware Solution AI Data Agent kit on GitHub, point it at your Azure VMware Solution-connected virtual network, and stand up your first bridge. I'd love to hear what you connect first. If you are interested in Azure VMware Solution, please use these resources to learn more about the service and the Azure AI building blocks used in this post: Azure VMware Solution Homepage: Azure VMware Solution Documentation: Azure VMware Solution SLA: SLA for Azure VMware Solution Azure Regions: Azure Products by Region Service Limits: Azure VMware Solution subscription limits and quotas Well-Architected Framework: Azure VMware Solution workloads Cloud Adoption Framework: Introduction to the Azure VMware Solution adoption scenario Enterprise Scale Landing Zone: Enterprise-scale for Microsoft Azure VMware Solution GitHub repository: Azure/azure-vmware-solution Learning Resources: Azure VMware Solution (microsoft.github.io) Networking and connectivity Network connectivity scenarios: Enterprise-scale network topology and connectivity for Azure VMware Solution Network Security: Azure VMware Solution Network Security Internet Connectivity: Internet connectivity design considerations Security and governance Identity & Access Management: Enterprise-scale identity and access management Security Recommendations: Concepts - Security recommendations for Azure VMware Solution Security Baseline: Azure security baseline for Azure VMware Solution WAF: Security considerations for Azure VMware Solution workloads Defender for Cloud: Integrate Microsoft Defender for Cloud with Azure VMware Solution Customer-managed keys: Configure customer-managed key encryption at rest Azure AI and the agent platform Azure AI Foundry: Azure AI Foundry Foundry Agent Service: What is Azure AI Foundry Agent Service? Model Context Protocol: Model Context Protocol specification Azure Container Apps: Azure Container Apps overview VNet integration: Networking in Azure Container Apps environments Managed identities: What are managed identities for Azure resources? Azure Key Vault: About Azure Key Vault Private endpoints: What is Azure Private Endpoint? Deployment kit: Azure VMware Solution AI Data Agent Tooling and automation Azure CLI: Azure Command-Line Interface (CLI) Overview PowerShell module: Az.VMware Module Azure Resource Manager: Microsoft.AVS/privateClouds REST API: Azure VMware Solution REST API Terraform provider: azurerm_vmware_private_cloud Terraform Registry Enterprise Scale GitHub repository: Azure/Enterprise-Scale-for-AVS Author Bio Nivas Narayanasamy is a Senior Software Engineer on the Azure VMware Solution team at Microsoft. He works across the private cloud platform, networking, and automation that customers rely on to run VMware workloads on Azure and is currently focused on secure patterns for bringing Azure AI to private enterprise data.Fast cloud migration, measurable ROI: Forrester Total Economic Impact study of Azure VMware Solution
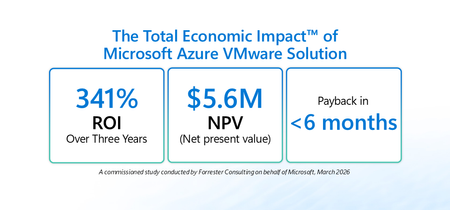
Many organizations are balancing near-term continuity for VMware-based workloads with longer-term cloud modernization goals – all while managing cost, security, and resiliency. Azure VMware Solution (AVS) is built for this moment: a Microsoft-managed service verified by VMware that enables running VMware Cloud Foundation (VCF) workloads (vSphere, NSX-T, vSAN, HCX) on dedicated Azure infrastructure. It gives organizations a practical way to move or extend VMware environments into Azure while maintaining operational consistency and leveraging the skills of existing VMware teams. To help leaders quantify the potential value of this approach, Microsoft commissioned Forrester Consulting to conduct The Total Economic Impact™ (TEI) of Microsoft Azure VMware Solution (March 2026). The study models the financial impact over three years and risk-adjusts results. Access the full study here: aka.ms/AVS-TEI Here’s what the study found and how IT leaders can use it as a framework for decision-making: Topline results from the study Forrester’s risk-adjusted financial analysis for a composite organization 1 found: 341% ROI over three years 2 $5.6M net present value (NPV) 3 <6 months payback 4 These metrics are meaningful on their own, but the bigger story for leadership is where the value comes from: improved operational stability, reduced infrastructure costs driven by data center exit and hardware refresh avoidance, and the ability to redeploy skilled IT resources from maintenance to modernization. The customer journey: why organizations turn to AVS AVS offers a bridge: Lift and shift VMware workloads into Azure without forcing immediate re-platforming then, modernize at a pace aligned to business priorities. In the study, Forrester interviewed decision-makers with experience using AVS. Interviewees described common challenges that led them to invest in AVS, including: Fragmented systems that complicated and slowed operations: Inherited stacks, duplicated tools, and unclear ownership of orphan machines made operations and governance harder. Rising cost and complexity of on-premises operation: Colocation fees, energy and cooling costs, server refresh cycles, and tooling renewals were difficult to justify against cloud economics. Limited capacity and skills to refactor at scale: Teams wanted the cost and agility benefits of the cloud but didn’t have the time or skills to rewrite hundreds (or thousands) of VMs on aggressive timelines. Security and audit pressure: Disparate environments and legacy access models elevated risk and created audit friction. Operational variability and end-user experience: VPN dependencies, inconsistent remote tooling, and endpoint logistics led to slow first-call resolution and downtime risks. Three quantified benefits that drive the business case 1) Reduction in downtime and associated costs by 80% In the study, interviewees reported that moving VMware workloads to AVS improved day-to-day reliability by eliminating fragile on-premises workflows and leveraging Azure’s managed infrastructure. Examples included fewer VPN-related failures, faster issue resolution through centralized tooling, and stronger service-level performance. For leadership teams, this benefit is about more than avoided cost. Better up time protects customer experience, employee productivity, and reduces the operational noise that can slow modernization programs. 2) Reduced infrastructure costs through data center exit, refresh avoidance, and cleanup A second driver is the ability to avoid or eliminate significant portions of data center cost and refresh spend. In the study, interviewees described using AVS to close data centers, avoid upcoming hardware refresh cycles, and reduce ongoing capital and operating costs. Importantly, interviewees also reported that migration waves prompted additional savings through portfolio hygiene by validating each VM, decommissioning redundant systems, and rightsizing oversized workloads. Those actions helped organizations reduce their ongoing compute, storage, and licensing footprint after migration. 3) Redeployment of 50% of IT team members from maintenance to modernization The TEI study quantifies a practical advantage of a managed VMware environment in Azure: fewer hours spent on hardware lifecycle, cluster patching, upgrades, and other routine data center tasks. In practice, many leaders treat this as capacity created rather than budget eliminated: the opportunity to shift experienced engineers toward modernization, automation, cloud governance, proactive incident prevention, and higher-value business initiatives. Unquantified benefits organizations should weigh Beyond the quantified categories, the study also highlights benefits that are strategically important, but not fully quantified in the model: Acceleration of future modernization: With workloads running in Azure via AVS, organizations can integrate platform services across security, identity, data, and analytics and build a runway for new capabilities, including AI-driven scenarios in Azure. Fast, cost-effective migration of legacy workloads: Interviewees described avoiding major consulting or hiring costs that would have been required to refactor complex workloads into cloud-native designs. Improved audit readiness and security posture: Consolidating fragmented environments into governed Azure landing zones can simplify audit preparation and strengthen governance and monitoring. For many leadership teams, these benefits strengthen the business case because they support broader transformation outcomes that extend beyond infrastructure cost alone. Things to consider in your own decision process If you’re building a business case to move workloads to Azure, whether it be lifting and shifting to AVS or replatforming and refactoring to Azure IaaS and managed services, consider mapping your environment across these areas: Data center timelines: Refresh cycles, colocation exit deadlines, and contract constraints. Operating model readiness: How quickly teams can adopt cloud-native services versus preserving VMware operations during transition. Modernization roadmap: Determine which applications are candidates for investment in replatforming, refactoring, replacement, or retirement once in Azure. Next steps Read the full TEI study: aka.ms/AVS-TEI Explore more about AVS: aka.ms/AzureVMwareSolution Get the VMware to Azure VMware Solution Planning Guide: aka.ms/VMwareToAVSguide Learn more about the Azure Copilot migration agent: aka.ms/migrate/AMA Join the AVS Pros group on LinkedIn for the latest updates and news: aka.ms/AVSPros 1 Composite organization: Forrester designed a composite organization based on characteristics of the interviewees’ organizations. 2 Return on Investment (ROI): A project’s expected return in percentage terms. ROI is calculated by dividing net benefits (benefits less costs) by costs. 3 Net present value (NPV): The present or current value of (discounted) future net cash flows given an interest rate (the discount rate). A positive project NPV normally indicates that the investment should be made unless other projects have higher NPVs. 4 Payback: The breakeven point for an investment. This is the point in time at which net benefits (benefits minus costs) equal initial investment or cost.
AWS to Azure Migration — From the Cloud Economics & FinOps Lens
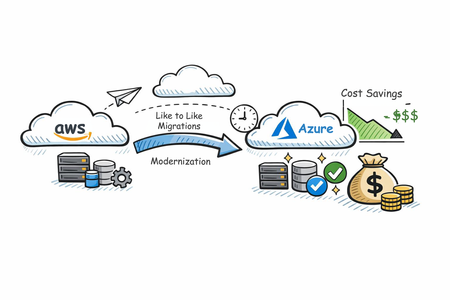
“ROI fails when FinOps joins late.” That single pattern explains why many cloud migrations deliver technical success but financial disappointment. Workloads move. SLAs hold. Teams celebrate go‑live. Then the CFO asks: Where are the savings we modeled? In most cases, FinOps was engaged after architecture decisions were locked, licenses were double‑paid, and governance debt had already accumulated. This article frames AWS‑to‑Azure migration through a FinOps lens—not to chase immediate modernization, but to deliver defensible, incremental cost savings during and after migration, without increasing risk. Azure migration guidance consistently emphasizes a structured, phased approach—discover, migrate like‑for‑like, stabilize, then optimize. From a FinOps perspective, this sequencing is not conservative—it is economically rational: Like‑for‑like preserves performance baselines and business KPIs Cost comparisons remain apples‑to‑apples Optimization levers can be applied surgically, not blindly The real value emerges in the first 90 days after migration, when cost signals stabilize and commitment‑based savings become safe to apply. {TLDR: Cloud migrations miss ROI when FinOps joins late. AWS → Azure migrations deliver real savings when FinOps leads early, migrations stay like‑for‑like, and optimization is applied after costs stabilize. Azure enables this through four levers: AI‑assisted planning (Copilot + Azure Migrate), cheaper non‑prod with Dev/Test pricing, license reuse via Azure Hybrid Benefit, and low‑risk long‑term savings with Reservations—across compute and storage. Result: lower migration risk, controlled spend, and sustainable savings post‑move.} This Article talks about top 4 FinOps Levers in AWS → Azure Migration 1. Azure Copilot Migration Agent + Azure Migrate. Azure Copilot Migration Agent (currently in public preview) is a planning‑focused, AI‑assisted experience built on Azure Migrate. It analyzes inventory, readiness, landing zone requirements, and ROI before execution. You can interact with the Agent using natural language prompts to explore inventory, migration readiness, strategies, ROI considerations, and landing zone requirements. From a FinOps perspective, this directly translates into faster decision cycles and lower planning overhead. By simplifying and compressing activities that traditionally required weeks of manual analysis or external managed services support, organizations can reduce the cost of migration planning, accelerate business case creation, and bring cost and ROI discussions forward—before environments are deployed and financial commitments are made. 2. Azure Dev/Test pricing: Azure Dev/Test pricing provides discounted rates for non‑production workloads for eligible subscriptions, significantly reducing dev and test environment costs (Azure Dev/Test pricing). You can save up to 57 percent for a typical web app dev/test environment running SQL Database and App Service. Unlike other Cloud Providers, this directly reduces environment sprawl costs, which often exceed production waste post‑migration. It also enables wave‑based migration by lowering the cost of parallel environments, allowing teams to migrate deliberately rather than under financial pressure. 3. Azure Hybrid Benefit: Azure Hybrid Benefit allows organizations to reuse existing Windows Server, SQL Server, and supported Linux subscriptions (RHEL and SLES) on Azure, reducing both migration and steady‑state run costs. It enables license portability across Azure services, helping organizations avoid repurchasing software licenses they already own and redirect savings toward innovation and modernization. During migration, Azure Hybrid Benefit is especially impactful because it addresses migration overlap costs. The 180‑day migration allowance for Windows Server and SQL Server allows workloads to run on‑premises and in Azure simultaneously, supporting parallel validation, phased cutovers, and rollback readiness without double‑paying for licenses. For Linux, Azure Hybrid Benefit enables RHEL and SLES workloads to move to Azure without redeployment, ensuring continuity and avoiding downtime. From a FinOps perspective, this reduces one of the most underestimated migration cost drivers, delivering up to 76% savings versus pay‑as‑you‑go pricing for Linux and up to 29% versus leading cloud providers for SQL Server, while keeping migration timelines driven by readiness—not cost pressure. 4. Azure Reservations: Azure Reservations enable organizations to reduce costs by committing to one‑year or three‑year plans for eligible Azure services, receiving a billing discount that is automatically applied to matching resources. Reservations provide discounts of up to 72% compared to pay‑as‑you‑go pricing, do not affect the runtime state of workloads, and can be paid upfront or monthly with no difference in total cost. Importantly, Azure Reservations apply not only to compute and database, but also to storage services like Azure Blob storage, Azure Data Lake Gen2 Storage and Azure Files (for storage capacity) which often represent a significant portion of enterprise cloud spend. In the context of migration, Azure Reservations matter because they allow FinOps teams to optimize baseline costs across both compute and data layers once workloads stabilize. Unlike AWS, where commitment‑based discounts are largely compute‑centric and storage services such as Amazon S3 do not offer reservation‑style pricing, Azure enables long‑term cost optimization for persistent storage footprints that continue to grow post‑migration. Additionally, Azure Reservations offer greater flexibility—customers can modify, exchange, or cancel reservations through a self‑service program, subject to defined limits. This is particularly valuable during wave‑based migrations, where workload shapes evolve over time. From a FinOps perspective, Azure Reservations allow organizations to commit to predictable savings with broader scope and lower risk, covering both infrastructure and data‑heavy workloads common in migration scenarios. Successful migrations are no longer measured by workloads moved, but by cost control maintained and value unlocked. Azure’s FinOps‑aligned migration capabilities allow organizations to reduce risk first, optimize deliberately, and ensure that savings are sustained long after the last workload migrates.
Accelerate Cloud Migration with Wave Planning in Azure Migrate
Introduction Migrating to the cloud is more than a technical upgrade - it's a strategic leap toward agility, scalability, and innovation. Yet, for many organizations, the journey can feel overwhelming, with complex dependencies and business risks threatening to slow progress. Today, we’re excited to announce the public preview of wave planning in Azure Migrate - a new capability designed to make large-scale migrations more manageable and predictable. With wave planning, you can now organize your migration journey into logical, iterative waves, enabling your teams to plan, execute, and track progress with greater speed, confidence, and control. Key Benefits: Accelerate migrations: Quickly identify and prioritize “quick win” workloads and applications by surfacing relevant information from discovery and assessments. Reduced risks: Group systems that work together using application grouping, dependency analysis and tags allowing safer iterative planning. Increased predictability: Visualize migration progress and timelines centrally, enabling continuous feedback and proactive adjustments. Application-centric migrations and modernization: Plan, execute, and track every step at the application level for greater control and business alignment. Wave Planning in Azure Migrate Concepts and Stages Planning Stage During the planning stage, you can organize their applications and workloads into waves and determine the order in which these groups will be migrated. By doing so, you can establish a comprehensive plan that outlines the specific steps, timelines, and resources required for each wave, ensuring a structured and efficient approach to migration and modernization. Key aspects of the wave planning in this stage includes: Group and sequence applications and workloads using tags, dependency analysis, and workload data. Set Azure targets and migration tools based on Azure Migrate assessment recommendations. Outline planning steps, timelines, and create a wave plan for application migration and modernization. Execution Stage Using wave planning you can perform the migration and modernization activities of the application withing the wave, as per the plan and track the progress as workloads are moved, tested, and migrated / modernized in Azure. Key aspects of wave planning at this stage includes: Centrally track migration and modernization activities for all applications and workloads within the wave. You can start migrating servers and databases using Server migration and Azure database Migration Service using in-product integrations. Integrated end-to-end workflows to facilitate server migrations from on-premises environments and various public clouds to Azure Virtual Machines. Monitor and visualize wave timelines in relation to planned migration and modernization dates and implement corrective actions as required based on status updates. In a nutshell, wave planning transforms migration from a one-time event into a continuous journey of improvement. By iterating, learning, and adapting, organizations build institutional knowledge, reduce risk, and unlock the full benefits of cloud adoption. Getting Started Ready to accelerate your migration? Get start today: Learn more about using Azure Migrate – Wave planning. Explore wave planning guidance through the Cloud Adoption Framework. Learn more about Azure Migrate. Checkout application-centric migration in Azure Migrate.Migrate or modernize your applications using Azure Migrate
Introduction Moving to cloud is an essential step for enterprises looking to leverage the benefits of security, innovation (AI), scalability, flexibility, and cost-efficiency. To help unlock these benefits migration or modernization to Azure is critical for reasons such as colocation of IT assets. A crucial part of this transformation is understanding the current state of your IT infrastructure, including workloads, applications, and their interdependencies. Cloud migration is most effective when you can decide, plan and execute it holistically focusing on applications rather than focusing on individual servers or workloads in isolation. In our endeavour to both simplify and enrich your cloud adoption journey, we are evolving Application awareness in Azure Migrate that we introduced last year with features summarized below. Overview “The new design of Azure Migrate is much more intuitive, it allows us to group workloads into applications and track them throughout the migration journey. The Business Case Generator is a true game changer, providing insights that are ready for presentation at Leadership meetings. Azure Migrate continues to improve, making the execution of migration programs more seamless, faster, and secure. It has been an invaluable tool for our customers who are in the path of migrating to Azure” - Karthik Balachandran | Architect | EY Azure Migrate delivers a major evolution in cloud migration capabilities with application awareness. Here are key new features and why they matter: Multi-Server Dependency Mapping – Provides a holistic view of application topology, so you understand all server interactions before migrating. This reduces risk by ensuring no server is left behind and dependencies are respected during cloud transition. Software & Security Insights– Offers built-in intelligence on software inventory and vulnerabilities (e.g. highlighting outdated software and missing patches). This helps improve your environment’s security and stability as part of the migration journey, benefiting IT admins and security teams. Application definition & import– Allows you to treat applications as first-class citizens in Azure Migrate (not just tag groupings). You can create and manage app groupings easily, enabling a shift from managing individual workloads to managing whole applications in your migration project. Application migration or modernization RoI – Allows you to identify investments required in respective migration strategies as well as savings that would accrue as application are moved to Azure. Application Assessments– Delivers holistic migration plans per app, including recommended strategies (Rehost, Replatform, Refactor), target Azure services, sizing, cost estimates, and readiness checks. This empowers cloud architects to make informed decisions with an application-level focus. Code insight integration – GitHub Copilot assessment – Enables a developer-driven assessment loop by incorporating GitHub App Modernization Assessment reports. This tightens collaboration with dev teams and can dynamically adjust migration recommendations (e.g., flagging apps that need refactoring). CAST Highlight– Brings code-level analytics at scale into the migration plan. By importing CAST’s code scan results, you can identify technical debt and required code changes upfront, ensuring the recommended cloud approach truly fits the app’s codebase. Wave Planning with 1P Tool Integration– Provides a planning and execution framework to migrate in phases and launch the appropriate migration tools for each component seamlessly. This ensures end-to-end coverage – from migration scheduling to real-time execution – all within Azure Migrate. Capability deep dive Identify your applications using multi-server dependency mapping and subsequently define them One of the first steps in cloud migration planning is identifying application boundaries and dependencies. Azure Migrate’s new multi-server dependency mapping provides a rich visualization of how servers communicate with each other in your environment. This goes beyond the single-server dependency view of the past – now you can visualize an entire datacenter’s topology in one view. When you discover your on-premises environment, Azure Migrate’s agentless dependency analysis automatically begins mapping connections. It even measures connection strength, helping distinguish steady, critical communication from ephemeral connections. You can subsequently define applications, and assign metadata such as Name, type – Custom or Packaged (Commercial off the shelf), Criticality, Complexity (based on the number of dependencies), etc. Additionally, you can export your discovered inventory, assign application names in a spreadsheet, and import it back to quickly create many application grouping. You are free to refine or correct groupings, too. If during analysis you realize a server or workload was grouped incorrectly, simply update the application to add or remove that member (with no need to re-run discovery). Deleting an application grouping will not delete the underlying servers; it just removes the logical app wrapper, so you can reorganize safely as needed. Now, you can plan migrations by application units rather than individual workloads. This leads to more predictable outcomes (since all interdependent pieces move together), and it eliminates guesswork that used to come from manually correlating server relationships. Proactive Software and Security Insights Migration is not just about moving workloads – it’s an opportunity to remediate and improve what you have. The new Software and Security Insights surface critical information about your IT estate early on, so you can address potential issues before migration. Once your inventory is discovered, Azure Migrate now highlights: Software Insights:The portal flags certain software or OS components that might need attention or have cloud-friendly alternatives. For example, it might detect that some VMs run outdated middleware or unsupported OS versions. The tool provides recommendations for replacement or upgrade – e.g. suggesting you Repurchase a legacy product through Azure Marketplace or move to a SaaS solution for that functionality. This helps you plan modernization (repurchasing or upgrading software) as part of the migration project, rather than carrying technical debt to the cloud. Security Insights:Azure Migrate also integrates with security monitoring to detect vulnerabilities and missing updates in your servers. More importantly, it advises how to fix them: e.g. enabling Microsoft Defender for Cloud to address vulnerabilities, and using Azure Update Manager to apply pending updates. In essence, you get a mini security assessment alongside your inventory. These insights empower IT admins and security teams to tackle risks as part of migration planning. Rather than “lift-and-shift and then fix later,” you can remediate issues in parallel with migration, leading to a more secure and optimized environment on Azure. RoI for modernizing applications We are bringing in updates to Azure Migrate Business case to help ascertain the value you stand to gain by modernizing your applications – Custom or Packaged, as well as providing spend analysis across recommended migration strategies – Rehost, Replatform and Refactor. Holistic application assessments covering Infra-Data-Web tiers Application assessment builds on Azure Migrate’s existing server, database and webapp assessments, to give a migration game-plan for an entire application. It analyzes each component and then recommends An overall migration strategyamong Rehost, Replatform and Refactor, for the application under consideration. Migration readiness, and blockers that need to be addressed for respective strategy Target Azure Services and SKUs for workloads comprising the application Monthly cost estimates to run the application on Azure Migration tooling recommendations per workload comprising the application. Instead of piecemeal workload assessments, Cloud architects get a unified view per application – making it much easier to prioritize and plan. For example, you might discover that one application is an easy rehost (quick win), while another would clearly benefit from refactoring to eliminate costly components. Application assessments surface such insights with data, so stakeholders (including application owners and developers) can agree on a path forward with confidence. Ultimately, this leads to high-confidence migration plans and minimizes surprises during execution. Improve analysis with Code-Level Insights from Github Copilot assessment and CAST Most times, whether an application can be easily Replatformed or needs Refactoring depends on the application’s source code. Hence, we are bridging the gap between infrastructure and application development realities and are offering Integration with code analysis tools – GitHub Copilot assessment and CAST Highlight – to incorporate code-level insights into Azure Migrate’s recommendations. Talking about GitHub copilot – it is an indispensable tool for the application development. Developers can identify changes required in the code bases of their applications to make them ready for modernization to PaaS services such as AKS, App Service, etc. The cloud architect running Azure Migrate application assessment can request the application developers to ingest the code change insights from GitHub copilot assessment into Azure Migrate assessment. Once this report is ingested, you’ll see the Azure Migrate assessment refine its recommendations conclusively – such readiness, effort to make the code changes, migration strategy – depending upon whether the code changes are minimal or significant. Similarly, at-scale/ portfolio level code analysis performed using CAST Highlight, a prominent software intelligence platform, can be imported into Azure Migrate to improve the assessment recommendations. In practice, this means Azure Migrate will know if the code has, say, outdated libraries or many hard-coded dependencies that make cloud migration harder. Overall, the integration of code insights leads to more realistic migration plans and smoother hand-offs between cloud infrastructure teams and dev teams. Wave Planning and Integrated Migration Execution After discovering applications, assessing them, and incorporating any code insights, you’re ready to migrate or modernize – but large migrations often happen in phases. That’s where the new Wave Planning feature comes in. Wave planning in Azure Migrate helps you organize and sequence the actual migration execution in waves or batches, plan the migration activities and execute using integrated first party migration tools and track the end-to-end migrations; thereby providing a single place where different users – Cloud architects, developers, application owners, etc. can collaborate and coordinate through the migration journey. If your strategy for an application (or a particular server in the application) is Rehost (lift-and-shift to Azure VMs), Azure Migrate will use its built-in Server Migration capability. You can start the replication of that server to Azure right from the wave plan. If your strategy is Replatform or Refactor and involves migrating data, the wave plan can redirect you to Azure Database Migration Service (DMS). All these integrations mean you can coordinate multi-step migrations from one place. Wave planning is aware of various target strategies and helps orchestrate them, so cloud administrators don’t have to juggle separate tool interfaces for VMs vs. databases vs. web apps. As each part of a wave completes, Azure Migrate updates the wave status for Rehost scenarios and users can manually update the status’ for Refactor or Replatform scenarios where some steps may take out of band. Interested in trying the new feature set and experience? All the above features are available in Azure Migrate now (in preview as of 7 th November, 2025). Just create a new Azure Migrate project and you’ll be greeted with the new interface. From there, you can start defining applications and exploring these capabilities with your own data. About Azure Migrate Azure Migrate is Microsoft’s free platform for migrating and modernizing to Azure. It provides IT resource discovery, assessment, business case analysis, wave planning, migration, and modernization capabilities in a workload agnostic manner. You can run and monitor your migration/ modernization journey from a single, secure portal. Currently, Azure Migrate's application aware experience supports the discovery of following workloads: Windows Server, Linux Server, SQL Server, PostgreSQL, .NET webapp on IIS, and Java on Tomcat running on various platforms including, VMware, Microsoft, Bare-metal, AWS EC2, GCP CE, and Xen. Further, it supports assessments and wave planning for Azure VM, Azure VMware Solution (AVS), Azure SQL Managed Instance, Azure SQL Database, Azure Database for PostgreSQL Flexible Server, App Service Code, App Service Containers, and Azure Kubernetes Service. Last, it supports in-line Lift and Shift migration to Azure VM and Azure Local. Note: MySQL discovery and assessment is available in the classic experience only
Unlock cost savings with utilization-based storage recommendations in Azure Migrate
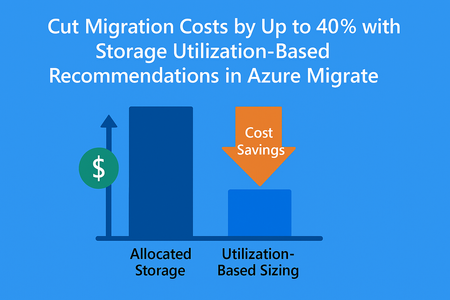
We’re thrilled to announce a game-changing enhancement in Azure Migrate. The storage utilization-based recommendations, a feature designed to help you right-size your storage workloads and maximize savings. By focusing on actual storage usage instead of allocated capacity, you can significantly reduce costs and accelerate their cloud journey. This feature brings a new level of precision to your migration planning and business case. Why This Matters In our analysis across thousands of on-premises environments, we observed a striking trend: nearly 40% of allocated storage is overprovisioned. This means customers are paying for capacity they don’t actually use. Traditional assessments often rely on allocated storage, leading to inflated cost estimates and suboptimal resource planning. What’s New Azure Migrate now honors actual storage utilization rather than allocated capacity when generating: Assessment recommendations for right-sizing your storage workloads. Business case calculations for accurate cost projections. This shift ensures: Lower migration cost projections: Pay for what you use, not what you’ve overprovisioned. Optimized cloud footprint: Reduce unnecessary storage allocation in Azure. Faster ROI: Build a business case that reflects true utilization, accelerating decision-making. Customer Impact By leveraging utilization-based insights, organizations can unlock significant savings and operate with greater efficiency. For example, if 40% of your storage is overprovisioned, this feature could cut your projected Azure storage costs dramatically, freeing up budget for innovation. How to Get Started Deploy an appliance in your on-premises environment. Build the business case or create an Azure Migrate Assessment for your on-premises workloads. Review the utilization-based recommendations in your assessment report or business case. Learn More Visit Azure Migrate documentation for detailed guidance and start optimizing your migration journey today.Empower your migration decisions with negotiated agreements (EA/MCA) in Azure Migrate
Cost plays the most important part in cloud migration accelerating the decisions. Organizations often hesitate because retail pricing doesn’t reflect their reality. That’s where Microsoft Customer Agreement (MCA) comes in, offering discounts of up to 60% off retail prices, based on your negotiated contract. Now, with Azure Migrate’s support for MCA pricing, you can bring those negotiated rates directly into your assessments. The result? Accurate cost projections, faster decision-making, and a clear path to the cloud. What is MCA? The Microsoft Customer Agreement (MCA) is a modern, flexible purchasing agreement designed to simplify how organizations buy and manage Microsoft services. It replaces older, complex agreements like the Enterprise Agreement (EA) for many customers, offering: Simplified Terms: A single, digital agreement that covers all Microsoft services. Flexible Purchasing: Pay-as-you-go or commit to specific services based on your needs. Negotiated Discounts: Depending on your contract, MCA can offer up to 60% off retail pricing, making Azure more cost-effective. Centralized Billing: Consolidated invoices and transparent cost tracking across subscriptions. With MCA, customers gain predictability, transparency, and control over their cloud spend—critical for planning large-scale migrations. Why MCA Integration in Azure Migrate Matters Previously, Azure Migrate assessments used standard retail pricing, which often didn’t reflect your negotiated terms. This created uncertainty and slowed decision-making. Now, by integrating MCA pricing: No More Guesswork: Assessments reflect your actual negotiated rates. True Cost Visibility: Understand the real financial impact of your migration strategy. Better Planning: Prioritize workloads and optimize budgets with confidence. How It Works? It is very simple to create assessments with negotiated agreement. Just start from the overview click on Create Assessment, add all the required workloads to the assessment scope. Once you move ahead in general settings select Microsoft Customer Agreement (MCA) as Offer/License program and in the Subscription Id field select the appropriate subscription id. After the assessments are created visualize and compare the costs with retail pricing and MCA cost to compare. Key benefits Accuracy: Realistic cost projections based on your MCA. Flexibility: Model multiple migration scenarios with confidence. Speed: Eliminate manual adjustments and accelerate planning. Ready to Get Started? Don’t let cost ambiguity slow down your cloud journey. Start leveraging MCA-powered assessments in Azure Migrate today and move forward with confidence. 👉 Learn more and get started: Assessment Properties - Azure Migrate | Microsoft LearnAzure Migrate: Connected Experiences
Shiva Shastri Sr Product Marketing Manager, Azure Migrate—Product & Ecosystem. Modernization in motion: Evolving at the speed of change. Modernization is the process of transforming legacy IT systems into technologies and architectures that improve agility, scalability, performance and cost-efficiency. It enables businesses to stay competitive by aligning their capabilities with evolving customer and market demands. Modernization is not a one-time event with a finish-line but a continuous journey of evolution. As technology, customer expectations, and competitive landscapes shift, so must the systems and processes that support them. Cloud-native architectures are inherently aligned with modernization while providing access to innovations such as AI. By treating modernization as an ongoing discipline, organizations can stay ahead of disruption, adapt faster to change, and unlock new opportunities. This ability to move faster and smarter is fully realized in Azure — where modernization becomes both a technical upgrade and a strategic advantage. It enables organizations to refocus on core priorities, respond to market shifts in real time, and reduce operational costs. At the heart of this transformation is Azure Migrate — Microsoft’s free, unified platform for cloud migration and modernization. It offers comprehensive capabilities including IT resource discovery, assessment, business case analysis, planning, and execution — all in a workload-agnostic manner. From a single, secure portal, users can manage and monitor the entire journey and cut over to production in Azure with confidence. Today, we’re excited to introduce several impactful Azure Migrate features designed to help you move your on-premises workloads to Azure more efficiently: Accelerated migration and modernization to the cloud. Azure Migrate Agentic method offers an intuitive and insightful approach to cloud transformation. AI assistance assesses on-prem environments, identifies dependencies, and orchestrates workload transitions with minimal manual intervention. By continuously adapting and delegating activities to the appropriate persona, the agents streamline complex migration paths, reduce risk, and accelerate time-to-value. For organizations moving to Azure, the agentic method provides a fast, frictionless route, turning what was once a daunting task into a guided, efficient journey toward modernization. Infrastructure as Code (IaC) plays a pivotal role in cloud migration and modernization by enabling organizations to automate the provisioning and management of infrastructure through code. This approach ensures consistency, scalability, and repeatability across environments, reducing manual errors and accelerating deployment timelines. Azure Migrate now supports IaC, thus simplifying the transition from legacy systems to cloud-native architectures by codifying infrastructure configurations, making it easier to replicate and validate setups. Comprehensive coverage and consistent user experience for your IT estate. No single migration or modernization tool can address the full spectrum of enterprise scenarios and technologies. That’s why Azure Migrate takes a platform-centric approach — delivering a unified, intelligent experience that spans the entire IT estate. By seamlessly interoperating with specialized tools like Database Migration Service (DMS) and GitHub Copilot (GHCP), Azure Migrate empowers organizations to modernize with confidence, flexibility, and speed. Advanced capabilities like 6R analysis — Rehost, Refactor, Rearchitect, Rebuild, Replace, and Retire — empower organizations to tailor modernization strategies to each application, driving smarter, scenario-specific decisions. Support for migration of Arc-enabled resources extends Azure Migrate’s management and governance capabilities to hybrid and multi-cloud environments, ensuring consistency and control regardless of where workloads reside. Additionally, support for Rocky Linux, PostgreSQL, and application awareness empowers teams to assess entire open-source application stacks with dependencies for readiness to migrate to Azure. Secure by design with human in-the-loop. Azure Migrate has recently introduced several security enhancements that reinforce Microsoft's commitment to a "secure by design" and "secure by default" approach. Among the key updates is the friction-free collector, which simplifies secure data collection for migration assessments while minimizing exposure risks. The friction-free discovery in Azure Migrate eliminates the need for deploying discovery appliances for initial assessments. As a result, it accelerates time-to-value, reduces setup complexity, and aligns well with security-conscious environments, making it an efficient and low-risk way to begin cloud migration planning. Azure Migrate supports Private Link and disabling public network access, ensuring that migration traffic remains within secure, private channels. Additionally, the platform enforces data encryption both in transit and at rest, with options for customer-managed keys, and integrates tightly with Azure Key Vault for secure credential and secret management. A security vulnerability report during migration and modernization identifies misconfigurations, outdated components, or exposed services, and the report provides actionable insights that align with Microsoft Defender for Cloud (MDC) threat protection and posture management capabilities. This allows teams to proactively remediate risks and apply MDC’s security controls ensuring the environment is secure from day-1 in Azure. As organizations navigate shifting markets, supply chains, and climate challenges, sustainability has become a strategic imperative. Azure’s carbon optimization capabilities provide clear visibility into potential emission reductions and cost savings, helping IT teams prioritize impactful actions. By unifying planning, execution, and continuity across infrastructure and applications, Azure delivers a consistent modernization experience. Ultimately, cloud-powered innovation enables businesses to drive efficiency, reduce environmental impact, and stay competitive in a rapidly evolving landscape. Learn more Start with a free Azure account if you are new. Sign up for previews of new capabilities and learn more about the workload agnostic method of Azure Migrate. For expert migration help, please try Azure Accelerate. You can also contact your preferred partner or Microsoft field for next steps. Get started in Azure today!Migrating Application Load Balancer from AWS to Azure Application Gateway
Accelerate Innovation and Business Growth with Azure In today’s digital-first world, organizations are reimagining their cloud architectures to drive agility, resilience, and growth. Migrating your application load balancing from AWS Application Load Balancer (ALB) to Azure Application Gateway is more than a technical upgrade—it’s a strategic move to future-proof your business. Azure Application Gateway delivers enterprise-grade performance, security, and flexibility, empowering you to unlock new opportunities and maximize your cloud investment. Key Insights for a Successful Migration 1. Strategic Assessment: Map Capabilities and Opportunities Begin your journey by evaluating your current AWS ALB environment. Identify critical features—path-based routing, health checks, SSL/TLS termination, autoscaling, and security integrations. Map these capabilities to Azure Application Gateway’s advanced features, including zone redundancy, integrated Web Application Firewall (WAF), and seamless certificate management with Azure Key Vault. This assessment is your blueprint for a migration that preserves business continuity and unlocks new value. 2. Preparation: Build a Foundation for Success Preparation is the cornerstone of a smooth migration. Document your existing configurations, export and convert SSL/TLS certificates, and update backend services to leverage Azure’s intelligent routing and monitoring. Reduce DNS TTL values to enable rapid cutover and minimize downtime. Leverage Infrastructure as Code to deploy Azure resources with speed and consistency, ensuring your environment is ready for transformation. 3. Migration Execution: Seamless Transition, Minimal Disruption Deploy Azure Application Gateway and backend resources in parallel with your AWS environment. Validate routing, security, and health probe configurations to ensure flawless operation. During DNS cutover, monitor propagation and service health to deliver a seamless experience for your users. Azure’s integrated diagnostics and monitoring tools provide real-time visibility, empowering you to resolve issues proactively and maintain peak performance. 4. Validation and Optimization: Drive Continuous Improvement Success is measured by outcomes—performance, reliability, and user satisfaction. Compare Azure metrics against your AWS baselines, validate routing accuracy, and test failover scenarios. Use Azure Monitor and Log Analytics to gain actionable insights and optimize your configuration. Embrace an iterative approach to refine your environment, ensuring it evolves with your business needs. Best Practices for Enterprise Migration Leverage Azure’s integrated ecosystem: Use Key Vault for secure certificate management, Monitor for deep observability, and WAF for robust protection. Automate and standardize: Adopt Infrastructure as Code for repeatable, error-free deployments. Test and validate: Employ automated and manual testing to ensure every capability meets your requirements. Minimize downtime: Plan cutover during low-traffic periods and prepare rollback strategies for business assurance. Monitor and optimize: Continuously improve with Azure’s analytics and alerting tools. The Azure Advantage: Empower Your Business Migrating to Azure Application Gateway is a catalyst for digital transformation. With Microsoft’s commitment to security, reliability, and innovation, your organization is equipped to thrive in a dynamic marketplace. Ready to unlock the full potential of your cloud strategy? Discover Azure Application Gateway best practices and join the leaders who are shaping the future of cloud networking.
Pre-Migration Vulnerability Scans:
Migrating applications to the cloud or modernizing infrastructure requires thorough preparation. Whether it’s a cloud platform, a new data center, or a hybrid infrastructure — is a complex process. While organizations focus on optimizing performance, costs, and scalability, security often takes a backseat, leading to potential risks post-migration. One crucial step before migration is conducting a pre-migration scan to identify security vulnerabilities, licensing risks, and code quality issues. Several tools help in pre-migration scanning, including Blackduck, Coverity, Gitleaks, and Semgrep. In this article, we will explore the role of these tools in migration readiness. Why Perform a Pre-Migration Scan? When an application moves from an on-premises environment to the cloud, it interacts with new infrastructures, security models, and compliance regulations. Security scanning tools analyze various aspects of an application, including: Source Code: Detects insecure coding practices, injection vulnerabilities, and logic flaws. Third-Party Dependencies: Identifies vulnerabilities in open-source libraries and software components. Secrets & Credentials: Scans for hardcoded passwords, API keys, and authentication tokens. Infrastructure as Code (IaC): Checks for misconfigurations in Terraform, Kubernetes, Docker, and cloud resources. Compliance Risks: Ensures adherence to security standards like SOC 2, GDPR, HIPAA, and NIST. A pre-migration scan helps in: Identifying Security Vulnerabilities — Detecting potential security threats before moving to the cloud. Ensuring License Compliance — Avoiding open-source license violations. Code Quality Assurance — Identifying issues that could lead to performance degradation post-migration. Reducing Migration Risks — Understanding potential blockers early in the process. Optimizes Performance: Detecting inefficiencies early reduces technical debt. What to use? One of the biggest challenges organizations face during migration is understanding where vulnerabilities exist within their application. This is where scanning tools come into play, each addressing a specific aspect of security and compliance. Take BlackDuck, for instance. Many applications rely on open-source components, but these dependencies come with risks. BlackDuck helps teams analyze these libraries, identifying outdated dependencies and ensuring compliance with licensing policies. If an application heavily relies on open-source libraries, it should be prioritized to check for outdated or vulnerable dependencies. Key Features: Detects Open-Source Vulnerabilities: Identifies known CVEs (Common Vulnerabilities and Exposures) in third-party libraries. License Compliance Management: Ensures adherence to open-source licenses like GPL, MIT, Apache, etc. Integration with DevOps: Works seamlessly with CI/CD pipelines to automate security checks. Then there’s Coverity, which tackles security flaws hidden in the source code. A migration process should not only move applications but also ensure they are stable and secure in the new environment. Coverity, a Static Application Security Testing (SAST) tool, scans code for potential weaknesses — whether it’s SQL injection, cross-site scripting (XSS), or memory leaks. By fixing these defects before migration, teams can prevent costly failures post-deployment. Key Features: Deep Code Analysis: Identifies issues such as buffer overflows, SQL injection, cross-site scripting (XSS), and memory leaks. Supports Multiple Languages: Works with C, C++, Java, JavaScript, Python, Go, and more. Seamless CI/CD Integration: Can be integrated into GitHub, GitLab, and Azure DevOps workflows. Another key concern is secrets management. Hardcoded API keys, passwords, and tokens often find their way into repositories, creating a massive security risk. Gitleaks scans Git repositories to detect and eliminate these vulnerabilities before they can be exploited. Imagine pushing an application to the cloud, only to realize that an exposed API key is granting unauthorized access to critical services. By integrating Gitleaks into the pre-migration process, organizations can avoid such missteps. Key Features: Scans for Hardcoded Secrets: Detects sensitive information in commits, branches, and history. Pre-Commit Hooks: Prevents secrets from being pushed to Git repositories. Customizable Rulesets: Allows teams to define their own secret detection policies. Compatible with GitHub & GitLab: Easily integrates with popular version control platforms. Finally, Semgrep provides a flexible approach to enforcing security best practices. Unlike traditional scanning tools, it allows teams to define custom security rules to catch coding patterns that may lead to vulnerabilities. Whether it’s identifying misconfigurations or enforcing secure coding standards, Semgrep adds an extra layer of protection, ensuring applications follow best practices before going live in the cloud. Comparing the Tools: Tool Primary Use Case Best for CI/CD Integration BlackDuck Open-source security & license compliance Dependency scanning Yes Coverity Static code analysis Code vulnerabilities Yes Gitleaks Secret & credential scanning Preventing secret leaks Yes Semgrep Customizable code analysis Secure coding & policy enforcement Yes Intergration with the code: Automation is key to ensuring that security scans are not overlooked or treated as one-time activities. To streamline the process, organizations integrate these scanning tools directly into their Continuous Integration/Continuous Deployment (CI/CD) pipeline, ensuring security checks are part of every development cycle. A typical setup involves defining a pipeline configuration that automates the execution of each tool at various stages: Once the scans are complete, the results are typically stored as JSON reports in pipeline artifacts or logging systems, making it easy to track, analyze, and prioritize issues before proceeding with the migration. By integrating these tools into the CI/CD pipeline, security becomes an automated and continuous process, rather than a last-minute checkpoint. Challenges in Pre-Migration Security Scanning False Positives: Some tools generate excessive alerts, requiring manual verification. Lack of Security Awareness: Developers may not be trained to interpret scan results effectively. Integration with DevOps: Security scans must fit into existing CI/CD pipelines without slowing down deployments. Handling Legacy Code: Older applications may contain security issues that modern tools struggle to assess. Conclusion By proactively addressing these challenges and incorporating security scanning into the migration strategy, organizations can minimize risks and ensure a smooth, secure transition to their new environment. However, scanning alone is not enough. Following best practices — such as defining a security baseline, automating security checks in CI/CD pipelines, prioritizing remediation, and securing the migration process — ensures a smooth, risk-free transition. A secure migration is not just about moving workloads; it’s about ensuring that security remains a top priority at every stage. By taking a proactive security approach, organizations can prevent security incidents before they happen, making the migration process safer, smoother, and more resilient.