endpoint security
11 TopicsThe Worm in the Supply Chain: How Defender for Endpoint and Sentinel for SAP BTP Caught Shai-Hulud
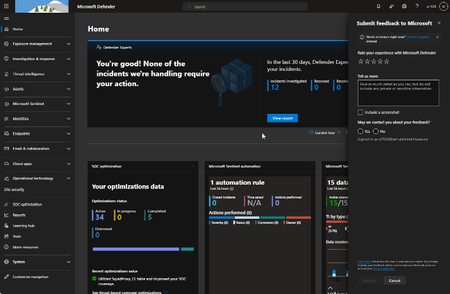
On 29 April 2026, malicious versions of multiple SAP ecosystem npm packages were briefly published, creating a supply-chain exposure for SAP Cloud Application Programming (CAP) development environments and CI/CD pipelines. For a brief window that morning, affected developers have executed a credential-stealing payload on a workstation or, in higher-impact cases, within a CI/CD pipeline. SAP developers don't usually think of themselves as a juicy npm target. CAP, BTP, Fiori - that's enterprise turf, not crypto-stealer type territory – Until it is. Join me for the ride. See our latest click-video for an even more dynamic experience of SAP compromises. Affected packages and scope Four official npm packages from the SAP development ecosystem were published in malicious versions that day. Security researchers are calling the campaign "Mini Shai-Hulud" - the little cousin of the worm family that has been chewing its way through open-source registries for months. So, the "mini" part is a generous description in my opinion. Shai-Hulud has wriggled directly into the SAP supply chain, and that detail alone deserves a pause... SAP CAP is now interesting enough to have become a target. Four packages, all wearing legitimate SAP branding, all quietly swapped for evil twins: @cap-js/sqlite v2.2.2 @cap-js/postgres v2.2.2 @cap-js/db-service v2.10.1 mbt v1.2.48 These packages are not peripheral dependencies. The @cap-js/* modules are part of the SAP CAP Model used across custom development on SAP BTP, while mbt is the Cloud MTA Build Tool commonly embedded in CI/CD workflows that package and deploy Multi-Target Applications to BTP and on-premises environments. At roughly 930,000 weekly downloads, the combined exposure created meaningful downstream attack surface. The good news: SAP spotted the compromise fast, yanked the bad versions, and shipped clean replacements. The official guidance lives in SAP Security Note 3747787 - which carries the list of indicators of compromise, file hashes, and mitigation steps. Enough theory and evidence talk! Now, SHOW ME the detection! When the worm stirs beneath the sand, weak defenses vanish first. Observed telemetry in Microsoft Security products See below excerpt of Microsoft Defender for Endpoint from a compromised developer machine. The worm was neutralized immediately. Check the detection time (same day of release): Windows Defender AV detected malware ToString: DefenderDetection: File: /Users/User***/Projects/dara-api-manager-ui/node_modules/mbt/File***.js, Sha256: *** [Trojan:JS/SPchnStlr.BB], BlockingStatus: Prevented, BlockingStatusPriority: 900 DetectionTime: 2026-04-29 11:52:11Z DetectorName: Microsoft.Cyber.ObservationDetectors.DefenderConcreteDetector Observations (2): DefenderObservation Description: Defender detected and quarantined 'Trojan:JS/SPchnStlr.BB' in file 'File***.js' ThreatCategory = Trojan, ThreatFamily = SPchnStlr, How the Threat Actors Operationalized the Stolen Data The compromise allowed harvesting GitHub tokens, AWS/Azure/GCP secrets, npm credentials, Kubernetes config, SSH keys, .npmrc and .git-credentials files, and CI/CD environment variables. The hackers created a public GitHub repository on the victim’s own account, tagged with the description “A Mini Shai-Hulud has Appeared“ to exfiltrate their reaping. Within hours, more than a thousand such repositories were visible in public GitHub search. For additional views on the topic check out the blogs of our Sentinel for SAP partners: Onapsis, Pathlock, and SecurityBridge. Containment and Impact Reduction If you were not as lucky as the developer using Defender for Endpoint and VS Code, you need end to end monitoring of your landscape in and around SAP. Once the worm is loose with cloud tokens it may appear in various unexpected places. Microsoft Sentinel Solution for SAP covers your ERP crown jewels, your SAP BTP landscape and allows informed correlation with the rest of your IT estate. Microsoft’s correlation engine: ensures traceability automatic attack disruption and just-in-time hardening of potential attack paths. Developers using the cloud-based IDE SAP Business Application Studio are out of reach by Defender for Endpoint but profit from threat monitoring through Sentinel for SAP BTP integrating SAP BTP’s malware scanner the same way. See this in action in this click-video and in below screenshot. SOC analysts get actionable insights and tailored guidance from Security Copilot once SAP BTP signals are added to the Microsoft incident graph - no matter where the threat involving SAP originates from. Getting Started with Sentinel Solution for SAP Rollout of Sentinel for SAP BTP can happen immediately. Learn more from our deployment guide. Check out the security content reference for more info out-of-the-box detections. Sentinel for SAP which covers your ERP solutions and more, requires configuration of SAP Integration Suite as intermediary step. Learn more from our deployment guide. Check out the security content reference for more info out-of-the-box detections Final Words This incident illustrates how far the SAP BTP attack surface now extends and why patching alone is insufficient once malicious code reaches developer tooling and build infrastructure. Effective defense also requires telemetry, correlation, and response coverage across SAP and non-SAP environments. See you out there folks! #Kudos to Mahesh Mandva and Cameron Gardiner on riding shai-holud with me. Feel free to reach out to talk more about SAP Cyber Security. Cheers, Martin Useful Links SAP Note 3747787 with mitigation guide Mini Shai-Hulud: Multi-Ecosystem Developer Supply Chain Attack – Lab Space Click-Demo for SAP Cyber Security with Microsoft Sentinel for SAP Security Content | Microsoft Learn Sentinel for SAP BTP Security Content | Microsoft Learn719Views0likes0CommentsMicrosoft Sentinel Solution for SAP® Applications - New data exfiltration detection rules
On August 2022, Microsoft Sentinel solution for SAP was made generally available (GA). Together with releasing the Microsoft Sentinel Solution for SAP® Applications, new additional OOTB content has been added. This blog covers five new data exfiltration detection rules included with the Microsoft Sentinel Solution for SAP® Applications (these rules are currently in preview).9.4KViews2likes1CommentPublic preview announcement: Defender for IOT solution for Microsoft Sentinel
We are excited to announce the public preview of our Defender for IoT solution for Microsoft Sentinel. With this solution, Microsoft Sentinel delivers the first in the industry native SOC experience for IT and OT environments5.3KViews2likes1CommentIoT Entity Page - Enhance IoT/OT Threat Monitoring in Your SOC with Sentinel and Defender for IoT
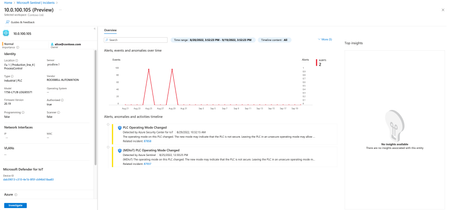
The new IoT device entity page is designed to help your SOC investigate incidents that involve IoT/OT devices in your environment, by providing the full OT/IoT context through Microsoft Defender for IoT, our agentless IoT/OT security monitoring solution, to Sentinel. This enables SOC teams to detect and respond more quickly across all domains to the entire attack timeline.6.3KViews2likes0Comments
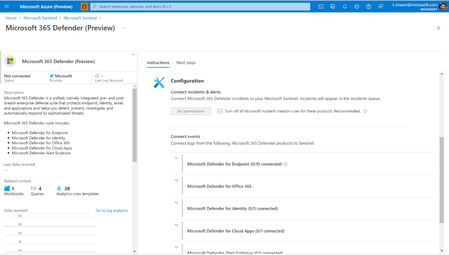
What’s new: Closer integration between Microsoft Sentinel and Microsoft 365 Defender
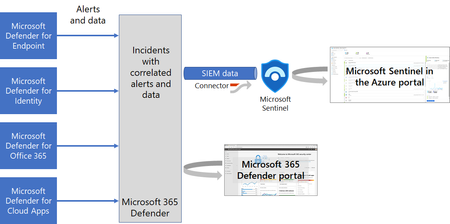
Over a year ago, we first announced the integration between Microsoft Sentinel and Microsoft 365 Defender as part of the Microsoft SIEM and XDR story. Combining the breadth of a SIEM with the depth of XDR to give security professionals the integrated toolset they need to fight against attacks that take advantage of today’s diverse, distributed, and complex environments. Today, we are happy to share several new preview updates8.1KViews1like1CommentModernize Log Management with the Maturity Model for Event Log Management (M-21-31) Solution
Announcing the Microsoft Sentinel: Maturity Model for Event Log Management (M-21-31) Solution. This solution consists of (1) Workbook, (8) Analytics Rules, (4) Hunting Queries, and (3) Playbooks. The solution provides actionable insights into log management posture and intuitive steps for remediation to drive compliance across event logging maturity levels. The workbook serves as a starting point for designing and reporting event log management capabilities by providing visibility into current posture mapped against the four maturity tiers. 12KViews2likes6Comments
Defending Critical Infrastructure with the Microsoft Sentinel: IT/OT Threat Monitoring Solution
The Microsoft Sentinel: IT/OT Threat Monitoring with Defender for IoT Solution provides the foundation for building a SOC for monitoring IoT/ OT and includes (1) workbook for visibility/reporting, (14) analytics rules for monitoring, and (4) playbooks for response. The workbook leverages Microsoft Sentinel telemetry to create visualization to understand, analyze, and respond to IoT/OT threats. Understanding alerts over time provides unprecedented insights into security posture and where teams need to focus to harden against threats. Deep links directly to Microsoft Defender for IoT alerts empower analysts to focus on remediating threats rather than pivoting between tools.8.4KViews4likes1Comment
Integrating SIEM + XDR: Azure Sentinel and Azure Defender bi-directional incident sync
Azure Sentinel and Azure Defender now share the concept of an incident. This new capability enables you to update or close Azure Defender incidents from within Azure Sentinel and complements a similar feature already available for Microsoft 365 Defender incidents and Azure Sentinel15KViews3likes3Comments