endpoint security
11 Topics
Integrating SIEM + XDR: Azure Sentinel and Azure Defender bi-directional incident sync
Azure Sentinel and Azure Defender now share the concept of an incident. This new capability enables you to update or close Azure Defender incidents from within Azure Sentinel and complements a similar feature already available for Microsoft 365 Defender incidents and Azure Sentinel15KViews3likes3CommentsModernize Log Management with the Maturity Model for Event Log Management (M-21-31) Solution
Announcing the Microsoft Sentinel: Maturity Model for Event Log Management (M-21-31) Solution. This solution consists of (1) Workbook, (8) Analytics Rules, (4) Hunting Queries, and (3) Playbooks. The solution provides actionable insights into log management posture and intuitive steps for remediation to drive compliance across event logging maturity levels. The workbook serves as a starting point for designing and reporting event log management capabilities by providing visibility into current posture mapped against the four maturity tiers. 12KViews2likes6Comments
Microsoft Sentinel Solution for SAP® Applications - New data exfiltration detection rules
On August 2022, Microsoft Sentinel solution for SAP was made generally available (GA). Together with releasing the Microsoft Sentinel Solution for SAP® Applications, new additional OOTB content has been added. This blog covers five new data exfiltration detection rules included with the Microsoft Sentinel Solution for SAP® Applications (these rules are currently in preview).9.4KViews2likes1CommentDefending Critical Infrastructure with the Microsoft Sentinel: IT/OT Threat Monitoring Solution
The Microsoft Sentinel: IT/OT Threat Monitoring with Defender for IoT Solution provides the foundation for building a SOC for monitoring IoT/ OT and includes (1) workbook for visibility/reporting, (14) analytics rules for monitoring, and (4) playbooks for response. The workbook leverages Microsoft Sentinel telemetry to create visualization to understand, analyze, and respond to IoT/OT threats. Understanding alerts over time provides unprecedented insights into security posture and where teams need to focus to harden against threats. Deep links directly to Microsoft Defender for IoT alerts empower analysts to focus on remediating threats rather than pivoting between tools.8.4KViews4likes1Comment
What’s new: Closer integration between Microsoft Sentinel and Microsoft 365 Defender
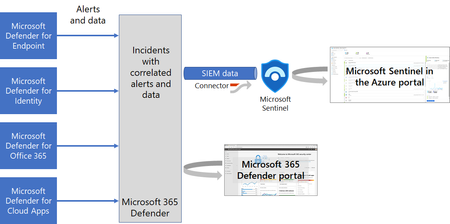
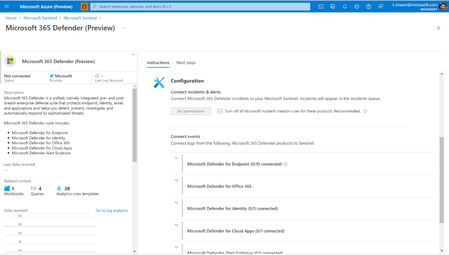
Over a year ago, we first announced the integration between Microsoft Sentinel and Microsoft 365 Defender as part of the Microsoft SIEM and XDR story. Combining the breadth of a SIEM with the depth of XDR to give security professionals the integrated toolset they need to fight against attacks that take advantage of today’s diverse, distributed, and complex environments. Today, we are happy to share several new preview updates8.1KViews1like1CommentIoT Entity Page - Enhance IoT/OT Threat Monitoring in Your SOC with Sentinel and Defender for IoT
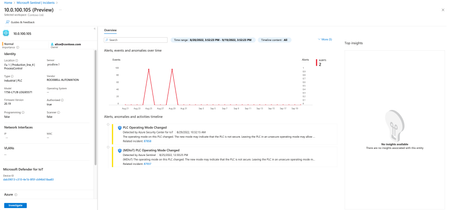
The new IoT device entity page is designed to help your SOC investigate incidents that involve IoT/OT devices in your environment, by providing the full OT/IoT context through Microsoft Defender for IoT, our agentless IoT/OT security monitoring solution, to Sentinel. This enables SOC teams to detect and respond more quickly across all domains to the entire attack timeline.6.3KViews2likes0CommentsPublic preview announcement: Defender for IOT solution for Microsoft Sentinel
We are excited to announce the public preview of our Defender for IoT solution for Microsoft Sentinel. With this solution, Microsoft Sentinel delivers the first in the industry native SOC experience for IT and OT environments5.3KViews2likes1Comment