azure backup
7 TopicsOperating Azure Backup at Scale: Day-2 Excellence for IaaS, PaaS, and Storage Workloads
Hello Folks! If you have ever inherited a sprawling Azure environment and quietly wondered whether every VM, database, AKS cluster, and storage account in it is actually being backed up the way the business thinks it is, you are in good company. In session this session of the Microsoft Azure Infra Summit 2026, Bhavya Tadikonda and Shobhit Garg from the Azure Resiliency product team walked us through how Azure Backup is evolving into a unified, application-centric service that protects IaaS, PaaS, AKS, PostgreSQL, and unstructured storage from a single pane of glass. Why IT Pros Should Care Backup is one of those topics nobody talks about until the day it really matters. Then it is the only topic. The session framed Azure Resiliency around three pillars (infrastructure resiliency, data resiliency, and cyber recovery), and Azure Backup sits squarely in the middle of the last two. The reason this session lands hard for ops teams is that the surface area we are expected to protect keeps growing: VMs, SQL on Azure VMs, SAP HANA, Sybase, AKS, PostgreSQL flexible servers, Azure Files, blobs, ADLS, and on it goes. Here is why this should matter to you: One vault model now protects IaaS, PaaS, AKS, PostgreSQL flexible server, and storage workloads, with consistent policies and reporting. Cyber resiliency is built into the vault layer with immutability, soft delete, and multi-user authorization, so backups themselves can survive a ransomware event. A new threat detection preview (powered by Microsoft Defender for Cloud) scans restore points and tags them healthy or suspicious before you recover. Azure Backup for AKS protects cluster resources and persistent volumes with granular restores and immutable recovery points. You can configure backups from VS Code through the Azure MCP server using natural language prompts, which is genuinely useful when you are protecting dozens of resources. In short, fewer point tools, fewer scripts, and a much better chance of actually meeting your RPO and RTO targets when the day comes. What Operating Azure Backup at Scale Means, a Technical Overview The session opened with a quick reminder that resiliency in Azure stands on three pillars working together. Infrastructure resiliency keeps the underlying VMs, zones, and networks alive. Data resiliency keeps your data intact, available, and recoverable. Cyber recovery assumes the worst (a ransomware attack or insider event) and gives you air-gapped, immutable backups plus isolated recovery to restore safely. Azure Backup is the connective tissue across data resiliency and cyber recovery. At the data layer, it offers snapshot tier backups for instant operational recovery (with up to a four-hour RPO), vault tier backups for long-term retention, and an archive tier for cold compliance storage. For databases, you get database-aware protection for SQL Server in Azure VMs, SAP HANA, and SAP ASE (Sybase), with point-in-time restore and log backups as frequent as every 15 minutes. That gets you to an RPO as low as 15 minutes for SQL, which is a number most IT pros will recognise as good enough for the vast majority of business apps. At the vault layer, three security primitives stack together: soft delete (deleted backups are kept for an additional retention window), immutability (no operation can shorten retention or destroy recovery points before expiry), and multi-user authorization (critical operations need approval from a second admin via a Resource Guard). These are not bolt-ons. They are baked into Recovery Services vaults and Backup vaults. How It Works, Under the Hood The session followed a Contoso scenario where John, a cloud architect, configures backup for an application VM and a database VM. He picks a Recovery Services vault, creates a backup policy, and defines frequency and retention based on his RTO and RPO requirements. For the Linux application tier, John enables the new agentless, crash-consistent backup, which is non-invasive and protects performance-sensitive workloads without an in-guest agent. For the database tier, John enables Azure Backup for SQL in Azure VMs. The service auto-discovers all databases inside the VM, removes the manual config dance, and lets him layer log backups, differential backups, and archival retention. For SQL Always On, HANA HSR, and Sybase HA clusters, snapshot-based acceleration gives him faster backups and instant restores. Then John turns to cyber resiliency. From vault properties he reviews soft delete, immutability, and multi-user authorization, then enables the new threat detection preview. This integration with Microsoft Defender for Cloud scans restore points for malware so you can confirm a recovery point is clean before you roll back. Inside the protected items view, each restore point is marked healthy or suspicious, which is exactly the signal you want during an incident response. For PaaS and cloud-native, Shobhit took over and walked through Azure Backup for AKS and Azure Backup for PostgreSQL flexible server. AKS protection covers the cluster resources, the persistent volumes, and the namespaces, with automated scheduled backups, granular restores, immutable recovery points, and flexible retention. PostgreSQL flexible server gets vaulted backups with long-term retention plus a unified view for monitoring and alerts. The piece that made the room sit up was the demo of configuring backup from VS Code using the Azure MCP server. John installs the Azure MCP extension, validates mcp.json, opens the chat window, and starts the MCP server. He prompts it to list unprotected AKS clusters in his subscription, then asks it to configure backup for a specific cluster. The MCP server reuses an existing vault and policy, creates the protected item, and applies the enterprise security defaults. That is the kind of conversational ops experience that scales nicely when you have hundreds of resources. For unstructured data, Azure Backup brings file shares, ADLS data, application artifacts, and large object stores into the same vault-based model, with off-site protection, long-term retention, immutability, soft delete, and MUA applied consistently. Real-World Value So where does the ROI show up? A few honest scenarios: Ransomware attack on production VMs. With immutability and MUA, even a compromised admin account cannot destroy your recovery points. With threat detection, you avoid restoring an infected snapshot. Accidental deletion of an AKS namespace. Granular AKS backup gets you a controlled, application-aware restore without redeploying the whole cluster. Compliance audit on a regulated workload. Vault tier plus archive tier gives you the retention you need without inflating hot storage costs. A cloud architect onboarding 30 new VMs and 10 PostgreSQL servers. Using Azure MCP from VS Code, they can configure backup conversationally instead of click-clicking through portal blades. A BCDR drill. The resiliency agent (powered by Azure Copilot) can recommend enabling Azure Site Recovery on top of Azure Backup for stricter RTO and RPO, then guide you through enabling it. Honest tradeoff: threat detection is in preview, agentless crash-consistent backup is newer than the in-guest variant, and multi-user authorization requires a Resource Guard that lives in a separate subscription (ideally a separate tenant). That is extra setup work, but it is the right design for separation of duties. Getting Started Concrete first steps you can take this week: Open Backup Center (or the new Resiliency in Azure experience) and inventory what is already protected versus exposed. Pick one Recovery Services vault and turn on enhanced soft delete with a meaningful retention period, then make it AlwaysOn for production. Stand up a Resource Guard in a separate subscription or tenant and wire up MUA on your most critical vault. For a non-production AKS cluster, install the Backup extension and protect a namespace end to end, including a test restore. Try the Azure MCP server from VS Code to list unprotected resources and configure backup with a prompt. If you run SQL on Azure VMs, enable log backups every 15 minutes on one database and validate a point-in-time restore. Resources Azure Backup documentation (official docs for vaults, policies, and workload protection) Configure Multi-user authorization using Resource Guard (separation of duties for critical backup operations) Threat detection in Azure Backup with Microsoft Defender for Cloud (preview) (healthy or suspicious tagging for VM restore points) Back up Azure Kubernetes Service by using Azure Backup (cluster resources, namespaces, and persistent volumes) Azure Backup for PostgreSQL flexible server (vaulted backups with long-term retention) Azure Site Recovery documentation (DR replication on top of Azure Backup) Keep Learning... Catch the full Microsoft Azure Infra Summit 2026 session playlist here Cheers! Pierre426Views1like0CommentsAZ-500: Microsoft Azure Security Technologies Study Guide
The AZ-500 certification provides professionals with the skills and knowledge needed to secure Azure infrastructure, services, and data. The exam covers identity and access management, data protection, platform security, and governance in Azure. Learners can prepare for the exam with Microsoft's self-paced curriculum, instructor-led course, and documentation. The certification measures the learner’s knowledge of managing, monitoring, and implementing security for resources in Azure, multi-cloud, and hybrid environments. Azure Firewall, Key Vault, and Azure Active Directory are some of the topics covered in the exam.23KViews4likes3CommentsWhat Nonprofits Need to Know About Cloud Storage Redundancy
At the heart of this post is Kairos IMS, an innovative Impact Management System designed to empower human-serving nonprofits and social impact organizations. Co-developed by the Urban League of Broward County and our trusted technology partner, Impactful, Kairos IMS reduces administrative burdens, enhances holistic care, and enables organizations to leverage data for increased agility and seamless service delivery. In this blog series, we’ll take a closer look at the powerful technologies that fuel Kairos IMS, from Azure services to security frameworks, offering insight into how modern infrastructure supports mission-driven impact. Click here to learn more. What Is Azure Storage Redundancy? Azure storage redundancy refers to how your data is copied and stored across multiple physical locations to keep it safe and accessible—even if hardware fails or a data center goes offline. Think of it as creating backup copies in real-time, so if one server goes down, another one picks up right where it left off. Azure offers several redundancy options, each with a different level of protection and cost: Locally Redundant Storage (LRS): Data is replicated three times within a single data center. Great for budget-conscious orgs. Cheapest option. Zone-Redundant Storage (ZRS): Data is stored across three different availability zones in the same region. Offers higher resilience. Mid-tier pricing. Geo-Redundant Storage (GRS): Data is copied to a secondary region hundreds of miles away. Ideal for disaster recovery. Higher cost. Read-Access Geo-Redundant Storage (RA-GRS): Like GRS, but you can read from the secondary region even if the primary one is down. Why Redundancy Matters for Nonprofits Nonprofits are often targets of cyberattacks and also operate in environments where internet outages or power failures can occur. Redundancy ensures that: You don’t lose important grant or donor data. Services like SharePoint or hosted databases stay online. You can continue serving your community even in unexpected situations. Using Your $2,000 in Azure Credits Wisely Microsoft offers approved nonprofits $2,000 in Azure credits each year through its Microsoft for Nonprofits program. Here’s how you can use those credits for storage redundancy: Start small with LRS or ZRS for frequently used files or backups. Use GRS for mission-critical data like financial or compliance documents. Back up virtual machines or databases with geo-redundancy for restore-anywhere capabilities. Pair with Azure Backup or Site Recovery for additional resilience. Tip: Monitor your credit usage in the Azure Cost Management and Billing dashboard so you don’t overspend. Getting Started If your nonprofit already has an Azure subscription through Microsoft's grant, you're ready to go! Here’s what to do next: Log into the Azure portal with admin credentials. Navigate to Storage Accounts > + Create. Choose your region and desired redundancy level. Configure Advanced, Networking, Data protection, Encryption, and Tag settings and then select Review + create to go over your configuration. Select Create to make your storage account. Start uploading files or connecting services like Microsoft 365 or backup tools. If you’re unsure which redundancy level is right for your nonprofit, a good starting point is to use LRS for general storage and reserve GRS for the most critical data. Storage redundancy isn’t just a technical term—it’s peace of mind. With Azure and your nonprofit credits, you can build a more resilient and secure digital foundation without spending out of pocket. Not sure how to get started? Microsoft has nonprofit partners and tech support that can help you make the most of your credits. Your mission is too important to risk downtime—let’s make sure your data is always safe and accessible.243Views0likes0CommentsProtecting Your Data: How to Back up a Virtual Machine in Azure
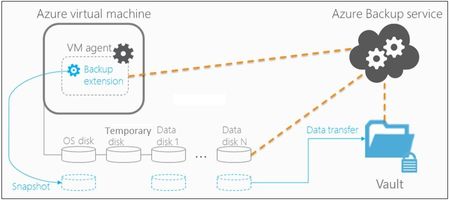
Backing up a virtual machine (VM) in Azure is a critical step in protecting your data. By following the steps outlined in this blog post, you can ensure that your virtual machine is regularly backed up and your data is protected. Nonprofits can use this feature to safeguard their critical data and ensure that they can continue to serve their mission even in the face of a disaster.7.6KViews4likes0CommentsAzure Backup: Best Practices for Secure Data Protection and Restoration
Azure Backup is a powerful and flexible backup solution that can help protect your critical data and applications in a scalable and cost-effective way and can be easily integrated with other Azure services for a comprehensive data protection strategy.12KViews3likes0CommentsCMMC Recovery (RE) Domain Overview and Strategy
One of the key areas where the Cybersecurity Maturity Model Certification (CMMC) expands on NIST 800-171 is system recovery, specifically the ability to recover from any event that compromises the integrity and availability of data. Backups are called out in the Recovery (RE) Domain and include the requirement to backup all content, not just CUI and other critical content. Further, testing backups is now a requirement and likely to be validated during a CMMC assessment.5.4KViews0likes0Comments
Friday Five: Creating a Multi-Arch Docker Image with Azure DevOps, and More!
First published on MSDN on Nov 16, 2018 Creating a multi-arch Docker image with Azure DevOpsTobias Fenster has worked for 15 years in various development and infrastructure roles including head of development and head of technical consulting before becoming CTO for German D365 Business Central ISV Axians Infoma602Views0likes0Comments