active directory
1037 Topics
Kerberos Event ID 4771 (0x18) occurring for all domain users despite successful manual logons
Hello, At one of our clients, we are experiencing repeated Kerberos Pre-Authentication Failed - Event ID 4771, with Failure Code 0x18, on the primary Domain Controller. The issue affects all domain users. All users are able to log in manually without any issues using their credentials. However, Event ID 4771 failures continue to be generated in the background, including outside normal working hours. From the Event ID 4771 entries, we can see authentication attempts originating from different internal systems, including user workstations, the secondary Domain Controller, and the proxy server. As part of the troubleshooting, we performed the following command for one of the affected users in order to clear the Kerberos ticket cache: klist purge The cache was cleared successfully, but after monitoring the environment again, Event ID 4771 continued to be generated and the issue remained unchanged. We would appreciate your assistance in identifying the root cause of these repeated Kerberos pre-authentication failures and advising us on the recommended next troubleshooting steps. Thank you.2Views0likes0Comments
2026-04 Update Breaks Domain Logins
I have an Active Directory domain that is old (from 2000!) that has been upgraded and moved to newer versions of Windows Server and Active Directory. I have domain controller VMs running Windows Server 2025 Standard Edition. Unfortunately they installed the latest 2026-04 patches which my have changed the Kerberos encryption from RC4 to AES. This has resulted in my not being able to log into any Active Directory domain accounts and the domain controllers themselves. I can only log into workstations using the local account. Suffice to say this a nightmare. Any ideas how to fix it since I can't access the usual tools like Active Directory Users and Computers, Hyper-V won't connect to the VMs, etc. Thanks. SSolved5.8KViews2likes9Comments
Update Daylight saving time on Windows server client from domain controller
Hello, The September 2026 cumulative update includes the Morocco Daylight Saving Time update. We are planning to update our domain controllers to apply the new DST schedule. Is there any option for domain-joined Windows Servers to update their Daylight Saving Time configuration from the domain controller without installing the September 2026 cumulative update on each server ? Or does the update need to be installed on every Windows Server individually ?Solved118Views0likes2Comments
Strict users to use specific software windows server 2022
I have MT5 installed on (C:\Program Files\MetaTrader 5) there are the meta trader 5 terminal64.exe and MetaEditor64.exe applications, mt5 data folder as follow C:\Users\Administrator\AppData\Roaming\MetaQuotes\Terminal\ MT4 on (C:\Program Files (x86)\MetaTrader 4) there are applications terminal.exe and metaeditor.exe and data folder as follow C:\Users\Administrator\AppData\Roaming\MetaQuotes\Terminal\ I use windows server 2022 and I want to create user accounts each account have access only to MT4 or MT5 and the meta editor and data folder only and each user can use the software MT4 or MT5 based on assigned group, users can use the same software at the same time in their own accounts I need 2 windows powershell scripts 1-create 2 user groups for MT4 and MT5 with the access restrcicted to all windows software and features execpt the MT4 or MT5 and the meta editor, and the data folder and desktop showing these icons/shortcuts and webview2 runtime to installed be allowed because it is needed by meta trader ( user cannot see windows bar cannot use any windows software, and the most important that the MT4 or MT5 software to be always running and start always after windows reboot/restart not when user log on, these software run trading algoeithms and must be working around the clock even if the user is not logged in 2- interactive script that use to create the users44Views1like0Comments
Two-tier AD Certificate Services error importing cert into SubCA
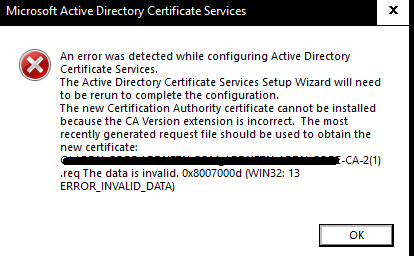
Hello, I'm new here, but excited about being able to hob nob with all you in furthering our IT goals. I'm setting up my root and Subordinate CA and I'm importing my rootCA issued, subCA certificate into the subCA. I get I get the same error when the subCA automatically exports its cert req to the root Ca and when I do it manually. I also get this error whether i'm using X.509 or p7b files. what's unusual about this error is that it seems to be referencing a .req file with a '(1)' added to the end of the title. Original .req did not have the '(1)'. any assistance I can get from the community would be appreciated.245Views0likes2CommentsHow are you managing Group Policy changes after AGPM end of support?
Hi, I’m interested in how organizations are handling Group Policy change management now that AGPM is no longer supported. In environments where GPOs are still heavily used, what are you relying on today for version history, change tracking, rollback and approvals? Are you continuing with AGPM, moving to products such as GPOADmin or Cayosoft, or mainly using native GPMC backups and PowerShell? I’m also interested in whether there is still a gap around having a clear web-based view of GPO history and changes, especially being able to understand exactly what changed and which users or computers may be affected before a change is applied. I’d be interested to hear how this is handled in real production environments and what parts of the process are still manual or difficult.147Views0likes1CommentIssue with Temporary Profile on Windows Server 2025 after renaming built-in Administrator account
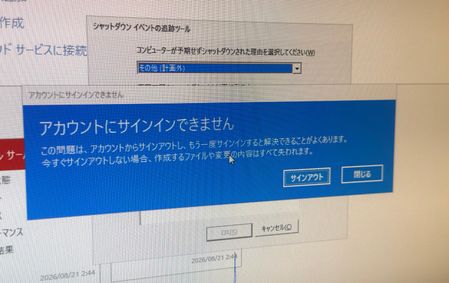
Hi everyone, I am facing an issue with a temporary profile on Windows Server. Environment details: ・OS: Windows Server 2025 Datacenter ・Setup: On-premises environment with 2 servers (AD DS Domain Controller and Web Server) ・Affected Server: Web Server (Domain joined) Recently, I renamed the built-in Administrator account on the Web Server. After that, the system became completely unresponsive, so I had to force a power off. Upon signing in after the reboot, I received the error message: "We can't sign in to your account" (or "You've been signed in with a temporary profile"). It seems the profile folder or registry mapping for the renamed Administrator account was corrupted due to the force shutdown. I tried restarting the server, but the issue persists. Could anyone please advise on the proper way to resolve this registry/profile conflict and safely restore the renamed Administrator profile? Please note that I am a native Japanese speaker and a beginner in IT, so I may not fully understand complex technical English. Simple, step-by-step instructions would be greatly appreciated! Thank you in advance for your help! Translated by Gemini, grammar checked by DeepL515Views2likes7Comments
Can't share a folder on a local network in Microsoft Windows Server 2025 STD
We have two Microsoft Windows Server 2025 Standard (Version 24H2, Build Number 26100.32995) servers in our Active Directory. We can't share folders; it constantly asks for a username and password. We've tried every solution, but nothing worked. I found a similar thread, but the solutions there didn't work either. topic : https://learn.microsoft.com/en-us/answers/questions/5559013/opening-fire-share-on-2025-server-from-another-202 How can i solve this sharing problem ?267Views0likes3CommentsRemoval of old CA server stale data
Hi, I'm rebuilding some DC's and figured I'd tidy everything up before doing so as I've come into this with a messy environment. from this, I found an old Trusted Root CA, the certificate authority server was decommissioned in 2021 and all certificates have had an expiry date from 2021. its still being pushed out to domain devices such as servers and desktops. I tried running the 'certutil -dsdelca' command however this comes back with invalid command. I guess the best option is just to remove the class objects from the ADSI edit? as there is a class in AIA, CDP, Certification Authorities, KRA with the certificate nameSolved296Views0likes1Comment