Events
Recent Blogs
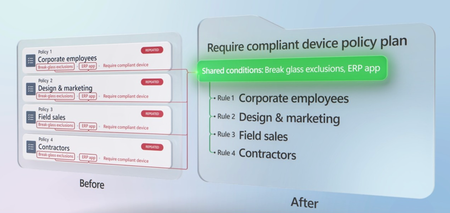
- Add a rule for each requirement, like phishing-resistant MFA or compliant devices, and keep the shared scope in one place. Build a plan around a user group, like headquarters staff, or a share...Oct 29, 20261.2KViews1like0Comments
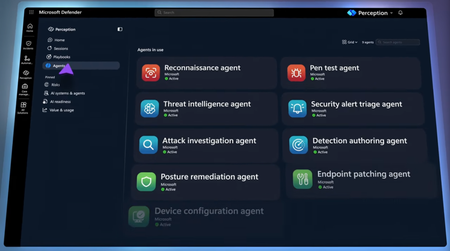
- Point red, blue, and green AI agent teams at a known threat actor, confirm which vulnerabilities attackers can reach, then deploy KQL detections, harden your posture, and merge a tested code fix...Oct 20, 2026365Views0likes0Comments
Tags
No tags to show