Forum Discussion

Genntoo
Nov 03, 2026Copper Contributor
Microsoft Defender: Problems with correlations in Azure Sentinel
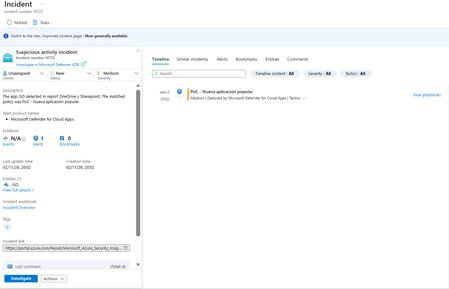
Hi community! Sharing something we've noticed this week, in case anyone else is running into the same thing. Since around October 31, several of our environments have been generating more incidents...

Genntoo
Nov 05, 2026Copper Contributor
Thank you very much for the response. It turns out it was some kind of bug or issue on the Defender side that affected all clients; it was resolved on November 3rd around 11:12 UTC, and the nonsensical correlations stopped appearing. That said, we’ve learned that automation rules should be based on the "analytic rule name" rather than the incident "title," as a change in the name could cause a mismatch and prevent the automation from executing. Thank you very much for your response, Jamony.