Forum Discussion

Microsoft Defender: Problems with correlations in Azure Sentinel
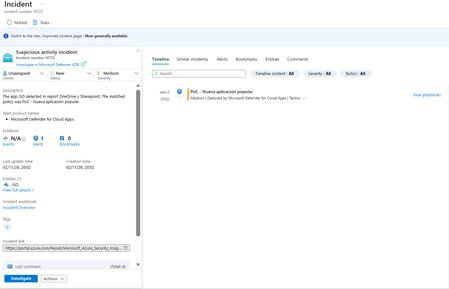

Your screenshots show the alert name remaining specific while the incident receives a broader Defender title, even with one alert. Microsoft documents that Defender correlation can rename incidents, so incident titles are unsuitable as stable automation identifiers. A different title alone does not establish that the alert was grouped incorrectly.
For Sentinel-generated alerts, rebuild the conditions around the originating analytics rule and add tags where further distinction is needed. For Defender-origin alerts, evaluate the Enhanced Alert Trigger, which supports Defender/XDR alerts and granular conditions; the Sentinel analytics-rule-name condition cannot identify a Defender detection.
Test the replacement against both examples before replacing the existing automation. Also compare incident and alert counts separately around October 31 and review each rule’s correlation setting. If the increase remains unexplained, send representative incident IDs and timestamps through a support case; the screenshots cannot establish a service regression.