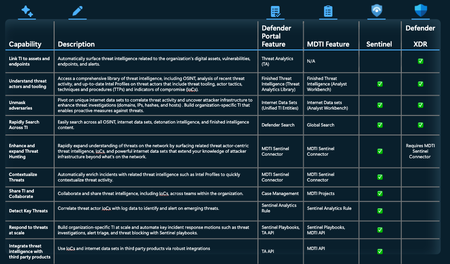
The convergence of MDTI value will provide unified, real-time threat insights at no additional cost
Updated Aug 11, 2026
Version 9.0
Mike_Browning Microsoft
MicrosoftMicrosoft
After the consolidation of Defender TI through XDR, will the "Microsoft Defender Threat Intelligence Analytics rule" (Sentinel Analytics Rule) still be available?
Reference: https://learn.microsoft.com/en-us/azure/sentinel/use-matching-analytics-to-detect-threats